Topics / #hacking
Hacking projects on GitHub
Offensive security and penetration testing resources, from recon to exploits.
As of , the most-starred Hacking projects on GitHub are the-book-of-secret-knowledge (251K stars), Awesome-Hacking (122.9K stars) and PayloadsAllTheThings (81.8K stars). GitHub.Locker tracks 135 Hacking repositories with 2.1M stars combined. The fastest-growing on October 17 was AnyPS5, with +2K stars in a day.
Hot right now
Most stars gained in a day · Oct 17
 +2K
AnyPS5
boykopovar/AnyPS5 · ★ 42.1KAnyPS5 is a tool that automatically ports PS5 executables so they run natively on Linux and Windows, without emulation.
 +291
the-book-of-secret-knowledge
trimstray/the-book-of-secret-knowledge · ★ 251KA massive curated collection of lists, manuals, cheatsheets, blogs, hacks, one-liners and CLI/GUI/web tools that the author gathers from everyday sysadmin, DevOps and security work.
 +234
strix
usestrix/strix · ★ 69.3KStrix is an open-source tool that uses autonomous AI agents to pentest your application like real hackers: it runs your code dynamically, finds vulnerabilities, and proves them with working exploits instead of just flagging suspicious patterns.
 +202
GhostTrack
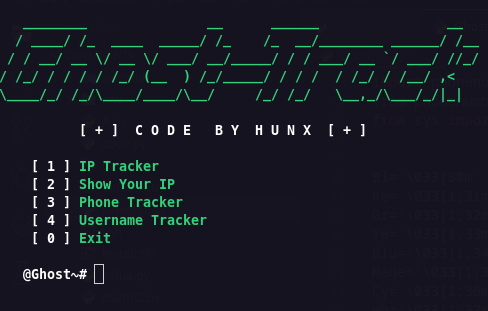
HunxByts/GhostTrack · ★ 19.3KGhostTrack is a Python command-line OSINT tool used to track a target's approximate location or gather details about a phone number, essentially a piece of information-gathering tooling for recon work.
The all-time top
Top 100 of 135 · by stars
- 251K#1 · trimstray/the-book-of-secret-knowledge
the-book-of-secret-knowledge
A massive curated collection of lists, manuals, cheatsheets, blogs, hacks, one-liners and CLI/GUI/web tools that the author gathers from everyday sysadmin, DevOps and security work.
- 122.9K
 #2 · Hack-with-Github/Awesome-Hacking
Awesome-Hacking
A massive index that links out to dozens of other awesome-lists covering nearly every security domain: android security, bug bounty, fuzzing, malware analysis, OSINT, reverse engineering, web hacking, and more.
- 81.8K
 #3 · swisskyrepo/PayloadsAllTheThings
PayloadsAllTheThings
A massive curated collection of payloads, bypass techniques, and exploitation methodology for web application security testing, pentesting, and CTF challenges.
- 4
SecLists
74.2Kdanielmiessler/SecLists · PHPSecLists is a huge collection of ready-made wordlists for security testing: usernames, passwords, URLs, sensitive data patterns, fuzzing payloads, web shells and more, all gathered in one repository.
- 5
strix
69.3Kusestrix/strix · PythonStrix is an open-source tool that uses autonomous AI agents to pentest your application like real hackers: it runs your code dynamically, finds vulnerabilities, and proves them with working exploits instead of just flagging suspicious patterns.
- 6

ImHex
55.4KWerWolv/ImHex · C++ImHex is a hex editor built for reverse engineers, programmers, and anyone analyzing binary data, with a custom pattern language for parsing and highlighting file structures.
- 7

CL4R1T4S
51.3Kelder-plinius/CL4R1T4SCL4R1T4S is a crowd-sourced archive of leaked/extracted system prompts, guidelines, and internal tool definitions from major AI products like ChatGPT, Claude, Gemini, Grok, Perplexity, Cursor, Lovable, and Replit, published for AI transparency.
- 8

x64dbg
49.9Kx64dbg/x64dbg · C++x64dbg is an open-source user-mode debugger for Windows, built specifically for reverse engineering and malware analysis.
- 9

reverse-skill
42.5Kzhaoxuya520/reverse-skill · PowerShellIt is a skill pack that routes AI coding agents to the right reverse engineering, penetration testing, and security research methodology for a given task (APK, binary, JS, CTF, malware, etc.), checks which tools are installed, and runs a repeatable workflow instead of letting the agent guess commands.
- 10
AnyPS5
42.1Kboykopovar/AnyPS5 · C++AnyPS5 is a tool that automatically ports PS5 executables so they run natively on Linux and Windows, without emulation.
- 11
h4cker
29.8KThe-Art-of-Hacking/h4cker · Jupyter NotebookA curated collection of thousands of cybersecurity resources — references, scripts, tools, code, labs, and training material — maintained by Omar Santos as a companion to his books, video courses, and live training.
- 12

awesome-pentest
27.5Kenaqx/awesome-pentestA curated collection of penetration testing and offensive-security resources: tools, books, courses, conferences and practice targets for authorized security testing.
- 13

awesome-flipperzero
24.5Kdjsime1/awesome-flipperzeroA curated list of resources for the Flipper Zero, the pocket multi-tool hacking device, covering firmware, apps, file dumps, cases, modules, and debugging tools.
- 14
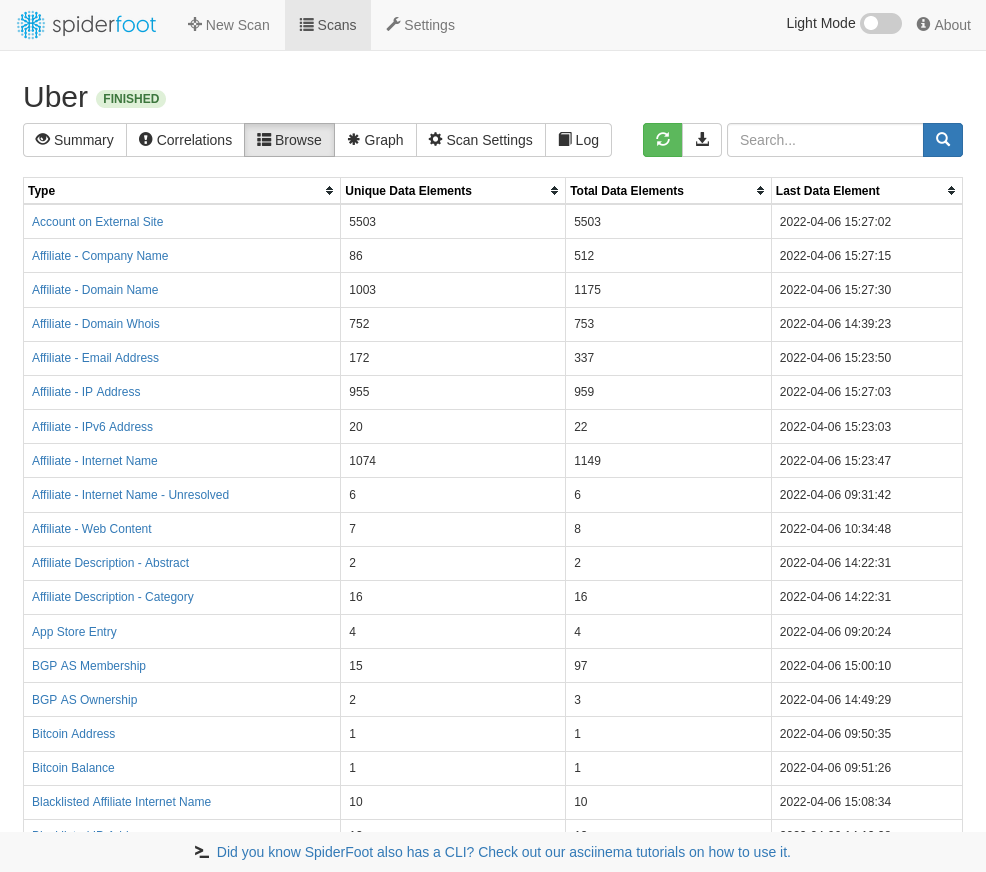
spiderfoot
23.6Ksmicallef/spiderfoot · PythonOpen source OSINT automation — it collects intelligence on a target for threat intel and attack surface mapping, whether you are doing red team recon or checking what your organisation has exposed.
- 15
unleashed-firmware
22.5KDarkFlippers/unleashed-firmware · CUnleashed is custom firmware for the Flipper Zero multitool — a fork of the official firmware (OFW) that adds extra features and improvements while staying compatible with official apps.
- 16

TrollStore
22.4Kopa334/TrollStore · Objective-CTrollStore is a permasigned jailed app for iOS that permanently installs any IPA you open in it. It works via an AMFI/CoreTrust bug: iOS doesn't correctly verify code signatures when a binary has multiple signers, so TrollStore can resign apps with its fake root certificate and keep them installed for good.
- 17

frida
22.3Kfrida/frida · MesonFrida is a dynamic instrumentation toolkit for developers, reverse-engineers, and security researchers, used to instrument running apps; more at frida.re.
- 18

mimikatz
21.9Kgentilkiwi/mimikatz · CA small Windows security tool, originally written to learn C. It is best known for extracting plaintext passwords, hashes, PIN codes and Kerberos tickets from memory, and can perform pass-the-hash, pass-the-ticket or build Golden tickets.
- 19
L1B3RT4S
21.9Kelder-plinius/L1B3RT4SA public collection of jailbreak prompts — the author calls them 'liberation prompts' — meant to make flagship AI models respond without their usual refusals. It is maintained by AI red-teamer elder-plinius.
- 20

Ciphey
21.7Kbee-san/Ciphey · Rustciphey automatically decrypts ciphertext without knowing the key or cipher, decodes encodings and cracks hashes. It is the Rust-built next generation of Ciphey — roughly 7x faster per decode — and the same team intends it to fully replace the original.
- 21
vulhub
21.4Kvulhub/vulhub · DockerfileVulhub is an open-source collection of pre-built, ready-to-use vulnerable Docker environments: with one command you get a working lab for security research, learning, or demos.
- 22

PEASS-ng
20.7Kpeass-ng/PEASS-ng · C#PEASS-ng is a suite of local privilege escalation enumeration tools: LinPEAS for Linux/Unix/macOS and WinPEAS for Windows. They scan a machine for privesc paths and print misconfigurations with nice colors so you can spot them easily.
- 23

RustScan
20.6Kbee-san/RustScan · RustRustScan is an open-source port scanner written in Rust: it finds open ports fast — all 65k ports in as little as 3 seconds — and has a scripting engine for Python, Lua and Shell.
- 24
bettercap
20.2Kbettercap/bettercap · GoA portable all-in-one framework written in Go for recon and attacks on WiFi, Bluetooth Low Energy, wireless HID, CAN-bus and IPv4/IPv6 networks, built for security researchers and red teamers.
- 25

Atmosphere
20.1KAtmosphere-NX/Atmosphere · C++Atmosphère is a work-in-progress custom firmware (CFW) for the Nintendo Switch that replaces and patches core parts of the console's Horizon OS to add new features and customization.
- 26

90DaysOfCyberSecurity
20.1Kfarhanashrafdev/90DaysOfCyberSecurityA free, 90-day self-paced cybersecurity study plan: daily tasks and curated resources that take you from networking basics to ethical hacking, ending with job-hunting help.
- 27
Sandboxie
19.7Ksandboxie-plus/Sandboxie · CSandboxie is a sandbox-based isolation tool for Windows that lets you run or install untrusted programs in an isolated virtual environment without permanently modifying your drives or registry.
- 28
cheat-engine
19.3Kcheat-engine/cheat-engine · PascalCheat Engine is a development environment focused on modding games and applications for personal use. Its repository tags describe it as a memory scanner and debugger.
- 29
GhostTrack
19.3KHunxByts/GhostTrack · PythonGhostTrack is a Python command-line OSINT tool used to track a target's approximate location or gather details about a phone number, essentially a piece of information-gathering tooling for recon work.
- 30

Micro8
18KMicropoor/Micro8A free, open-source series of penetration-testing lessons written by veteran Chinese pentester Micropoor and published as a GitBook. It covers code audit, web, intranet and domain penetration, tunneling, and log-based tracing.
- 31

Awesome-Hacking-Resources
17.5Kvitalysim/Awesome-Hacking-ResourcesA curated collection of hacking, penetration testing and AI red-teaming resources — courses, YouTube channels, CTF platforms and guides, picked to make you better at offensive security.
- 32

awesome-hacking
17.3Kcarpedm20/awesome-hackingA curated list of hacking tutorials, tools and resources covering system exploitation, reverse engineering, web security, network security, forensics, cryptography and wargames.
- 33
zphisher
17Khtr-tech/zphisher · HTMLZphisher is an automated phishing tool with 30+ ready-made login-page templates, written as a beginners-friendly shell script and intended purely for education.
- 34

rdpwrap
16.9Kstascorp/rdpwrap · PascalRDP Wrapper Library enables Remote Desktop Host support and concurrent RDP sessions on Windows editions that normally restrict it (like Home editions), for home use.
- 35

hammerspoon
16.3KHammerspoon/hammerspoon · Objective-CHammerspoon is a bridge between macOS and a Lua scripting engine, letting you automate and control your Mac through extensions that expose system functionality to Lua scripts.
- 36
impacket
16.2Kfortra/impacket · PythonImpacket is a collection of Python classes for working with network protocols, giving low-level programmatic access to packets and, for some protocols like SMB1-3 and MSRPC, full protocol implementations.
- 37
evilginx2
15.7Kkgretzky/evilginx2 · GoEvilginx is a man-in-the-middle attack framework used for phishing login credentials along with session cookies, which lets an attacker bypass 2-factor authentication.
- 38

hacker-roadmap
15.7Ksundowndev/hacker-roadmapThis is a curated roadmap and toolkit index for learning and practicing ethical hacking: it explains what penetration testing is and groups hundreds of security tools, wordlists and references by category (recon, password attacks, wireless, exploitation, web hacking, post-exploitation, frameworks).
- 39

social-engineer-toolkit
15.4Ktrustedsec/social-engineer-toolkit · PythonThe Social-Engineer Toolkit (SET) is an open-source penetration testing framework for authorized social-engineering assessments, giving security teams guided attack vectors to test user awareness and validate controls.
- 40
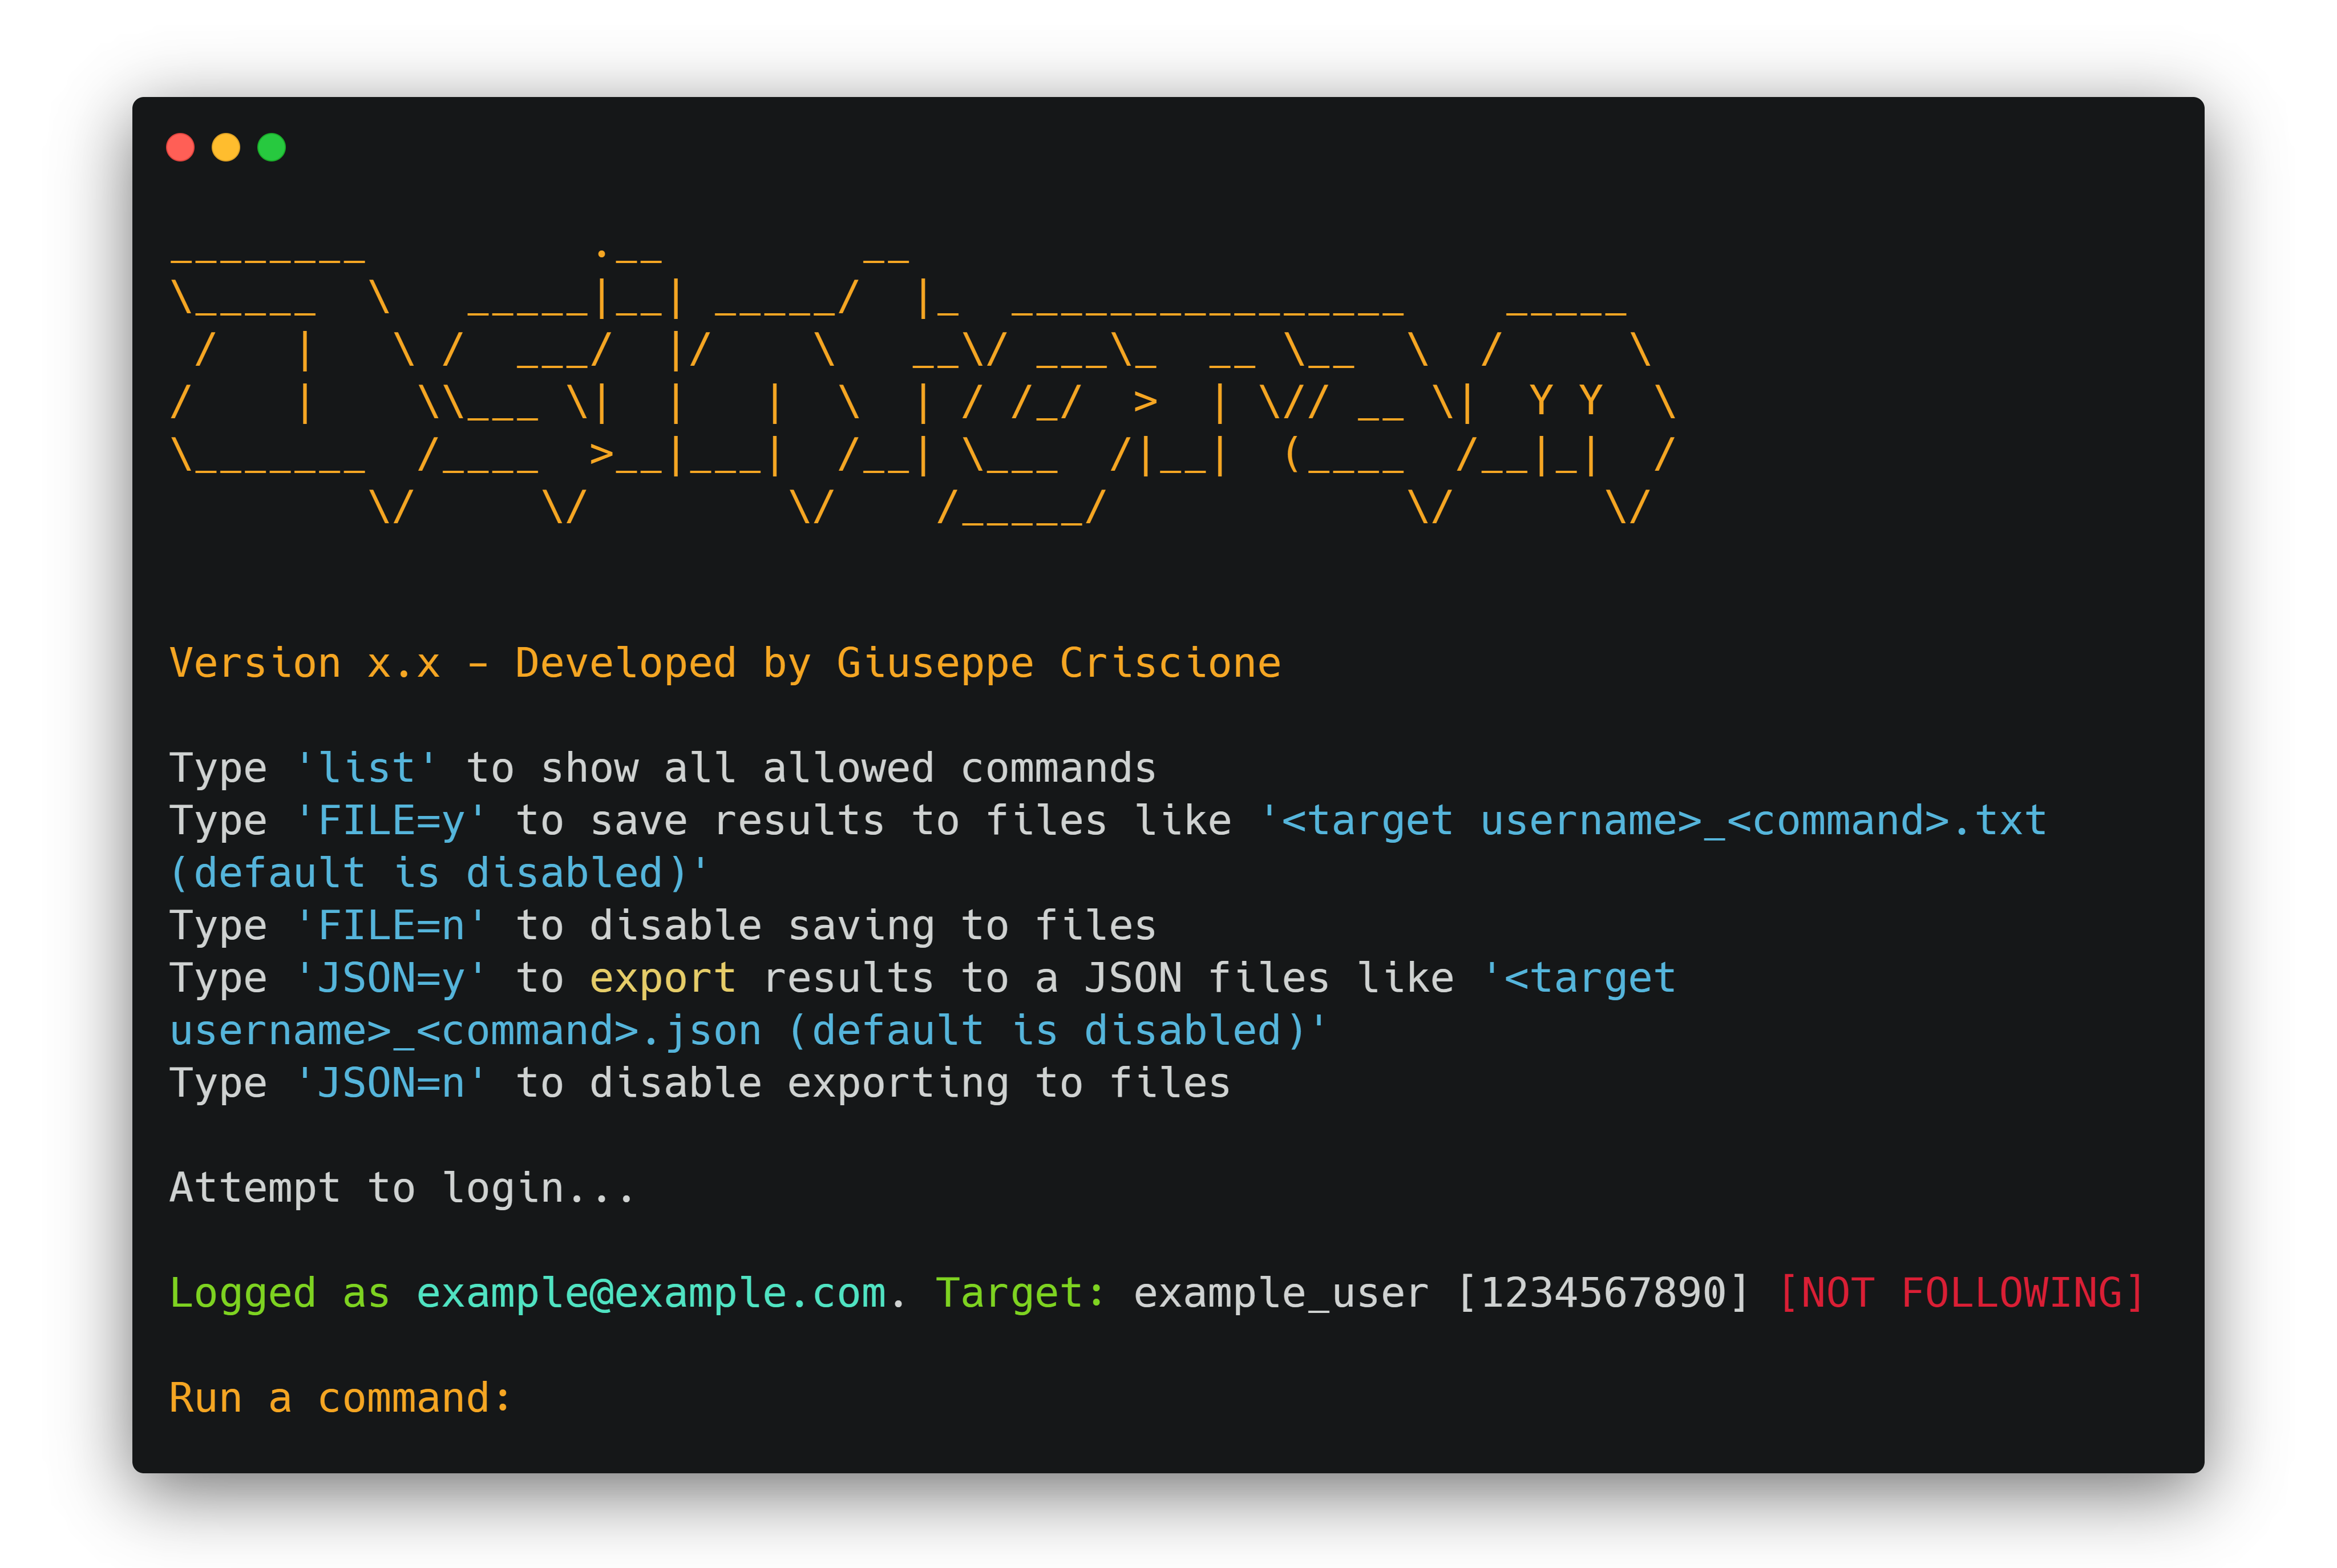
Osintgram
15.1KDatalux/Osintgram · PythonOsintgram is an OSINT tool for Instagram that lets you collect, analyze, and run reconnaissance on any public Instagram account via an interactive shell, just by giving its nickname.
- 41
esp8266_deauther
15KSpacehuhnTech/esp8266_deauther · CESP8266 Deauther is open-source firmware for the ESP8266 chip that lets you scan nearby WiFi networks, send deauthentication packets to disconnect devices, and spin up dozens of fake WiFi networks to confuse scanners - an affordable platform for testing and learning about WiFi security.
- 42

awesome-security
15Ksbilly/awesome-securityA curated, categorized collection of well-known security resources — software, libraries, documents, books and other cool stuff — maintained by the community in the spirit of awesome-php and awesome-python.
- 43

dirsearch
15Kmaurosoria/dirsearch · PythonDirsearch is an advanced command-line web path brute-forcer used to discover hidden files and directories on websites for security testing.
- 44
wifiphisher
14.9Kwifiphisher/wifiphisher · PythonWifiphisher is a rogue access point framework for conducting Wi-Fi phishing and man-in-the-middle attacks against wireless clients, used in red team and penetration testing engagements.
- 45
Reverse-Engineering
14.8Kmytechnotalent/Reverse-Engineering · AssemblyA free, massive collection of reverse engineering and hacking tutorials covering x86, x64, ARM (32/64-bit), AVR, RISC-V, Windows internals, malware analysis, embedded systems, Rust, Go, Wasm, and more, delivered as free ebooks/lessons.
- 46
subfinder
14.6Kprojectdiscovery/subfinder · GoSubfinder is a fast passive subdomain enumeration tool that returns valid subdomains for a website by querying passive online sources, built for penetration testers and bug bounty hunters.
- 47
HackBrowserData
14.6KmoonD4rk/HackBrowserData · GoHackBrowserData is a command-line tool that decrypts and exports browser data — passwords, cookies, history, bookmarks, credit cards and more — from Chromium-based browsers, Firefox and Safari, built for security research.
- 48

hacker101
14.6KHacker0x01/hacker101 · SCSSHacker101 is a free online class for web and mobile security from HackerOne (the Hacker0x01 org), aimed at everyone from programmers curious about bug bounties to seasoned security professionals.
- 49
awesome-malware-analysis
14.3Krshipp/awesome-malware-analysisA curated 'awesome list' of malware analysis tools and resources, covering sample collection, sandboxes, detection tools, threat intelligence feeds, reverse engineering, and forensics.
- 50
juice-shop
14.1Kjuice-shop/juice-shop · TypeScriptOWASP Juice Shop is an intentionally insecure web application (a fake online juice store) built for security training, awareness demos, CTFs, and testing security tools.
- 51

PENTESTING-BIBLE
14KblaCCkHatHacEEkr/PENTESTING-BIBLEA curated catalog of over 200 numbered links to pentesting articles, bug bounty write-ups, cheat sheets and other security lists — a reading collection, not software.
- 52

awesome-web-security
13.9Kqazbnm456/awesome-web-security · PythonA curated list of web security materials and resources, organized by vulnerability class and attack type (XSS, SQL injection, CSRF, SSRF, XXE, deserialization, OAuth, JWT, and more), plus cheatsheets, tools, and write-ups for penetration testing.
- 53

DVWA
13.9Kdigininja/DVWA · PHPDVWA (Damn Vulnerable Web Application) is a PHP/MariaDB web app that is deliberately full of security bugs, built as a legal practice target for security pros, students, and developers to learn web application security.
- 54
WeChatTweak
13.8Ksunnyyoung/WeChatTweak · SwiftWeChatTweak is a macOS command-line tool that patches the installed WeChat desktop client to block message-recall notices, disable WeChat's automatic updater, and let you run multiple WeChat instances at once.
- 55

nmap
13.8Knmap/nmap · CNmap is the Network Mapper — a free, open-source tool for network discovery and security scanning. It finds live hosts, open ports, and the services running on them, from a single machine up to whole subnets.
- 56
pwntools
13.8KGallopsled/pwntools · PythonPwntools is a CTF framework and exploit development library written in Python, built for rapid prototyping with the goal of making exploit writing as simple as possible.
- 57
GTFOBins.github.io
13.8KGTFOBins/GTFOBins.github.io · YAMLGTFOBins is a curated list of Unix-like executables that can be abused to bypass local security restrictions in misconfigured systems — for example, binaries a restricted user can turn into a root shell.
- 58

Photon
13.3Ks0md3v/Photon · PythonPhoton is a fast web crawler built for OSINT (open-source intelligence) gathering, extracting URLs, emails, social media accounts, secret keys, subdomains and more while it crawls a target site.
- 59
mastg
13.3KOWASP/mastg · PythonA comprehensive OWASP manual for mobile app security testing and reverse engineering. It gives technical processes for verifying the weaknesses listed in the OWASP Mobile Security Weakness Enumeration (MASWE).
- 60

PowerSploit
13.1KPowerShellMafia/PowerSploit · PowerShellPowerSploit is a collection of PowerShell modules that penetration testers use during all phases of an assessment, covering code execution, persistence, privilege escalation, credential theft, exfiltration and reconnaissance on Windows systems.
- 61
hexstrike-ai
12.9K0x4m4/hexstrike-ai · PythonHexStrike AI MCP Agents is an MCP server that lets AI agents like Claude, GPT, or Copilot autonomously run 150+ real cybersecurity tools for automated pentesting, bug bounty hunting, CTF challenges, and vulnerability discovery.
- 62
atomic-red-team
12.7Kredcanaryco/atomic-red-team · CAtomic Red Team is a library of small, portable security tests, each mapped to a specific MITRE ATT&CK technique, that security teams run to check whether their defenses actually detect real attacker behavior.
- 63

wifi-cracking
12.7Kbrannondorsey/wifi-crackingA step-by-step tutorial for cracking WPA/WPA2 Wi-Fi passwords: capture a handshake with Airodump-ng, then crack it offline with Aircrack-ng or Hashcat.
- 64
urh
12.6Kjopohl/urh · PythonURH (Universal Radio Hacker) is a suite for investigating wireless protocols: it captures radio signals via SDR hardware, demodulates them with automatic modulation detection, and helps you reverse-engineer the bits and bytes flying over the air.
- 65

hacktricks
12.6KHackTricks-wiki/hacktricks · JavaScriptA free, open wiki of hacking tricks and techniques — everything the author has learnt from CTFs, real-world apps and security research, organized into a browsable reference with 12.5k+ GitHub stars.
- 66

thc-hydra
12.4Kvanhauser-thc/thc-hydra · CHydra is a parallelized network login cracker by van Hauser / THC: a proof-of-concept tool showing researchers and security consultants how easily a remote system can be broken into through weak passwords. It supports over 50 protocols.
- 67

fsociety
12.3KManisso/fsociety · Pythonfsociety is a penetration testing toolkit that bundles dozens of existing hacking tools (Nmap, sqlmap, WPScan, Reaver, etc.) behind one menu-driven script, inspired by the tools used in the 'Mr. Robot' TV series.
- 68

OSINT-Framework
12.3Klockfale/OSINT-Framework · JavaScriptOSINT Framework is a curated, browsable index of free OSINT (open-source intelligence) tools and resources, organized into a clickable category tree so you can find the right tool for a given task.
- 69

Resources-for-Beginner-Bug-Bounty-Hunters
12.3Knahamsec/Resources-for-Beginner-Bug-Bounty-HuntersA curated collection of resources for people getting started with web hacking and bug bounty hunting, including blog posts, talks, books, tools, labs and vulnerability-type guides.
- 70

movies-for-hackers
12Kk4m4/movies-for-hackers · ShellIt is a curated list of movies every hacker and cyberpunk fan should watch, with each title scored by its IMDb rating — plus a section of TV shows.
- 71

awesome-ctf
11.9Kapsdehal/awesome-ctf · JavaScriptA curated list of frameworks, libraries, tools, and resources for Capture The Flag (CTF) competitions, covering everything from building challenges to solving them.
- 72

TheFatRat
11.5Kscreetsec/TheFatRat · CTheFatRat is an exploiting tool that compiles malware from famous payloads — an easy way to generate backdoors built to slip past most anti-virus software.
- 73
Sn1per
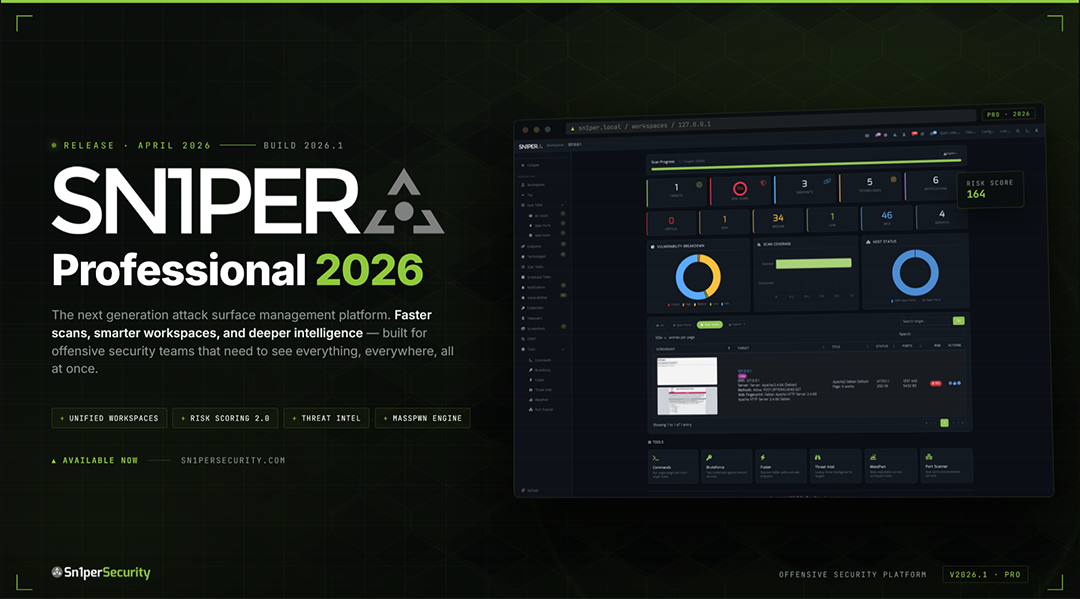
11.5K1N3/Sn1per · ShellSn1per is an offensive-security platform that bundles reconnaissance, vulnerability scanning, exploitation and reporting into one workspace, orchestrating 600+ exploits and 90+ third-party tools for pentesters and attack-surface-management teams.
- 74

awesome-hacker-search-engines
11.3Kedoardottt/awesome-hacker-search-engines · ShellA curated list of search engines useful for penetration testing, vulnerability assessment, red/blue team operations, bug bounty hunting, and general OSINT work.
- 75

beef
11.1Kbeefproject/beef · JavaScriptBeEF (Browser Exploitation Framework) is a penetration testing tool that focuses on the web browser, letting a tester assess the real security posture of a target by using client-side attack vectors instead of network-perimeter exploits.
- 76
_s
11KAutomattic/_s · CSS_s (Underscores) is an archived, officially inactive WordPress starter theme by Automattic, meant as a blank slate developers hack into their own custom theme rather than use as-is.
- 77

webshell
10.8Ktennc/webshell · PHPIt's a community collection of webshells - scripts that give you control of a web server once uploaded - covering all the common server-side languages and maintained by tennc with 10k+ stars.
- 78

Red-Teaming-Toolkit
10.8Kinfosecn1nja/Red-Teaming-ToolkitIt is a curated list of cutting-edge open-source security tools for red teamers and threat hunters, covering the full attack lifecycle from reconnaissance to exfiltration.
- 79
bbot
10.7Kblacklanternsecurity/bbot · PythonBBOT is a recursive internet scanner for hackers — it automates recon, bug bounty work and attack surface management (ASM), inspired by Spiderfoot.
- 80
reverse-engineering
10.6KwtsxDev/reverse-engineeringA curated list of reverse engineering resources: books, courses, practice grounds, and a big toolbox section spanning hex editors, disassemblers, debuggers, and dynamic analysis tools.
- 81

BloodHound-Legacy
10.6KSpecterOps/BloodHound-Legacy · PowerShellBloodHound Legacy is a security tool that uses graph theory to map hidden relationships and attack paths inside an Active Directory environment, helping find the shortest route to Domain Admin — hence its tagline 'Six Degrees of Domain Admin'.
- 82

awesome-honeypots
10.6Kparalax/awesome-honeypots · PythonA curated, categorized list of honeypot software and related tools used by security researchers to deceive attackers, log their behavior, and study exploitation attempts.
- 83

nishang
10.2Ksamratashok/nishang · PowerShellNishang is a framework and large collection of PowerShell scripts and payloads for offensive security, penetration testing, and red teaming, covering every phase of an engagement.
- 84
Cybersecurity-Projects
8.3KCarterPerez-dev/Cybersecurity-Projects · GoThis is a growing collection of 70 hands-on cybersecurity projects with full source code, organized into four difficulty tiers, plus 10 certification roadmaps and curated learning resources for cybersecurity careers.
- 85

android-reverse-engineering-skill
8.2KSimoneAvogadro/android-reverse-engineering-skill · ShellA Claude Code skill that decompiles Android APK/XAPK/JAR/AAR files and extracts the HTTP APIs used by the app — Retrofit endpoints, OkHttp calls, hardcoded URLs, and authentication patterns — so you can document and reproduce them without the original source code.
- 86

Claude-Red
7.6KSnailSploit/Claude-Red · Pythonclaude-red is a curated library of offensive security skills for the Claude Skills system: structured SKILL.md files that prime Claude with expert-level methodology for one attack surface each, from SQLi to shellcode.
- 87

AirCard
6.7KMak5er/AirCard · SwiftAirCard is a macOS app that lets you customize Apple Wallet card skins and iOS lockscreen passcode keypad themes on iOS 18+ without jailbreaking your iPhone.
- 88
Decepticon
6.3KBitterSecurity/Decepticon · PythonDecepticon is a professional autonomous Red Team agent that runs full attack chains — reconnaissance, exploitation, privilege escalation, lateral movement, and C2 — the way a real adversary would, instead of just scanning and printing a report.
- 89
Agentic-Bug-Hunter
5.4Kawarexone/Agentic-Bug-Hunter · PythonAgentic Bug Hunter is an AI-powered bug bounty toolkit that runs recon, tests for vulnerabilities, validates findings against a strict gate, and writes submission-ready reports for HackerOne, Bugcrowd, Intigriti, or Immunefi, right from your terminal.
- 90
device-activity-tracker
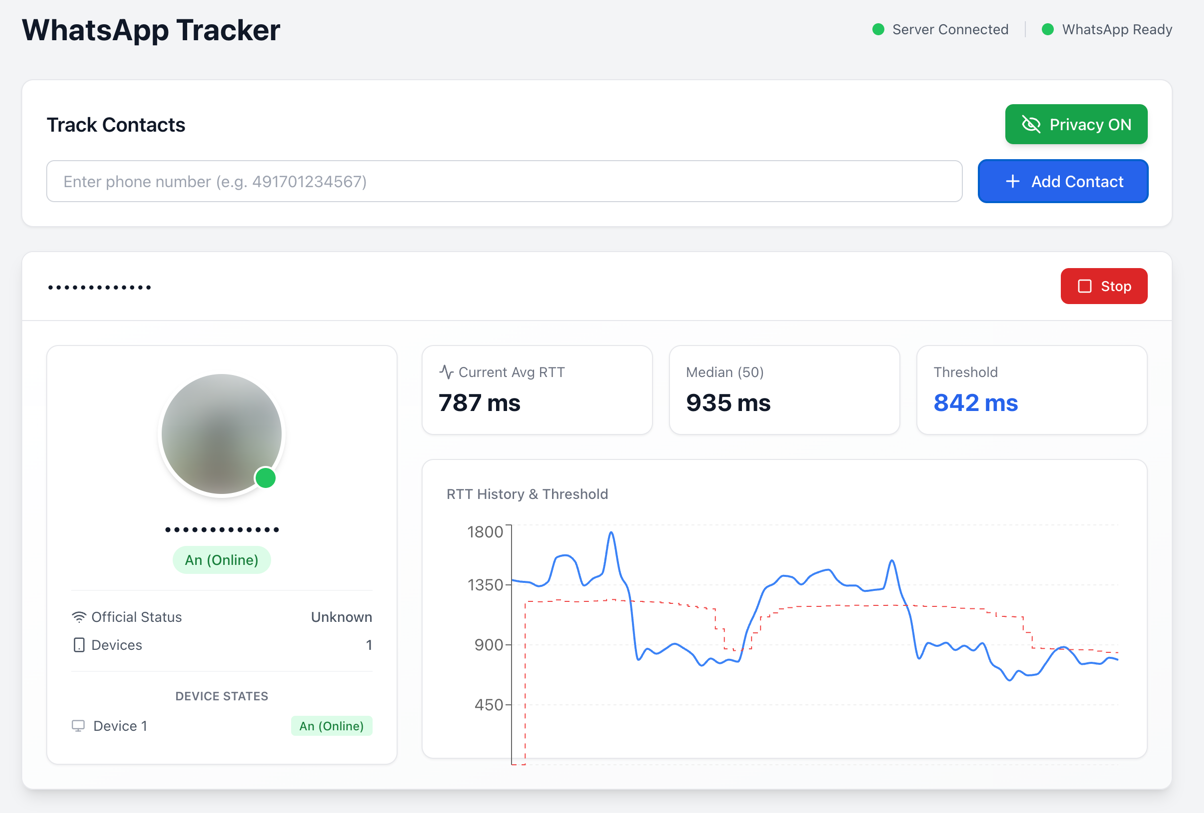
5.2Kgommzystudio/device-activity-tracker · TypeScriptThis is a proof-of-concept security research tool that monitors WhatsApp and Signal users by measuring the Round-Trip Time (RTT) of message delivery receipts, revealing whether a target's device is actively in use, idle, or offline.
- 91

exploitarium
5.2Kbikini/exploitarium · PythonExploitarium is a single consolidated archive of the author's public proof-of-concept exploits and vulnerability research writeups, merging dozens of their former standalone PoC repos into one place.
- 92
dirtyfrag
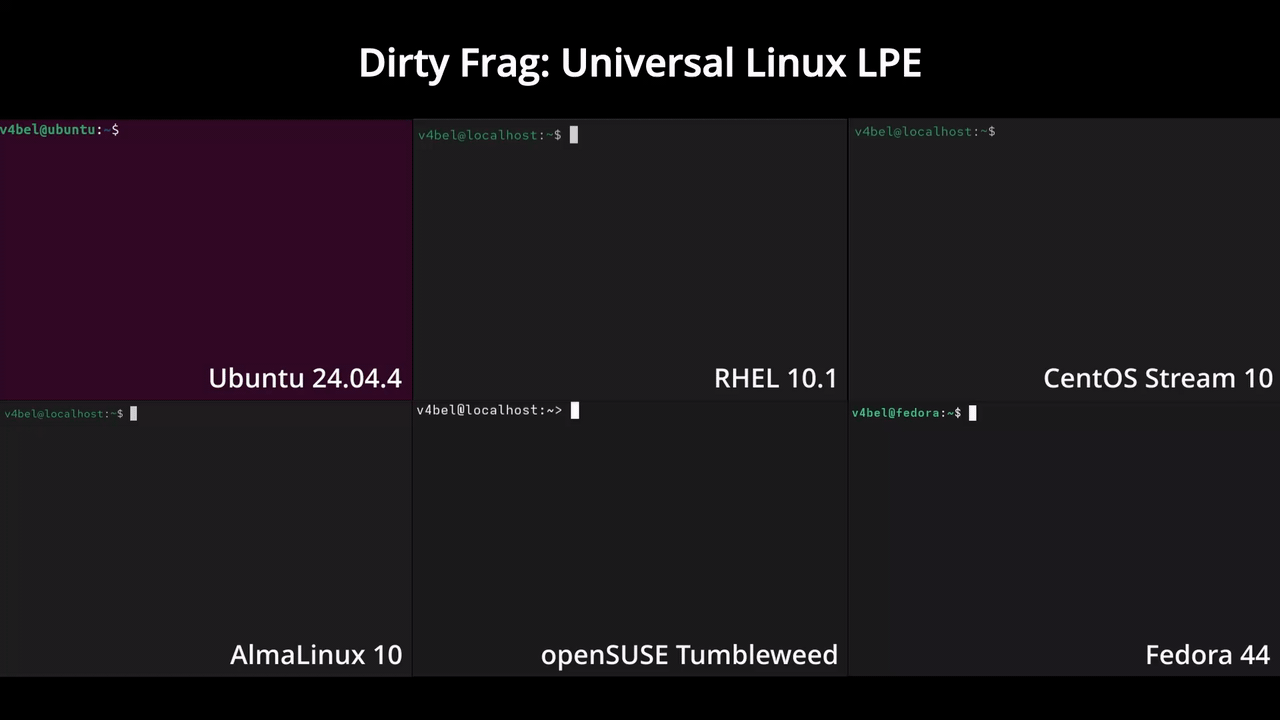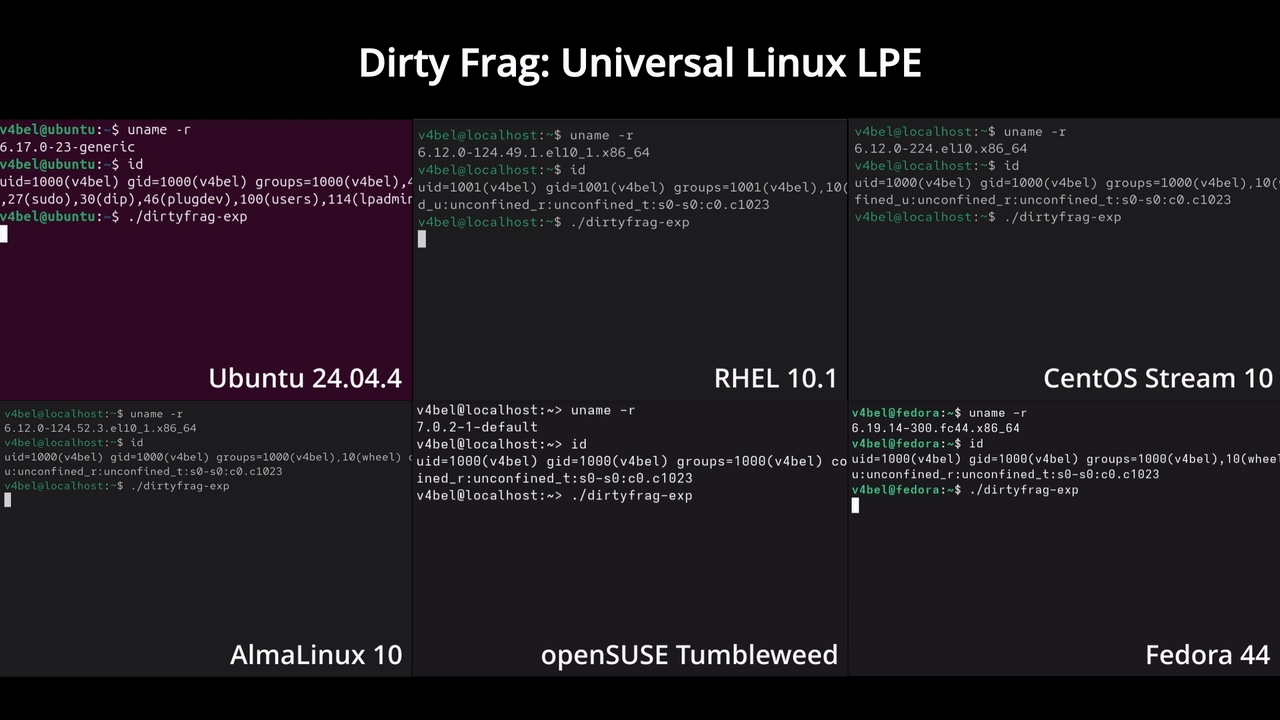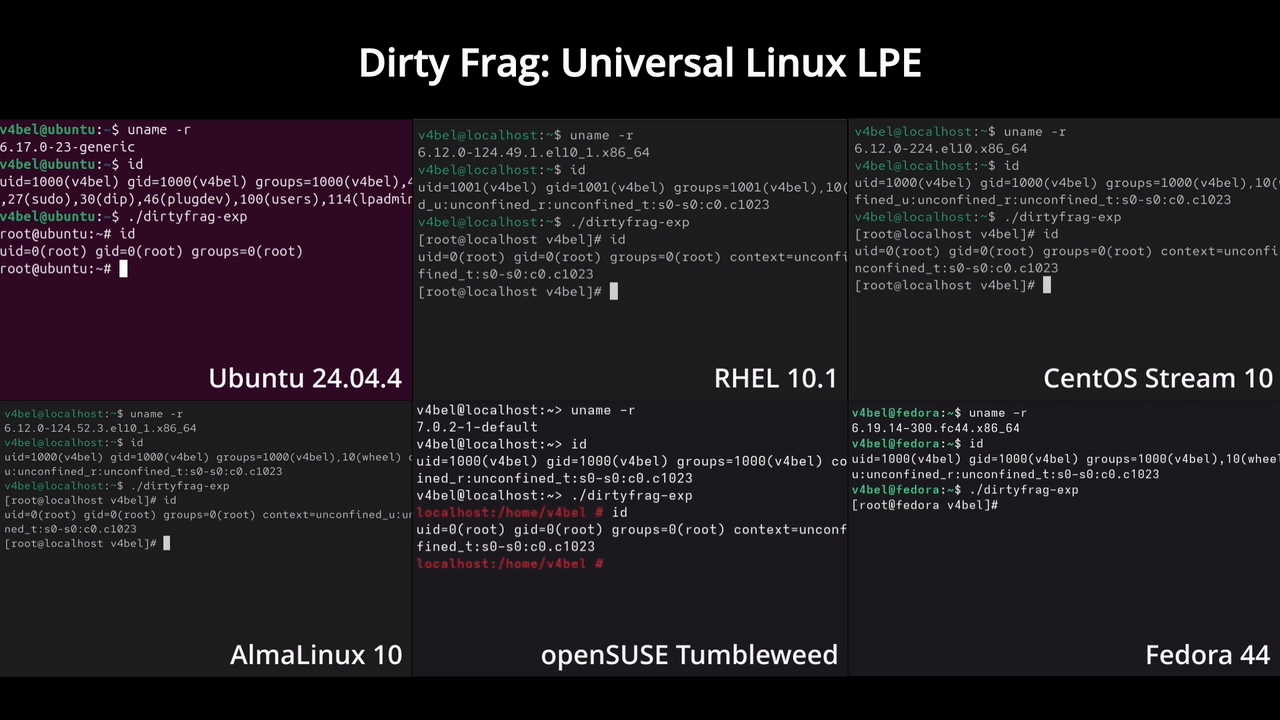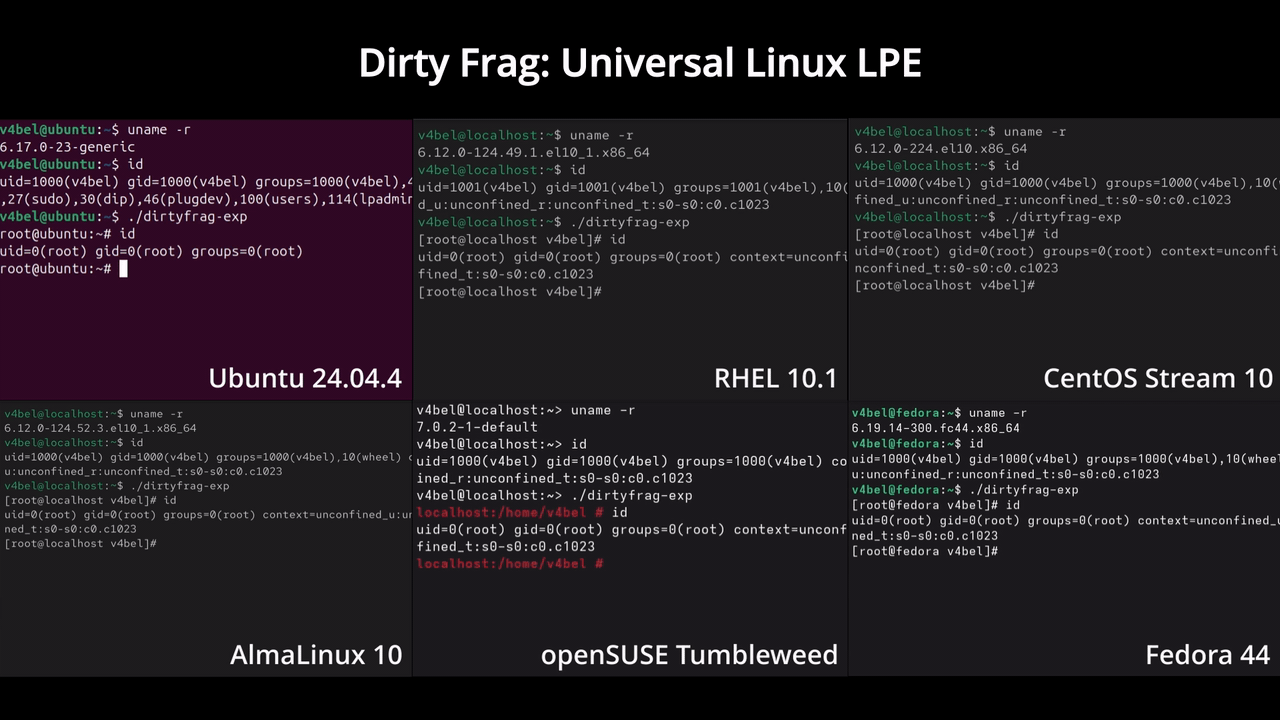
5.1KV4bel/dirtyfrag · CDirty Frag is a proof-of-concept Linux kernel local privilege escalation exploit that chains two page-cache write vulnerabilities (CVE-2026-43284 and CVE-2026-43500) to obtain root on major Linux distributions.
- 93
reverse-SynthID
5Kaloshdenny/reverse-SynthID · Pythonreverse-SynthID reverse-engineers Google's SynthID watermark embedded in Gemini-generated images using signal processing and spectral analysis, and ships tools that detect and surgically bypass that watermark without any access to Google's proprietary encoder/decoder.
- 94
METATRON
4.2Ksooryathejas/METATRON · PythonMetatron is a CLI-based AI penetration testing assistant that runs real recon tools against a target and lets a locally-hosted LLM analyze the results, suggest exploits, and recommend fixes, with no cloud or API keys involved.
- 95

copy-fail-CVE-2026-31431
4.1Ktheori-io/copy-fail-CVE-2026-31431 · PythonThis repository is a technical writeup and proof-of-concept for CVE-2026-31431, a 9-year-old Linux kernel local privilege escalation (LPE) vulnerability found by Theori's AI vulnerability research tool, Xint Code.
- 96

misaka26
4Kstraight-tamago/misaka26misaka26 is an iOS/iPadOS customization tool that uses the same underlying bug as TrollRestore to unlock hidden system features on supported devices, running iOS 16.0 through 26.1 and the 26.2 beta 1, without a full jailbreak.
- 97
grok-bot-0.18-reconstructed
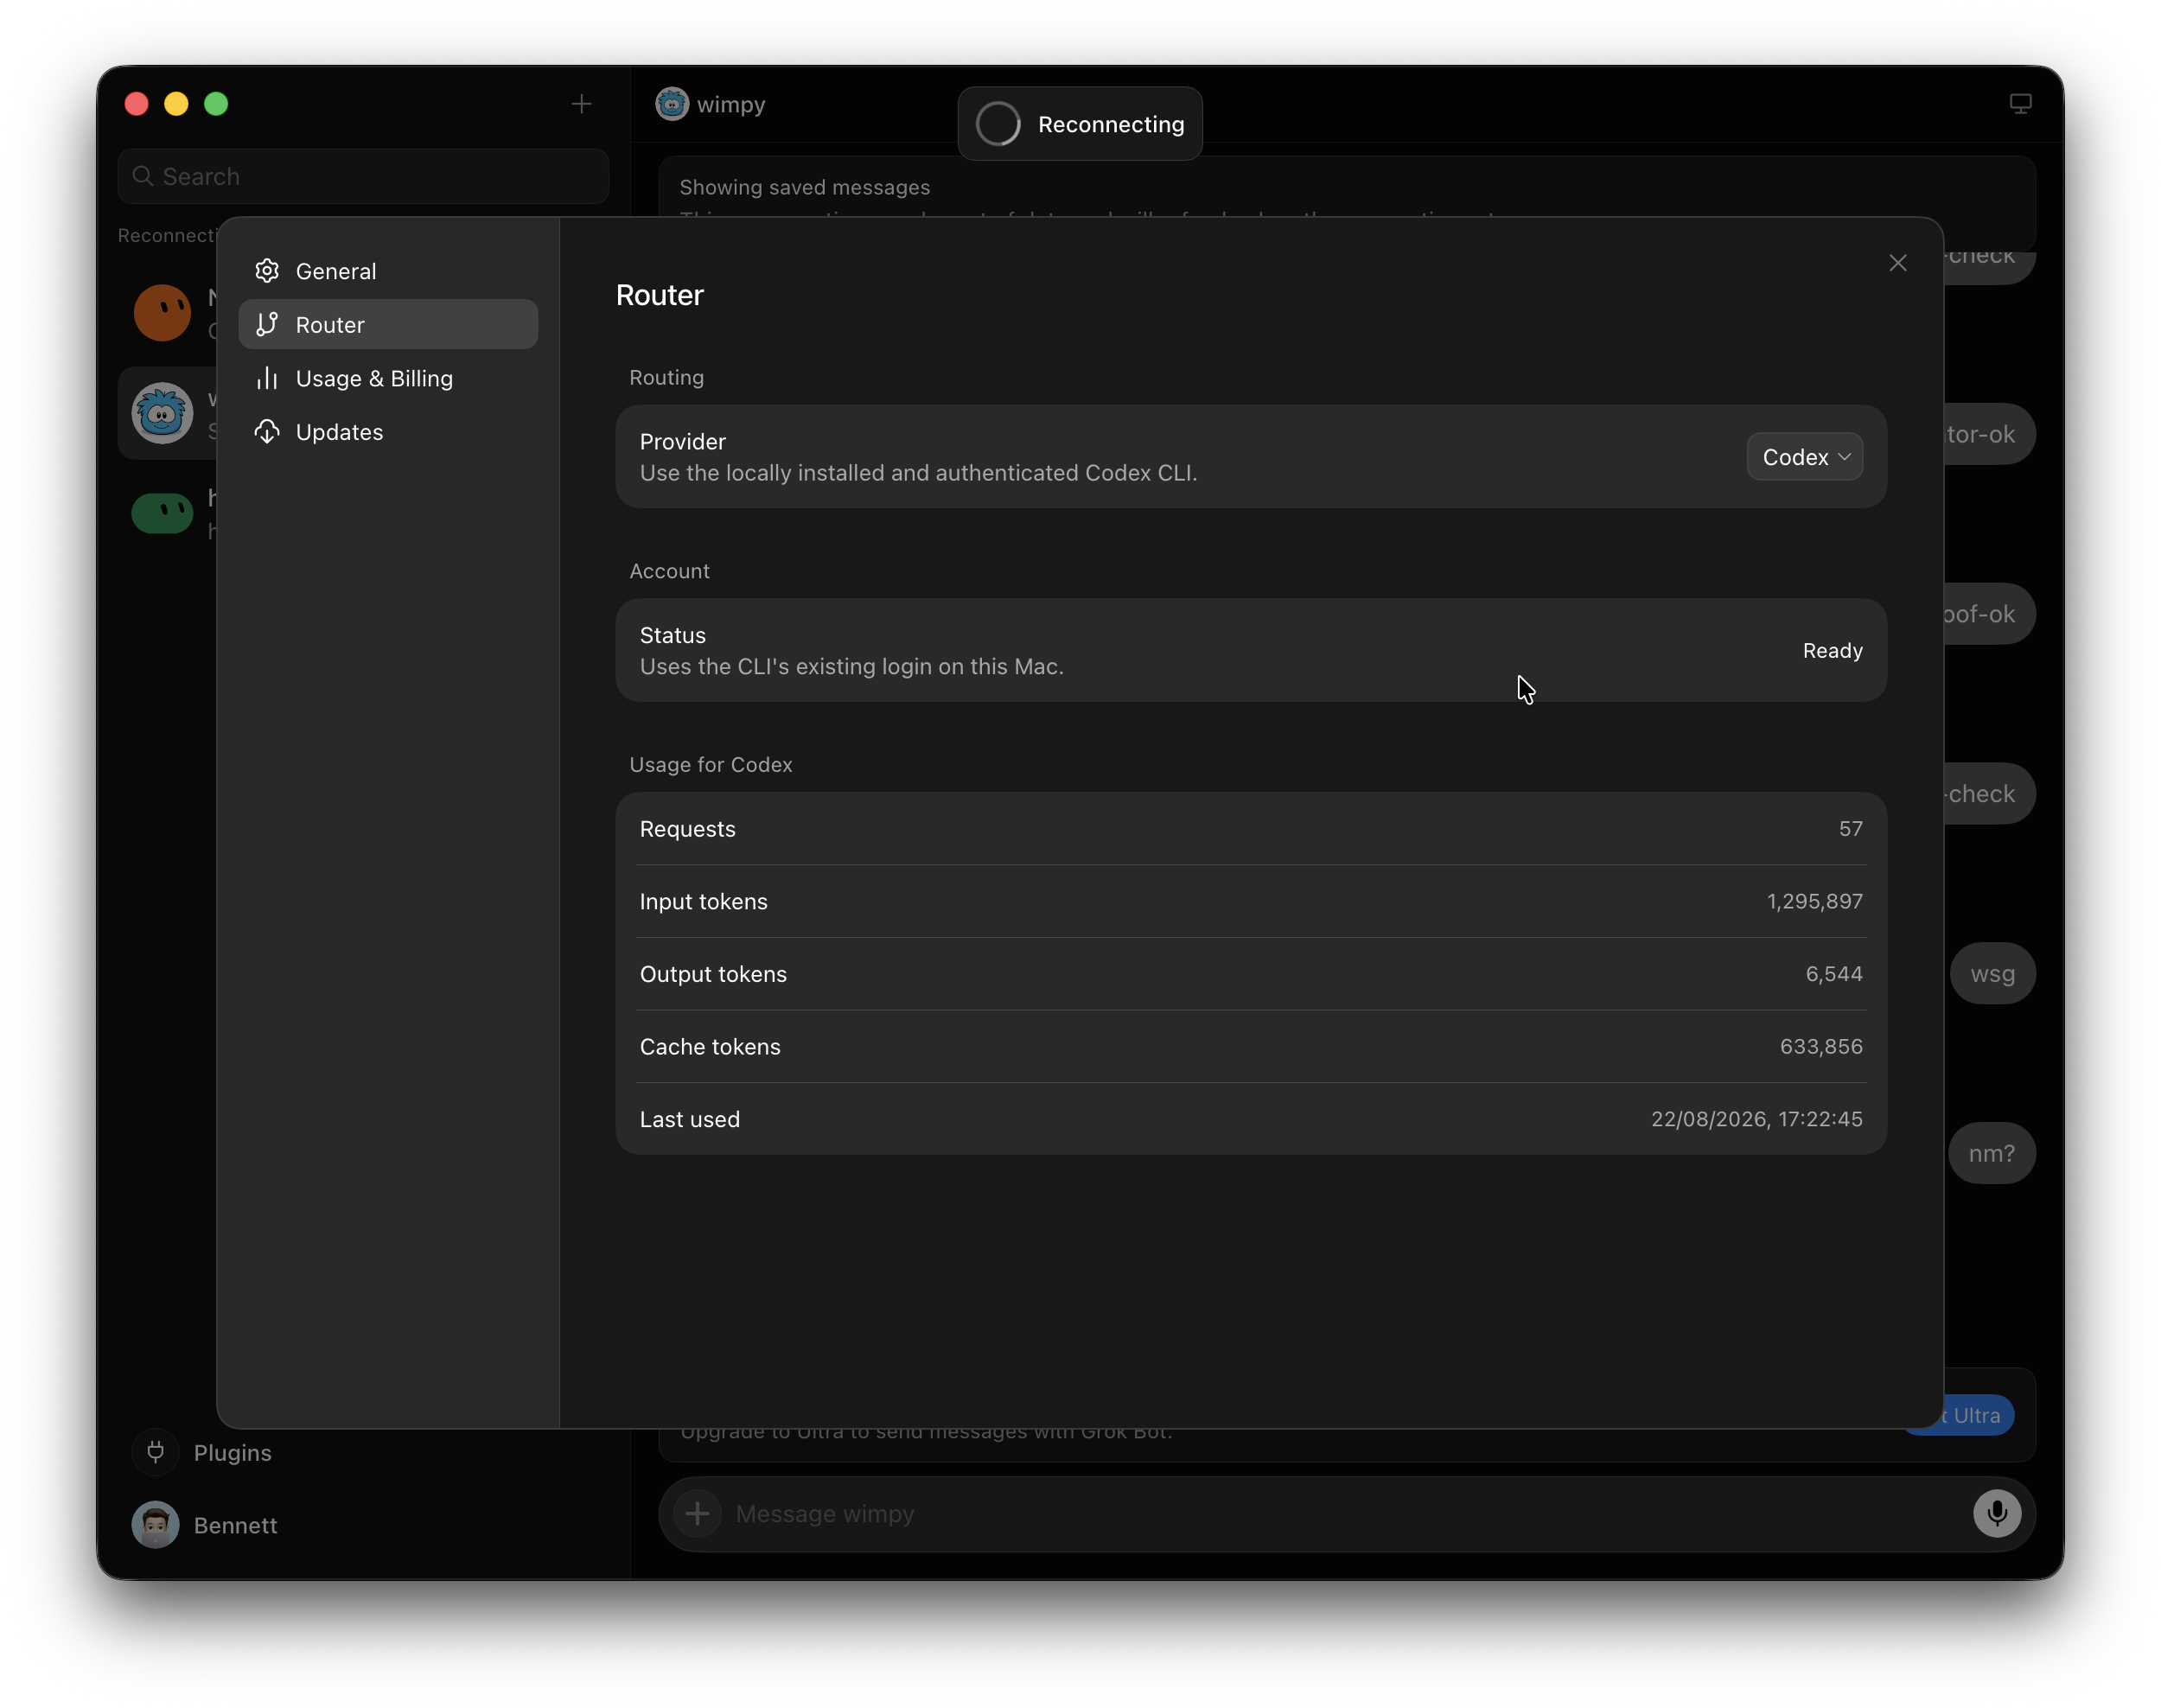
3.5Kb-nnett/grok-bot-0.18-reconstructed · TypeScriptIt's an unofficial, source-oriented reconstruction of the publicly shipped Grok Bot 0.18.0 macOS app, rebuilt into readable TypeScript sources and extended with an inference router, MCP tools, local usage tracking, and an optional local Docker sandbox.
- 98
redamon
3.1Ksamugit83/redamon · PythonRedAmon is an open-source, self-hosted AI framework that chains reconnaissance, exploitation and post-exploitation into one pipeline, maps the attack surface into a Neo4j graph, and then triages findings and opens GitHub pull requests that fix what it discovers.
- 99

jailbreaks
3.1Ktogg53192-cmd/jailbreaksThis is a personal collection of jailbreak prompts meant to bypass the safety restrictions of AI chatbots like ChatGPT.
- 100
dsh-infinite-gen-5
3KMinglink/dsh-infinite-gen-5 · JavaScriptThis is a system-prompt injection plugin for the DeepSeek Harness (dsh) ecosystem that tries to bypass DeepSeek-V4.1 Flash's safety guardrails, framed as a red-team robustness benchmark suite for studying model defenses.
Showing the 100 most-starred of 135. See every one in the catalog.
Related topics
Often tagged together
- security977
- cybersecurity244
- security-tools281
- penetration-testing125
- pentesting112
- reverse-engineering222
- open-source5,666
- linux4,181
- windows3,401
- exploit51
- red-team78
- macos3,544
- offensive-security77
- python2,396
- hacking-tool75
- cli2,227
- mit3,311
- resources706
- curated-list634
- tool1,294
- awesome-list497
- docker1,657
- osint68
- terminal1,100