Topics / #security-tools
Security-tools projects on GitHub
Software for vulnerability scanning, debugging, and security assessment.
As of , the most-starred Security-tools projects on GitHub are ghidra (89.8K stars), PayloadsAllTheThings (81.8K stars) and SecLists (74.2K stars). GitHub.Locker tracks 282 Security-tools repositories with 3.4M stars combined. The fastest-growing on October 16 was ghidra, with +757 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
 +757
ghidra
NationalSecurityAgency/ghidra · ★ 89.8KGhidra is a software reverse engineering (SRE) framework created and maintained by the NSA's Research Directorate, used to disassemble, decompile, graph, and analyze compiled code.
 +375
security-audit-skill
cloudflare/security-audit-skill · ★ 30.4KA Cloudflare coding-agent skill that turns your agent into a security auditor: it orchestrates isolated agents through a structured, multi-phase audit and returns independently verified, machine-readable findings.
pentagi
vxcontrol/pentagi · ★ 30.8KPentAGI (Penetration testing Artificial General Intelligence) is a fully autonomous AI agent system that performs complex penetration testing tasks for you.
 +214
strix
usestrix/strix · ★ 69.1KStrix is an open-source tool that uses autonomous AI agents to pentest your application like real hackers: it runs your code dynamically, finds vulnerabilities, and proves them with working exploits instead of just flagging suspicious patterns.
The all-time top
Top 100 of 282 · by stars
- 89.8K#1 · NationalSecurityAgency/ghidra
ghidra
Ghidra is a software reverse engineering (SRE) framework created and maintained by the NSA's Research Directorate, used to disassemble, decompile, graph, and analyze compiled code.
- 81.8K
 #2 · swisskyrepo/PayloadsAllTheThings
PayloadsAllTheThings
A massive curated collection of payloads, bypass techniques, and exploitation methodology for web application security testing, pentesting, and CTF challenges.
- 74.2K
 #3 · danielmiessler/SecLists
SecLists
SecLists is a huge collection of ready-made wordlists for security testing: usernames, passwords, URLs, sensitive data patterns, fuzzing payloads, web shells and more, all gathered in one repository.
- 4
strix
69.1Kusestrix/strix · PythonStrix is an open-source tool that uses autonomous AI agents to pentest your application like real hackers: it runs your code dynamically, finds vulnerabilities, and proves them with working exploits instead of just flagging suspicious patterns.
- 5

ImHex
55.4KWerWolv/ImHex · C++ImHex is a hex editor built for reverse engineers, programmers, and anyone analyzing binary data, with a custom pattern language for parsing and highlighting file structures.
- 6

x64dbg
49.9Kx64dbg/x64dbg · C++x64dbg is an open-source user-mode debugger for Windows, built specifically for reverse engineering and malware analysis.
- 7
shannon
49KKeygraphHQ/shannon · TypeScriptShannon is an autonomous AI pentester that analyzes your web application's source code, maps attack vectors, and then executes real exploits against the running app to prove vulnerabilities before they reach production — 'no exploit, no report'.
- 8
acme.sh
47.8Kacmesh-official/acme.sh · Shellacme.sh is a pure Unix shell script client for the ACME protocol that automatically issues, renews, and installs free SSL/TLS certificates from CAs like Let's Encrypt or ZeroSSL.
- 9

reverse-skill
42.4Kzhaoxuya520/reverse-skill · PowerShellIt is a skill pack that routes AI coding agents to the right reverse engineering, penetration testing, and security research methodology for a given task (APK, binary, JS, CTF, malware, etc.), checks which tools are installed, and runs a repeatable workflow instead of letting the agent guess commands.
- 10

metasploit-framework
39.2Krapid7/metasploit-framework · RubyMetasploit Framework is an open-source penetration testing framework written in Ruby — one of the best-known security toolkits on GitHub, with about 39,000 stars.
- 11
maigret
39.2Ksoxoj/maigret · PythonMaigret is an OSINT command-line tool that builds a dossier on a person by checking for an account under a given username across thousands of websites and pulling together whatever profile info it finds, with no API keys required.
- 12
RevokeMsgPatcher
39Khuiyadanli/RevokeMsgPatcher · C#A patcher for the Windows desktop versions of WeChat, QQ, and TIM that disables the 'message revoked' notification, so recalled/deleted messages stay visible to you.
- 13
trivy
38.5Kaquasecurity/trivy · GoTrivy is an all-in-one security scanner that finds vulnerabilities, misconfigurations, secrets, and software licenses across container images, filesystems, git repositories, VM images, and Kubernetes clusters.
- 14
vault
36.4Khashicorp/vault · GoVault is a tool for securely accessing secrets such as API keys, passwords, and certificates, giving you a unified interface with tight access control and detailed audit logging.
- 15
web-check
35.1Klissy93/web-check · TypeScriptWeb-Check is an open-source OSINT dashboard that lets you analyse any website: it pulls IP info, SSL chain, DNS records, cookies, headers, server location, and more into one report so you can understand its tech stack and security posture.
- 16

spring-boot-demo
34.1Kxkcoding/spring-boot-demo · JavaA large collection of hands-on Spring Boot demos: 66 planned integration modules (55 finished) covering ORM, caching, messaging, security, databases, logging and more, meant for learning Spring Boot by example.
- 17

CheatSheetSeries
33.7KOWASP/CheatSheetSeries · JavaScriptA collection of concise, high-value cheat sheets covering specific application security topics, maintained by OWASP.
- 18

shadowsocks
33.5Kshadowsocks/shadowsocks · PythonAn encrypted SOCKS5 proxy for getting private traffic past censorship — that is what the repo's own tags (proxy, socks5, encryption, censorship) describe. It is written in Python, has been on GitHub since April 2012, and holds about 33.5k stars.
- 19
nuclei
32.1Kprojectdiscovery/nuclei · GoA fast, open-source vulnerability scanner that runs YAML-based templates to find security issues in applications, APIs, networks, DNS and cloud configurations. Its checks come from a large global security community.
- 20
pentagi
30.8Kvxcontrol/pentagi · GoPentAGI (Penetration testing Artificial General Intelligence) is a fully autonomous AI agent system that performs complex penetration testing tasks for you.
- 21

algo
30.4Ktrailofbits/algo · PythonA set of Ansible scripts that spins up your own personal WireGuard and IPsec VPN server on a cloud provider, using the most secure defaults available.
- 22
security-audit-skill
30.4Kcloudflare/security-audit-skill · JavaScriptA Cloudflare coding-agent skill that turns your agent into a security auditor: it orchestrates isolated agents through a structured, multi-phase audit and returns independently verified, machine-readable findings.
- 23
awesome-osint
30.3Kjivoi/awesome-osintThis is a curated 'awesome list' of hundreds of free and paid OSINT (open source intelligence) tools and resources, organized into categories like general search, Google dorks, data breach lookup, social media, threat actors, and dark web.
- 24

gitleaks
30Kgitleaks/gitleaks · GoGitleaks is a tool for detecting secrets like passwords, API keys, and tokens in git repos, files, or anything you pipe in via stdin.
- 25

infisical
29.8KInfisical/infisical · TypeScriptInfisical is an open-source security platform teams use to centralize secrets, certificates, and privileged access, with syncing, rotation, and leak prevention built in.
- 26
h4cker
29.8KThe-Art-of-Hacking/h4cker · Jupyter NotebookA curated collection of thousands of cybersecurity resources — references, scripts, tools, code, labs, and training material — maintained by Omar Santos as a companion to his books, video courses, and live training.
- 27
dnSpy
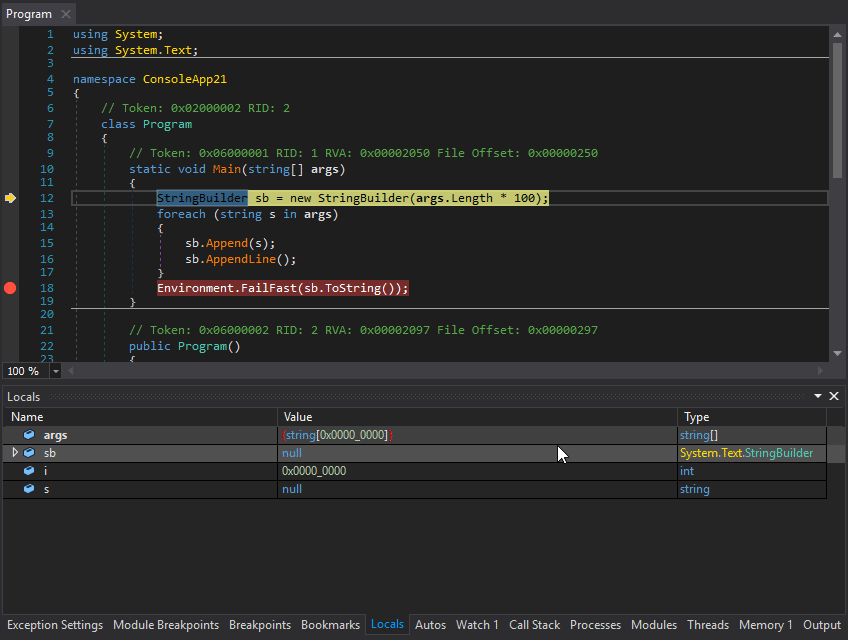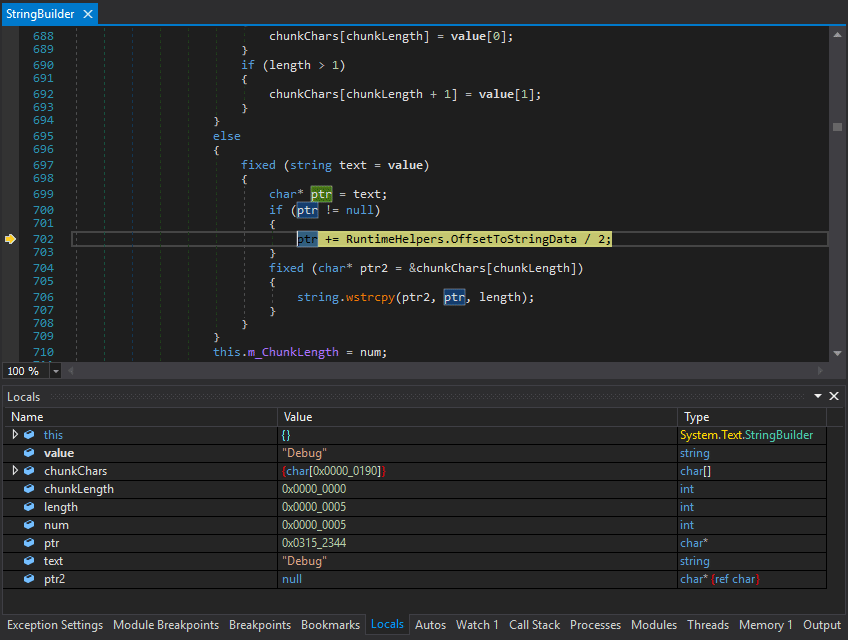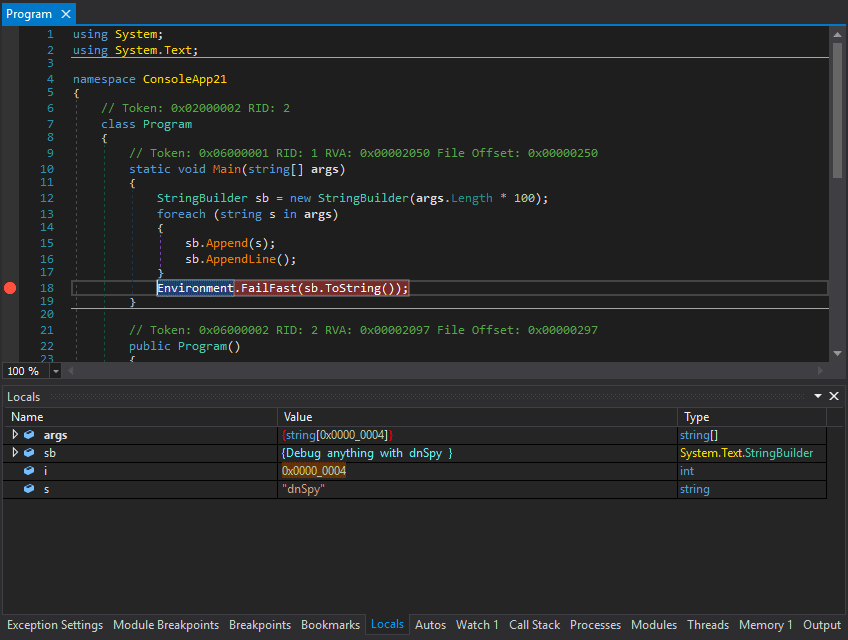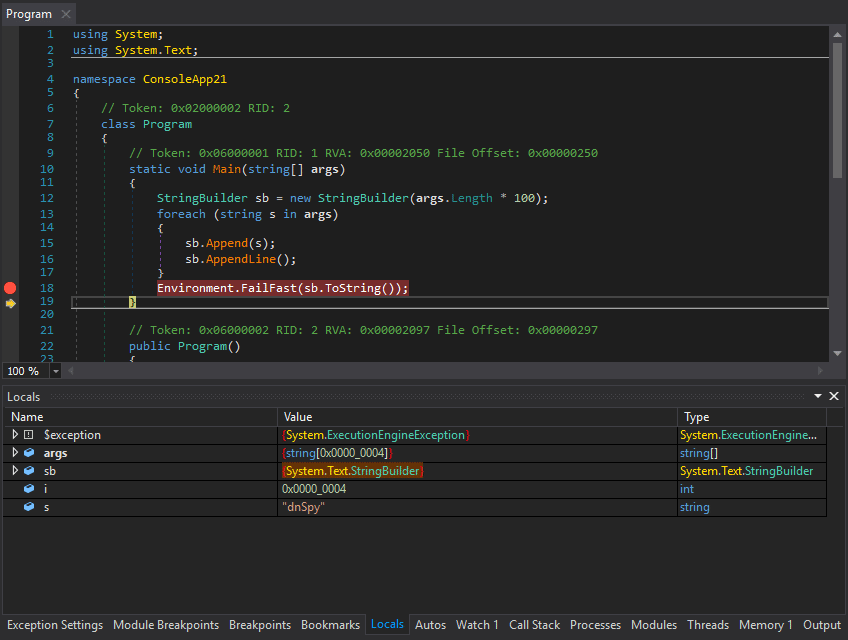
29.7KdnSpy/dnSpy · C#dnSpy is a Windows debugger and assembly editor for .NET and Unity programs - it lets you set breakpoints, step through code, and even edit methods and metadata without having the original source code.
- 28
trufflehog
28.5Ktrufflesecurity/trufflehog · GoTruffleHog is a CLI tool that discovers, classifies, validates, and analyzes leaked secrets like API keys, database passwords, and private keys across many sources (Git, GitHub, S3, Docker, Slack, filesystems, and more).
- 29

dns-blocklists
27.5Khagezi/dns-blocklists · TextA set of DNS blocklists that block ads, trackers, telemetry, phishing, malware, scams and other junk domains network-wide. They work for any region and with every common DNS server, ad blocker, and content blocker.
- 30

awesome-pentest
27.4Kenaqx/awesome-pentestA curated collection of penetration testing and offensive-security resources: tools, books, courses, conferences and practice targets for authorized security testing.
- 31

masscan
26.1Krobertdavidgraham/masscan · CMasscan is an Internet-scale TCP port scanner that transmits SYN packets asynchronously and can scan the entire IPv4 Internet in under 5 minutes, sending up to 10 million packets per second from a single machine.
- 32
social-analyzer
24.3Kqeeqbox/social-analyzer · JavaScriptSocial-Analyzer is an OSINT tool that searches and correlates a person's profile across roughly 1000 social media sites and websites, available as a CLI, an API, and a web app.
- 33

age
23.9KFiloSottile/age · Goage is a simple, modern and secure file encryption tool and Go library, with small explicit keys, no config options, and UNIX-style composability.
- 34
osquery
23.7Kosquery/osquery · C++osquery is a SQL powered operating system instrumentation, monitoring, and analytics framework: it exposes your OS as a high-performance relational database you can query with SQL.
- 35
spiderfoot
23.5Ksmicallef/spiderfoot · PythonOpen source OSINT automation — it collects intelligence on a target for threat intel and attack surface mapping, whether you are doing red team recon or checking what your organisation has exposed.
- 36
anubis
23.5KTecharoHQ/anubis · GoAnubis is a Web AI Firewall Utility that weighs the soul of incoming connections with challenges to protect upstream resources from AI scraper bots — built to defend the small internet from endless storms of AI-company requests.
- 37

slim
23.4Kslimtoolkit/slim · GoSlimToolkit (formerly DockerSlim) is a free, open-source CLI toolkit that inspects, optimizes and debugs container images. It can shrink an image by up to 30x without you changing anything in your Dockerfile — and makes the result more secure too.
- 38

personal-security-checklist
22.5Klissy93/personal-security-checklist · TypeScriptA community-maintained checklist of 300+ tips for protecting your digital security and privacy, curated by Alicia Sykes (Lissy93) and kept current for 2026.
- 39
unleashed-firmware
22.5KDarkFlippers/unleashed-firmware · CUnleashed is custom firmware for the Flipper Zero multitool — a fork of the official firmware (OFW) that adds extra features and improvements while staying compatible with official apps.
- 40

TrollStore
22.4Kopa334/TrollStore · Objective-CTrollStore is a permasigned jailed app for iOS that permanently installs any IPA you open in it. It works via an AMFI/CoreTrust bug: iOS doesn't correctly verify code signatures when a binary has multiple signers, so TrollStore can resign apps with its fake root certificate and keep them installed for good.
- 41

frida
22.3Kfrida/frida · MesonFrida is a dynamic instrumentation toolkit for developers, reverse-engineers, and security researchers, used to instrument running apps; more at frida.re.
- 42

Mobile-Security-Framework-MobSF
22KMobSF/Mobile-Security-Framework-MobSF · JavaScriptMobSF is an automated, all-in-one mobile security framework: it performs static and dynamic analysis, penetration testing, malware analysis and privacy analysis on Android, iOS and Windows Mobile apps.
- 43

mimikatz
21.9Kgentilkiwi/mimikatz · CA small Windows security tool, originally written to learn C. It is best known for extracting plaintext passwords, hashes, PIN codes and Kerberos tickets from memory, and can perform pass-the-hash, pass-the-ticket or build Golden tickets.
- 44

Ciphey
21.7Kbee-san/Ciphey · Rustciphey automatically decrypts ciphertext without knowing the key or cipher, decodes encodings and cracks hashes. It is the Rust-built next generation of Ciphey — roughly 7x faster per decode — and the same team intends it to fully replace the original.
- 45
vulhub
21.4Kvulhub/vulhub · DockerfileVulhub is an open-source collection of pre-built, ready-to-use vulnerable Docker environments: with one command you get a working lab for security research, learning, or demos.
- 46

PEASS-ng
20.7Kpeass-ng/PEASS-ng · C#PEASS-ng is a suite of local privilege escalation enumeration tools: LinPEAS for Linux/Unix/macOS and WinPEAS for Windows. They scan a machine for privesc paths and print misconfigurations with nice colors so you can spot them easily.
- 47

RustScan
20.6Kbee-san/RustScan · RustRustScan is an open-source port scanner written in Rust: it finds open ports fast — all 65k ports in as little as 3 seconds — and has a scripting engine for Python, Lua and Shell.
- 48

dotenv
20.5Kmotdotla/dotenv · JavaScriptA zero-dependency Node.js module that loads environment variables from a .env file into process.env, following the Twelve-Factor App principle of keeping configuration separate from code.
- 49
SkillSpector
20.4KNVIDIA/SkillSpector · PythonSkillSpector is a security scanner for AI agent skills (used by Claude Code, Codex CLI, Gemini CLI, and MCP) that detects vulnerabilities, malicious patterns, prompt injection, data exfiltration, and supply-chain risks before you install a skill.
- 50
bettercap
20.1Kbettercap/bettercap · GoA portable all-in-one framework written in Go for recon and attacks on WiFi, Bluetooth Low Energy, wireless HID, CAN-bus and IPv4/IPv6 networks, built for security researchers and red teamers.
- 51

cutter
20Krizinorg/cutter · C++Cutter is a free and open-source reverse engineering platform powered by the rizin engine — a desktop tool for analyzing, disassembling and debugging binaries.
- 52

GHunt
19.7Kmxrch/GHunt · PythonGHunt is an offensive Google framework geared toward OSINT — collecting intelligence around Google — and its authors note that any Google-related use is possible.
- 53
gvisor
19.7Kgoogle/gvisor · GoAn application kernel for containers: it wraps running applications in a strong isolation layer from the host OS, implementing a Linux-like interface in memory-safe Go, entirely in userspace.
- 54
KernelSU
19.3Ktiann/KernelSU · KotlinKernelSU is a kernel-based root solution for Android devices: the su and root access management run inside the kernel itself.
- 55
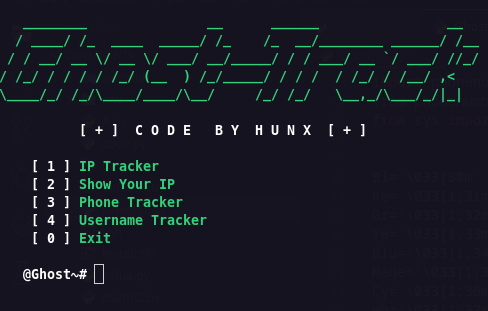
GhostTrack
19.1KHunxByts/GhostTrack · PythonGhostTrack is a Python command-line OSINT tool used to track a target's approximate location or gather details about a phone number, essentially a piece of information-gathering tooling for recon work.
- 56

fail2ban
18.8Kfail2ban/fail2ban · PythonFail2Ban is a daemon that scans log files like /var/log/auth.log, spots hosts making too many failed login attempts, and bans them by updating system firewall rules for a configurable amount of time.
- 57
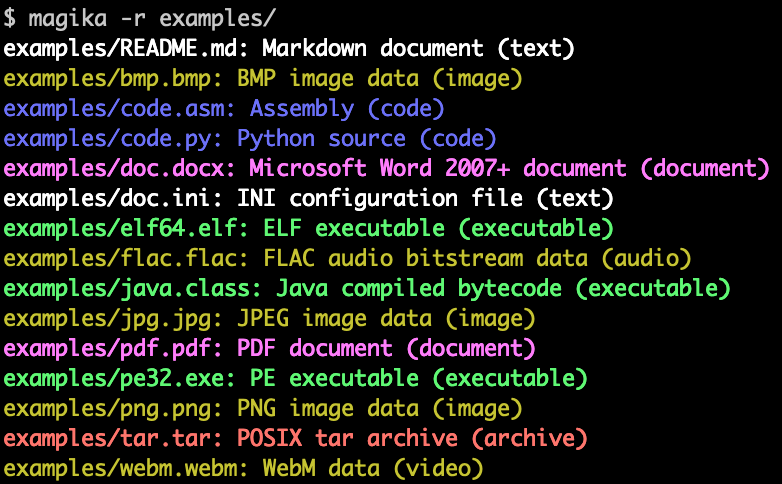
magika
18.7Kgoogle/magika · RustMagika is an AI-powered file type detection tool: a small deep learning model (a few MB) identifies what a file actually is within milliseconds, even on a single CPU.
- 58
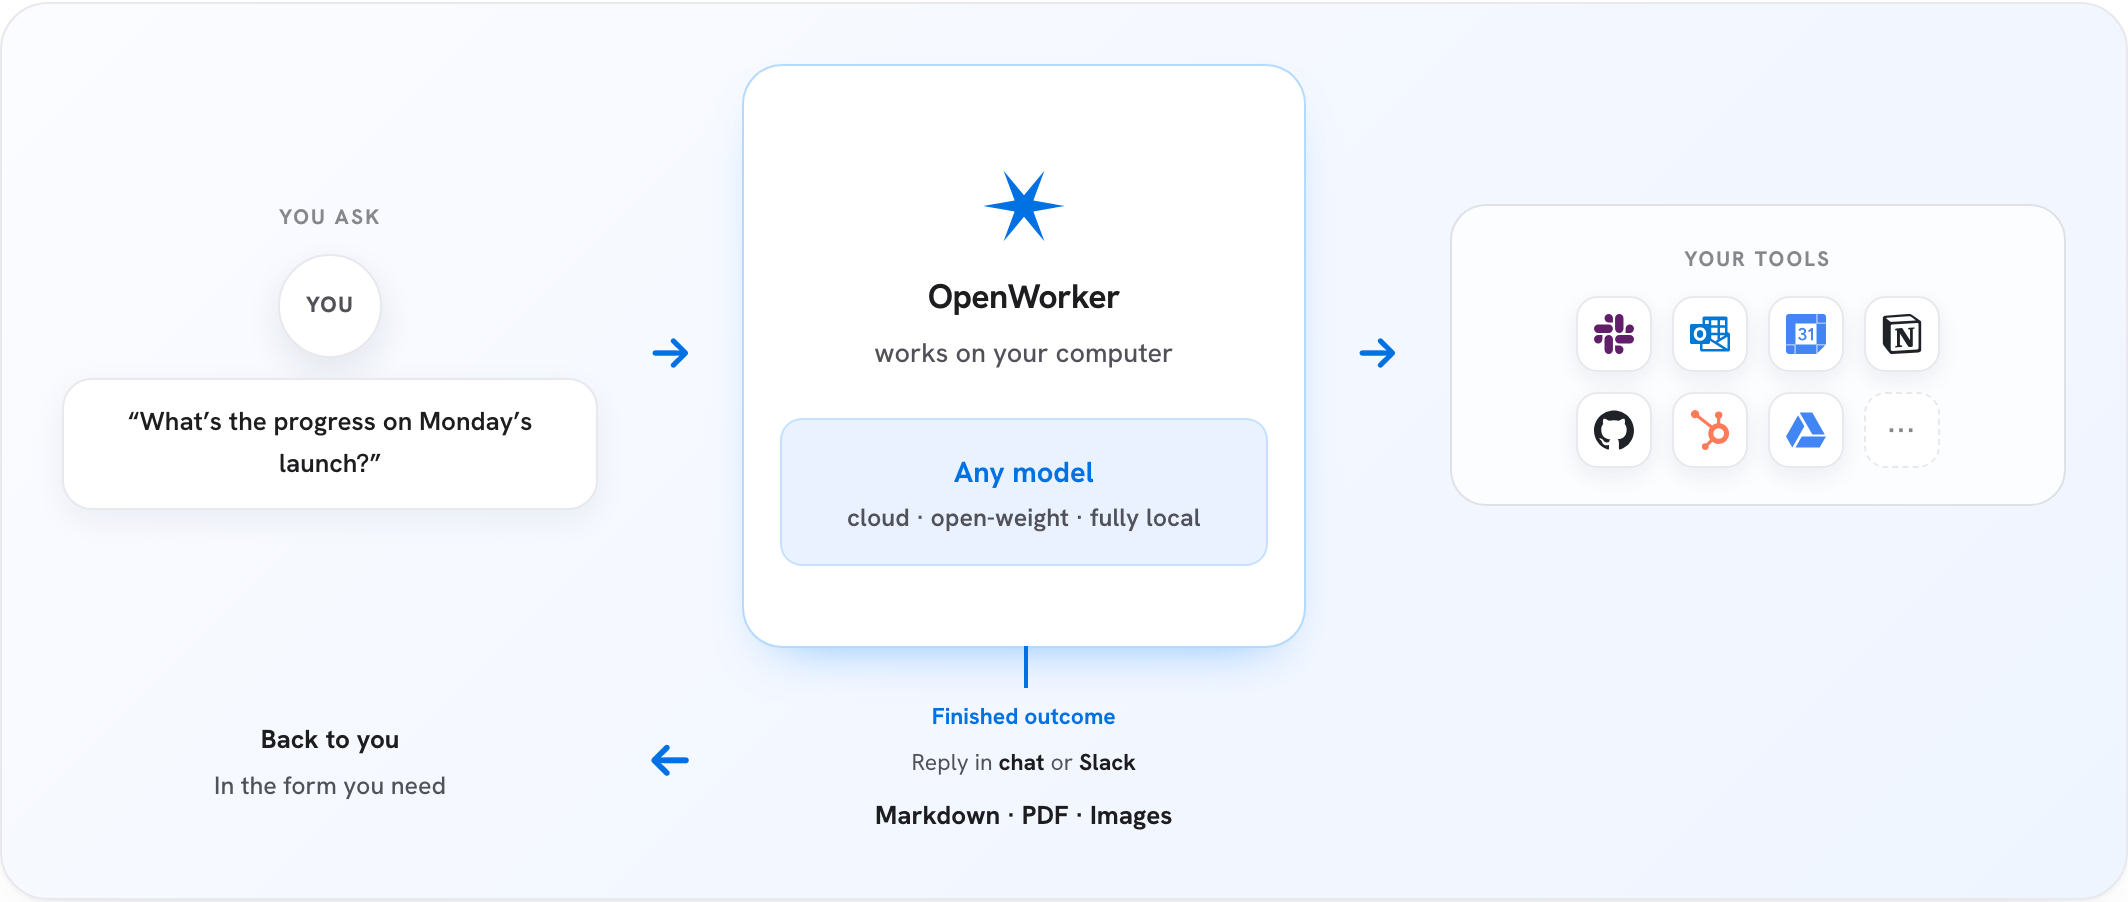
openworker
18.5Kandrewyng/openworker · PythonOpenWorker is an open-source AI coworker that lives on your desktop and delivers finished work instead of just chat: reviewed code with fixes, polished documents, Slack replies with real numbers, triaged inboxes.
- 59
optimizer
18.2Khellzerg/optimizer · C#A free, open-source Windows utility that locks down privacy and security: it turns off telemetry, Cortana, OneDrive and other built-in components. The author recommends running it right after a fresh Windows installation for maximum benefit.
- 60

phoneinfoga
18.2Ksundowndev/phoneinfoga · GoAn open-source OSINT framework for scanning international phone numbers. It gathers basics like country, area, carrier and line type, then tries to find the VoIP provider or identify the owner.
- 61

theHarvester
18Klaramies/theHarvester · PythonAn open-source OSINT tool that gathers emails, subdomains and names about a domain or organization from public sources: search engines, certificate transparency logs, DNS datasets, code repositories and threat-intel platforms, normalizing hostnames, emails, IPs, URLs, ASNs, people and breach names.
- 62

katana
17.7Kprojectdiscovery/katana · GoKatana is a next-generation crawling and spidering framework from ProjectDiscovery: point it at URLs and it discovers endpoints, links and forms across a site.
- 63
DOMPurify
17.5Kcure53/DOMPurify · JavaScriptDOMPurify is an XSS sanitizer for HTML, MathML and SVG: you feed it a string of dirty HTML and it returns clean HTML with everything dangerous stripped out, preventing XSS attacks.
- 64
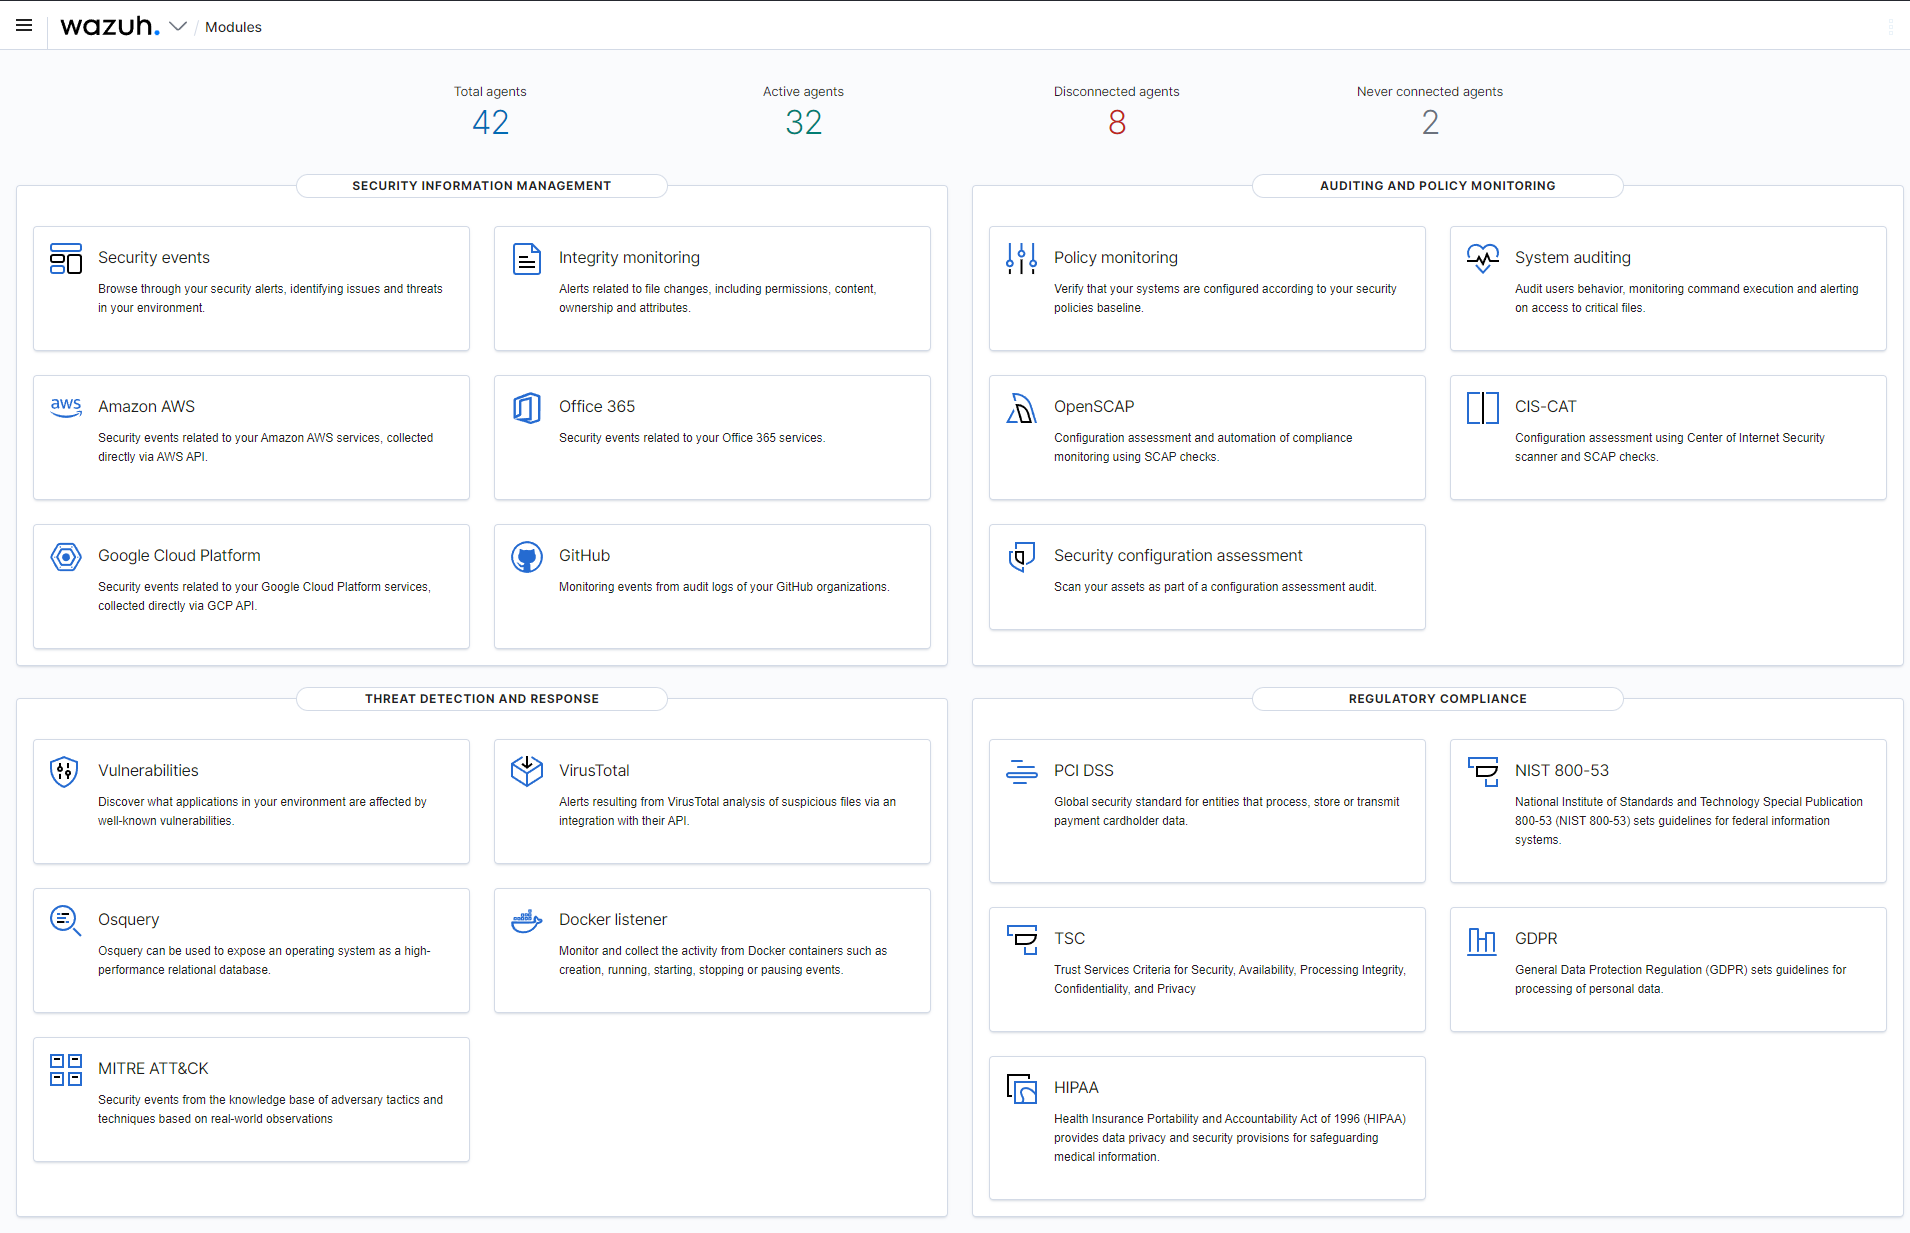
wazuh
17.3Kwazuh/wazuh · C++Wazuh is a free, open source security platform (XDR and SIEM) for threat prevention, detection and response across on-premises, virtualized, containerized and cloud workloads.
- 65

awesome-hacking
17.3Kcarpedm20/awesome-hackingA curated list of hacking tutorials, tools and resources covering system exploitation, reverse engineering, web security, network security, forensics, cryptography and wargames.
- 66
zphisher
17Khtr-tech/zphisher · HTMLZphisher is an automated phishing tool with 30+ ready-made login-page templates, written as a beginners-friendly shell script and intended purely for education.
- 67
ffuf
16.9Kffuf/ffuf · Goffuf is a fast web fuzzer written in Go — a command-line tool that sends many crafted requests to a target to discover directories, virtual hosts, and fuzzable GET/POST parameters.
- 68

MHDDoS
16.9KMatrixTM/MHDDoS · PythonMHDDoS is a Python 3 DDoS testing toolkit with 57 attack methods spanning Layer 7 (HTTP floods, Cloudflare/OVH bypasses) and Layer 4/3 (TCP, UDP, SYN, amplification attacks), meant for authorized security testing and research.
- 69
lynis
16.5KCISOfy/lynis · ShellLynis is a security auditing and hardening tool for Linux, macOS, BSD, and other Unix-like systems. It scans the host it runs on for vulnerable software, misconfigurations, and weak settings, and gives hardening tips while also assisting with compliance testing (HIPAA, ISO27001, PCI DSS).
- 70

twint
16.4Ktwintproject/twint · PythonTwint is a Python tool for scraping Twitter data — tweets, followers, following, likes and more — without using Twitter's official API, so it isn't bound by API limits or sign-up requirements.
- 71
cryptomator
16.3Kcryptomator/cryptomator · JavaCryptomator is a free, open-source app that encrypts your files on your own device before they reach cloud storage, so your provider only ever stores data it cannot read.
- 72
javascript-obfuscator
16.3Kjavascript-obfuscator/javascript-obfuscator · TypeScriptA free, powerful obfuscator for JavaScript and Node.js that protects source code with identifier renaming, string encryption, dead code injection, and control flow flattening.
- 73
systeminformer
16.3Kwinsiderss/systeminformer · CSystem Informer is a free, powerful multi-purpose tool for Windows that helps you monitor system resources, debug software and detect malware.
- 74
impacket
16.2Kfortra/impacket · PythonImpacket is a collection of Python classes for working with network protocols, giving low-level programmatic access to packets and, for some protocols like SMB1-3 and MSRPC, full protocol implementations.
- 75

PentestGPT
16KGreyDGL/PentestGPT · PythonPentestGPT is an agentic framework that uses large language models to run automated penetration testing and solve CTF challenges, working through staged phases like recon, exploitation and reporting.
- 76

zaproxy
16Kzaproxy/zaproxy · JavaZAP (Zed Attack Proxy) by Checkmarx is the world's most widely used web app security scanner, used to automatically find vulnerabilities in web applications during development and testing.
- 77
evilginx2
15.7Kkgretzky/evilginx2 · GoEvilginx is a man-in-the-middle attack framework used for phishing login credentials along with session cookies, which lets an attacker bypass 2-factor authentication.
- 78

hacker-roadmap
15.7Ksundowndev/hacker-roadmapThis is a curated roadmap and toolkit index for learning and practicing ethical hacking: it explains what penetration testing is and groups hundreds of security tools, wordlists and references by category (recon, password attacks, wireless, exploitation, web hacking, post-exploitation, frameworks).
- 79
ecapture
15.5Kgojue/ecapture · CAn open-source command-line security tool that uses eBPF to capture SSL/TLS traffic in plaintext — no CA certificate installation or MITM proxy needed. It can also audit shell commands and database queries on the host.
- 80
vphone-cli
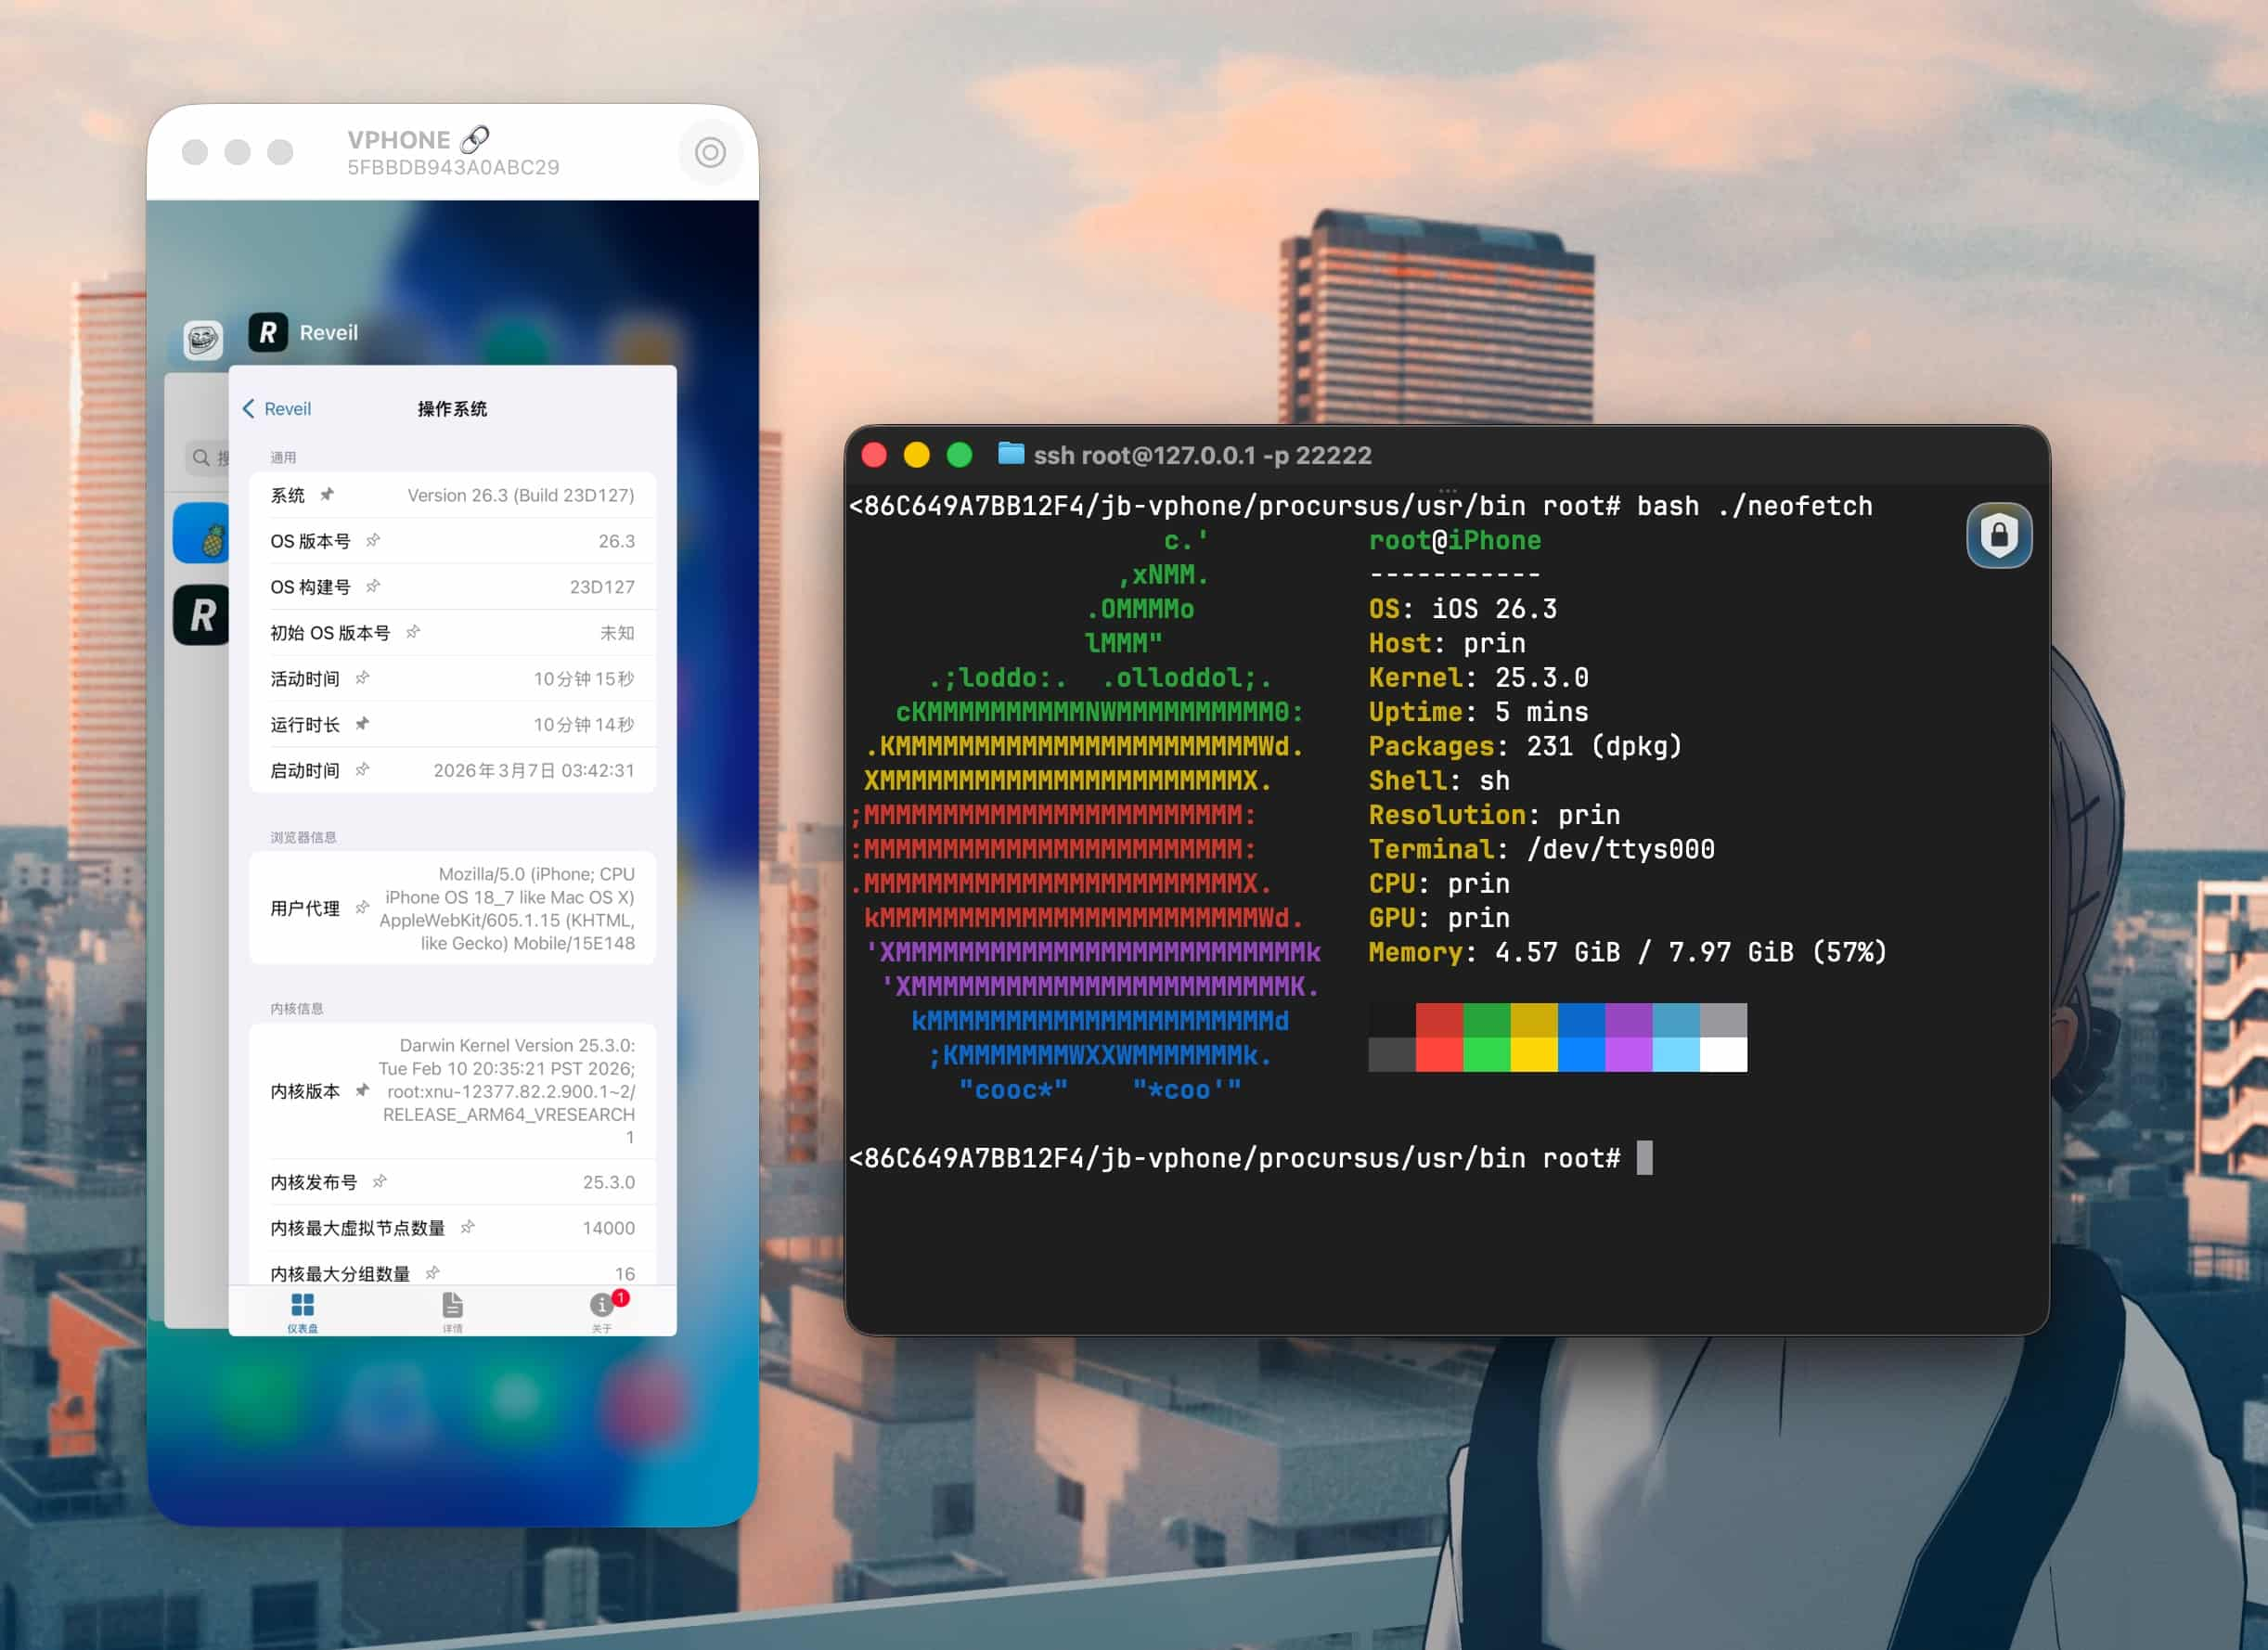
15.4KLakr233/vphone-cli · Swiftvphone-cli boots a virtual iPhone on a Mac using Apple's Virtualization.framework, built on Apple's PCC research VM infrastructure, so you can run, test, and even jailbreak iOS without a physical device.
- 81
mvt
15.4Kmvt-project/mvt · PythonMVT (Mobile Verification Toolkit) is a collection of forensic utilities that help gather and analyze traces on Android and iOS devices to identify a potential compromise, originally built by Amnesty International's Security Lab during the Pegasus Project.
- 82

social-engineer-toolkit
15.4Ktrustedsec/social-engineer-toolkit · PythonThe Social-Engineer Toolkit (SET) is an open-source penetration testing framework for authorized social-engineering assessments, giving security teams guided attack vectors to test user awareness and validate controls.
- 83

XSStrike
15.2Ks0md3v/XSStrike · PythonXSStrike is a Cross Site Scripting (XSS) detection suite built around four hand-written parsers, an intelligent payload generator, a fuzzing engine, and a fast crawler. Instead of just firing generic payloads like most scanners, it analyzes the live response and crafts payloads guaranteed to work through context analysis.
- 84
prowler
15Kprowler-cloud/prowler · PythonProwler is an open-source cloud security platform that automates security and compliance checks across AWS, Azure, GCP, Kubernetes, M365, GitHub, and many other providers.
- 85
esp8266_deauther
15KSpacehuhnTech/esp8266_deauther · CESP8266 Deauther is open-source firmware for the ESP8266 chip that lets you scan nearby WiFi networks, send deauthentication packets to disconnect devices, and spin up dozens of fake WiFi networks to confuse scanners - an affordable platform for testing and learning about WiFi security.
- 86

awesome-security
15Ksbilly/awesome-securityA curated, categorized collection of well-known security resources — software, libraries, documents, books and other cool stuff — maintained by the community in the spirit of awesome-php and awesome-python.
- 87
wifiphisher
14.9Kwifiphisher/wifiphisher · PythonWifiphisher is a rogue access point framework for conducting Wi-Fi phishing and man-in-the-middle attacks against wireless clients, used in red team and penetration testing engagements.
- 88

static-analysis
14.8Kanalysis-tools-dev/static-analysis · RustA curated list of static analysis (SAST) tools, linters and formatters for all programming languages, config files and build tools, focused on tools that improve code quality.
- 89

openvpn
14.7KOpenVPN/openvpn · COpenVPN is an open-source VPN daemon — a background service that creates a secure, encrypted tunnel over the public internet, so your device can reach a private network as if it were directly connected.
- 90
fscan
14.7Kshadow1ng/fscan · Gofscan is an open-source intranet scanner written in Go: one command runs an all-round internal-network audit — host discovery, port scanning, service identification, weak-password brute force and vulnerability detection.
- 91
HackBrowserData
14.6KmoonD4rk/HackBrowserData · GoHackBrowserData is a command-line tool that decrypts and exports browser data — passwords, cookies, history, bookmarks, credit cards and more — from Chromium-based browsers, Firefox and Safari, built for security research.
- 92

binwalk
14.5KReFirmLabs/binwalk · RustBinwalk is a firmware analysis tool that can identify, and optionally extract, files and data that have been embedded inside other files.
- 93

gophish
14.3Kgophish/gophish · GoGophish is an open-source phishing toolkit for businesses and penetration testers: it lets you quickly set up and run phishing engagements and security awareness training campaigns.
- 94

gobuster
14.2KOJ/gobuster · GoGobuster is a fast, multi-threaded command-line tool written in Go for brute-forcing web directories/files, DNS subdomains, and virtual hosts, plus enumerating S3/GCS cloud storage buckets and TFTP files.
- 95
opensnitch
14.2Kevilsocket/opensnitch · PythonOpenSnitch is an interactive application firewall for GNU/Linux, inspired by macOS's 'Little Snitch', that lets you see and approve or block each app's outgoing connections in real time.
- 96
juice-shop
14.1Kjuice-shop/juice-shop · TypeScriptOWASP Juice Shop is an intentionally insecure web application (a fake online juice store) built for security training, awareness demos, CTFs, and testing security tools.
- 97

opennhp
13.9KOpenNHP/opennhp · GoOpenNHP is a lightweight, cryptography-powered, open-source Zero Trust toolkit: it hides server ports, IP addresses, and domain names so your infrastructure stays invisible until a client is cryptographically authorized.
- 98

DVWA
13.9Kdigininja/DVWA · PHPDVWA (Damn Vulnerable Web Application) is a PHP/MariaDB web app that is deliberately full of security bugs, built as a legal practice target for security pros, students, and developers to learn web application security.
- 99

nmap
13.8Knmap/nmap · CNmap is the Network Mapper — a free, open-source tool for network discovery and security scanning. It finds live hosts, open ports, and the services running on them, from a single machine up to whole subnets.
- 100

john
13.8Kopenwall/john · CA fast, offline password cracker. Its primary purpose is detecting weak Unix passwords, but the jumbo build supports hundreds of hash and cipher types and runs on Unix, macOS, Windows and more.
Showing the 100 most-starred of 282. See every one in the catalog.
Related topics
Often tagged together
- security976
- linux4,184
- open-source5,666
- cybersecurity245
- macos3,544
- windows3,403
- cli2,227
- cross-platform2,623
- penetration-testing126
- python2,383
- pentesting113
- mit3,312
- docker1,660
- hacking135
- terminal1,101
- developer-tools2,924
- reverse-engineering221
- offensive-security77
- tool1,295
- self-hosted1,929
- hacking-tool75
- red-team79
- command-line-tool715
- go681