Topics / #cve
Cve projects on GitHub
Tracking known CVEs, proofs of concept, and vulnerability intelligence.
As of , the most-starred Cve projects on GitHub are nuclei (32.1K stars), SafeLine (22.8K stars) and nuclei-templates (13.1K stars). GitHub.Locker tracks 13 Cve repositories with 94.5K stars combined. The fastest-growing on October 16 was ghostlock-app, with +31 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
 +31
ghostlock-app
YuKongA/ghostlock-app · ★ 2KGhostLock is a one-tap Android app that runs the CVE-2026-43499 kernel exploit to grant uid 0 (root) on a matching vulnerable kernel, optionally loading a KernelSU-style module afterward.
 +21
nuclei
projectdiscovery/nuclei · ★ 32.1KA fast, open-source vulnerability scanner that runs YAML-based templates to find security issues in applications, APIs, networks, DNS and cloud configurations. Its checks come from a large global security community.
 +12
SafeLine
chaitin/SafeLine · ★ 22.8KSafeLine is a self-hosted web application firewall (WAF) and reverse proxy that protects your web apps from attacks and exploits by filtering and monitoring HTTP traffic.
 +12
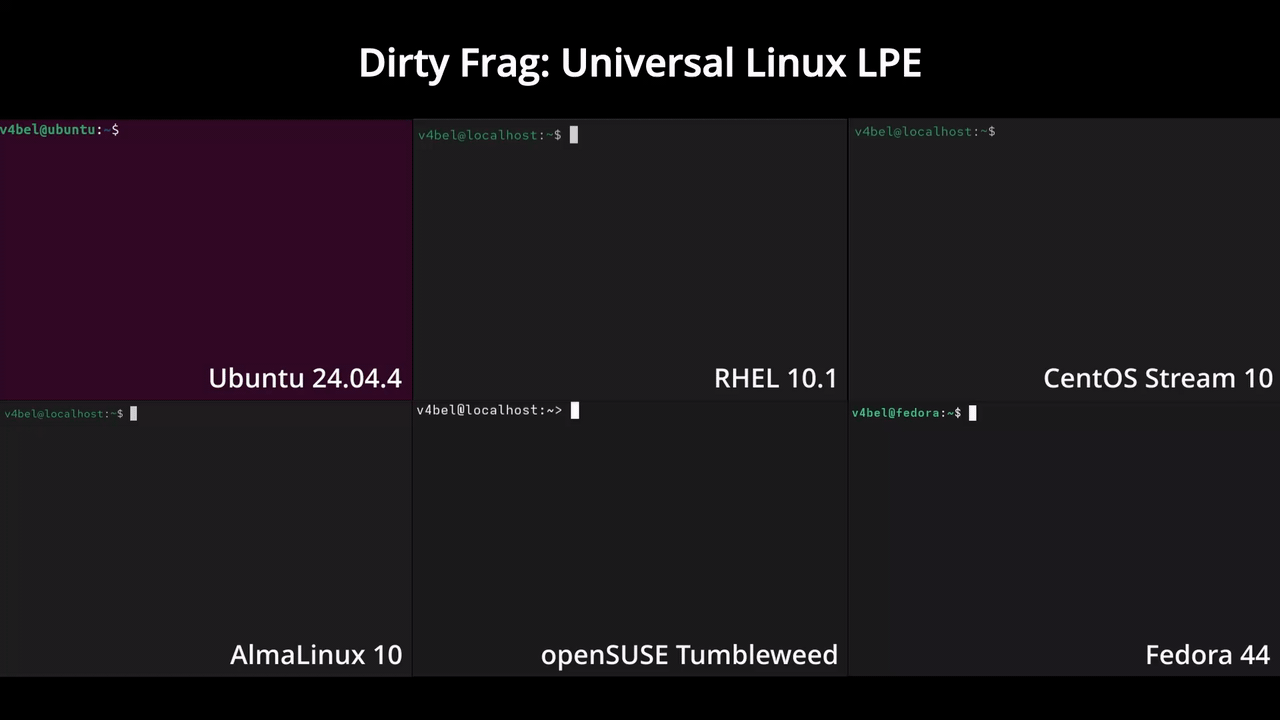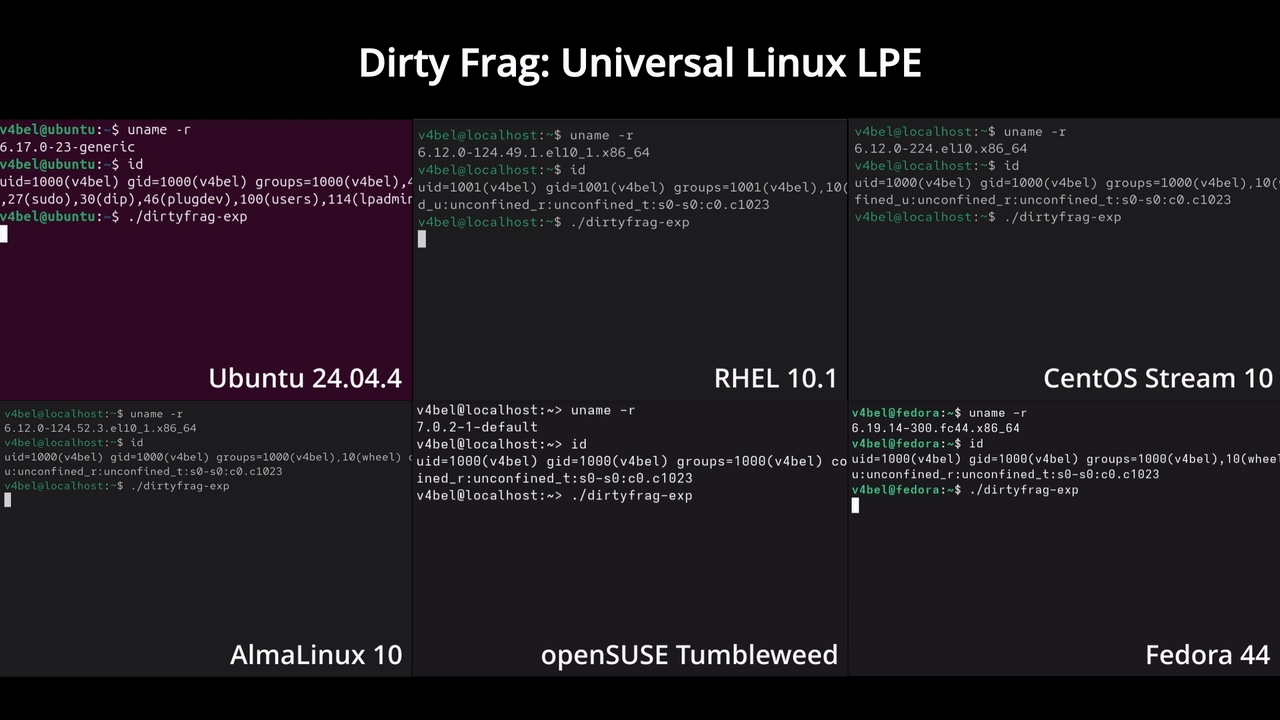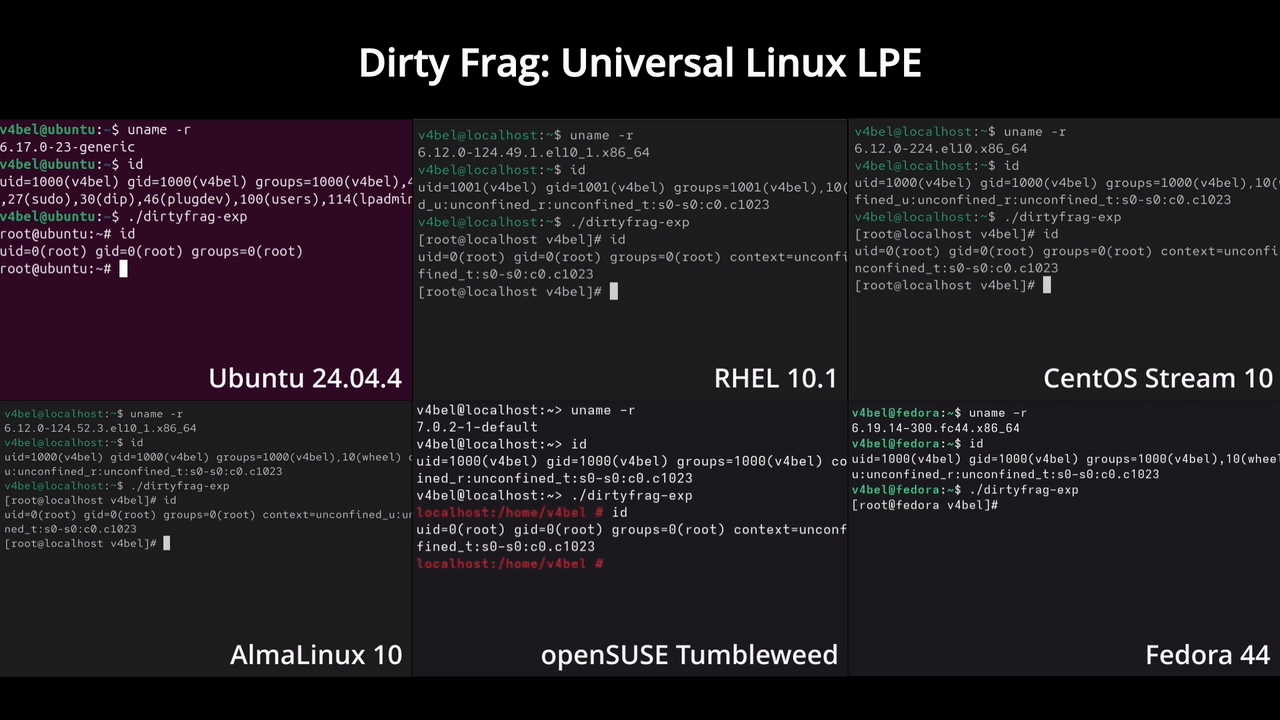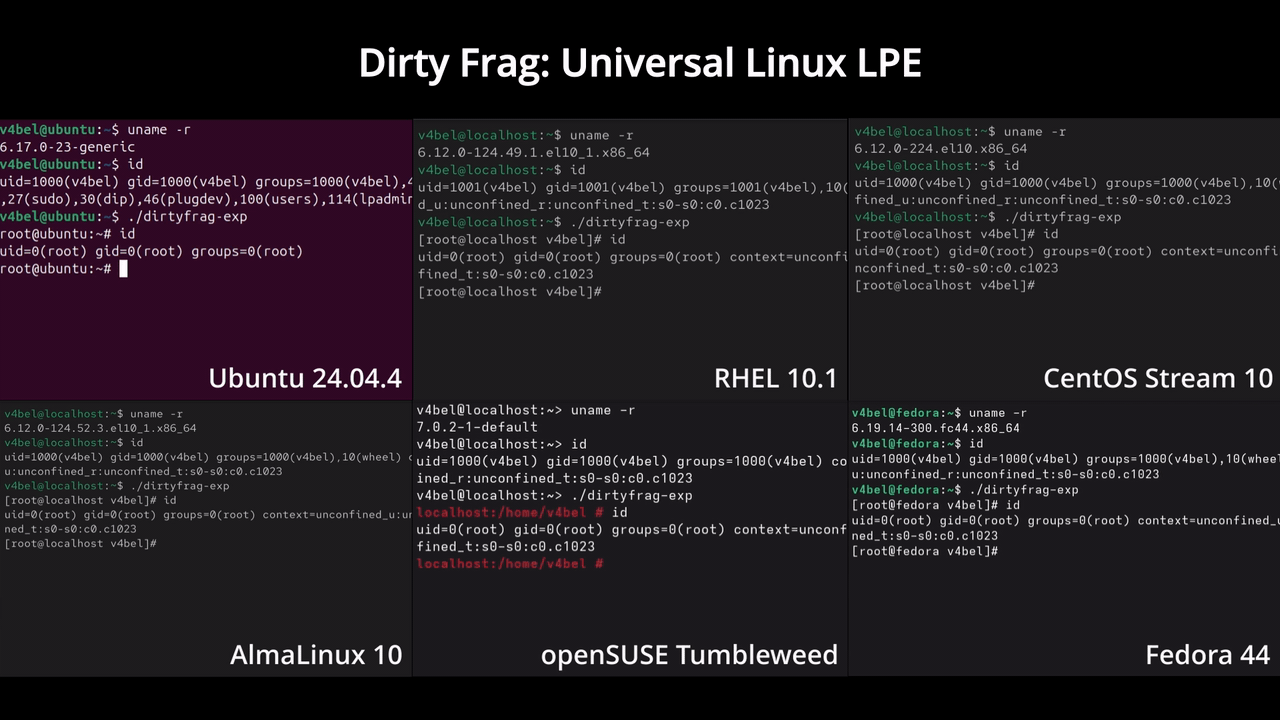
dirtyfrag
V4bel/dirtyfrag · ★ 5.1KDirty Frag is a proof-of-concept Linux kernel local privilege escalation exploit that chains two page-cache write vulnerabilities (CVE-2026-43284 and CVE-2026-43500) to obtain root on major Linux distributions.
The all-time top
13 projects · by stars
- 32.1K#1 · projectdiscovery/nuclei
nuclei
A fast, open-source vulnerability scanner that runs YAML-based templates to find security issues in applications, APIs, networks, DNS and cloud configurations. Its checks come from a large global security community.
- 22.8K#2 · chaitin/SafeLine
SafeLine
SafeLine is a self-hosted web application firewall (WAF) and reverse proxy that protects your web apps from attacks and exploits by filtering and monitoring HTTP traffic.
- 13.1K
 #3 · projectdiscovery/nuclei-templates
nuclei-templates
This is a community-curated collection of over 11,000 detection templates for the Nuclei vulnerability scanner, covering CVEs, misconfigurations, exposed panels, and other security issues.
- 4

awesome-hacker-search-engines
11.3Kedoardottt/awesome-hacker-search-engines · ShellA curated list of search engines useful for penetration testing, vulnerability assessment, red/blue team operations, bug bounty hunting, and general OSINT work.
- 5

exploitarium
5.2Kbikini/exploitarium · PythonExploitarium is a single consolidated archive of the author's public proof-of-concept exploits and vulnerability research writeups, merging dozens of their former standalone PoC repos into one place.
- 6
dirtyfrag
5.1KV4bel/dirtyfrag · CDirty Frag is a proof-of-concept Linux kernel local privilege escalation exploit that chains two page-cache write vulnerabilities (CVE-2026-43284 and CVE-2026-43500) to obtain root on major Linux distributions.
- 7
ghostlock-app
2KYuKongA/ghostlock-app · KotlinGhostLock is a one-tap Android app that runs the CVE-2026-43499 kernel exploit to grant uid 0 (root) on a matching vulnerable kernel, optionally loading a KernelSU-style module afterward.
- 8

cve-lite-cli
769OWASP/cve-lite-cli · TypeScriptMost tools tell you what's wrong. CVE Lite CLI tells you what to run.
- 9
Offensive-Security-AI-Models
691JoasASantos/Offensive-Security-AI-ModelsA curated list of open-weight, uncensored language models fine-tuned for offensive-security tasks like penetration testing, red teaming, and security research. The README documents over 20 models sourced from HuggingFace model cards as of September 2026.
- 10
0
5120sec-labs/0 · TypeScript0 is an open-source, self-evolving, multi-model AI harness for security research that finds, verifies, and fixes vulnerabilities, built by the Swiss Applied AI & Cybersecurity Research Lab.
- 11

CVE-2026-9830
477opaxial/CVE-2026-9830 · PythonA Python proof-of-concept that validates a reported unauthenticated REST API exposure in the BookingPress Pro WordPress plugin, which can leak booking and customer data.
- 12

Comfyui-MMH3-UltimateUpscale
236bbaudio-2025/Comfyui-MMH3-UltimateUpscale · PythonA ComfyUI custom node that upscales long, high-resolution MiniMax H3 AV video latents on VRAM-limited GPUs, using temporal chunking and spatial tiling inside a single node while keeping the audio track intact.
- 13

UniRoot
229kuuky29/UniRoot · KotlinUniRoot is a one-tap rooting app for Samsung Galaxy devices. It ships a new unprivileged kernel exploit (DirtyFrag, CVE-2026-43284) that roots the phone with a single button press, plus an older CVE-2026-43499-based exploit with per-device profiles, and it automatically re-roots the device on every boot.
Related topics
Often tagged together
- security977
- cybersecurity244
- security-tools281
- vulnerability49
- linux4,181
- penetration-testing125
- exploit51
- hacking135
- mit3,311
- offensive-security77
- open-source5,666
- red-team78
- vulnerability-scanner44
- macos3,544
- windows3,401
- apache-2.01,434
- exploit-development15
- pentesting112
- ai1,954
- appsec16
- cli2,227
- cross-platform2,622
- curated-list634
- fuzzing23