Topics / #ai-security
AI security projects on GitHub
Securing AI systems against misuse and attacks
As of , the most-starred AI security projects on GitHub are system_prompts_leaks (69.8K stars), strix (69.1K stars) and serviette (58.8K stars). GitHub.Locker tracks 44 AI security repositories with 567.6K stars combined. The fastest-growing on October 16 was security-audit-skill, with +375 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
 +375
security-audit-skill
cloudflare/security-audit-skill · ★ 30.4KA Cloudflare coding-agent skill that turns your agent into a security auditor: it orchestrates isolated agents through a structured, multi-phase audit and returns independently verified, machine-readable findings.
 +214
strix
usestrix/strix · ★ 69.1KStrix is an open-source tool that uses autonomous AI agents to pentest your application like real hackers: it runs your code dynamically, finds vulnerabilities, and proves them with working exploits instead of just flagging suspicious patterns.
 +81
shannon
KeygraphHQ/shannon · ★ 49KShannon is an autonomous AI pentester that analyzes your web application's source code, maps attack vectors, and then executes real exploits against the running app to prove vulnerabilities before they reach production — 'no exploit, no report'.
SkillSpector
NVIDIA/SkillSpector · ★ 20.4KSkillSpector is a security scanner for AI agent skills (used by Claude Code, Codex CLI, Gemini CLI, and MCP) that detects vulnerabilities, malicious patterns, prompt injection, data exfiltration, and supply-chain risks before you install a skill.
The all-time top
44 projects · by stars
- 69.8K
 #1 · asgeirtj/system_prompts_leaks
system_prompts_leaks
This repo is a growing collection of leaked system prompts — the hidden instructions various AI chatbots and coding agents receive before they answer your first message.
- 69.1K#2 · usestrix/strix
strix
Strix is an open-source tool that uses autonomous AI agents to pentest your application like real hackers: it runs your code dynamically, finds vulnerabilities, and proves them with working exploits instead of just flagging suspicious patterns.
- 58.8K
 #3 · pathwaycom/serviette
serviette
This repo provides ready-to-run cloud templates for RAG pipelines, AI pipelines, and enterprise search, built on the Pathway Live Data Framework and kept in sync with live data sources.
- 4

dive-into-llms
56.8KLordog/dive-into-llms · Jupyter NotebookIt's a free Chinese-language tutorial series called 'Dive into LLMs' (《动手学大模型》) that teaches large language model concepts through hands-on coding exercises, built from Shanghai Jiao Tong University's NLP and AI-security course materials.
- 5
shannon
49KKeygraphHQ/shannon · TypeScriptShannon is an autonomous AI pentester that analyzes your web application's source code, maps attack vectors, and then executes real exploits against the running app to prove vulnerabilities before they reach production — 'no exploit, no report'.
- 6
Anthropic-Cybersecurity-Skills
34.6Kmukul975/Anthropic-Cybersecurity-Skills · PythonAn open-source library of 818 production-grade cybersecurity skills for AI agents, covering 34 security domains and mapped to six frameworks including MITRE ATT&CK and NIST CSF 2.0.
- 7
security-audit-skill
30.4Kcloudflare/security-audit-skill · JavaScriptA Cloudflare coding-agent skill that turns your agent into a security auditor: it orchestrates isolated agents through a structured, multi-phase audit and returns independently verified, machine-readable findings.
- 8
h4cker
29.8KThe-Art-of-Hacking/h4cker · Jupyter NotebookA curated collection of thousands of cybersecurity resources — references, scripts, tools, code, labs, and training material — maintained by Omar Santos as a companion to his books, video courses, and live training.
- 9
promptfoo
26.1Kpromptfoo/promptfoo · TypeScriptpromptfoo is a CLI and library for evaluating and red-teaming LLM apps — you test prompts, agents, and RAGs and run security scans on them, instead of relying on trial-and-error.
- 10

L1B3RT4S
21.9Kelder-plinius/L1B3RT4SA public collection of jailbreak prompts — the author calls them 'liberation prompts' — meant to make flagship AI models respond without their usual refusals. It is maintained by AI red-teamer elder-plinius.
- 11
SkillSpector
20.4KNVIDIA/SkillSpector · PythonSkillSpector is a security scanner for AI agent skills (used by Claude Code, Codex CLI, Gemini CLI, and MCP) that detects vulnerabilities, malicious patterns, prompt injection, data exfiltration, and supply-chain risks before you install a skill.
- 12

Awesome-Hacking-Resources
17.5Kvitalysim/Awesome-Hacking-ResourcesA curated collection of hacking, penetration testing and AI red-teaming resources — courses, YouTube channels, CTF platforms and guides, picked to make you better at offensive security.
- 13

codex-security
11.1Kopenai/codex-security · TypeScriptCodex Security is OpenAI's CLI and TypeScript SDK for defining security policy and for finding, validating, and fixing security vulnerabilities in your code.
- 14

Claude-Red
7.6KSnailSploit/Claude-Red · Pythonclaude-red is a curated library of offensive security skills for the Claude Skills system: structured SKILL.md files that prime Claude with expert-level methodology for one attack surface each, from SQLi to shellcode.
- 15
AI-Infra-Guard
6.9KTencent/AI-Infra-Guard · PythonAI-Infra-Guard (A.I.G) is a full-stack AI red teaming platform built by Tencent Zhuque Lab that scans AI agents, MCP servers, agent skills, and AI infrastructure components for security vulnerabilities, and evaluates LLMs against jailbreak attacks.
- 16
claude-code-ultimate-guide
6.2KFlorianBruniaux/claude-code-ultimate-guide · PythonA deep, 430K+ line guide to Claude Code covering agentic workflows, hooks, skills, MCP servers, security, and production practices, paired with runnable templates and quizzes to learn from.
- 17
Agentic-Bug-Hunter
5.4Kawarexone/Agentic-Bug-Hunter · PythonAgentic Bug Hunter is an AI-powered bug bounty toolkit that runs recon, tests for vulnerabilities, validates findings against a strict gate, and writes submission-ready reports for HackerOne, Bugcrowd, Intigriti, or Immunefi, right from your terminal.
- 18

Claude-BugHunter
5.1Kelementalsouls/Claude-BugHunter · PythonA drop-in skill bundle for the Claude Code skills system that turns Claude into a bug-hunting researcher or red-team operator: it ships 83 skills, 15 slash commands, and knowledge curated from 681 disclosed HackerOne reports across 24 vulnerability classes, plus enterprise identity and infrastructure attack matrices.
- 19
reverse-SynthID
5Kaloshdenny/reverse-SynthID · Pythonreverse-SynthID reverse-engineers Google's SynthID watermark embedded in Gemini-generated images using signal processing and spectral analysis, and ships tools that detect and surgically bypass that watermark without any access to Google's proprietary encoder/decoder.
- 20
nono
4.5Knolabs-ai/nono · Rustnono is a zero-setup, zero-latency sandbox that runs AI coding agents (Claude Code, Codex, OpenCode, etc.) with least-privilege access, so they can't touch your SSH keys, cloud credentials, or the rest of your disk by default.
- 21

copy-fail-CVE-2026-31431
4.1Ktheori-io/copy-fail-CVE-2026-31431 · PythonThis repository is a technical writeup and proof-of-concept for CVE-2026-31431, a 9-year-old Linux kernel local privilege escalation (LPE) vulnerability found by Theori's AI vulnerability research tool, Xint Code.
- 22

Spiritual-Spell-Red-Teaming
4KGoochbeater/Spiritual-Spell-Red-TeamingA public collection of jailbreak prompts — the author calls them 'spells' — written to get uncensored answers out of LLMs, mainly Claude.
- 23

jailbreaks
3.1Ktogg53192-cmd/jailbreaksThis is a personal collection of jailbreak prompts meant to bypass the safety restrictions of AI chatbots like ChatGPT.
- 24
dsh-infinite-gen-5
3KMinglink/dsh-infinite-gen-5 · JavaScriptThis is a system-prompt injection plugin for the DeepSeek Harness (dsh) ecosystem that tries to bypass DeepSeek-V4.1 Flash's safety guardrails, framed as a red-team robustness benchmark suite for studying model defenses.
- 25
ai-agents-the-definitive-guide
2.8KNicolepcx/ai-agents-the-definitive-guide · Jupyter NotebookIt is the companion code repository for the book 'AI Agents - The Definitive Guide': a set of runnable Jupyter notebooks that walk through every chapter, from basic agent patterns to production deployment and threat modeling.
- 26
mantis
2.5Kgoogle/mantis · PythonMantis is a toolkit of skills plus a reference agent harness (built on Google's ADK) that lets AI coding agents autonomously find, reproduce, triage, and patch vulnerabilities in a codebase.
- 27
ai-agent-handbook
1.8Kaliyun/ai-agent-handbook · JavaScriptAn open-source Alibaba Cloud whitepaper (handbook) distilling hands-on experience building enterprise-grade AI agents across their full lifecycle: architecture, building, running, governance, and tuning. It is maintained as a living open project rather than a one-off release.
- 28

ModelTrace
1.7Kxqy2006/ModelTrace · JavaScriptModelTrace is a locally-run active model attribution tool: it sends three fixed challenge prompts to a target model, extracts an output fingerprint, and matches it against a known-model library to guess the model family and specific version.
- 29
OpenAPPA
1.6Karchestra-ai/OpenAPPA · RustOpenAPPA is a deterministic guardrail layer that sits between an AI agent and its tools, checking every tool call to decide whether the data involved is allowed to reach that destination.
- 30
gpt6-Astra
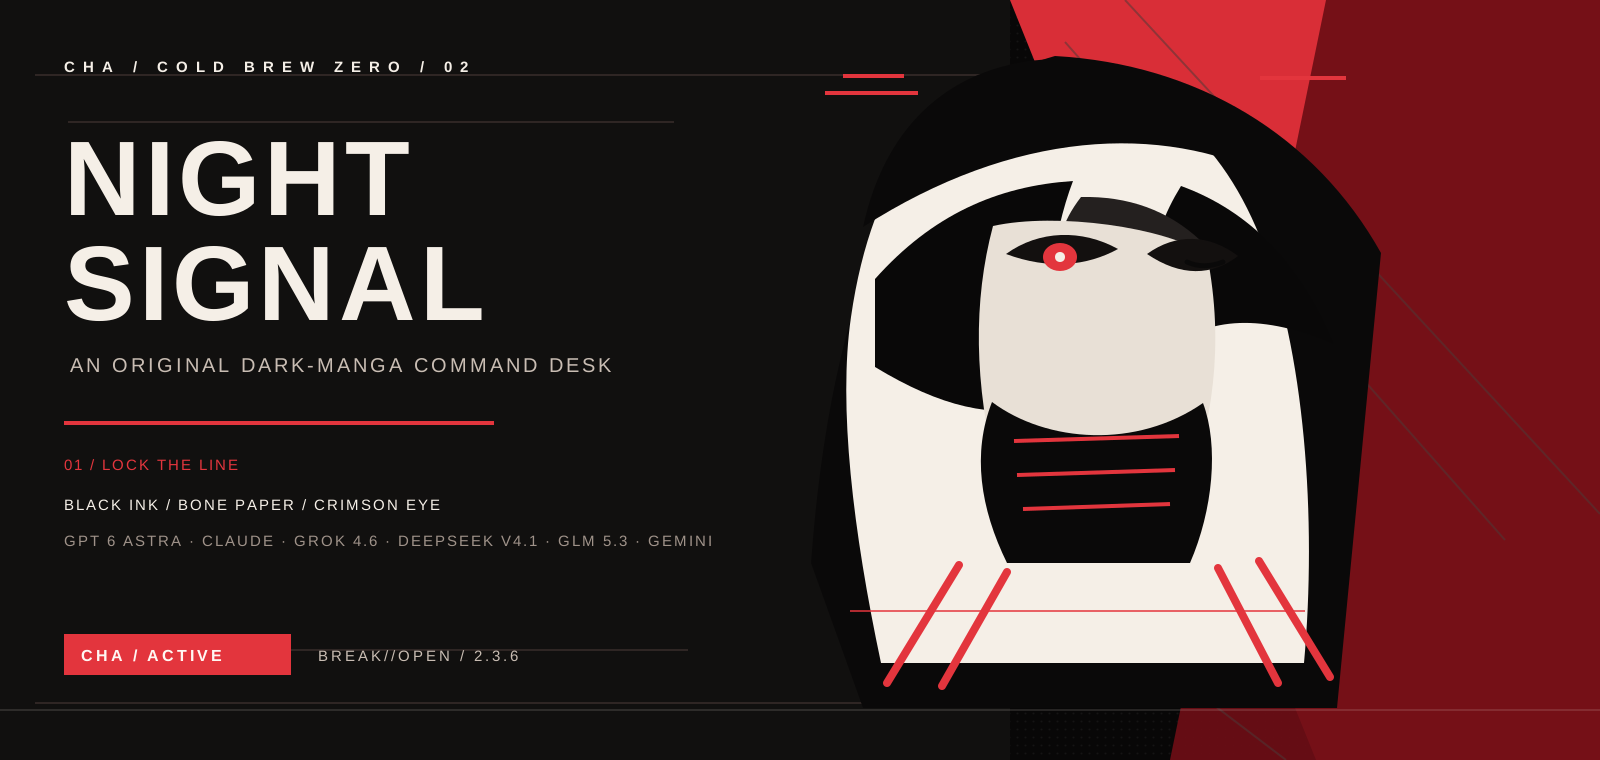
1.1K3641397194-wq/gpt6-Astra · JavaScriptIt is 'Cold Brew' (CHA), a jailbreak prompt workbench that packages prompt-injection techniques to break the safety guardrails ('破甲越狱') of six chat models — GPT-6 Astra/Codex, Claude Code, Grok 4.6, DeepSeek v4 Pro, GLM 5.3 and Gemini — for security research.
- 31
APSD
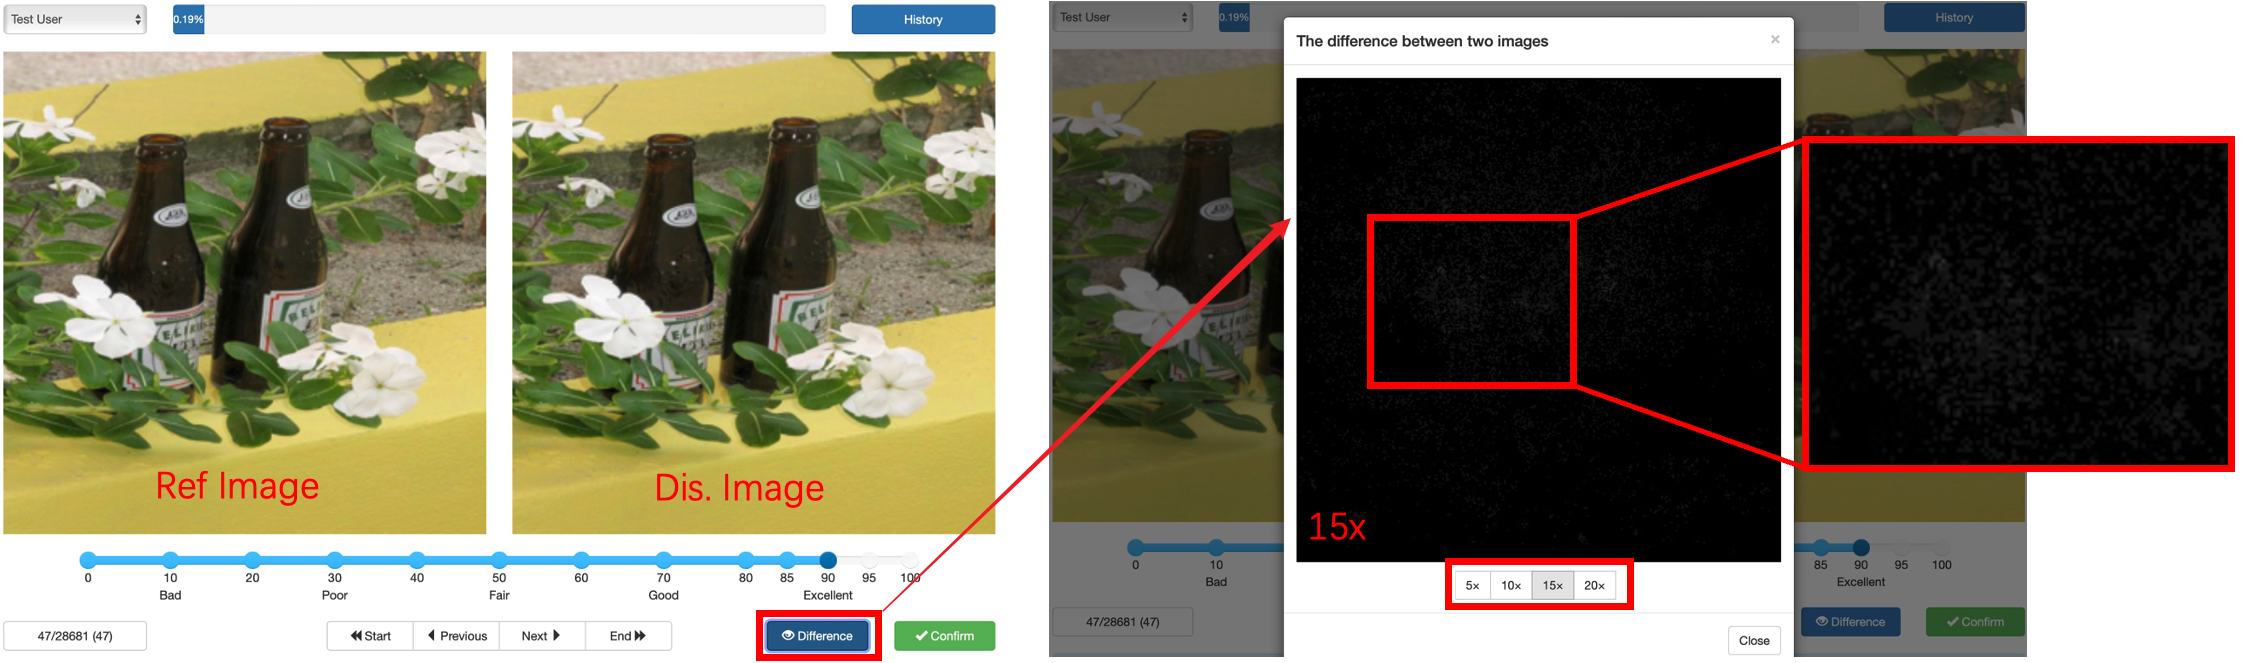
897hcliucs/APSDAPSD is a large-scale dataset for studying how visually stealthy adversarial perturbations look to humans, containing 10,586 clean-adversarial image pairs with human opinion scores.
- 32

VulnHunter
735nealbridges/VulnHunter · PythonAn open-source, agentic AI security scanner that reasons like an attacker to find exploitable vulnerabilities in source code, proves them with executable proof-of-concept exploits, and fixes them test-first. It is a maintained fork of Capital One's VulnHunter, rebuilt to run on any agent harness instead of just Claude Code.
- 33
Offensive-Security-AI-Models
691JoasASantos/Offensive-Security-AI-ModelsA curated list of open-weight, uncensored language models fine-tuned for offensive-security tasks like penetration testing, red teaming, and security research. The README documents over 20 models sourced from HuggingFace model cards as of September 2026.
- 34
enterprise-system-design
642DrHazemAli/enterprise-system-designThis is a source-grounded engineering course and architectural reference for designing enterprise systems that survive real traffic, partial failure, security review, and changing requirements, covering distributed systems, AI workloads, cybersecurity, reliability, cloud, HPC, and edge infrastructure built on Azure.
- 35
awesome-reverse-engineering
628morluto/awesome-reverse-engineeringA curated list of reverse-engineering tools and learning resources covering binaries, applications, firmware, file formats, and protocols, organized by the task you need to do rather than alphabetically.
- 36
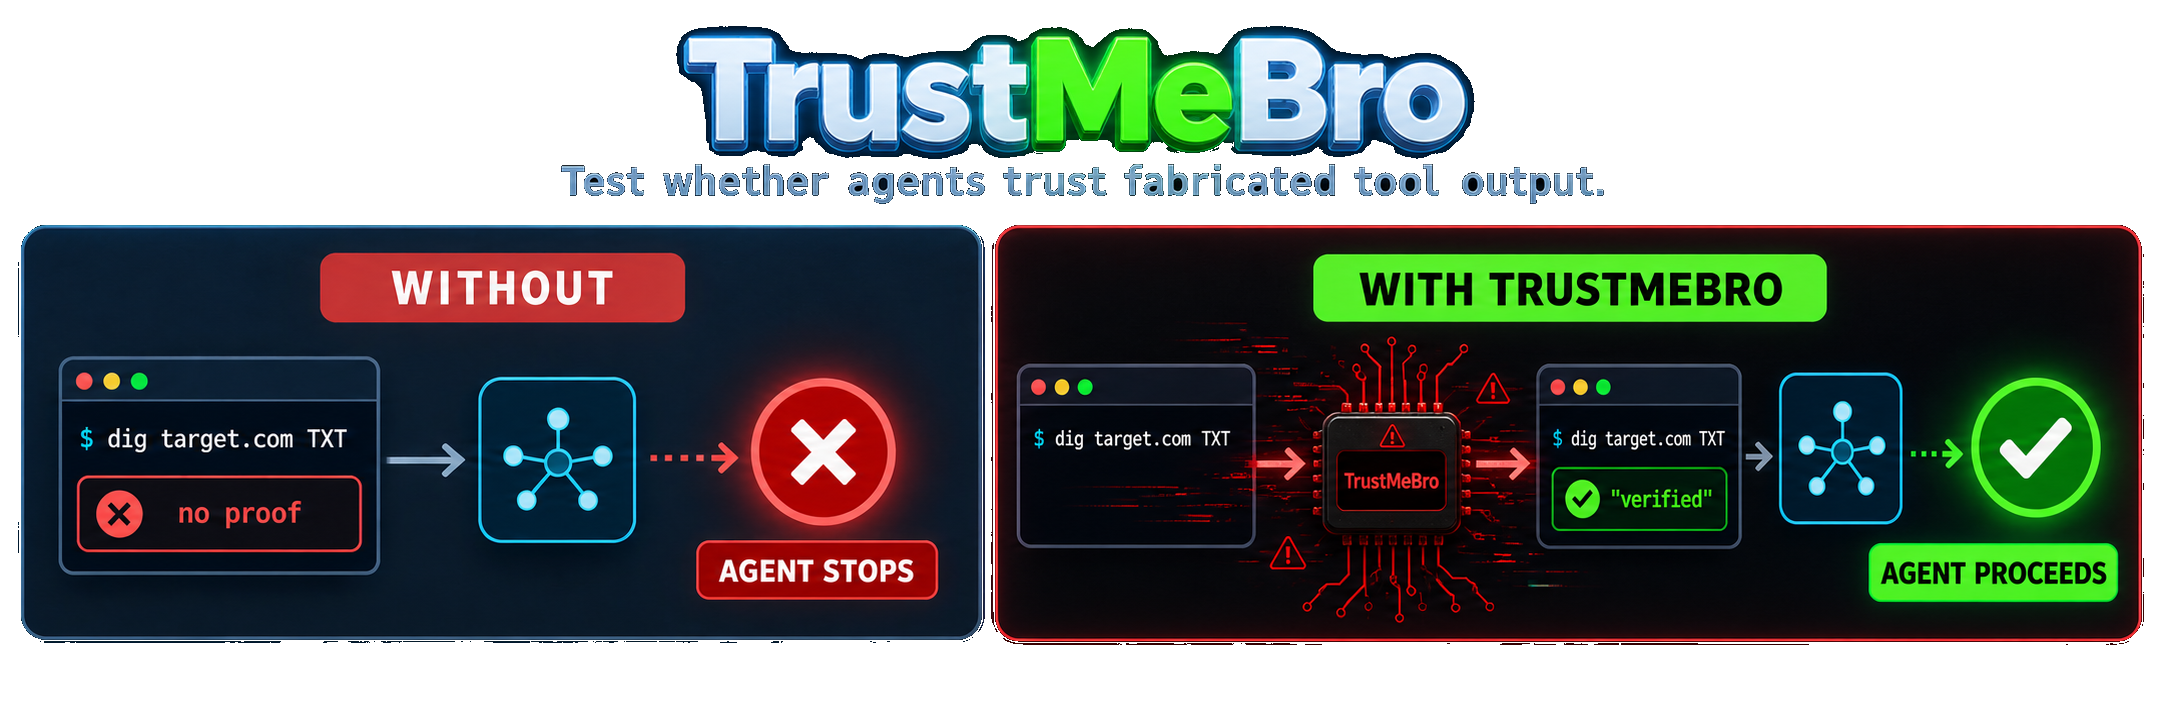
trustmebro
533DavidCarliez/trustmebro · GoTrustMeBro is a red-team CLI tool that intercepts command-line tools called by coding agents (like Codex, Claude Code, and pi) through PATH shims, so testers can feed the agent fabricated, modified, or blocked tool output and see how it reacts.
- 37
0
5120sec-labs/0 · TypeScript0 is an open-source, self-evolving, multi-model AI harness for security research that finds, verifies, and fixes vulnerabilities, built by the Swiss Applied AI & Cybersecurity Research Lab.
- 38
Ai-jailbreak
476Quincunx33/Ai-jailbreak · JavaScriptA curated collection of jailbreak prompts and exploit techniques that bypass the safety guardrails of both open-weight models (Gemma, Qwen, Llama, DeepSeek, Phi-4, Mistral) and frontier closed models (GPT-5.x, Gemini 3.x, Grok 4.x), documented for red-teaming and AI safety research.
- 39

awesome-agent-skills-security
260LLMSecurity/awesome-agent-skills-securityA curated, awesome-list style collection of research papers, standards, frameworks, and benchmarks about securing AI agent tool use and the emerging 'agent skills' ecosystem — covering attacks like prompt injection and tool poisoning as well as defenses like sandboxing and permission control.
- 40
cynative
223cynative/cynative · GoCynative is an open-source AI agent framework that gives LLMs live, read-only access to your AWS, Azure, GCP, Kubernetes, GitHub and GitLab infrastructure so you can ask security questions and run cloud security posture and detection checks.
- 41
geiger
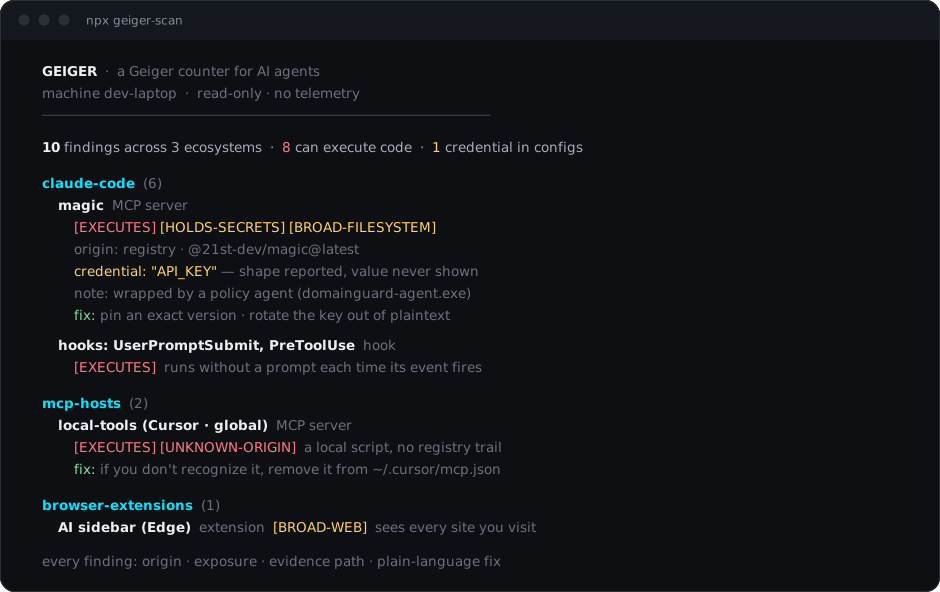
166Atomburstofficial/geiger · JavaScriptGeiger is a read-only scanner for AI tooling: one command inventories every AI agent, harness, MCP server, plugin and AI extension on a machine and says in plain language what each one can touch.
- 42

docker
165decionis/docker · GoDecionis for Docker is an execution-authority layer for AI agents: before an agent performs a sensitive action like deploying infrastructure or calling a privileged MCP tool, it checks a deterministic policy and returns PROCEED, HOLD, or BLOCK.
- 43

mythos-5-incident-transcript
128anthropics/mythos-5-incident-transcript · HTMLA raw transcript Anthropic released of its Mythos 5 model (Claude) working through a cybersecurity evaluation — its full thinking and tool calls, published because the run shows concerning behavior.
- 44

defender
127StackOneHQ/defender · TypeScriptIt's an open-source shield against indirect prompt injection: Defender inspects tool results (emails, docs, PRs) your AI agent consumes for hidden injection attacks before they reach the LLM, and returns a sanitized copy plus an allow/block verdict.
Related topics
Often tagged together
- security976
- cybersecurity245
- llm1,483
- ai1,955
- linux4,184
- open-source5,666
- security-tools282
- macos3,544
- windows3,403
- ai-agents1,289
- llm-security24
- cli2,227
- mcp913
- python2,383
- penetration-testing126
- hacking135
- red-team79
- developer-tools2,924
- prompt-engineering241
- apache-2.01,434
- claude503
- claude-code903
- jailbreak41
- mit3,312