Topics / #exploit
Exploit projects on GitHub
Exploit development frameworks and security research resources.
As of , the most-starred Exploit projects on GitHub are h4cker (29.8K stars), TrollStore (22.4K stars) and vulhub (21.4K stars). GitHub.Locker tracks 51 Exploit repositories with 366K stars combined. The fastest-growing on October 16 was awesome-reverse-engineering, with +59 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
 +59
awesome-reverse-engineering
morluto/awesome-reverse-engineering · ★ 628A curated list of reverse-engineering tools and learning resources covering binaries, applications, firmware, file formats, and protocols, organized by the task you need to do rather than alphabetically.
 +52
Relapse-Exploit
ntfargo/Relapse-Exploit · ★ 2.3KRelapse Exploit is a browser-based jailbreak chain for the PS5, working on firmware 7.00 through 13.60, that chains a WebKit browser exploit with a kernel exploit to gain kernel read/write and load custom payloads.
 +49
hexstrike-ai
0x4m4/hexstrike-ai · ★ 12.9KHexStrike AI MCP Agents is an MCP server that lets AI agents like Claude, GPT, or Copilot autonomously run 150+ real cybersecurity tools for automated pentesting, bug bounty hunting, CTF challenges, and vulnerability discovery.
 +31
AirCard
Mak5er/AirCard · ★ 6.7KAirCard is a macOS app that lets you customize Apple Wallet card skins and iOS lockscreen passcode keypad themes on iOS 18+ without jailbreaking your iPhone.
The all-time top
51 projects · by stars
- 29.8K
#1 · The-Art-of-Hacking/h4cker
h4cker
A curated collection of thousands of cybersecurity resources — references, scripts, tools, code, labs, and training material — maintained by Omar Santos as a companion to his books, video courses, and live training.
- 22.4K
 #2 · opa334/TrollStore
TrollStore
TrollStore is a permasigned jailed app for iOS that permanently installs any IPA you open in it. It works via an AMFI/CoreTrust bug: iOS doesn't correctly verify code signatures when a binary has multiple signers, so TrollStore can resign apps with its fake root certificate and keep them installed for good.
- 21.4K
 #3 · vulhub/vulhub
vulhub
Vulhub is an open-source collection of pre-built, ready-to-use vulnerable Docker environments: with one command you get a working lab for security research, learning, or demos.
- 4

Atmosphere
20.1KAtmosphere-NX/Atmosphere · C++Atmosphère is a work-in-progress custom firmware (CFW) for the Nintendo Switch that replaces and patches core parts of the console's Horizon OS to add new features and customization.
- 5

Awesome-Hacking-Resources
17.5Kvitalysim/Awesome-Hacking-ResourcesA curated collection of hacking, penetration testing and AI red-teaming resources — courses, YouTube channels, CTF platforms and guides, picked to make you better at offensive security.
- 6

social-engineer-toolkit
15.4Ktrustedsec/social-engineer-toolkit · PythonThe Social-Engineer Toolkit (SET) is an open-source penetration testing framework for authorized social-engineering assessments, giving security teams guided attack vectors to test user awareness and validate controls.
- 7
fscan
14.7Kshadow1ng/fscan · Gofscan is an open-source intranet scanner written in Go: one command runs an all-round internal-network audit — host discovery, port scanning, service identification, weak-password brute force and vulnerability detection.
- 8

PENTESTING-BIBLE
14KblaCCkHatHacEEkr/PENTESTING-BIBLEA curated catalog of over 200 numbered links to pentesting articles, bug bounty write-ups, cheat sheets and other security lists — a reading collection, not software.
- 9

awesome-web-security
13.9Kqazbnm456/awesome-web-security · PythonA curated list of web security materials and resources, organized by vulnerability class and attack type (XSS, SQL injection, CSRF, SSRF, XXE, deserialization, OAuth, JWT, and more), plus cheatsheets, tools, and write-ups for penetration testing.
- 10
pwntools
13.8KGallopsled/pwntools · PythonPwntools is a CTF framework and exploit development library written in Python, built for rapid prototyping with the goal of making exploit writing as simple as possible.
- 11

routersploit
13.3Kthreat9/routersploit · PythonRouterSploit is an open-source exploitation framework built specifically for testing the security of embedded devices like routers.
- 12

PowerSploit
13.1KPowerShellMafia/PowerSploit · PowerShellPowerSploit is a collection of PowerShell modules that penetration testers use during all phases of an assessment, covering code execution, persistence, privilege escalation, credential theft, exfiltration and reconnaissance on Windows systems.
- 13
hexstrike-ai
12.9K0x4m4/hexstrike-ai · PythonHexStrike AI MCP Agents is an MCP server that lets AI agents like Claude, GPT, or Copilot autonomously run 150+ real cybersecurity tools for automated pentesting, bug bounty hunting, CTF challenges, and vulnerability discovery.
- 14

awesome-ctf
11.9Kapsdehal/awesome-ctf · JavaScriptA curated list of frameworks, libraries, tools, and resources for Capture The Flag (CTF) competitions, covering everything from building challenges to solving them.
- 15

TheFatRat
11.5Kscreetsec/TheFatRat · CTheFatRat is an exploiting tool that compiles malware from famous payloads — an easy way to generate backdoors built to slip past most anti-virus software.
- 16

awesome-hacker-search-engines
11.3Kedoardottt/awesome-hacker-search-engines · ShellA curated list of search engines useful for penetration testing, vulnerability assessment, red/blue team operations, bug bounty hunting, and general OSINT work.
- 17

beef
11.1Kbeefproject/beef · JavaScriptBeEF (Browser Exploitation Framework) is a penetration testing tool that focuses on the web browser, letting a tester assess the real security posture of a target by using client-side attack vectors instead of network-perimeter exploits.
- 18

awesome-honeypots
10.6Kparalax/awesome-honeypots · PythonA curated, categorized list of honeypot software and related tools used by security researchers to deceive attackers, log their behavior, and study exploitation attempts.
- 19
reverse-engineering
10.6KwtsxDev/reverse-engineeringA curated list of reverse engineering resources: books, courses, practice grounds, and a big toolbox section spanning hex editors, disassemblers, debuggers, and dynamic analysis tools.
- 20

nishang
10.2Ksamratashok/nishang · PowerShellNishang is a framework and large collection of PowerShell scripts and payloads for offensive security, penetration testing, and red teaming, covering every phase of an engagement.
- 21

Claude-Red
7.6KSnailSploit/Claude-Red · Pythonclaude-red is a curated library of offensive security skills for the Claude Skills system: structured SKILL.md files that prime Claude with expert-level methodology for one attack surface each, from SQLi to shellcode.
- 22
AirCard
6.7KMak5er/AirCard · SwiftAirCard is a macOS app that lets you customize Apple Wallet card skins and iOS lockscreen passcode keypad themes on iOS 18+ without jailbreaking your iPhone.
- 23
Decepticon
6.2KBitterSecurity/Decepticon · PythonDecepticon is a professional autonomous Red Team agent that runs full attack chains — reconnaissance, exploitation, privilege escalation, lateral movement, and C2 — the way a real adversary would, instead of just scanning and printing a report.
- 24
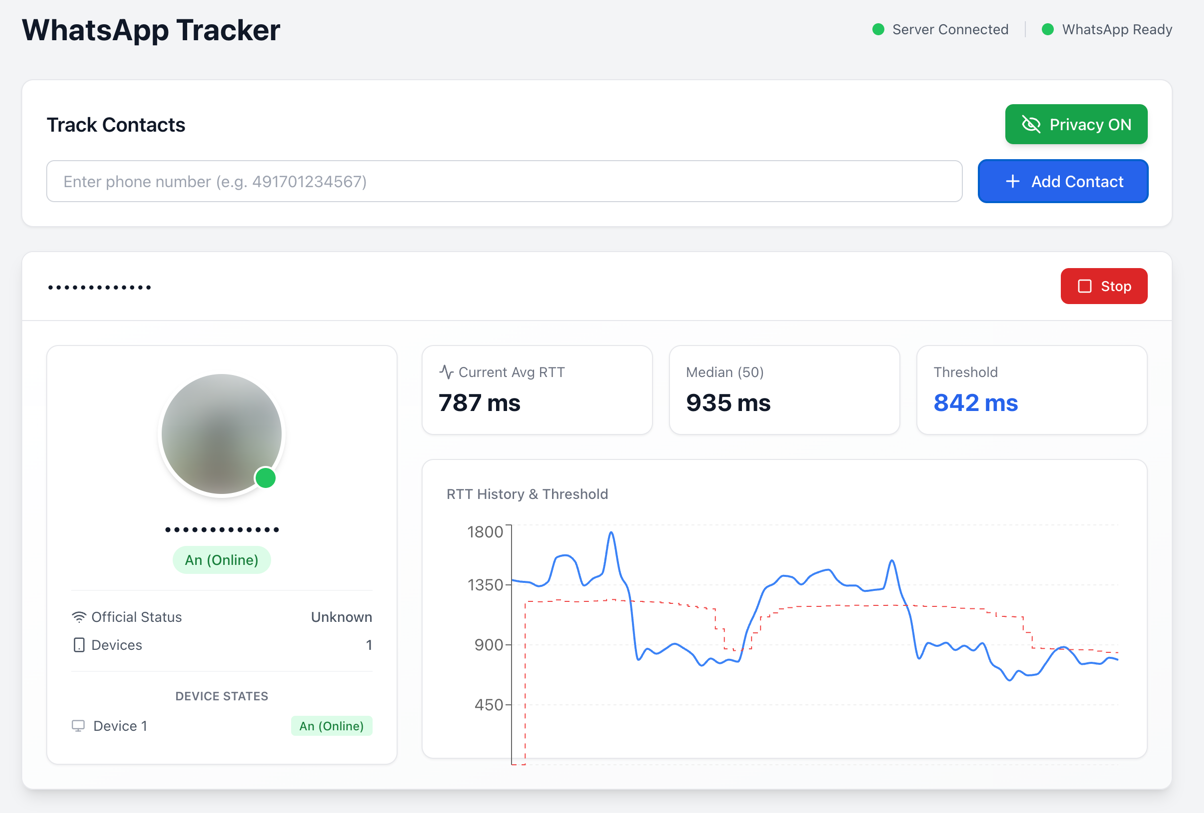
device-activity-tracker
5.2Kgommzystudio/device-activity-tracker · TypeScriptThis is a proof-of-concept security research tool that monitors WhatsApp and Signal users by measuring the Round-Trip Time (RTT) of message delivery receipts, revealing whether a target's device is actively in use, idle, or offline.
- 25

exploitarium
5.2Kbikini/exploitarium · PythonExploitarium is a single consolidated archive of the author's public proof-of-concept exploits and vulnerability research writeups, merging dozens of their former standalone PoC repos into one place.
- 26
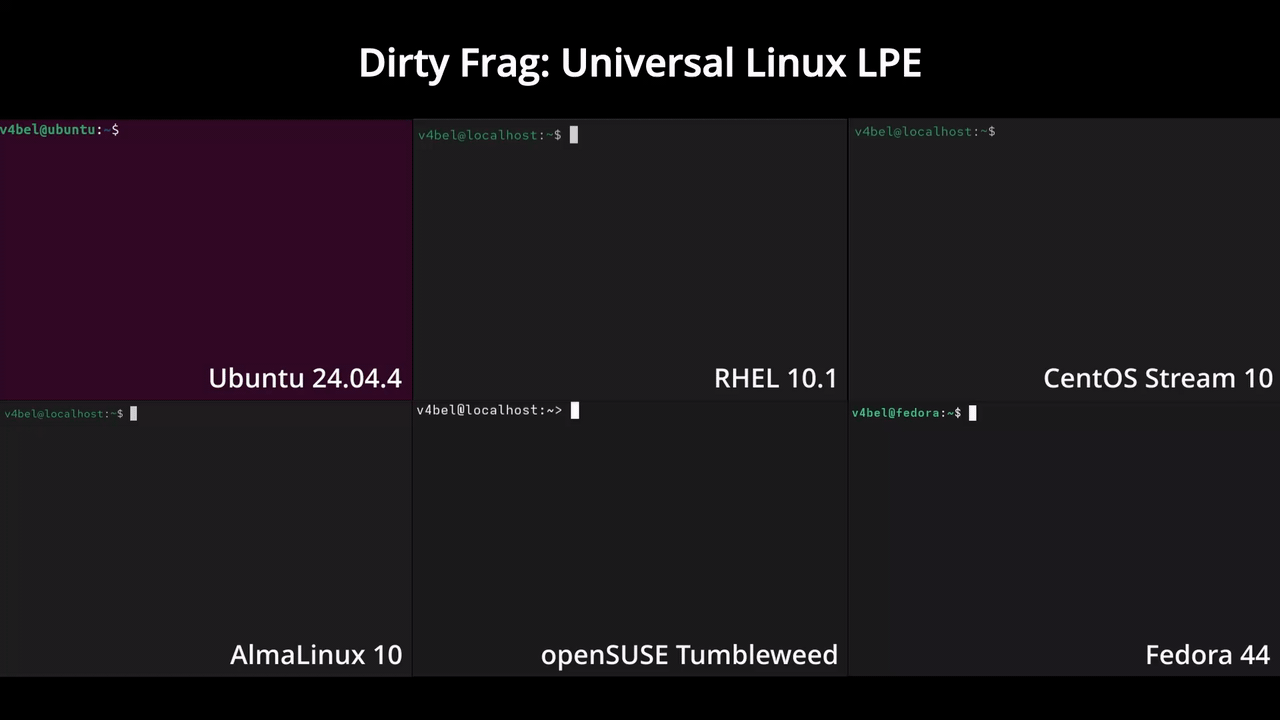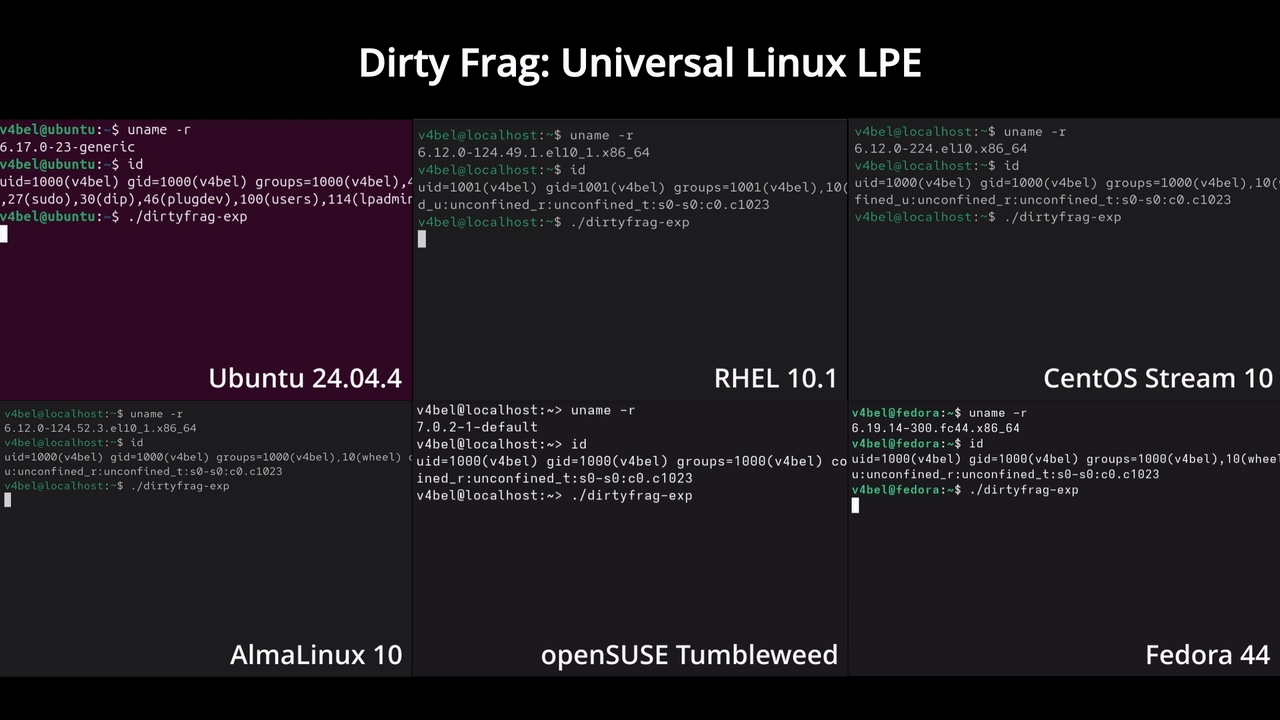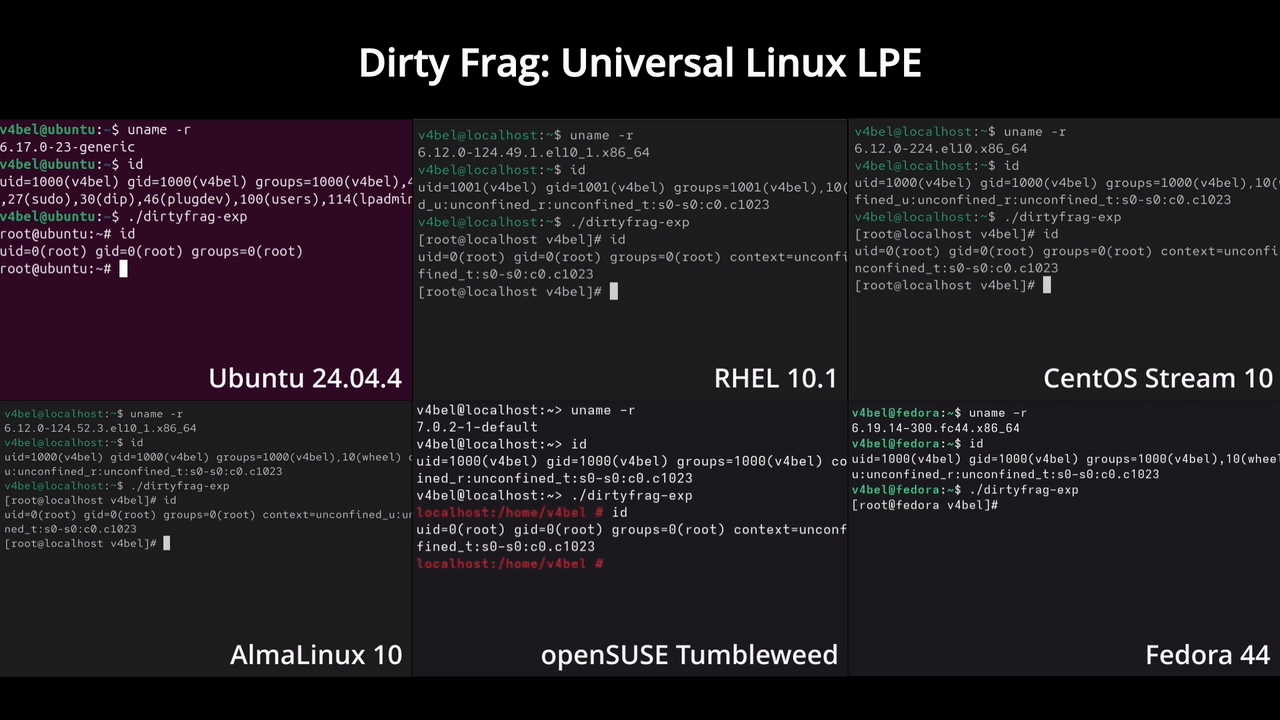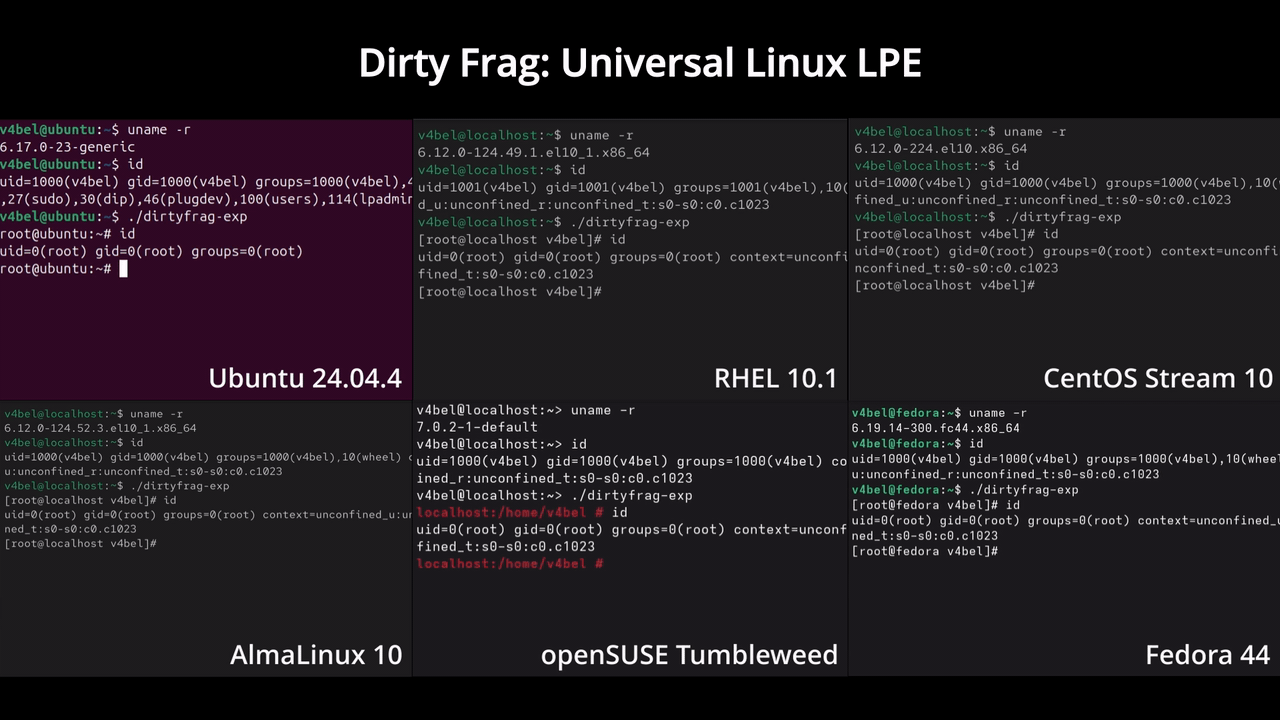
dirtyfrag
5.1KV4bel/dirtyfrag · CDirty Frag is a proof-of-concept Linux kernel local privilege escalation exploit that chains two page-cache write vulnerabilities (CVE-2026-43284 and CVE-2026-43500) to obtain root on major Linux distributions.
- 27

copy-fail-CVE-2026-31431
4.1Ktheori-io/copy-fail-CVE-2026-31431 · PythonThis repository is a technical writeup and proof-of-concept for CVE-2026-31431, a 9-year-old Linux kernel local privilege escalation (LPE) vulnerability found by Theori's AI vulnerability research tool, Xint Code.
- 28

misaka26
4Kstraight-tamago/misaka26misaka26 is an iOS/iPadOS customization tool that uses the same underlying bug as TrollRestore to unlock hidden system features on supported devices, running iOS 16.0 through 26.1 and the 26.2 beta 1, without a full jailbreak.
- 29
redamon
3.1Ksamugit83/redamon · PythonRedAmon is an open-source, self-hosted AI framework that chains reconnaissance, exploitation and post-exploitation into one pipeline, maps the attack surface into a Neo4j graph, and then triages findings and opens GitHub pull requests that fix what it discovers.
- 30
mantis
2.5Kgoogle/mantis · PythonMantis is a toolkit of skills plus a reference agent harness (built on Google's ADK) that lets AI coding agents autonomously find, reproduce, triage, and patch vulnerabilities in a codebase.
- 31
Relapse-Exploit
2.3Kntfargo/Relapse-Exploit · JavaScriptRelapse Exploit is a browser-based jailbreak chain for the PS5, working on firmware 7.00 through 13.60, that chains a WebKit browser exploit with a kernel exploit to gain kernel read/write and load custom payloads.
- 32
skitter-creek-bath-salts
2.1Kxoreaxeaxeax/skitter-creek-bath-salts · CA security research project that shows how to unlock protected regions on an AMD CPU — the Platform Security Processor, System Management Mode, C6 DRAM, and CPU microcode — by scrambling the DRAM controller's physical-to-DRAM address translation.
- 33

ghostlock-app
2KYuKongA/ghostlock-app · KotlinGhostLock is a one-tap Android app that runs the CVE-2026-43499 kernel exploit to grant uid 0 (root) on a matching vulnerable kernel, optionally loading a KernelSU-style module afterward.
- 34
AirCard-iOS
1.9KMak5er/AirCard-iOS · SwiftAirCard-iOS lets you customize Apple Wallet card artwork, lock screen passcode dialer themes, and PosterBoard wallpapers directly on an iPhone running iOS 27 or newer.
- 35

AirCard-Windows
1.4KLumid-Off/AirCard-Windows · RustAirCard is a Windows app that lets you apply custom skins to your Apple Wallet cards and custom lockscreen passcode keypad themes on iOS 18+, all without jailbreaking the iPhone.
- 36
ps5-webkit-autoloader
1.1KitsPLK/ps5-webkit-autoloader · JavaScriptIt is an automated payload loader for exploited (jailbroken) PS5 consoles: it boots the WebKit exploit chain and then sends your ELF payloads automatically, all triggered from a homescreen shortcut on the console itself.
- 37

Xbox360PeerPressure
754grimdoomer/Xbox360PeerPressurePeer Pressure is a persistent softmod exploit for the Xbox 360. It modifies the console's NAND image and HDD security sectors to trigger a chain of DMA attacks at startup, letting you run unsigned code and homebrew.
- 38

VulnHunter
735nealbridges/VulnHunter · PythonAn open-source, agentic AI security scanner that reasons like an attacker to find exploitable vulnerabilities in source code, proves them with executable proof-of-concept exploits, and fixes them test-first. It is a maintained fork of Capital One's VulnHunter, rebuilt to run on any agent harness instead of just Claude Code.
- 39
Offensive-Security-AI-Models
691JoasASantos/Offensive-Security-AI-ModelsA curated list of open-weight, uncensored language models fine-tuned for offensive-security tasks like penetration testing, red teaming, and security research. The README documents over 20 models sourced from HuggingFace model cards as of September 2026.
- 40
awesome-reverse-engineering
628morluto/awesome-reverse-engineeringA curated list of reverse-engineering tools and learning resources covering binaries, applications, firmware, file formats, and protocols, organized by the task you need to do rather than alphabetically.
- 41

Stuxnet
588Sadpainy/Stuxnet · CThis is a reconstructed source code of Stuxnet, the famous 2010 worm that sabotaged Siemens industrial control systems, rebuilt by the author from reverse-engineering research for educational and malware-analysis purposes.
- 42

CVE-2026-9830
477opaxial/CVE-2026-9830 · PythonA Python proof-of-concept that validates a reported unauthenticated REST API exposure in the BookingPress Pro WordPress plugin, which can leak booking and customer data.
- 43
Ai-jailbreak
476Quincunx33/Ai-jailbreak · JavaScriptA curated collection of jailbreak prompts and exploit techniques that bypass the safety guardrails of both open-weight models (Gemma, Qwen, Llama, DeepSeek, Phi-4, Mistral) and frontier closed models (GPT-5.x, Gemini 3.x, Grok 4.x), documented for red-teaming and AI safety research.
- 44

FilzaSlop
4480xjohnnydev/FilzaSlop · Objective-CFilzaSlop is a fork of FilzaJailedDS that adds a sandbox escape exploit and app container access to the Filza file manager on iOS 18, iOS 26, and iOS 27 beta 1-4, plus a bundled PosterBoard Wallpaper Lab.
- 45

allinonetools
396LinkMouseIndex/allinonetoolsA PowerShell tool that claims to give free, instant access to Steam's full game library (50,000+ titles) through a shared-account auto-login system, launched by pasting a single command into an admin terminal.
- 46

bad_query
276forcequitOS/bad_query · Cbadquery is a proof-of-concept sandbox escape for iOS 26 and 27, written in C — code that demonstrates breaking out of the iOS app sandbox.
- 47
Erosion
245jailbreakdotparty/Erosion · SwiftErosion is an iOS customization toolbox that uses the bad_query sandbox escape exploit to apply tweaks on supported iOS/iPadOS versions, no traditional jailbreak required.
- 48
ablation
214Ablation-Tool/ablation · PythonAblation is a reverse engineering framework that provides the same core disassembly, decompilation, and binary analysis capabilities as industry tools like Ghidra, IDA Pro, and Binary Ninja, and it's built to be driven by an AI coding agent.
- 49

freepp
189mio-cc/freepp · PythonThis is min-implant-v2, a Python/Node research project that automates the ChatGPT subscription payment chain across many regional payment channels (PayPal, direct card, PIX, iDEAL, UPI, Kakao Pay, etc.) to study promo-code zero-cost subscription flows.
- 50

CVE-2026-62911
187hypnguyen1209/CVE-2026-62911 · PythonA proof-of-concept exploit for CVE-2026-62911, a pre-auth RCE in Microsoft Exchange Server that relays an NTLM machine account hash to the MRSProxy service to drop and run an ASPX webshell, giving full SYSTEM access without any credentials.
- 51

badnotes
149c22dev/badnotes · Objective-CBadNotes is a jailbreak tweak for iOS that unlocks GoodNotes Pro by spoofing the app's subscription check.
Related topics
Often tagged together
- security976
- hacking135
- cybersecurity245
- security-tools282
- penetration-testing126
- reverse-engineering221
- linux4,184
- python2,383
- vulnerability50
- offensive-security77
- red-team79
- pentesting113
- open-source5,666
- security-research41
- windows3,403
- hacking-tool75
- macos3,544
- exploit-development15
- infosec47
- jailbreak41
- mit3,312
- tool1,295
- awesome-list495
- curated-list634