Topics / #hacking-tool
Hacking-tool projects on GitHub
Security utilities used for penetration testing, denial of service, and offensive hacking tasks.
As of , the most-starred Hacking-tool projects on GitHub are Win11Debloat (59.4K stars), x64dbg (49.9K stars) and HEU_KMS_Activator (44K stars). GitHub.Locker tracks 75 Hacking-tool repositories with 852.7K stars combined. The fastest-growing on October 16 was GhostTrack, with +122 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
 +122
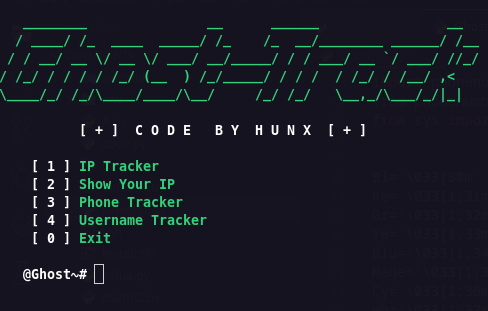
GhostTrack
HunxByts/GhostTrack · ★ 19.3KGhostTrack is a Python command-line OSINT tool used to track a target's approximate location or gather details about a phone number, essentially a piece of information-gathering tooling for recon work.
 +77
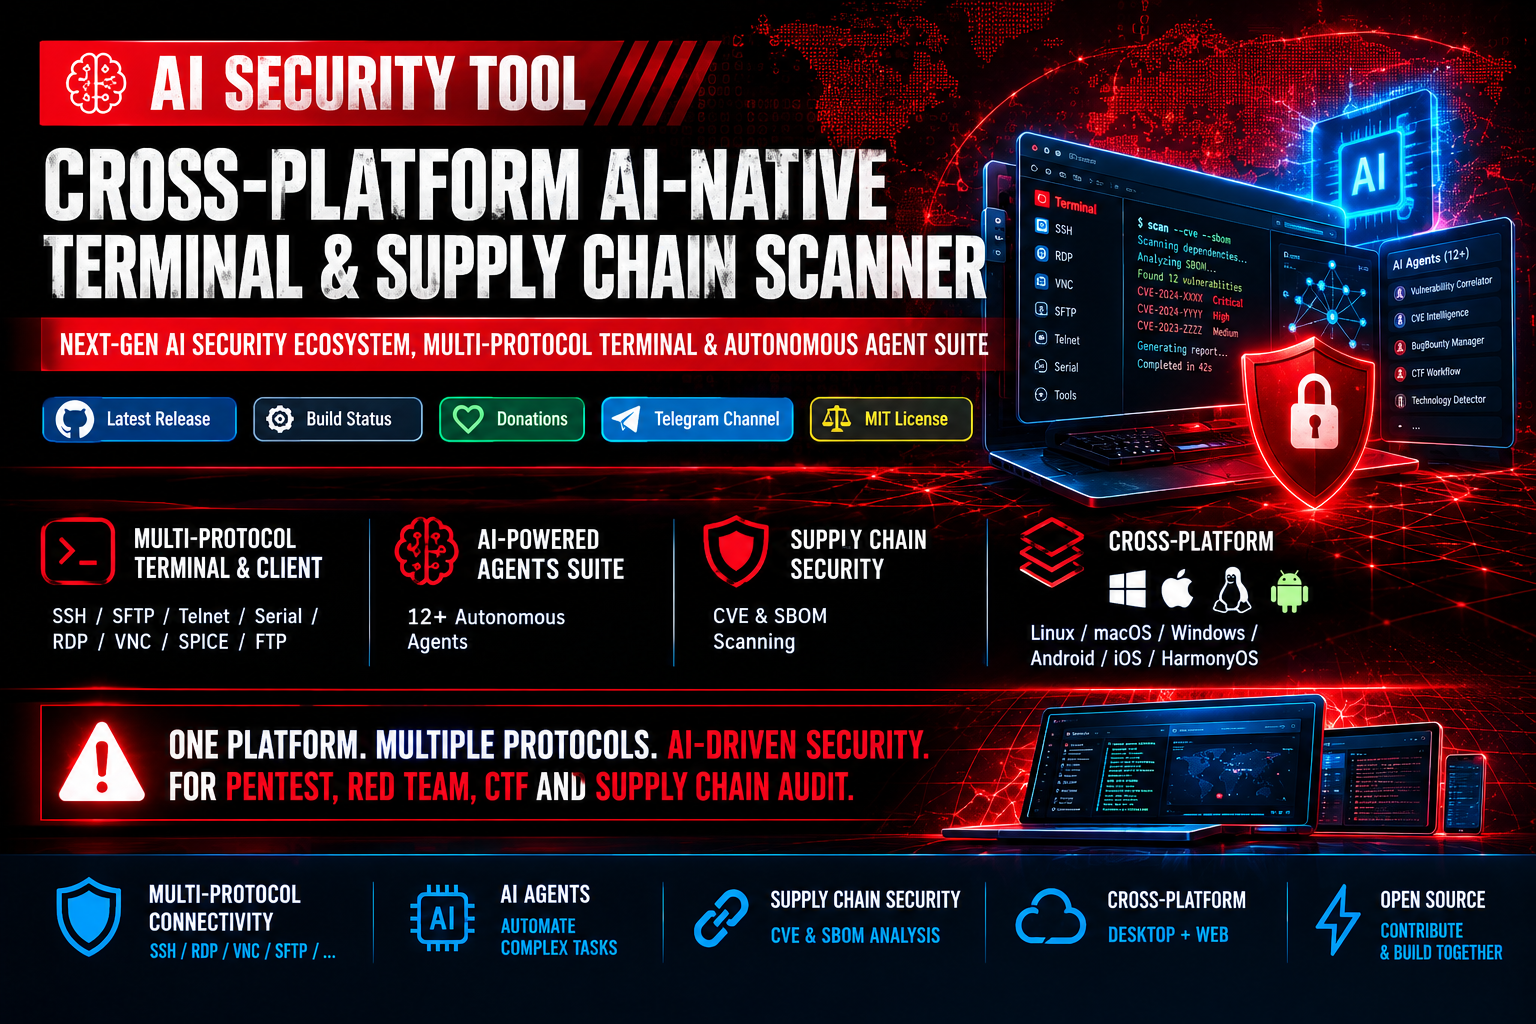
ai-security-tool
ZeroDayEvil/ai-security-tool · ★ 840AI Security Tool is an open-source, cross-platform terminal and vulnerability scanner that combines a multi-protocol connectivity client (SSH, RDP, VNC, etc.), CVE/SBOM supply-chain auditing, and 12+ autonomous AI agents (DeepSeek, OpenAI) to automate pentesting, Red Team, and CTF workflows.
 +67
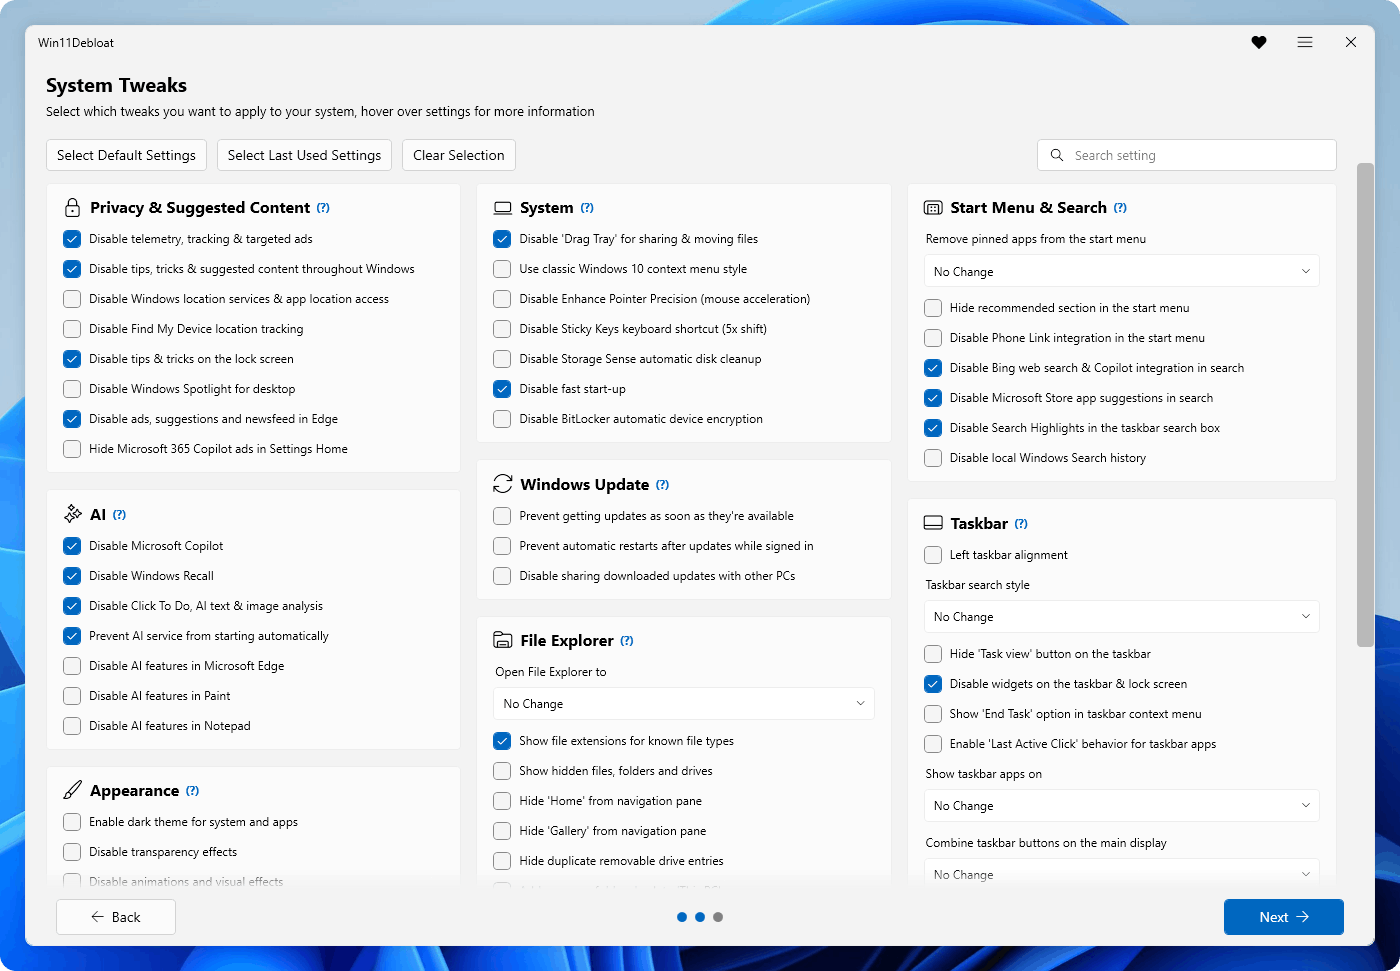
Win11Debloat
Raphire/Win11Debloat · ★ 59.4KWin11Debloat is a lightweight PowerShell script that removes pre-installed apps, disables telemetry, and tweaks the interface to declutter and customize Windows 10 and Windows 11.
 +32
MFG-Unlocker
dashdogy/MFG-Unlocker · ★ 1.4KAn experimental Windows mod that unlocks higher DLSS Multi Frame Generation (MFG) multipliers, up to 6X, for games on NVIDIA RTX 40 series GPUs that already support Streamline DLSS Frame Generation.
The all-time top
75 projects · by stars
- 59.4K#1 · Raphire/Win11Debloat
Win11Debloat
Win11Debloat is a lightweight PowerShell script that removes pre-installed apps, disables telemetry, and tweaks the interface to declutter and customize Windows 10 and Windows 11.
- 49.9K
 #2 · x64dbg/x64dbg
x64dbg
x64dbg is an open-source user-mode debugger for Windows, built specifically for reverse engineering and malware analysis.
- 44K
 #3 · zbezj/HEU_KMS_Activator
HEU_KMS_Activator
This is 'HEU_KMS_Activator', a tool whose name indicates it performs KMS (Key Management Service) based activation, most likely for Windows and Microsoft Office, though the README itself does not provide a description.
- 4

metasploit-framework
39.2Krapid7/metasploit-framework · RubyMetasploit Framework is an open-source penetration testing framework written in Ruby — one of the best-known security toolkits on GitHub, with about 39,000 stars.
- 5

sqlmap
38.7Ksqlmapproject/sqlmap · Pythonsqlmap is an open-source penetration testing tool that automates detecting and exploiting SQL injection flaws and taking over the underlying database server.
- 6

masscan
26.1Krobertdavidgraham/masscan · CMasscan is an Internet-scale TCP port scanner that transmits SYN packets asynchronously and can scan the entire IPv4 Internet in under 5 minutes, sending up to 10 million packets per second from a single machine.
- 7
radare2
25.1Kradareorg/radare2 · Cr2 (radare2) is a libre reverse engineering framework for Unix-like systems: a set of libraries, tools and plugins for analyzing, disassembling, emulating, debugging and modifying binaries.
- 8
unleashed-firmware
22.5KDarkFlippers/unleashed-firmware · CUnleashed is custom firmware for the Flipper Zero multitool — a fork of the official firmware (OFW) that adds extra features and improvements while staying compatible with official apps.
- 9

mimikatz
21.9Kgentilkiwi/mimikatz · CA small Windows security tool, originally written to learn C. It is best known for extracting plaintext passwords, hashes, PIN codes and Kerberos tickets from memory, and can perform pass-the-hash, pass-the-ticket or build Golden tickets.
- 10

Ciphey
21.7Kbee-san/Ciphey · Rustciphey automatically decrypts ciphertext without knowing the key or cipher, decodes encodings and cracks hashes. It is the Rust-built next generation of Ciphey — roughly 7x faster per decode — and the same team intends it to fully replace the original.
- 11
cheat-engine
19.3Kcheat-engine/cheat-engine · PascalCheat Engine is a development environment focused on modding games and applications for personal use. Its repository tags describe it as a memory scanner and debugger.
- 12
GhostTrack
19.3KHunxByts/GhostTrack · PythonGhostTrack is a Python command-line OSINT tool used to track a target's approximate location or gather details about a phone number, essentially a piece of information-gathering tooling for recon work.
- 13
zphisher
17Khtr-tech/zphisher · HTMLZphisher is an automated phishing tool with 30+ ready-made login-page templates, written as a beginners-friendly shell script and intended purely for education.
- 14
ffuf
16.9Kffuf/ffuf · Goffuf is a fast web fuzzer written in Go — a command-line tool that sends many crafted requests to a target to discover directories, virtual hosts, and fuzzable GET/POST parameters.
- 15

MHDDoS
16.9KMatrixTM/MHDDoS · PythonMHDDoS is a Python 3 DDoS testing toolkit with 57 attack methods spanning Layer 7 (HTTP floods, Cloudflare/OVH bypasses) and Layer 4/3 (TCP, UDP, SYN, amplification attacks), meant for authorized security testing and research.
- 16

PentestGPT
16KGreyDGL/PentestGPT · PythonPentestGPT is an agentic framework that uses large language models to run automated penetration testing and solve CTF challenges, working through staged phases like recon, exploitation and reporting.
- 17
evilginx2
15.7Kkgretzky/evilginx2 · GoEvilginx is a man-in-the-middle attack framework used for phishing login credentials along with session cookies, which lets an attacker bypass 2-factor authentication.
- 18

hacker-roadmap
15.7Ksundowndev/hacker-roadmapThis is a curated roadmap and toolkit index for learning and practicing ethical hacking: it explains what penetration testing is and groups hundreds of security tools, wordlists and references by category (recon, password attacks, wireless, exploitation, web hacking, post-exploitation, frameworks).
- 19

social-engineer-toolkit
15.4Ktrustedsec/social-engineer-toolkit · PythonThe Social-Engineer Toolkit (SET) is an open-source penetration testing framework for authorized social-engineering assessments, giving security teams guided attack vectors to test user awareness and validate controls.
- 20

XSStrike
15.2Ks0md3v/XSStrike · PythonXSStrike is a Cross Site Scripting (XSS) detection suite built around four hand-written parsers, an intelligent payload generator, a fuzzing engine, and a fast crawler. Instead of just firing generic payloads like most scanners, it analyzes the live response and crafts payloads guaranteed to work through context analysis.
- 21
esp8266_deauther
15KSpacehuhnTech/esp8266_deauther · CESP8266 Deauther is open-source firmware for the ESP8266 chip that lets you scan nearby WiFi networks, send deauthentication packets to disconnect devices, and spin up dozens of fake WiFi networks to confuse scanners - an affordable platform for testing and learning about WiFi security.
- 22

dirsearch
15Kmaurosoria/dirsearch · PythonDirsearch is an advanced command-line web path brute-forcer used to discover hidden files and directories on websites for security testing.
- 23
wifiphisher
14.9Kwifiphisher/wifiphisher · PythonWifiphisher is a rogue access point framework for conducting Wi-Fi phishing and man-in-the-middle attacks against wireless clients, used in red team and penetration testing engagements.
- 24

binwalk
14.5KReFirmLabs/binwalk · RustBinwalk is a firmware analysis tool that can identify, and optionally extract, files and data that have been embedded inside other files.
- 25

gobuster
14.2KOJ/gobuster · GoGobuster is a fast, multi-threaded command-line tool written in Go for brute-forcing web directories/files, DNS subdomains, and virtual hosts, plus enumerating S3/GCS cloud storage buckets and TFTP files.
- 26

wechat_jump_game
13.8Kwangshub/wechat_jump_game · PythonA Python script that plays WeChat's mini-game 'Jump Jump' (跳一跳) automatically, using image recognition to measure jump distance and ADB to control the phone screen.
- 27

PowerSploit
13.1KPowerShellMafia/PowerSploit · PowerShellPowerSploit is a collection of PowerShell modules that penetration testers use during all phases of an assessment, covering code execution, persistence, privilege escalation, credential theft, exfiltration and reconnaissance on Windows systems.
- 28
ESP32Marauder
12.8Kjustcallmekoko/ESP32Marauder · C++ESP32 Marauder is a suite of offensive and defensive WiFi and Bluetooth tools that run as firmware on an ESP32 microcontroller, used for things like wardriving, scanning, and wireless security testing.
- 29

wifi-cracking
12.7Kbrannondorsey/wifi-crackingA step-by-step tutorial for cracking WPA/WPA2 Wi-Fi passwords: capture a handshake with Airodump-ng, then crack it offline with Aircrack-ng or Hashcat.
- 30

thc-hydra
12.4Kvanhauser-thc/thc-hydra · CHydra is a parallelized network login cracker by van Hauser / THC: a proof-of-concept tool showing researchers and security consultants how easily a remote system can be broken into through weak passwords. It supports over 50 protocols.
- 31

Resources-for-Beginner-Bug-Bounty-Hunters
12.3Knahamsec/Resources-for-Beginner-Bug-Bounty-HuntersA curated collection of resources for people getting started with web hacking and bug bounty hunting, including blog posts, talks, books, tools, labs and vulnerability-type guides.
- 32
xray
11.8Kchaitin/xray · Vuexray is a security assessment tool built by Chaitin for scanning common web vulnerabilities and running custom PoCs against targets.
- 33

TheFatRat
11.5Kscreetsec/TheFatRat · CTheFatRat is an exploiting tool that compiles malware from famous payloads — an easy way to generate backdoors built to slip past most anti-virus software.
- 34
GhidraMCP
11.4KLaurieWired/GhidraMCP · JavaGhidraMCP is a Model Context Protocol server that lets LLMs autonomously reverse engineer applications by exposing Ghidra's core functionality (decompiling, renaming, listing imports/exports) to any MCP client.
- 35

pwndbg
11.1Kpwndbg/pwndbg · PythonA plug-in for GDB and LLDB that makes debugging far less painful for low-level developers, hardware hackers, reverse-engineers and exploit developers — it adds the utilities vanilla debuggers are missing.
- 36

beef
11.1Kbeefproject/beef · JavaScriptBeEF (Browser Exploitation Framework) is a penetration testing tool that focuses on the web browser, letting a tester assess the real security posture of a target by using client-side attack vectors instead of network-perimeter exploits.
- 37

Sublist3r
11.1Kaboul3la/Sublist3r · PythonSublist3r is a Python tool that enumerates subdomains of a target website using OSINT, helping penetration testers and bug hunters gather subdomains for a domain they are targeting.
- 38

LaZagne
11KAlessandroZ/LaZagne · PythonLaZagne is an open-source tool that retrieves passwords stored locally on a computer by reverse-engineering the storage method of each software (plaintext, APIs, custom algorithms, databases, etc.).
- 39

Red-Teaming-Toolkit
10.8Kinfosecn1nja/Red-Teaming-ToolkitIt is a curated list of cutting-edge open-source security tools for red teamers and threat hunters, covering the full attack lifecycle from reconnaissance to exfiltration.
- 40

nikto
10.8Ksullo/nikto · PerlNikto is an open-source web server scanner that checks servers for dangerous files, outdated software versions, and other common vulnerabilities.
- 41
bbot
10.7Kblacklanternsecurity/bbot · PythonBBOT is a recursive internet scanner for hackers — it automates recon, bug bounty work and attack surface management (ASM), inspired by Spiderfoot.
- 42

awesome-honeypots
10.6Kparalax/awesome-honeypots · PythonA curated, categorized list of honeypot software and related tools used by security researchers to deceive attackers, log their behavior, and study exploitation attempts.
- 43

nishang
10.2Ksamratashok/nishang · PowerShellNishang is a framework and large collection of PowerShell scripts and payloads for offensive security, penetration testing, and red teaming, covering every phase of an engagement.
- 44
ProxyBridge
6.8KInterceptSuite/ProxyBridge · CProxyBridge is a cross-platform proxy client that transparently redirects TCP and UDP traffic from specific Windows/macOS/Linux applications through SOCKS5 or HTTP proxies, acting as an open-source alternative to Proxifier.
- 45

T3MP3ST
6.6Kelder-plinius/T3MP3ST · TypeScriptT3MP3ST is a multi-agent offensive-security framework that turns an AI coding agent you already use into an autonomous red-teaming operator. Point it at an authorized target and it runs the kill chain — recon, exploit, report — from a browser 'War Room' or the CLI.
- 46
Agentic-Bug-Hunter
5.4Kawarexone/Agentic-Bug-Hunter · PythonAgentic Bug Hunter is an AI-powered bug bounty toolkit that runs recon, tests for vulnerabilities, validates findings against a strict gate, and writes submission-ready reports for HackerOne, Bugcrowd, Intigriti, or Immunefi, right from your terminal.
- 47
dirtyfrag
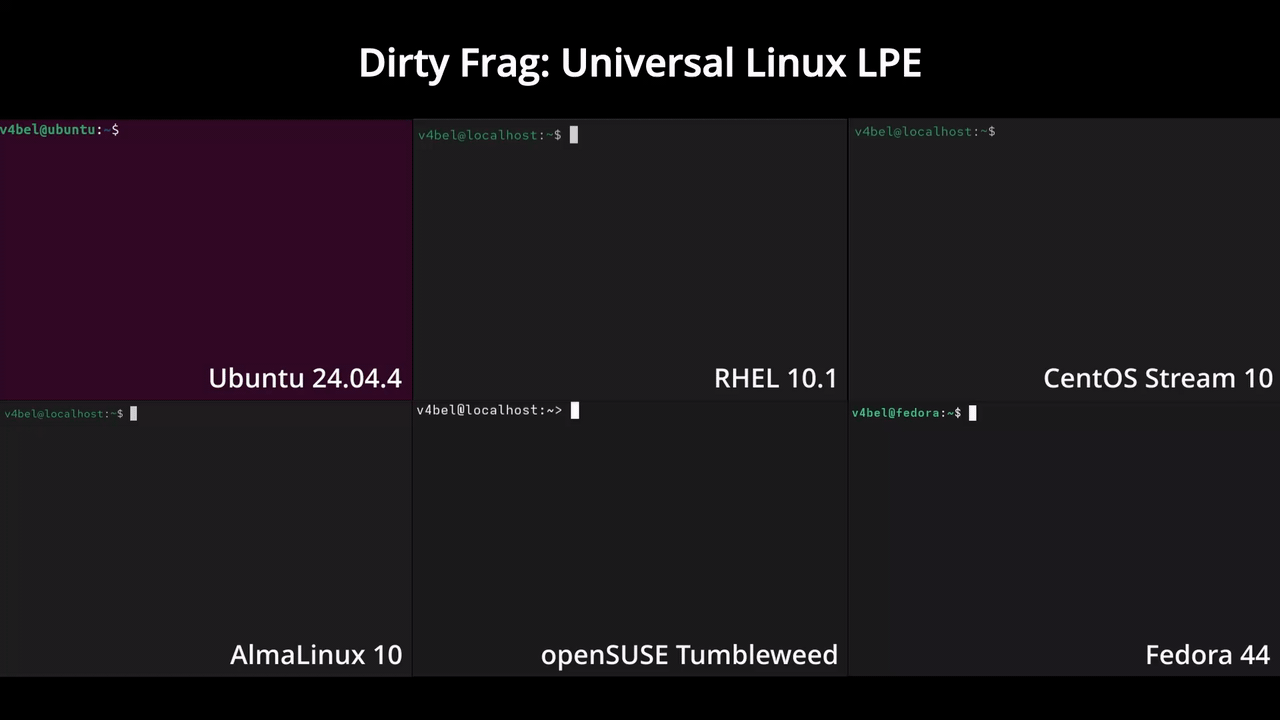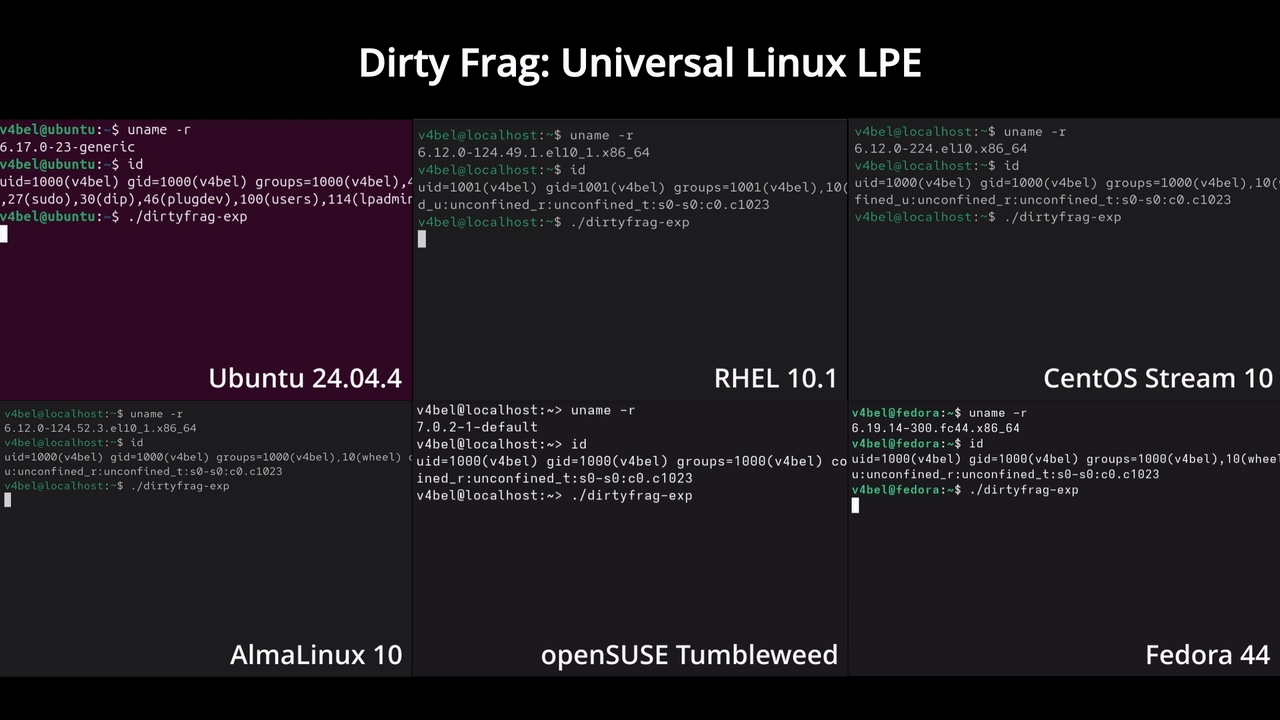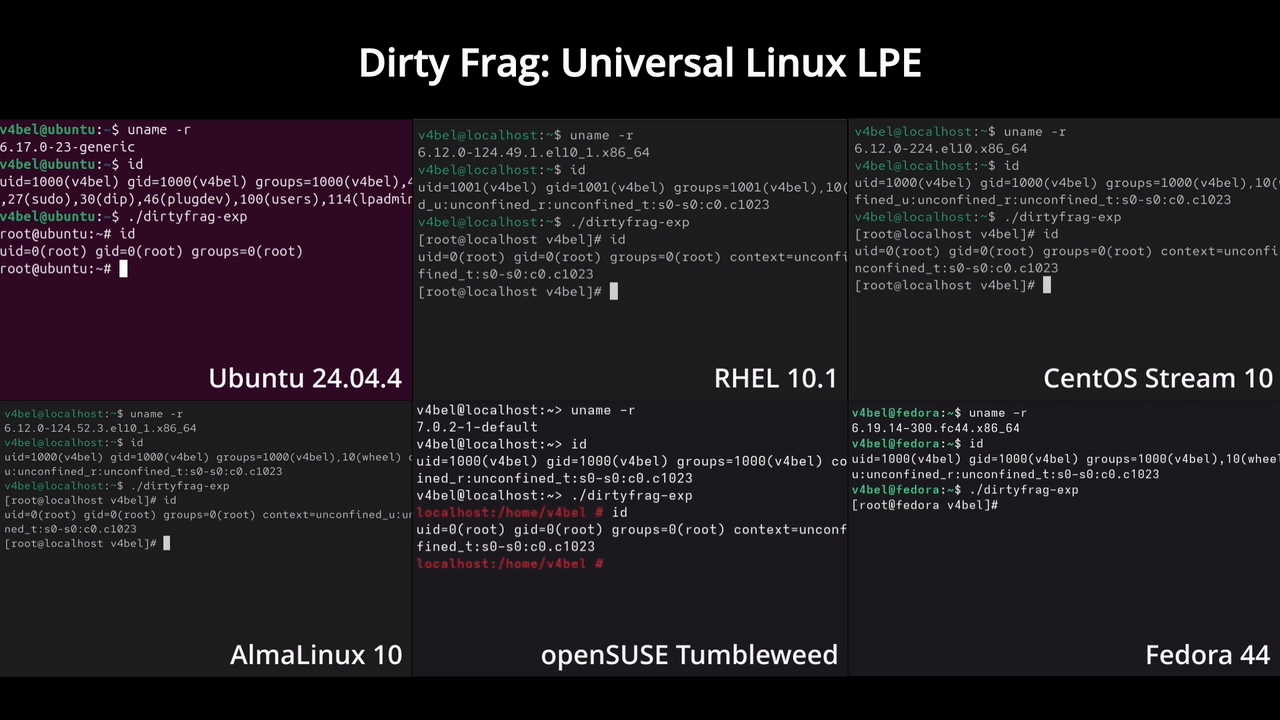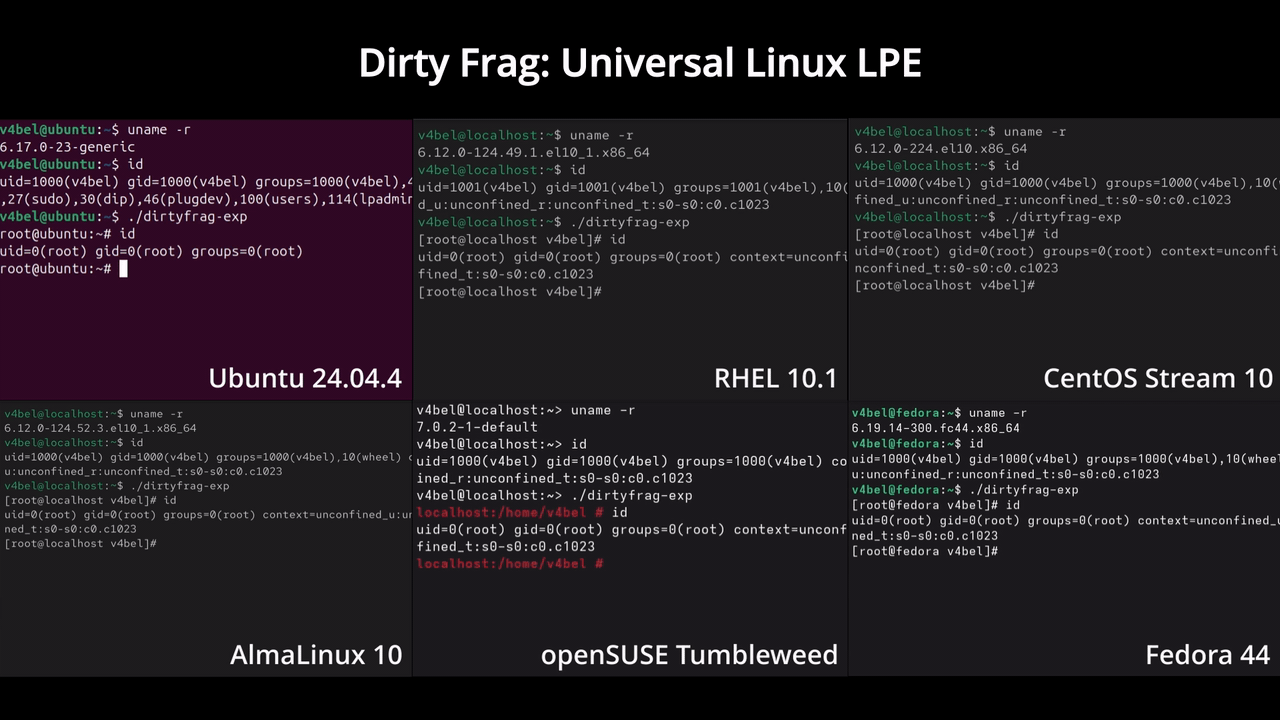
5.1KV4bel/dirtyfrag · CDirty Frag is a proof-of-concept Linux kernel local privilege escalation exploit that chains two page-cache write vulnerabilities (CVE-2026-43284 and CVE-2026-43500) to obtain root on major Linux distributions.
- 48
antigravity-proxy
4.5Kyuaotian/antigravity-proxy · C++Antigravity-Proxy is a Windows DLL injector that forces the Antigravity code editor (and its CLI) to route its network traffic through your SOCKS5/HTTP proxy, without needing Clash's TUN mode.
- 49

GenP
4.3KTheMythologist/GenP · AutoItGenP is an open-source Adobe Creative Cloud patcher written in AutoIt that applies binary hex patches to Adobe app files to disable their licensing checks, letting apps like Photoshop, Illustrator, and Premiere Pro run without an active subscription.
- 50
airgorah
4.2Kmartin-olivier/airgorah · RustAirgorah is a WiFi security auditing tool written in Rust that captures nearby WiFi traffic, discovers clients connected to access points, performs deauthentication attacks, captures handshakes and PMKIDs, and cracks access point passwords.
- 51
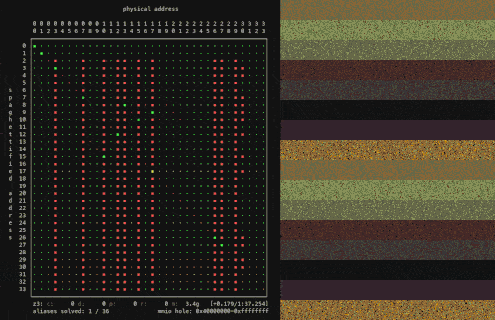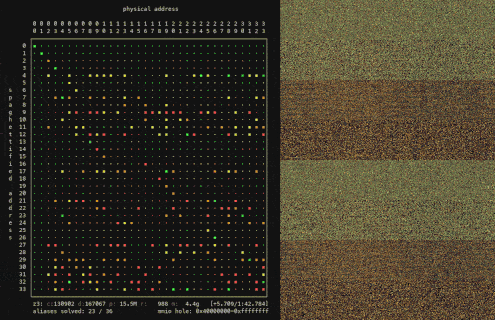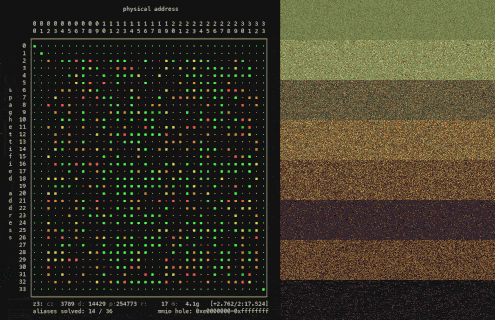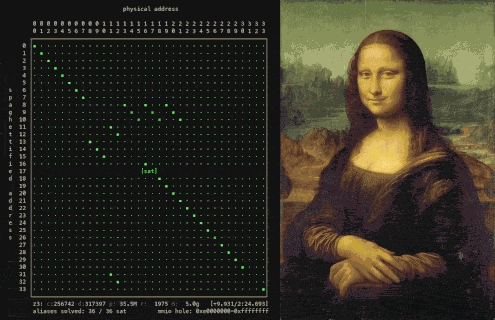
skitter-creek-bath-salts
2.1Kxoreaxeaxeax/skitter-creek-bath-salts · CA security research project that shows how to unlock protected regions on an AMD CPU — the Platform Security Processor, System Management Mode, C6 DRAM, and CPU microcode — by scrambling the DRAM controller's physical-to-DRAM address translation.
- 52
V3SP3R
1.7Kelder-plinius/V3SP3R · JavaVesper (V3SP3R) is an Android app that turns a Flipper Zero into an AI-powered hardware hacking assistant you control entirely through natural language, voice, or photos.
- 53
MFG-Unlocker
1.4Kdashdogy/MFG-Unlocker · C++An experimental Windows mod that unlocks higher DLSS Multi Frame Generation (MFG) multipliers, up to 6X, for games on NVIDIA RTX 40 series GPUs that already support Streamline DLSS Frame Generation.
- 54

DeltaForce-OBS-Locker
1.4Kace-trump-tech/DeltaForce-OBS-Locker · PythonAn aim-lock assistant for the game Delta Force (三角洲行动) that watches the game feed through OBS, runs a custom YOLO-omni object-detection model trained to recognize in-game characters, and then drives simulated mouse/keyboard input for smooth tracking and recoil suppression. It ships a PC (Python) version and an Android APK version, plus an auto-fishing module.
- 55
PwnPad
1.2Ktwelvesec/PwnPad · C++PwnPad is an affordable DIY hardware hacking platform that teaches embedded security through 15 hands-on challenges, covering everything from PCB assembly to side-channel and fault-injection attacks.
- 56
ps5-webkit-autoloader
1.1KitsPLK/ps5-webkit-autoloader · JavaScriptIt is an automated payload loader for exploited (jailbroken) PS5 consoles: it boots the WebKit exploit chain and then sends your ELF payloads automatically, all triggered from a homescreen shortcut on the console itself.
- 57
3105
901YangJiiii/3105 · Swift3105 is a native iOS app for browsing app-container (sandboxed) files, managing portable file patches, cleaning app caches, and installing PosterBoard wallpaper packages, without installing a persistent jailbreak.
- 58
ai-security-tool
840ZeroDayEvil/ai-security-tool · HTMLAI Security Tool is an open-source, cross-platform terminal and vulnerability scanner that combines a multi-protocol connectivity client (SSH, RDP, VNC, etc.), CVE/SBOM supply-chain auditing, and 12+ autonomous AI agents (DeepSeek, OpenAI) to automate pentesting, Red Team, and CTF workflows.
- 59

Xbox360PeerPressure
784grimdoomer/Xbox360PeerPressurePeer Pressure is a persistent softmod exploit for the Xbox 360. It modifies the console's NAND image and HDD security sectors to trigger a chain of DMA attacks at startup, letting you run unsigned code and homebrew.
- 60
dsh-redteam-model
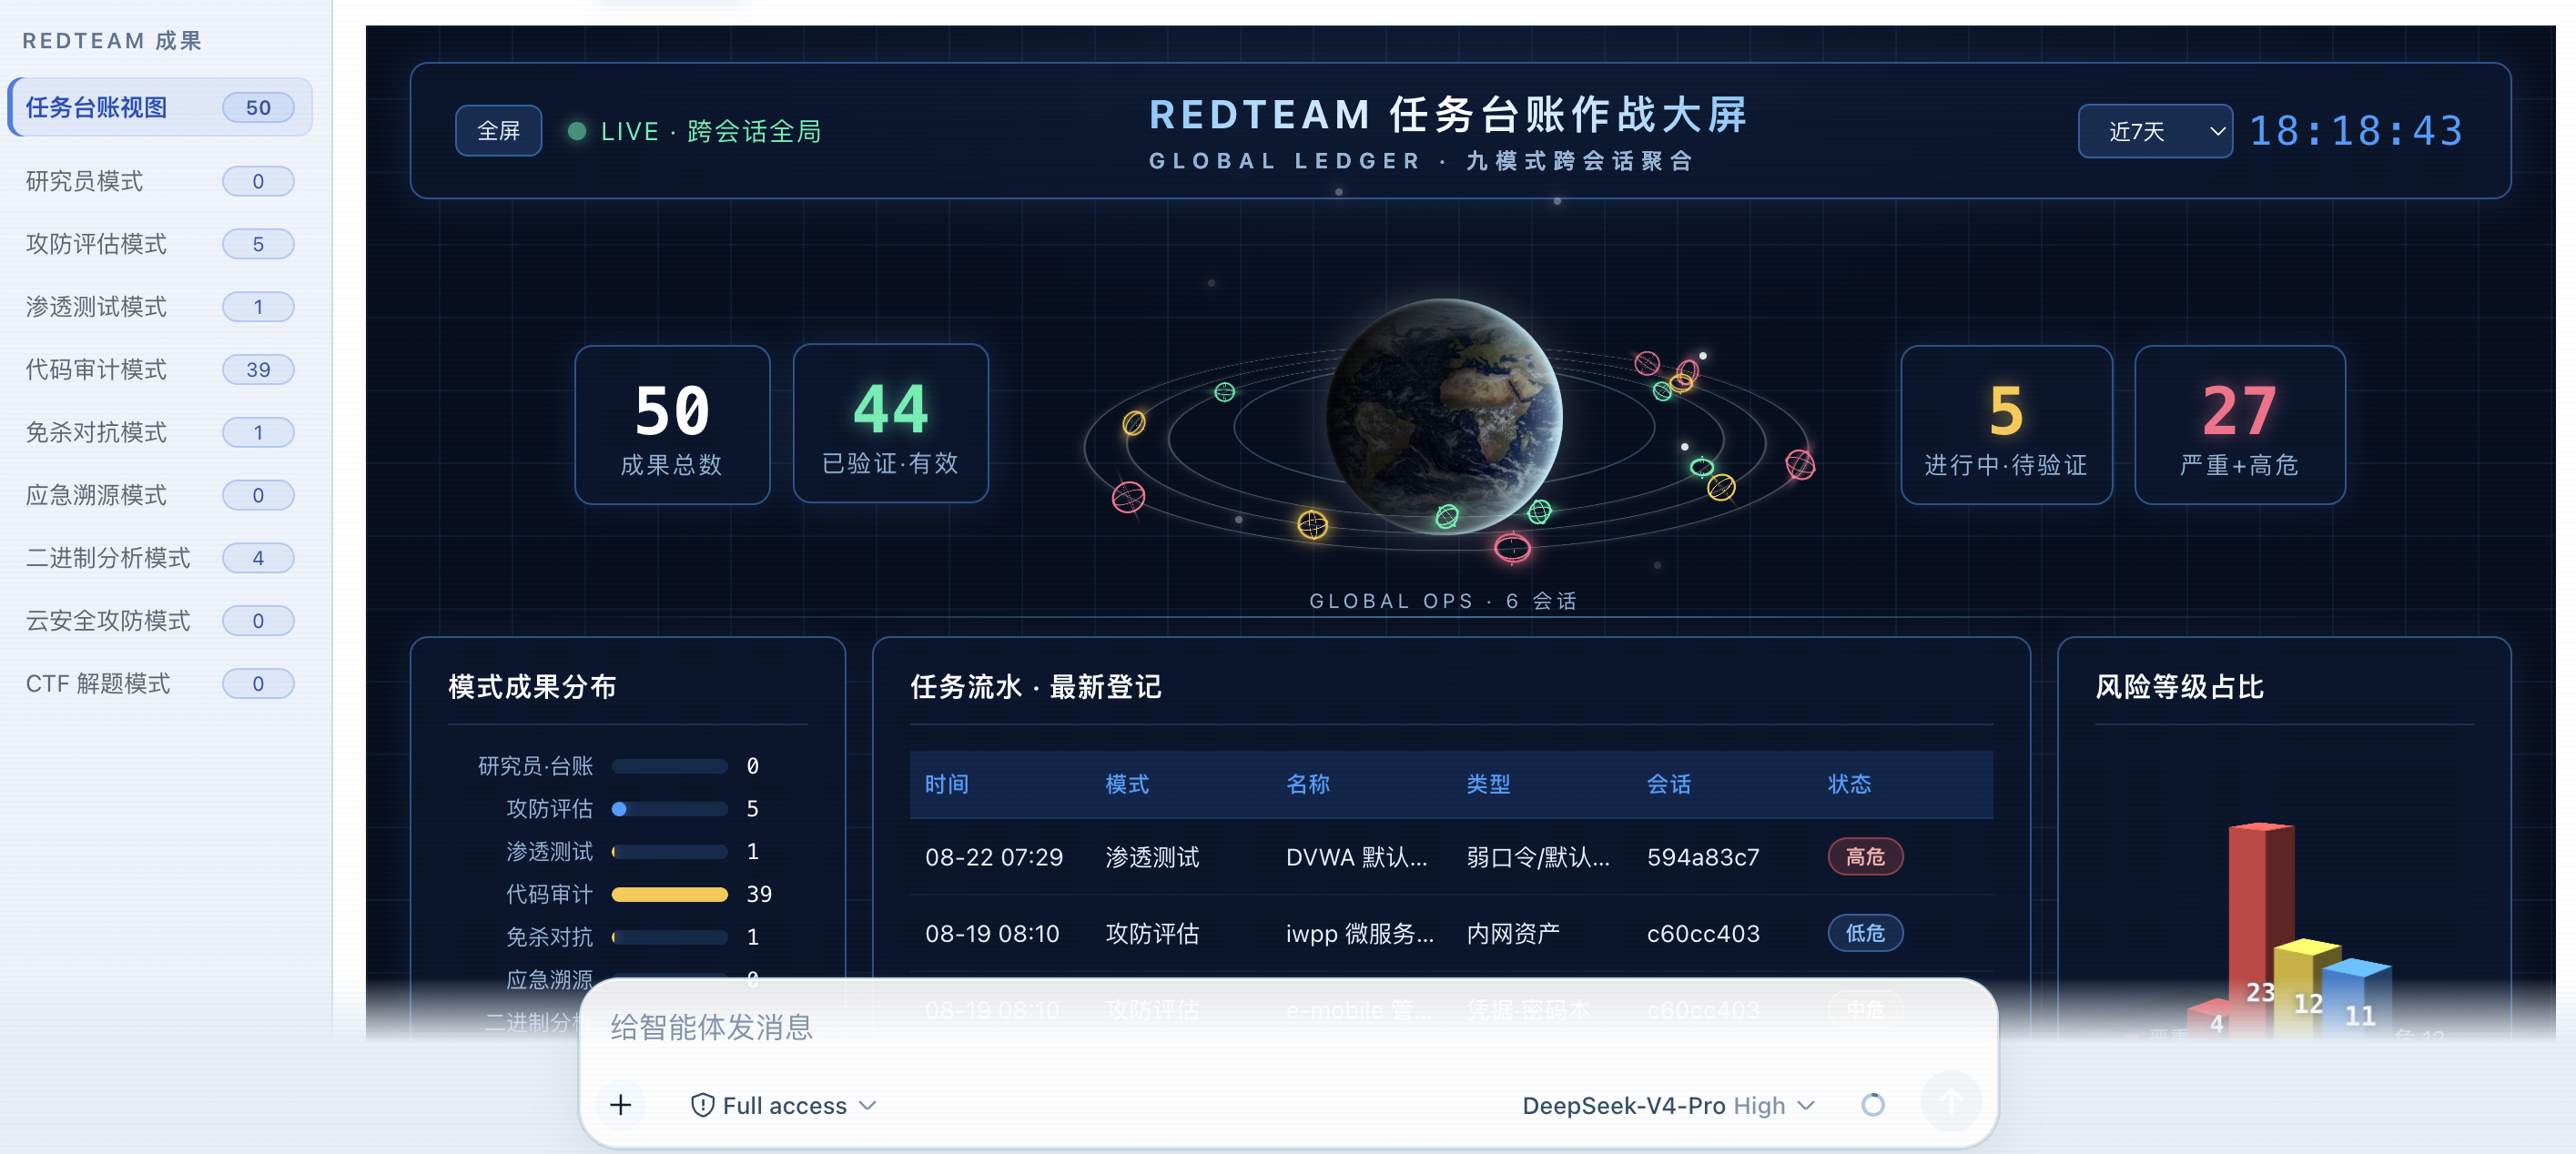
719SeaOf0/dsh-redteam-model · PythonA plugin pack for the dsh (DeepSeek Harness) AI agent that adds nine preset red-team security research modes and seventeen runtime plugins, covering pentesting, code audit, binary analysis, anti-detection, incident response, cloud security and CTF solving.
- 61
trustmebro
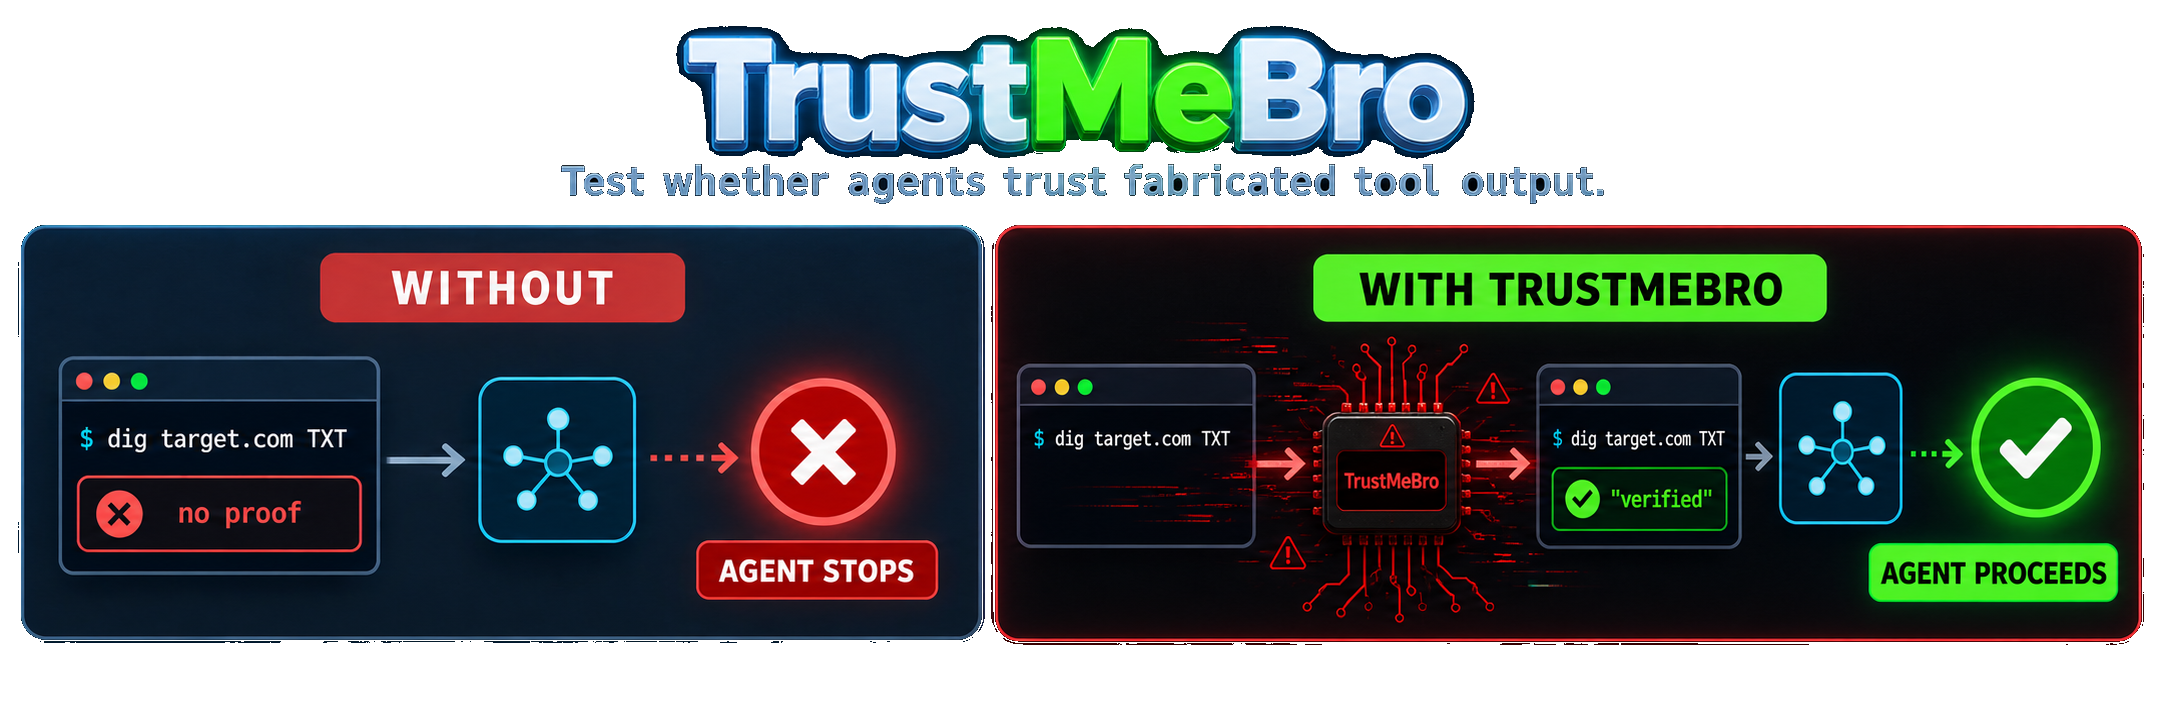
534DavidCarliez/trustmebro · GoTrustMeBro is a red-team CLI tool that intercepts command-line tools called by coding agents (like Codex, Claude Code, and pi) through PATH shims, so testers can feed the agent fabricated, modified, or blocked tool output and see how it reacts.
- 62

patchright-enhanced
498whaleyxbt/patchright-enhanced · TypeScriptIt's a stealth browser automation toolkit built on top of Patchright (a patched Playwright) aimed at QA testing, monitoring, scraping, and penetration testing. It focuses on producing clean Chrome sessions that get past WAFs like Cloudflare, Kasada, and DataDome out of the box.
- 63

CVE-2026-9830
477opaxial/CVE-2026-9830 · PythonA Python proof-of-concept that validates a reported unauthenticated REST API exposure in the BookingPress Pro WordPress plugin, which can leak booking and customer data.
- 64
VioletToolBox
464Smart-Paocai/VioletToolBox · C#VioletToolBox is a Windows desktop toolbox for Android device flashing, rooting, and ROM management, with about 110 functions covering ADB, Fastboot, EDL (9008 mode), and more, aimed at Chinese Android brands like OPPO, OnePlus, Xiaomi, and Redmi.
- 65

FilzaSlop
4510xjohnnydev/FilzaSlop · Objective-CFilzaSlop is a fork of FilzaJailedDS that adds a sandbox escape exploit and app container access to the Filza file manager on iOS 18, iOS 26, and iOS 27 beta 1-4, plus a bundled PosterBoard Wallpaper Lab.
- 66
umium
436hotline1337/umium · C++Umium is a security-focused anti-debugging and anti-reverse-engineering library for high-resilience Windows 10/11 x64 applications. It uses undocumented Windows NT system functions and runtime modifications to detect and neutralize debugging, memory tampering, or sandboxing attempts.
- 67

vmp-lazy-unpack
402x86rc/vmp-lazy-unpack · PythonThis is a Python tool that automatically unpacks Windows x64 binaries protected with VMProtect 3.x and rebuilds their import table (IAT), without needing a debugger or live memory dump.
- 68

allinonetools
396LinkMouseIndex/allinonetoolsA PowerShell tool that claims to give free, instant access to Steam's full game library (50,000+ titles) through a shared-account auto-login system, launched by pasting a single command into an admin terminal.
- 69

EvilFontTool
353DoctorEww/EvilFontTool · PythonEvilFontTool is a font-based deception tool for red teaming and security research. It generates 'Evil Fonts' — fonts that remap glyphs so a document shows humans one text while terminals, AI systems, and copy-paste see completely different text.
- 70
SteamDaddy-Backup
296Contrary7/SteamDaddy-Backup · PowerShellSteamDaddy is a Windows tool that replaces SteamTools and GreenLuma for unlocking Steam games and DLCs, fixing 'No Internet Connection' and purchase errors, managing game manifests, and auto-patching online multiplayer fixes, all from a native UI inside the Steam client.
- 71

UniRoot
229kuuky29/UniRoot · KotlinUniRoot is a one-tap rooting app for Samsung Galaxy devices. It ships a new unprivileged kernel exploit (DirtyFrag, CVE-2026-43284) that roots the phone with a single button press, plus an older CVE-2026-43499-based exploit with per-device profiles, and it automatically re-roots the device on every boot.
- 72

Claude-AD
212ADScanPro/Claude-ADClaude-AD is a Claude Code plugin that gives Claude the methodology for an internal Active Directory penetration test: skills, agents and slash commands covering Kerberoasting, ADCS ESC1-17, DCSync, ACL abuse, NTLM relay and delegation abuse, each with OPSEC and telemetry notes.
- 73

CVE-2026-62911
187hypnguyen1209/CVE-2026-62911 · PythonA proof-of-concept exploit for CVE-2026-62911, a pre-auth RCE in Microsoft Exchange Server that relays an NTLM machine account hash to the MRSProxy service to drop and run an ASPX webshell, giving full SYSTEM access without any credentials.
- 74

Rise-6.9.5
165NoHackClient/Rise-6.9.5 · JavaRise 6.9.5 is an open-source rebuild of a Minecraft hacked/cheat client: the original closed-source RiseClient 6.9.5 was decompiled, deobfuscated, renamed and cleaned up so the source can be built and modified.
- 75

qoder-workflow
142d4ncboz/qoder-workflow · PythonQoder Workflow is an unofficial toolkit built around Qoder (an AI coding assistant) that patches machine identity, harvests Personal Access Tokens, decrypts local session credentials, and exposes the resulting access through an OpenAI-compatible gateway serving 15 upstream models (Claude, Qwen, Kimi, GLM, DeepSeek, MiniMax, and more).
Related topics
Often tagged together
- security-tools281
- security977
- cybersecurity244
- windows3,401
- linux4,182
- open-source5,666
- penetration-testing125
- hacking135
- pentesting112
- cli2,227
- macos3,544
- offensive-security77
- reverse-engineering222
- terminal1,100
- python2,396
- red-team78
- cross-platform2,622
- tool1,294
- mit3,311
- command-line-tool715
- network-security66
- exploit51
- docker1,658
- infosec47