Topics / #binary-analysis
Binary-analysis projects on GitHub
Inspecting and reverse engineering compiled binaries.
As of , the most-starred Binary-analysis projects on GitHub are rea (322.1K stars), ghidra (91.1K stars) and ImHex (55.4K stars). GitHub.Locker tracks 48 Binary-analysis repositories with 848.3K stars combined. The fastest-growing on October 18 was rea, with +15.4K stars in a day.
Hot right now
Most stars gained in a day · Oct 18
rea
morluto/rea · ★ 322.1KREA lets AI coding agents reverse engineer apps, binaries, websites, and other software through a single MCP server and CLI, returning findings with the evidence behind them so an agent can explain a feature or rebuild it.
 +695
ghidra
NationalSecurityAgency/ghidra · ★ 91.1KGhidra is a software reverse engineering (SRE) framework created and maintained by the NSA's Research Directorate, used to disassemble, decompile, graph, and analyze compiled code.
 +551
EQAI
AhmadHassan-BTed/EQAI · ★ 742This is a reverse-engineering pipeline that transplants the original EverQuest Online Adventures (EQOA) character geometry into the EverQuest Online Adventures: Frontiers PS2 client, fixing engine-level bugs like VU1 shader errors, Emotion Engine memory overflows, and CDVD hardware faults so the original models load correctly.
 +332
awesome-decomp-games
SubmitGame/awesome-decomp-games · ★ 1.8KA curated, automatically updated list of games that have been decompiled, recompiled, or otherwise reverse-engineered, covering decomps, static recomps, source ports, engine remakes, and browser ports, with each entry rated for quality.
The all-time top
48 projects · by stars
- 322.1K
#1 · morluto/rea
rea
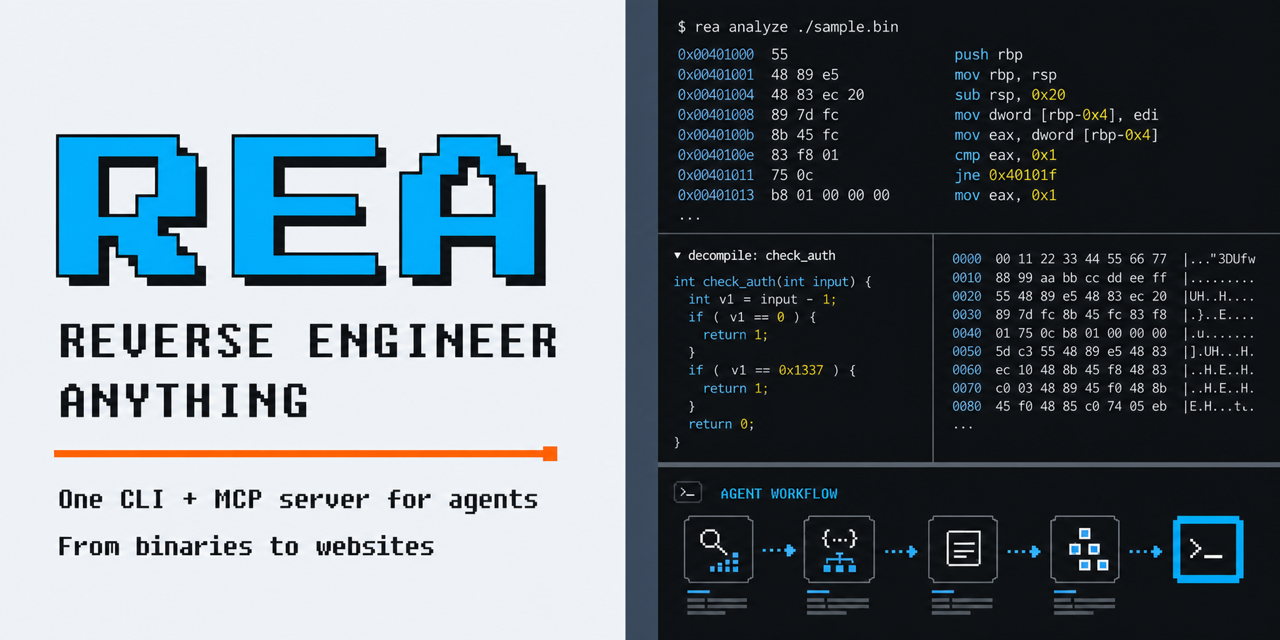
REA lets AI coding agents reverse engineer apps, binaries, websites, and other software through a single MCP server and CLI, returning findings with the evidence behind them so an agent can explain a feature or rebuild it.
- 91.1K#2 · NationalSecurityAgency/ghidra
ghidra
Ghidra is a software reverse engineering (SRE) framework created and maintained by the NSA's Research Directorate, used to disassemble, decompile, graph, and analyze compiled code.
- 55.4K
 #3 · WerWolv/ImHex
ImHex
ImHex is a hex editor built for reverse engineers, programmers, and anyone analyzing binary data, with a custom pattern language for parsing and highlighting file structures.
- 4
jadx
51.1Kskylot/jadx · Javajadx is a Dex to Java decompiler: command line and GUI tools that produce Java source code from Android Dex and Apk files.
- 5

x64dbg
49.9Kx64dbg/x64dbg · C++x64dbg is an open-source user-mode debugger for Windows, built specifically for reverse engineering and malware analysis.
- 6

reverse-skill
42.6Kzhaoxuya520/reverse-skill · PowerShellIt is a skill pack that routes AI coding agents to the right reverse engineering, penetration testing, and security research methodology for a given task (APK, binary, JS, CTF, malware, etc.), checks which tools are installed, and runs a repeatable workflow instead of letting the agent guess commands.
- 7
dnSpy
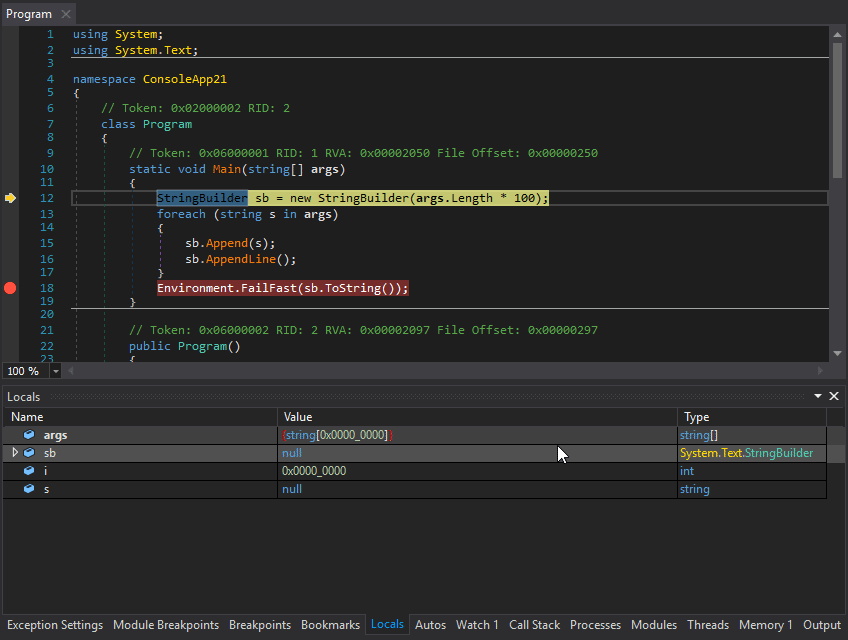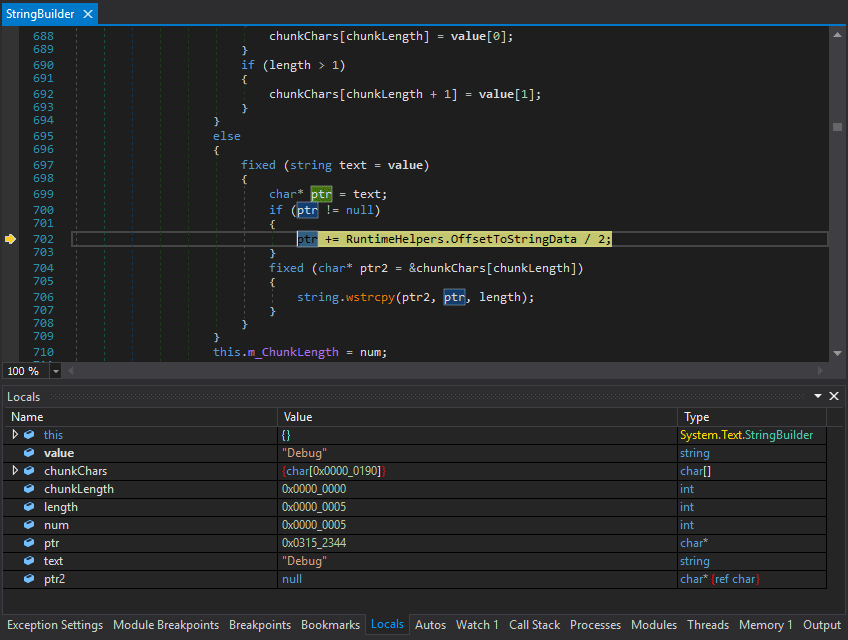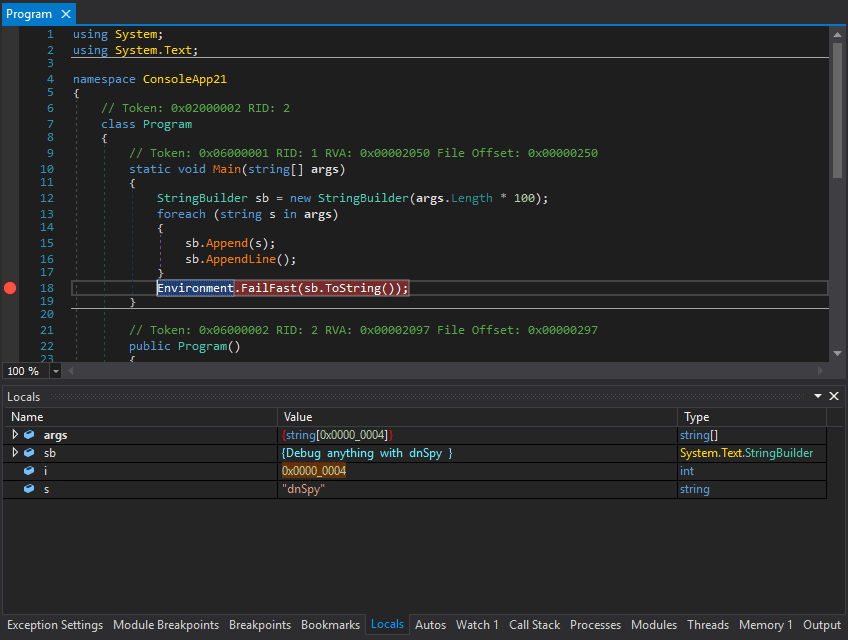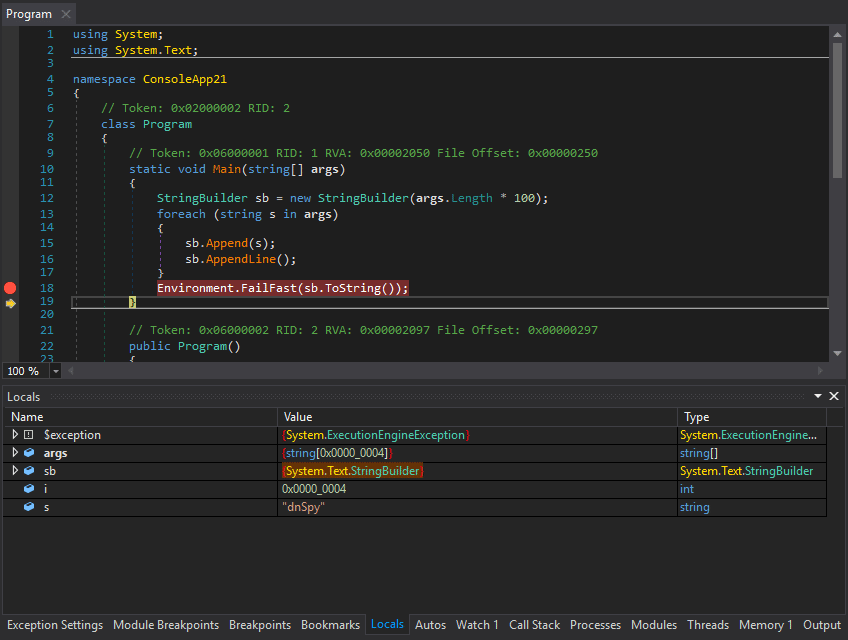
29.7KdnSpy/dnSpy · C#dnSpy is a Windows debugger and assembly editor for .NET and Unity programs - it lets you set breakpoints, step through code, and even edit methods and metadata without having the original source code.
- 8

Apktool
26.1KiBotPeaches/Apktool · JavaApktool is a command-line tool for reverse engineering third-party, closed, binary Android apps. It decodes an APK's resources to nearly original form and rebuilds the app after you make changes.
- 9
radare2
25.1Kradareorg/radare2 · Cr2 (radare2) is a libre reverse engineering framework for Unix-like systems: a set of libraries, tools and plugins for analyzing, disassembling, emulating, debugging and modifying binaries.
- 10
binwalk
14.5KReFirmLabs/binwalk · RustBinwalk is a firmware analysis tool that can identify, and optionally extract, files and data that have been embedded inside other files.
- 11
ida-pro-mcp
13Kmrexodia/ida-pro-mcp · PythonIt is an MCP server that bridges IDA Pro with AI language models, letting coding agents like Claude, Codex or Cursor help you reverse engineer binaries ('vibe reversing').
- 12
Detect-It-Easy
11.8Khorsicq/Detect-It-Easy · JavaScriptDetect It Easy (DiE) is a cross-platform tool that identifies file types and inspects executables (PE, ELF, Mach-O) for malware analysts, reverse engineers, and cybersecurity researchers, combining signature-based detection with a deep heuristic engine.
- 13
pics
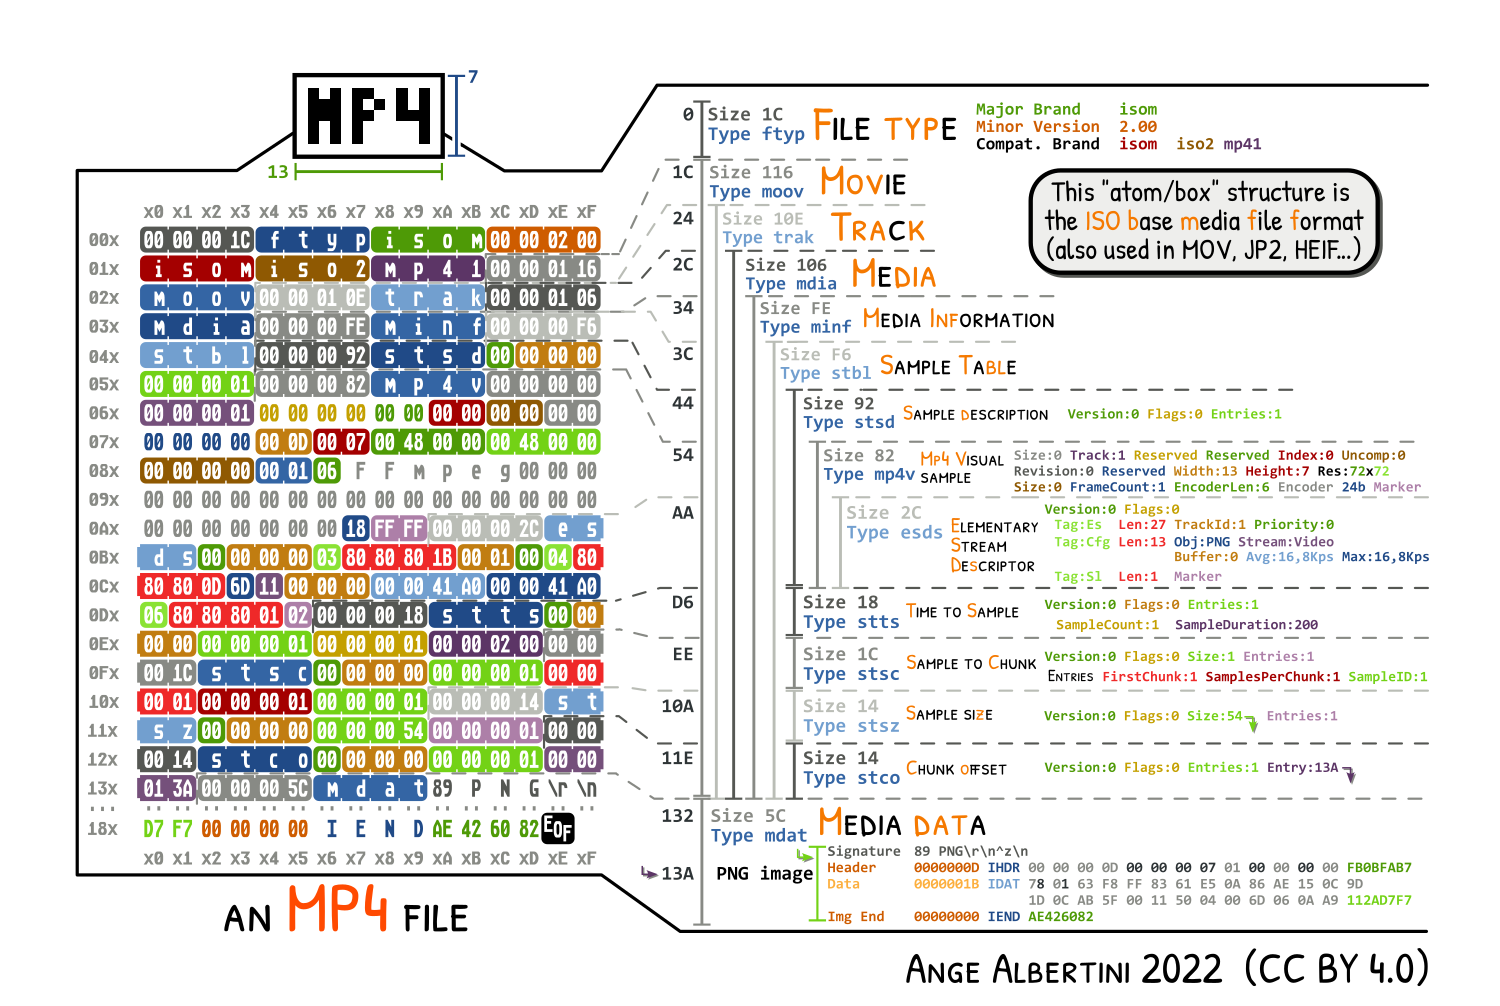
11.5Kcorkami/pics · AssemblyA gallery of visual dissections of binary file formats: annotated posters, tracings and outlines that map how binary files are structured inside.
- 14
GhidraMCP
11.4KLaurieWired/GhidraMCP · JavaGhidraMCP is a Model Context Protocol server that lets LLMs autonomously reverse engineer applications by exposing Ghidra's core functionality (decompiling, renaming, listing imports/exports) to any MCP client.
- 15

pwndbg
11.1Kpwndbg/pwndbg · PythonA plug-in for GDB and LLDB that makes debugging far less painful for low-level developers, hardware hackers, reverse-engineers and exploit developers — it adds the utilities vanilla debuggers are missing.
- 16
reverse-engineering
10.6KwtsxDev/reverse-engineeringA curated list of reverse engineering resources: books, courses, practice grounds, and a big toolbox section spanning hex editors, disassemblers, debuggers, and dynamic analysis tools.
- 17
fq
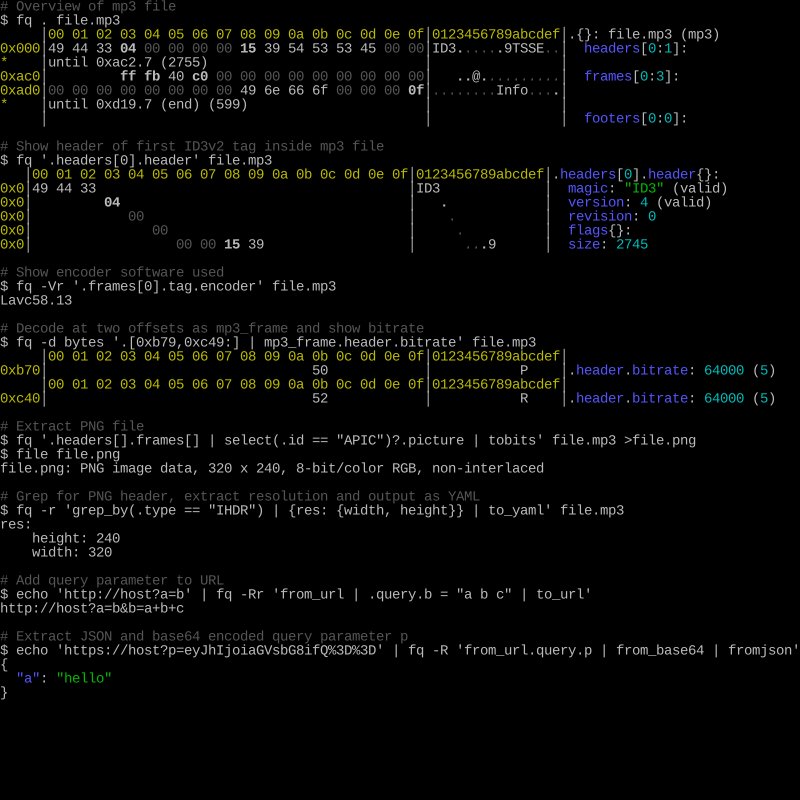
10.6Kwader/fq · Gofq is a command-line tool, language and collection of decoders for working with binary formats - often described as jq for binary data. You can dump a file's structure, run jq-style queries against it and explore results in an interactive REPL.
- 18

hexyl
10.3Ksharkdp/hexyl · Rusthexyl is a command-line hex viewer: it prints the raw bytes of a file in your terminal, with colors distinguishing NULL bytes, printable ASCII, whitespace, other ASCII and non-ASCII bytes.
- 19

ghidra-mcp
5.8Kbethington/ghidra-mcp · JavaThis is an MCP (Model Context Protocol) server that bridges Ghidra's reverse engineering engine with AI tools like Claude and Cursor, giving AI agents 245 tools to analyze, rename, document, and even emulate functions in binaries.
- 20

GenP
4.3KTheMythologist/GenP · AutoItGenP is an open-source Adobe Creative Cloud patcher written in AutoIt that applies binary hex patches to Adobe app files to disable their licensing checks, letting apps like Photoshop, Illustrator, and Premiere Pro run without an active subscription.
- 21

copy-fail-CVE-2026-31431
4.1Ktheori-io/copy-fail-CVE-2026-31431 · PythonThis repository is a technical writeup and proof-of-concept for CVE-2026-31431, a 9-year-old Linux kernel local privilege escalation (LPE) vulnerability found by Theori's AI vulnerability research tool, Xint Code.
- 22

raptor
3.9Kgadievron/raptor · PythonRAPTOR turns a Claude Code session into an offensive/defensive security agent: Claude.md rules, sub-agents and skills orchestrate tools like radare2, Frida, Z3 and CodeQL for binary reverse-engineering, exploit-feasibility research, and software supply-chain (SCA) analysis.
- 23

d2r-mobile
3.8Kjhaizhou-ops/d2r-mobile · CD2R Mobile is an open-source iOS compatibility layer that lets you run your own Switch copy of Diablo II: Resurrected (with the Reign of the Warlock expansion) natively on iPhone and iPad, with full touch controls and 60 fps.
- 24

PS2Recomp
3.6Kran-j/PS2Recomp · C++PS2Recomp statically recompiles PlayStation 2 ELF binaries into C++ source code and ships a runtime to execute that generated code, letting you build native PC ports of PS2 games.
- 25

Cpp2IL
3KSamboyCoding/Cpp2IL · C#Cpp2IL is a work-in-progress tool that reverses Unity's IL2CPP build process back into the original managed DLLs, letting you decompile IL2CPP Unity games into readable C#/CIL.
- 26
x64dbg-mcp-server
2.5Kduty1g/x64dbg-mcp-server · Zigx64dbg-MCP Server is a native plugin for the x64dbg debugger that exposes its full functionality over HTTP via the Model Context Protocol (MCP), letting any MCP-compatible AI assistant programmatically set breakpoints, step through code, read memory, dump registers, and more.
- 27
ASC
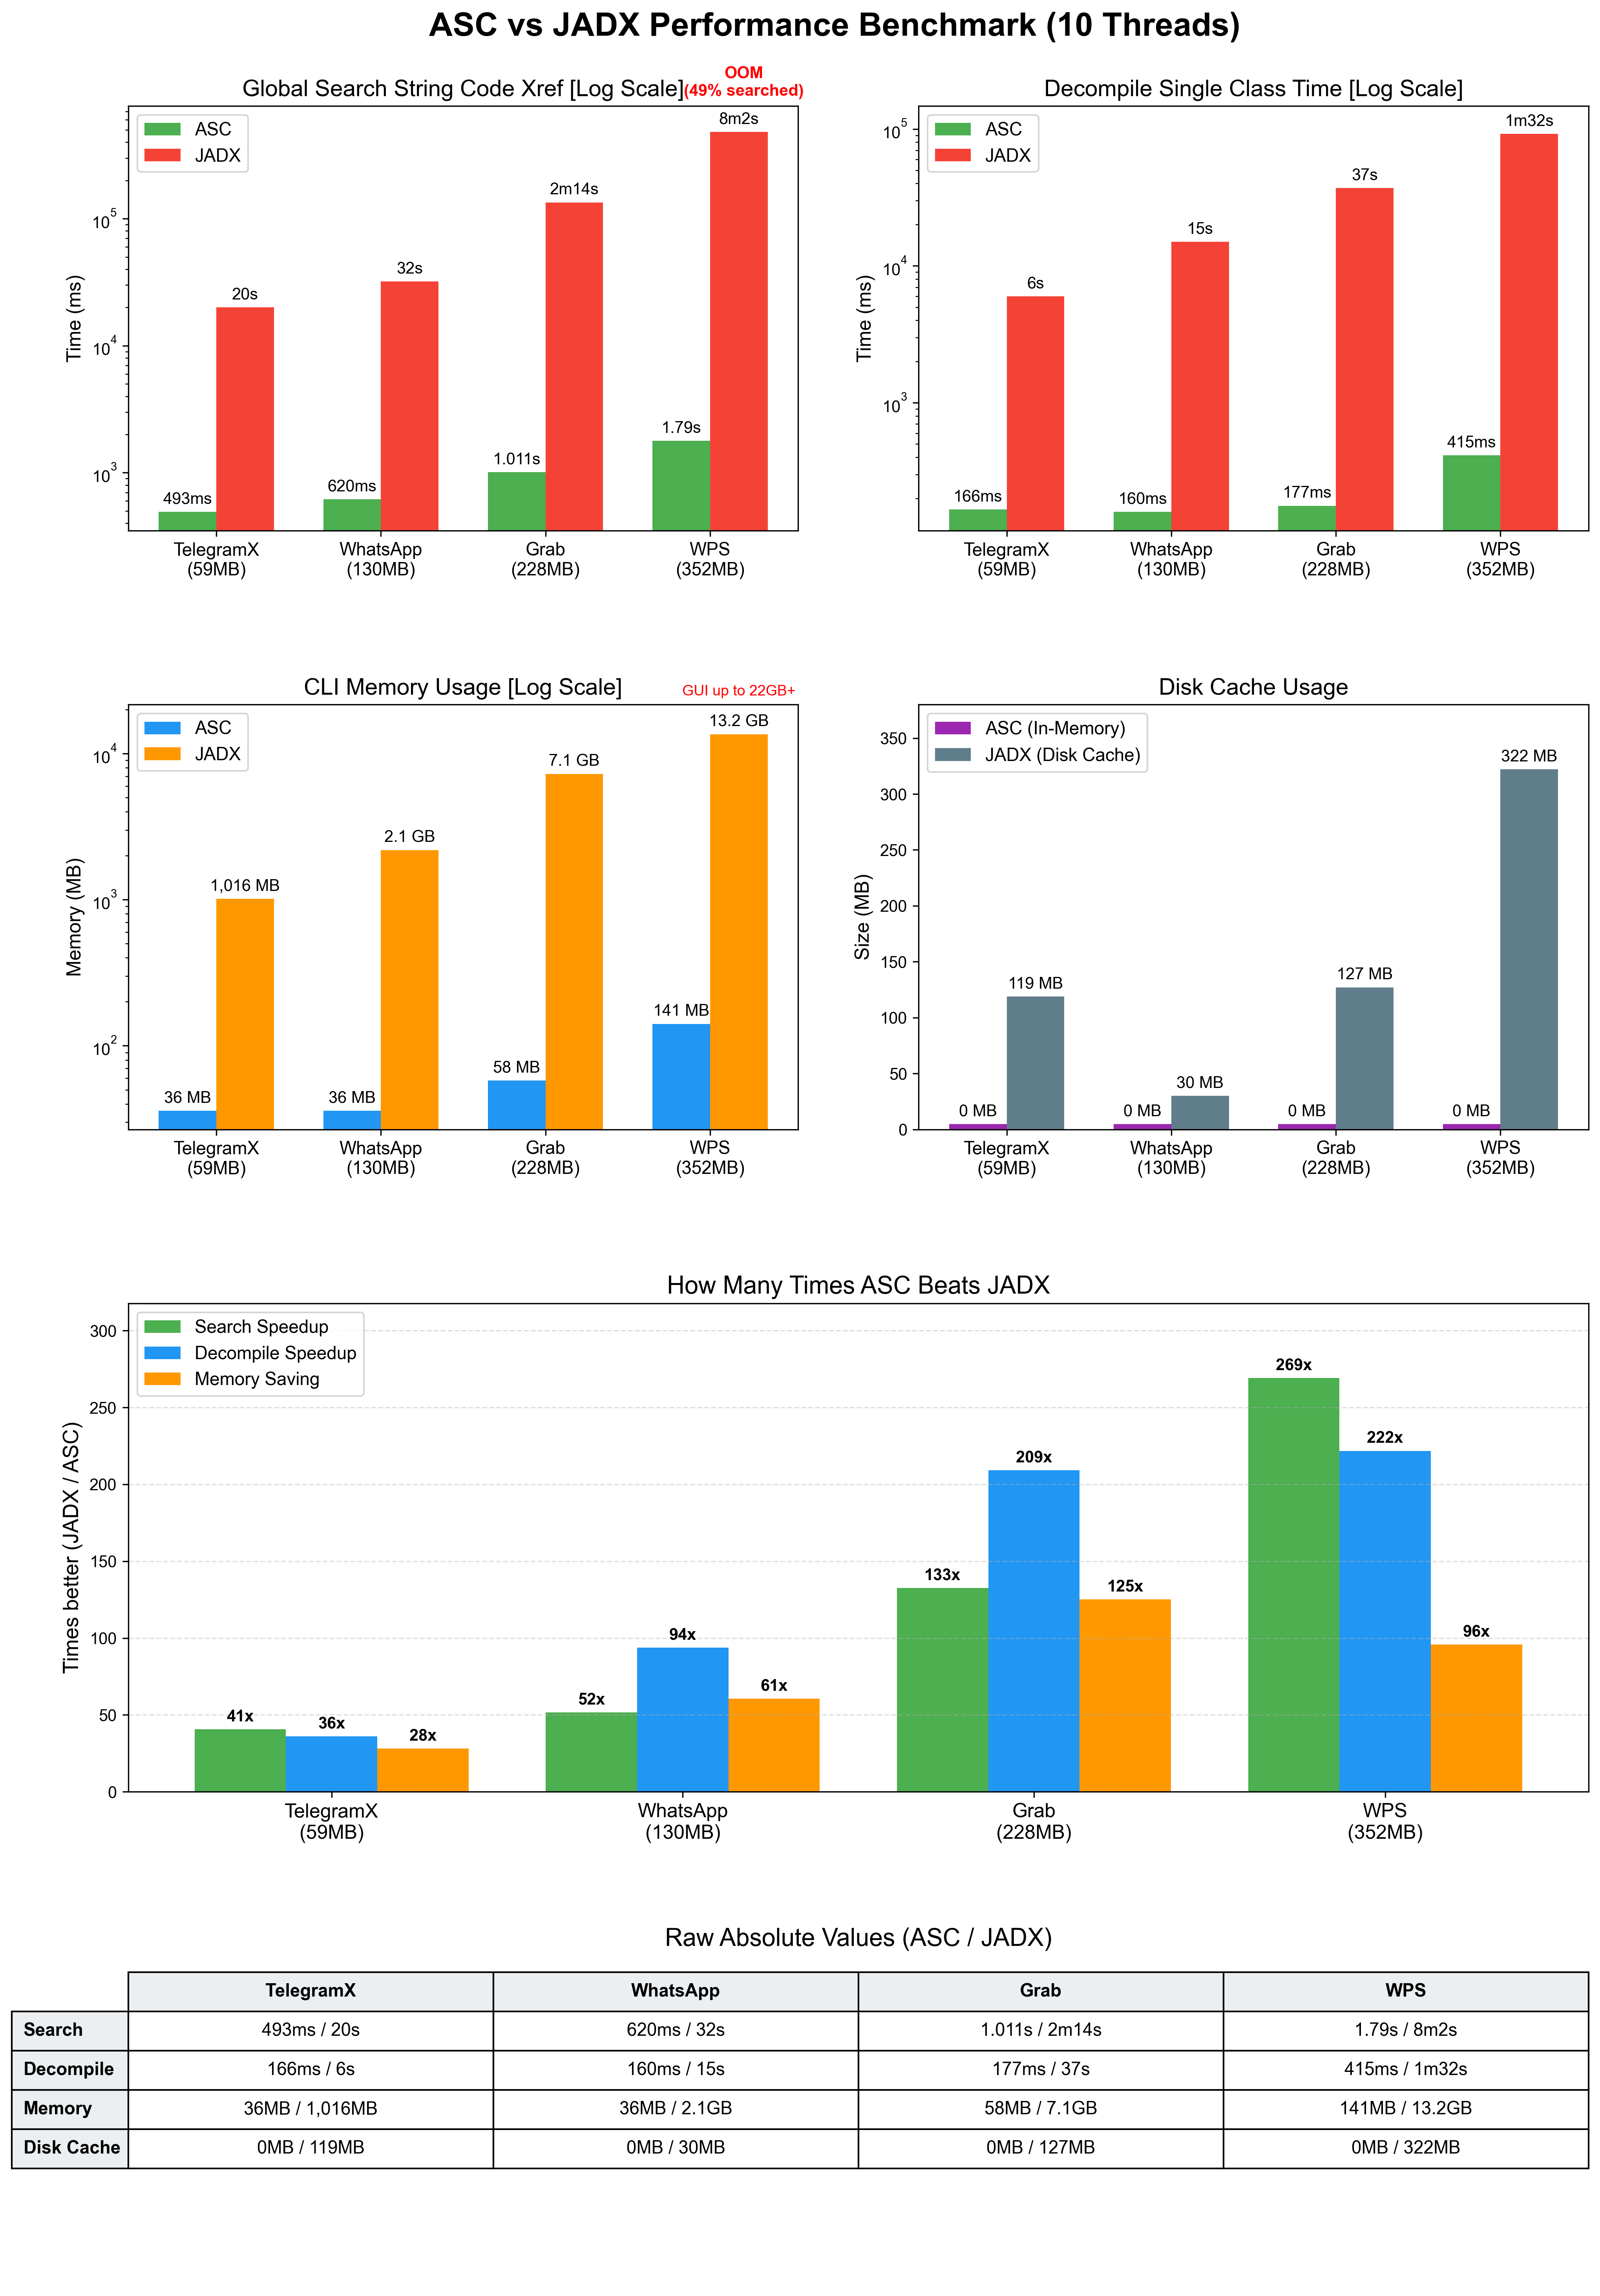
2.5KMG1937/ASC · PythonDroid ASC is a super FAST, lightweight Android decompiler built for AI agents and mobile researchers: instead of pre-indexing an APK, it extracts and decompiles code on demand in milliseconds.
- 28

ghostlock-app
2.1KYuKongA/ghostlock-app · KotlinGhostLock is a one-tap Android app that runs the CVE-2026-43499 kernel exploit to grant uid 0 (root) on a matching vulnerable kernel, optionally loading a KernelSU-style module afterward.
- 29
awesome-decomp-games
1.8KSubmitGame/awesome-decomp-games · PythonA curated, automatically updated list of games that have been decompiled, recompiled, or otherwise reverse-engineered, covering decomps, static recomps, source ports, engine remakes, and browser ports, with each entry rated for quality.
- 30
Seep-Reverse-Lab
1.7Kangusdevgo/Seep-Reverse-Lab · LuaSeep Reverse Lab is an agent-native reverse engineering and security-audit workbench that lets an AI coding agent autonomously run Radare2, JADX, Apktool and Frida to triage binaries, decompile APKs, and determine whether an app's feature gates are enforced locally or verified by a server (a CWE-602 authorization audit).
- 31

reverify
1.3K2akouwu/reverify · PythonReverify is a tool that stops AI agents from hallucinating facts by making a deterministic toolkit verify every claim the model makes against ground truth, with reverse engineering as the main proving ground.
- 32

Petari
1.3KSMGCommunity/Petari · C++This is an open-source, work-in-progress decompilation of Super Mario Galaxy 1, rebuilding the game's original C++ source code by matching it against the compiled binary.
- 33
awesome-reverse-engineering
832morluto/awesome-reverse-engineeringA curated list of reverse-engineering tools and learning resources covering binaries, applications, firmware, file formats, and protocols, organized by the task you need to do rather than alphabetically.
- 34
eleven
753Zfinix/eleven · TypeScriptEleven is a reverse-engineering desktop app for macOS, Windows and Linux built around AI agents: you open a binary, Android APK, GPU kernel, shader or model, and any agent that speaks the Agent Client Protocol (ACP) reads the code, renames functions, leaves notes and proposes patches while you watch and approve each change.
- 35
Reverse-Engineer-anything
751NabilRFG12/Reverse-Engineer-anythingREA is an MCP server that connects your coding agent to reverse-engineering tools, so it can inspect native binaries, JavaScript/Electron apps, .NET assemblies, websites, and more, then explain how a feature works with cited evidence.
- 36
EQAI
742AhmadHassan-BTed/EQAI · PythonThis is a reverse-engineering pipeline that transplants the original EverQuest Online Adventures (EQOA) character geometry into the EverQuest Online Adventures: Frontiers PS2 client, fixing engine-level bugs like VU1 shader errors, Emotion Engine memory overflows, and CDVD hardware faults so the original models load correctly.
- 37
dsh-redteam-model
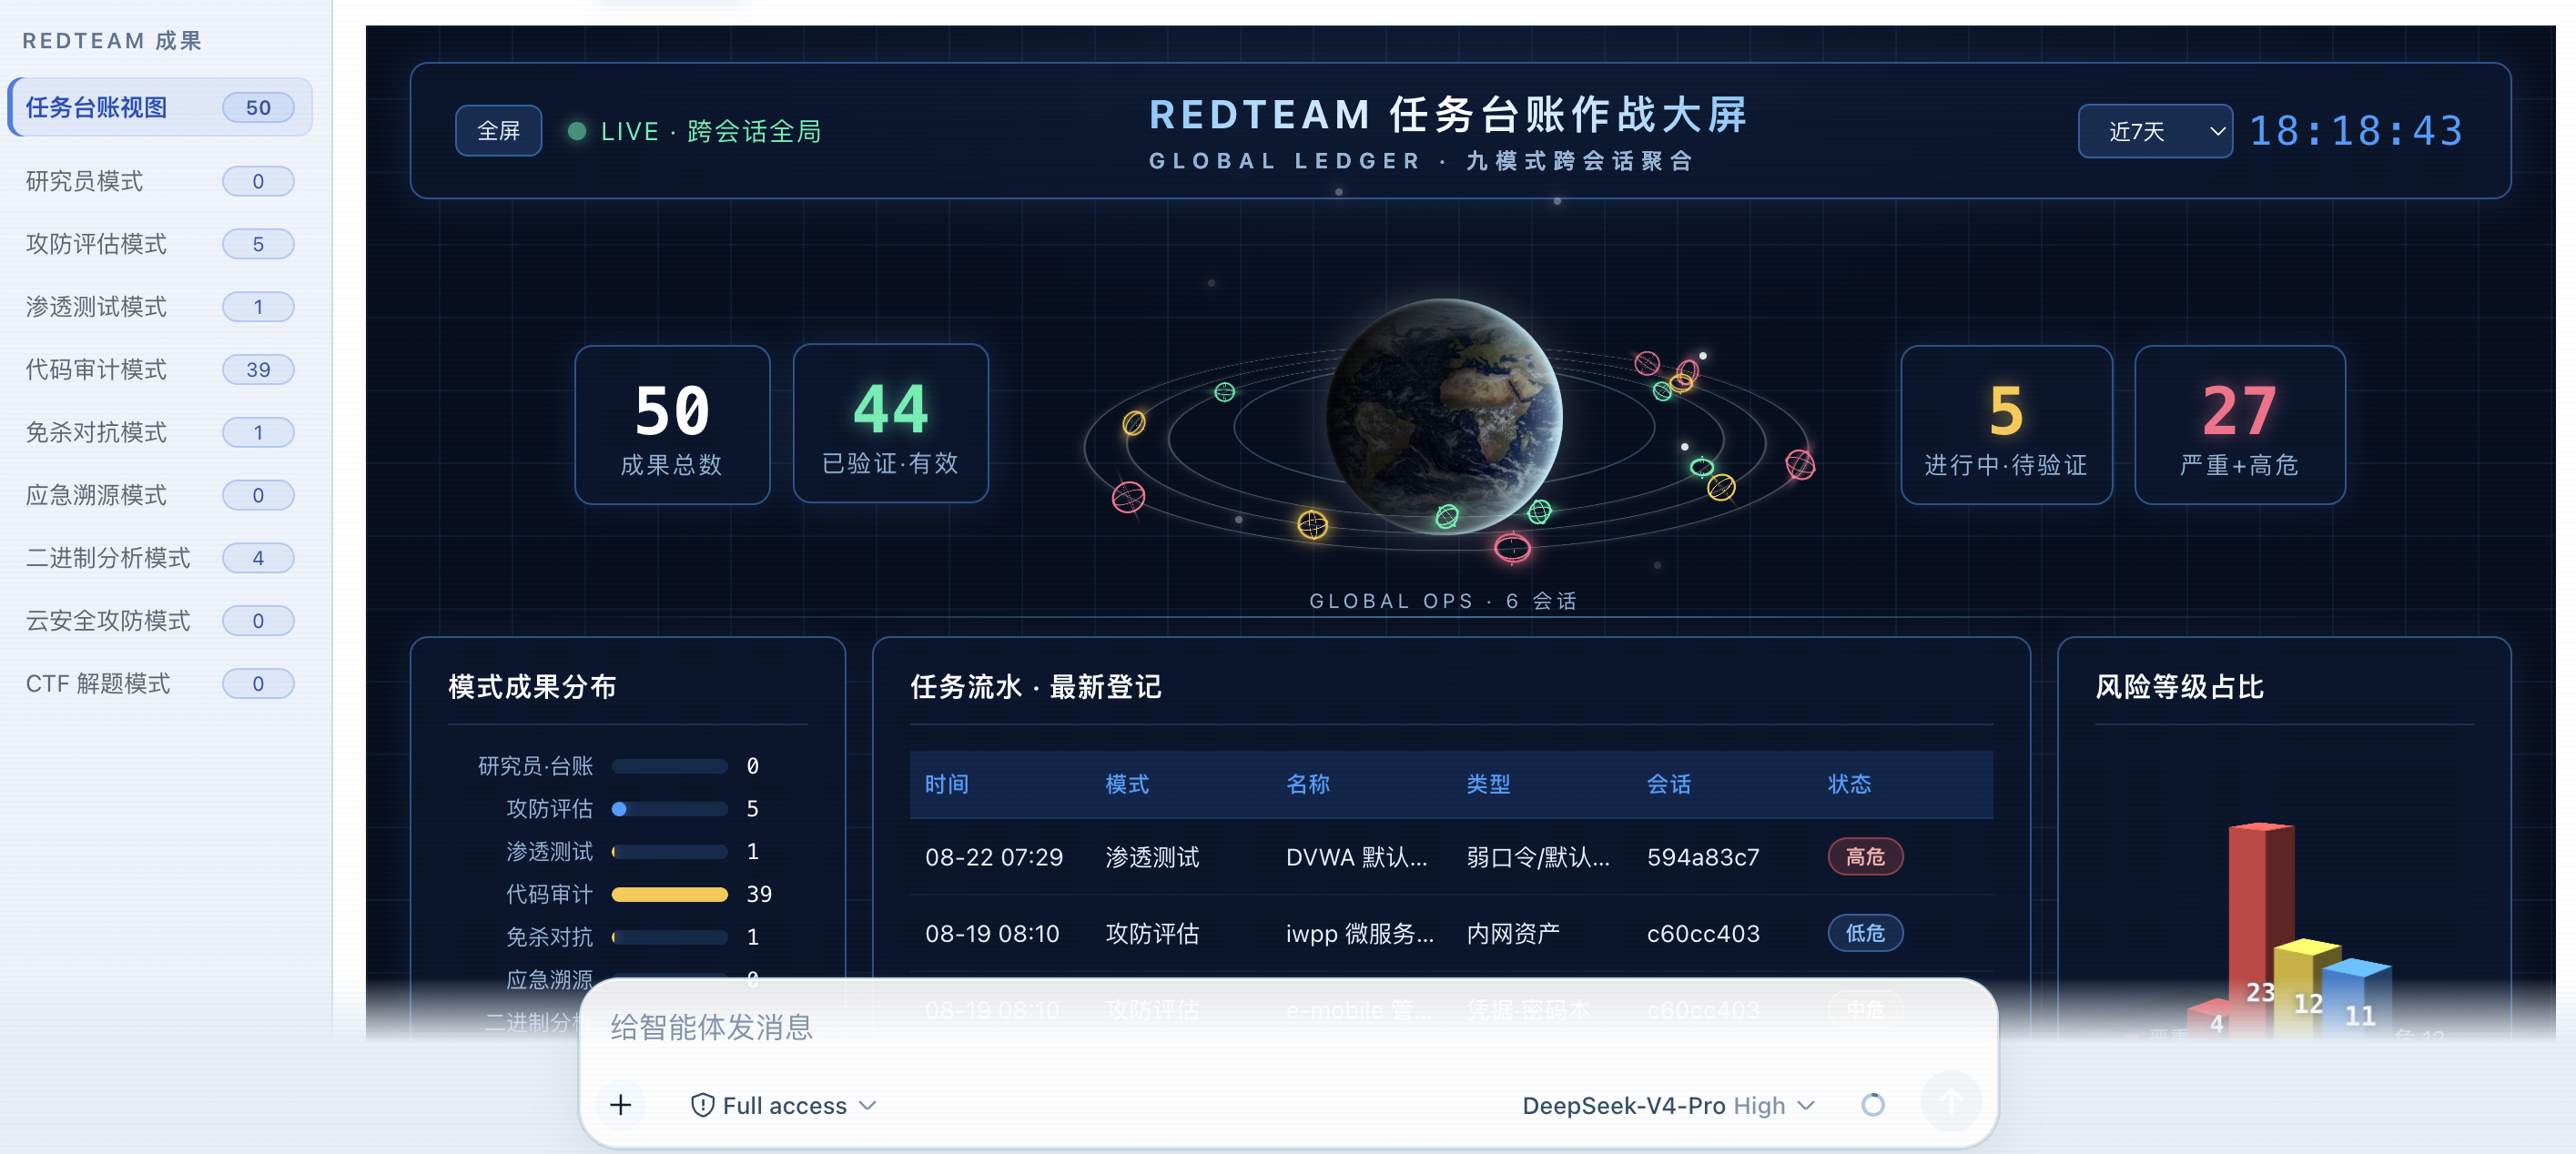
741SeaOf0/dsh-redteam-model · PythonA plugin pack for the dsh (DeepSeek Harness) AI agent that adds nine preset red-team security research modes and seventeen runtime plugins, covering pentesting, code audit, binary analysis, anti-detection, incident response, cloud security and CTF solving.
- 38
rea
692shijianzhong/rea · TypeScriptREA is a tool that connects your coding agent (Claude Code, Codex, Cursor, etc.) to reverse-engineering capabilities, letting it inspect how an app feature works down to native binary level and rebuild it, without needing the original source code.
- 39

wcdb-key-tool
661TANGandXUE/wcdb-key-tool · PythonA single-purpose Python tool that pulls the encryption keys out of WeChat's local WCDB/SQLCipher4 chat databases on Linux, macOS and Windows, so you can decrypt your own chat history.
- 40

leanrea
638aicodeking/leanrea · Pythonleanrea is a single 8 KB skill file (SKILL.md) that teaches a coding agent to reverse-engineer apps and binaries using plain CLI tools like otool, nm, jadx and apktool directly, instead of routing through the REA MCP server and its 207 bundled tools.
- 41

selfdb
572fzakaria/selfdb · Pythonselfdb (SELF, Structured Executable & Linkable Format) makes a program that is literally a SQLite database instead of an ELF binary, plus the loader machinery to actually execute that database on Linux/NixOS.
- 42
0
5140sec-labs/0 · TypeScript0 is an open-source, self-evolving, multi-model AI harness for security research that finds, verifies, and fixes vulnerabilities, built by the Swiss Applied AI & Cybersecurity Research Lab.
- 43

vmp-lazy-unpack
406x86rc/vmp-lazy-unpack · PythonThis is a Python tool that automatically unpacks Windows x64 binaries protected with VMProtect 3.x and rebuilds their import table (IAT), without needing a debugger or live memory dump.
- 44

re4
352adonis-singh/re4 · C++A complete, byte-identical decompilation of Resident Evil 4 for GameCube — the G4BE08 debug build, both discs — reconstructed as readable C/C++ that rebuilds the exact original binaries.
- 45

wowdecomp
327SatyPardus/wowdecomp · C++wowdecomp is a C++ decompilation of the World of Warcraft 3.3.5a client (Wow.exe, build 12340, June 2010), reconstructing the original game executable function by function from its binary.
- 46

The-Darkness-Recomp
311portingpete/The-Darkness-Recomp · C++It is a native Windows port of the Xbox 360 game The Darkness, built by statically translating the original 360 executable into C++ ahead of time and running it with a DirectX 11 renderer, no emulator involved.
- 47
ablation
222Ablation-Tool/ablation · PythonAblation is a reverse engineering framework that provides the same core disassembly, decompilation, and binary analysis capabilities as industry tools like Ghidra, IDA Pro, and Binary Ninja, and it's built to be driven by an AI coding agent.
- 48

vol-rs
197daffainfo/vol-rs · Rust'vol-rs' is a line-by-line port of the Volatility 3 memory forensics framework from Python to Rust. It reads the same memory images, runs the same plugins with the same options, and prints byte-for-byte identical output, just much faster.
Related topics
Often tagged together
- reverse-engineering238
- windows3,480
- linux4,248
- macos3,608
- open-source5,749
- security-tools287
- cli2,275
- developer-tools2,981
- security998
- cross-platform2,673
- decompiler35
- cybersecurity249
- disassembler25
- malware-analysis34
- python2,425
- static-analysis131
- mit3,387
- tool1,336
- mcp934
- ai-agents1,323
- android762
- claude-code928
- terminal1,128
- agent839