Topics / #vulnerability-detection
Vulnerability-detection projects on GitHub
Detecting and reporting vulnerabilities in systems and containers.
As of , the most-starred Vulnerability-detection projects on GitHub are trivy (38.5K stars), nuclei (32.1K stars) and wazuh (17.3K stars). GitHub.Locker tracks 11 Vulnerability-detection repositories with 166.8K stars combined. The fastest-growing on October 16 was wifit3, with +26 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
 +26
wifit3
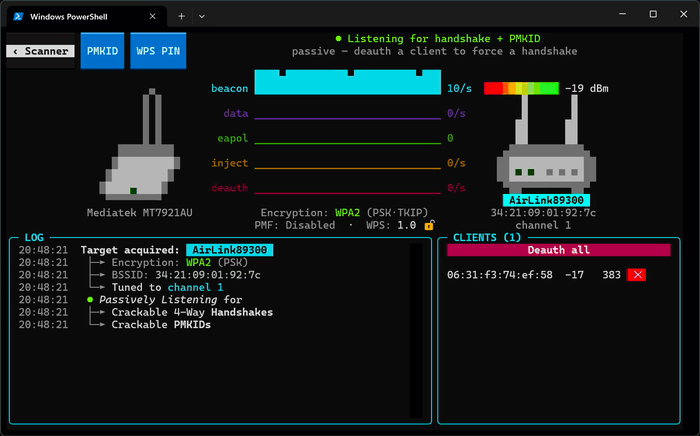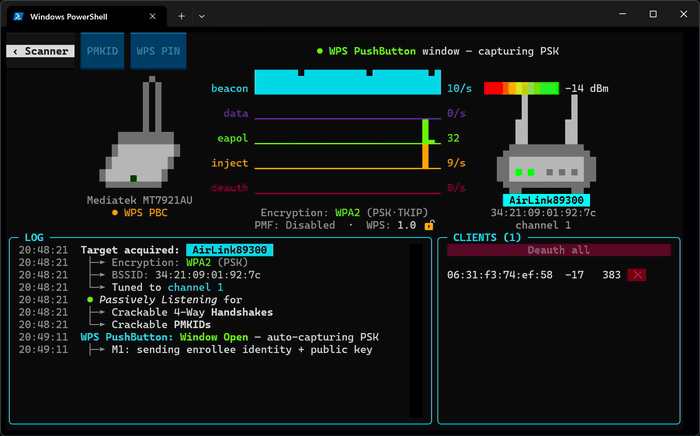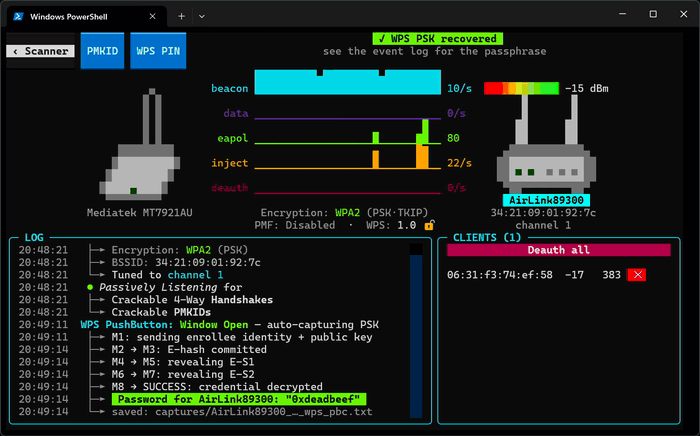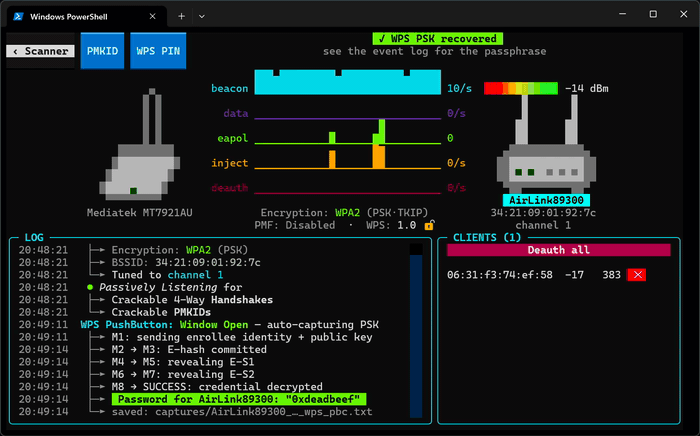
derv82/wifit3 · ★ 2.4Kwifit3 is a standalone Wi-Fi security auditing tool that scans networks, captures WPA/WPA2 handshakes, and exploits WPS/WEP weaknesses using a supported USB Wi-Fi adapter, without relying on aircrack-ng or OS kernel drivers.
 +23
skills
trailofbits/skills · ★ 7.6KThis is Trail of Bits' Claude Code plugin marketplace: a curated collection of AI-agent skills for security research, vulnerability detection, and audit workflows, covering everything from smart contract audits to malware analysis and reverse engineering.
 +22
trivy
aquasecurity/trivy · ★ 38.5KTrivy is an all-in-one security scanner that finds vulnerabilities, misconfigurations, secrets, and software licenses across container images, filesystems, git repositories, VM images, and Kubernetes clusters.
 +21
nuclei
projectdiscovery/nuclei · ★ 32.1KA fast, open-source vulnerability scanner that runs YAML-based templates to find security issues in applications, APIs, networks, DNS and cloud configurations. Its checks come from a large global security community.
The all-time top
11 projects · by stars
- 38.5K#1 · aquasecurity/trivy
trivy
Trivy is an all-in-one security scanner that finds vulnerabilities, misconfigurations, secrets, and software licenses across container images, filesystems, git repositories, VM images, and Kubernetes clusters.
- 32.1K#2 · projectdiscovery/nuclei
nuclei
A fast, open-source vulnerability scanner that runs YAML-based templates to find security issues in applications, APIs, networks, DNS and cloud configurations. Its checks come from a large global security community.
- 17.3K
 #3 · wazuh/wazuh
wazuh
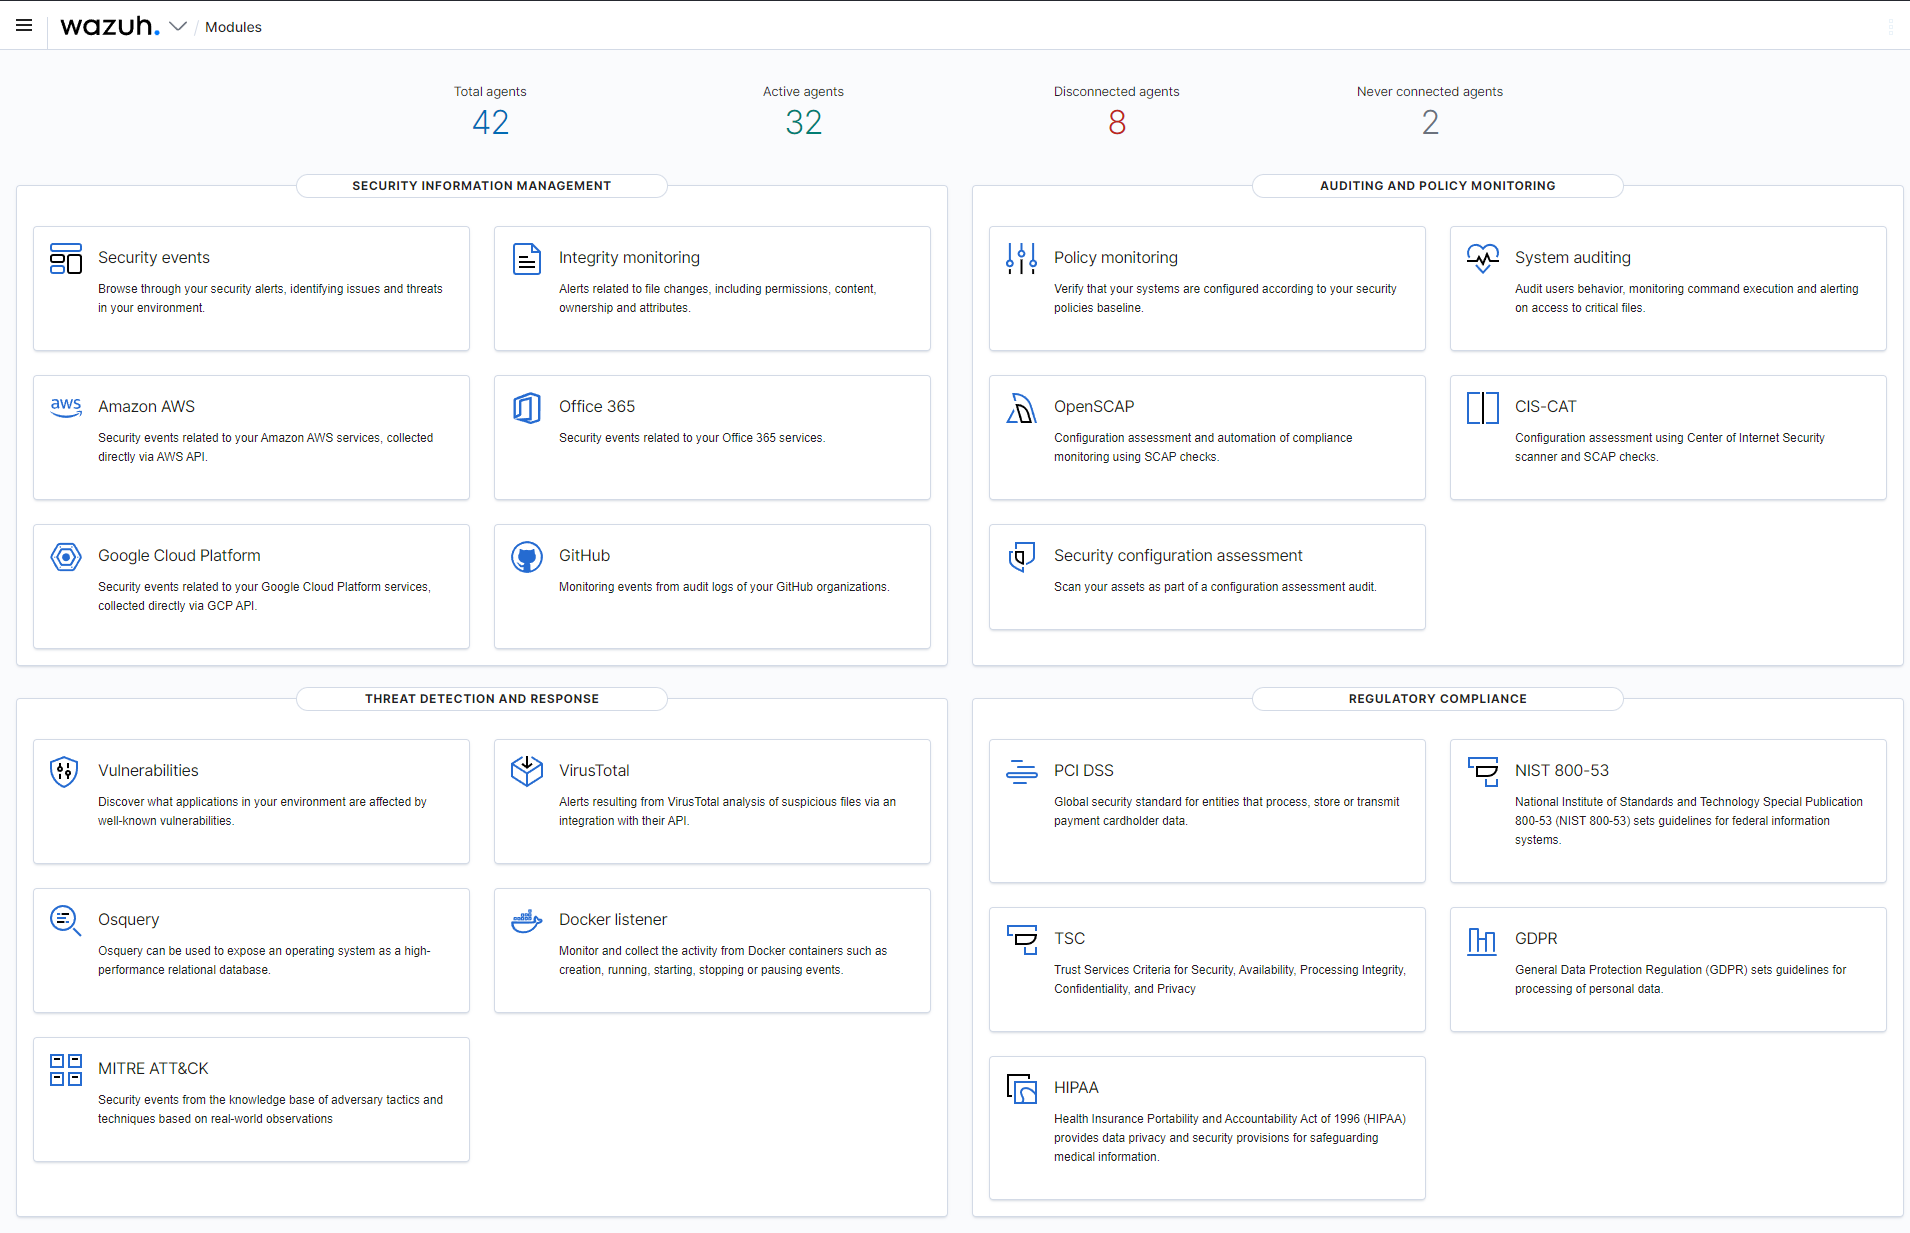
Wazuh is a free, open source security platform (XDR and SIEM) for threat prevention, detection and response across on-premises, virtualized, containerized and cloud workloads.
- 4
lynis
16.5KCISOfy/lynis · ShellLynis is a security auditing and hardening tool for Linux, macOS, BSD, and other Unix-like systems. It scans the host it runs on for vulnerable software, misconfigurations, and weak settings, and gives hardening tips while also assisting with compliance testing (HIPAA, ISO27001, PCI DSS).
- 5

nuclei-templates
13.1Kprojectdiscovery/nuclei-templates · JavaScriptThis is a community-curated collection of over 11,000 detection templates for the Nuclei vulnerability scanner, covering CVEs, misconfigurations, exposed panels, and other security issues.
- 6
oss-fuzz
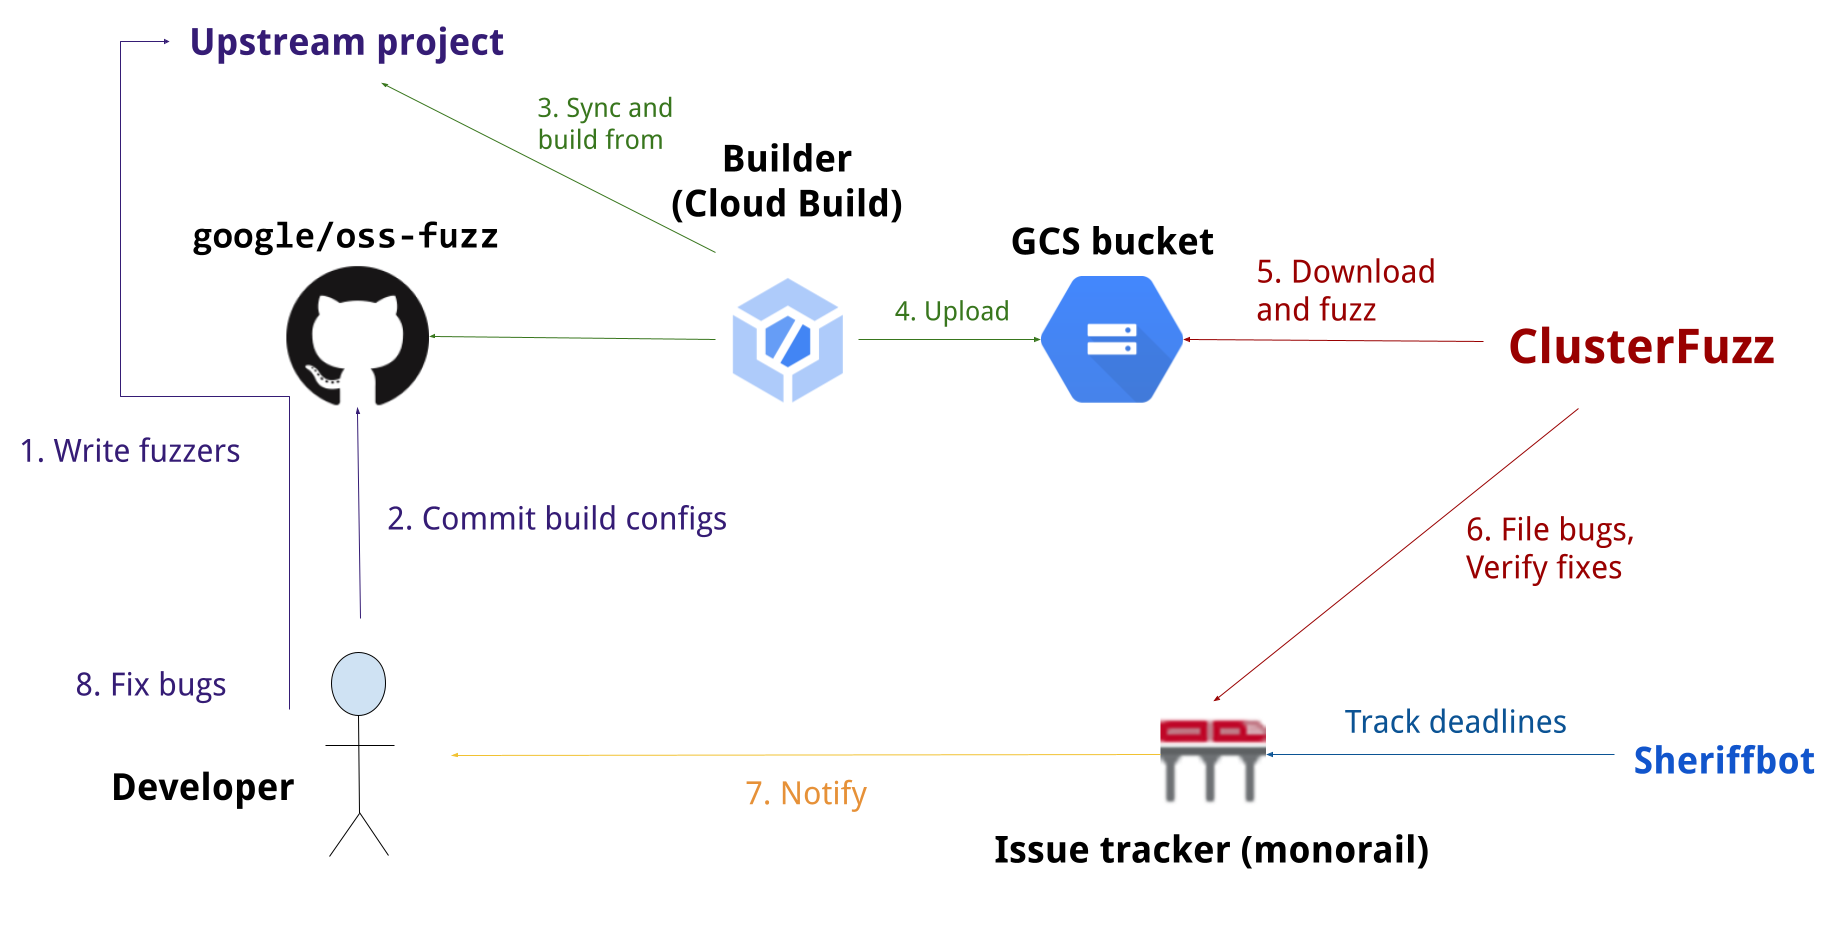
12.7Kgoogle/oss-fuzz · ShellOSS-Fuzz is Google's free continuous fuzzing service for open source software: it runs guided fuzzing nonstop to surface security vulnerabilities and stability bugs before attackers do.
- 7
vuls
12.3Kfuture-architect/vuls · GoVuls is an open-source, agent-less vulnerability scanner written in Go. It automatically detects vulnerabilities affecting your servers and can generate reports on a regular basis, for example via CRON.
- 8

kubescape
11.8Kkubescape/kubescape · GoKubescape is an open-source Kubernetes security platform that scans clusters, YAML files, Helm charts, and container images for misconfigurations and vulnerabilities, covering the whole lifecycle from development to runtime.
- 9
skills
7.6Ktrailofbits/skills · PythonThis is Trail of Bits' Claude Code plugin marketplace: a curated collection of AI-agent skills for security research, vulnerability detection, and audit workflows, covering everything from smart contract audits to malware analysis and reverse engineering.
- 10
mantis
2.5Kgoogle/mantis · PythonMantis is a toolkit of skills plus a reference agent harness (built on Google's ADK) that lets AI coding agents autonomously find, reproduce, triage, and patch vulnerabilities in a codebase.
- 11
wifit3
2.4Kderv82/wifit3 · Pythonwifit3 is a standalone Wi-Fi security auditing tool that scans networks, captures WPA/WPA2 handshakes, and exploits WPS/WEP weaknesses using a supported USB Wi-Fi adapter, without relying on aircrack-ng or OS kernel drivers.
Related topics
Often tagged together
- linux4,184
- open-source5,666
- security976
- macos3,544
- security-tools282
- windows3,403
- cli2,227
- cybersecurity245
- cross-platform2,623
- docker1,660
- devops455
- go681
- penetration-testing126
- security-audit23
- terminal1,101
- vulnerability-scanner43
- automation1,183
- compliance31
- developer-tools2,924
- devsecops38
- hacktoberfest454
- kubernetes316
- monitoring418
- python2,383