Topics / #reconnaissance
Reconnaissance projects on GitHub
OSINT gathering and information reconnaissance about targets.
As of , the most-starred Reconnaissance projects on GitHub are sherlock (94.3K stars), SecLists (74.2K stars) and maigret (39.2K stars). GitHub.Locker tracks 40 Reconnaissance repositories with 710.1K stars combined. The fastest-growing on October 16 was GhostTrack, with +122 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
 +122
GhostTrack
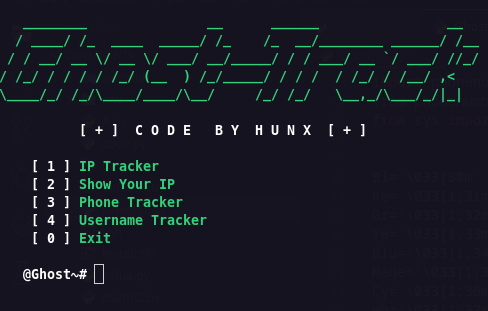
HunxByts/GhostTrack · ★ 19.1KGhostTrack is a Python command-line OSINT tool used to track a target's approximate location or gather details about a phone number, essentially a piece of information-gathering tooling for recon work.
 +93
sherlock
sherlock-project/sherlock · ★ 94.3KSherlock hunts down social media accounts by username: give it a name and it checks across social networks for accounts registered under it.
 +41
maigret
soxoj/maigret · ★ 39.2KMaigret is an OSINT command-line tool that builds a dossier on a person by checking for an account under a given username across thousands of websites and pulling together whatever profile info it finds, with no API keys required.
 +22
phoneinfoga
sundowndev/phoneinfoga · ★ 18.2KAn open-source OSINT framework for scanning international phone numbers. It gathers basics like country, area, carrier and line type, then tries to find the VoIP provider or identify the owner.
The all-time top
40 projects · by stars
- 94.3K#1 · sherlock-project/sherlock
sherlock
Sherlock hunts down social media accounts by username: give it a name and it checks across social networks for accounts registered under it.
- 74.2K
 #2 · danielmiessler/SecLists
SecLists
SecLists is a huge collection of ready-made wordlists for security testing: usernames, passwords, URLs, sensitive data patterns, fuzzing payloads, web shells and more, all gathered in one repository.
- 39.2K#3 · soxoj/maigret
maigret
Maigret is an OSINT command-line tool that builds a dossier on a person by checking for an account under a given username across thousands of websites and pulling together whatever profile info it finds, with no API keys required.
- 4
web-check
35.1Klissy93/web-check · TypeScriptWeb-Check is an open-source OSINT dashboard that lets you analyse any website: it pulls IP info, SSL chain, DNS records, cookies, headers, server location, and more into one report so you can understand its tech stack and security posture.
- 5
awesome-osint
30.3Kjivoi/awesome-osintThis is a curated 'awesome list' of hundreds of free and paid OSINT (open source intelligence) tools and resources, organized into categories like general search, Google dorks, data breach lookup, social media, threat actors, and dark web.
- 6

awesome-pentest
27.4Kenaqx/awesome-pentestA curated collection of penetration testing and offensive-security resources: tools, books, courses, conferences and practice targets for authorized security testing.
- 7

masscan
26.1Krobertdavidgraham/masscan · CMasscan is an Internet-scale TCP port scanner that transmits SYN packets asynchronously and can scan the entire IPv4 Internet in under 5 minutes, sending up to 10 million packets per second from a single machine.
- 8
social-analyzer
24.3Kqeeqbox/social-analyzer · JavaScriptSocial-Analyzer is an OSINT tool that searches and correlates a person's profile across roughly 1000 social media sites and websites, available as a CLI, an API, and a web app.
- 9

RustScan
20.6Kbee-san/RustScan · RustRustScan is an open-source port scanner written in Rust: it finds open ports fast — all 65k ports in as little as 3 seconds — and has a scripting engine for Python, Lua and Shell.
- 10

GHunt
19.7Kmxrch/GHunt · PythonGHunt is an offensive Google framework geared toward OSINT — collecting intelligence around Google — and its authors note that any Google-related use is possible.
- 11
GhostTrack
19.1KHunxByts/GhostTrack · PythonGhostTrack is a Python command-line OSINT tool used to track a target's approximate location or gather details about a phone number, essentially a piece of information-gathering tooling for recon work.
- 12
phoneinfoga
18.2Ksundowndev/phoneinfoga · GoAn open-source OSINT framework for scanning international phone numbers. It gathers basics like country, area, carrier and line type, then tries to find the VoIP provider or identify the owner.
- 13

theHarvester
18Klaramies/theHarvester · PythonAn open-source OSINT tool that gathers emails, subdomains and names about a domain or organization from public sources: search engines, certificate transparency logs, DNS datasets, code repositories and threat-intel platforms, normalizing hostnames, emails, IPs, URLs, ASNs, people and breach names.
- 14

katana
17.7Kprojectdiscovery/katana · GoKatana is a next-generation crawling and spidering framework from ProjectDiscovery: point it at URLs and it discovers endpoints, links and forms across a site.
- 15
ffuf
16.9Kffuf/ffuf · Goffuf is a fast web fuzzer written in Go — a command-line tool that sends many crafted requests to a target to discover directories, virtual hosts, and fuzzable GET/POST parameters.
- 16
Osintgram
15.1KDatalux/Osintgram · PythonOsintgram is an OSINT tool for Instagram that lets you collect, analyze, and run reconnaissance on any public Instagram account via an interactive shell, just by giving its nickname.
- 17
fscan
14.7Kshadow1ng/fscan · Gofscan is an open-source intranet scanner written in Go: one command runs an all-round internal-network audit — host discovery, port scanning, service identification, weak-password brute force and vulnerability detection.
- 18
subfinder
14.6Kprojectdiscovery/subfinder · GoSubfinder is a fast passive subdomain enumeration tool that returns valid subdomains for a website by querying passive online sources, built for penetration testers and bug bounty hunters.
- 19

gobuster
14.2KOJ/gobuster · GoGobuster is a fast, multi-threaded command-line tool written in Go for brute-forcing web directories/files, DNS subdomains, and virtual hosts, plus enumerating S3/GCS cloud storage buckets and TFTP files.
- 20

Photon
13.3Ks0md3v/Photon · PythonPhoton is a fast web crawler built for OSINT (open-source intelligence) gathering, extracting URLs, emails, social media accounts, secret keys, subdomains and more while it crawls a target site.
- 21

PowerSploit
13.1KPowerShellMafia/PowerSploit · PowerShellPowerSploit is a collection of PowerShell modules that penetration testers use during all phases of an assessment, covering code execution, persistence, privilege escalation, credential theft, exfiltration and reconnaissance on Windows systems.
- 22
ESP32Marauder
12.8Kjustcallmekoko/ESP32Marauder · C++ESP32 Marauder is a suite of offensive and defensive WiFi and Bluetooth tools that run as firmware on an ESP32 microcontroller, used for things like wardriving, scanning, and wireless security testing.
- 23

OSINT-Framework
12.3Klockfale/OSINT-Framework · JavaScriptOSINT Framework is a curated, browsable index of free OSINT (open-source intelligence) tools and resources, organized into a clickable category tree so you can find the right tool for a given task.
- 24
Sn1per
11.5K1N3/Sn1per · ShellSn1per is an offensive-security platform that bundles reconnaissance, vulnerability scanning, exploitation and reporting into one workspace, orchestrating 600+ exploits and 90+ third-party tools for pentesters and attack-surface-management teams.
- 25

404StarLink
11.4Kknownsec/404StarLink404StarLink is a curated list of security-focused open-source projects maintained by Knownsec 404 Lab, created to showcase, support, and track high-quality, actively-maintained security tools.
- 26

awesome-hacker-search-engines
11.3Kedoardottt/awesome-hacker-search-engines · ShellA curated list of search engines useful for penetration testing, vulnerability assessment, red/blue team operations, bug bounty hunting, and general OSINT work.
- 27

Sublist3r
11.1Kaboul3la/Sublist3r · PythonSublist3r is a Python tool that enumerates subdomains of a target website using OSINT, helping penetration testers and bug hunters gather subdomains for a domain they are targeting.
- 28
bbot
10.7Kblacklanternsecurity/bbot · PythonBBOT is a recursive internet scanner for hackers — it automates recon, bug bounty work and attack surface management (ASM), inspired by Spiderfoot.
- 29

BloodHound-Legacy
10.6KSpecterOps/BloodHound-Legacy · PowerShellBloodHound Legacy is a security tool that uses graph theory to map hidden relationships and attack paths inside an Active Directory environment, helping find the shortest route to Domain Admin — hence its tagline 'Six Degrees of Domain Admin'.
- 30
httpx
10.5Kprojectdiscovery/httpx · Gohttpx is a fast, multi-purpose HTTP toolkit from ProjectDiscovery that runs many probes against lists of hosts and URLs, built on the retryablehttp library to stay reliable under high thread counts.
- 31

OneForAll
10.1Kshmilylty/OneForAll · PythonOneForAll is a powerful subdomain collection tool: point it at a target domain and it gathers subdomains from many sources — a core reconnaissance step in penetration testing, which is why the author built it.
- 32
flowsint
9.8Kreconurge/flowsint · TypeScriptFlowsint is an open-source, graph-based OSINT investigation tool that lets analysts explore relationships between people, domains, IPs, organizations and more through a visual graph interface with automated enrichers.
- 33
Decepticon
6.2KBitterSecurity/Decepticon · PythonDecepticon is a professional autonomous Red Team agent that runs full attack chains — reconnaissance, exploitation, privilege escalation, lateral movement, and C2 — the way a real adversary would, instead of just scanning and printing a report.
- 34
airgorah
4.2Kmartin-olivier/airgorah · RustAirgorah is a WiFi security auditing tool written in Rust that captures nearby WiFi traffic, discovers clients connected to access points, performs deauthentication attacks, captures handshakes and PMKIDs, and cracks access point passwords.
- 35
METATRON
4.2Ksooryathejas/METATRON · PythonMetatron is a CLI-based AI penetration testing assistant that runs real recon tools against a target and lets a locally-hosted LLM analyze the results, suggest exploits, and recommend fixes, with no cloud or API keys involved.
- 36
redamon
3.1Ksamugit83/redamon · PythonRedAmon is an open-source, self-hosted AI framework that chains reconnaissance, exploitation and post-exploitation into one pipeline, maps the attack surface into a Neo4j graph, and then triages findings and opens GitHub pull requests that fix what it discovers.
- 37
WireTapper
2.5Kh9zdev/WireTapper · HTMLWireTapper is a wireless OSINT tool that passively discovers, maps, and analyzes nearby radio-based devices — Wi-Fi, Bluetooth, CCTV cameras, vehicles, IoT gadgets, and cell towers — without actively intruding on anything.
- 38
Cybermes
946Zyrexnn/Cybermes · PythonCybermes is an offensive security assistant and automation framework for authorized bug bounty hunting, reconnaissance, vulnerability research, and structured reporting, driven by AI agents and a library of 200+ playbooks.
- 39
getcontact-cli
613xdreizein666/getcontact-cli · PythonGetContact CLI is a Python command-line tool that talks directly to the GetContact phone-lookup API, letting you check a number's display name, tags and email without installing the Android app or using a browser.
- 40

EvilFontTool
353DoctorEww/EvilFontTool · PythonEvilFontTool is a font-based deception tool for red teaming and security research. It generates 'Evil Fonts' — fonts that remap glyphs so a document shows humans one text while terminals, AI systems, and copy-paste see completely different text.
Related topics
Often tagged together
- security-tools282
- security976
- linux4,184
- cybersecurity245
- windows3,403
- macos3,544
- cli2,227
- pentesting113
- osint68
- penetration-testing126
- open-source5,666
- terminal1,101
- docker1,660
- python2,383
- cross-platform2,623
- hacking135
- information-gathering20
- mit3,312
- offensive-security77
- command-line-tool715
- tool1,295
- hacking-tool75
- red-team79
- self-hosted1,929