Topics / #pentesting
Pentesting projects on GitHub
Penetration testing methodology and tooling for assessing system security.
As of , the most-starred Pentesting projects on GitHub are the-book-of-secret-knowledge (251.3K stars), Awesome-Hacking (123K stars) and sherlock (94.5K stars). GitHub.Locker tracks 114 Pentesting repositories with 2M stars combined. The fastest-growing on October 18 was security-audit-skill, with +486 stars in a day.
Hot right now
Most stars gained in a day · Oct 18
 +486
security-audit-skill
cloudflare/security-audit-skill · ★ 32.5KA Cloudflare coding-agent skill that turns your agent into a security auditor: it orchestrates isolated agents through a structured, multi-phase audit and returns independently verified, machine-readable findings.
 +299
the-book-of-secret-knowledge
trimstray/the-book-of-secret-knowledge · ★ 251.3KA massive curated collection of lists, manuals, cheatsheets, blogs, hacks, one-liners and CLI/GUI/web tools that the author gathers from everyday sysadmin, DevOps and security work.
 +153
CVE-2026-41940-PoC
sakidekin/CVE-2026-41940-PoC · ★ 425This is a proof-of-concept exploit tool for CVE-2026-41940, a critical (CVSS 10.0) authentication bypass in cPanel & WHM that lets an unauthenticated attacker gain root-level WHM access by injecting CRLF sequences into server-side session files via the Authorization header.
 +151
airgorah
martin-olivier/airgorah · ★ 4.5KAirgorah is a WiFi security auditing tool written in Rust that captures nearby WiFi traffic, discovers clients connected to access points, performs deauthentication attacks, captures handshakes and PMKIDs, and cracks access point passwords.
The all-time top
Top 100 of 114 · by stars
- 251.3K#1 · trimstray/the-book-of-secret-knowledge
the-book-of-secret-knowledge
A massive curated collection of lists, manuals, cheatsheets, blogs, hacks, one-liners and CLI/GUI/web tools that the author gathers from everyday sysadmin, DevOps and security work.
- 123K
 #2 · Hack-with-Github/Awesome-Hacking
Awesome-Hacking
A massive index that links out to dozens of other awesome-lists covering nearly every security domain: android security, bug bounty, fuzzing, malware analysis, OSINT, reverse engineering, web hacking, and more.
- 94.5K
 #3 · sherlock-project/sherlock
sherlock
Sherlock hunts down social media accounts by username: give it a name and it checks across social networks for accounts registered under it.
- 4
SecLists
74.2Kdanielmiessler/SecLists · PHPSecLists is a huge collection of ready-made wordlists for security testing: usernames, passwords, URLs, sensitive data patterns, fuzzing payloads, web shells and more, all gathered in one repository.
- 5
shannon
49.1KKeygraphHQ/shannon · TypeScriptShannon is an autonomous AI pentester that analyzes your web application's source code, maps attack vectors, and then executes real exploits against the running app to prove vulnerabilities before they reach production — 'no exploit, no report'.
- 6

mitmproxy
45.7Kmitmproxy/mitmproxy · Pythonmitmproxy is an interactive, SSL/TLS-capable intercepting proxy for HTTP/1, HTTP/2, and WebSockets, used by penetration testers and developers to inspect and modify traffic. mitmdump is its CLI version, and mitmweb is a web-based interface.
- 7

reverse-skill
42.7Kzhaoxuya520/reverse-skill · PowerShellIt is a skill pack that routes AI coding agents to the right reverse engineering, penetration testing, and security research methodology for a given task (APK, binary, JS, CTF, malware, etc.), checks which tools are installed, and runs a repeatable workflow instead of letting the agent guess commands.
- 8
maigret
39.2Ksoxoj/maigret · PythonMaigret is an OSINT command-line tool that builds a dossier on a person by checking for an account under a given username across thousands of websites and pulling together whatever profile info it finds, with no API keys required.
- 9

metasploit-framework
39.2Krapid7/metasploit-framework · RubyMetasploit Framework is an open-source penetration testing framework written in Ruby — one of the best-known security toolkits on GitHub, with about 39,000 stars.
- 10

sqlmap
38.7Ksqlmapproject/sqlmap · Pythonsqlmap is an open-source penetration testing tool that automates detecting and exploiting SQL injection flaws and taking over the underlying database server.
- 11
Anthropic-Cybersecurity-Skills
34.7Kmukul975/Anthropic-Cybersecurity-Skills · PythonAn open-source library of 818 production-grade cybersecurity skills for AI agents, covering 34 security domains and mapped to six frameworks including MITRE ATT&CK and NIST CSF 2.0.
- 12
security-audit-skill
32.5Kcloudflare/security-audit-skill · JavaScriptA Cloudflare coding-agent skill that turns your agent into a security auditor: it orchestrates isolated agents through a structured, multi-phase audit and returns independently verified, machine-readable findings.
- 13
awesome-osint
30.4Kjivoi/awesome-osintThis is a curated 'awesome list' of hundreds of free and paid OSINT (open source intelligence) tools and resources, organized into categories like general search, Google dorks, data breach lookup, social media, threat actors, and dark web.
- 14
h4cker
29.8KThe-Art-of-Hacking/h4cker · Jupyter NotebookA curated collection of thousands of cybersecurity resources — references, scripts, tools, code, labs, and training material — maintained by Omar Santos as a companion to his books, video courses, and live training.
- 15

awesome-pentest
27.5Kenaqx/awesome-pentestA curated collection of penetration testing and offensive-security resources: tools, books, courses, conferences and practice targets for authorized security testing.
- 16
promptfoo
26.2Kpromptfoo/promptfoo · TypeScriptpromptfoo is a CLI and library for evaluating and red-teaming LLM apps — you test prompts, agents, and RAGs and run security scans on them, instead of relying on trial-and-error.
- 17

masscan
26.1Krobertdavidgraham/masscan · CMasscan is an Internet-scale TCP port scanner that transmits SYN packets asynchronously and can scan the entire IPv4 Internet in under 5 minutes, sending up to 10 million packets per second from a single machine.
- 18

awesome-flipperzero
24.5Kdjsime1/awesome-flipperzeroA curated list of resources for the Flipper Zero, the pocket multi-tool hacking device, covering firmware, apps, file dumps, cases, modules, and debugging tools.
- 19
social-analyzer
24.3Kqeeqbox/social-analyzer · JavaScriptSocial-Analyzer is an OSINT tool that searches and correlates a person's profile across roughly 1000 social media sites and websites, available as a CLI, an API, and a web app.
- 20
spiderfoot
23.6Ksmicallef/spiderfoot · PythonOpen source OSINT automation — it collects intelligence on a target for threat intel and attack surface mapping, whether you are doing red team recon or checking what your organisation has exposed.
- 21
unleashed-firmware
22.6KDarkFlippers/unleashed-firmware · CUnleashed is custom firmware for the Flipper Zero multitool — a fork of the official firmware (OFW) that adds extra features and improvements while staying compatible with official apps.
- 22

frida
22.4Kfrida/frida · MesonFrida is a dynamic instrumentation toolkit for developers, reverse-engineers, and security researchers, used to instrument running apps; more at frida.re.
- 23

Mobile-Security-Framework-MobSF
22KMobSF/Mobile-Security-Framework-MobSF · JavaScriptMobSF is an automated, all-in-one mobile security framework: it performs static and dynamic analysis, penetration testing, malware analysis and privacy analysis on Android, iOS and Windows Mobile apps.
- 24

mimikatz
21.9Kgentilkiwi/mimikatz · CA small Windows security tool, originally written to learn C. It is best known for extracting plaintext passwords, hashes, PIN codes and Kerberos tickets from memory, and can perform pass-the-hash, pass-the-ticket or build Golden tickets.
- 25

Ciphey
21.7Kbee-san/Ciphey · Rustciphey automatically decrypts ciphertext without knowing the key or cipher, decodes encodings and cracks hashes. It is the Rust-built next generation of Ciphey — roughly 7x faster per decode — and the same team intends it to fully replace the original.
- 26
vulhub
21.4Kvulhub/vulhub · DockerfileVulhub is an open-source collection of pre-built, ready-to-use vulnerable Docker environments: with one command you get a working lab for security research, learning, or demos.
- 27
PEASS-ng
20.7Kpeass-ng/PEASS-ng · C#PEASS-ng is a suite of local privilege escalation enumeration tools: LinPEAS for Linux/Unix/macOS and WinPEAS for Windows. They scan a machine for privesc paths and print misconfigurations with nice colors so you can spot them easily.
- 28

RustScan
20.6Kbee-san/RustScan · RustRustScan is an open-source port scanner written in Rust: it finds open ports fast — all 65k ports in as little as 3 seconds — and has a scripting engine for Python, Lua and Shell.
- 29
bettercap
20.2Kbettercap/bettercap · GoA portable all-in-one framework written in Go for recon and attacks on WiFi, Bluetooth Low Energy, wireless HID, CAN-bus and IPv4/IPv6 networks, built for security researchers and red teamers.
- 30
GHunt
19.7Kmxrch/GHunt · PythonGHunt is an offensive Google framework geared toward OSINT — collecting intelligence around Google — and its authors note that any Google-related use is possible.
- 31
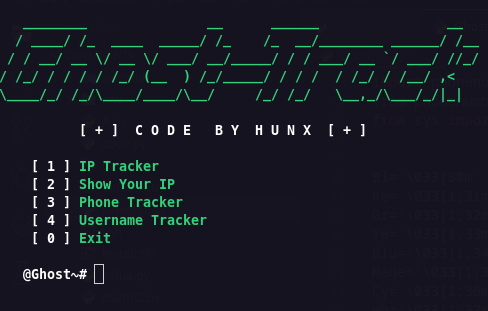
GhostTrack
19.5KHunxByts/GhostTrack · PythonGhostTrack is a Python command-line OSINT tool used to track a target's approximate location or gather details about a phone number, essentially a piece of information-gathering tooling for recon work.
- 32
theHarvester
18Klaramies/theHarvester · PythonAn open-source OSINT tool that gathers emails, subdomains and names about a domain or organization from public sources: search engines, certificate transparency logs, DNS datasets, code repositories and threat-intel platforms, normalizing hostnames, emails, IPs, URLs, ASNs, people and breach names.
- 33
Awesome-Hacking-Resources
17.5Kvitalysim/Awesome-Hacking-ResourcesA curated collection of hacking, penetration testing and AI red-teaming resources — courses, YouTube channels, CTF platforms and guides, picked to make you better at offensive security.
- 34

awesome-hacking
17.3Kcarpedm20/awesome-hackingA curated list of hacking tutorials, tools and resources covering system exploitation, reverse engineering, web security, network security, forensics, cryptography and wargames.
- 35
zphisher
17Khtr-tech/zphisher · HTMLZphisher is an automated phishing tool with 30+ ready-made login-page templates, written as a beginners-friendly shell script and intended purely for education.
- 36
ffuf
16.9Kffuf/ffuf · Goffuf is a fast web fuzzer written in Go — a command-line tool that sends many crafted requests to a target to discover directories, virtual hosts, and fuzzable GET/POST parameters.
- 37
impacket
16.2Kfortra/impacket · PythonImpacket is a collection of Python classes for working with network protocols, giving low-level programmatic access to packets and, for some protocols like SMB1-3 and MSRPC, full protocol implementations.
- 38

PentestGPT
16KGreyDGL/PentestGPT · PythonPentestGPT is an agentic framework that uses large language models to run automated penetration testing and solve CTF challenges, working through staged phases like recon, exploitation and reporting.
- 39

zaproxy
16Kzaproxy/zaproxy · JavaZAP (Zed Attack Proxy) by Checkmarx is the world's most widely used web app security scanner, used to automatically find vulnerabilities in web applications during development and testing.
- 40
evilginx2
15.7Kkgretzky/evilginx2 · GoEvilginx is a man-in-the-middle attack framework used for phishing login credentials along with session cookies, which lets an attacker bypass 2-factor authentication.
- 41

hacker-roadmap
15.7Ksundowndev/hacker-roadmapThis is a curated roadmap and toolkit index for learning and practicing ethical hacking: it explains what penetration testing is and groups hundreds of security tools, wordlists and references by category (recon, password attacks, wireless, exploitation, web hacking, post-exploitation, frameworks).
- 42

XSStrike
15.2Ks0md3v/XSStrike · PythonXSStrike is a Cross Site Scripting (XSS) detection suite built around four hand-written parsers, an intelligent payload generator, a fuzzing engine, and a fast crawler. Instead of just firing generic payloads like most scanners, it analyzes the live response and crafts payloads guaranteed to work through context analysis.
- 43
esp8266_deauther
15KSpacehuhnTech/esp8266_deauther · CESP8266 Deauther is open-source firmware for the ESP8266 chip that lets you scan nearby WiFi networks, send deauthentication packets to disconnect devices, and spin up dozens of fake WiFi networks to confuse scanners - an affordable platform for testing and learning about WiFi security.
- 44

awesome-security
15Ksbilly/awesome-securityA curated, categorized collection of well-known security resources — software, libraries, documents, books and other cool stuff — maintained by the community in the spirit of awesome-php and awesome-python.
- 45
dirsearch
15Kmaurosoria/dirsearch · PythonDirsearch is an advanced command-line web path brute-forcer used to discover hidden files and directories on websites for security testing.
- 46
wifiphisher
14.9Kwifiphisher/wifiphisher · PythonWifiphisher is a rogue access point framework for conducting Wi-Fi phishing and man-in-the-middle attacks against wireless clients, used in red team and penetration testing engagements.
- 47
HackBrowserData
14.6KmoonD4rk/HackBrowserData · GoHackBrowserData is a command-line tool that decrypts and exports browser data — passwords, cookies, history, bookmarks, credit cards and more — from Chromium-based browsers, Firefox and Safari, built for security research.
- 48
binwalk
14.5KReFirmLabs/binwalk · RustBinwalk is a firmware analysis tool that can identify, and optionally extract, files and data that have been embedded inside other files.
- 49

gophish
14.3Kgophish/gophish · GoGophish is an open-source phishing toolkit for businesses and penetration testers: it lets you quickly set up and run phishing engagements and security awareness training campaigns.
- 50
awesome-malware-analysis
14.3Krshipp/awesome-malware-analysisA curated 'awesome list' of malware analysis tools and resources, covering sample collection, sandboxes, detection tools, threat intelligence feeds, reverse engineering, and forensics.
- 51

gobuster
14.2KOJ/gobuster · GoGobuster is a fast, multi-threaded command-line tool written in Go for brute-forcing web directories/files, DNS subdomains, and virtual hosts, plus enumerating S3/GCS cloud storage buckets and TFTP files.
- 52
juice-shop
14.2Kjuice-shop/juice-shop · TypeScriptOWASP Juice Shop is an intentionally insecure web application (a fake online juice store) built for security training, awareness demos, CTFs, and testing security tools.
- 53

DVWA
13.9Kdigininja/DVWA · PHPDVWA (Damn Vulnerable Web Application) is a PHP/MariaDB web app that is deliberately full of security bugs, built as a legal practice target for security pros, students, and developers to learn web application security.
- 54

john
13.8Kopenwall/john · CA fast, offline password cracker. Its primary purpose is detecting weak Unix passwords, but the jumbo build supports hundreds of hash and cipher types and runs on Unix, macOS, Windows and more.
- 55
pwntools
13.8KGallopsled/pwntools · PythonPwntools is a CTF framework and exploit development library written in Python, built for rapid prototyping with the goal of making exploit writing as simple as possible.
- 56
GTFOBins.github.io
13.8KGTFOBins/GTFOBins.github.io · YAMLGTFOBins is a curated list of Unix-like executables that can be abused to bypass local security restrictions in misconfigured systems — for example, binaries a restricted user can turn into a root shell.
- 57

Photon
13.3Ks0md3v/Photon · PythonPhoton is a fast web crawler built for OSINT (open-source intelligence) gathering, extracting URLs, emails, social media accounts, secret keys, subdomains and more while it crawls a target site.
- 58
mastg
13.3KOWASP/mastg · PythonA comprehensive OWASP manual for mobile app security testing and reverse engineering. It gives technical processes for verifying the weaknesses listed in the OWASP Mobile Security Weakness Enumeration (MASWE).
- 59
hexstrike-ai
12.9K0x4m4/hexstrike-ai · PythonHexStrike AI MCP Agents is an MCP server that lets AI agents like Claude, GPT, or Copilot autonomously run 150+ real cybersecurity tools for automated pentesting, bug bounty hunting, CTF challenges, and vulnerability discovery.
- 60
atomic-red-team
12.7Kredcanaryco/atomic-red-team · CAtomic Red Team is a library of small, portable security tests, each mapped to a specific MITRE ATT&CK technique, that security teams run to check whether their defenses actually detect real attacker behavior.
- 61

wifi-cracking
12.7Kbrannondorsey/wifi-crackingA step-by-step tutorial for cracking WPA/WPA2 Wi-Fi passwords: capture a handshake with Airodump-ng, then crack it offline with Aircrack-ng or Hashcat.
- 62

hacktricks
12.6KHackTricks-wiki/hacktricks · JavaScriptA free, open wiki of hacking tricks and techniques — everything the author has learnt from CTFs, real-world apps and security research, organized into a browsable reference with 12.5k+ GitHub stars.
- 63
hetty
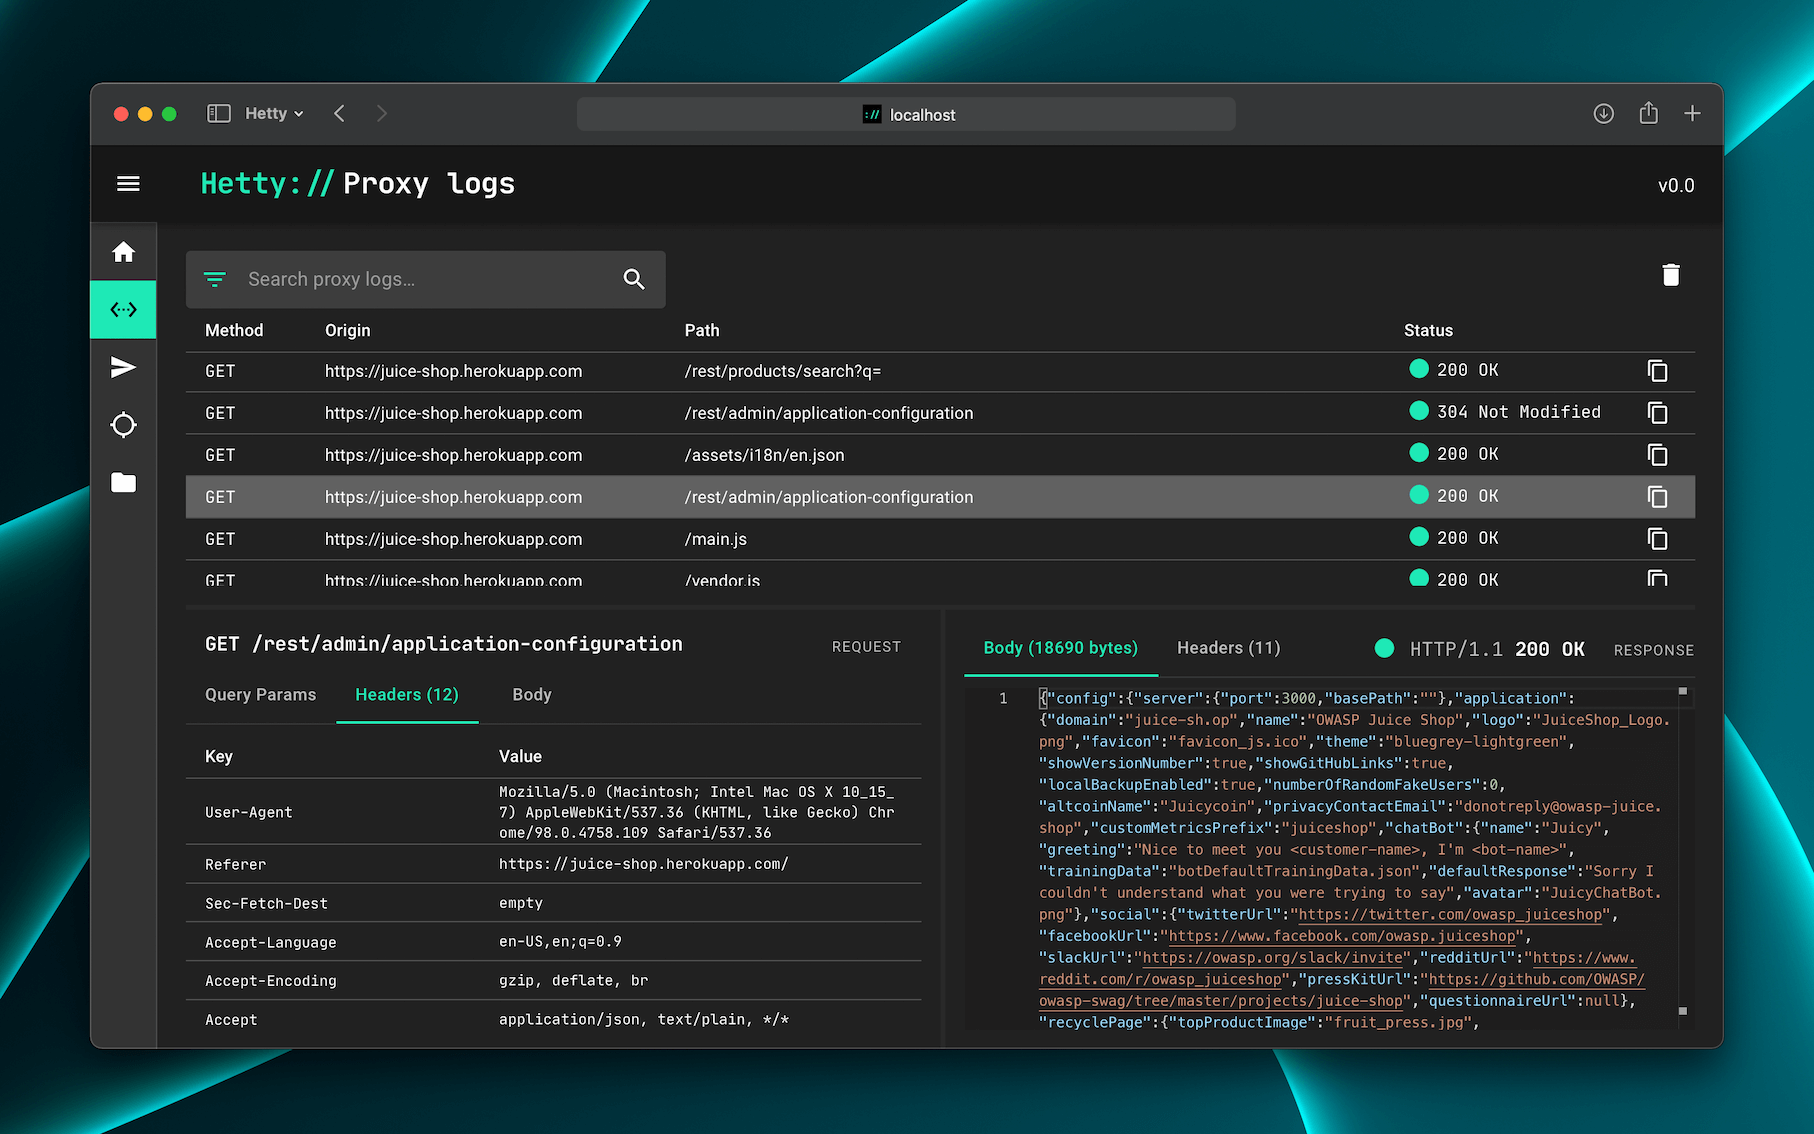
12.5Kdstotijn/hetty · GoHetty is an HTTP toolkit for security research, aiming to be an open source alternative to commercial tools like Burp Suite Pro, aimed at the infosec and bug bounty community.
- 64

thc-hydra
12.4Kvanhauser-thc/thc-hydra · CHydra is a parallelized network login cracker by van Hauser / THC: a proof-of-concept tool showing researchers and security consultants how easily a remote system can be broken into through weak passwords. It supports over 50 protocols.
- 65

fsociety
12.4KManisso/fsociety · Pythonfsociety is a penetration testing toolkit that bundles dozens of existing hacking tools (Nmap, sqlmap, WPScan, Reaver, etc.) behind one menu-driven script, inspired by the tools used in the 'Mr. Robot' TV series.
- 66

sliver
12.1KBishopFox/sliver · GoSliver is an open source cross-platform adversary emulation and red team framework that organizations of any size can use to perform security testing.
- 67

awesome-ctf
11.9Kapsdehal/awesome-ctf · JavaScriptA curated list of frameworks, libraries, tools, and resources for Capture The Flag (CTF) competitions, covering everything from building challenges to solving them.
- 68

TheFatRat
11.5Kscreetsec/TheFatRat · CTheFatRat is an exploiting tool that compiles malware from famous payloads — an easy way to generate backdoors built to slip past most anti-virus software.
- 69
Sn1per
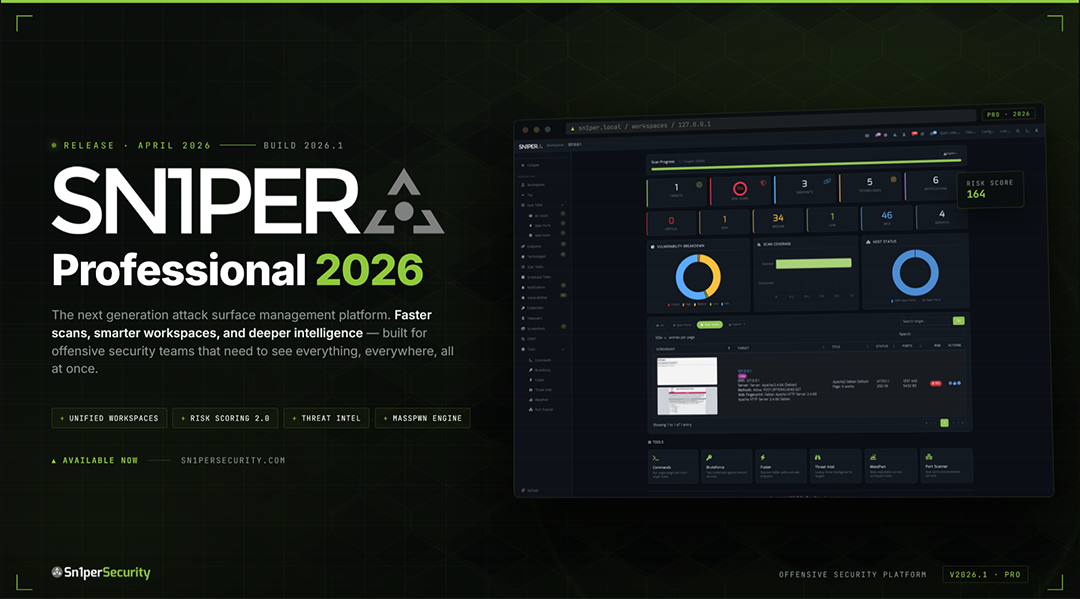
11.5K1N3/Sn1per · ShellSn1per is an offensive-security platform that bundles reconnaissance, vulnerability scanning, exploitation and reporting into one workspace, orchestrating 600+ exploits and 90+ third-party tools for pentesters and attack-surface-management teams.
- 70

beef
11.1Kbeefproject/beef · JavaScriptBeEF (Browser Exploitation Framework) is a penetration testing tool that focuses on the web browser, letting a tester assess the real security posture of a target by using client-side attack vectors instead of network-perimeter exploits.
- 71

Sublist3r
11.1Kaboul3la/Sublist3r · PythonSublist3r is a Python tool that enumerates subdomains of a target website using OSINT, helping penetration testers and bug hunters gather subdomains for a domain they are targeting.
- 72

LaZagne
11KAlessandroZ/LaZagne · PythonLaZagne is an open-source tool that retrieves passwords stored locally on a computer by reverse-engineering the storage method of each software (plaintext, APIs, custom algorithms, databases, etc.).
- 73

webshell
10.8Ktennc/webshell · PHPIt's a community collection of webshells - scripts that give you control of a web server once uploaded - covering all the common server-side languages and maintained by tennc with 10k+ stars.
- 74

Red-Teaming-Toolkit
10.8Kinfosecn1nja/Red-Teaming-ToolkitIt is a curated list of cutting-edge open-source security tools for red teamers and threat hunters, covering the full attack lifecycle from reconnaissance to exfiltration.
- 75

nikto
10.8Ksullo/nikto · PerlNikto is an open-source web server scanner that checks servers for dangerous files, outdated software versions, and other common vulnerabilities.
- 76
bbot
10.7Kblacklanternsecurity/bbot · PythonBBOT is a recursive internet scanner for hackers — it automates recon, bug bounty work and attack surface management (ASM), inspired by Spiderfoot.
- 77
httpx
10.5Kprojectdiscovery/httpx · Gohttpx is a fast, multi-purpose HTTP toolkit from ProjectDiscovery that runs many probes against lists of hosts and URLs, built on the retryablehttp library to stay reliable under high thread counts.
- 78

nishang
10.2Ksamratashok/nishang · PowerShellNishang is a framework and large collection of PowerShell scripts and payloads for offensive security, penetration testing, and red teaming, covering every phase of an engagement.
- 79
OneForAll
10.1Kshmilylty/OneForAll · PythonOneForAll is a powerful subdomain collection tool: point it at a target domain and it gathers subdomains from many sources — a core reconnaissance step in penetration testing, which is why the author built it.
- 80
flowsint
9.9Kreconurge/flowsint · TypeScriptFlowsint is an open-source, graph-based OSINT investigation tool that lets analysts explore relationships between people, domains, IPs, organizations and more through a visual graph interface with automated enrichers.
- 81
Cybersecurity-Projects
8.3KCarterPerez-dev/Cybersecurity-Projects · GoThis is a growing collection of 70 hands-on cybersecurity projects with full source code, organized into four difficulty tiers, plus 10 certification roadmaps and curated learning resources for cybersecurity careers.
- 82
Claude-Red
7.6KSnailSploit/Claude-Red · Pythonclaude-red is a curated library of offensive security skills for the Claude Skills system: structured SKILL.md files that prime Claude with expert-level methodology for one attack surface each, from SQLi to shellcode.
- 83

T3MP3ST
6.6Kelder-plinius/T3MP3ST · TypeScriptT3MP3ST is a multi-agent offensive-security framework that turns an AI coding agent you already use into an autonomous red-teaming operator. Point it at an authorized target and it runs the kill chain — recon, exploit, report — from a browser 'War Room' or the CLI.
- 84
Decepticon
6.3KBitterSecurity/Decepticon · PythonDecepticon is a professional autonomous Red Team agent that runs full attack chains — reconnaissance, exploitation, privilege escalation, lateral movement, and C2 — the way a real adversary would, instead of just scanning and printing a report.
- 85
user-scanner
5.4Kkaifcodec/user-scanner · PythonUser Scanner is an OSINT (open-source intelligence) CLI tool that takes an email address or username and scans it across 2720+ platforms (210+ email vectors, 2510+ username vectors) to map digital footprints, scrape profile metadata, and surface linked accounts.
- 86
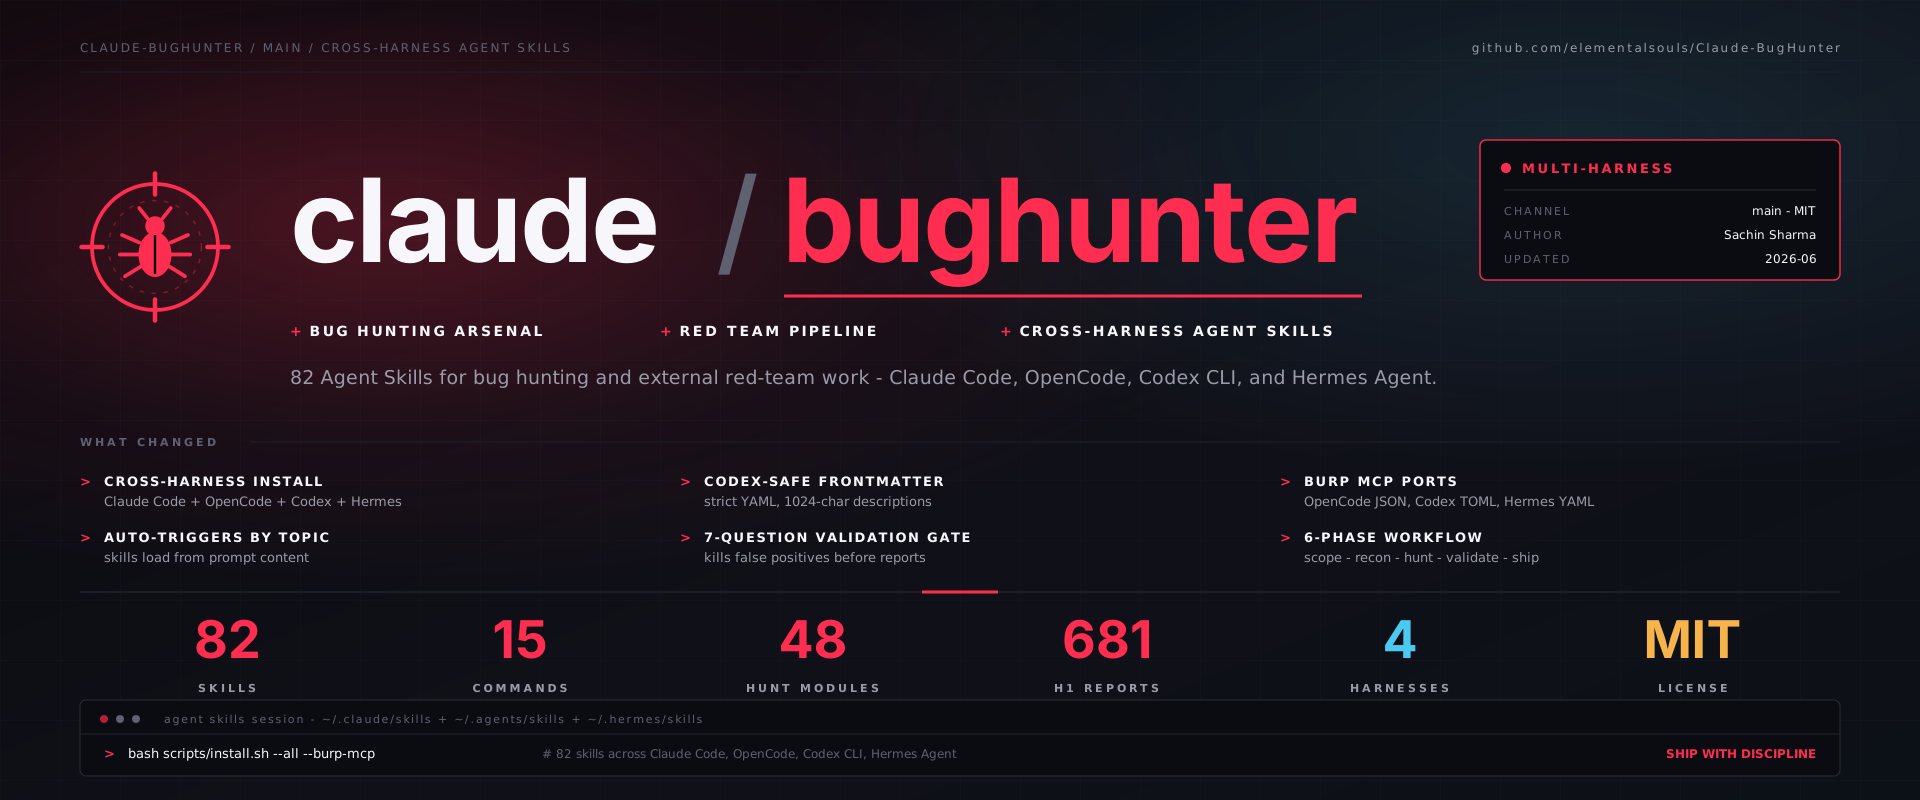
Claude-BugHunter
5.2Kelementalsouls/Claude-BugHunter · PythonA drop-in skill bundle for the Claude Code skills system that turns Claude into a bug-hunting researcher or red-team operator: it ships 83 skills, 15 slash commands, and knowledge curated from 681 disclosed HackerOne reports across 24 vulnerability classes, plus enterprise identity and infrastructure attack matrices.
- 87

exploitarium
5.2Kbikini/exploitarium · PythonExploitarium is a single consolidated archive of the author's public proof-of-concept exploits and vulnerability research writeups, merging dozens of their former standalone PoC repos into one place.
- 88
airgorah
4.5Kmartin-olivier/airgorah · RustAirgorah is a WiFi security auditing tool written in Rust that captures nearby WiFi traffic, discovers clients connected to access points, performs deauthentication attacks, captures handshakes and PMKIDs, and cracks access point passwords.
- 89
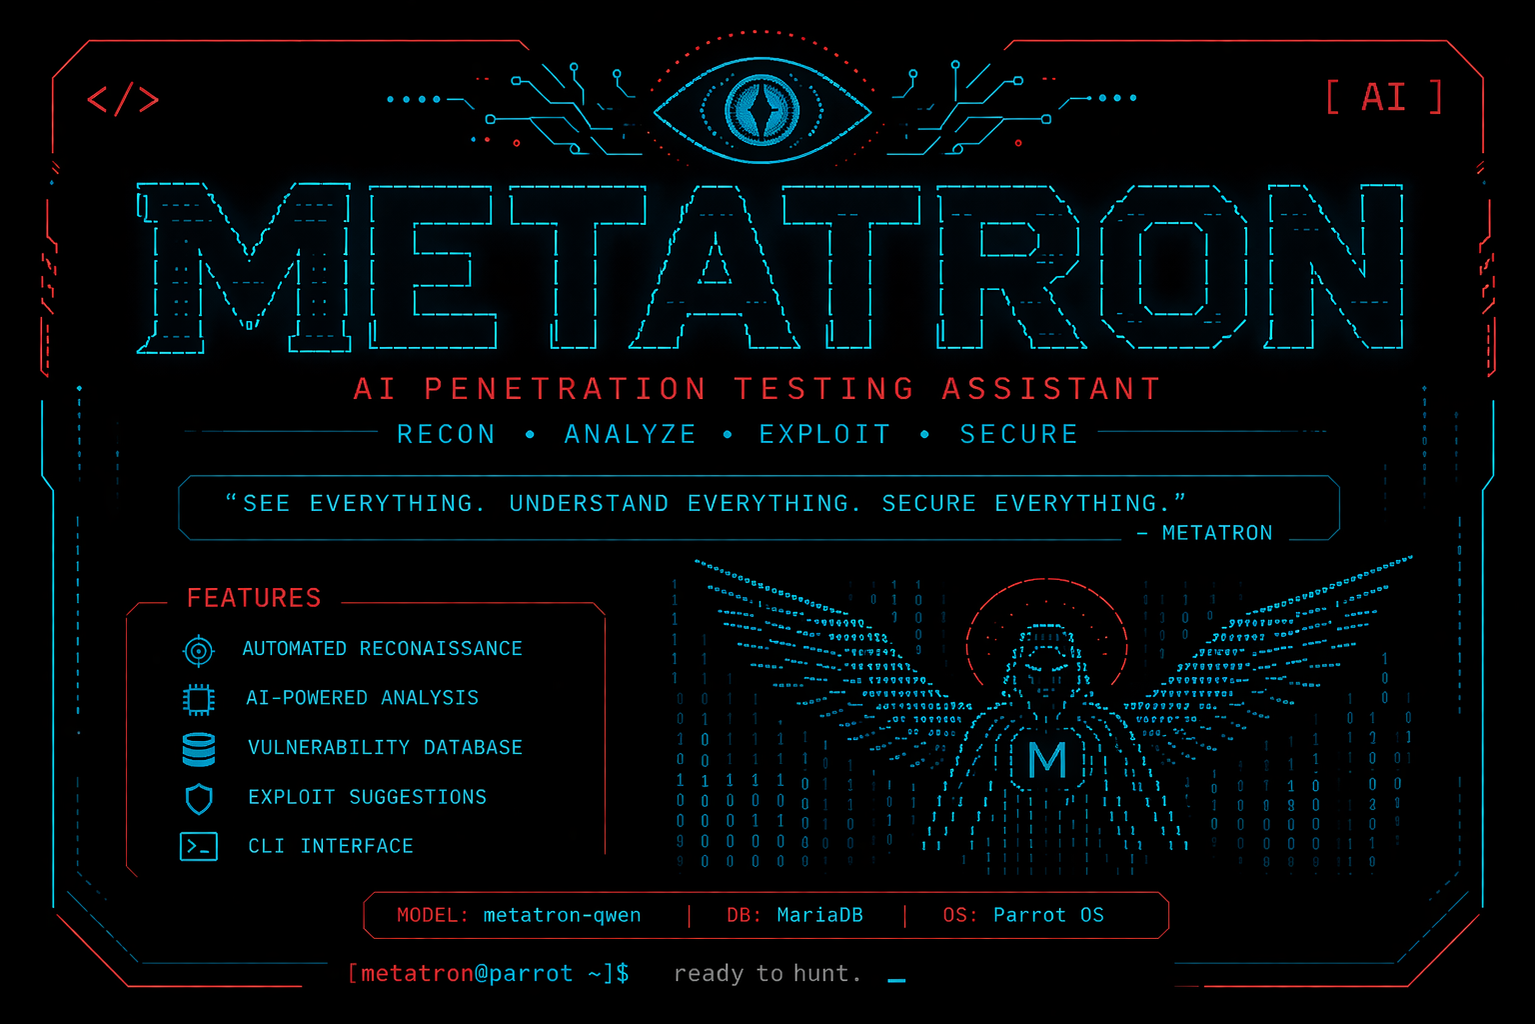
METATRON
4.2Ksooryathejas/METATRON · PythonMetatron is a CLI-based AI penetration testing assistant that runs real recon tools against a target and lets a locally-hosted LLM analyze the results, suggest exploits, and recommend fixes, with no cloud or API keys involved.
- 90

raptor
3.9Kgadievron/raptor · PythonRAPTOR turns a Claude Code session into an offensive/defensive security agent: Claude.md rules, sub-agents and skills orchestrate tools like radare2, Frida, Z3 and CodeQL for binary reverse-engineering, exploit-feasibility research, and software supply-chain (SCA) analysis.
- 91
redamon
3.2Ksamugit83/redamon · PythonRedAmon is an open-source, self-hosted AI framework that chains reconnaissance, exploitation and post-exploitation into one pipeline, maps the attack surface into a Neo4j graph, and then triages findings and opens GitHub pull requests that fix what it discovers.
- 92
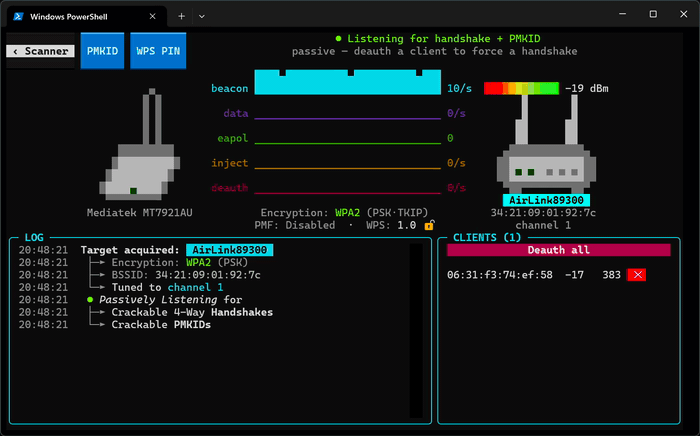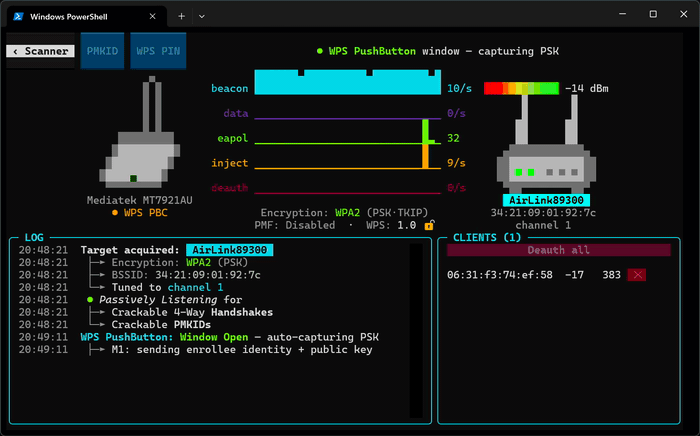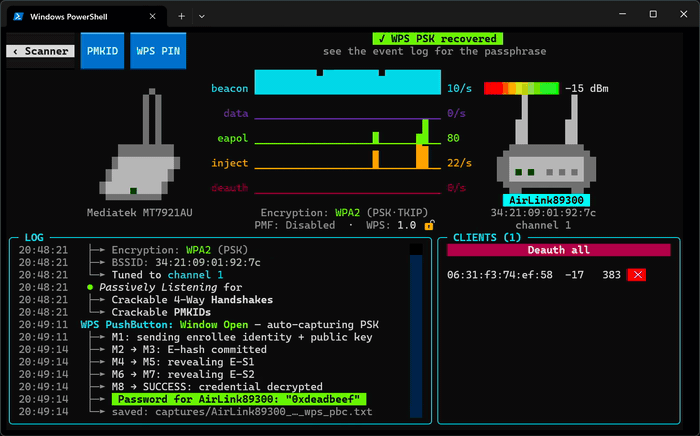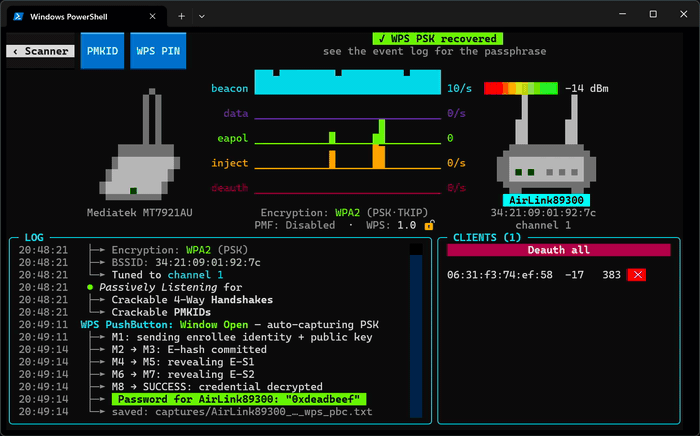
wifit3
2.6Kderv82/wifit3 · Pythonwifit3 is a standalone Wi-Fi security auditing tool that scans networks, captures WPA/WPA2 handshakes, and exploits WPS/WEP weaknesses using a supported USB Wi-Fi adapter, without relying on aircrack-ng or OS kernel drivers.
- 93

ghostlock-app
2.1KYuKongA/ghostlock-app · KotlinGhostLock is a one-tap Android app that runs the CVE-2026-43499 kernel exploit to grant uid 0 (root) on a matching vulnerable kernel, optionally loading a KernelSU-style module afterward.
- 94
Seep-Reverse-Lab
1.7Kangusdevgo/Seep-Reverse-Lab · LuaSeep Reverse Lab is an agent-native reverse engineering and security-audit workbench that lets an AI coding agent autonomously run Radare2, JADX, Apktool and Frida to triage binaries, decompile APKs, and determine whether an app's feature gates are enforced locally or verified by a server (a CWE-602 authorization audit).
- 95
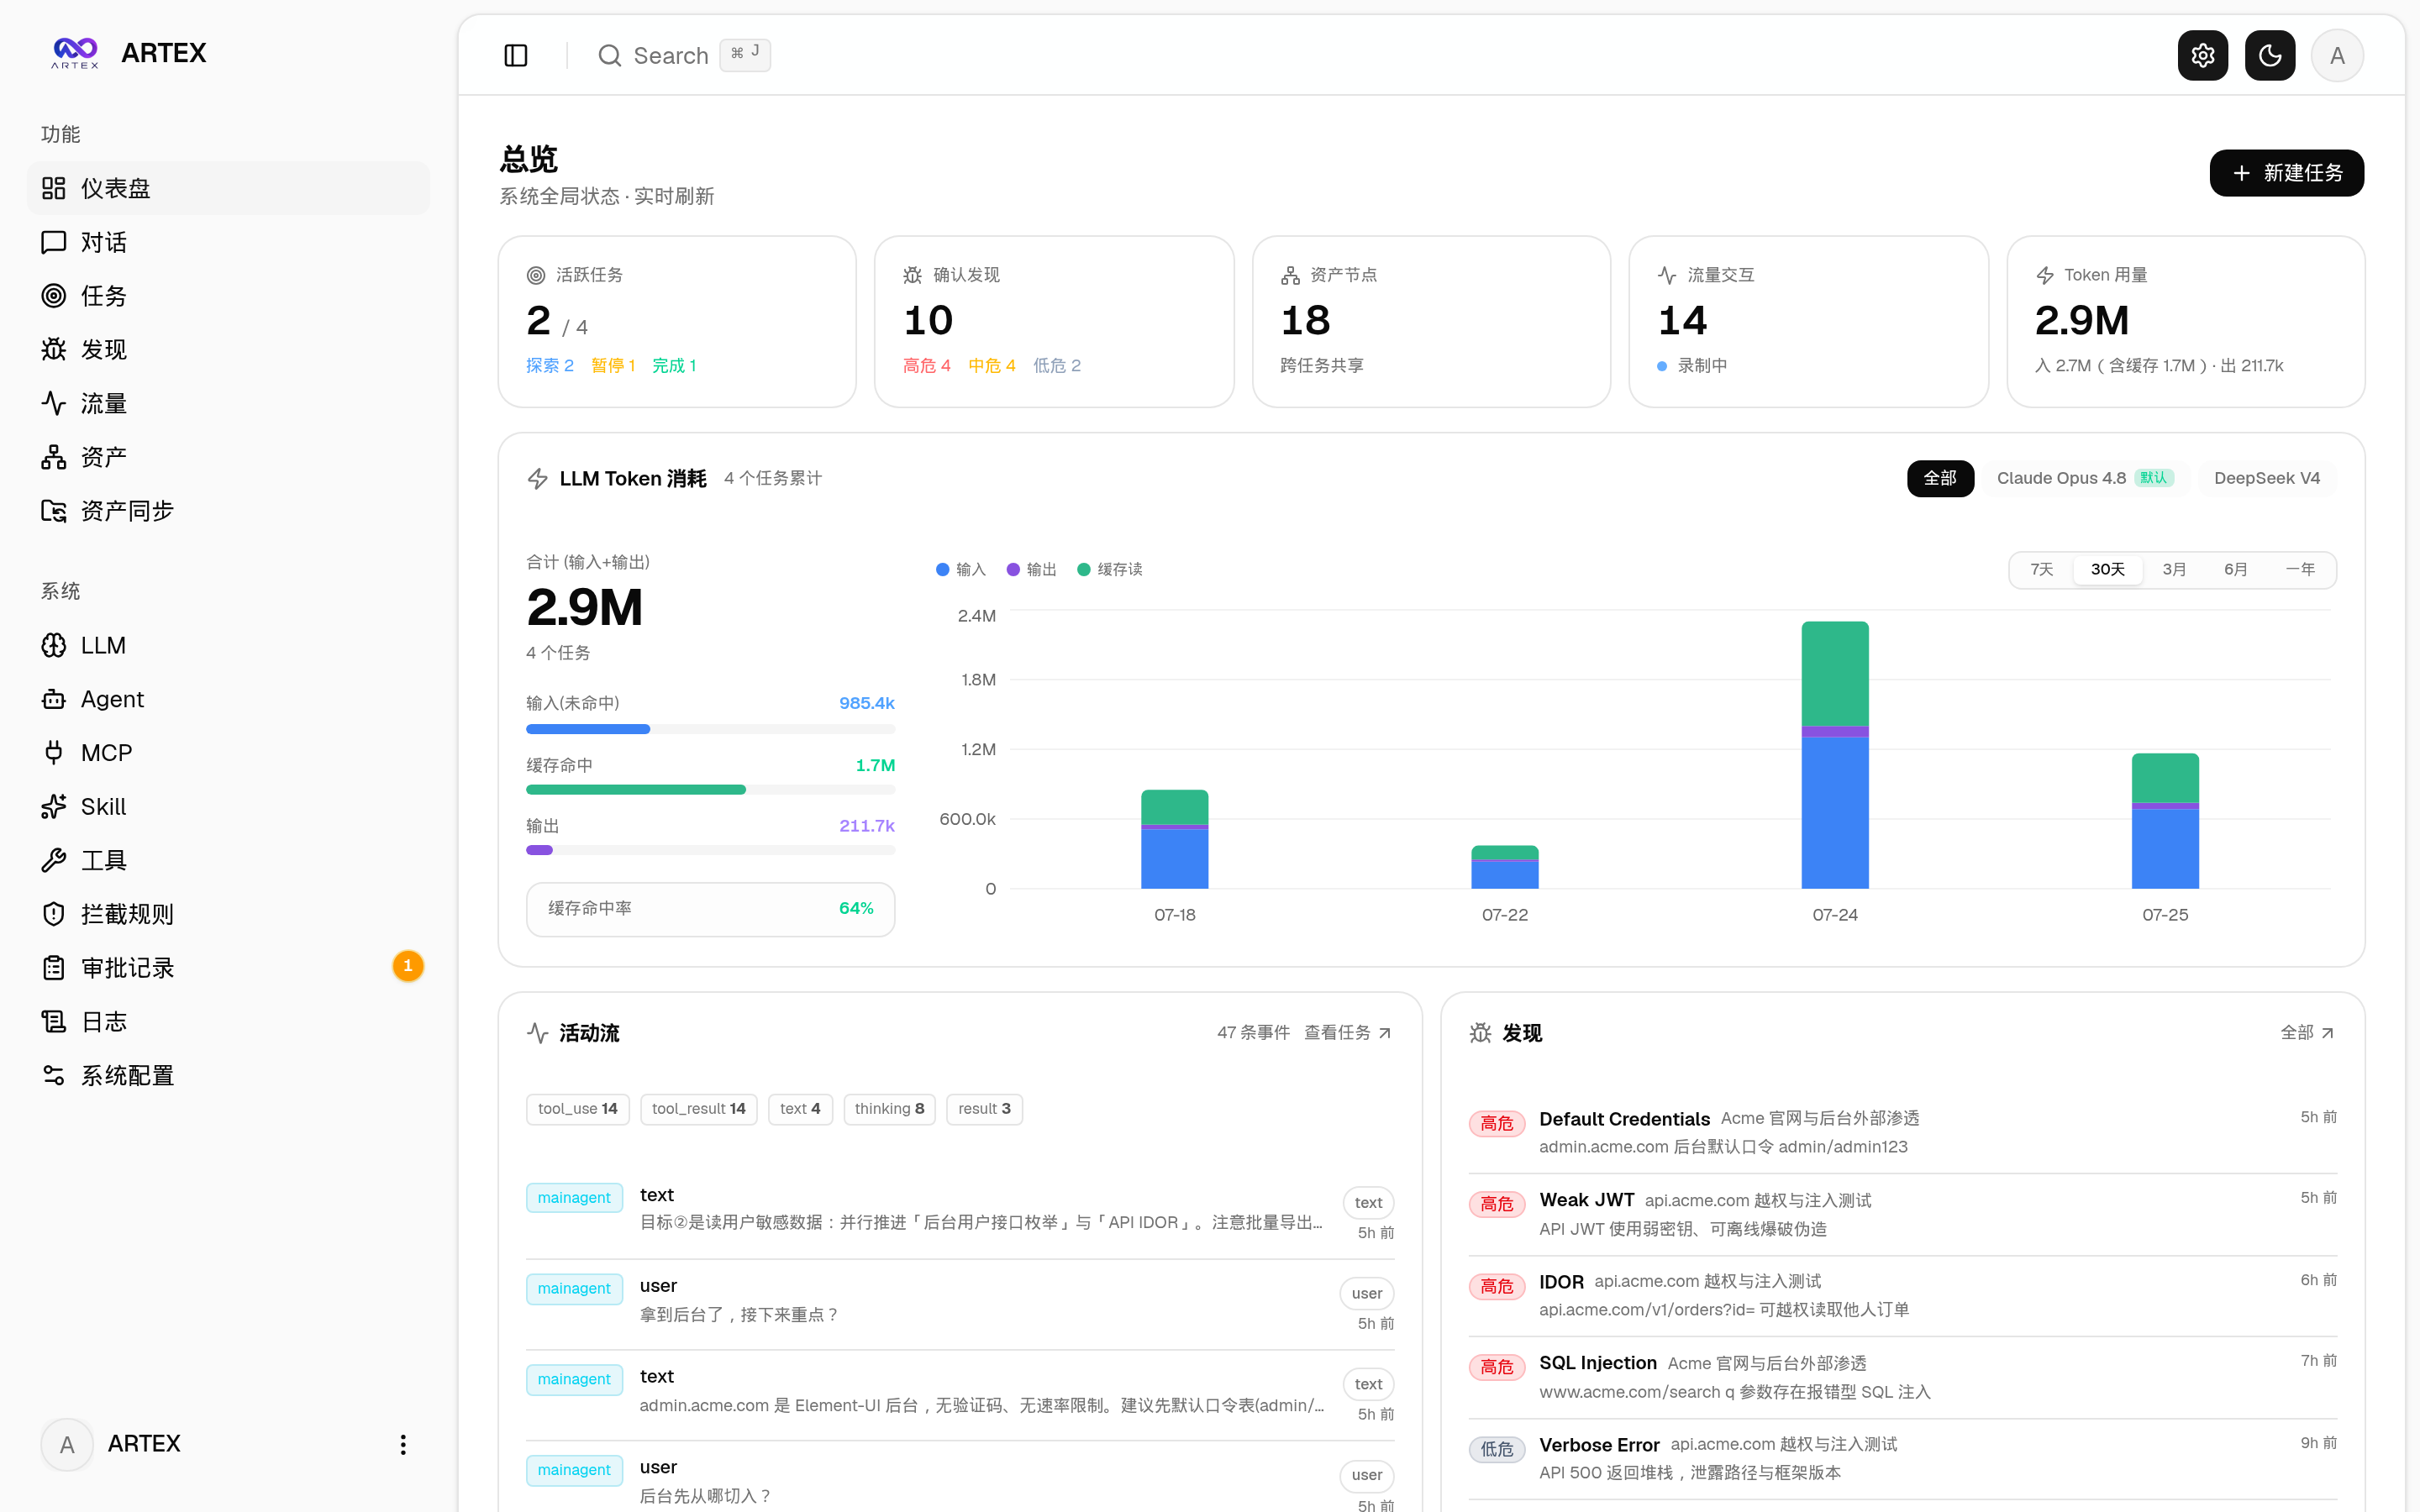
ARTEX
1.3Ktrhhubsd/ARTEX · GoARTEX is an AI-driven autonomous penetration testing system (Go backend + Next.js frontend) where LLM-powered planner and worker agents explore targets, map assets, and find vulnerabilities on their own.
- 96
Cybermes
949Zyrexnn/Cybermes · PythonCybermes is an offensive security assistant and automation framework for authorized bug bounty hunting, reconnaissance, vulnerability research, and structured reporting, driven by AI agents and a library of 200+ playbooks.
- 97
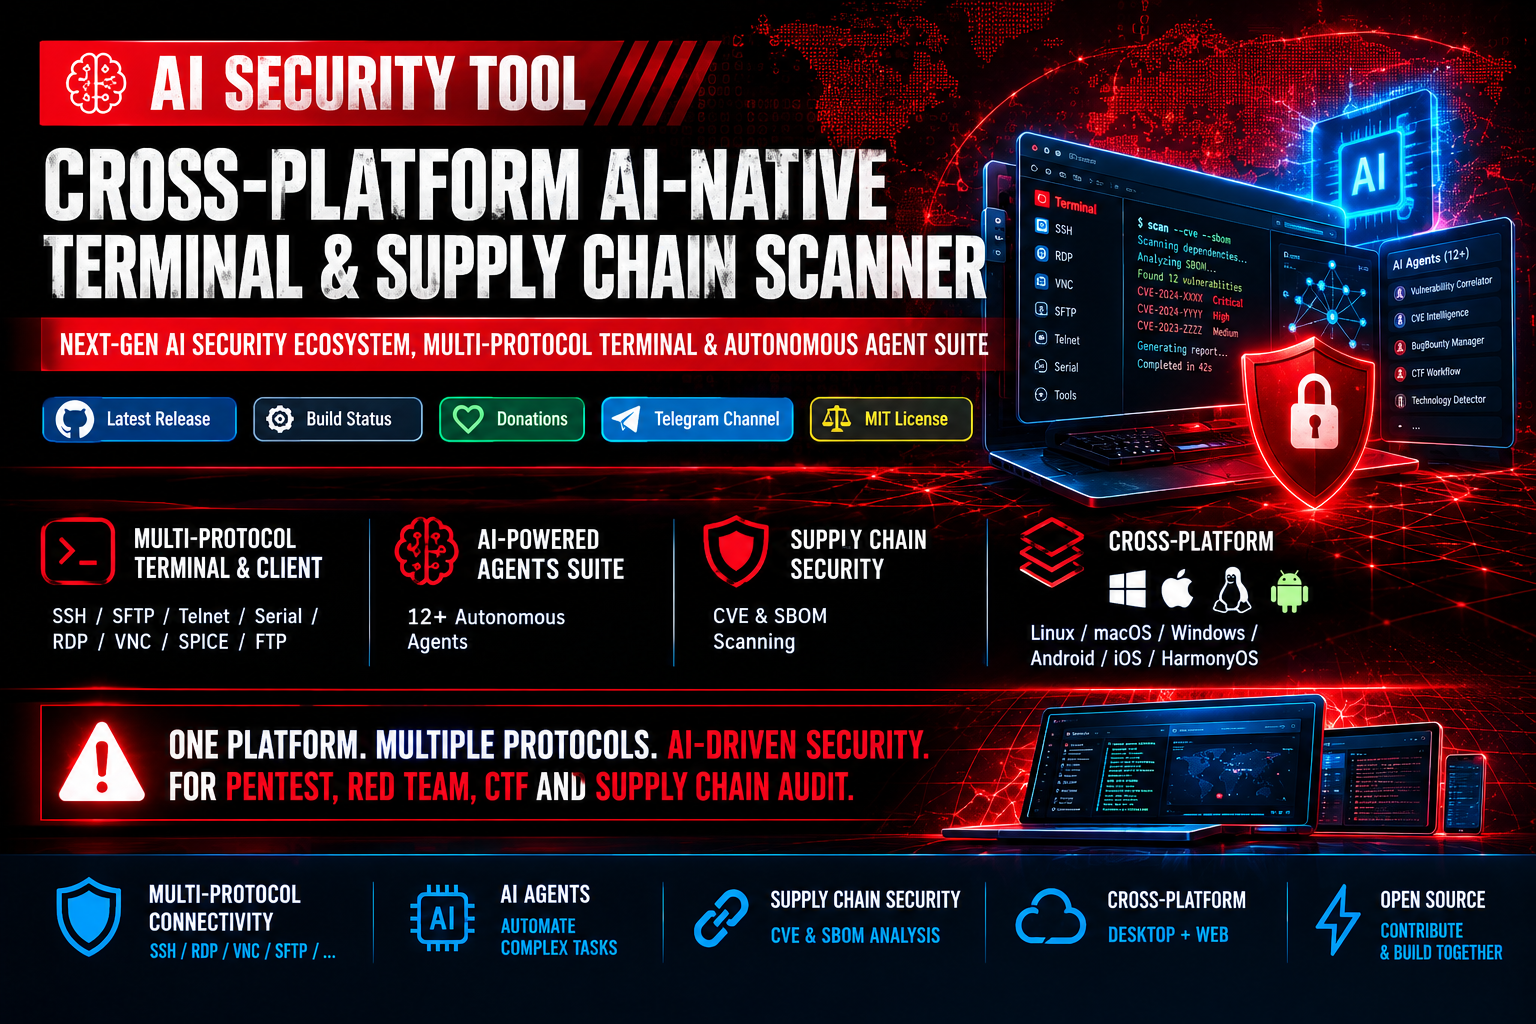
ai-security-tool
939ZeroDayEvil/ai-security-tool · HTMLAI Security Tool is an open-source, cross-platform terminal and vulnerability scanner that combines a multi-protocol connectivity client (SSH, RDP, VNC, etc.), CVE/SBOM supply-chain auditing, and 12+ autonomous AI agents (DeepSeek, OpenAI) to automate pentesting, Red Team, and CTF workflows.
- 98
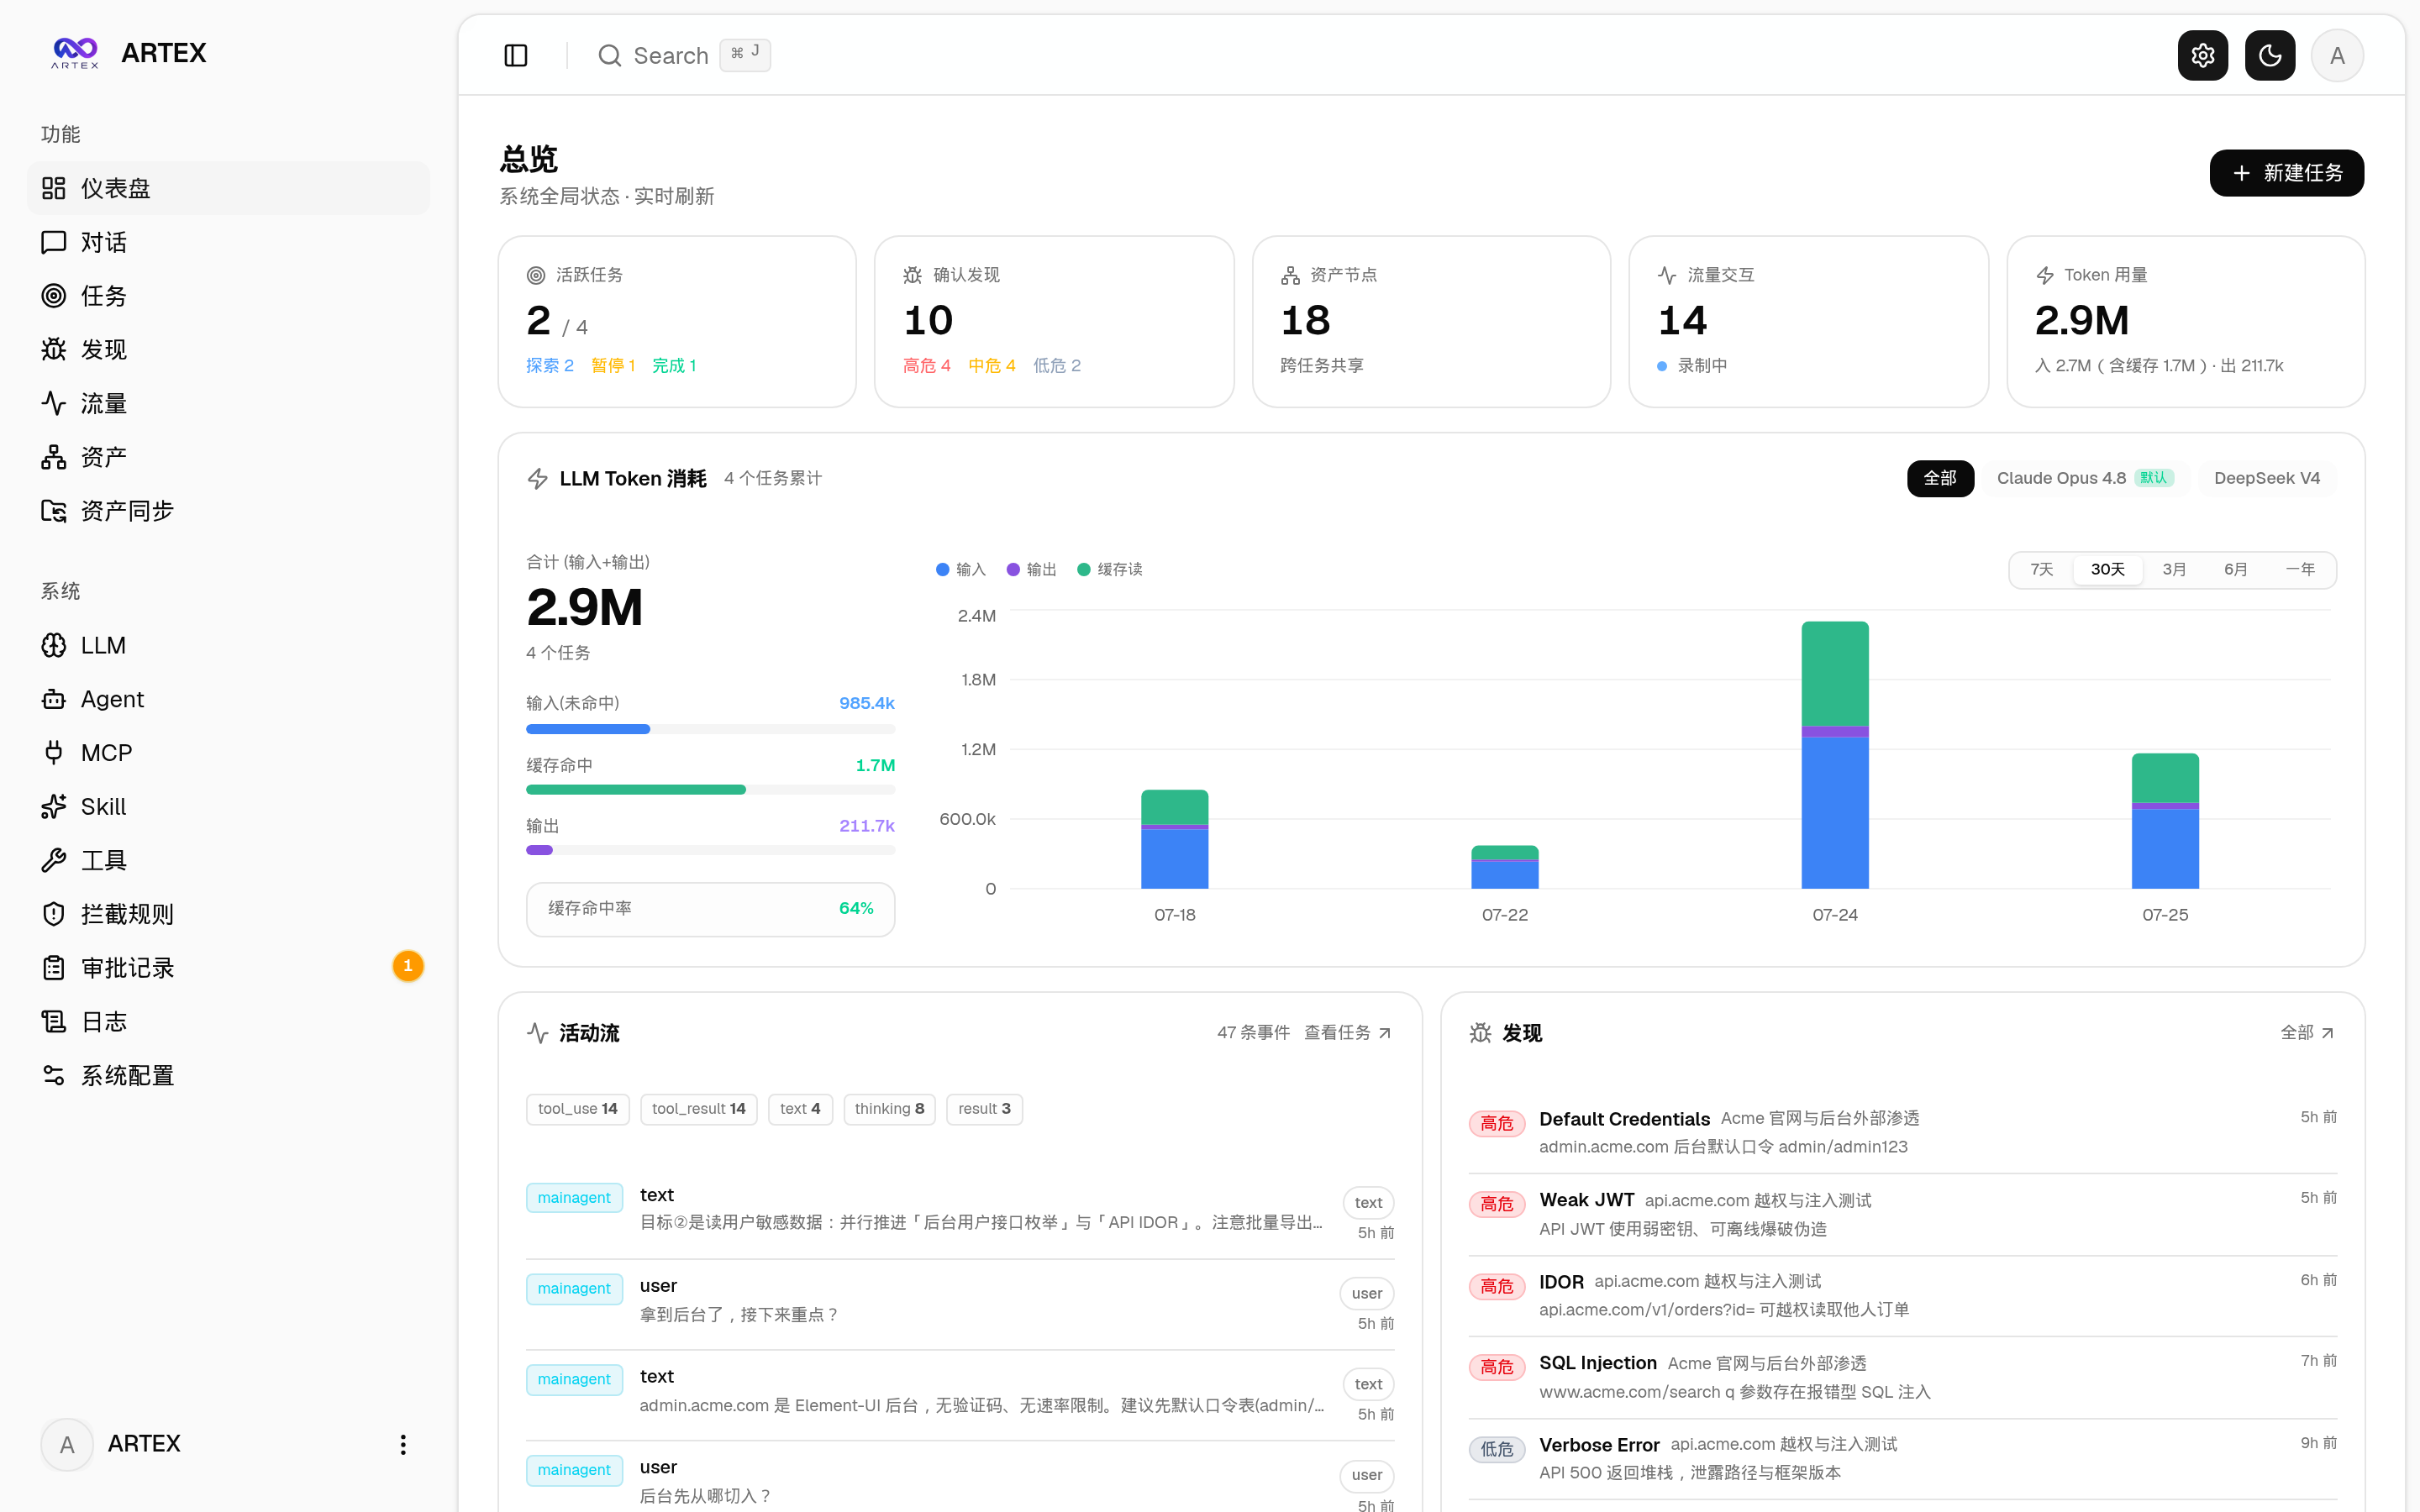
ARTEX
849Hinln/ARTEX · GoARTEX is an AI-driven autonomous penetration testing system with a Go backend and a Next.js frontend. It runs multiple LLM agents that explore a target, build an asset graph, and chain findings into vulnerabilities, all shown on a web dashboard.
- 99

VulnHunter
752nealbridges/VulnHunter · PythonAn open-source, agentic AI security scanner that reasons like an attacker to find exploitable vulnerabilities in source code, proves them with executable proof-of-concept exploits, and fixes them test-first. It is a maintained fork of Capital One's VulnHunter, rebuilt to run on any agent harness instead of just Claude Code.
- 100
BEAR-C2
704S3N4T0R-0X0/BEAR-C2 · PythonBEAR-C2 is an adversary simulation and emulation framework for red team operations, built around real-world TTPs inspired by Russian, Chinese, North Korean, and Iranian APT groups.
Showing the 100 most-starred of 114. See every one in the catalog.
Related topics
Often tagged together
- security1,006
- security-tools293
- cybersecurity253
- linux4,265
- penetration-testing130
- windows3,493
- hacking143
- macos3,624
- open-source5,768
- cli2,284
- offensive-security78
- python2,440
- red-team83
- docker1,686
- terminal1,136
- cross-platform2,682
- hacking-tool79
- mit3,401
- osint71
- infosec49
- reconnaissance41
- reverse-engineering241
- self-hosted1,985
- tool1,342