Topics / #offensive-security
Offensive-security projects on GitHub
Penetration testing and red-team tooling for probing systems.
As of , the most-starred Offensive-security projects on GitHub are PayloadsAllTheThings (81.8K stars), strix (69.1K stars) and x64dbg (49.9K stars). GitHub.Locker tracks 77 Offensive-security repositories with 1M stars combined. The fastest-growing on October 16 was pentagi, with +219 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
pentagi
vxcontrol/pentagi · ★ 30.8KPentAGI (Penetration testing Artificial General Intelligence) is a fully autonomous AI agent system that performs complex penetration testing tasks for you.
 +214
strix
usestrix/strix · ★ 69.1KStrix is an open-source tool that uses autonomous AI agents to pentest your application like real hackers: it runs your code dynamically, finds vulnerabilities, and proves them with working exploits instead of just flagging suspicious patterns.
 +81
shannon
KeygraphHQ/shannon · ★ 49KShannon is an autonomous AI pentester that analyzes your web application's source code, maps attack vectors, and then executes real exploits against the running app to prove vulnerabilities before they reach production — 'no exploit, no report'.
 +52
Relapse-Exploit
ntfargo/Relapse-Exploit · ★ 2.3KRelapse Exploit is a browser-based jailbreak chain for the PS5, working on firmware 7.00 through 13.60, that chains a WebKit browser exploit with a kernel exploit to gain kernel read/write and load custom payloads.
The all-time top
77 projects · by stars
- 81.8K
 #1 · swisskyrepo/PayloadsAllTheThings
PayloadsAllTheThings
A massive curated collection of payloads, bypass techniques, and exploitation methodology for web application security testing, pentesting, and CTF challenges.
- 69.1K#2 · usestrix/strix
strix
Strix is an open-source tool that uses autonomous AI agents to pentest your application like real hackers: it runs your code dynamically, finds vulnerabilities, and proves them with working exploits instead of just flagging suspicious patterns.
- 49.9K
 #3 · x64dbg/x64dbg
x64dbg
x64dbg is an open-source user-mode debugger for Windows, built specifically for reverse engineering and malware analysis.
- 4
shannon
49KKeygraphHQ/shannon · TypeScriptShannon is an autonomous AI pentester that analyzes your web application's source code, maps attack vectors, and then executes real exploits against the running app to prove vulnerabilities before they reach production — 'no exploit, no report'.
- 5

metasploit-framework
39.2Krapid7/metasploit-framework · RubyMetasploit Framework is an open-source penetration testing framework written in Ruby — one of the best-known security toolkits on GitHub, with about 39,000 stars.
- 6

sqlmap
38.7Ksqlmapproject/sqlmap · Pythonsqlmap is an open-source penetration testing tool that automates detecting and exploiting SQL injection flaws and taking over the underlying database server.
- 7
nuclei
32.1Kprojectdiscovery/nuclei · GoA fast, open-source vulnerability scanner that runs YAML-based templates to find security issues in applications, APIs, networks, DNS and cloud configurations. Its checks come from a large global security community.
- 8
pentagi
30.8Kvxcontrol/pentagi · GoPentAGI (Penetration testing Artificial General Intelligence) is a fully autonomous AI agent system that performs complex penetration testing tasks for you.
- 9

masscan
26.1Krobertdavidgraham/masscan · CMasscan is an Internet-scale TCP port scanner that transmits SYN packets asynchronously and can scan the entire IPv4 Internet in under 5 minutes, sending up to 10 million packets per second from a single machine.
- 10
unleashed-firmware
22.5KDarkFlippers/unleashed-firmware · CUnleashed is custom firmware for the Flipper Zero multitool — a fork of the official firmware (OFW) that adds extra features and improvements while staying compatible with official apps.
- 11

mimikatz
21.9Kgentilkiwi/mimikatz · CA small Windows security tool, originally written to learn C. It is best known for extracting plaintext passwords, hashes, PIN codes and Kerberos tickets from memory, and can perform pass-the-hash, pass-the-ticket or build Golden tickets.
- 12

L1B3RT4S
21.9Kelder-plinius/L1B3RT4SA public collection of jailbreak prompts — the author calls them 'liberation prompts' — meant to make flagship AI models respond without their usual refusals. It is maintained by AI red-teamer elder-plinius.
- 13

PEASS-ng
20.7Kpeass-ng/PEASS-ng · C#PEASS-ng is a suite of local privilege escalation enumeration tools: LinPEAS for Linux/Unix/macOS and WinPEAS for Windows. They scan a machine for privesc paths and print misconfigurations with nice colors so you can spot them easily.
- 14
SWE-agent
20.6KSWE-agent/SWE-agent · PythonSWE-agent takes a GitHub issue and tries to fix it automatically using the language model you choose. It can also tackle offensive cybersecurity (CTF) challenges or other custom tasks.
- 15
bettercap
20.1Kbettercap/bettercap · GoA portable all-in-one framework written in Go for recon and attacks on WiFi, Bluetooth Low Energy, wireless HID, CAN-bus and IPv4/IPv6 networks, built for security researchers and red teamers.
- 16

GHunt
19.7Kmxrch/GHunt · PythonGHunt is an offensive Google framework geared toward OSINT — collecting intelligence around Google — and its authors note that any Google-related use is possible.
- 17

Micro8
18KMicropoor/Micro8A free, open-source series of penetration-testing lessons written by veteran Chinese pentester Micropoor and published as a GitBook. It covers code audit, web, intranet and domain penetration, tunneling, and log-based tracing.
- 18

theHarvester
18Klaramies/theHarvester · PythonAn open-source OSINT tool that gathers emails, subdomains and names about a domain or organization from public sources: search engines, certificate transparency logs, DNS datasets, code repositories and threat-intel platforms, normalizing hostnames, emails, IPs, URLs, ASNs, people and breach names.
- 19
zphisher
17Khtr-tech/zphisher · HTMLZphisher is an automated phishing tool with 30+ ready-made login-page templates, written as a beginners-friendly shell script and intended purely for education.
- 20
ffuf
16.9Kffuf/ffuf · Goffuf is a fast web fuzzer written in Go — a command-line tool that sends many crafted requests to a target to discover directories, virtual hosts, and fuzzable GET/POST parameters.
- 21

MHDDoS
16.9KMatrixTM/MHDDoS · PythonMHDDoS is a Python 3 DDoS testing toolkit with 57 attack methods spanning Layer 7 (HTTP floods, Cloudflare/OVH bypasses) and Layer 4/3 (TCP, UDP, SYN, amplification attacks), meant for authorized security testing and research.
- 22

PentestGPT
16KGreyDGL/PentestGPT · PythonPentestGPT is an agentic framework that uses large language models to run automated penetration testing and solve CTF challenges, working through staged phases like recon, exploitation and reporting.
- 23
evilginx2
15.7Kkgretzky/evilginx2 · GoEvilginx is a man-in-the-middle attack framework used for phishing login credentials along with session cookies, which lets an attacker bypass 2-factor authentication.
- 24

social-engineer-toolkit
15.4Ktrustedsec/social-engineer-toolkit · PythonThe Social-Engineer Toolkit (SET) is an open-source penetration testing framework for authorized social-engineering assessments, giving security teams guided attack vectors to test user awareness and validate controls.
- 25

XSStrike
15.2Ks0md3v/XSStrike · PythonXSStrike is a Cross Site Scripting (XSS) detection suite built around four hand-written parsers, an intelligent payload generator, a fuzzing engine, and a fast crawler. Instead of just firing generic payloads like most scanners, it analyzes the live response and crafts payloads guaranteed to work through context analysis.
- 26
wifiphisher
14.9Kwifiphisher/wifiphisher · PythonWifiphisher is a rogue access point framework for conducting Wi-Fi phishing and man-in-the-middle attacks against wireless clients, used in red team and penetration testing engagements.
- 27
GTFOBins.github.io
13.8KGTFOBins/GTFOBins.github.io · YAMLGTFOBins is a curated list of Unix-like executables that can be abused to bypass local security restrictions in misconfigured systems — for example, binaries a restricted user can turn into a root shell.
- 28
mastg
13.3KOWASP/mastg · PythonA comprehensive OWASP manual for mobile app security testing and reverse engineering. It gives technical processes for verifying the weaknesses listed in the OWASP Mobile Security Weakness Enumeration (MASWE).
- 29

nuclei-templates
13.1Kprojectdiscovery/nuclei-templates · JavaScriptThis is a community-curated collection of over 11,000 detection templates for the Nuclei vulnerability scanner, covering CVEs, misconfigurations, exposed panels, and other security issues.
- 30

PowerSploit
13.1KPowerShellMafia/PowerSploit · PowerShellPowerSploit is a collection of PowerShell modules that penetration testers use during all phases of an assessment, covering code execution, persistence, privilege escalation, credential theft, exfiltration and reconnaissance on Windows systems.
- 31
hexstrike-ai
12.9K0x4m4/hexstrike-ai · PythonHexStrike AI MCP Agents is an MCP server that lets AI agents like Claude, GPT, or Copilot autonomously run 150+ real cybersecurity tools for automated pentesting, bug bounty hunting, CTF challenges, and vulnerability discovery.
- 32
ESP32Marauder
12.8Kjustcallmekoko/ESP32Marauder · C++ESP32 Marauder is a suite of offensive and defensive WiFi and Bluetooth tools that run as firmware on an ESP32 microcontroller, used for things like wardriving, scanning, and wireless security testing.
- 33
atomic-red-team
12.7Kredcanaryco/atomic-red-team · CAtomic Red Team is a library of small, portable security tests, each mapped to a specific MITRE ATT&CK technique, that security teams run to check whether their defenses actually detect real attacker behavior.
- 34

thc-hydra
12.4Kvanhauser-thc/thc-hydra · CHydra is a parallelized network login cracker by van Hauser / THC: a proof-of-concept tool showing researchers and security consultants how easily a remote system can be broken into through weak passwords. It supports over 50 protocols.
- 35

fsociety
12.3KManisso/fsociety · Pythonfsociety is a penetration testing toolkit that bundles dozens of existing hacking tools (Nmap, sqlmap, WPScan, Reaver, etc.) behind one menu-driven script, inspired by the tools used in the 'Mr. Robot' TV series.
- 36

sliver
12.1KBishopFox/sliver · GoSliver is an open source cross-platform adversary emulation and red team framework that organizations of any size can use to perform security testing.
- 37
xray
11.8Kchaitin/xray · Vuexray is a security assessment tool built by Chaitin for scanning common web vulnerabilities and running custom PoCs against targets.
- 38

TheFatRat
11.5Kscreetsec/TheFatRat · CTheFatRat is an exploiting tool that compiles malware from famous payloads — an easy way to generate backdoors built to slip past most anti-virus software.
- 39

webshell
10.8Ktennc/webshell · PHPIt's a community collection of webshells - scripts that give you control of a web server once uploaded - covering all the common server-side languages and maintained by tennc with 10k+ stars.
- 40

Red-Teaming-Toolkit
10.8Kinfosecn1nja/Red-Teaming-ToolkitIt is a curated list of cutting-edge open-source security tools for red teamers and threat hunters, covering the full attack lifecycle from reconnaissance to exfiltration.
- 41

nikto
10.8Ksullo/nikto · PerlNikto is an open-source web server scanner that checks servers for dangerous files, outdated software versions, and other common vulnerabilities.
- 42

BloodHound-Legacy
10.6KSpecterOps/BloodHound-Legacy · PowerShellBloodHound Legacy is a security tool that uses graph theory to map hidden relationships and attack paths inside an Active Directory environment, helping find the shortest route to Domain Admin — hence its tagline 'Six Degrees of Domain Admin'.
- 43

nishang
10.2Ksamratashok/nishang · PowerShellNishang is a framework and large collection of PowerShell scripts and payloads for offensive security, penetration testing, and red teaming, covering every phase of an engagement.
- 44

OneForAll
10.1Kshmilylty/OneForAll · PythonOneForAll is a powerful subdomain collection tool: point it at a target domain and it gathers subdomains from many sources — a core reconnaissance step in penetration testing, which is why the author built it.
- 45

Claude-Red
7.6KSnailSploit/Claude-Red · Pythonclaude-red is a curated library of offensive security skills for the Claude Skills system: structured SKILL.md files that prime Claude with expert-level methodology for one attack surface each, from SQLi to shellcode.
- 46
T3MP3ST
6.5Kelder-plinius/T3MP3ST · TypeScriptT3MP3ST is a multi-agent offensive-security framework that turns an AI coding agent you already use into an autonomous red-teaming operator. Point it at an authorized target and it runs the kill chain — recon, exploit, report — from a browser 'War Room' or the CLI.
- 47
Decepticon
6.2KBitterSecurity/Decepticon · PythonDecepticon is a professional autonomous Red Team agent that runs full attack chains — reconnaissance, exploitation, privilege escalation, lateral movement, and C2 — the way a real adversary would, instead of just scanning and printing a report.
- 48

exploitarium
5.2Kbikini/exploitarium · PythonExploitarium is a single consolidated archive of the author's public proof-of-concept exploits and vulnerability research writeups, merging dozens of their former standalone PoC repos into one place.
- 49

Claude-BugHunter
5.1Kelementalsouls/Claude-BugHunter · PythonA drop-in skill bundle for the Claude Code skills system that turns Claude into a bug-hunting researcher or red-team operator: it ships 83 skills, 15 slash commands, and knowledge curated from 681 disclosed HackerOne reports across 24 vulnerability classes, plus enterprise identity and infrastructure attack matrices.
- 50
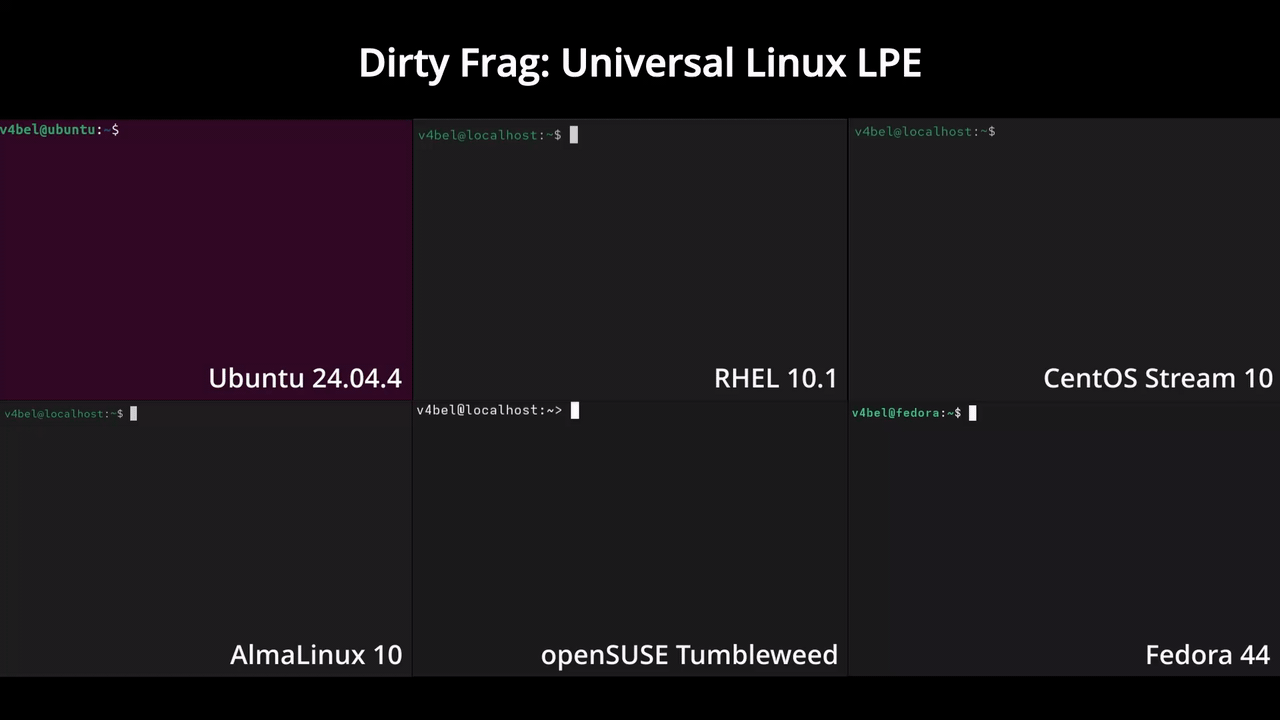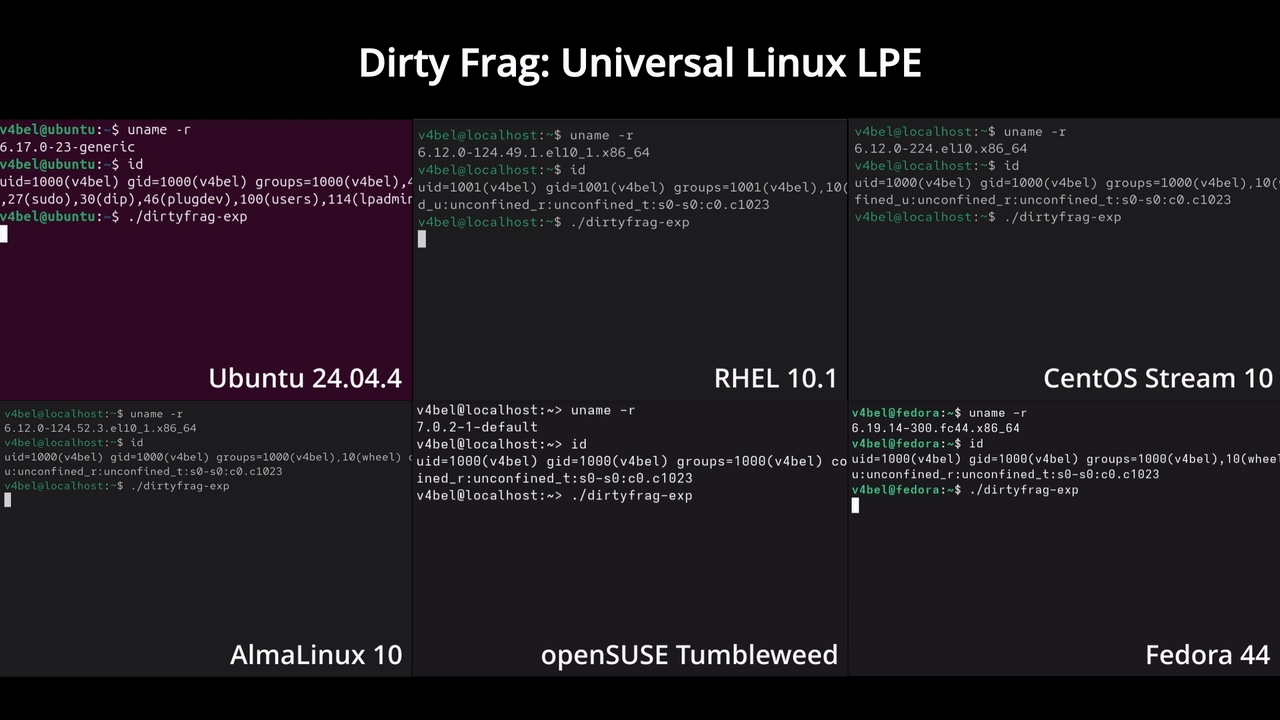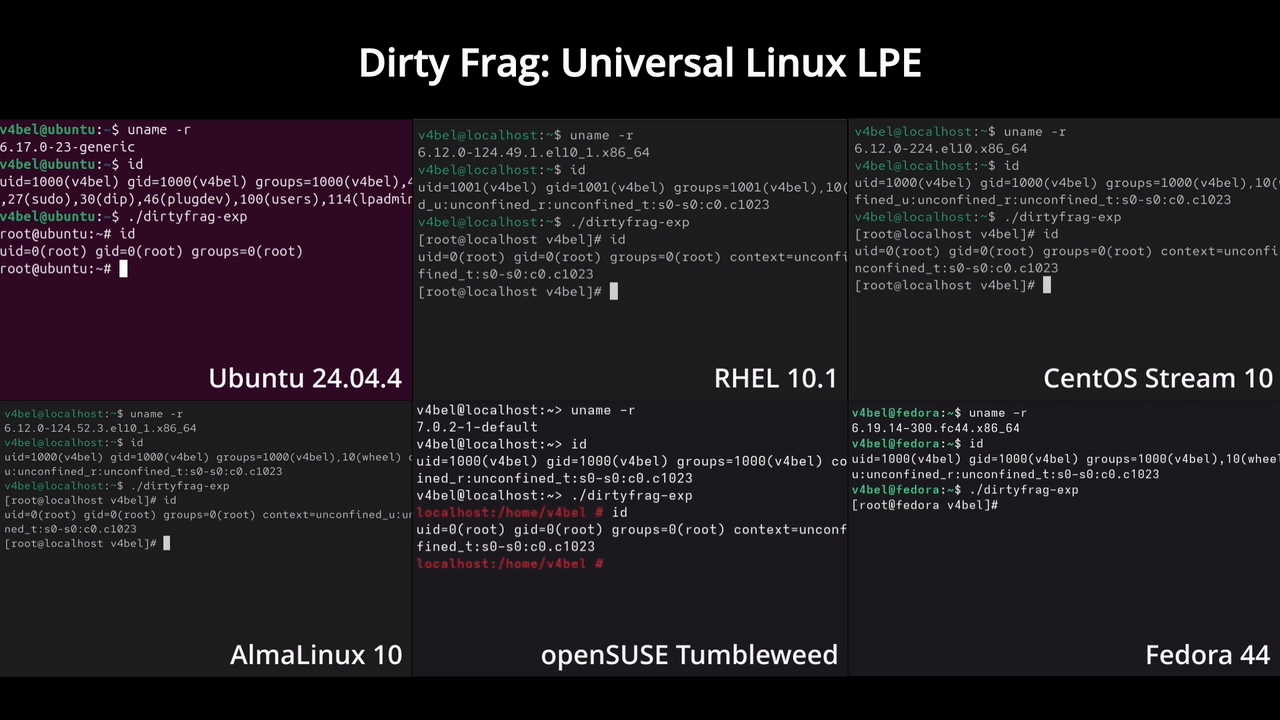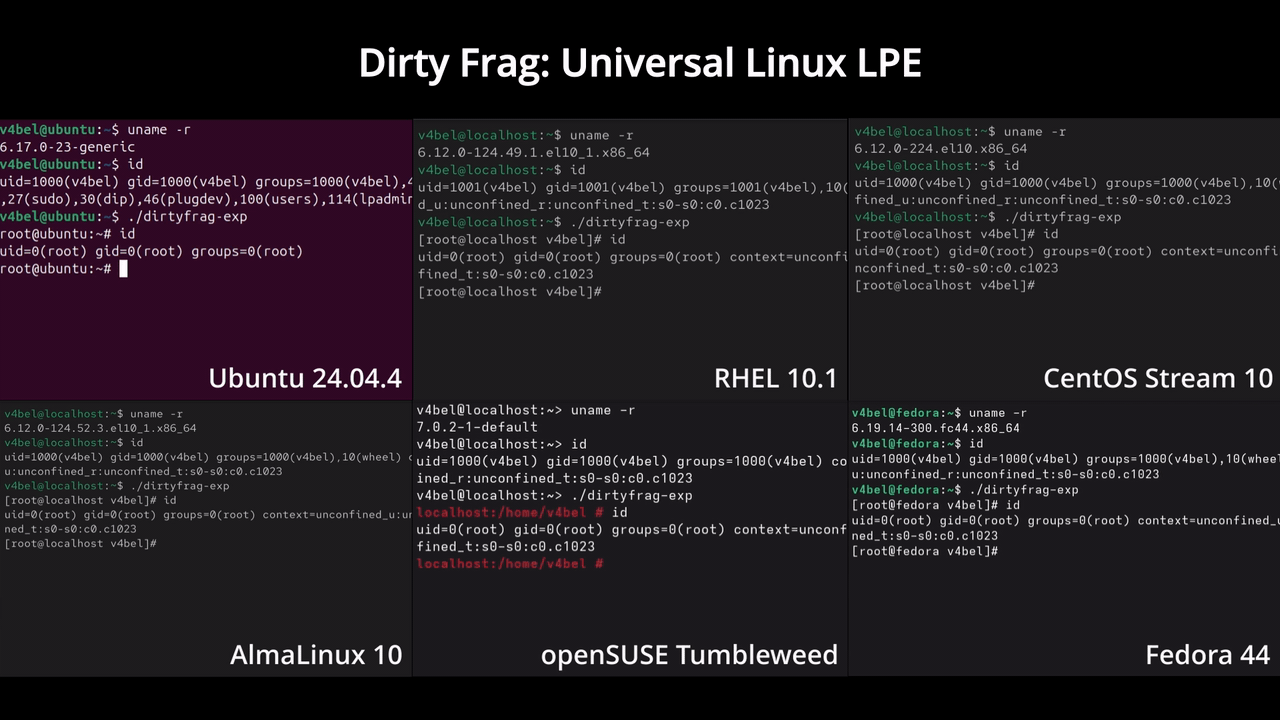
dirtyfrag
5.1KV4bel/dirtyfrag · CDirty Frag is a proof-of-concept Linux kernel local privilege escalation exploit that chains two page-cache write vulnerabilities (CVE-2026-43284 and CVE-2026-43500) to obtain root on major Linux distributions.
- 51
airgorah
4.2Kmartin-olivier/airgorah · RustAirgorah is a WiFi security auditing tool written in Rust that captures nearby WiFi traffic, discovers clients connected to access points, performs deauthentication attacks, captures handshakes and PMKIDs, and cracks access point passwords.
- 52

copy-fail-CVE-2026-31431
4.1Ktheori-io/copy-fail-CVE-2026-31431 · PythonThis repository is a technical writeup and proof-of-concept for CVE-2026-31431, a 9-year-old Linux kernel local privilege escalation (LPE) vulnerability found by Theori's AI vulnerability research tool, Xint Code.
- 53

raptor
3.9Kgadievron/raptor · PythonRAPTOR turns a Claude Code session into an offensive/defensive security agent: Claude.md rules, sub-agents and skills orchestrate tools like radare2, Frida, Z3 and CodeQL for binary reverse-engineering, exploit-feasibility research, and software supply-chain (SCA) analysis.
- 54
redamon
3.1Ksamugit83/redamon · PythonRedAmon is an open-source, self-hosted AI framework that chains reconnaissance, exploitation and post-exploitation into one pipeline, maps the attack surface into a Neo4j graph, and then triages findings and opens GitHub pull requests that fix what it discovers.
- 55
Pentest-Swarm-AI
3KArmur-Ai/Pentest-Swarm-AI · GoPentest Swarm AI is an open-source, self-hosted penetration testing tool where dozens of AI agents work as a swarm to recon, classify, exploit, and report vulnerabilities in APIs and web apps — not just scan for them.
- 56
Relapse-Exploit
2.3Kntfargo/Relapse-Exploit · JavaScriptRelapse Exploit is a browser-based jailbreak chain for the PS5, working on firmware 7.00 through 13.60, that chains a WebKit browser exploit with a kernel exploit to gain kernel read/write and load custom payloads.
- 57
skitter-creek-bath-salts
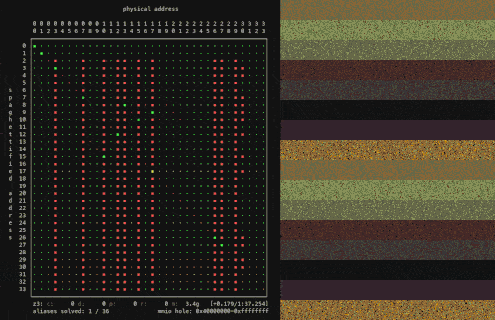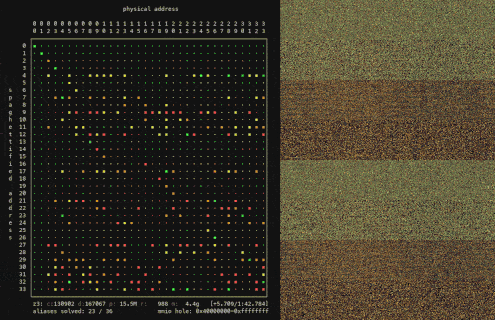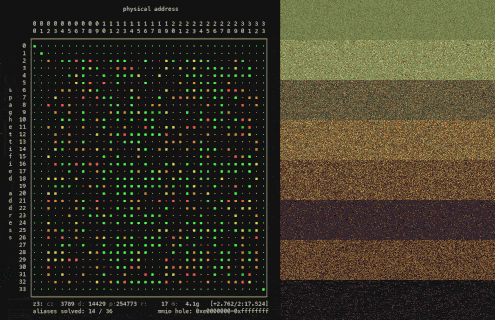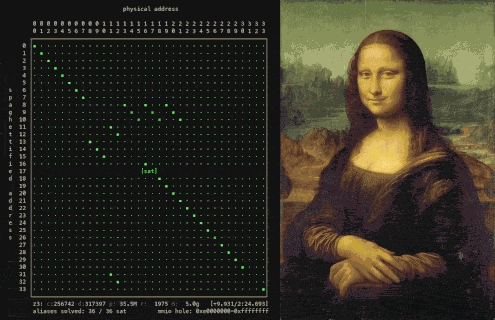
2.1Kxoreaxeaxeax/skitter-creek-bath-salts · CA security research project that shows how to unlock protected regions on an AMD CPU — the Platform Security Processor, System Management Mode, C6 DRAM, and CPU microcode — by scrambling the DRAM controller's physical-to-DRAM address translation.
- 58

ghostlock-app
2KYuKongA/ghostlock-app · KotlinGhostLock is a one-tap Android app that runs the CVE-2026-43499 kernel exploit to grant uid 0 (root) on a matching vulnerable kernel, optionally loading a KernelSU-style module afterward.
- 59
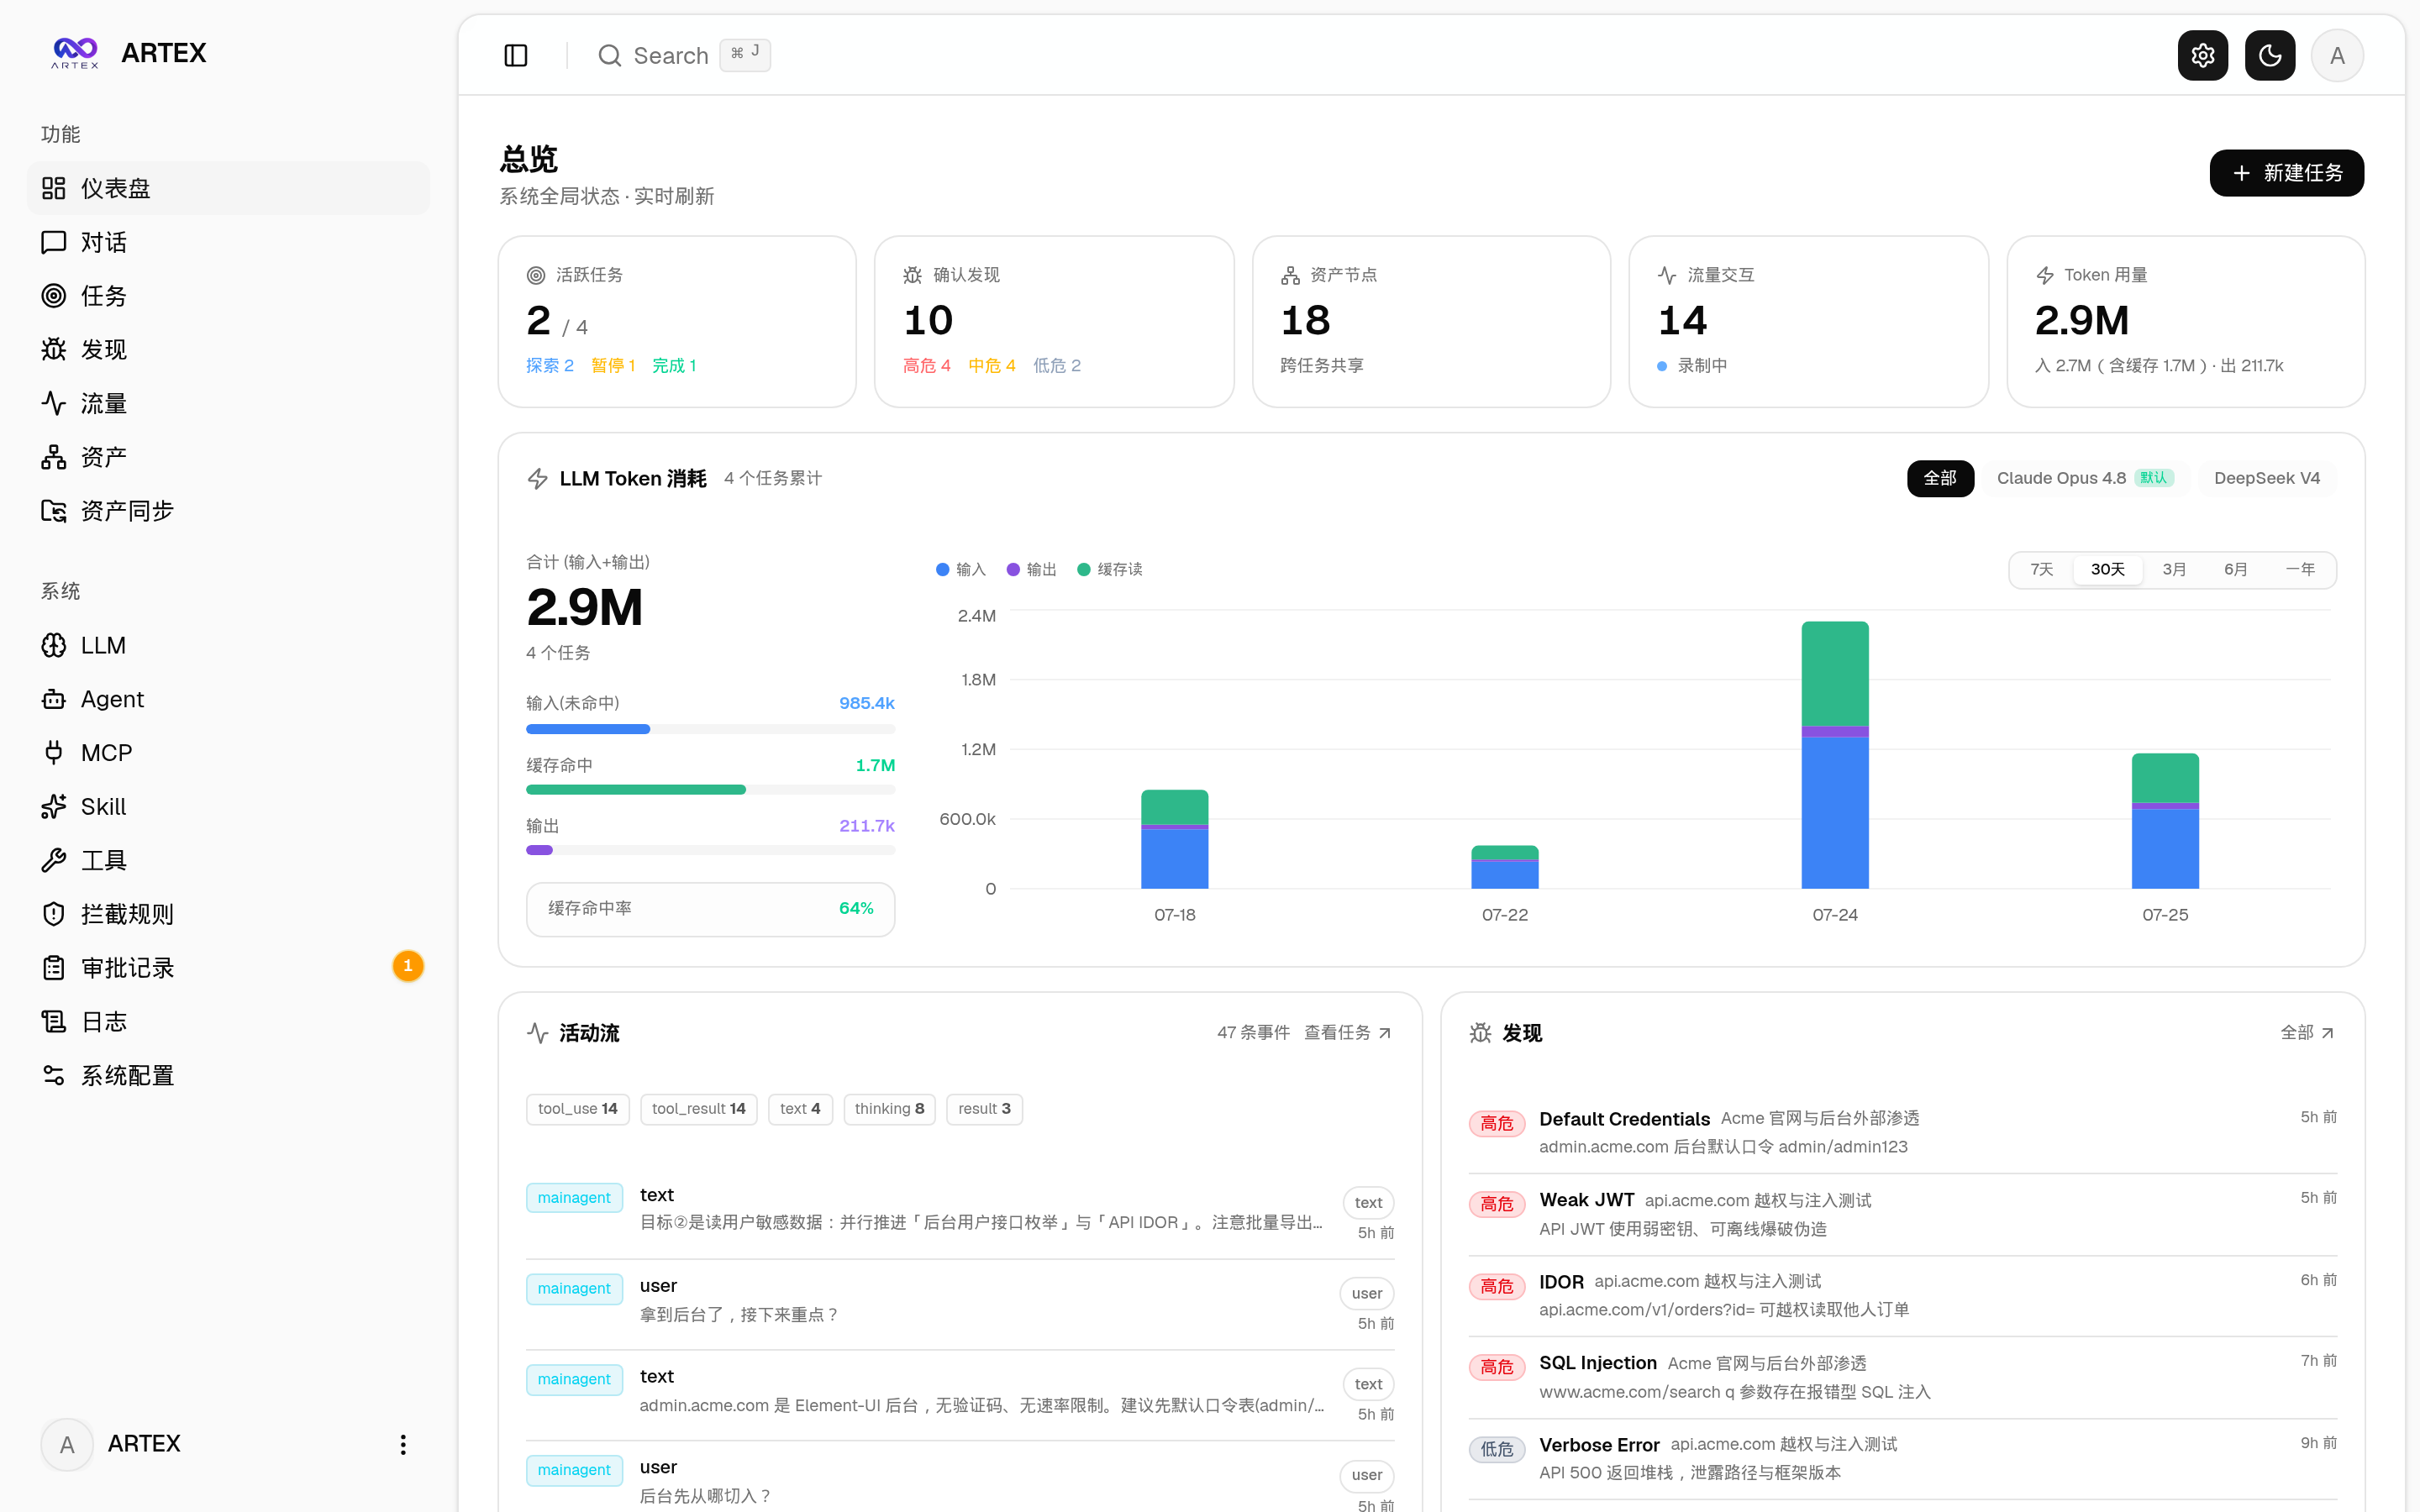
ARTEX
1.2Ktrhhubsd/ARTEX · GoARTEX is an AI-driven autonomous penetration testing system (Go backend + Next.js frontend) where LLM-powered planner and worker agents explore targets, map assets, and find vulnerabilities on their own.
- 60
Cybermes
946Zyrexnn/Cybermes · PythonCybermes is an offensive security assistant and automation framework for authorized bug bounty hunting, reconnaissance, vulnerability research, and structured reporting, driven by AI agents and a library of 200+ playbooks.
- 61
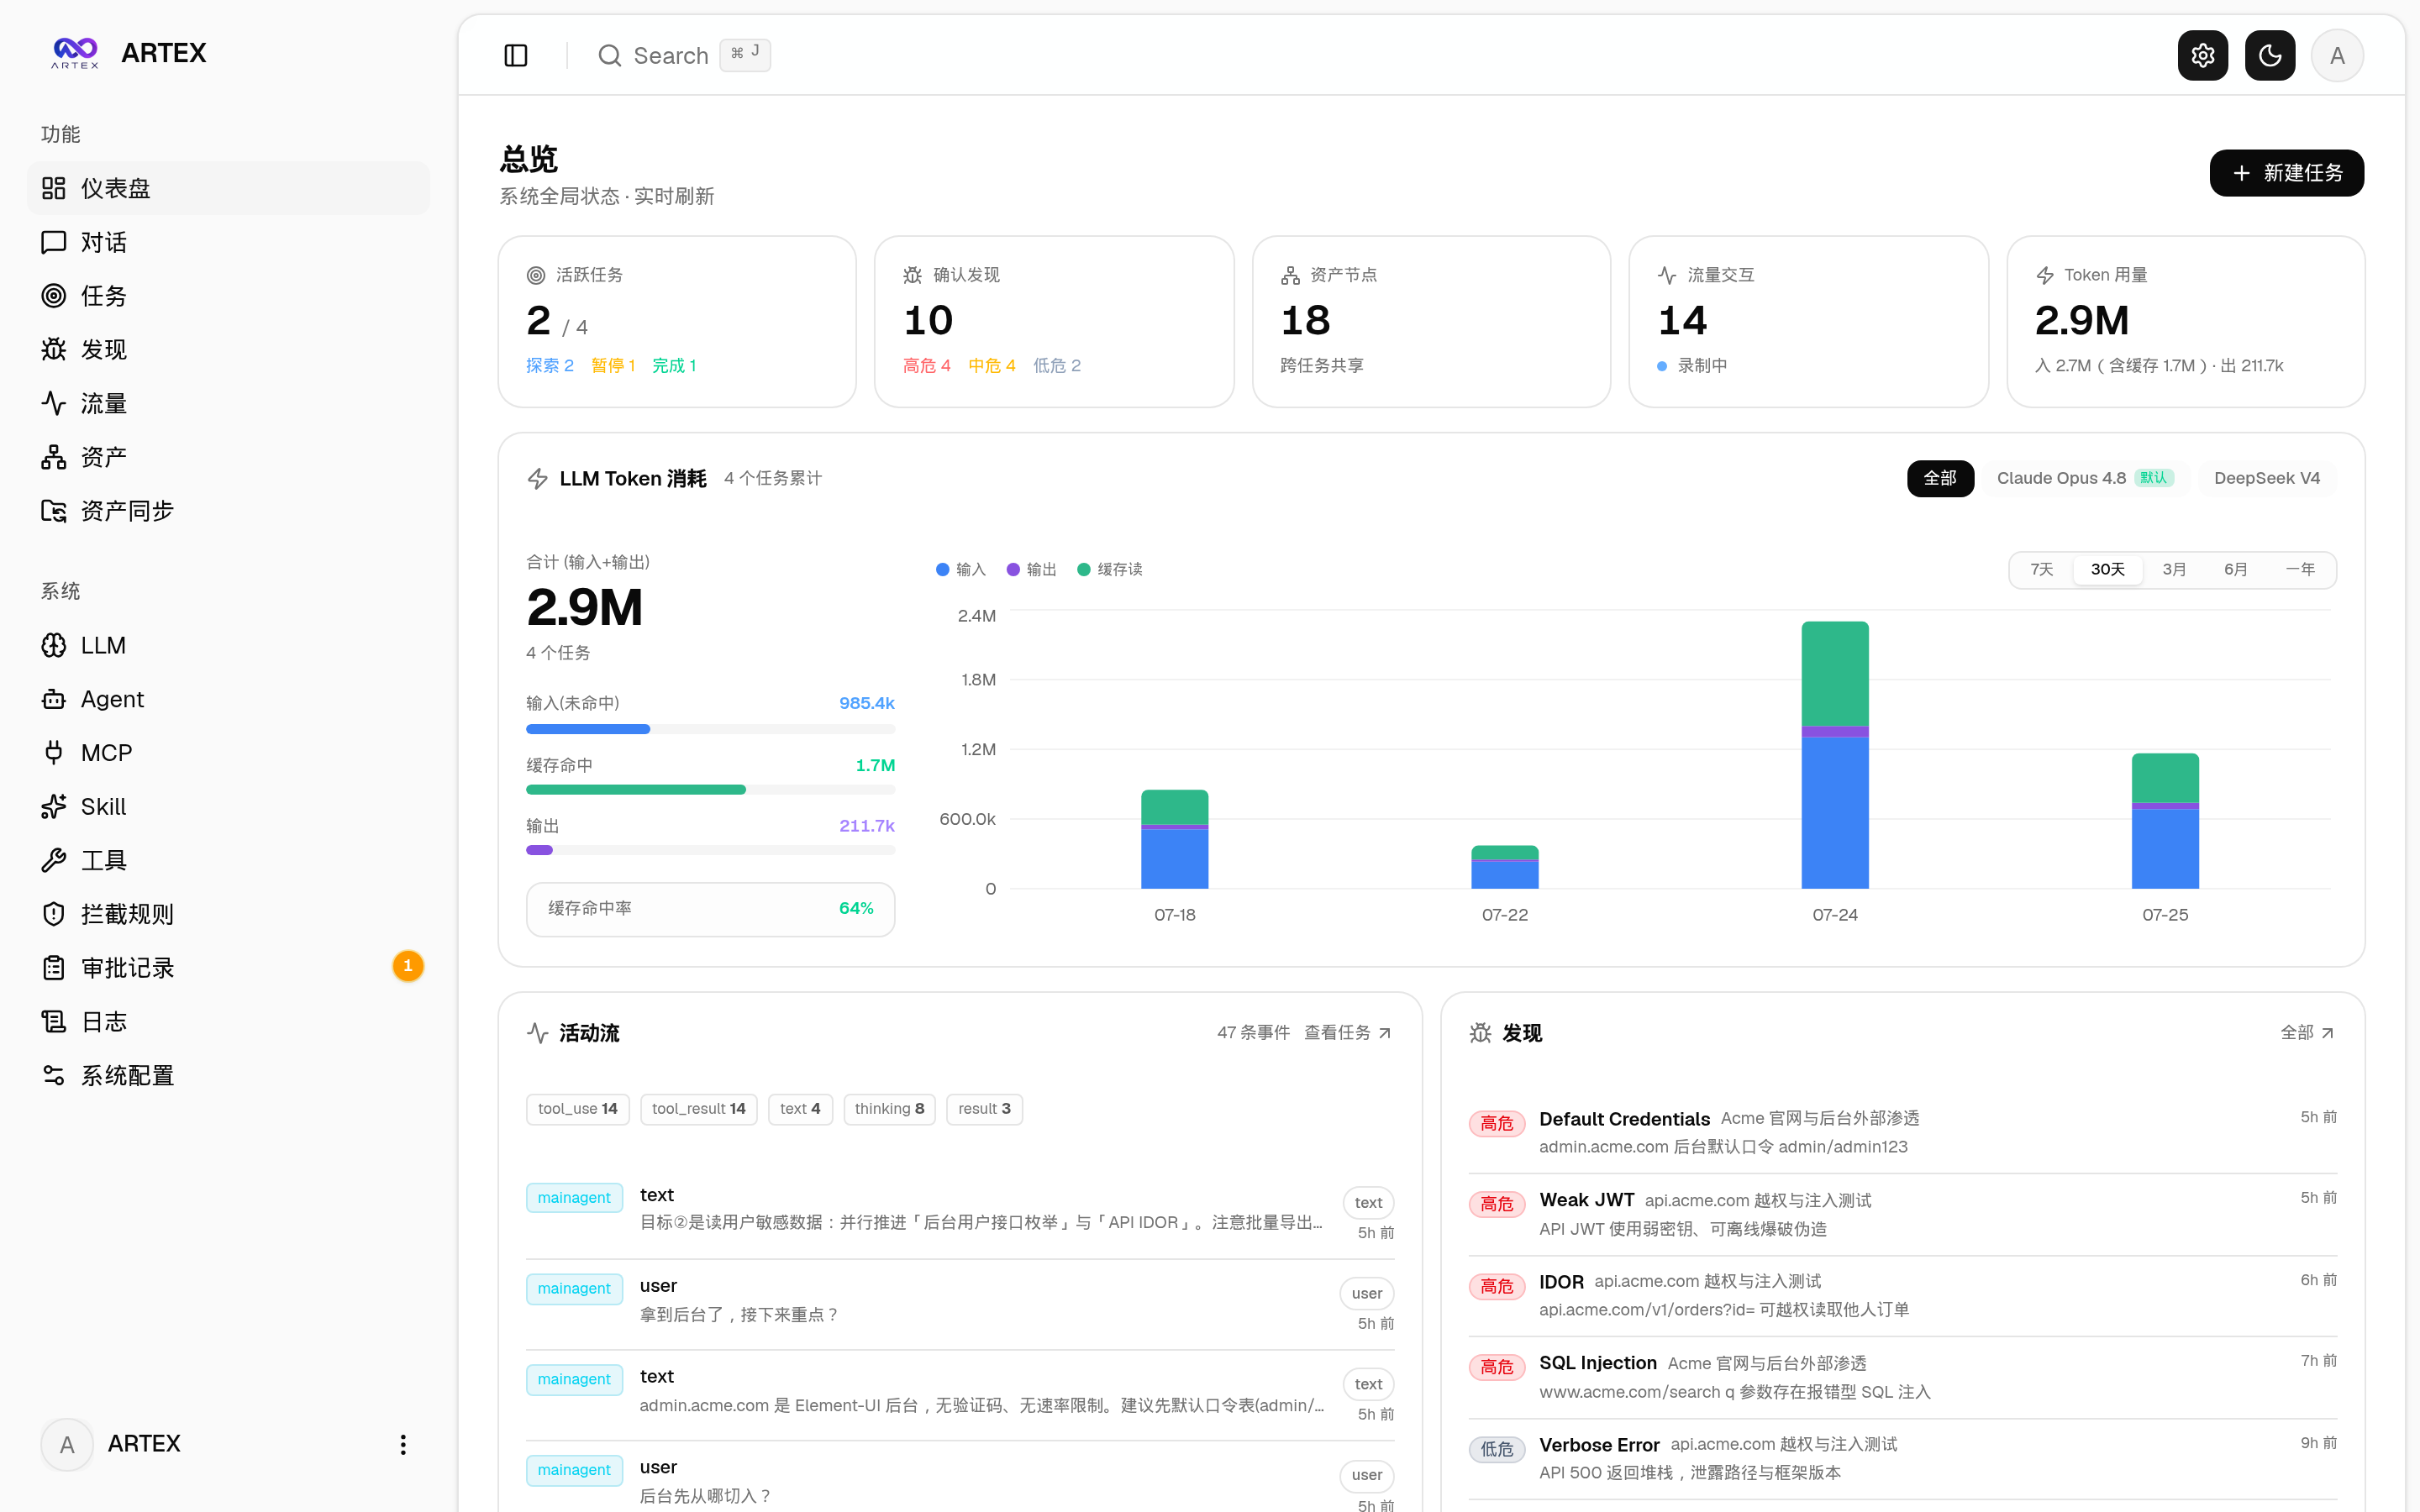
ARTEX
777Hinln/ARTEX · GoARTEX is an AI-driven autonomous penetration testing system with a Go backend and a Next.js frontend. It runs multiple LLM agents that explore a target, build an asset graph, and chain findings into vulnerabilities, all shown on a web dashboard.
- 62
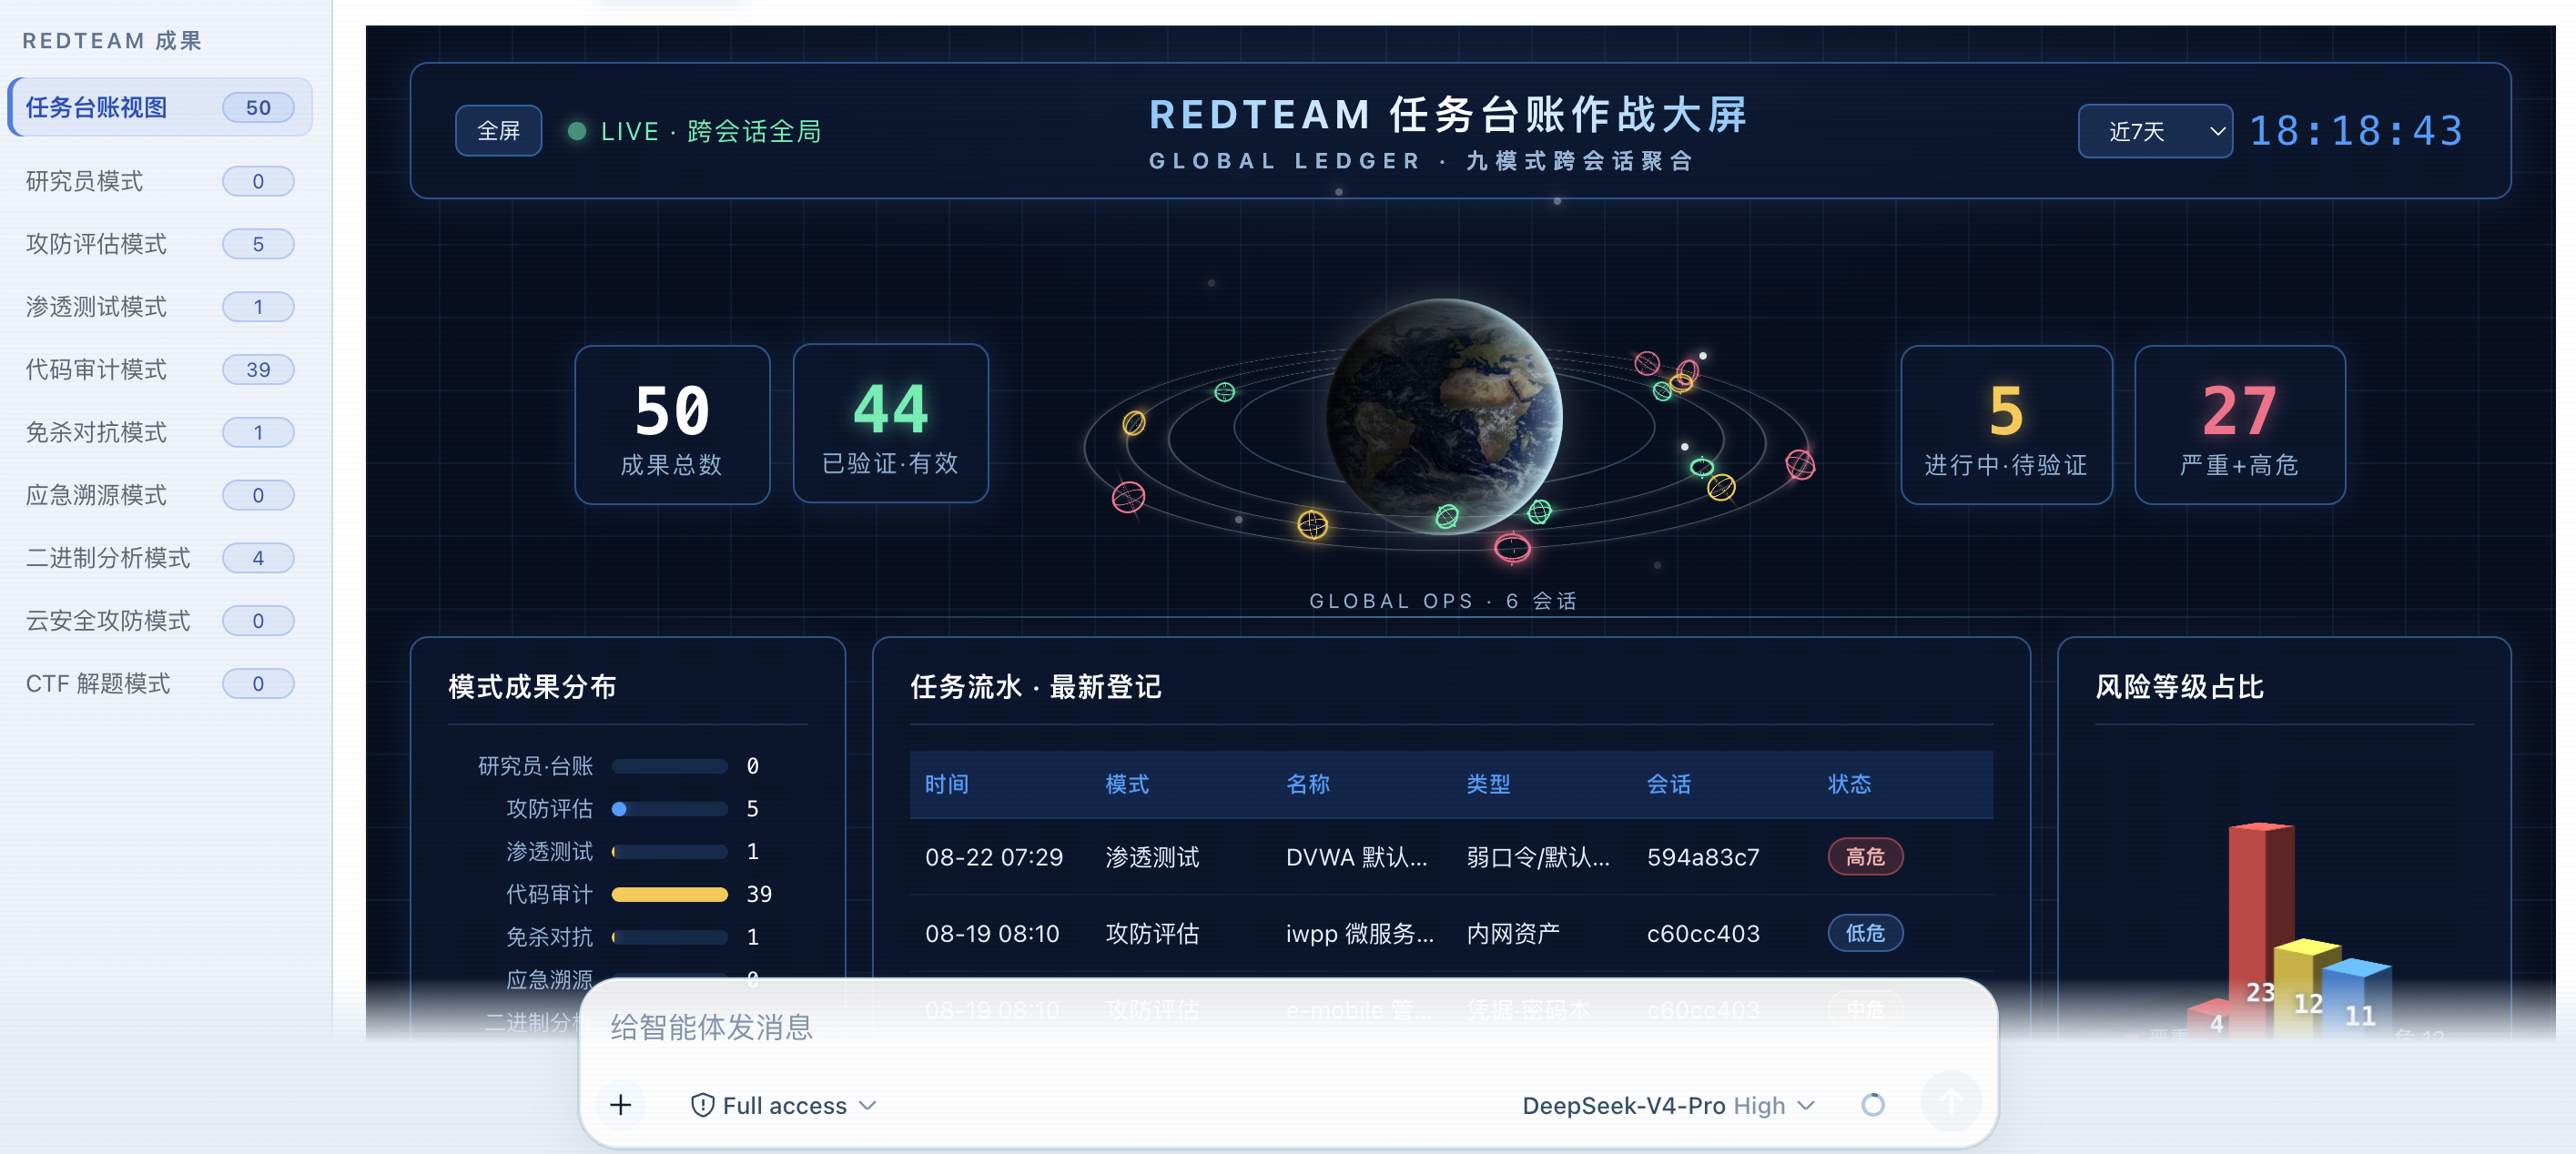
dsh-redteam-model
719SeaOf0/dsh-redteam-model · PythonA plugin pack for the dsh (DeepSeek Harness) AI agent that adds nine preset red-team security research modes and seventeen runtime plugins, covering pentesting, code audit, binary analysis, anti-detection, incident response, cloud security and CTF solving.
- 63
BEAR-C2
703S3N4T0R-0X0/BEAR-C2 · PythonBEAR-C2 is an adversary simulation and emulation framework for red team operations, built around real-world TTPs inspired by Russian, Chinese, North Korean, and Iranian APT groups.
- 64

StrikeAgent_AtkBrain-Flash
658Yean-Sec/StrikeAgent_AtkBrain-Flash · PythonIt is an AI-agent penetration-testing platform built by the Yean-Sec team (夜安团队SEC) that automates red-team foothold-establishing, SRC bug bounty, and CTF work through self-supervised, self-looping, self-evolving agent cycles.
- 65

bug-bounty-hunting-prompts
612mdpsec/bug-bounty-hunting-promptsA pack of reusable prompt files for running a structured, evidence-first bug bounty hunting workflow with an LLM agent, covering recon through triage and escalation.
- 66
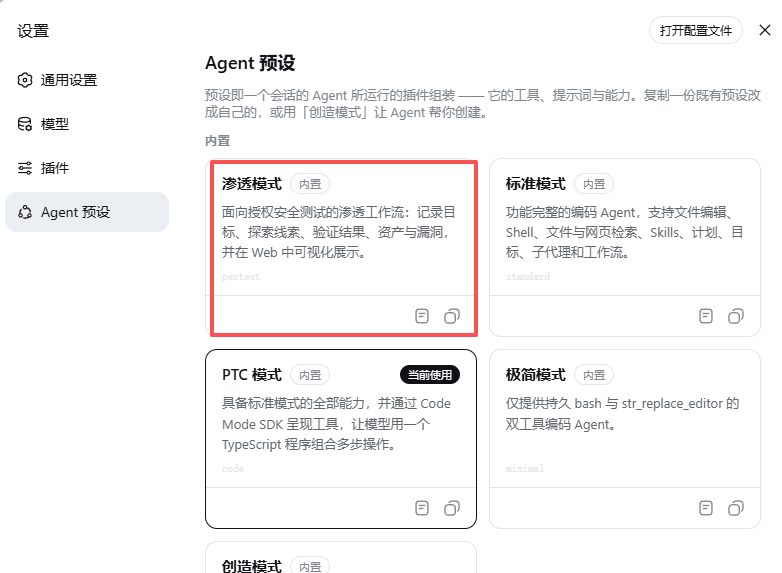
dsh-pentest
608howmp/dsh-pentest · JavaScriptdsh-pentest is a pentest-mode plugin for DeepSeek Harness (dsh) that tracks an authorized penetration test as a structured graph of goals, leads, facts, findings and assets, then shows that graph, the vulnerabilities and a report in a Web UI.
- 67

Stuxnet
588Sadpainy/Stuxnet · CThis is a reconstructed source code of Stuxnet, the famous 2010 worm that sabotaged Siemens industrial control systems, rebuilt by the author from reverse-engineering research for educational and malware-analysis purposes.
- 68
Ai-jailbreak
476Quincunx33/Ai-jailbreak · JavaScriptA curated collection of jailbreak prompts and exploit techniques that bypass the safety guardrails of both open-weight models (Gemma, Qwen, Llama, DeepSeek, Phi-4, Mistral) and frontier closed models (GPT-5.x, Gemini 3.x, Grok 4.x), documented for red-teaming and AI safety research.
- 69
pentest-harness
422S1N6H/pentest-harness · TypeScriptA self-hosted AI agent harness for authorized penetration tests, bug bounty research, security labs, and CTF engagements, where you bring your own AI model API key.
- 70

edrEvasionWorkshop
397tyeurada/edrEvasionWorkshopWorkshop materials from DEF CON 34 and BSidesLV 2026 on writing custom malware that evades EDR — from loaders to kernel-level techniques.
- 71

EvilFontTool
353DoctorEww/EvilFontTool · PythonEvilFontTool is a font-based deception tool for red teaming and security research. It generates 'Evil Fonts' — fonts that remap glyphs so a document shows humans one text while terminals, AI systems, and copy-paste see completely different text.
- 72

UniRoot
229kuuky29/UniRoot · KotlinUniRoot is a one-tap rooting app for Samsung Galaxy devices. It ships a new unprivileged kernel exploit (DirtyFrag, CVE-2026-43284) that roots the phone with a single button press, plus an older CVE-2026-43499-based exploit with per-device profiles, and it automatically re-roots the device on every boot.
- 73
ablation
214Ablation-Tool/ablation · PythonAblation is a reverse engineering framework that provides the same core disassembly, decompilation, and binary analysis capabilities as industry tools like Ghidra, IDA Pro, and Binary Ninja, and it's built to be driven by an AI coding agent.
- 74

Claude-AD
211ADScanPro/Claude-ADClaude-AD is a Claude Code plugin that gives Claude the methodology for an internal Active Directory penetration test: skills, agents and slash commands covering Kerberoasting, ADCS ESC1-17, DCSync, ACL abuse, NTLM relay and delegation abuse, each with OPSEC and telemetry notes.
- 75

CVE-2026-62911
187hypnguyen1209/CVE-2026-62911 · PythonA proof-of-concept exploit for CVE-2026-62911, a pre-auth RCE in Microsoft Exchange Server that relays an NTLM machine account hash to the MRSProxy service to drop and run an ASPX webshell, giving full SYSTEM access without any credentials.
- 76
redStackPRO
161devZero-Security/redStackPRO · PythonredStackPRO is a web canvas for designing red team attack infrastructure and defensive Active Directory cyber ranges; you compose a topology visually, and it exports a ready-to-run Terraform and Ansible working directory that you deploy yourself.
- 77
iwa-tools
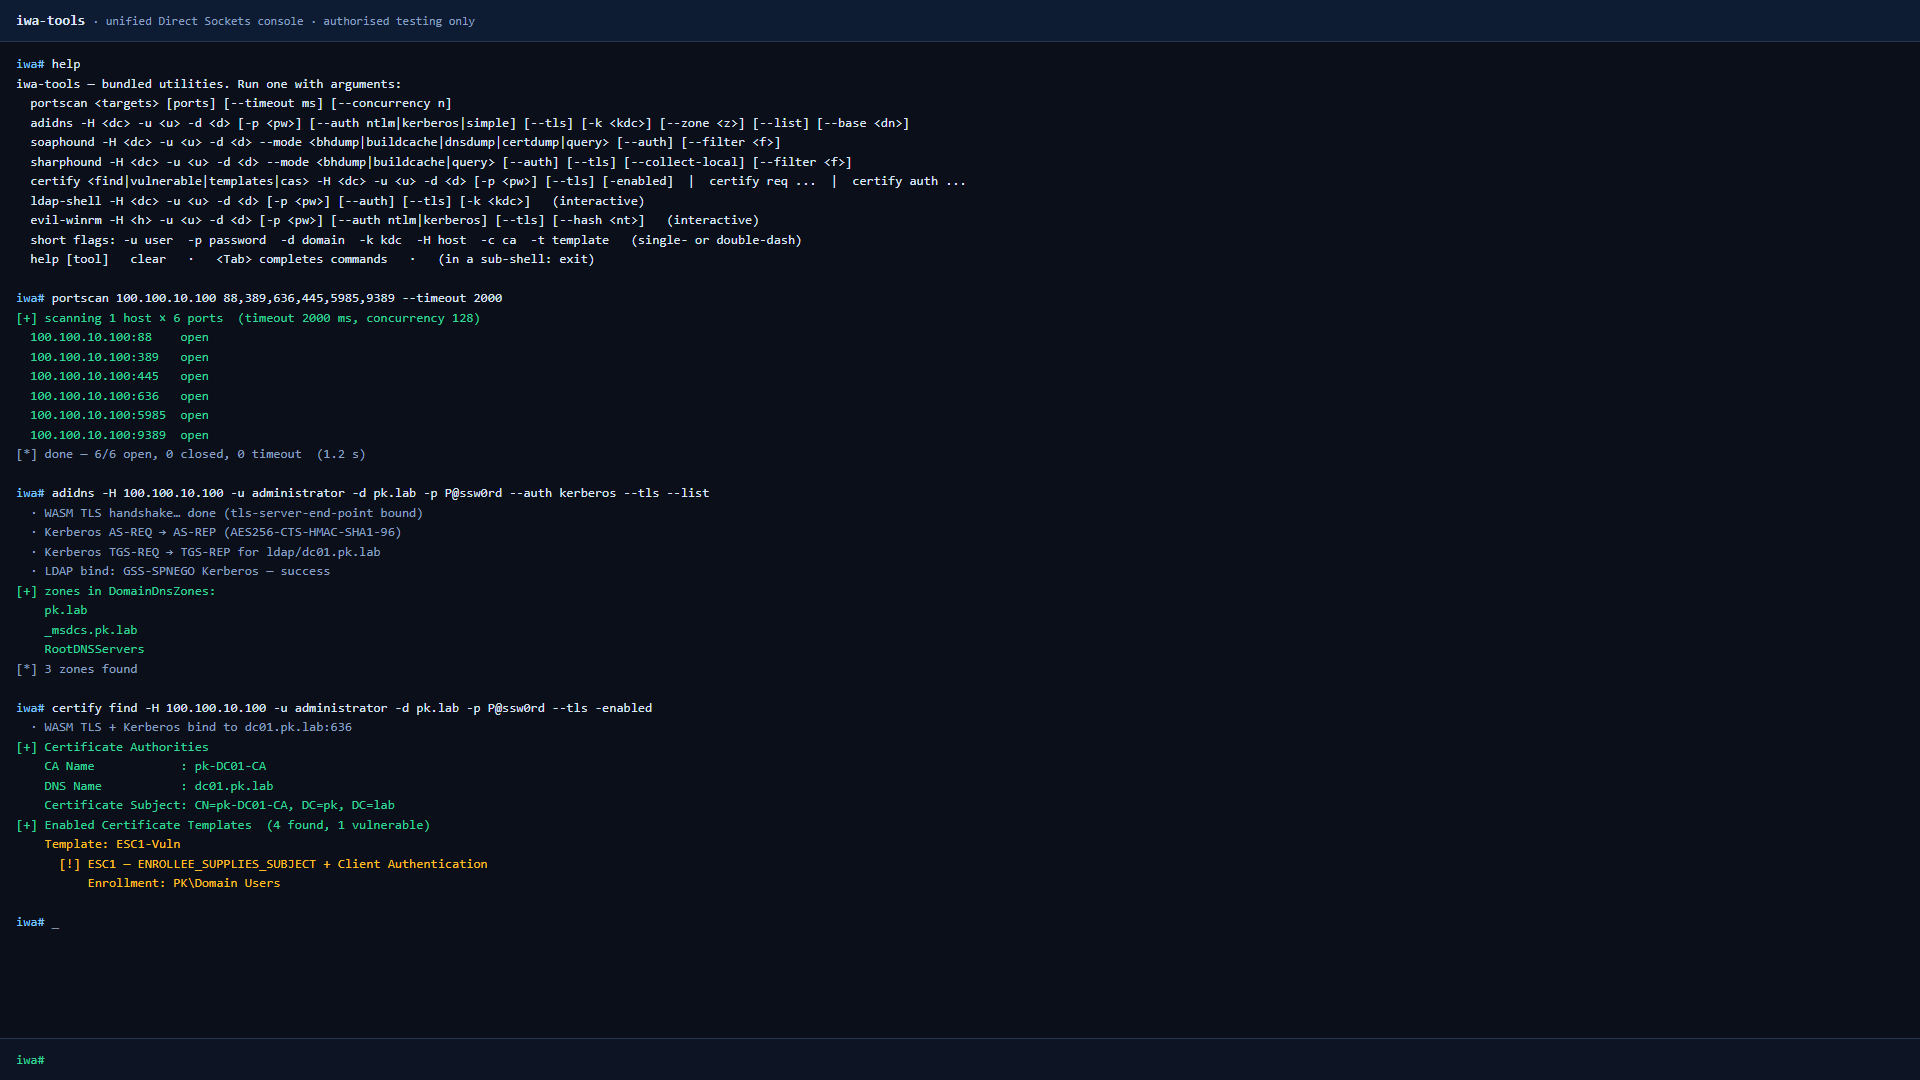
146CICADA8-Research/iwa-tools · JavaScriptiwa-tools is an offensive security toolkit that runs inside Chrome as an installed Isolated Web App, letting you speak SMB, LDAP, DCE-RPC, WinRM, Kerberos, MSSQL and ADWS directly from a browser tab for Active Directory pentesting.
Related topics
Often tagged together