Topics / #exploitation
Exploitation projects on GitHub
Penetration testing and exploitation frameworks.
As of , the most-starred Exploitation projects on GitHub are metasploit-framework (39.2K stars), sqlmap (38.7K stars) and Micro8 (18K stars). GitHub.Locker tracks 13 Exploitation repositories with 172.5K stars combined. The fastest-growing on October 19 was hacktricks, with +24 stars in a day.
Hot right now
Most stars gained in a day · Oct 19
 +24
hacktricks
HackTricks-wiki/hacktricks · ★ 12.6KA free, open wiki of hacking tricks and techniques — everything the author has learnt from CTFs, real-world apps and security research, organized into a browsable reference with 12.5k+ GitHub stars.
 +15
sqlmap
sqlmapproject/sqlmap · ★ 38.7Ksqlmap is an open-source penetration testing tool that automates detecting and exploiting SQL injection flaws and taking over the underlying database server.
 +14
redamon
samugit83/redamon · ★ 3.2KRedAmon is an open-source, self-hosted AI framework that chains reconnaissance, exploitation and post-exploitation into one pipeline, maps the attack surface into a Neo4j graph, and then triages findings and opens GitHub pull requests that fix what it discovers.
 +10
CVE-2026-41940-PoC
sakidekin/CVE-2026-41940-PoC · ★ 425This is a proof-of-concept exploit tool for CVE-2026-41940, a critical (CVSS 10.0) authentication bypass in cPanel & WHM that lets an unauthenticated attacker gain root-level WHM access by injecting CRLF sequences into server-side session files via the Authorization header.
The all-time top
13 projects · by stars
- 39.2K
 #1 · rapid7/metasploit-framework
metasploit-framework
Metasploit Framework is an open-source penetration testing framework written in Ruby — one of the best-known security toolkits on GitHub, with about 39,000 stars.
- 38.7K#2 · sqlmapproject/sqlmap
sqlmap
sqlmap is an open-source penetration testing tool that automates detecting and exploiting SQL injection flaws and taking over the underlying database server.
- 18K
 #3 · Micropoor/Micro8
Micro8
A free, open-source series of penetration-testing lessons written by veteran Chinese pentester Micropoor and published as a GitBook. It covers code audit, web, intranet and domain penetration, tunneling, and log-based tracing.
- 4

hacker-roadmap
15.7Ksundowndev/hacker-roadmapThis is a curated roadmap and toolkit index for learning and practicing ethical hacking: it explains what penetration testing is and groups hundreds of security tools, wordlists and references by category (recon, password attacks, wireless, exploitation, web hacking, post-exploitation, frameworks).
- 5
GTFOBins.github.io
13.8KGTFOBins/GTFOBins.github.io · YAMLGTFOBins is a curated list of Unix-like executables that can be abused to bypass local security restrictions in misconfigured systems — for example, binaries a restricted user can turn into a root shell.
- 6
hacktricks
12.6KHackTricks-wiki/hacktricks · JavaScriptA free, open wiki of hacking tricks and techniques — everything the author has learnt from CTFs, real-world apps and security research, organized into a browsable reference with 12.5k+ GitHub stars.
- 7

fsociety
12.4KManisso/fsociety · Pythonfsociety is a penetration testing toolkit that bundles dozens of existing hacking tools (Nmap, sqlmap, WPScan, Reaver, etc.) behind one menu-driven script, inspired by the tools used in the 'Mr. Robot' TV series.
- 8

beef
11.1Kbeefproject/beef · JavaScriptBeEF (Browser Exploitation Framework) is a penetration testing tool that focuses on the web browser, letting a tester assess the real security posture of a target by using client-side attack vectors instead of network-perimeter exploits.
- 9
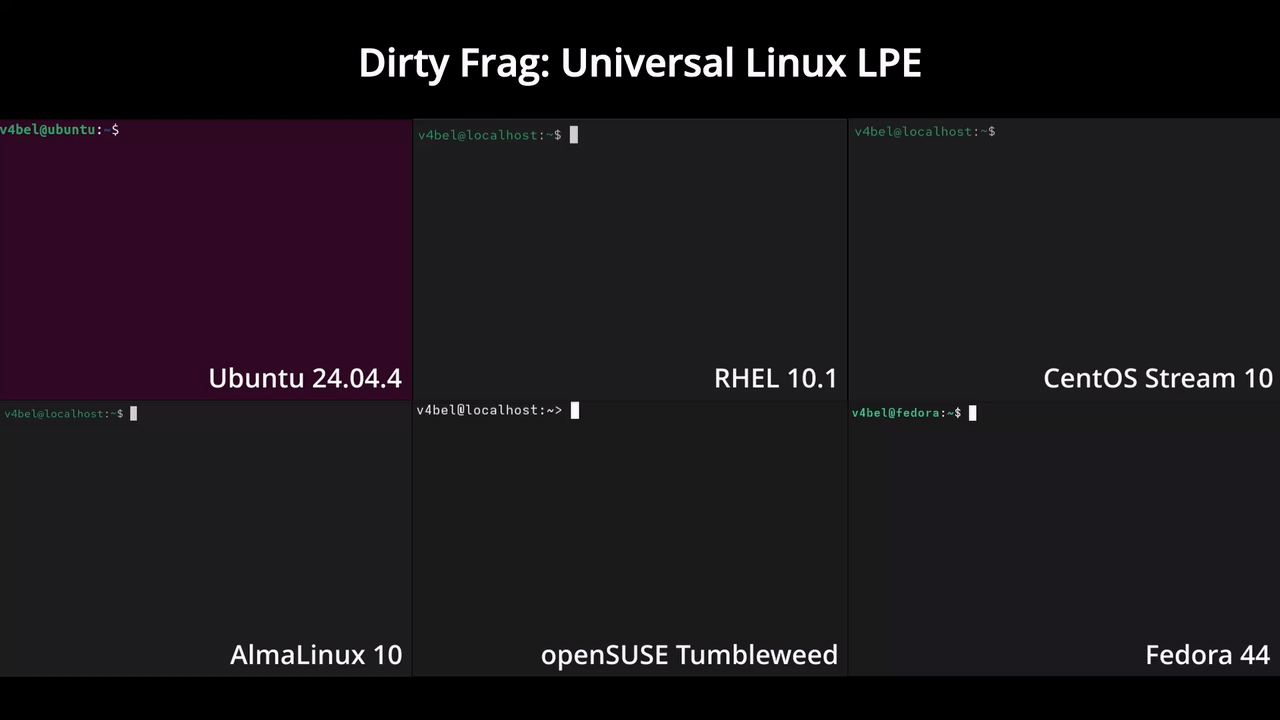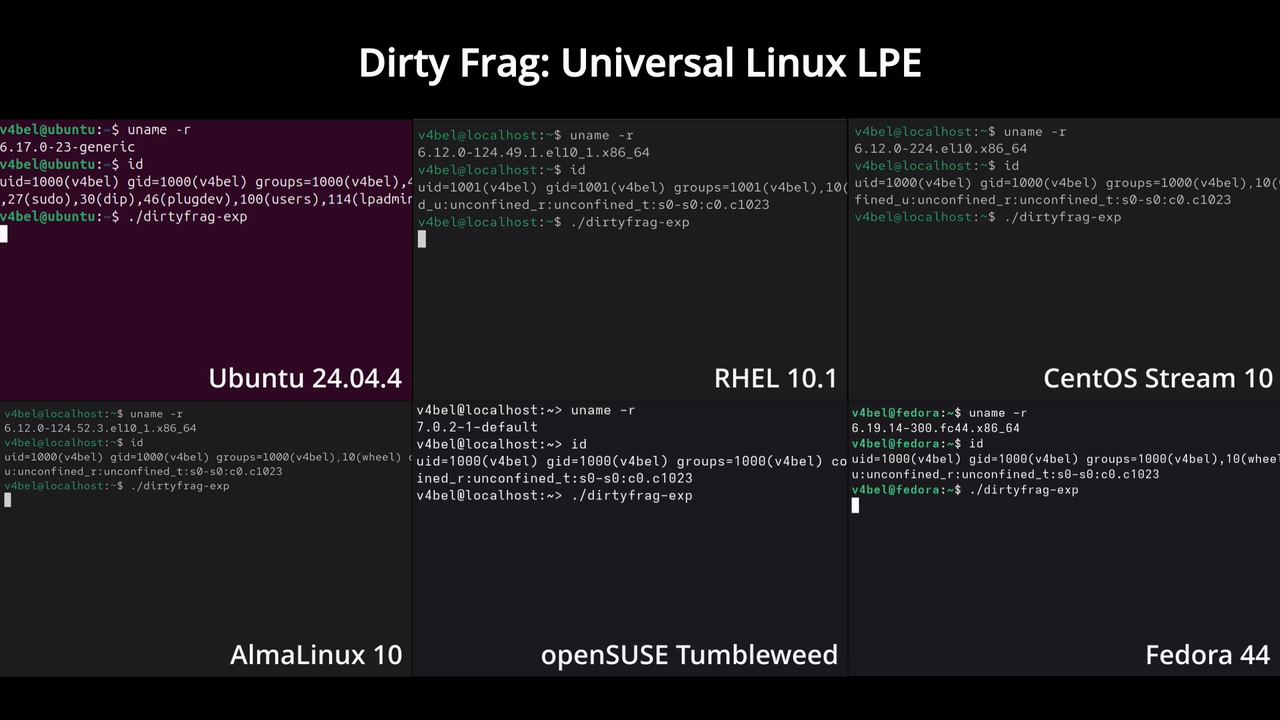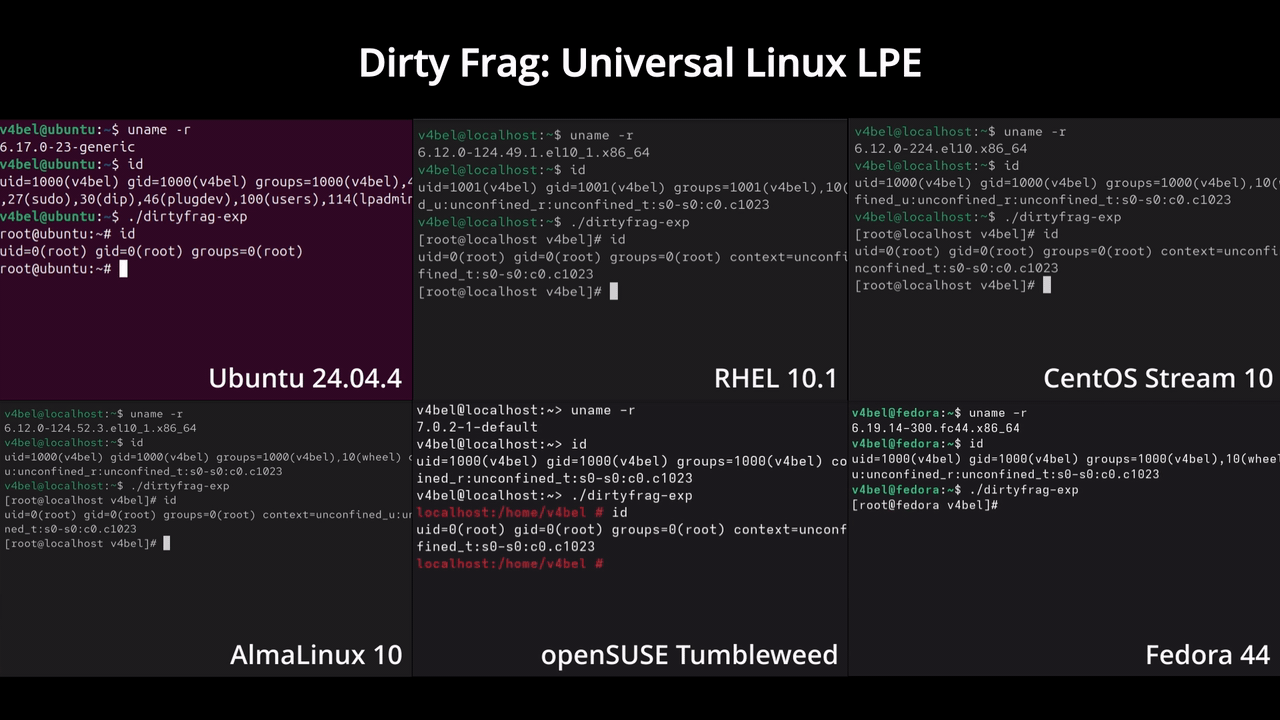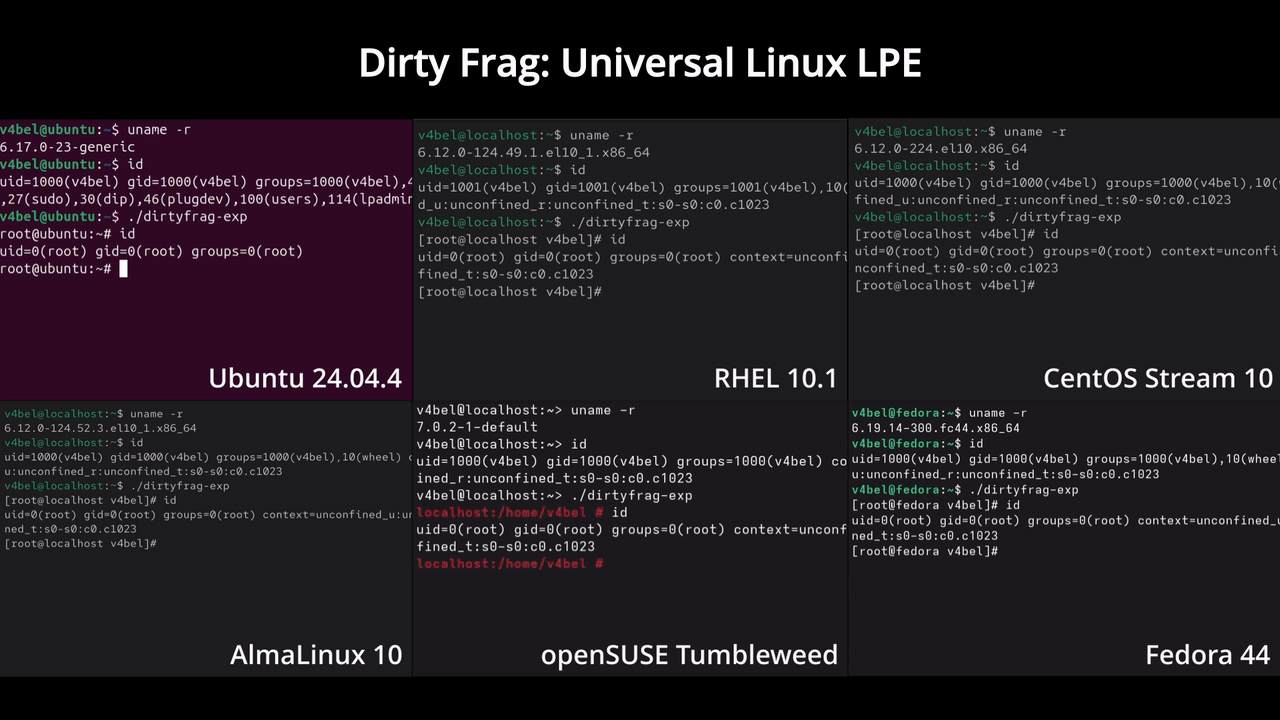
dirtyfrag
5.1KV4bel/dirtyfrag · CDirty Frag is a proof-of-concept Linux kernel local privilege escalation exploit that chains two page-cache write vulnerabilities (CVE-2026-43284 and CVE-2026-43500) to obtain root on major Linux distributions.
- 10
redamon
3.2Ksamugit83/redamon · PythonRedAmon is an open-source, self-hosted AI framework that chains reconnaissance, exploitation and post-exploitation into one pipeline, maps the attack surface into a Neo4j graph, and then triages findings and opens GitHub pull requests that fix what it discovers.
- 11
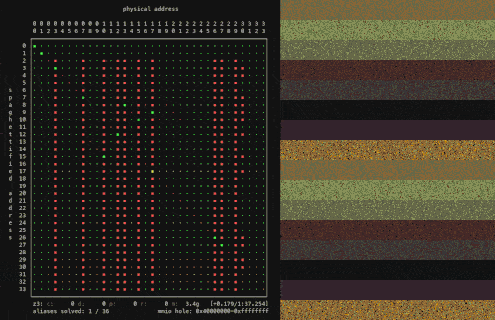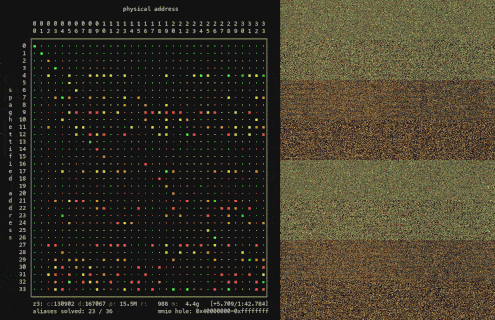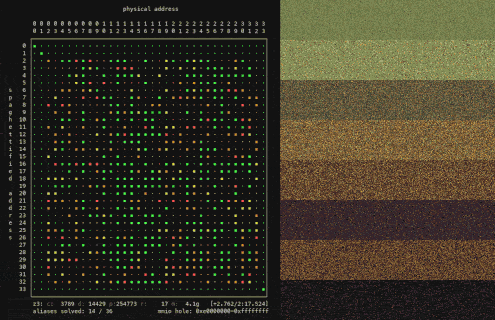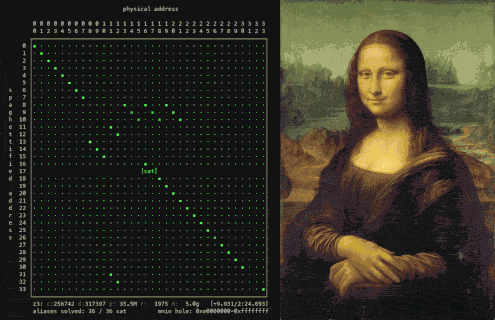
skitter-creek-bath-salts
2.2Kxoreaxeaxeax/skitter-creek-bath-salts · CA security research project that shows how to unlock protected regions on an AMD CPU — the Platform Security Processor, System Management Mode, C6 DRAM, and CPU microcode — by scrambling the DRAM controller's physical-to-DRAM address translation.
- 12
CVE-2026-41940-PoC
425sakidekin/CVE-2026-41940-PoC · PythonThis is a proof-of-concept exploit tool for CVE-2026-41940, a critical (CVSS 10.0) authentication bypass in cPanel & WHM that lets an unauthenticated attacker gain root-level WHM access by injecting CRLF sequences into server-side session files via the Authorization header.
- 13

UniRoot
236kuuky29/UniRoot · KotlinUniRoot is a one-tap rooting app for Samsung Galaxy devices. It ships a new unprivileged kernel exploit (DirtyFrag, CVE-2026-43284) that roots the phone with a single button press, plus an older CVE-2026-43499-based exploit with per-device profiles, and it automatically re-roots the device on every boot.
Related topics
Often tagged together
- cybersecurity253
- security1,006
- hacking143
- pentesting114
- offensive-security78
- hacking-tool79
- linux4,264
- penetration-testing130
- red-team83
- security-tools293
- pentest28
- cli2,284
- exploit53
- macos3,624
- vulnerability52
- docker1,685
- ethical-hacking27
- infosec49
- open-source5,767
- privilege-escalation16
- python2,440
- terminal1,136
- web2,487
- windows3,493