Topics / #poc
Poc projects on GitHub
Proof-of-concept exploits and security vulnerability demonstrations.
As of , the most-starred Poc projects on GitHub are xray (11.8K stars), device-activity-tracker (5.2K stars) and dirtyfrag (5.1K stars). GitHub.Locker tracks 8 Poc repositories with 27.6K stars combined. The fastest-growing on October 16 was dirtyfrag, with +12 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
 +12
dirtyfrag
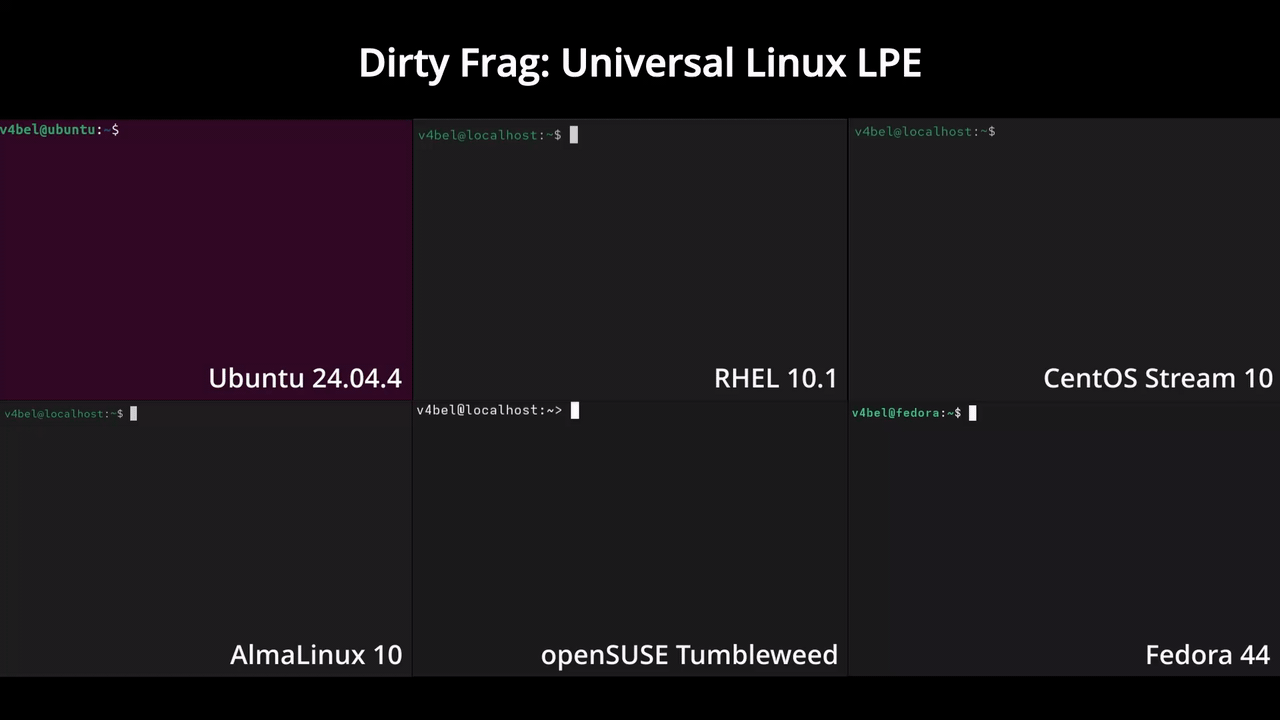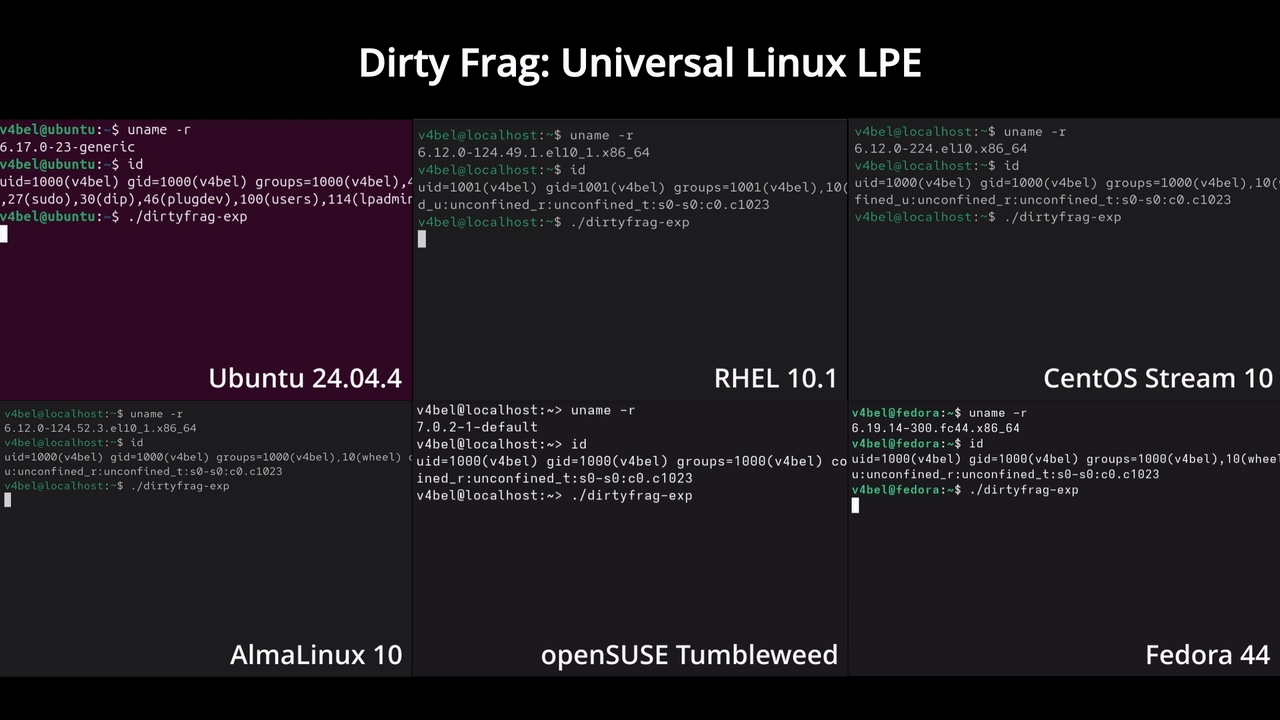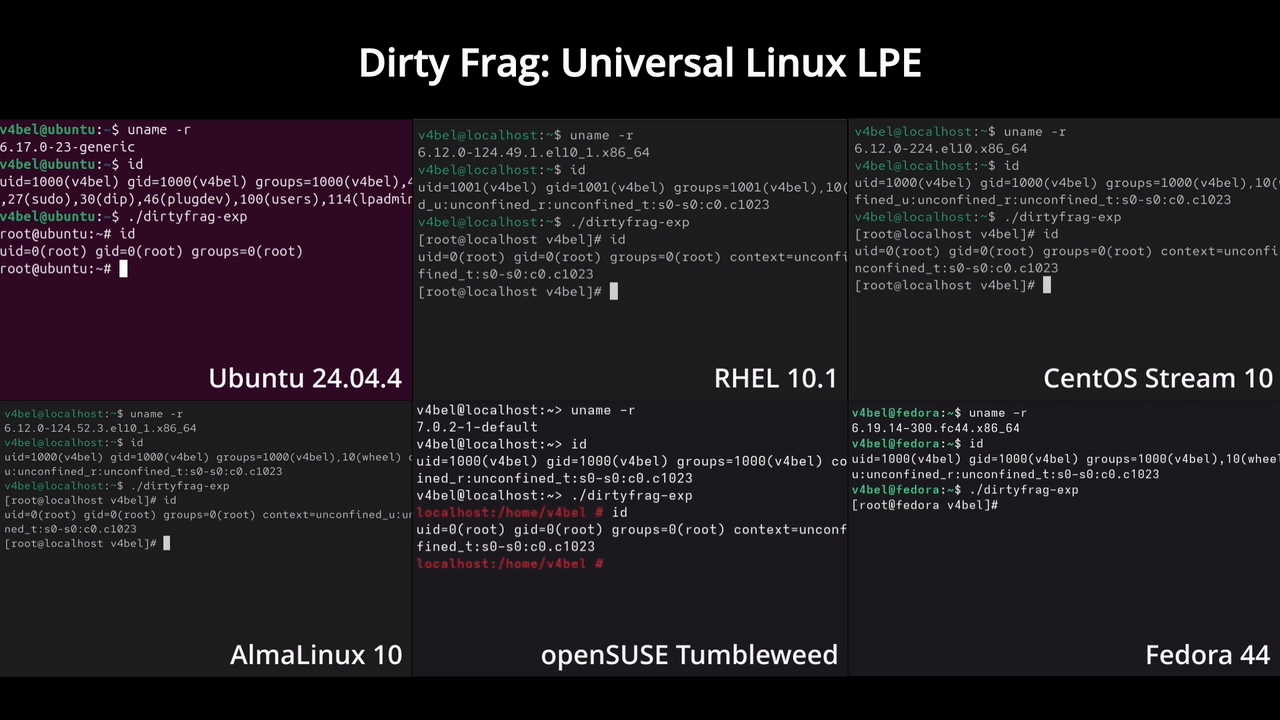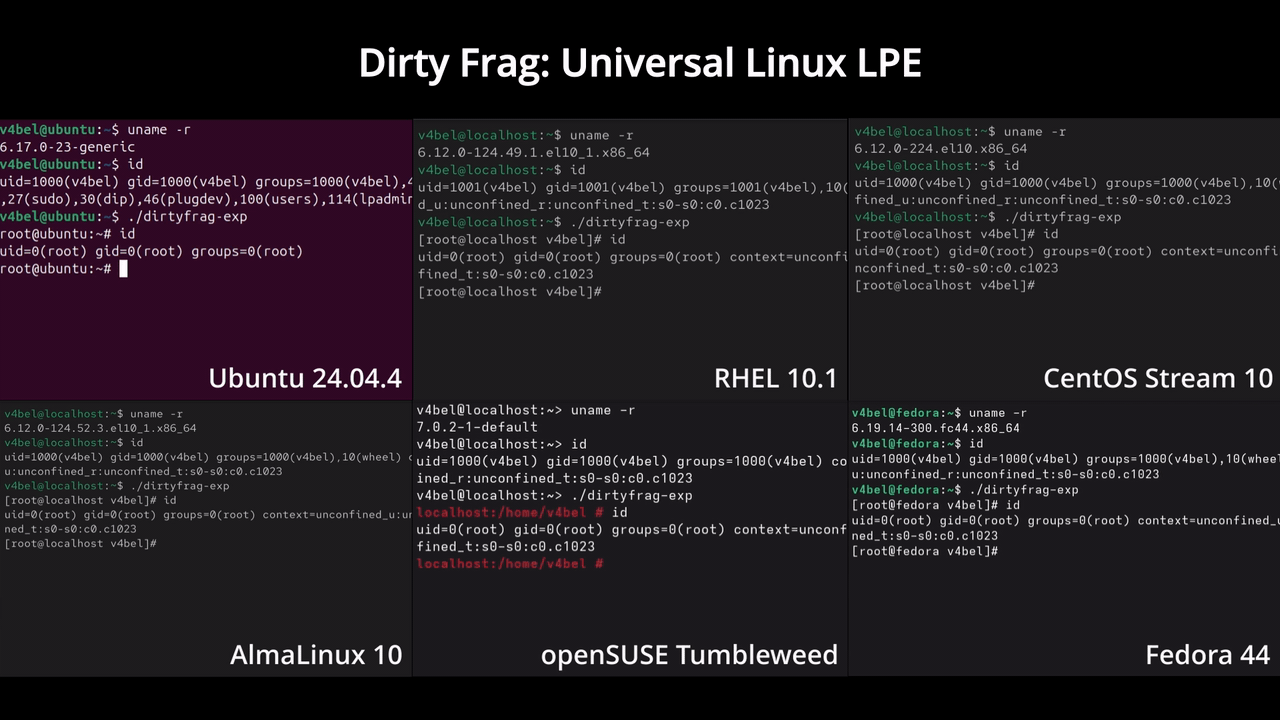
V4bel/dirtyfrag · ★ 5.1KDirty Frag is a proof-of-concept Linux kernel local privilege escalation exploit that chains two page-cache write vulnerabilities (CVE-2026-43284 and CVE-2026-43500) to obtain root on major Linux distributions.
 +4
VulnHunter
nealbridges/VulnHunter · ★ 735An open-source, agentic AI security scanner that reasons like an attacker to find exploitable vulnerabilities in source code, proves them with executable proof-of-concept exploits, and fixes them test-first. It is a maintained fork of Capital One's VulnHunter, rebuilt to run on any agent harness instead of just Claude Code.
 +1
xray
chaitin/xray · ★ 11.8Kxray is a security assessment tool built by Chaitin for scanning common web vulnerabilities and running custom PoCs against targets.
 +1
device-activity-tracker
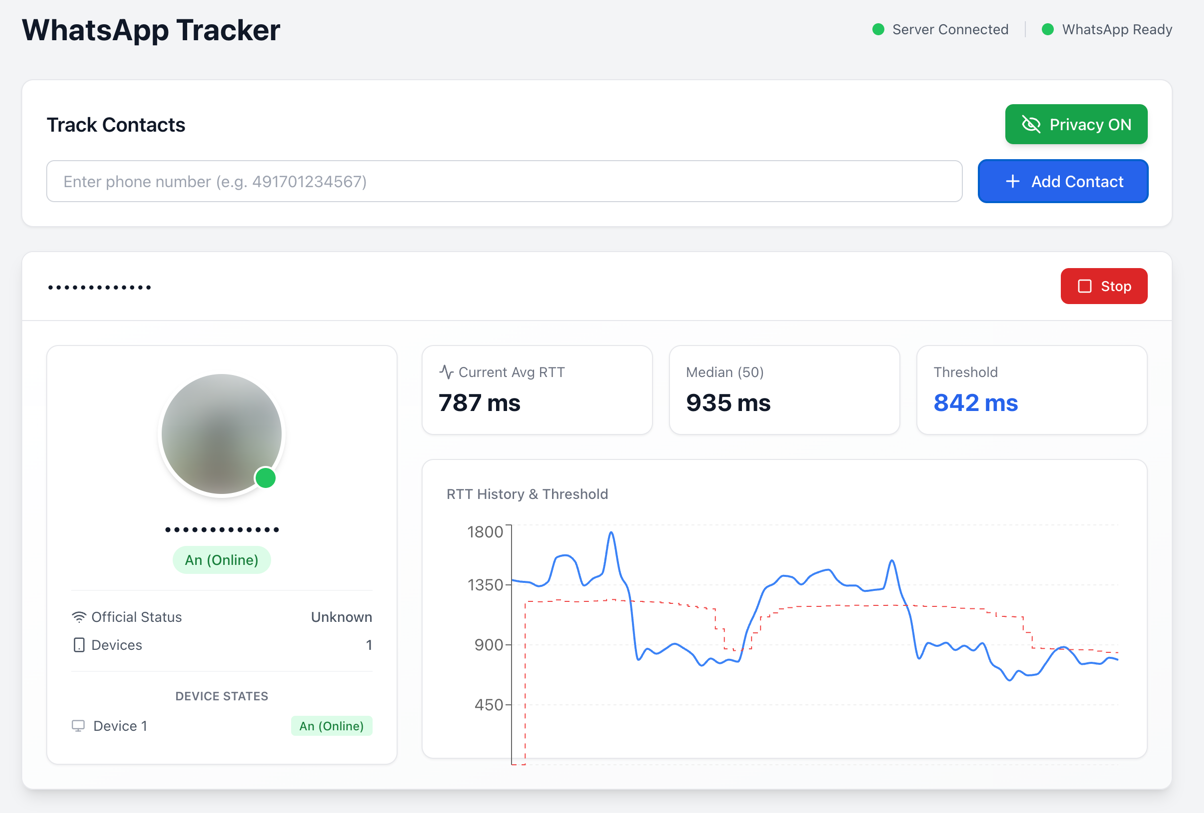
gommzystudio/device-activity-tracker · ★ 5.2KThis is a proof-of-concept security research tool that monitors WhatsApp and Signal users by measuring the Round-Trip Time (RTT) of message delivery receipts, revealing whether a target's device is actively in use, idle, or offline.
The all-time top
8 projects · by stars
- 11.8K#1 · chaitin/xray
xray
xray is a security assessment tool built by Chaitin for scanning common web vulnerabilities and running custom PoCs against targets.
- 5.2K#2 · gommzystudio/device-activity-tracker
device-activity-tracker
This is a proof-of-concept security research tool that monitors WhatsApp and Signal users by measuring the Round-Trip Time (RTT) of message delivery receipts, revealing whether a target's device is actively in use, idle, or offline.
- 5.1K#3 · V4bel/dirtyfrag
dirtyfrag
Dirty Frag is a proof-of-concept Linux kernel local privilege escalation exploit that chains two page-cache write vulnerabilities (CVE-2026-43284 and CVE-2026-43500) to obtain root on major Linux distributions.
- 4

MANPADS-System-Launcher-and-Rocket
3.9Knovatic14/MANPADS-System-Launcher-and-RocketA proof-of-concept man-portable air-defense system: a DIY launcher and interceptor built from consumer electronics and 3D-printed components, documented on GitHub as a hardware project.
- 5
VulnHunter
735nealbridges/VulnHunter · PythonAn open-source, agentic AI security scanner that reasons like an attacker to find exploitable vulnerabilities in source code, proves them with executable proof-of-concept exploits, and fixes them test-first. It is a maintained fork of Capital One's VulnHunter, rebuilt to run on any agent harness instead of just Claude Code.
- 6

CVE-2026-9830
477opaxial/CVE-2026-9830 · PythonA Python proof-of-concept that validates a reported unauthenticated REST API exposure in the BookingPress Pro WordPress plugin, which can leak booking and customer data.
- 7

bad_query
276forcequitOS/bad_query · Cbadquery is a proof-of-concept sandbox escape for iOS 26 and 27, written in C — code that demonstrates breaking out of the iOS app sandbox.
- 8

CVE-2026-62911
187hypnguyen1209/CVE-2026-62911 · PythonA proof-of-concept exploit for CVE-2026-62911, a pre-auth RCE in Microsoft Exchange Server that relays an NTLM machine account hash to the MRSProxy service to drop and run an ASPX webshell, giving full SYSTEM access without any credentials.
Related topics
Often tagged together
- cybersecurity245
- exploit51
- security976
- vulnerability50
- linux4,184
- red-team79
- security-tools282
- hacking135
- hacking-tool75
- penetration-testing126
- security-research41
- windows3,403
- cli2,227
- macos3,544
- offensive-security77
- pentesting113
- python2,383
- vulnerability-scanner43
- apache-2.01,434
- c320
- cross-platform2,623
- cve13
- docker1,660
- exploit-development15