Topics / #recon
Recon projects on GitHub
Reconnaissance frameworks that map attack surfaces by discovering domains, subdomains, and assets.
As of , the most-starred Recon projects on GitHub are spiderfoot (23.5K stars), theHarvester (18K stars) and amass (15.4K stars). GitHub.Locker tracks 13 Recon repositories with 158.2K stars combined. The fastest-growing on October 16 was wifit3, with +26 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
 +26
wifit3
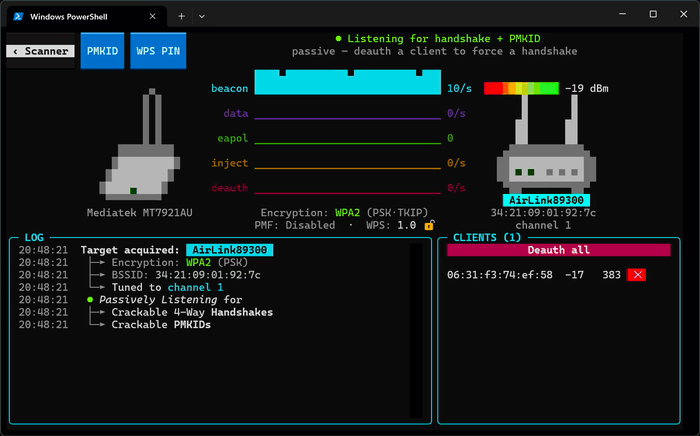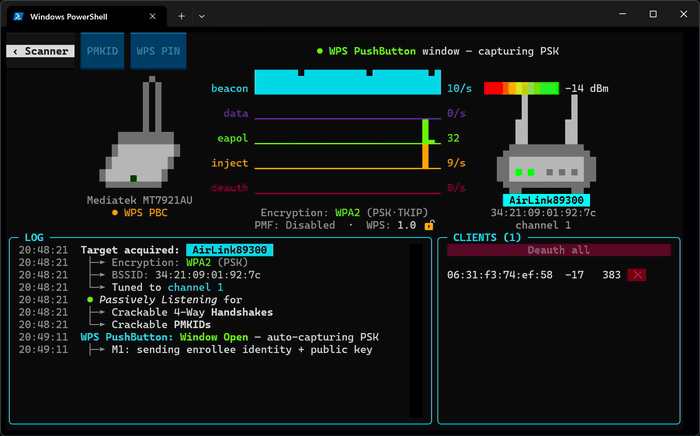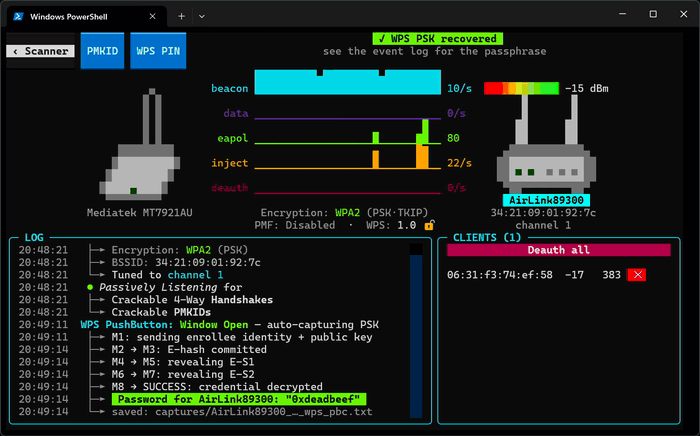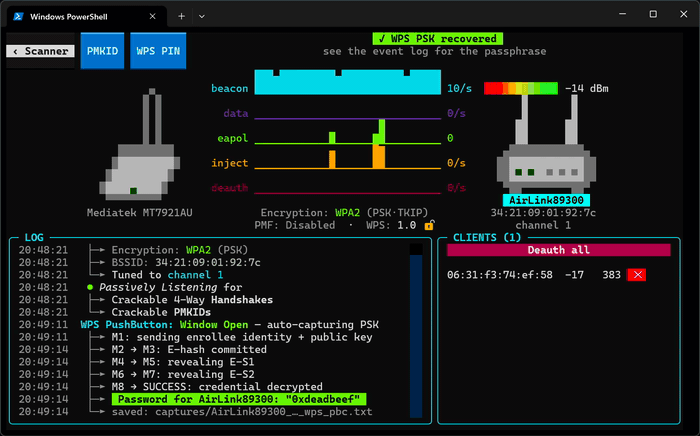
derv82/wifit3 · ★ 2.4Kwifit3 is a standalone Wi-Fi security auditing tool that scans networks, captures WPA/WPA2 handshakes, and exploits WPS/WEP weaknesses using a supported USB Wi-Fi adapter, without relying on aircrack-ng or OS kernel drivers.
flowsint
reconurge/flowsint · ★ 9.8KFlowsint is an open-source, graph-based OSINT investigation tool that lets analysts explore relationships between people, domains, IPs, organizations and more through a visual graph interface with automated enrichers.
 +19
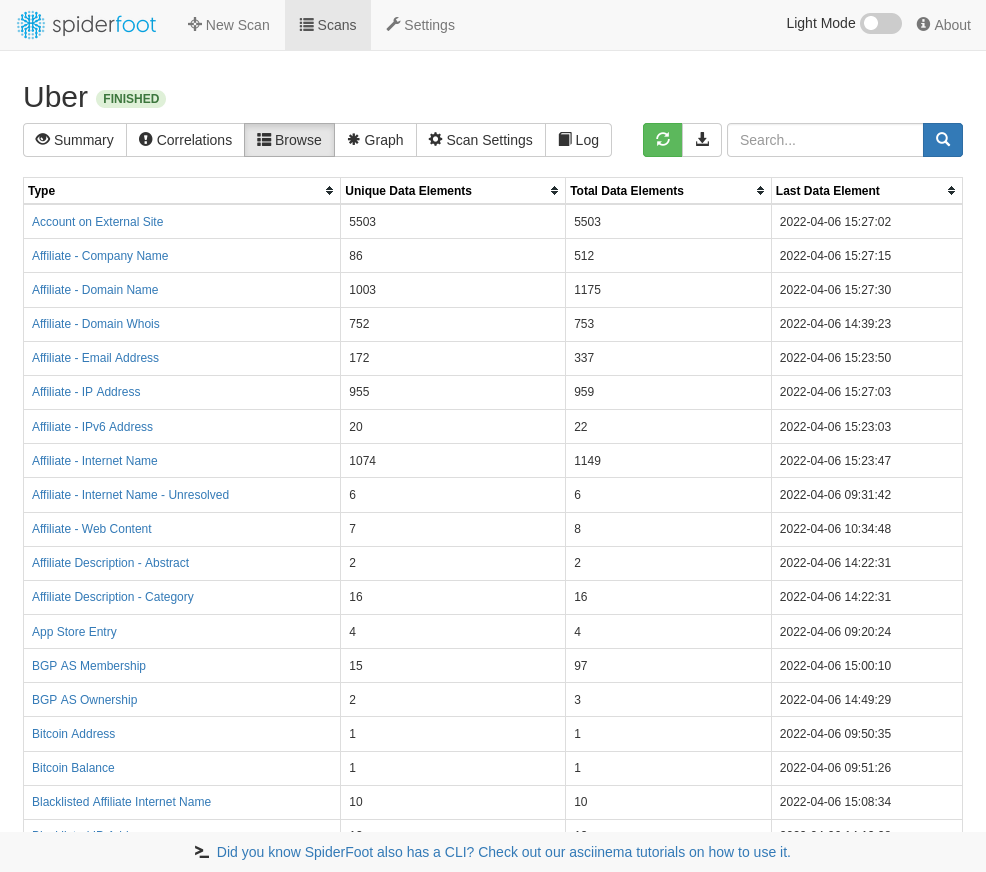
spiderfoot
smicallef/spiderfoot · ★ 23.5KOpen source OSINT automation — it collects intelligence on a target for threat intel and attack surface mapping, whether you are doing red team recon or checking what your organisation has exposed.
 +11
theHarvester
laramies/theHarvester · ★ 18KAn open-source OSINT tool that gathers emails, subdomains and names about a domain or organization from public sources: search engines, certificate transparency logs, DNS datasets, code repositories and threat-intel platforms, normalizing hostnames, emails, IPs, URLs, ASNs, people and breach names.
The all-time top
13 projects · by stars
- 23.5K#1 · smicallef/spiderfoot
spiderfoot
Open source OSINT automation — it collects intelligence on a target for threat intel and attack surface mapping, whether you are doing red team recon or checking what your organisation has exposed.
- 18K#2 · laramies/theHarvester
theHarvester
An open-source OSINT tool that gathers emails, subdomains and names about a domain or organization from public sources: search engines, certificate transparency logs, DNS datasets, code repositories and threat-intel platforms, normalizing hostnames, emails, IPs, URLs, ASNs, people and breach names.
- 15.4K
 #3 · owasp-amass/amass
amass
Amass is an OWASP project that maps attack surfaces and discovers external assets (like subdomains, IPs, and infrastructure) using open source intelligence gathering and active reconnaissance.
- 4

PENTESTING-BIBLE
14KblaCCkHatHacEEkr/PENTESTING-BIBLEA curated catalog of over 200 numbered links to pentesting articles, bug bounty write-ups, cheat sheets and other security lists — a reading collection, not software.
- 5

awesome-web-security
13.9Kqazbnm456/awesome-web-security · PythonA curated list of web security materials and resources, organized by vulnerability class and attack type (XSS, SQL injection, CSRF, SSRF, XXE, deserialization, OAuth, JWT, and more), plus cheatsheets, tools, and write-ups for penetration testing.
- 6

hacktricks
12.6KHackTricks-wiki/hacktricks · JavaScriptA free, open wiki of hacking tricks and techniques — everything the author has learnt from CTFs, real-world apps and security research, organized into a browsable reference with 12.5k+ GitHub stars.
- 7
Sn1per
11.5K1N3/Sn1per · ShellSn1per is an offensive-security platform that bundles reconnaissance, vulnerability scanning, exploitation and reporting into one workspace, orchestrating 600+ exploits and 90+ third-party tools for pentesters and attack-surface-management teams.
- 8

Sublist3r
11.1Kaboul3la/Sublist3r · PythonSublist3r is a Python tool that enumerates subdomains of a target website using OSINT, helping penetration testers and bug hunters gather subdomains for a domain they are targeting.
- 9
bbot
10.7Kblacklanternsecurity/bbot · PythonBBOT is a recursive internet scanner for hackers — it automates recon, bug bounty work and attack surface management (ASM), inspired by Spiderfoot.
- 10

OneForAll
10.1Kshmilylty/OneForAll · PythonOneForAll is a powerful subdomain collection tool: point it at a target domain and it gathers subdomains from many sources — a core reconnaissance step in penetration testing, which is why the author built it.
- 11
flowsint
9.8Kreconurge/flowsint · TypeScriptFlowsint is an open-source, graph-based OSINT investigation tool that lets analysts explore relationships between people, domains, IPs, organizations and more through a visual graph interface with automated enrichers.
- 12
Agentic-Bug-Hunter
5.4Kawarexone/Agentic-Bug-Hunter · PythonAgentic Bug Hunter is an AI-powered bug bounty toolkit that runs recon, tests for vulnerabilities, validates findings against a strict gate, and writes submission-ready reports for HackerOne, Bugcrowd, Intigriti, or Immunefi, right from your terminal.
- 13
wifit3
2.4Kderv82/wifit3 · Pythonwifit3 is a standalone Wi-Fi security auditing tool that scans networks, captures WPA/WPA2 handshakes, and exploits WPS/WEP weaknesses using a supported USB Wi-Fi adapter, without relying on aircrack-ng or OS kernel drivers.
Related topics
Often tagged together
- security976
- osint68
- cybersecurity245
- linux4,184
- penetration-testing126
- macos3,544
- pentesting113
- python2,383
- security-tools282
- cli2,227
- docker1,660
- hacking135
- windows3,403
- open-source5,666
- information-gathering20
- reconnaissance40
- dns90
- terminal1,101
- web2,447
- api1,094
- bugbounty16
- cross-platform2,623
- network-security66
- networking565