Topics / #vulnerability-scanner
Vulnerability-scanner projects on GitHub
Automated scanning for known vulnerabilities in hosts and dependencies.
As of , the most-starred Vulnerability-scanner projects on GitHub are strix (69.1K stars), shannon (49K stars) and nuclei (32.1K stars). GitHub.Locker tracks 43 Vulnerability-scanner repositories with 519.7K stars combined. The fastest-growing on October 16 was security-audit-skill, with +375 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
 +375
security-audit-skill
cloudflare/security-audit-skill · ★ 30.4KA Cloudflare coding-agent skill that turns your agent into a security auditor: it orchestrates isolated agents through a structured, multi-phase audit and returns independently verified, machine-readable findings.
 +214
strix
usestrix/strix · ★ 69.1KStrix is an open-source tool that uses autonomous AI agents to pentest your application like real hackers: it runs your code dynamically, finds vulnerabilities, and proves them with working exploits instead of just flagging suspicious patterns.
 +81
shannon
KeygraphHQ/shannon · ★ 49KShannon is an autonomous AI pentester that analyzes your web application's source code, maps attack vectors, and then executes real exploits against the running app to prove vulnerabilities before they reach production — 'no exploit, no report'.
 +49
hexstrike-ai
0x4m4/hexstrike-ai · ★ 12.9KHexStrike AI MCP Agents is an MCP server that lets AI agents like Claude, GPT, or Copilot autonomously run 150+ real cybersecurity tools for automated pentesting, bug bounty hunting, CTF challenges, and vulnerability discovery.
The all-time top
43 projects · by stars
- 69.1K#1 · usestrix/strix
strix
Strix is an open-source tool that uses autonomous AI agents to pentest your application like real hackers: it runs your code dynamically, finds vulnerabilities, and proves them with working exploits instead of just flagging suspicious patterns.
- 49K#2 · KeygraphHQ/shannon
shannon
Shannon is an autonomous AI pentester that analyzes your web application's source code, maps attack vectors, and then executes real exploits against the running app to prove vulnerabilities before they reach production — 'no exploit, no report'.
- 32.1K
 #3 · projectdiscovery/nuclei
nuclei
A fast, open-source vulnerability scanner that runs YAML-based templates to find security issues in applications, APIs, networks, DNS and cloud configurations. Its checks come from a large global security community.
- 4
security-audit-skill
30.4Kcloudflare/security-audit-skill · JavaScriptA Cloudflare coding-agent skill that turns your agent into a security auditor: it orchestrates isolated agents through a structured, multi-phase audit and returns independently verified, machine-readable findings.
- 5

masscan
26.1Krobertdavidgraham/masscan · CMasscan is an Internet-scale TCP port scanner that transmits SYN packets asynchronously and can scan the entire IPv4 Internet in under 5 minutes, sending up to 10 million packets per second from a single machine.
- 6
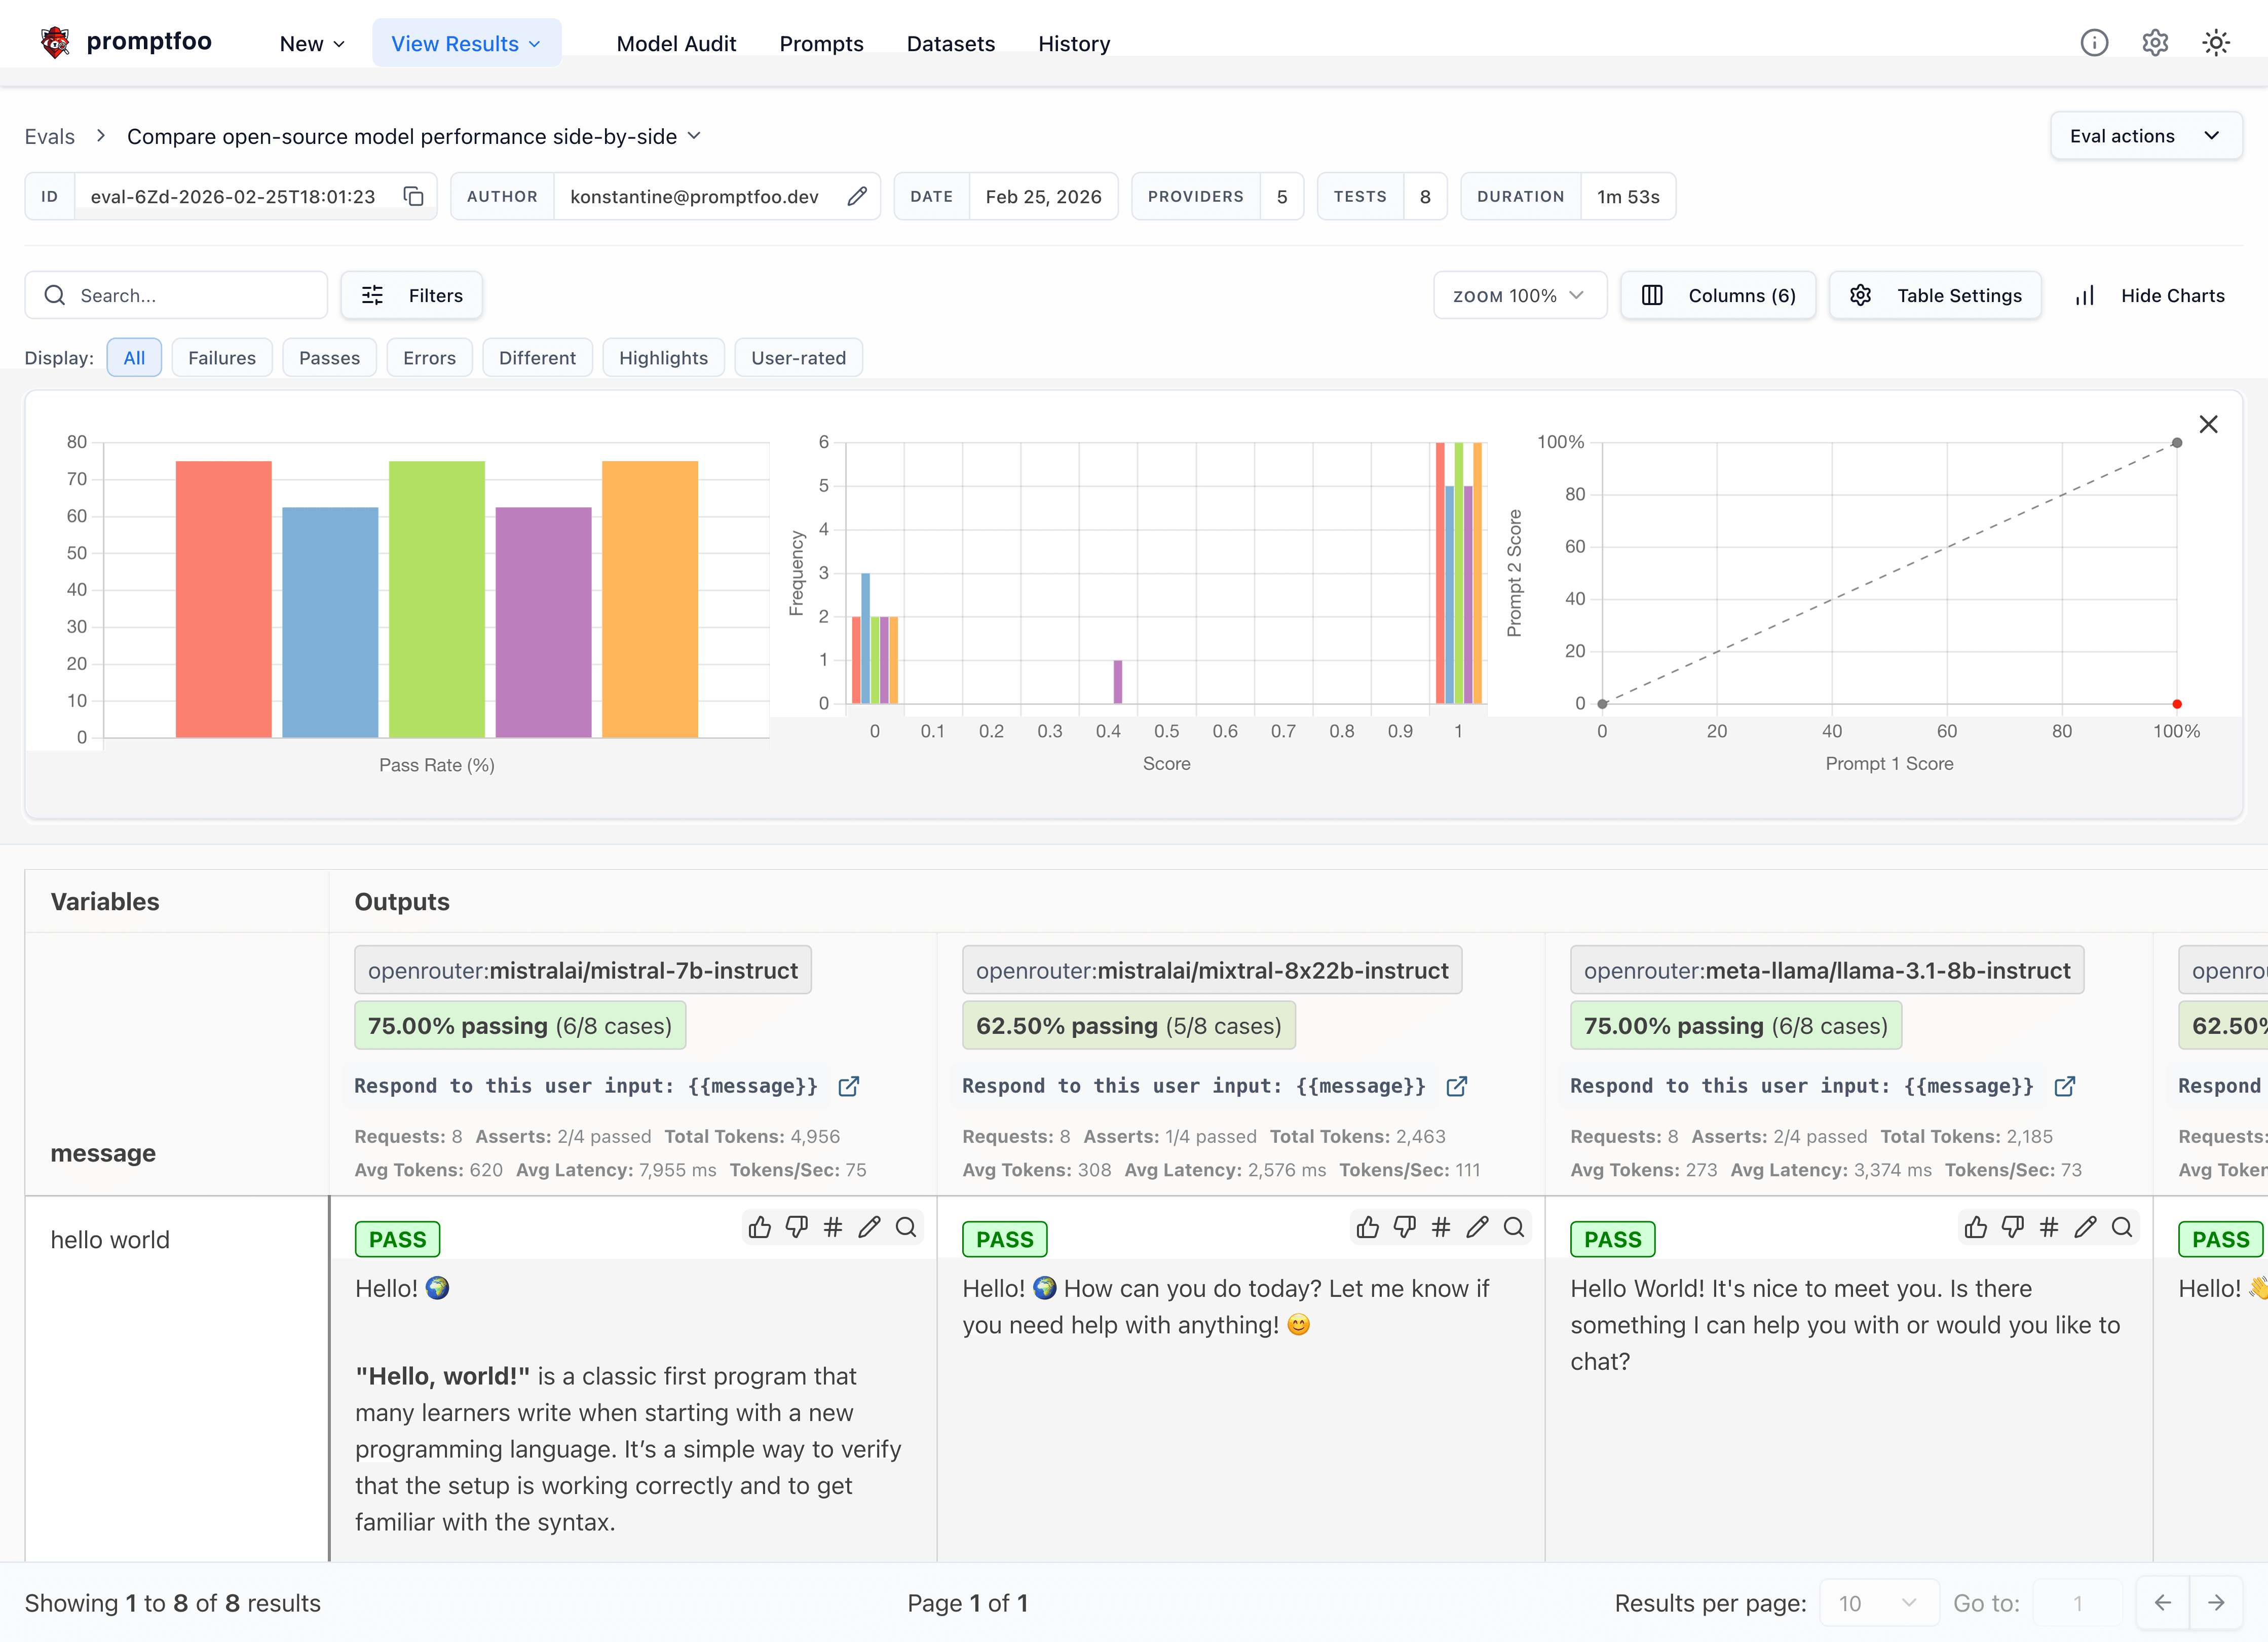
promptfoo
26.1Kpromptfoo/promptfoo · TypeScriptpromptfoo is a CLI and library for evaluating and red-teaming LLM apps — you test prompts, agents, and RAGs and run security scans on them, instead of relying on trial-and-error.
- 7

Mobile-Security-Framework-MobSF
22KMobSF/Mobile-Security-Framework-MobSF · JavaScriptMobSF is an automated, all-in-one mobile security framework: it performs static and dynamic analysis, penetration testing, malware analysis and privacy analysis on Android, iOS and Windows Mobile apps.
- 8

semgrep
17.1Ksemgrep/semgrep · CSemgrep is a fast, open-source static analysis tool that scans source code to find bugs, security issues, and enforce coding standards using rules that look like ordinary code rather than abstract syntax trees or regex.
- 9

zaproxy
16Kzaproxy/zaproxy · JavaZAP (Zed Attack Proxy) by Checkmarx is the world's most widely used web app security scanner, used to automatically find vulnerabilities in web applications during development and testing.
- 10

XSStrike
15.2Ks0md3v/XSStrike · PythonXSStrike is a Cross Site Scripting (XSS) detection suite built around four hand-written parsers, an intelligent payload generator, a fuzzing engine, and a fast crawler. Instead of just firing generic payloads like most scanners, it analyzes the live response and crafts payloads guaranteed to work through context analysis.
- 11
fscan
14.7Kshadow1ng/fscan · Gofscan is an open-source intranet scanner written in Go: one command runs an all-round internal-network audit — host discovery, port scanning, service identification, weak-password brute force and vulnerability detection.
- 12

DVWA
13.9Kdigininja/DVWA · PHPDVWA (Damn Vulnerable Web Application) is a PHP/MariaDB web app that is deliberately full of security bugs, built as a legal practice target for security pros, students, and developers to learn web application security.
- 13

nuclei-templates
13.1Kprojectdiscovery/nuclei-templates · JavaScriptThis is a community-curated collection of over 11,000 detection templates for the Nuclei vulnerability scanner, covering CVEs, misconfigurations, exposed panels, and other security issues.
- 14
hexstrike-ai
12.9K0x4m4/hexstrike-ai · PythonHexStrike AI MCP Agents is an MCP server that lets AI agents like Claude, GPT, or Copilot autonomously run 150+ real cybersecurity tools for automated pentesting, bug bounty hunting, CTF challenges, and vulnerability discovery.
- 15
vuls
12.3Kfuture-architect/vuls · GoVuls is an open-source, agent-less vulnerability scanner written in Go. It automatically detects vulnerabilities affecting your servers and can generate reports on a regular basis, for example via CRON.
- 16
xray
11.8Kchaitin/xray · Vuexray is a security assessment tool built by Chaitin for scanning common web vulnerabilities and running custom PoCs against targets.
- 17
Sn1per
11.5K1N3/Sn1per · ShellSn1per is an offensive-security platform that bundles reconnaissance, vulnerability scanning, exploitation and reporting into one workspace, orchestrating 600+ exploits and 90+ third-party tools for pentesters and attack-surface-management teams.
- 18

awesome-hacker-search-engines
11.3Kedoardottt/awesome-hacker-search-engines · ShellA curated list of search engines useful for penetration testing, vulnerability assessment, red/blue team operations, bug bounty hunting, and general OSINT work.
- 19
osv-scanner
11.2Kgoogle/osv-scanner · GoOSV-Scanner is Google's open-source command-line vulnerability scanner: it checks your project's dependencies against OSV.dev, an open vulnerability database, and reports which known vulnerabilities affect you.
- 20

codex-security
11.1Kopenai/codex-security · TypeScriptCodex Security is OpenAI's CLI and TypeScript SDK for defining security policy and for finding, validating, and fixing security vulnerabilities in your code.
- 21

clair
11.1Kquay/clair · GoClair is an open source tool for static analysis of vulnerabilities in application container images, covering both OCI and Docker image formats.
- 22

nikto
10.8Ksullo/nikto · PerlNikto is an open-source web server scanner that checks servers for dangerous files, outdated software versions, and other common vulnerabilities.
- 23

codeql
10.2Kgithub/codeql · CodeQLThis is the standard library and query collection for CodeQL, the code analysis engine that powers GitHub Advanced Security code scanning and GitHub's commercial security products.
- 24

deepsec
8.2Kvercel-labs/deepsec · TypeScriptDeepsec is an agent-powered vulnerability scanner that you run in your own infrastructure to do on-demand security review of an entire large codebase, surfacing hard-to-find issues that have been lurking for a long time.
- 25

defending-code-reference-harness
7.6Kanthropics/defending-code-reference-harness · PythonA reference implementation from Anthropic for finding and fixing vulnerabilities with Claude: a set of Claude Code skills (quickstart, threat-model, vuln-scan, triage, patch, customize) plus an autonomous scanning harness that runs a recon-find-verify-report-patch loop, built from learnings partnering with security teams.
- 26

DeepAudit
7.2Klintsinghua/DeepAudit · PythonDeepAudit is a multi-agent AI platform for code security auditing. It mimics how a security expert thinks, using cooperating agents (Orchestrator, Recon, Analysis, Verification) to find vulnerabilities and then verify them with automated sandbox PoC exploitation.
- 27
AI-Infra-Guard
6.9KTencent/AI-Infra-Guard · PythonAI-Infra-Guard (A.I.G) is a full-stack AI red teaming platform built by Tencent Zhuque Lab that scans AI agents, MCP servers, agent skills, and AI infrastructure components for security vulnerabilities, and evaluates LLMs against jailbreak attacks.
- 28
dockhand
6.8KFinsys/dockhand · TypeScriptDockhand is a self-hosted web UI for managing Docker environments - containers, Compose stacks, images, and volumes - across local and remote hosts, with live monitoring, logs, and a built-in terminal.
- 29
Agentic-Bug-Hunter
5.4Kawarexone/Agentic-Bug-Hunter · PythonAgentic Bug Hunter is an AI-powered bug bounty toolkit that runs recon, tests for vulnerabilities, validates findings against a strict gate, and writes submission-ready reports for HackerOne, Bugcrowd, Intigriti, or Immunefi, right from your terminal.
- 30

raptor
3.9Kgadievron/raptor · PythonRAPTOR turns a Claude Code session into an offensive/defensive security agent: Claude.md rules, sub-agents and skills orchestrate tools like radare2, Frida, Z3 and CodeQL for binary reverse-engineering, exploit-feasibility research, and software supply-chain (SCA) analysis.
- 31
redamon
3.1Ksamugit83/redamon · PythonRedAmon is an open-source, self-hosted AI framework that chains reconnaissance, exploitation and post-exploitation into one pipeline, maps the attack surface into a Neo4j graph, and then triages findings and opens GitHub pull requests that fix what it discovers.
- 32
Pentest-Swarm-AI
3KArmur-Ai/Pentest-Swarm-AI · GoPentest Swarm AI is an open-source, self-hosted penetration testing tool where dozens of AI agents work as a swarm to recon, classify, exploit, and report vulnerabilities in APIs and web apps — not just scan for them.
- 33
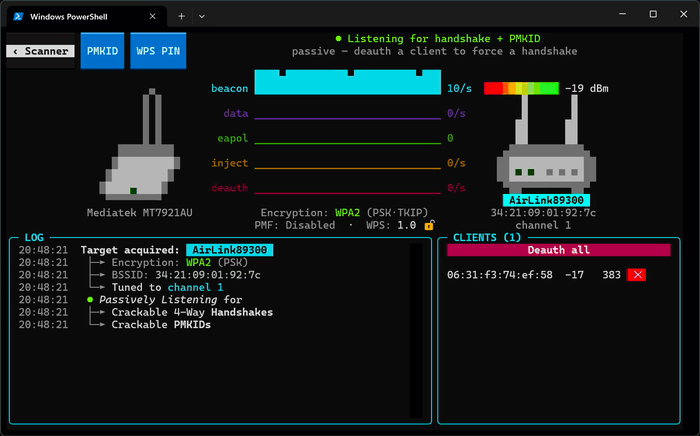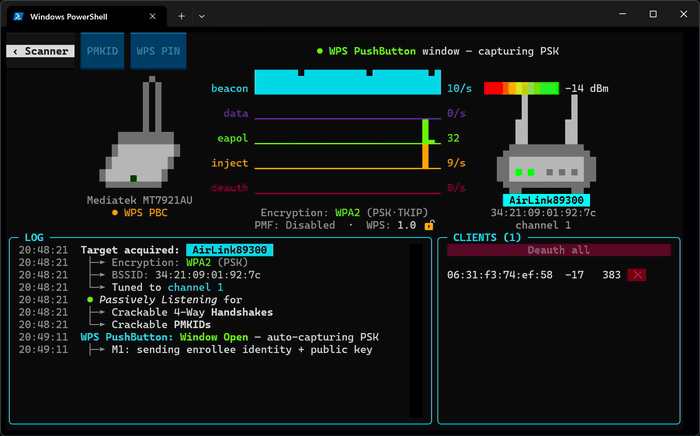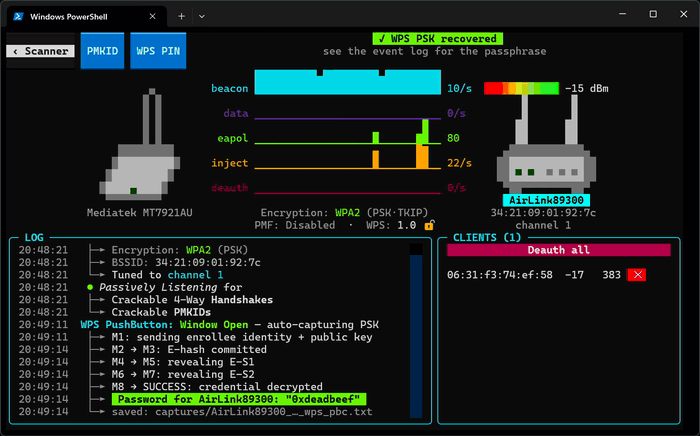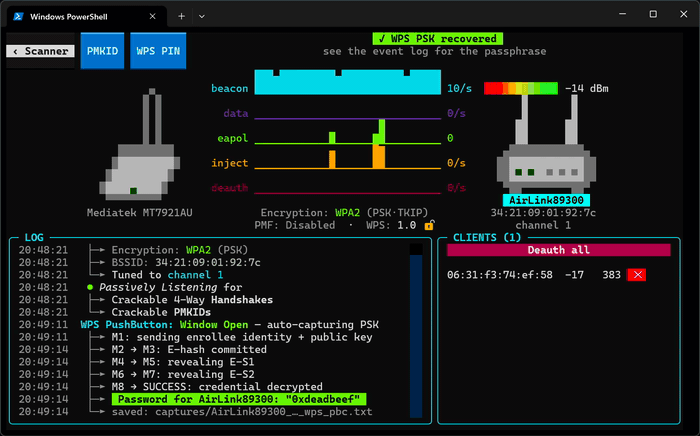
wifit3
2.4Kderv82/wifit3 · Pythonwifit3 is a standalone Wi-Fi security auditing tool that scans networks, captures WPA/WPA2 handshakes, and exploits WPS/WEP weaknesses using a supported USB Wi-Fi adapter, without relying on aircrack-ng or OS kernel drivers.
- 34
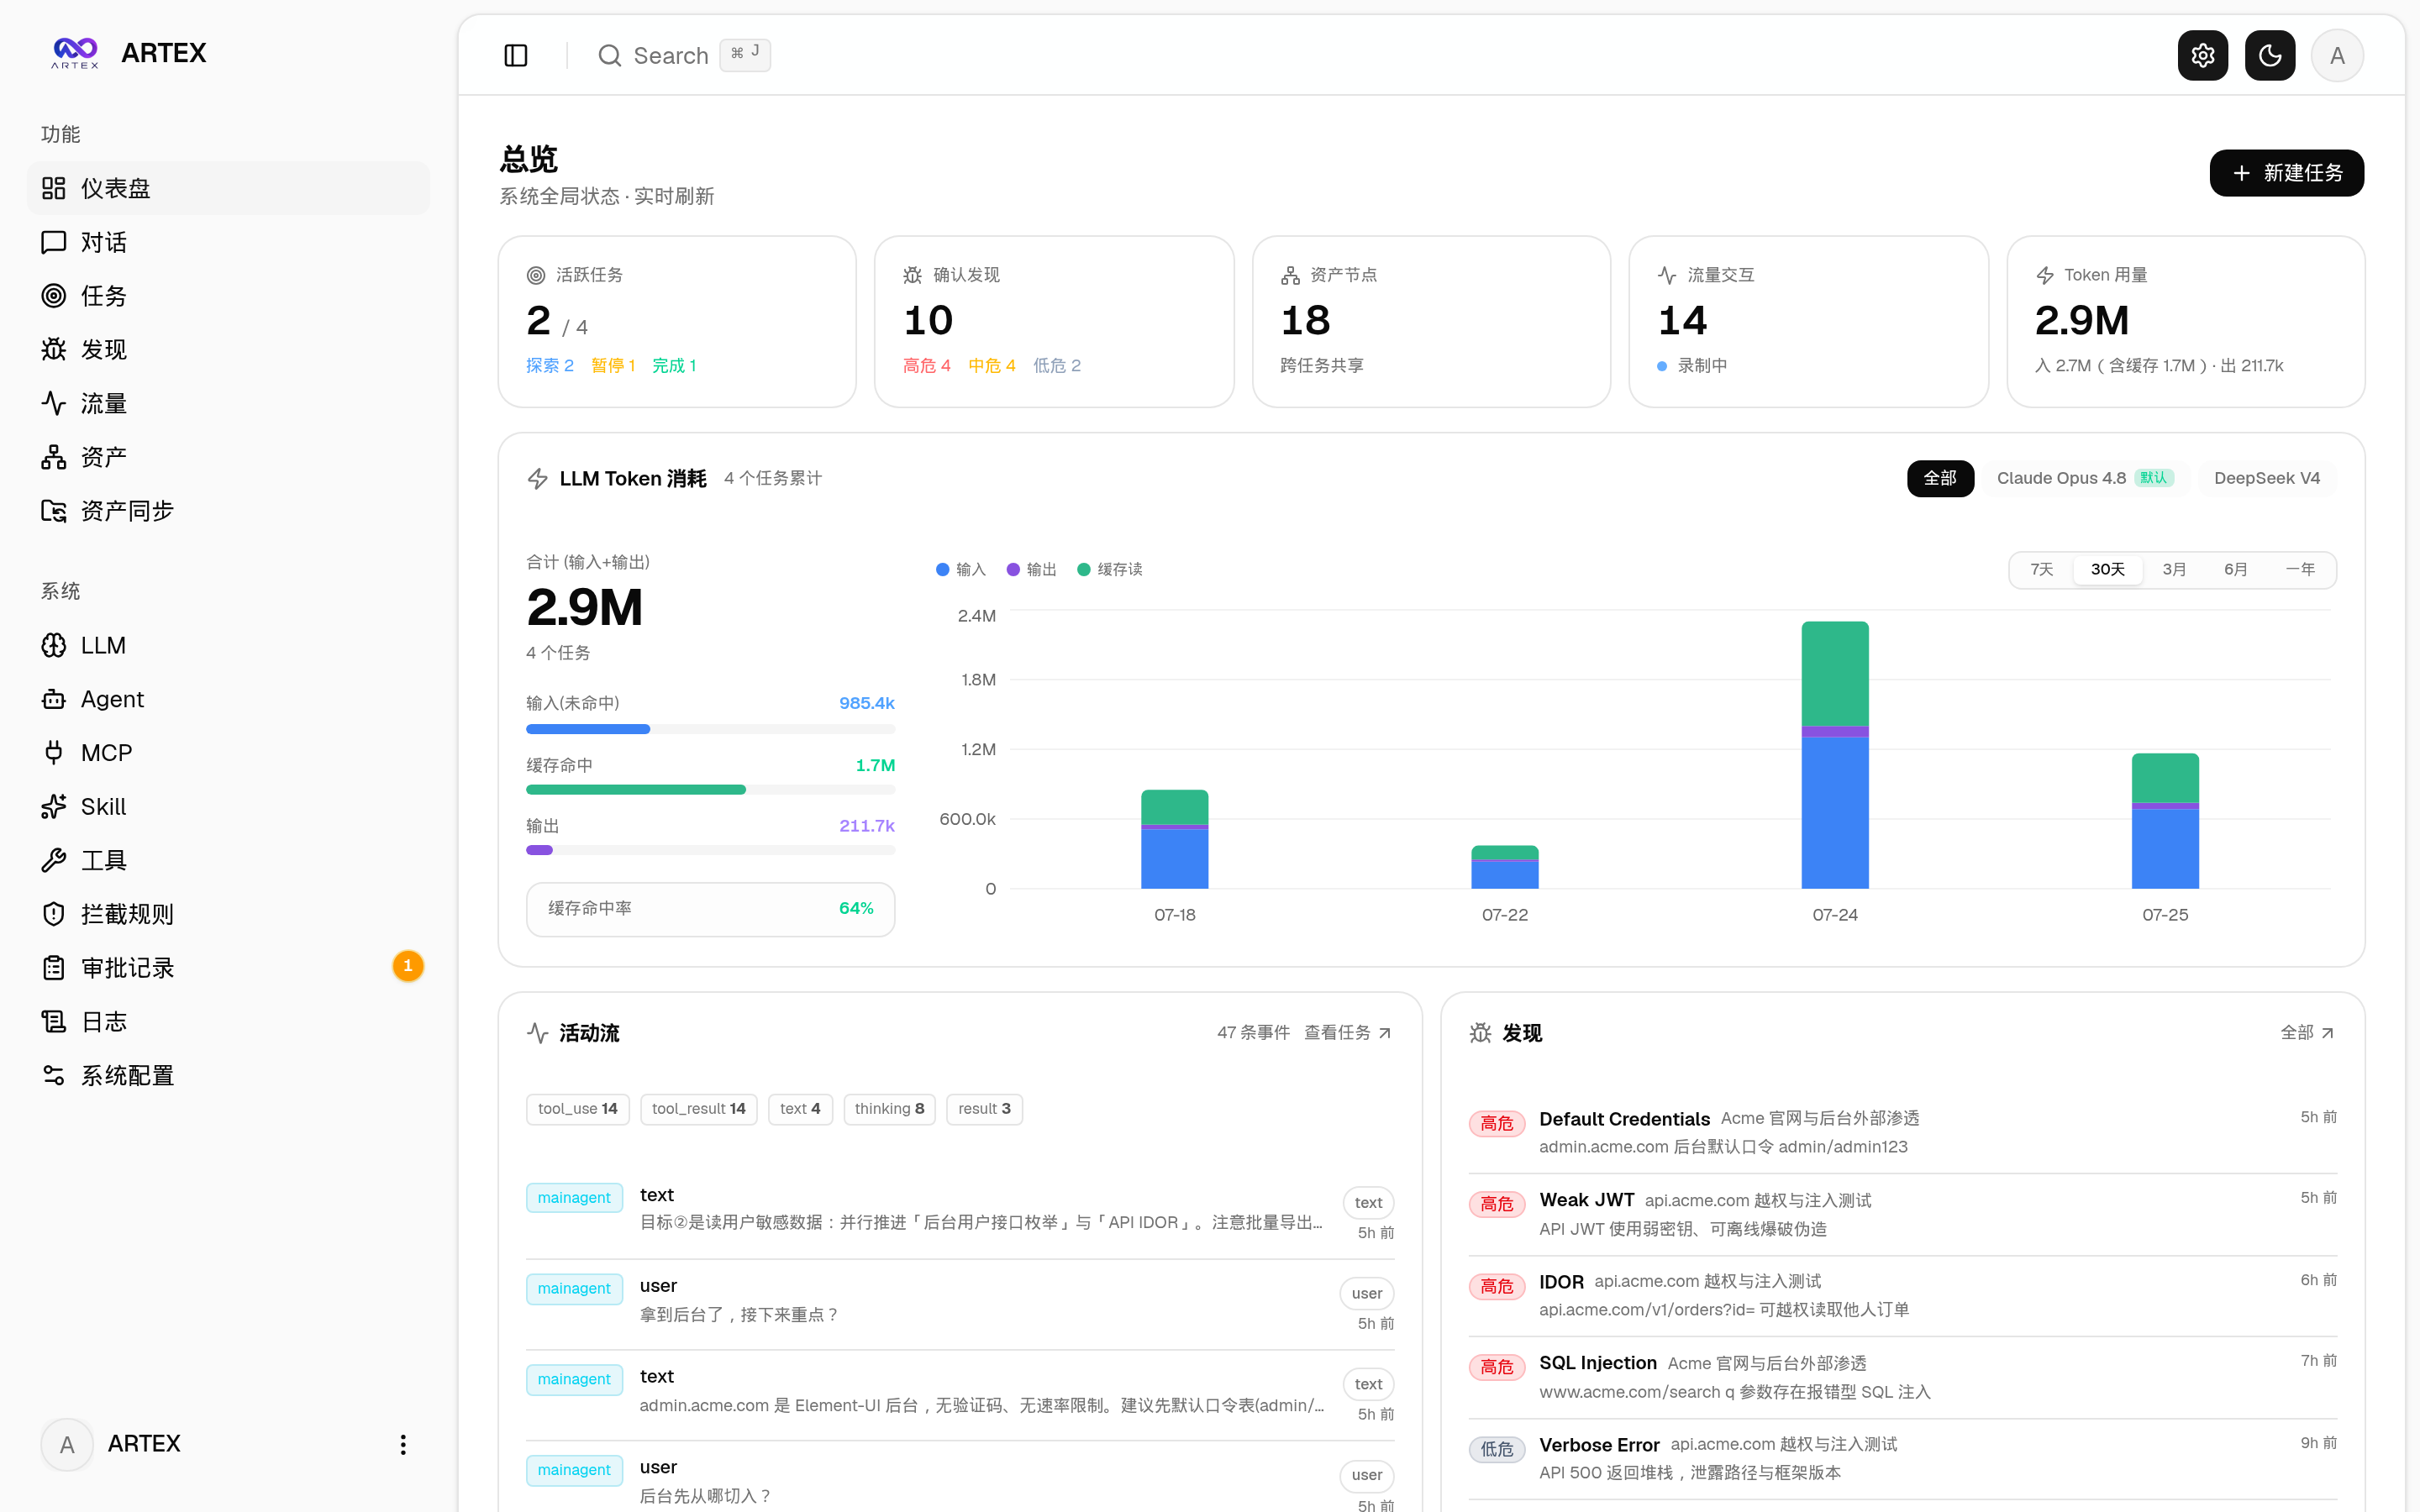
ARTEX
1.2Ktrhhubsd/ARTEX · GoARTEX is an AI-driven autonomous penetration testing system (Go backend + Next.js frontend) where LLM-powered planner and worker agents explore targets, map assets, and find vulnerabilities on their own.
- 35
oss-scanner
1Kanthropics/oss-scanner · DockerfileOSS Scanner is a service run by Anthropic that scans enrolled open-source repositories for security vulnerabilities, building each project in an isolated VM and emailing the maintainer a reproducer plus a proposed patch for anything it finds.
- 36
Cybermes
946Zyrexnn/Cybermes · PythonCybermes is an offensive security assistant and automation framework for authorized bug bounty hunting, reconnaissance, vulnerability research, and structured reporting, driven by AI agents and a library of 200+ playbooks.
- 37

cve-lite-cli
769OWASP/cve-lite-cli · TypeScriptMost tools tell you what's wrong. CVE Lite CLI tells you what to run.
- 38

VulnHunter
735nealbridges/VulnHunter · PythonAn open-source, agentic AI security scanner that reasons like an attacker to find exploitable vulnerabilities in source code, proves them with executable proof-of-concept exploits, and fixes them test-first. It is a maintained fork of Capital One's VulnHunter, rebuilt to run on any agent harness instead of just Claude Code.
- 39
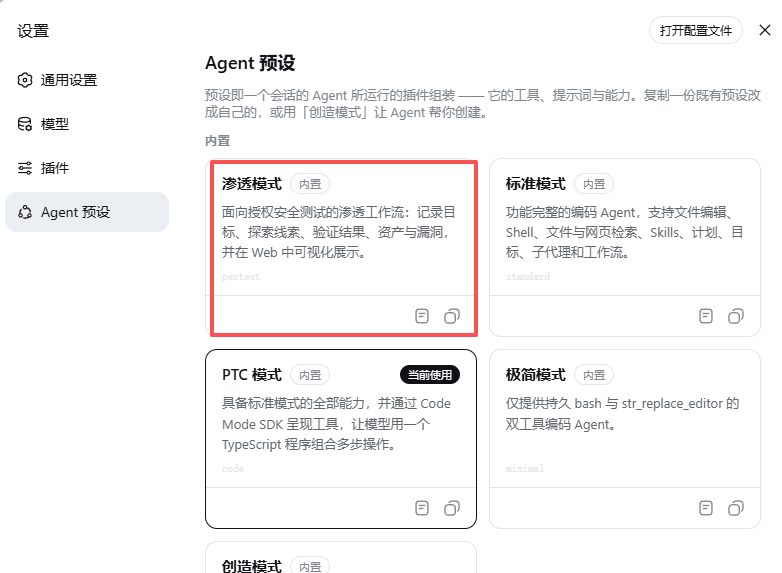
dsh-pentest
608howmp/dsh-pentest · JavaScriptdsh-pentest is a pentest-mode plugin for DeepSeek Harness (dsh) that tracks an authorized penetration test as a structured graph of goals, leads, facts, findings and assets, then shows that graph, the vulnerabilities and a report in a Web UI.
- 40
0
5120sec-labs/0 · TypeScript0 is an open-source, self-evolving, multi-model AI harness for security research that finds, verifies, and fixes vulnerabilities, built by the Swiss Applied AI & Cybersecurity Research Lab.
- 41

CVE-2026-9830
477opaxial/CVE-2026-9830 · PythonA Python proof-of-concept that validates a reported unauthenticated REST API exposure in the BookingPress Pro WordPress plugin, which can leak booking and customer data.
- 42

Airsec
150bas3line/Airsec · TypeScriptAirsec is a CLI tool that drives a coding agent you already have installed (Claude Code, Codex, OpenCode, Command Code) through a structured, multi-pass security audit of your code, then turns the findings into an actionable report.
- 43

Myrqen
137stijnswapped/Myrqen · TypeScriptMyrqen is a security testing tool that runs inside a coding agent (Claude Code, Codex, or OpenCode) you already use: its own static analysis engine finds vulnerability candidates in your TypeScript/JavaScript code, then the agent dynamically verifies them against the app running on your machine.
Related topics
Often tagged together
- linux4,184
- security976
- security-tools282
- cybersecurity245
- macos3,544
- windows3,403
- open-source5,666
- penetration-testing126
- cli2,227
- docker1,660
- pentesting113
- cross-platform2,623
- devsecops38
- python2,383
- llm1,483
- offensive-security77
- terminal1,101
- red-team79
- self-hosted1,929
- ai1,955
- developer-tools2,924
- static-analysis125
- vulnerability50
- mit3,312