Topics / #pentest
Pentest projects on GitHub
Penetration testing payloads, roadmaps and attack tooling.
As of , the most-starred Pentest projects on GitHub are PayloadsAllTheThings (81.8K stars), shannon (49K stars) and nuclei (32.1K stars). GitHub.Locker tracks 26 Pentest repositories with 416K stars combined. The fastest-growing on October 16 was shannon, with +81 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
 +81
shannon
KeygraphHQ/shannon · ★ 49KShannon is an autonomous AI pentester that analyzes your web application's source code, maps attack vectors, and then executes real exploits against the running app to prove vulnerabilities before they reach production — 'no exploit, no report'.
 +27
PayloadsAllTheThings
swisskyrepo/PayloadsAllTheThings · ★ 81.8KA massive curated collection of payloads, bypass techniques, and exploitation methodology for web application security testing, pentesting, and CTF challenges.
 +21
nuclei
projectdiscovery/nuclei · ★ 32.1KA fast, open-source vulnerability scanner that runs YAML-based templates to find security issues in applications, APIs, networks, DNS and cloud configurations. Its checks come from a large global security community.
 +21
Decepticon
BitterSecurity/Decepticon · ★ 6.3KDecepticon is a professional autonomous Red Team agent that runs full attack chains — reconnaissance, exploitation, privilege escalation, lateral movement, and C2 — the way a real adversary would, instead of just scanning and printing a report.
The all-time top
26 projects · by stars
- 81.8K#1 · swisskyrepo/PayloadsAllTheThings
PayloadsAllTheThings
A massive curated collection of payloads, bypass techniques, and exploitation methodology for web application security testing, pentesting, and CTF challenges.
- 49K#2 · KeygraphHQ/shannon
shannon
Shannon is an autonomous AI pentester that analyzes your web application's source code, maps attack vectors, and then executes real exploits against the running app to prove vulnerabilities before they reach production — 'no exploit, no report'.
- 32.1K#3 · projectdiscovery/nuclei
nuclei
A fast, open-source vulnerability scanner that runs YAML-based templates to find security issues in applications, APIs, networks, DNS and cloud configurations. Its checks come from a large global security community.
- 4
social-analyzer
24.3Kqeeqbox/social-analyzer · JavaScriptSocial-Analyzer is an OSINT tool that searches and correlates a person's profile across roughly 1000 social media sites and websites, available as a CLI, an API, and a web app.
- 5

Micro8
18KMicropoor/Micro8A free, open-source series of penetration-testing lessons written by veteran Chinese pentester Micropoor and published as a GitBook. It covers code audit, web, intranet and domain penetration, tunneling, and log-based tracing.
- 6
evilginx2
15.7Kkgretzky/evilginx2 · GoEvilginx is a man-in-the-middle attack framework used for phishing login credentials along with session cookies, which lets an attacker bypass 2-factor authentication.
- 7

hacker-roadmap
15.7Ksundowndev/hacker-roadmapThis is a curated roadmap and toolkit index for learning and practicing ethical hacking: it explains what penetration testing is and groups hundreds of security tools, wordlists and references by category (recon, password attacks, wireless, exploitation, web hacking, post-exploitation, frameworks).
- 8

social-engineer-toolkit
15.4Ktrustedsec/social-engineer-toolkit · PythonThe Social-Engineer Toolkit (SET) is an open-source penetration testing framework for authorized social-engineering assessments, giving security teams guided attack vectors to test user awareness and validate controls.
- 9
fscan
14.7Kshadow1ng/fscan · Gofscan is an open-source intranet scanner written in Go: one command runs an all-round internal-network audit — host discovery, port scanning, service identification, weak-password brute force and vulnerability detection.
- 10

PENTESTING-BIBLE
14KblaCCkHatHacEEkr/PENTESTING-BIBLEA curated catalog of over 200 numbered links to pentesting articles, bug bounty write-ups, cheat sheets and other security lists — a reading collection, not software.
- 11

nmap
13.8Knmap/nmap · CNmap is the Network Mapper — a free, open-source tool for network discovery and security scanning. It finds live hosts, open ports, and the services running on them, from a single machine up to whole subnets.
- 12
GTFOBins.github.io
13.8KGTFOBins/GTFOBins.github.io · YAMLGTFOBins is a curated list of Unix-like executables that can be abused to bypass local security restrictions in misconfigured systems — for example, binaries a restricted user can turn into a root shell.
- 13

PowerSploit
13.1KPowerShellMafia/PowerSploit · PowerShellPowerSploit is a collection of PowerShell modules that penetration testers use during all phases of an assessment, covering code execution, persistence, privilege escalation, credential theft, exfiltration and reconnaissance on Windows systems.
- 14

hacktricks
12.6KHackTricks-wiki/hacktricks · JavaScriptA free, open wiki of hacking tricks and techniques — everything the author has learnt from CTFs, real-world apps and security research, organized into a browsable reference with 12.5k+ GitHub stars.
- 15

thc-hydra
12.4Kvanhauser-thc/thc-hydra · CHydra is a parallelized network login cracker by van Hauser / THC: a proof-of-concept tool showing researchers and security consultants how easily a remote system can be broken into through weak passwords. It supports over 50 protocols.
- 16

Resources-for-Beginner-Bug-Bounty-Hunters
12.3Knahamsec/Resources-for-Beginner-Bug-Bounty-HuntersA curated collection of resources for people getting started with web hacking and bug bounty hunting, including blog posts, talks, books, tools, labs and vulnerability-type guides.
- 17
xray
11.8Kchaitin/xray · Vuexray is a security assessment tool built by Chaitin for scanning common web vulnerabilities and running custom PoCs against targets.
- 18
Detect-It-Easy
11.7Khorsicq/Detect-It-Easy · JavaScriptDetect It Easy (DiE) is a cross-platform tool that identifies file types and inspects executables (PE, ELF, Mach-O) for malware analysts, reverse engineers, and cybersecurity researchers, combining signature-based detection with a deep heuristic engine.
- 19

beef
11.1Kbeefproject/beef · JavaScriptBeEF (Browser Exploitation Framework) is a penetration testing tool that focuses on the web browser, letting a tester assess the real security posture of a target by using client-side attack vectors instead of network-perimeter exploits.
- 20

webshell
10.8Ktennc/webshell · PHPIt's a community collection of webshells - scripts that give you control of a web server once uploaded - covering all the common server-side languages and maintained by tennc with 10k+ stars.
- 21
Decepticon
6.3KBitterSecurity/Decepticon · PythonDecepticon is a professional autonomous Red Team agent that runs full attack chains — reconnaissance, exploitation, privilege escalation, lateral movement, and C2 — the way a real adversary would, instead of just scanning and printing a report.
- 22
redamon
3.1Ksamugit83/redamon · PythonRedAmon is an open-source, self-hosted AI framework that chains reconnaissance, exploitation and post-exploitation into one pipeline, maps the attack surface into a Neo4j graph, and then triages findings and opens GitHub pull requests that fix what it discovers.
- 23
dsh-redteam-model
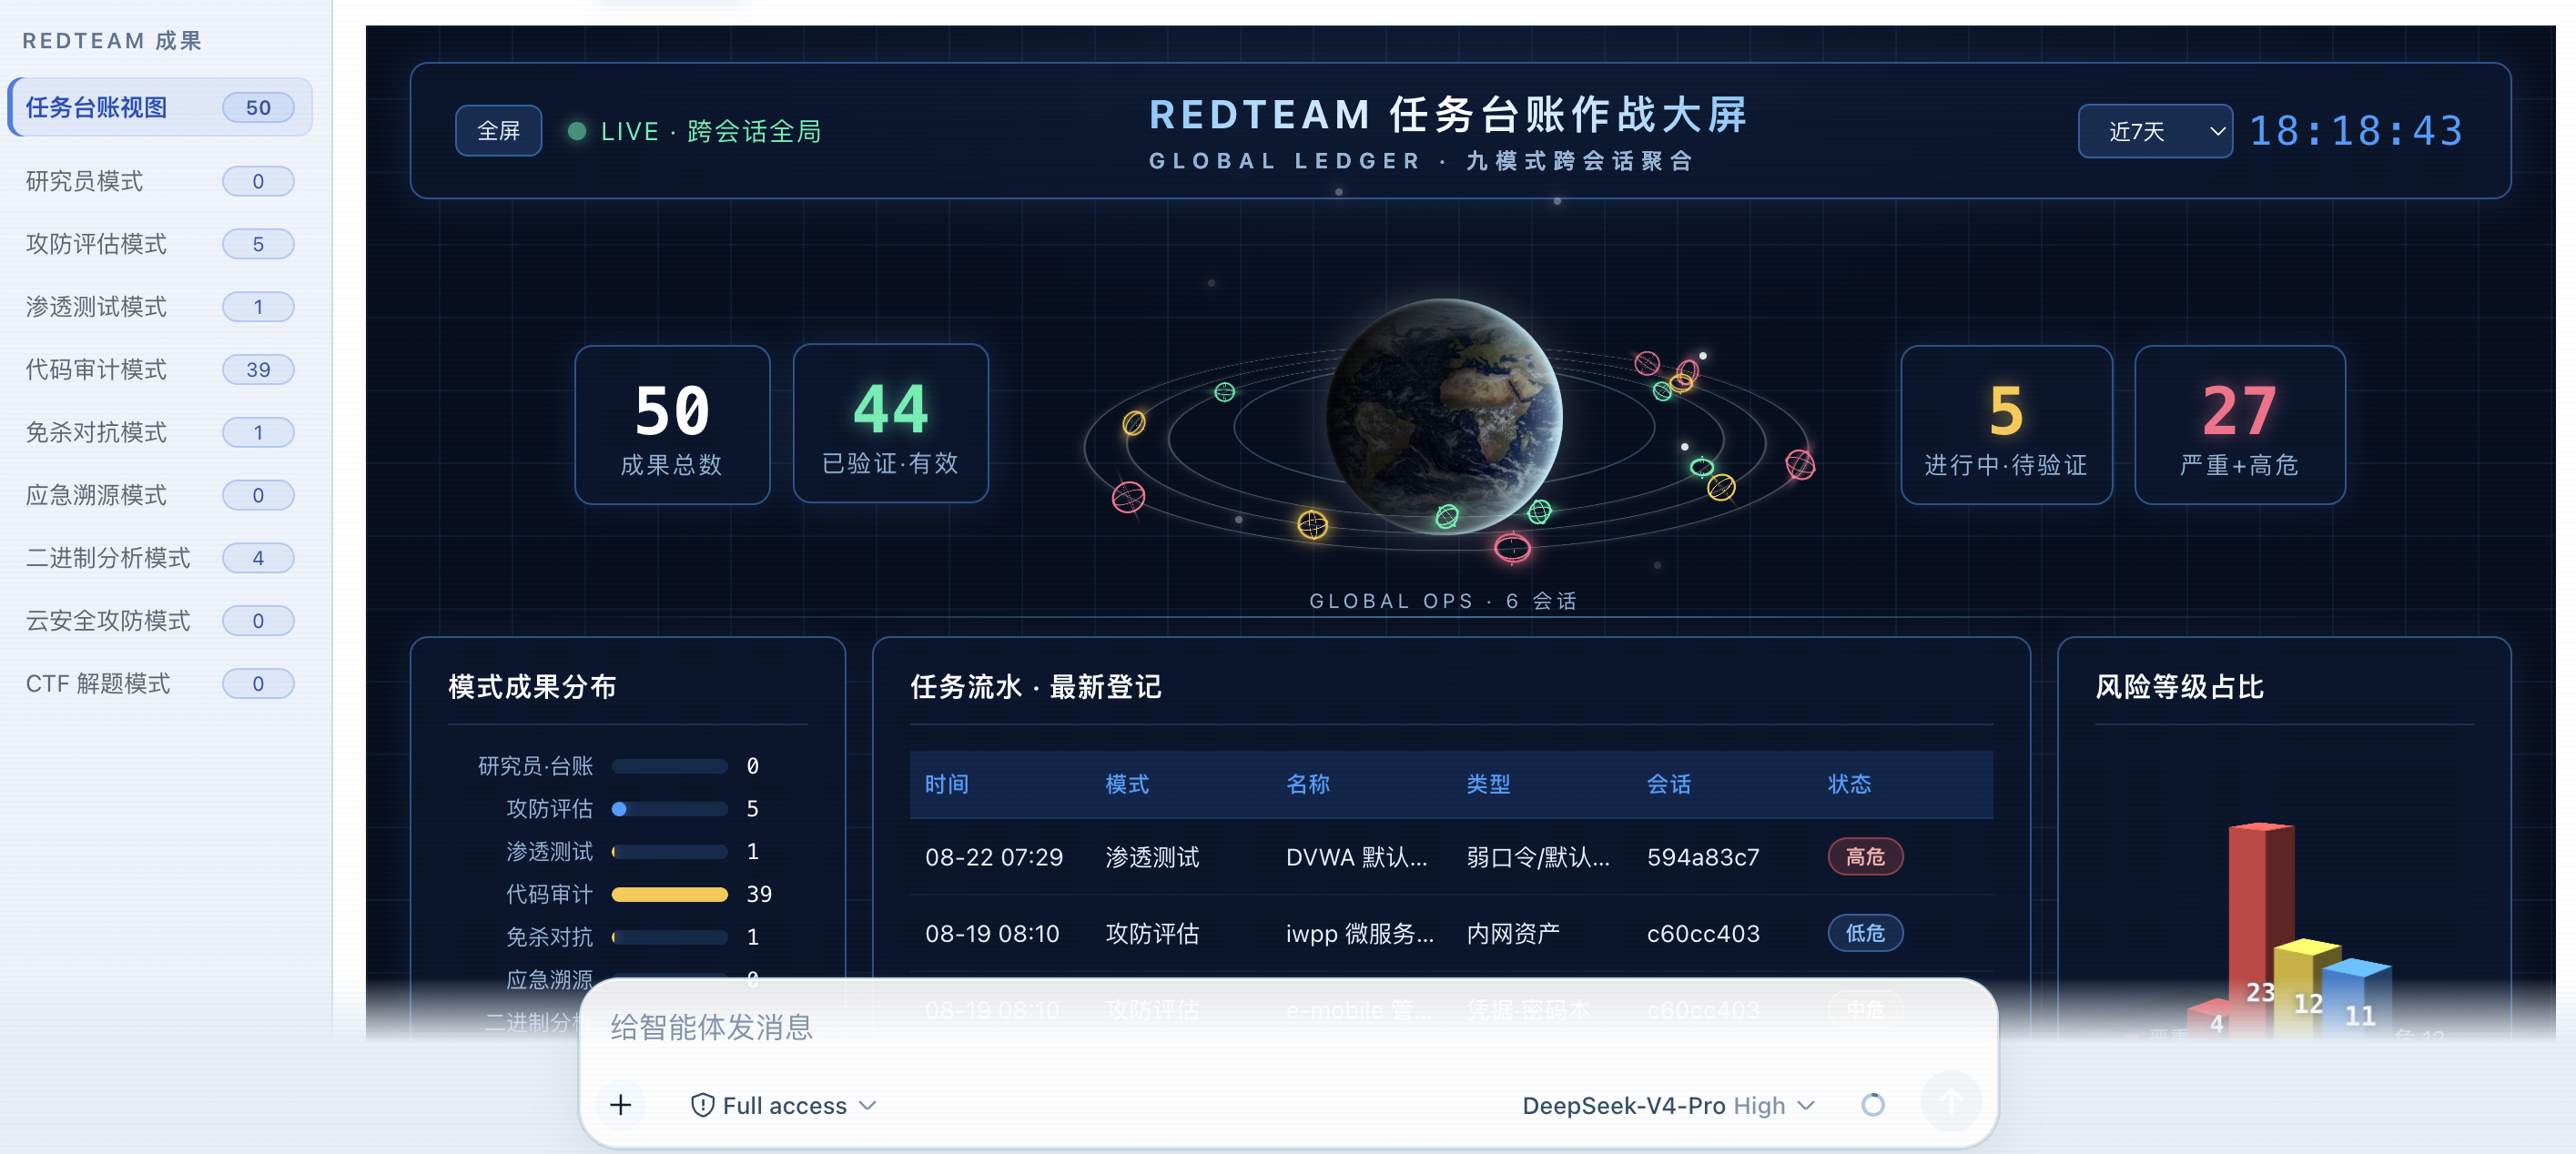
719SeaOf0/dsh-redteam-model · PythonA plugin pack for the dsh (DeepSeek Harness) AI agent that adds nine preset red-team security research modes and seventeen runtime plugins, covering pentesting, code audit, binary analysis, anti-detection, incident response, cloud security and CTF solving.
- 24
Offensive-Security-AI-Models
691JoasASantos/Offensive-Security-AI-ModelsA curated list of open-weight, uncensored language models fine-tuned for offensive-security tasks like penetration testing, red teaming, and security research. The README documents over 20 models sourced from HuggingFace model cards as of September 2026.
- 25

bug-bounty-hunting-prompts
621mdpsec/bug-bounty-hunting-promptsA pack of reusable prompt files for running a structured, evidence-first bug bounty hunting workflow with an LLM agent, covering recon through triage and escalation.
- 26
dsh-pentest
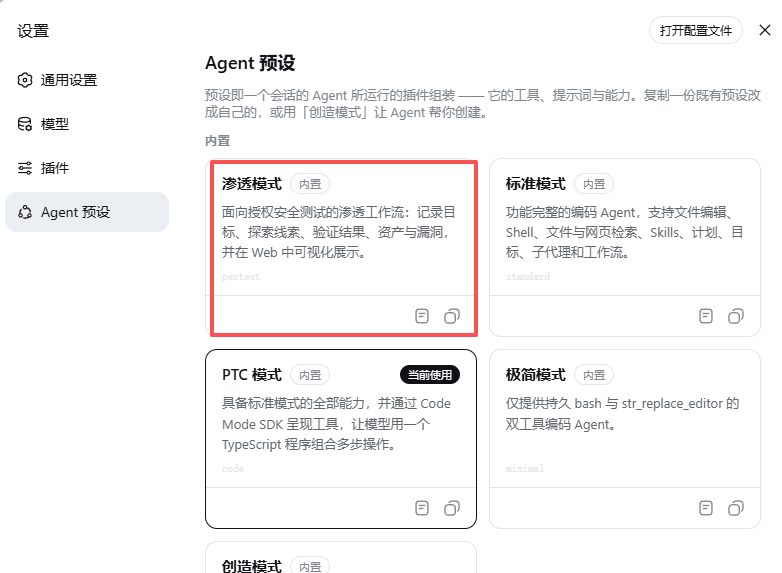
608howmp/dsh-pentest · JavaScriptdsh-pentest is a pentest-mode plugin for DeepSeek Harness (dsh) that tracks an authorized penetration test as a structured graph of goals, leads, facts, findings and assets, then shows that graph, the vulnerabilities and a report in a Web UI.
Related topics
Often tagged together
- security977
- penetration-testing125
- cybersecurity244
- security-tools281
- hacking135
- linux4,182
- offensive-security77
- red-team78
- macos3,544
- open-source5,666
- windows3,401
- pentesting112
- cli2,227
- cross-platform2,622
- hacking-tool75
- exploit51
- self-hosted1,927
- tool1,294
- vulnerability49
- docker1,658
- ethical-hacking24
- mit3,311
- osint68
- python2,396