Topics / #bugbounty
Bugbounty projects on GitHub
Bug bounty hunting and web security testing
As of , the most-starred Bugbounty projects on GitHub are PayloadsAllTheThings (81.8K stars), runtime (18.4K stars) and ffuf (16.9K stars). GitHub.Locker tracks 16 Bugbounty repositories with 269.4K stars combined. The fastest-growing on October 18 was hexstrike-ai, with +32 stars in a day.
Hot right now
Most stars gained in a day · Oct 18
 +32
hexstrike-ai
0x4m4/hexstrike-ai · ★ 12.9KHexStrike AI MCP Agents is an MCP server that lets AI agents like Claude, GPT, or Copilot autonomously run 150+ real cybersecurity tools for automated pentesting, bug bounty hunting, CTF challenges, and vulnerability discovery.
 +30
PayloadsAllTheThings
swisskyrepo/PayloadsAllTheThings · ★ 81.8KA massive curated collection of payloads, bypass techniques, and exploitation methodology for web application security testing, pentesting, and CTF challenges.
 +20
Claude-BugHunter
elementalsouls/Claude-BugHunter · ★ 5.2KA drop-in skill bundle for the Claude Code skills system that turns Claude into a bug-hunting researcher or red-team operator: it ships 83 skills, 15 slash commands, and knowledge curated from 681 disclosed HackerOne reports across 24 vulnerability classes, plus enterprise identity and infrastructure attack matrices.
 +14
nuclei-templates
projectdiscovery/nuclei-templates · ★ 13.1KThis is a community-curated collection of over 11,000 detection templates for the Nuclei vulnerability scanner, covering CVEs, misconfigurations, exposed panels, and other security issues.
The all-time top
16 projects · by stars
- 81.8K#1 · swisskyrepo/PayloadsAllTheThings
PayloadsAllTheThings
A massive curated collection of payloads, bypass techniques, and exploitation methodology for web application security testing, pentesting, and CTF challenges.
- 18.4K
 #2 · dotnet/runtime
runtime
This is the source code for the .NET runtime itself - the code that builds the runtime, its base class libraries, and the shared host (dotnet) installers for all supported platforms.
- 16.9K
 #3 · ffuf/ffuf
ffuf
ffuf is a fast web fuzzer written in Go — a command-line tool that sends many crafted requests to a target to discover directories, virtual hosts, and fuzzable GET/POST parameters.
- 4
dirsearch
15Kmaurosoria/dirsearch · PythonDirsearch is an advanced command-line web path brute-forcer used to discover hidden files and directories on websites for security testing.
- 5
subfinder
14.6Kprojectdiscovery/subfinder · GoSubfinder is a fast passive subdomain enumeration tool that returns valid subdomains for a website by querying passive online sources, built for penetration testers and bug bounty hunters.
- 6
nuclei-templates
13.1Kprojectdiscovery/nuclei-templates · JavaScriptThis is a community-curated collection of over 11,000 detection templates for the Nuclei vulnerability scanner, covering CVEs, misconfigurations, exposed panels, and other security issues.
- 7
hexstrike-ai
12.9K0x4m4/hexstrike-ai · PythonHexStrike AI MCP Agents is an MCP server that lets AI agents like Claude, GPT, or Copilot autonomously run 150+ real cybersecurity tools for automated pentesting, bug bounty hunting, CTF challenges, and vulnerability discovery.
- 8

hacktricks
12.6KHackTricks-wiki/hacktricks · JavaScriptA free, open wiki of hacking tricks and techniques — everything the author has learnt from CTFs, real-world apps and security research, organized into a browsable reference with 12.5k+ GitHub stars.
- 9
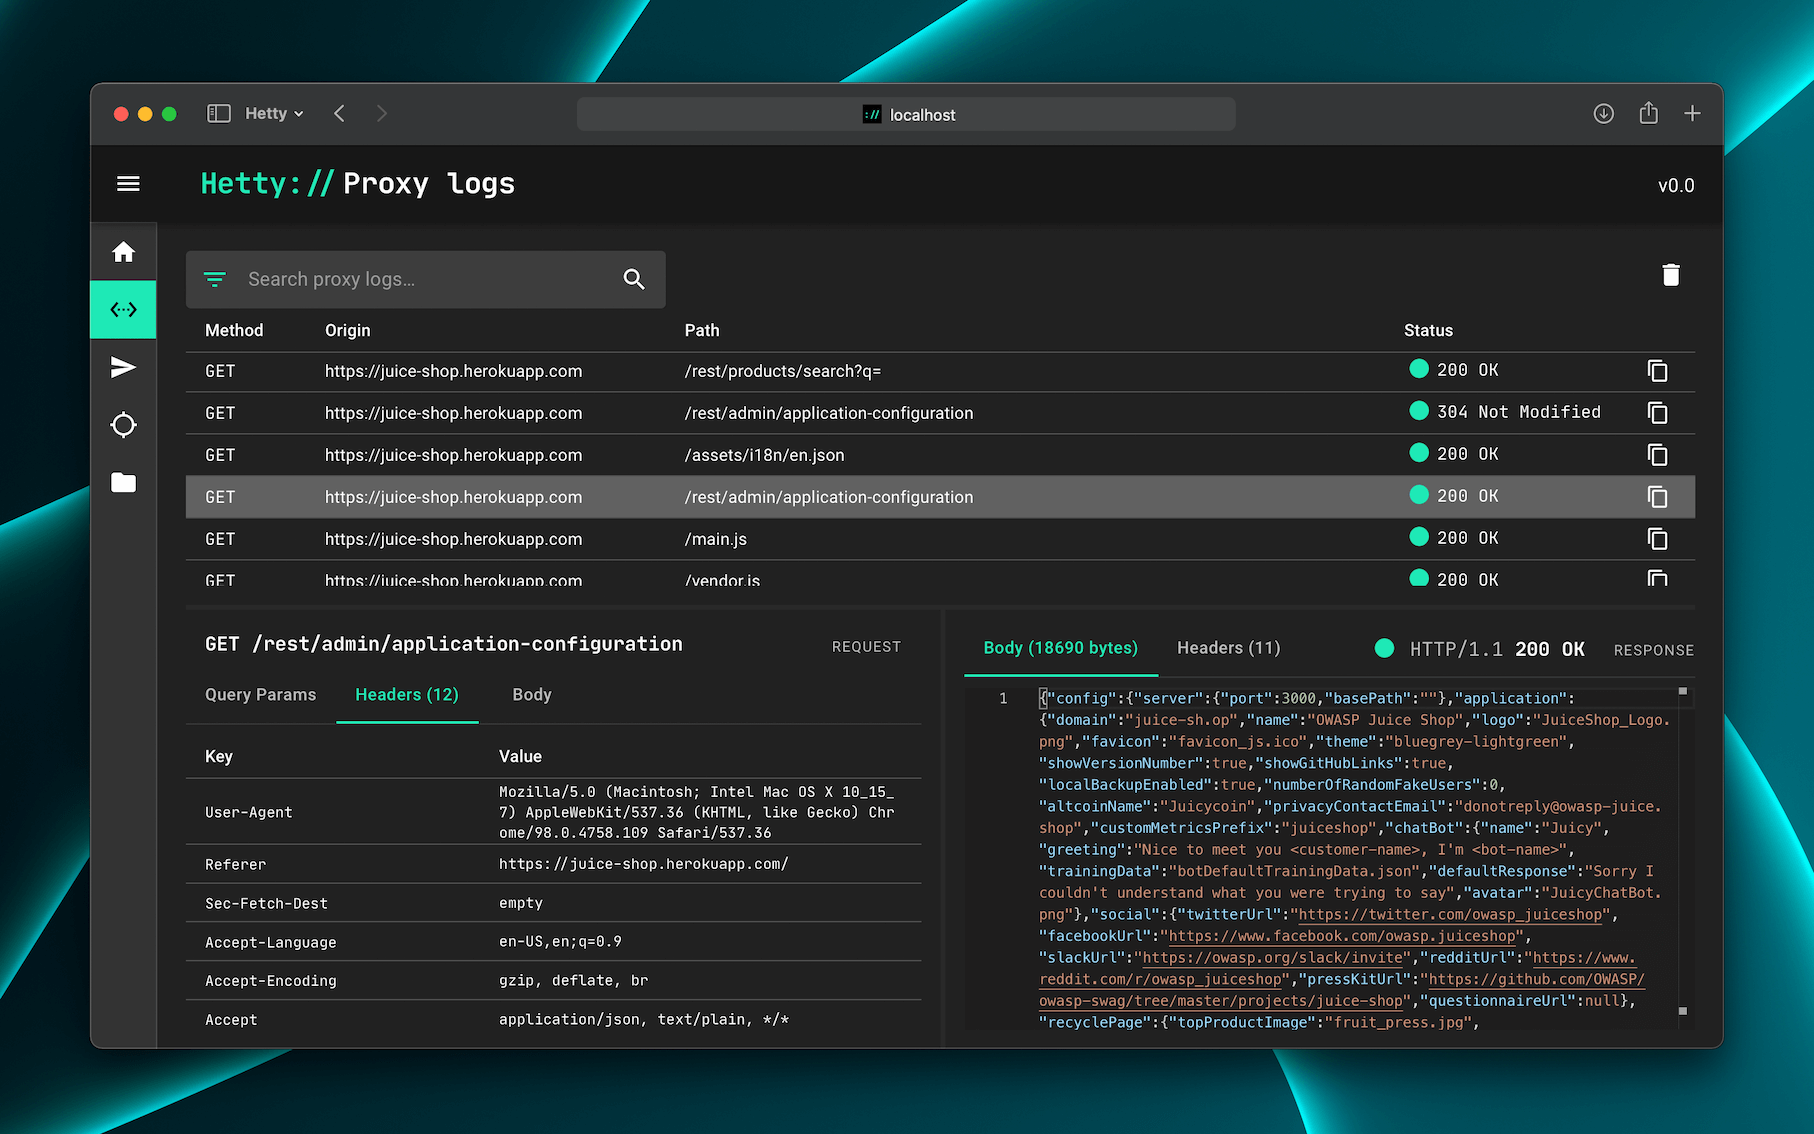
hetty
12.5Kdstotijn/hetty · GoHetty is an HTTP toolkit for security research, aiming to be an open source alternative to commercial tools like Burp Suite Pro, aimed at the infosec and bug bounty community.
- 10

Resources-for-Beginner-Bug-Bounty-Hunters
12.3Knahamsec/Resources-for-Beginner-Bug-Bounty-HuntersA curated collection of resources for people getting started with web hacking and bug bounty hunting, including blog posts, talks, books, tools, labs and vulnerability-type guides.
- 11
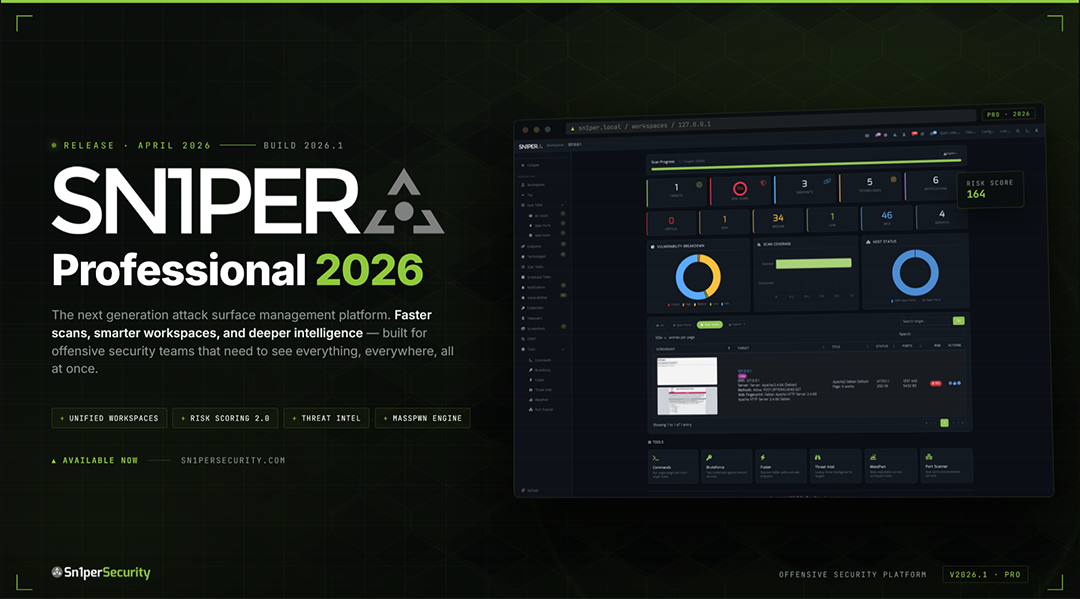
Sn1per
11.5K1N3/Sn1per · ShellSn1per is an offensive-security platform that bundles reconnaissance, vulnerability scanning, exploitation and reporting into one workspace, orchestrating 600+ exploits and 90+ third-party tools for pentesters and attack-surface-management teams.
- 12
awesome-hacker-search-engines
11.3Kedoardottt/awesome-hacker-search-engines · ShellA curated list of search engines useful for penetration testing, vulnerability assessment, red/blue team operations, bug bounty hunting, and general OSINT work.
- 13
bbot
10.7Kblacklanternsecurity/bbot · PythonBBOT is a recursive internet scanner for hackers — it automates recon, bug bounty work and attack surface management (ASM), inspired by Spiderfoot.
- 14
httpx
10.5Kprojectdiscovery/httpx · Gohttpx is a fast, multi-purpose HTTP toolkit from ProjectDiscovery that runs many probes against lists of hosts and URLs, built on the retryablehttp library to stay reliable under high thread counts.
- 15
OneForAll
10.1Kshmilylty/OneForAll · PythonOneForAll is a powerful subdomain collection tool: point it at a target domain and it gathers subdomains from many sources — a core reconnaissance step in penetration testing, which is why the author built it.
- 16
Claude-BugHunter
5.2Kelementalsouls/Claude-BugHunter · PythonA drop-in skill bundle for the Claude Code skills system that turns Claude into a bug-hunting researcher or red-team operator: it ships 83 skills, 15 slash commands, and knowledge curated from 681 disclosed HackerOne reports across 24 vulnerability classes, plus enterprise identity and infrastructure attack matrices.
Related topics
Often tagged together
- penetration-testing128
- security998
- linux4,248
- cybersecurity249
- macos3,608
- pentesting114
- security-tools287
- windows3,480
- hacking139
- mit3,387
- open-source5,749
- osint69
- cli2,275
- docker1,684
- reconnaissance40
- red-team82
- cross-platform2,673
- hacktoberfest454
- offensive-security78
- python2,425
- terminal1,128
- infosec47
- web-security32
- bug-bounty17