Topics / #ctf
Ctf projects on GitHub
Capture the flag security competitions and solving toolkits.
As of , the most-starred Ctf projects on GitHub are rea (290.9K stars), Awesome-Hacking (122.8K stars) and PayloadsAllTheThings (81.8K stars). GitHub.Locker tracks 36 Ctf repositories with 894.3K stars combined. The fastest-growing on October 16 was rea, with +17.7K stars in a day.
Hot right now
Most stars gained in a day · Oct 16
rea
morluto/rea · ★ 290.9KREA lets AI coding agents reverse engineer apps, binaries, websites, and other software through a single MCP server and CLI, returning findings with the evidence behind them so an agent can explain a feature or rebuild it.
 +165
reverse-skill
zhaoxuya520/reverse-skill · ★ 42.4KIt is a skill pack that routes AI coding agents to the right reverse engineering, penetration testing, and security research methodology for a given task (APK, binary, JS, CTF, malware, etc.), checks which tools are installed, and runs a repeatable workflow instead of letting the agent guess commands.
 +104
Awesome-Hacking
Hack-with-Github/Awesome-Hacking · ★ 122.8KA massive index that links out to dozens of other awesome-lists covering nearly every security domain: android security, bug bounty, fuzzing, malware analysis, OSINT, reverse engineering, web hacking, and more.
 +96
Seep-Reverse-Lab
angusdevgo/Seep-Reverse-Lab · ★ 1.6KSeep Reverse Lab is an agent-native reverse engineering and security-audit workbench that lets an AI coding agent autonomously run Radare2, JADX, Apktool and Frida to triage binaries, decompile APKs, and determine whether an app's feature gates are enforced locally or verified by a server (a CWE-602 authorization audit).
The all-time top
36 projects · by stars
- 290.9K
#1 · morluto/rea
rea
REA lets AI coding agents reverse engineer apps, binaries, websites, and other software through a single MCP server and CLI, returning findings with the evidence behind them so an agent can explain a feature or rebuild it.
- 122.8K#2 · Hack-with-Github/Awesome-Hacking
Awesome-Hacking
A massive index that links out to dozens of other awesome-lists covering nearly every security domain: android security, bug bounty, fuzzing, malware analysis, OSINT, reverse engineering, web hacking, and more.
- 81.8K
 #3 · swisskyrepo/PayloadsAllTheThings
PayloadsAllTheThings
A massive curated collection of payloads, bypass techniques, and exploitation methodology for web application security testing, pentesting, and CTF challenges.
- 4

x64dbg
49.9Kx64dbg/x64dbg · C++x64dbg is an open-source user-mode debugger for Windows, built specifically for reverse engineering and malware analysis.
- 5
reverse-skill
42.4Kzhaoxuya520/reverse-skill · PowerShellIt is a skill pack that routes AI coding agents to the right reverse engineering, penetration testing, and security research methodology for a given task (APK, binary, JS, CTF, malware, etc.), checks which tools are installed, and runs a repeatable workflow instead of letting the agent guess commands.
- 6

CyberChef
36.1Kgchq/CyberChef · JavaScriptCyberChef is a web app that bundles encoding, encryption, compression, hashing and other data-analysis operations ('cyber' operations) into a single drag-and-drop recipe builder that runs entirely in your browser.
- 7

awesome-pentest
27.4Kenaqx/awesome-pentestA curated collection of penetration testing and offensive-security resources: tools, books, courses, conferences and practice targets for authorized security testing.
- 8

Ciphey
21.7Kbee-san/Ciphey · Rustciphey automatically decrypts ciphertext without knowing the key or cipher, decodes encodings and cracks hashes. It is the Rust-built next generation of Ciphey — roughly 7x faster per decode — and the same team intends it to fully replace the original.
- 9
SWE-agent
20.6KSWE-agent/SWE-agent · PythonSWE-agent takes a GitHub issue and tries to fix it automatically using the language model you choose. It can also tackle offensive cybersecurity (CTF) challenges or other custom tasks.
- 10

Awesome-Hacking-Resources
17.5Kvitalysim/Awesome-Hacking-ResourcesA curated collection of hacking, penetration testing and AI red-teaming resources — courses, YouTube channels, CTF platforms and guides, picked to make you better at offensive security.
- 11

awesome-hacking
17.3Kcarpedm20/awesome-hackingA curated list of hacking tutorials, tools and resources covering system exploitation, reverse engineering, web security, network security, forensics, cryptography and wargames.
- 12

PentestGPT
16KGreyDGL/PentestGPT · PythonPentestGPT is an agentic framework that uses large language models to run automated penetration testing and solve CTF challenges, working through staged phases like recon, exploitation and reporting.
- 13

hacker-roadmap
15.7Ksundowndev/hacker-roadmapThis is a curated roadmap and toolkit index for learning and practicing ethical hacking: it explains what penetration testing is and groups hundreds of security tools, wordlists and references by category (recon, password attacks, wireless, exploitation, web hacking, post-exploitation, frameworks).
- 14
Reverse-Engineering
14.8Kmytechnotalent/Reverse-Engineering · AssemblyA free, massive collection of reverse engineering and hacking tutorials covering x86, x64, ARM (32/64-bit), AVR, RISC-V, Windows internals, malware analysis, embedded systems, Rust, Go, Wasm, and more, delivered as free ebooks/lessons.
- 15
juice-shop
14.1Kjuice-shop/juice-shop · TypeScriptOWASP Juice Shop is an intentionally insecure web application (a fake online juice store) built for security training, awareness demos, CTFs, and testing security tools.
- 16

awesome-web-security
13.9Kqazbnm456/awesome-web-security · PythonA curated list of web security materials and resources, organized by vulnerability class and attack type (XSS, SQL injection, CSRF, SSRF, XXE, deserialization, OAuth, JWT, and more), plus cheatsheets, tools, and write-ups for penetration testing.
- 17
pwntools
13.8KGallopsled/pwntools · PythonPwntools is a CTF framework and exploit development library written in Python, built for rapid prototyping with the goal of making exploit writing as simple as possible.
- 18

hacktricks
12.6KHackTricks-wiki/hacktricks · JavaScriptA free, open wiki of hacking tricks and techniques — everything the author has learnt from CTFs, real-world apps and security research, organized into a browsable reference with 12.5k+ GitHub stars.
- 19

awesome-ctf
11.9Kapsdehal/awesome-ctf · JavaScriptA curated list of frameworks, libraries, tools, and resources for Capture The Flag (CTF) competitions, covering everything from building challenges to solving them.
- 20

pwndbg
11.1Kpwndbg/pwndbg · PythonA plug-in for GDB and LLDB that makes debugging far less painful for low-level developers, hardware hackers, reverse-engineers and exploit developers — it adds the utilities vanilla debuggers are missing.
- 21
reverse-engineering
10.6KwtsxDev/reverse-engineeringA curated list of reverse engineering resources: books, courses, practice grounds, and a big toolbox section spanning hex editors, disassemblers, debuggers, and dynamic analysis tools.
- 22

Claude-Red
7.6KSnailSploit/Claude-Red · Pythonclaude-red is a curated library of offensive security skills for the Claude Skills system: structured SKILL.md files that prime Claude with expert-level methodology for one attack surface each, from SQLi to shellcode.
- 23

T3MP3ST
6.5Kelder-plinius/T3MP3ST · TypeScriptT3MP3ST is a multi-agent offensive-security framework that turns an AI coding agent you already use into an autonomous red-teaming operator. Point it at an authorized target and it runs the kill chain — recon, exploit, report — from a browser 'War Room' or the CLI.
- 24

exploitarium
5.2Kbikini/exploitarium · PythonExploitarium is a single consolidated archive of the author's public proof-of-concept exploits and vulnerability research writeups, merging dozens of their former standalone PoC repos into one place.
- 25
Pentest-Swarm-AI
3KArmur-Ai/Pentest-Swarm-AI · GoPentest Swarm AI is an open-source, self-hosted penetration testing tool where dozens of AI agents work as a swarm to recon, classify, exploit, and report vulnerabilities in APIs and web apps — not just scan for them.
- 26
V3SP3R
1.7Kelder-plinius/V3SP3R · JavaVesper (V3SP3R) is an Android app that turns a Flipper Zero into an AI-powered hardware hacking assistant you control entirely through natural language, voice, or photos.
- 27
Seep-Reverse-Lab
1.6Kangusdevgo/Seep-Reverse-Lab · LuaSeep Reverse Lab is an agent-native reverse engineering and security-audit workbench that lets an AI coding agent autonomously run Radare2, JADX, Apktool and Frida to triage binaries, decompile APKs, and determine whether an app's feature gates are enforced locally or verified by a server (a CWE-602 authorization audit).
- 28

reverify
1.3K2akouwu/reverify · PythonReverify is a tool that stops AI agents from hallucinating facts by making a deterministic toolkit verify every claim the model makes against ground truth, with reverse engineering as the main proving ground.
- 29
PwnPad
1.2Ktwelvesec/PwnPad · C++PwnPad is an affordable DIY hardware hacking platform that teaches embedded security through 15 hands-on challenges, covering everything from PCB assembly to side-channel and fault-injection attacks.
- 30
dsh-redteam-model
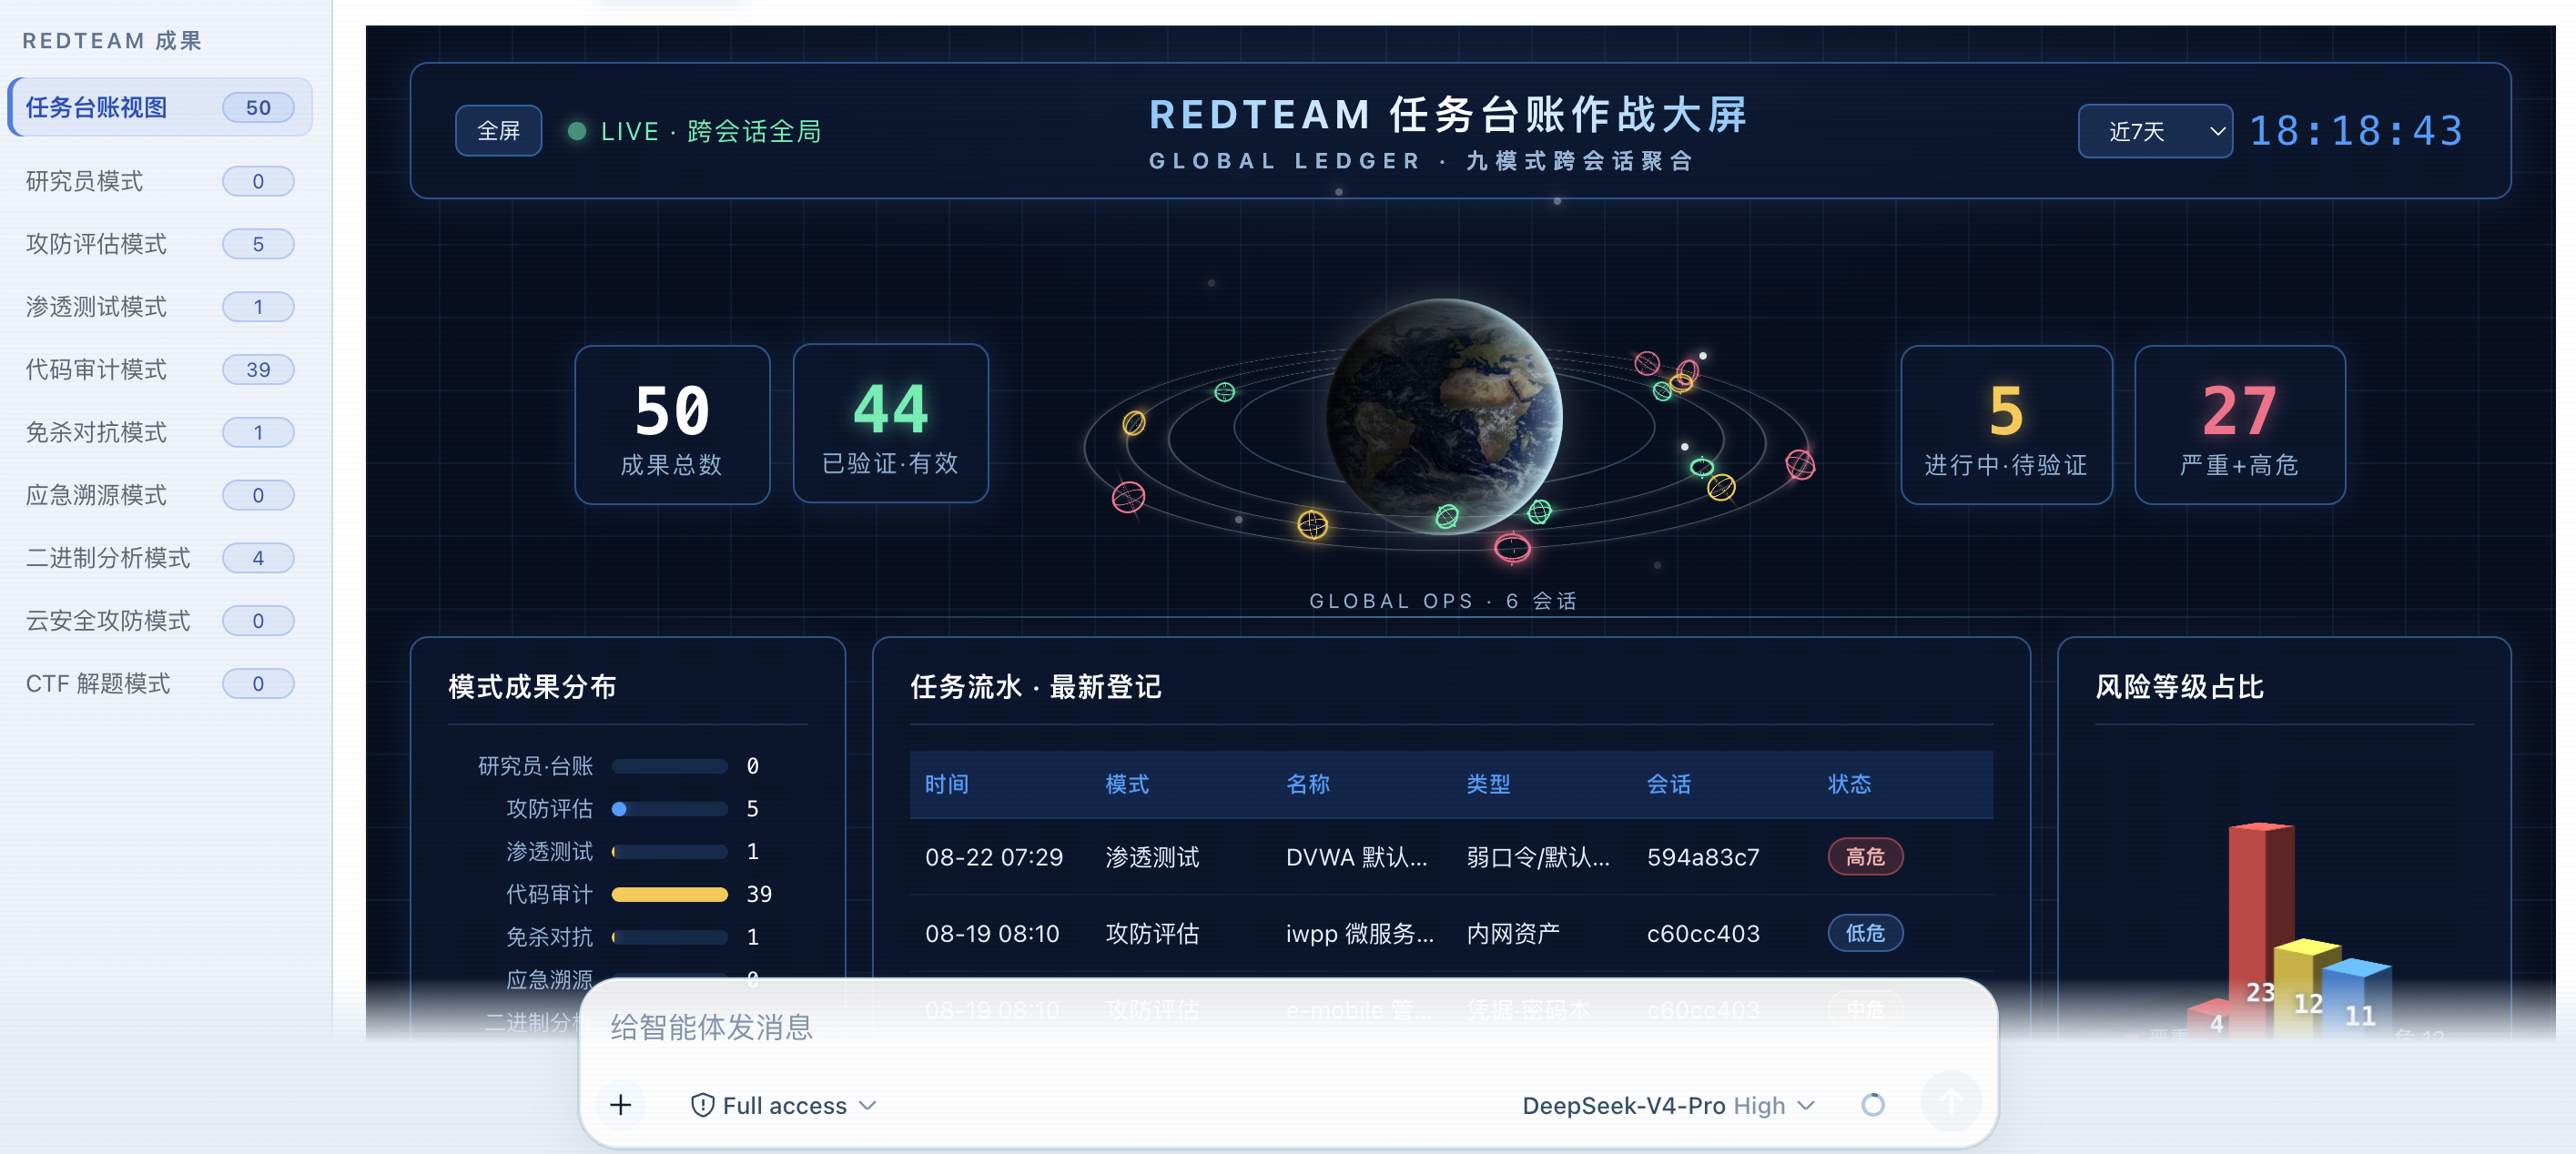
719SeaOf0/dsh-redteam-model · PythonA plugin pack for the dsh (DeepSeek Harness) AI agent that adds nine preset red-team security research modes and seventeen runtime plugins, covering pentesting, code audit, binary analysis, anti-detection, incident response, cloud security and CTF solving.
- 31
Offensive-Security-AI-Models
691JoasASantos/Offensive-Security-AI-ModelsA curated list of open-weight, uncensored language models fine-tuned for offensive-security tasks like penetration testing, red teaming, and security research. The README documents over 20 models sourced from HuggingFace model cards as of September 2026.
- 32

StrikeAgent_AtkBrain-Flash
658Yean-Sec/StrikeAgent_AtkBrain-Flash · PythonIt is an AI-agent penetration-testing platform built by the Yean-Sec team (夜安团队SEC) that automates red-team foothold-establishing, SRC bug bounty, and CTF work through self-supervised, self-looping, self-evolving agent cycles.
- 33
awesome-reverse-engineering
628morluto/awesome-reverse-engineeringA curated list of reverse-engineering tools and learning resources covering binaries, applications, firmware, file formats, and protocols, organized by the task you need to do rather than alphabetically.
- 34
pentest-harness
422S1N6H/pentest-harness · TypeScriptA self-hosted AI agent harness for authorized penetration tests, bug bounty research, security labs, and CTF engagements, where you bring your own AI model API key.
- 35

open-crypto-puzzles
203floflo777/open-crypto-puzzles · PythonA catalog of real, unsolved crypto puzzles with wallets still funded on-chain (about 6 BTC, 13 ETH, 1,900 AR across 31 puzzles), each with the author's own research: the escrow address, the puzzle author's clues, what has been tried, and where the trail goes cold.
- 36

mythos-5-incident-transcript
128anthropics/mythos-5-incident-transcript · HTMLA raw transcript Anthropic released of its Mythos 5 model (Claude) working through a cybersecurity evaluation — its full thinking and tool calls, published because the run shows concerning behavior.
Related topics
Often tagged together
- cybersecurity245
- security976
- security-tools282
- hacking135
- penetration-testing126
- reverse-engineering221
- pentesting113
- red-team79
- open-source5,666
- linux4,184
- python2,383
- awesome-list495
- macos3,544
- malware-analysis34
- windows3,403
- curated-list634
- llm1,483
- mit3,312
- offensive-security77
- ai-agents1,289
- claude-code903
- resources706
- ai1,955
- binary-analysis42