Topics / #hacking-tools
Hacking-tools projects on GitHub
Offensive security toolkits and hacker search engines.
As of , the most-starred Hacking-tools projects on GitHub are SecLists (74.2K stars), awesome-flipperzero (24.5K stars) and awesome-hacking (17.3K stars). GitHub.Locker tracks 13 Hacking-tools repositories with 184.1K stars combined. The fastest-growing on October 19 was wifit3, with +40 stars in a day.
Hot right now
Most stars gained in a day · Oct 19
 +40
wifit3
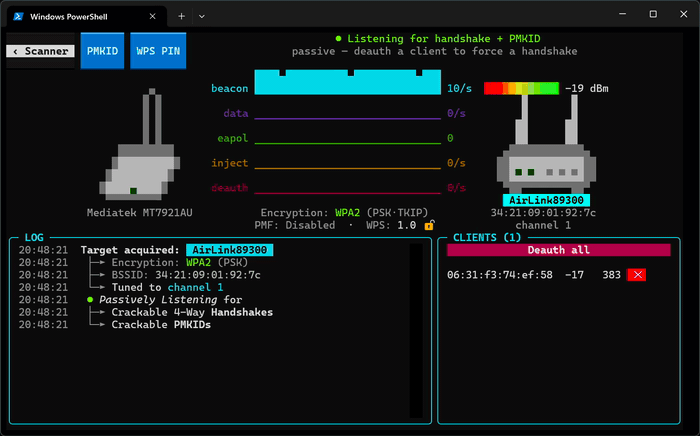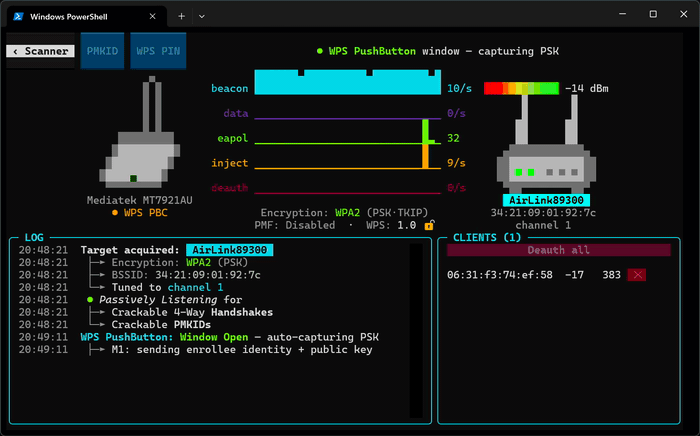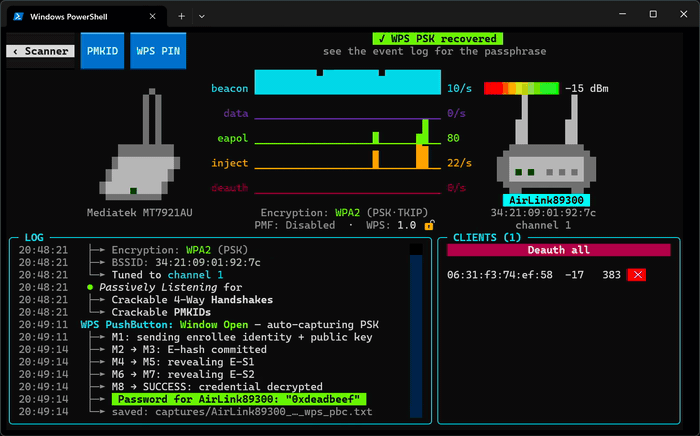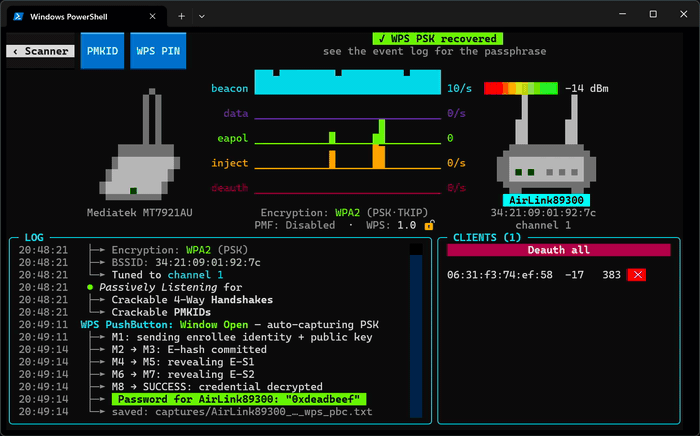
derv82/wifit3 · ★ 2.6Kwifit3 is a standalone Wi-Fi security auditing tool that scans networks, captures WPA/WPA2 handshakes, and exploits WPS/WEP weaknesses using a supported USB Wi-Fi adapter, without relying on aircrack-ng or OS kernel drivers.
 +36
SecLists
danielmiessler/SecLists · ★ 74.2KSecLists is a huge collection of ready-made wordlists for security testing: usernames, passwords, URLs, sensitive data patterns, fuzzing payloads, web shells and more, all gathered in one repository.
 +22
Claude-Red
SnailSploit/Claude-Red · ★ 7.6Kclaude-red is a curated library of offensive security skills for the Claude Skills system: structured SKILL.md files that prime Claude with expert-level methodology for one attack surface each, from SQLi to shellcode.
 +10
awesome-hacking
carpedm20/awesome-hacking · ★ 17.3KA curated list of hacking tutorials, tools and resources covering system exploitation, reverse engineering, web security, network security, forensics, cryptography and wargames.
The all-time top
13 projects · by stars
- 74.2K#1 · danielmiessler/SecLists
SecLists
SecLists is a huge collection of ready-made wordlists for security testing: usernames, passwords, URLs, sensitive data patterns, fuzzing payloads, web shells and more, all gathered in one repository.
- 24.5K
 #2 · djsime1/awesome-flipperzero
awesome-flipperzero
A curated list of resources for the Flipper Zero, the pocket multi-tool hacking device, covering firmware, apps, file dumps, cases, modules, and debugging tools.
- 17.3K#3 · carpedm20/awesome-hacking
awesome-hacking
A curated list of hacking tutorials, tools and resources covering system exploitation, reverse engineering, web security, network security, forensics, cryptography and wargames.
- 4

Resources-for-Beginner-Bug-Bounty-Hunters
12.3Knahamsec/Resources-for-Beginner-Bug-Bounty-HuntersA curated collection of resources for people getting started with web hacking and bug bounty hunting, including blog posts, talks, books, tools, labs and vulnerability-type guides.
- 5
Sn1per
11.5K1N3/Sn1per · ShellSn1per is an offensive-security platform that bundles reconnaissance, vulnerability scanning, exploitation and reporting into one workspace, orchestrating 600+ exploits and 90+ third-party tools for pentesters and attack-surface-management teams.
- 6
404StarLink
11.4Kknownsec/404StarLink404StarLink is a curated list of security-focused open-source projects maintained by Knownsec 404 Lab, created to showcase, support, and track high-quality, actively-maintained security tools.
- 7
awesome-hacker-search-engines
11.4Kedoardottt/awesome-hacker-search-engines · ShellA curated list of search engines useful for penetration testing, vulnerability assessment, red/blue team operations, bug bounty hunting, and general OSINT work.
- 8

webshell
10.8Ktennc/webshell · PHPIt's a community collection of webshells - scripts that give you control of a web server once uploaded - covering all the common server-side languages and maintained by tennc with 10k+ stars.
- 9
Claude-Red
7.6KSnailSploit/Claude-Red · Pythonclaude-red is a curated library of offensive security skills for the Claude Skills system: structured SKILL.md files that prime Claude with expert-level methodology for one attack surface each, from SQLi to shellcode.
- 10
wifit3
2.6Kderv82/wifit3 · Pythonwifit3 is a standalone Wi-Fi security auditing tool that scans networks, captures WPA/WPA2 handshakes, and exploits WPS/WEP weaknesses using a supported USB Wi-Fi adapter, without relying on aircrack-ng or OS kernel drivers.
- 11
Erosion
250jailbreakdotparty/Erosion · SwiftErosion is an iOS customization toolbox that uses the bad_query sandbox escape exploit to apply tweaks on supported iOS/iPadOS versions, no traditional jailbreak required.
- 12

CVE-2026-62911
188hypnguyen1209/CVE-2026-62911 · PythonA proof-of-concept exploit for CVE-2026-62911, a pre-auth RCE in Microsoft Exchange Server that relays an NTLM machine account hash to the MRSProxy service to drop and run an ASPX webshell, giving full SYSTEM access without any credentials.
- 13
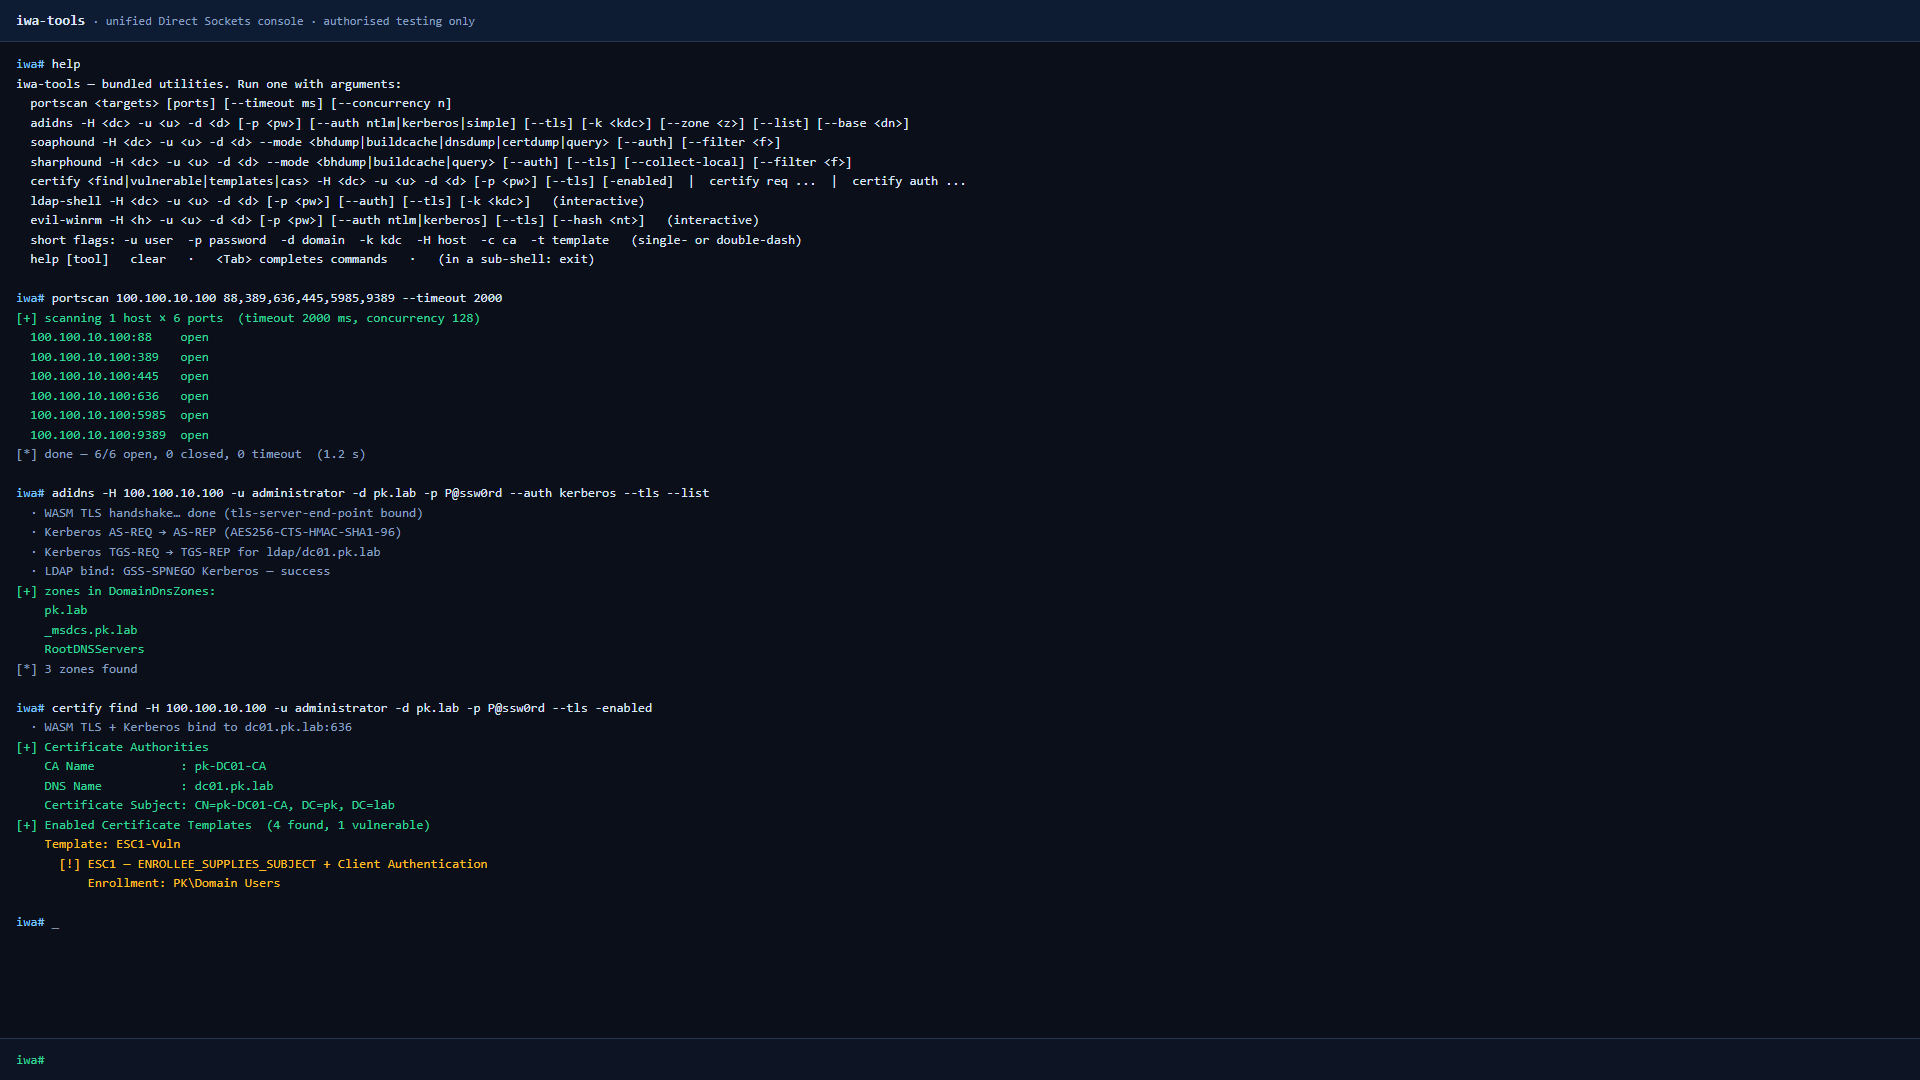
iwa-tools
146CICADA8-Research/iwa-tools · JavaScriptiwa-tools is an offensive security toolkit that runs inside Chrome as an installed Isolated Web App, letting you speak SMB, LDAP, DCE-RPC, WinRM, Kerberos, MSSQL and ADWS directly from a browser tab for Active Directory pentesting.
Related topics
Often tagged together
- security1,006
- cybersecurity253
- hacking143
- penetration-testing130
- security-tools293
- pentesting114
- network-security68
- awesome-list502
- curated-list640
- list547
- mit3,401
- red-team83
- resources714
- reverse-engineering241
- awesome267
- exploit53
- linux4,264
- offensive-security78
- osint71
- python2,440
- reconnaissance41
- redteam26
- security-research47
- bugbounty16