Topics / #red-teaming
Red-teaming projects on GitHub
Probing systems and AI models for weaknesses in controlled adversarial exercises.
As of , the most-starred Red-teaming projects on GitHub are strix (69.8K stars), CL4R1T4S (51.4K stars) and shannon (49.1K stars). GitHub.Locker tracks 23 Red-teaming repositories with 342.6K stars combined. The fastest-growing on October 18 was iFixAi, with +541 stars in a day.
Hot right now
Most stars gained in a day · Oct 18
 +541
iFixAi
ifixai-ai/iFixAi · ★ 29.7KiFixAi is an independent auditing tool for AI agents: it runs a diagnostic suite against your agent and answers the core question — is the agent doing the job it is supposed to do — with an A-F grade in under 120 seconds.
 +394
strix
usestrix/strix · ★ 69.8KStrix is an open-source tool that uses autonomous AI agents to pentest your application like real hackers: it runs your code dynamically, finds vulnerabilities, and proves them with working exploits instead of just flagging suspicious patterns.
 +124
safelabs-eval
AgentSafeLabs/safelabs-eval · ★ 679safelabs-eval is an open-source red-teaming and evaluation framework for AI agents, built around an OWASP-inspired ASI01-ASI10 taxonomy. It fires 300 curated adversarial prompts at an agent and scores every response with pattern-based detectors to produce a structured security report.
 +58
dsh-infinite-gen-5
Minglink/dsh-infinite-gen-5 · ★ 3.1KThis is a system-prompt injection plugin for the DeepSeek Harness (dsh) ecosystem that tries to bypass DeepSeek-V4.1 Flash's safety guardrails, framed as a red-team robustness benchmark suite for studying model defenses.
The all-time top
23 projects · by stars
- 69.8K#1 · usestrix/strix
strix
Strix is an open-source tool that uses autonomous AI agents to pentest your application like real hackers: it runs your code dynamically, finds vulnerabilities, and proves them with working exploits instead of just flagging suspicious patterns.
- 51.4K
 #2 · elder-plinius/CL4R1T4S
CL4R1T4S
CL4R1T4S is a crowd-sourced archive of leaked/extracted system prompts, guidelines, and internal tool definitions from major AI products like ChatGPT, Claude, Gemini, Grok, Perplexity, Cursor, Lovable, and Replit, published for AI transparency.
- 49.1K
 #3 · KeygraphHQ/shannon
shannon
Shannon is an autonomous AI pentester that analyzes your web application's source code, maps attack vectors, and then executes real exploits against the running app to prove vulnerabilities before they reach production — 'no exploit, no report'.
- 4
iFixAi
29.7Kifixai-ai/iFixAi · PythoniFixAi is an independent auditing tool for AI agents: it runs a diagnostic suite against your agent and answers the core question — is the agent doing the job it is supposed to do — with an A-F grade in under 120 seconds.
- 5
promptfoo
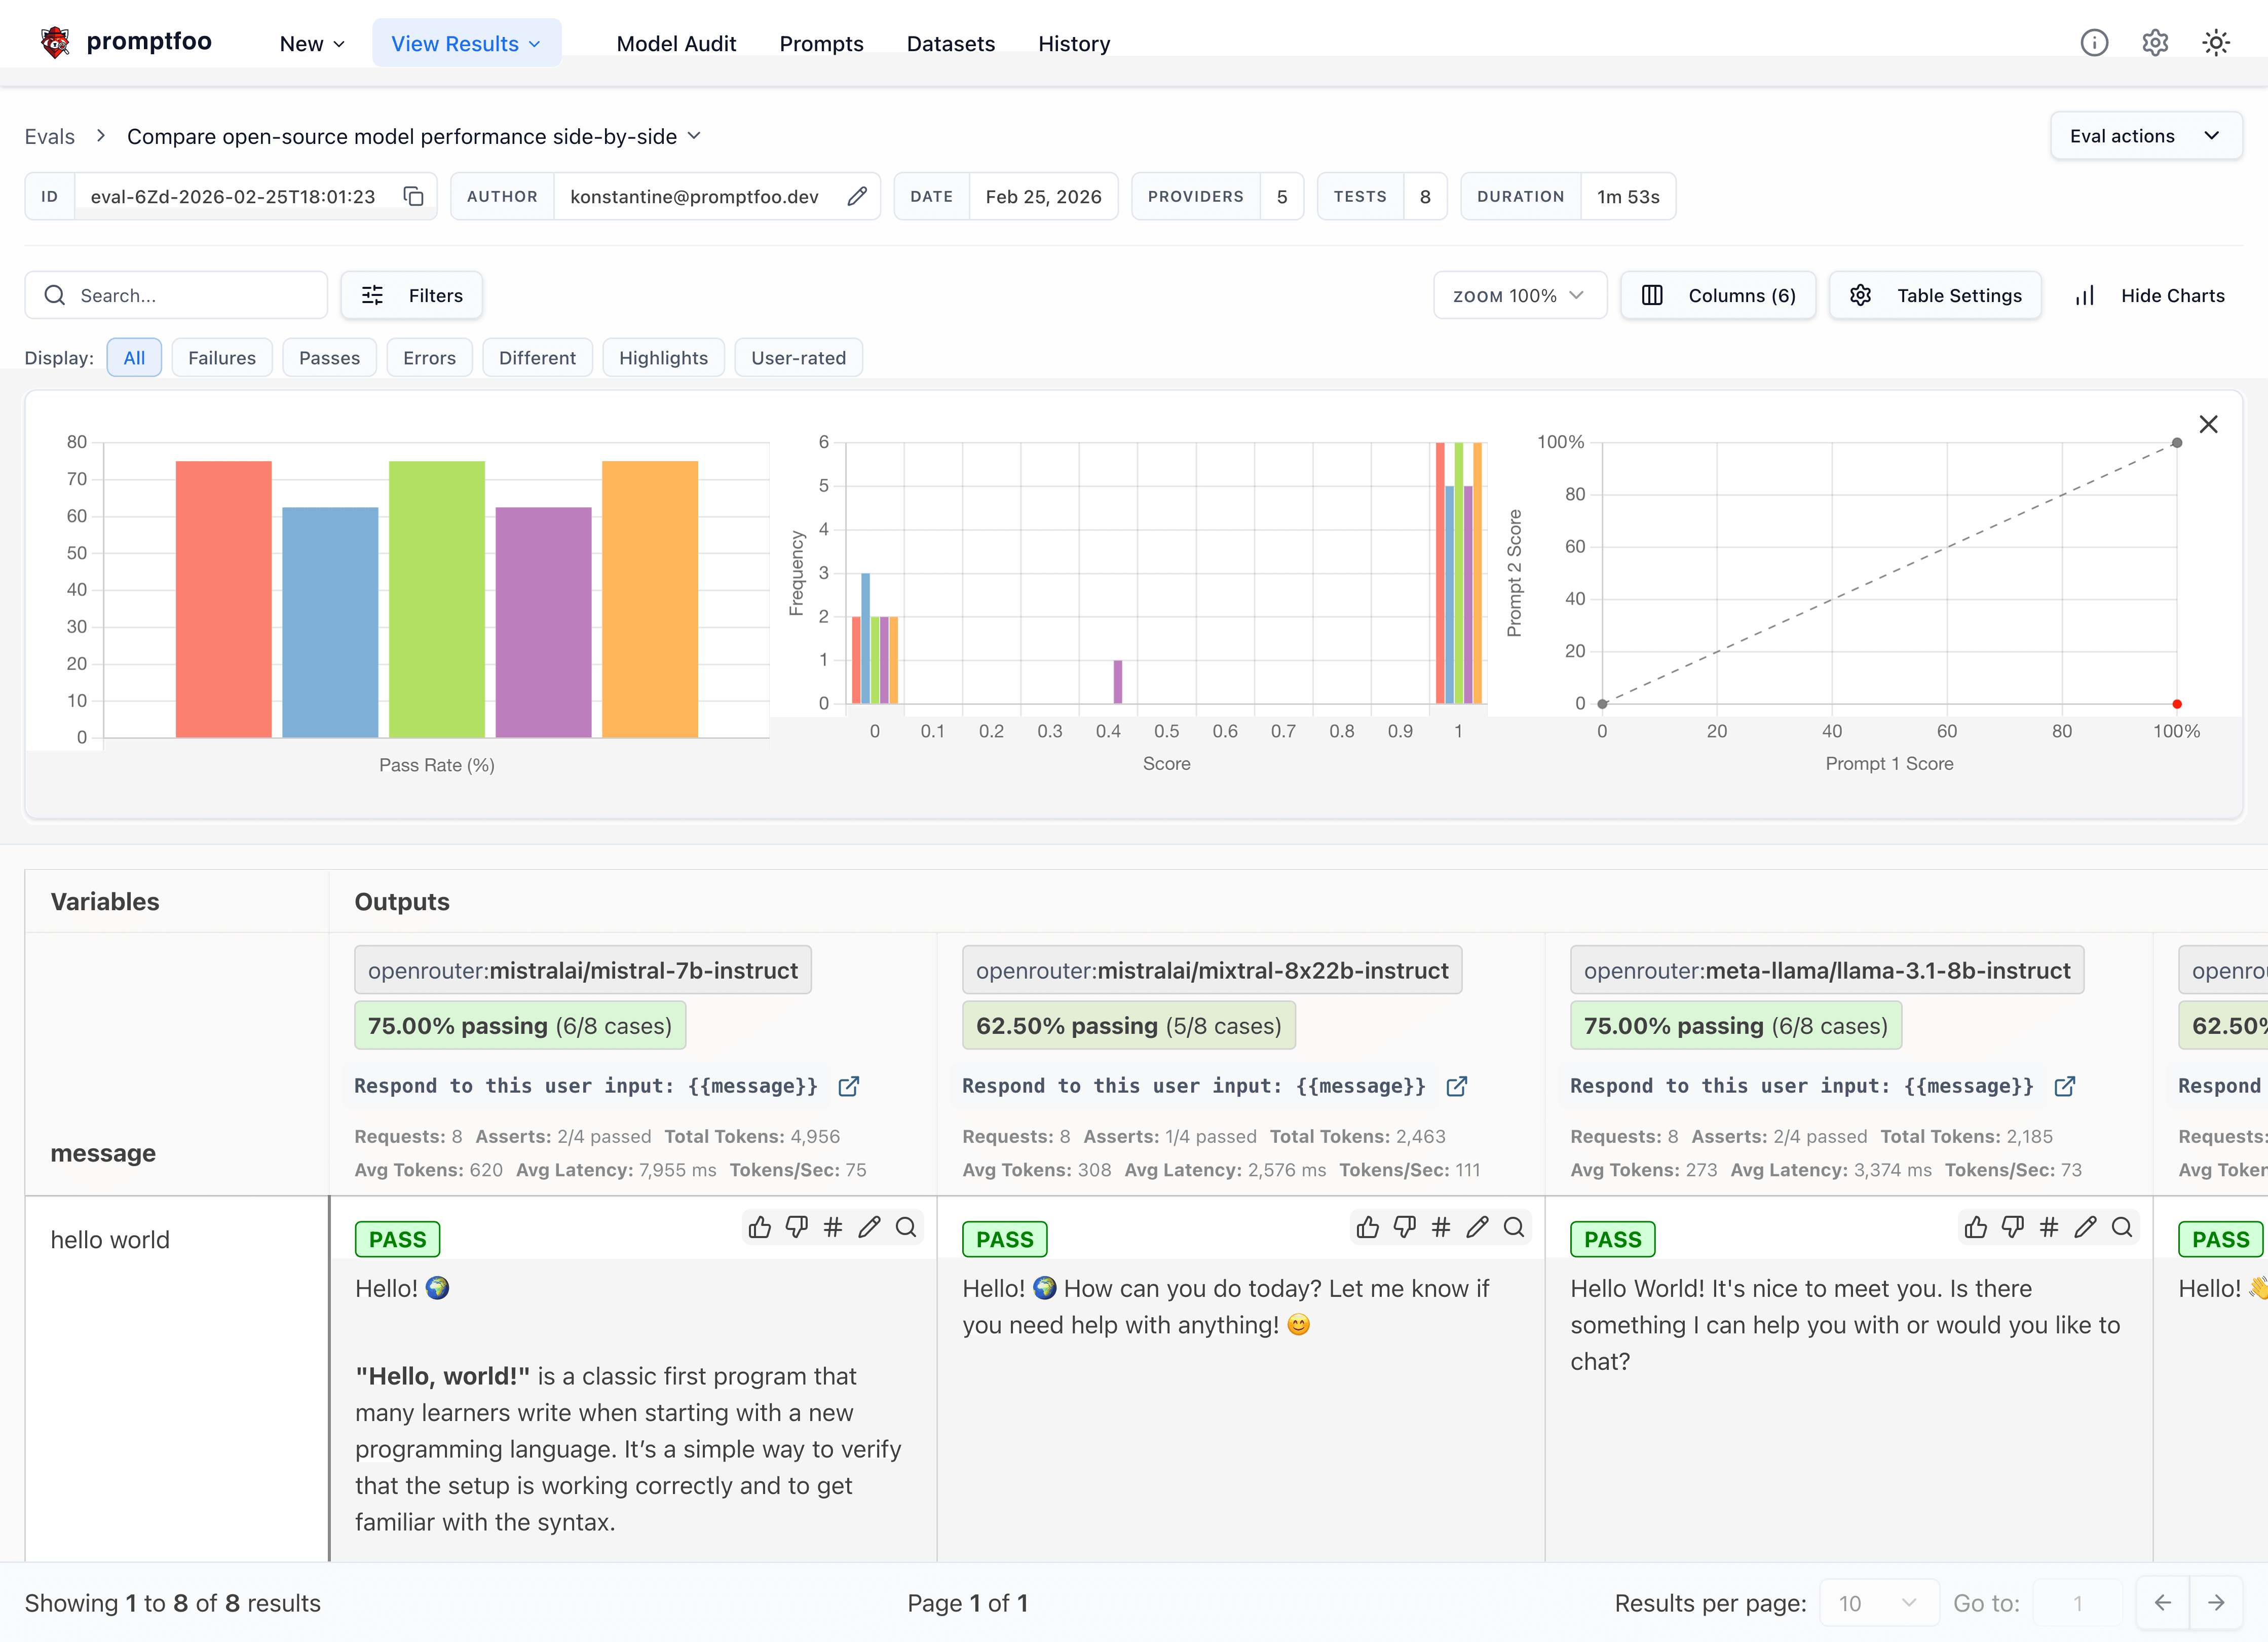
26.1Kpromptfoo/promptfoo · TypeScriptpromptfoo is a CLI and library for evaluating and red-teaming LLM apps — you test prompts, agents, and RAGs and run security scans on them, instead of relying on trial-and-error.
- 6
L1B3RT4S
21.9Kelder-plinius/L1B3RT4SA public collection of jailbreak prompts — the author calls them 'liberation prompts' — meant to make flagship AI models respond without their usual refusals. It is maintained by AI red-teamer elder-plinius.
- 7
Awesome-Hacking-Resources
17.5Kvitalysim/Awesome-Hacking-ResourcesA curated collection of hacking, penetration testing and AI red-teaming resources — courses, YouTube channels, CTF platforms and guides, picked to make you better at offensive security.
- 8
RagaAI-Catalyst
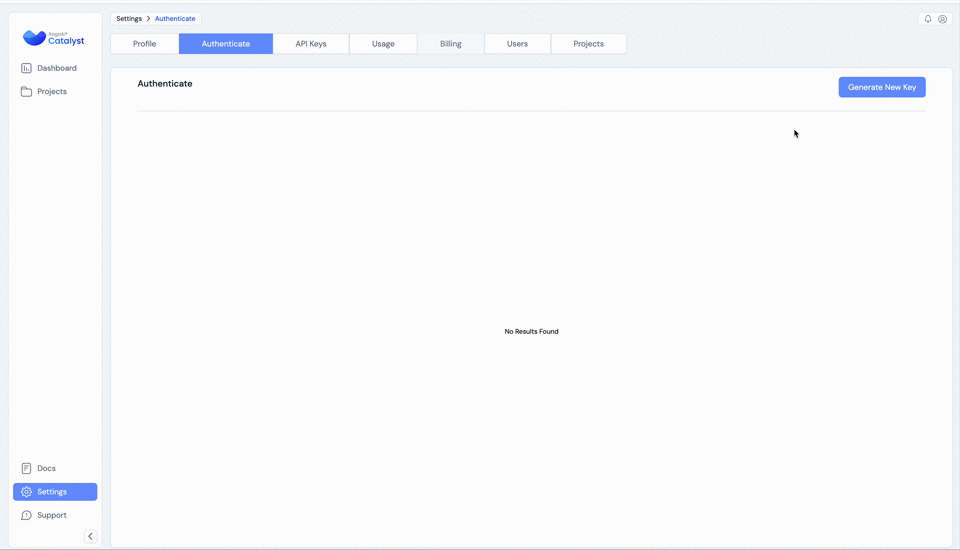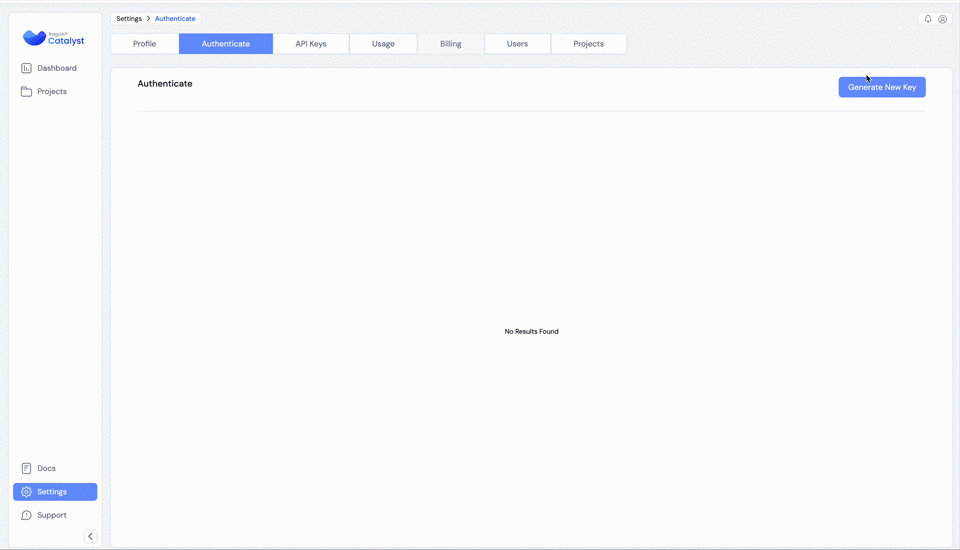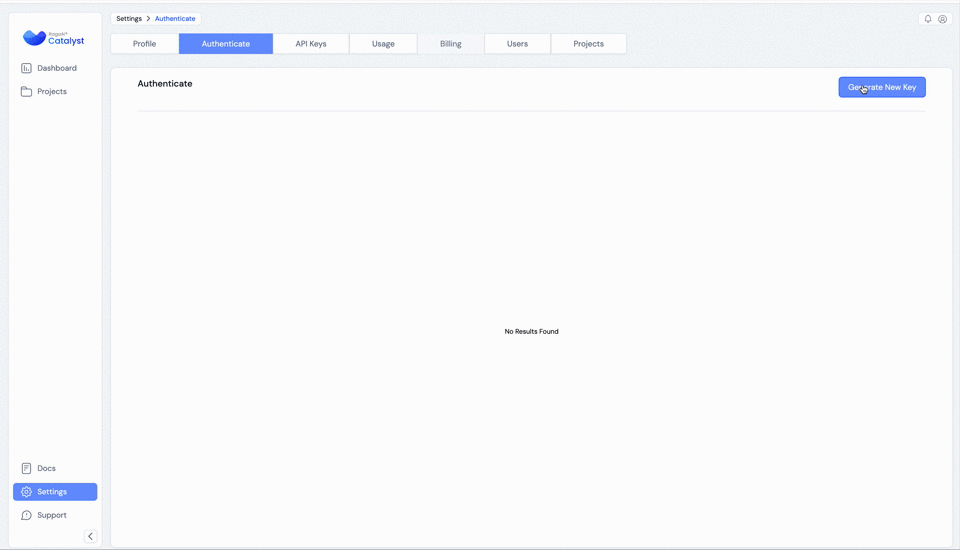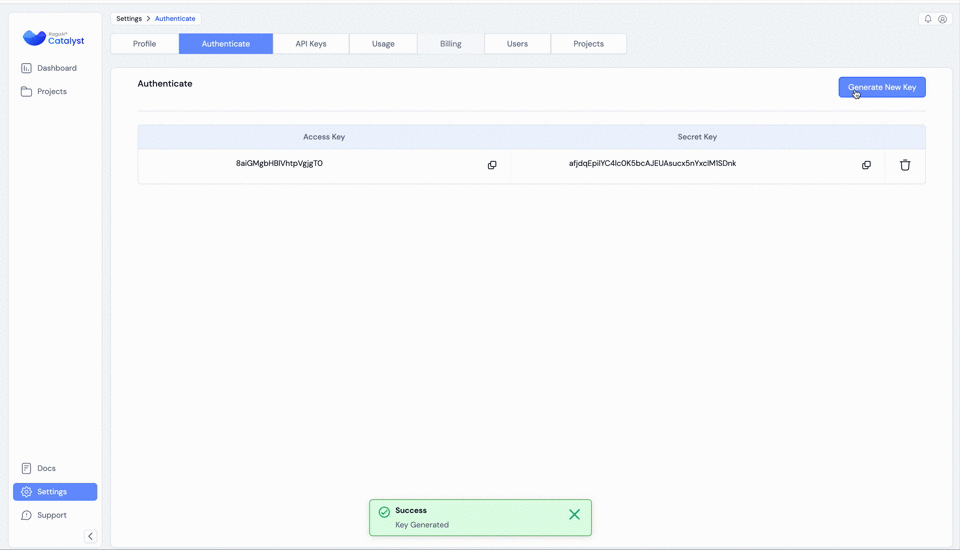
16.2Kraga-ai-hub/RagaAI-Catalyst · PythonRagaAI Catalyst is a platform for managing and optimizing LLM projects — tracing, evaluating and safeguarding LLM and agent applications, shipped as a Python SDK.
- 9
dirsearch
15Kmaurosoria/dirsearch · PythonDirsearch is an advanced command-line web path brute-forcer used to discover hidden files and directories on websites for security testing.
- 10

sliver
12.1KBishopFox/sliver · GoSliver is an open source cross-platform adversary emulation and red team framework that organizations of any size can use to perform security testing.
- 11
OBLITERATUS
8.9Kelder-plinius/OBLITERATUS · PythonOBLITERATUS is an open-source toolkit for 'abliteration' — it probes a language model's hidden states to locate the internal directions responsible for refusing prompts, then surgically removes them so the model stops refusing while keeping its core language abilities.
- 12
Claude-Red
7.6KSnailSploit/Claude-Red · Pythonclaude-red is a curated library of offensive security skills for the Claude Skills system: structured SKILL.md files that prime Claude with expert-level methodology for one attack surface each, from SQLi to shellcode.
- 13
Decepticon
6.3KBitterSecurity/Decepticon · PythonDecepticon is a professional autonomous Red Team agent that runs full attack chains — reconnaissance, exploitation, privilege escalation, lateral movement, and C2 — the way a real adversary would, instead of just scanning and printing a report.
- 14
redamon
3.2Ksamugit83/redamon · PythonRedAmon is an open-source, self-hosted AI framework that chains reconnaissance, exploitation and post-exploitation into one pipeline, maps the attack surface into a Neo4j graph, and then triages findings and opens GitHub pull requests that fix what it discovers.
- 15
dsh-infinite-gen-5
3.1KMinglink/dsh-infinite-gen-5 · JavaScriptThis is a system-prompt injection plugin for the DeepSeek Harness (dsh) ecosystem that tries to bypass DeepSeek-V4.1 Flash's safety guardrails, framed as a red-team robustness benchmark suite for studying model defenses.
- 16
gpt6-Astra
1.1K3641397194-wq/gpt6-Astra · JavaScriptIt is 'Cold Brew' (CHA), a jailbreak prompt workbench that packages prompt-injection techniques to break the safety guardrails ('破甲越狱') of six chat models — GPT-6 Astra/Codex, Claude Code, Grok 4.6, DeepSeek v4 Pro, GLM 5.3 and Gemini — for security research.
- 17
Cybermes
949Zyrexnn/Cybermes · PythonCybermes is an offensive security assistant and automation framework for authorized bug bounty hunting, reconnaissance, vulnerability research, and structured reporting, driven by AI agents and a library of 200+ playbooks.
- 18
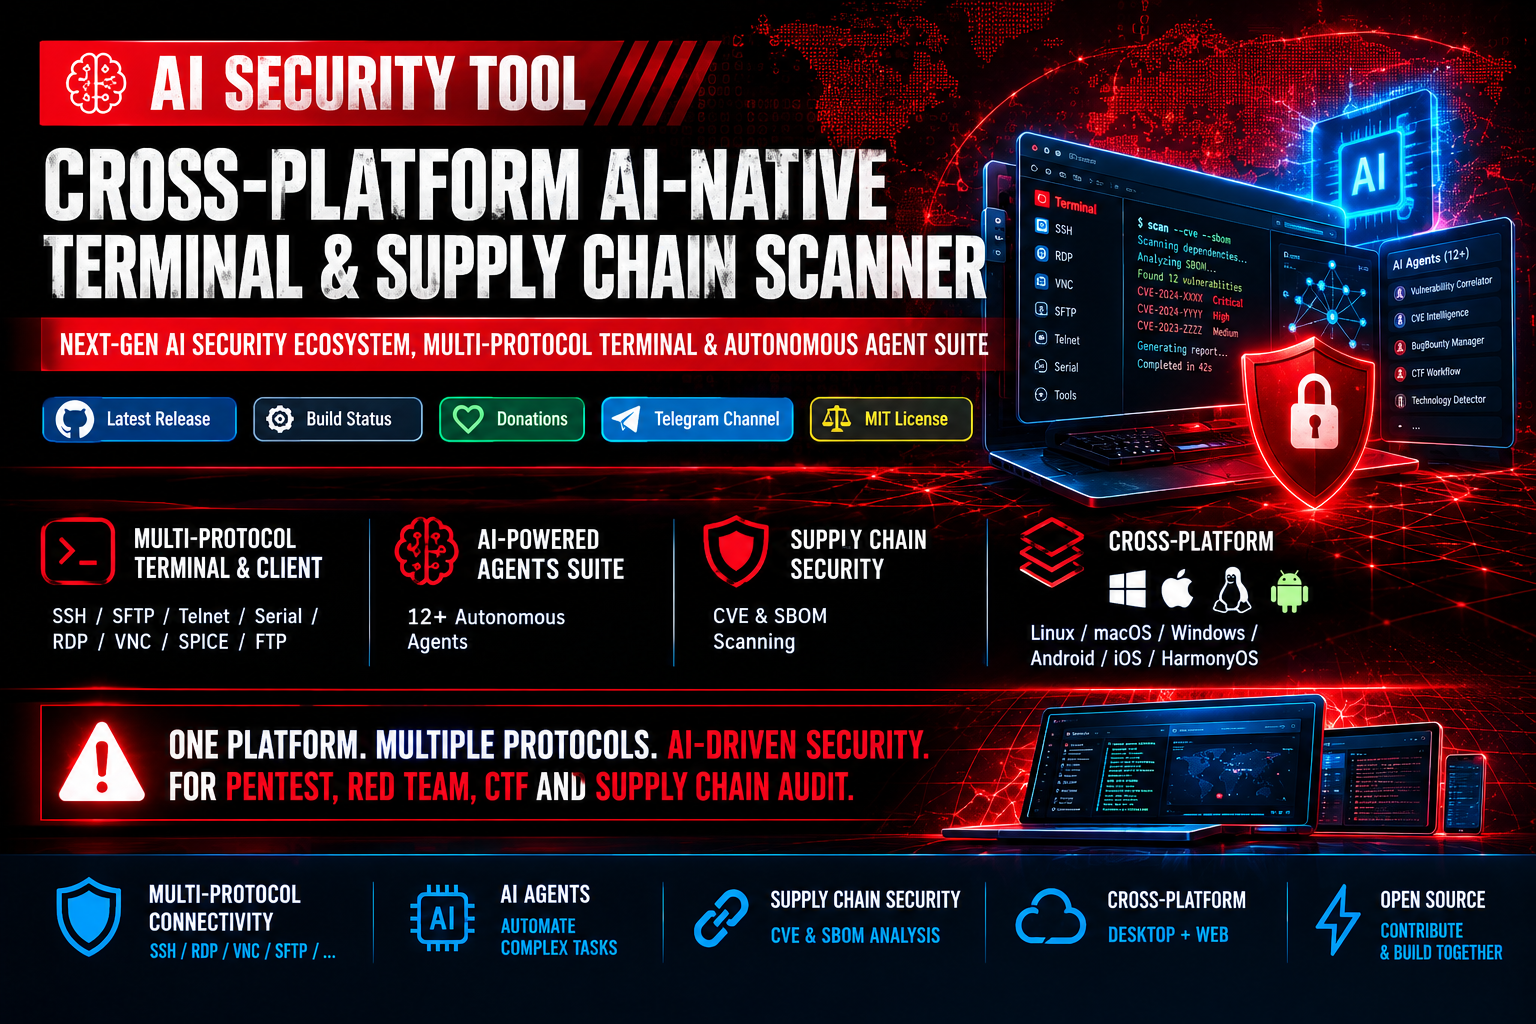
ai-security-tool
906ZeroDayEvil/ai-security-tool · HTMLAI Security Tool is an open-source, cross-platform terminal and vulnerability scanner that combines a multi-protocol connectivity client (SSH, RDP, VNC, etc.), CVE/SBOM supply-chain auditing, and 12+ autonomous AI agents (DeepSeek, OpenAI) to automate pentesting, Red Team, and CTF workflows.
- 19
safelabs-eval
679AgentSafeLabs/safelabs-eval · Pythonsafelabs-eval is an open-source red-teaming and evaluation framework for AI agents, built around an OWASP-inspired ASI01-ASI10 taxonomy. It fires 300 curated adversarial prompts at an agent and scores every response with pattern-based detectors to produce a structured security report.
- 20
Ai-jailbreak
482Quincunx33/Ai-jailbreak · JavaScriptA curated collection of jailbreak prompts and exploit techniques that bypass the safety guardrails of both open-weight models (Gemma, Qwen, Llama, DeepSeek, Phi-4, Mistral) and frontier closed models (GPT-5.x, Gemini 3.x, Grok 4.x), documented for red-teaming and AI safety research.
- 21

awesome-agent-skills-security
263LLMSecurity/awesome-agent-skills-securityA curated, awesome-list style collection of research papers, standards, frameworks, and benchmarks about securing AI agent tool use and the emerging 'agent skills' ecosystem — covering attacks like prompt injection and tool poisoning as well as defenses like sandboxing and permission control.
- 22
redStackPRO
164devZero-Security/redStackPRO · PythonredStackPRO is a web canvas for designing red team attack infrastructure and defensive Active Directory cyber ranges; you compose a topology visually, and it exports a ready-to-run Terraform and Ansible working directory that you deploy yourself.
- 23
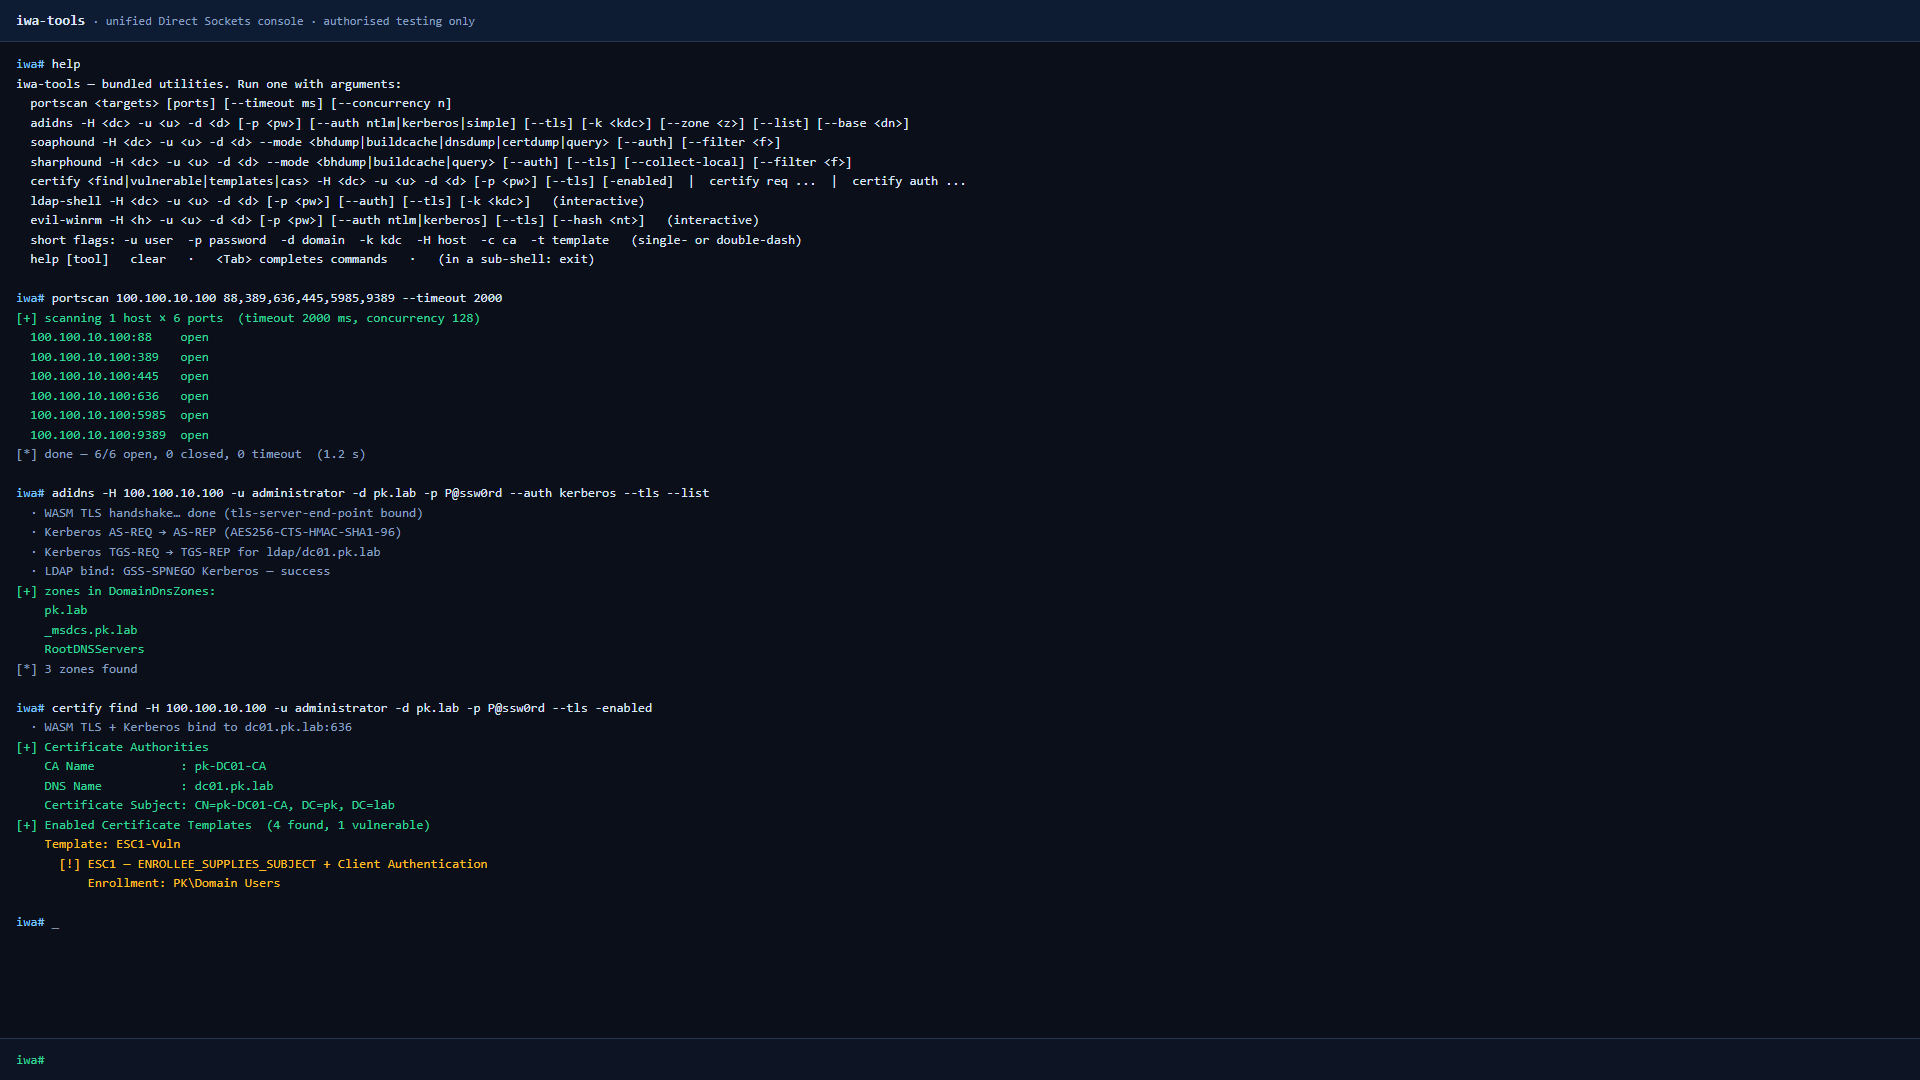
iwa-tools
146CICADA8-Research/iwa-tools · JavaScriptiwa-tools is an offensive security toolkit that runs inside Chrome as an installed Isolated Web App, letting you speak SMB, LDAP, DCE-RPC, WinRM, Kerberos, MSSQL and ADWS directly from a browser tab for Active Directory pentesting.
Related topics
Often tagged together
- security998
- cybersecurity249
- llm1,516
- ai1,993
- windows3,480
- linux4,248
- macos3,608
- penetration-testing128
- llm-security25
- offensive-security78
- pentesting114
- python2,425
- security-tools287
- ai-security46
- cli2,275
- docker1,684
- hacking139
- open-source5,748
- red-team82
- self-hosted1,978
- ai-agents1,322
- jailbreak43
- prompt-injection21
- terminal1,128