Topics / #fuzzing
Fuzzing projects on GitHub
Automated fuzz testing that feeds random inputs to find crashes and bugs.
As of , the most-starred Fuzzing projects on GitHub are Awesome-Hacking (123K stars), SecLists (74.2K stars) and big-list-of-naughty-strings (47.7K stars). GitHub.Locker tracks 23 Fuzzing repositories with 455.8K stars combined. The fastest-growing on October 18 was git-ai, with +1.2K stars in a day.
Hot right now
Most stars gained in a day · Oct 18
 +1.2K
git-ai
feder-cr/git-ai · ★ 2.3Kopenscion is an open-source, MIT-licensed reimplementation of Scion, the server-centric version control system Anthropic built internally for coding agents but never released publicly.
 +102
Awesome-Hacking
Hack-with-Github/Awesome-Hacking · ★ 123KA massive index that links out to dozens of other awesome-lists covering nearly every security domain: android security, bug bounty, fuzzing, malware analysis, OSINT, reverse engineering, web hacking, and more.
 +22
nuclei
projectdiscovery/nuclei · ★ 32.1KA fast, open-source vulnerability scanner that runs YAML-based templates to find security issues in applications, APIs, networks, DNS and cloud configurations. Its checks come from a large global security community.
 +21
SecLists
danielmiessler/SecLists · ★ 74.2KSecLists is a huge collection of ready-made wordlists for security testing: usernames, passwords, URLs, sensitive data patterns, fuzzing payloads, web shells and more, all gathered in one repository.
The all-time top
23 projects · by stars
- 123K#1 · Hack-with-Github/Awesome-Hacking
Awesome-Hacking
A massive index that links out to dozens of other awesome-lists covering nearly every security domain: android security, bug bounty, fuzzing, malware analysis, OSINT, reverse engineering, web hacking, and more.
- 74.2K#2 · danielmiessler/SecLists
SecLists
SecLists is a huge collection of ready-made wordlists for security testing: usernames, passwords, URLs, sensitive data patterns, fuzzing payloads, web shells and more, all gathered in one repository.
- 47.7K
 #3 · minimaxir/big-list-of-naughty-strings
big-list-of-naughty-strings
It is a curated collection of strings with a high probability of breaking software when used as user input, meant to help QA testing of input validation.
- 4
nuclei
32.1Kprojectdiscovery/nuclei · GoA fast, open-source vulnerability scanner that runs YAML-based templates to find security issues in applications, APIs, networks, DNS and cloud configurations. Its checks come from a large global security community.
- 5
fmt
25.9Kfmtlib/fmt · C++{fmt} is an open-source C++ formatting library — a fast, safe alternative to C stdio and C++ iostreams, with a format string syntax similar to Python's.
- 6
unleashed-firmware
22.5KDarkFlippers/unleashed-firmware · CUnleashed is custom firmware for the Flipper Zero multitool — a fork of the official firmware (OFW) that adds extra features and improvements while staying compatible with official apps.
- 7
dirsearch
15Kmaurosoria/dirsearch · PythonDirsearch is an advanced command-line web path brute-forcer used to discover hidden files and directories on websites for security testing.
- 8

gobuster
14.2KOJ/gobuster · GoGobuster is a fast, multi-threaded command-line tool written in Go for brute-forcing web directories/files, DNS subdomains, and virtual hosts, plus enumerating S3/GCS cloud storage buckets and TFTP files.
- 9

awesome-web-security
13.9Kqazbnm456/awesome-web-security · PythonA curated list of web security materials and resources, organized by vulnerability class and attack type (XSS, SQL injection, CSRF, SSRF, XXE, deserialization, OAuth, JWT, and more), plus cheatsheets, tools, and write-ups for penetration testing.
- 10

cJSON
13KDaveGamble/cJSON · CAn ultralightweight JSON parser written in plain ANSI C. The whole thing is one C file and one header, with the stated goal of being the dumbest parser that still gets your job done.
- 11
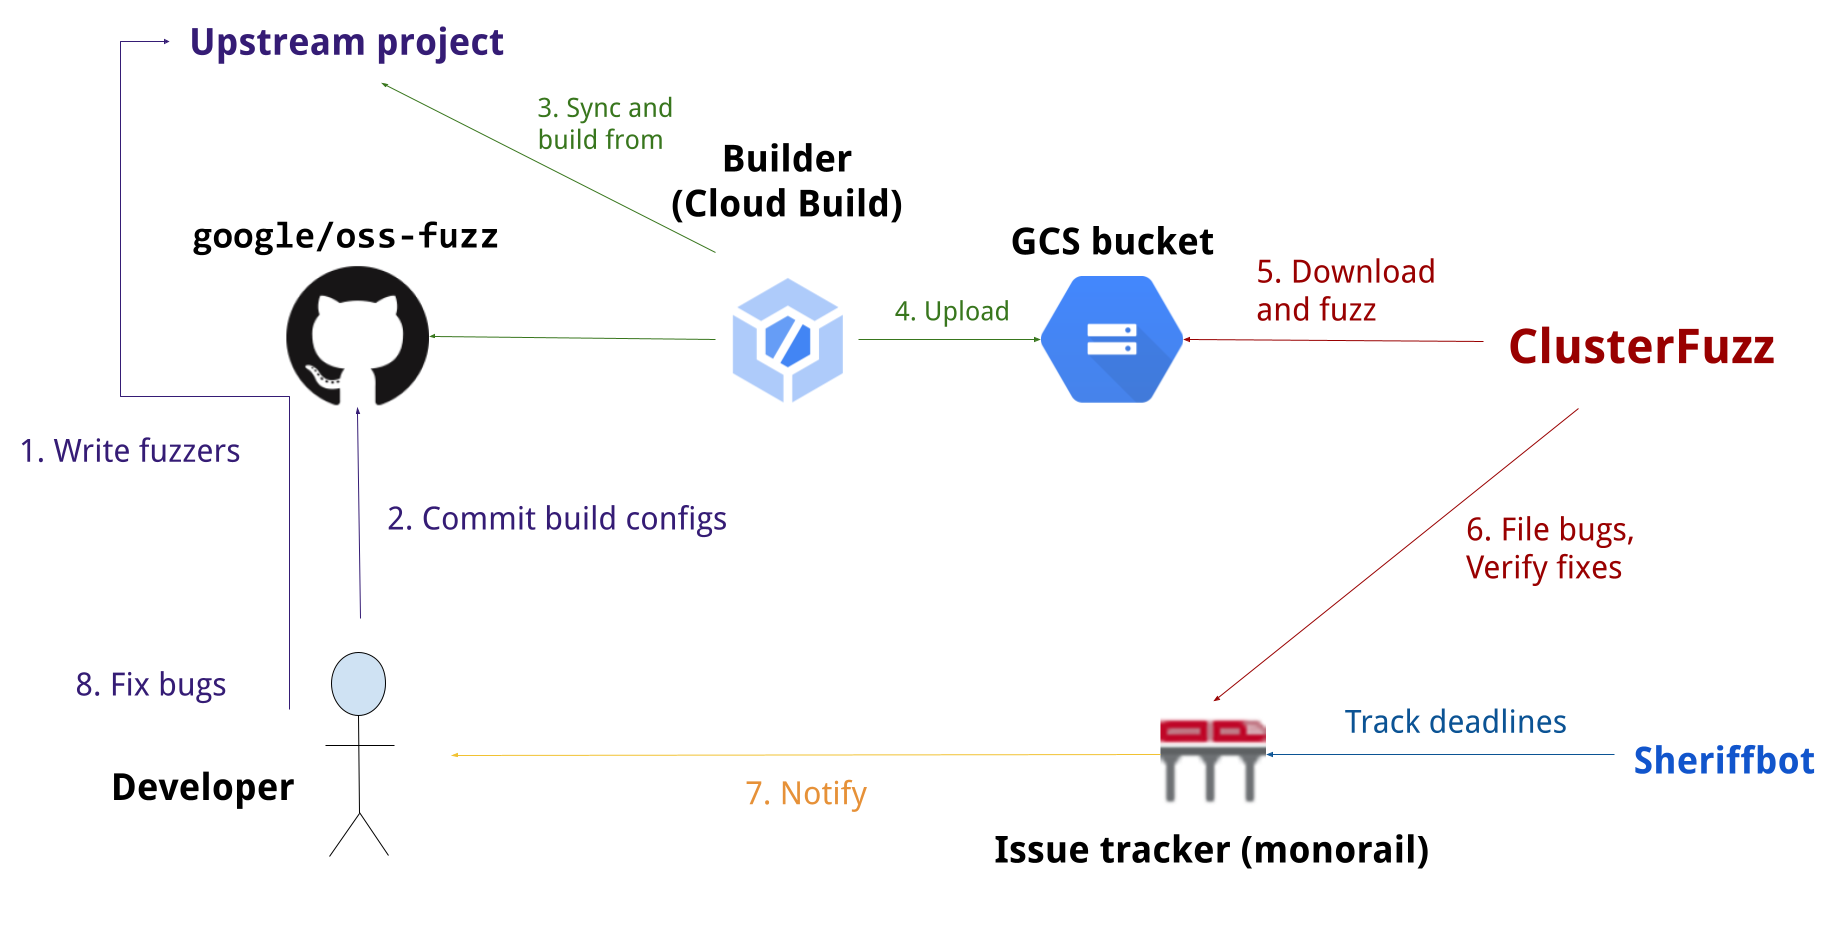
oss-fuzz
12.8Kgoogle/oss-fuzz · ShellOSS-Fuzz is Google's free continuous fuzzing service for open source software: it runs guided fuzzing nonstop to surface security vulnerabilities and stability bugs before attackers do.
- 12
urh
12.6Kjopohl/urh · PythonURH (Universal Radio Hacker) is a suite for investigating wireless protocols: it captures radio signals via SDR hardware, demodulates them with automatic modulation detection, and helps you reverse-engineer the bits and bytes flying over the air.
- 13
libevent
12Klibevent/libevent · CLibevent is a C library that provides an asynchronous event notification API, so programs can react to file descriptor readiness, timers, and signals without writing their own platform-specific event loop.
- 14
foundry
10.7Kfoundry-rs/foundry · RustFoundry is a blazing fast, portable and modular toolkit for Ethereum application development, written in Rust. It bundles four command-line tools: Forge, Cast, Anvil and Chisel.
- 15

defending-code-reference-harness
7.6Kanthropics/defending-code-reference-harness · PythonA reference implementation from Anthropic for finding and fixing vulnerabilities with Claude: a set of Claude Code skills (quickstart, threat-model, vuln-scan, triage, patch, customize) plus an autonomous scanning harness that runs a recon-find-verify-report-patch loop, built from learnings partnering with security teams.
- 16

pgrust
5.3Kmalisper/pgrust · Rustpgrust is a from-scratch reimplementation of PostgreSQL in Rust, built to be wire- and SQL-dialect compatible with Postgres while being faster than both Postgres and ClickHouse.
- 17

exploitarium
5.2Kbikini/exploitarium · PythonExploitarium is a single consolidated archive of the author's public proof-of-concept exploits and vulnerability research writeups, merging dozens of their former standalone PoC repos into one place.
- 18

raptor
3.9Kgadievron/raptor · PythonRAPTOR turns a Claude Code session into an offensive/defensive security agent: Claude.md rules, sub-agents and skills orchestrate tools like radare2, Frida, Z3 and CodeQL for binary reverse-engineering, exploit-feasibility research, and software supply-chain (SCA) analysis.
- 19
git-ai
2.3Kfeder-cr/git-ai · Goopenscion is an open-source, MIT-licensed reimplementation of Scion, the server-centric version control system Anthropic built internally for coding agents but never released publicly.
- 20

sort-research-rs
546Voultapher/sort-research-rs · RustA test, benchmark and fuzzing suite for sort implementations, written in Rust. It also hosts a novel sort called ipnsort, vendored Rust, C++ and C sorts for comparison, and the resulting research papers.
- 21
scuttle
521Continuum-AI-Corp/scuttle · GoScuttle is an open-source Go library that encrypts sensitive fields in application logs before they ever reach storage, so copies that survive in databases, replicas, snapshots and backups stay unreadable even if the datastore is later compromised.
- 22
0
5140sec-labs/0 · TypeScript0 is an open-source, self-evolving, multi-model AI harness for security research that finds, verifies, and fixes vulnerabilities, built by the Swiss Applied AI & Cybersecurity Research Lab.
- 23

libfyaml
346pantoniou/libfyaml · Clibfyaml is a high-performance YAML 1.2 and JSON parser/emitter for C, built for zero-copy operation with full document-tree and event-streaming APIs, and it passes the full YAML testsuite.
Related topics
Often tagged together
- security998
- linux4,248
- open-source5,748
- macos3,608
- cybersecurity249
- windows3,480
- cross-platform2,673
- developer-tools2,981
- mit3,387
- penetration-testing128
- security-tools287
- cli2,275
- docker1,684
- hacking139
- pentesting114
- python2,425
- red-team82
- reverse-engineering238
- testing341
- c325
- library1,595
- performance653
- apache-2.01,452
- ci212