Topics / #security-research
Security-research projects on GitHub
Vulnerability research, CVE analysis, and exploit studies.
As of , the most-starred Security-research projects on GitHub are L1B3RT4S (21.9K stars), vulhub (21.4K stars) and hacker-roadmap (15.7K stars). GitHub.Locker tracks 41 Security-research repositories with 168.7K stars combined. The fastest-growing on October 16 was awesome-reverse-engineering, with +59 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
 +59
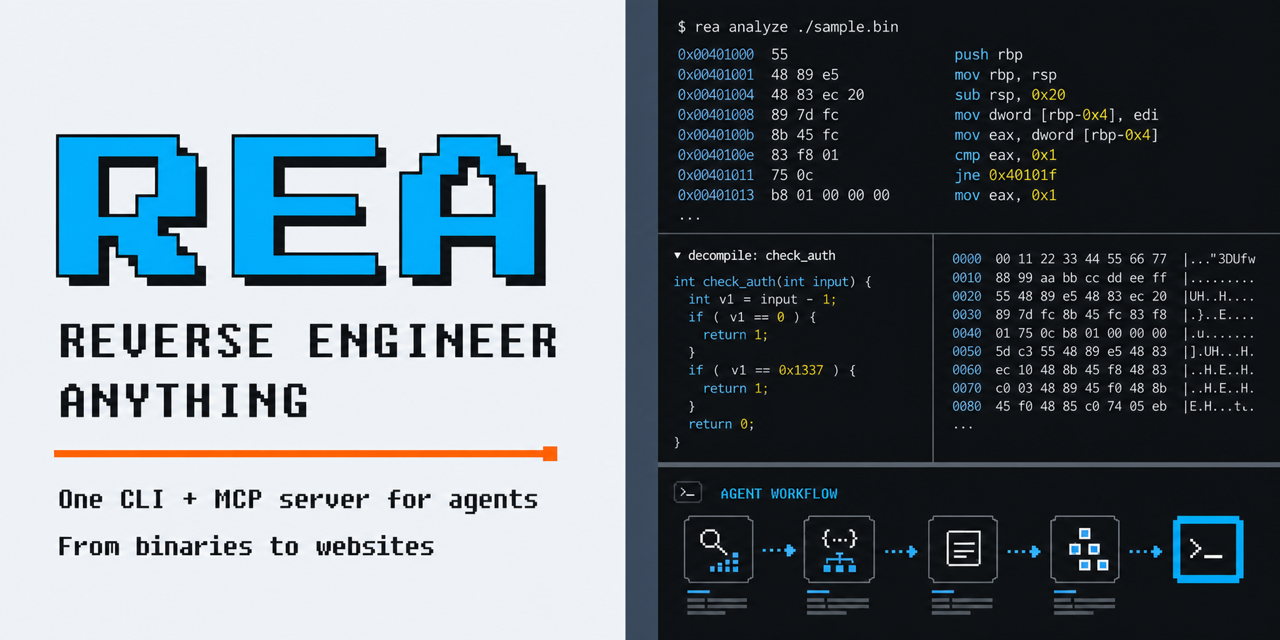
awesome-reverse-engineering
morluto/awesome-reverse-engineering · ★ 628A curated list of reverse-engineering tools and learning resources covering binaries, applications, firmware, file formats, and protocols, organized by the task you need to do rather than alphabetically.
 +52
Relapse-Exploit
ntfargo/Relapse-Exploit · ★ 2.3KRelapse Exploit is a browser-based jailbreak chain for the PS5, working on firmware 7.00 through 13.60, that chains a WebKit browser exploit with a kernel exploit to gain kernel read/write and load custom payloads.
GhidraMCP
LaurieWired/GhidraMCP · ★ 11.3KGhidraMCP is a Model Context Protocol server that lets LLMs autonomously reverse engineer applications by exposing Ghidra's core functionality (decompiling, renaming, listing imports/exports) to any MCP client.
 +30
artex-global
jiwoochris/artex-global · ★ 1.6KARTEX-KO is a Korean localization of the ARTEX (Autumn-27/ARTEX) framework: a system where multiple LLM-driven agents autonomously run a penetration test end-to-end, from reconnaissance to exploitation, with a Go backend and an embedded Next.js frontend.
The all-time top
41 projects · by stars
- 21.9K
 #1 · elder-plinius/L1B3RT4S
L1B3RT4S
A public collection of jailbreak prompts — the author calls them 'liberation prompts' — meant to make flagship AI models respond without their usual refusals. It is maintained by AI red-teamer elder-plinius.
- 21.4K
 #2 · vulhub/vulhub
vulhub
Vulhub is an open-source collection of pre-built, ready-to-use vulnerable Docker environments: with one command you get a working lab for security research, learning, or demos.
- 15.7K
 #3 · sundowndev/hacker-roadmap
hacker-roadmap
This is a curated roadmap and toolkit index for learning and practicing ethical hacking: it explains what penetration testing is and groups hundreds of security tools, wordlists and references by category (recon, password attacks, wireless, exploitation, web hacking, post-exploitation, frameworks).
- 4
HackBrowserData
14.6KmoonD4rk/HackBrowserData · GoHackBrowserData is a command-line tool that decrypts and exports browser data — passwords, cookies, history, bookmarks, credit cards and more — from Chromium-based browsers, Firefox and Safari, built for security research.
- 5
GhidraMCP
11.3KLaurieWired/GhidraMCP · JavaGhidraMCP is a Model Context Protocol server that lets LLMs autonomously reverse engineer applications by exposing Ghidra's core functionality (decompiling, renaming, listing imports/exports) to any MCP client.
- 6

webshell
10.8Ktennc/webshell · PHPIt's a community collection of webshells - scripts that give you control of a web server once uploaded - covering all the common server-side languages and maintained by tennc with 10k+ stars.
- 7

awesome-threat-intelligence
10.7Khslatman/awesome-threat-intelligenceA curated catalog of threat intelligence resources — feeds, tools, frameworks, standards and research for tracking online threats. It is a pointer list on GitHub, not software you install.
- 8

Claude-Red
7.6KSnailSploit/Claude-Red · Pythonclaude-red is a curated library of offensive security skills for the Claude Skills system: structured SKILL.md files that prime Claude with expert-level methodology for one attack surface each, from SQLi to shellcode.
- 9
AI-Infra-Guard
6.9KTencent/AI-Infra-Guard · PythonAI-Infra-Guard (A.I.G) is a full-stack AI red teaming platform built by Tencent Zhuque Lab that scans AI agents, MCP servers, agent skills, and AI infrastructure components for security vulnerabilities, and evaluates LLMs against jailbreak attacks.
- 10
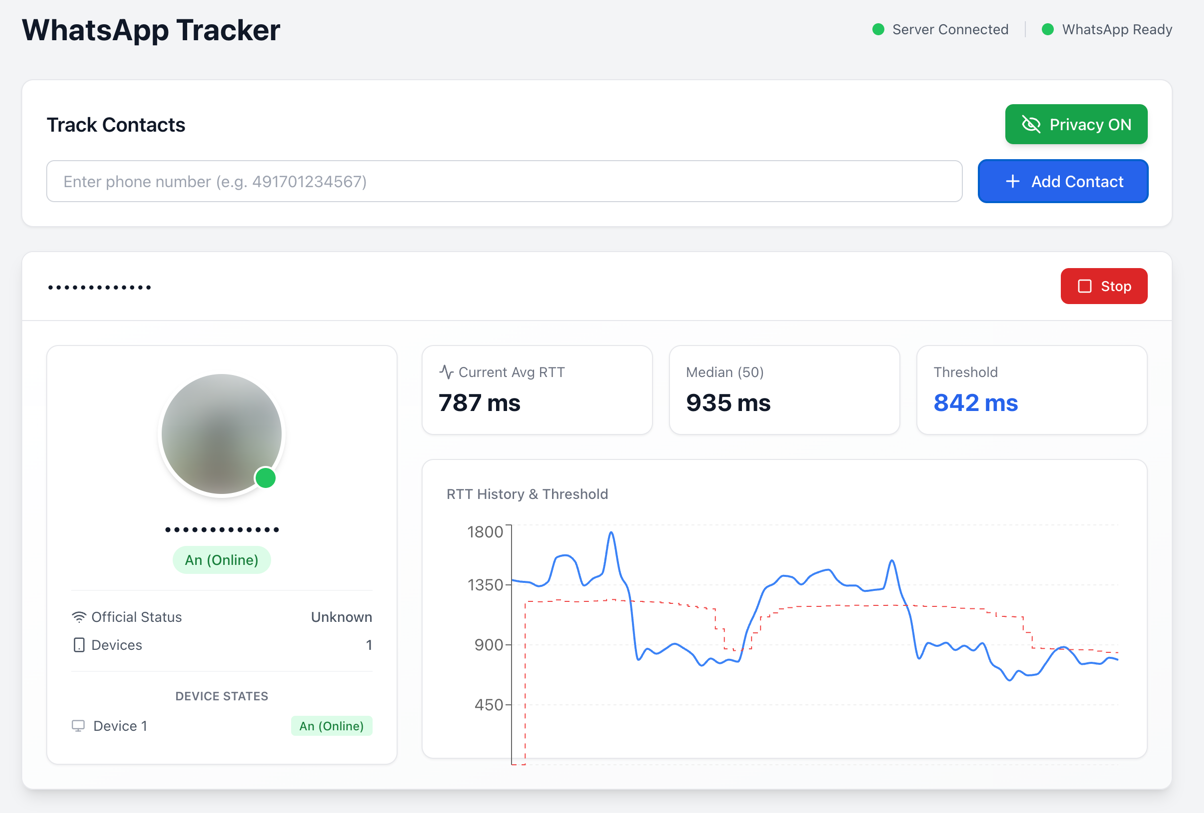
device-activity-tracker
5.2Kgommzystudio/device-activity-tracker · TypeScriptThis is a proof-of-concept security research tool that monitors WhatsApp and Signal users by measuring the Round-Trip Time (RTT) of message delivery receipts, revealing whether a target's device is actively in use, idle, or offline.
- 11

exploitarium
5.2Kbikini/exploitarium · PythonExploitarium is a single consolidated archive of the author's public proof-of-concept exploits and vulnerability research writeups, merging dozens of their former standalone PoC repos into one place.
- 12
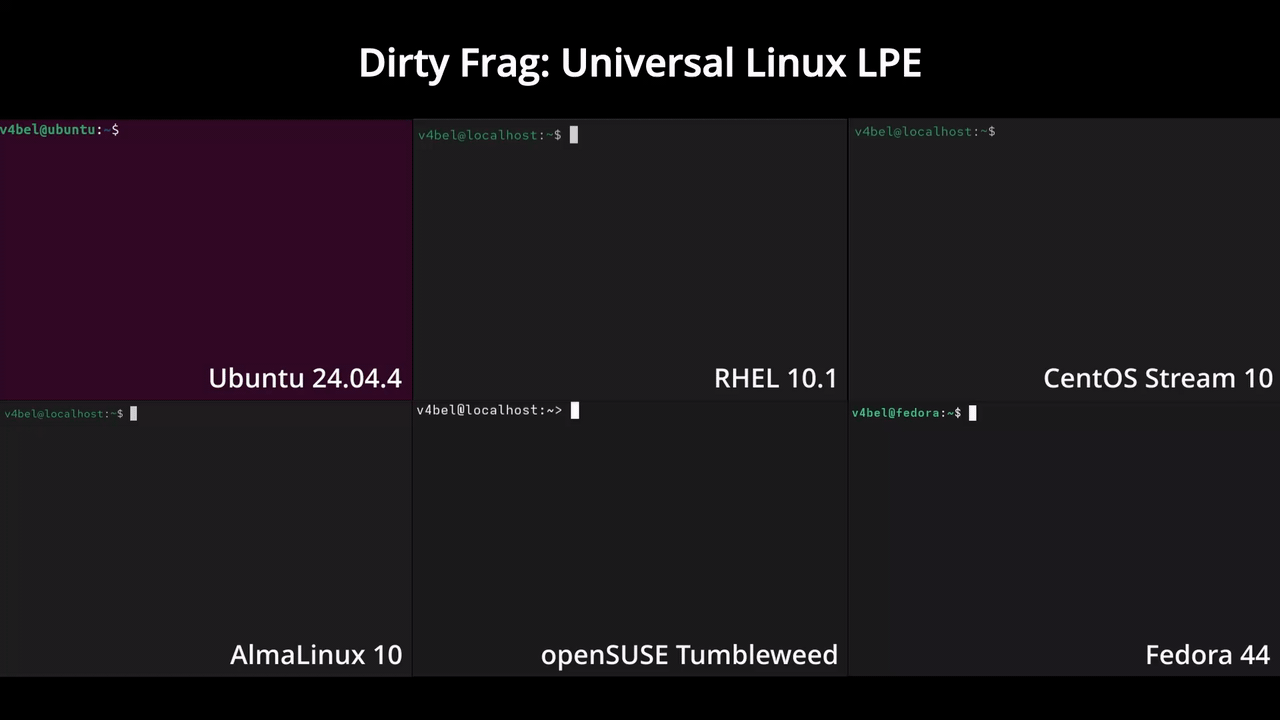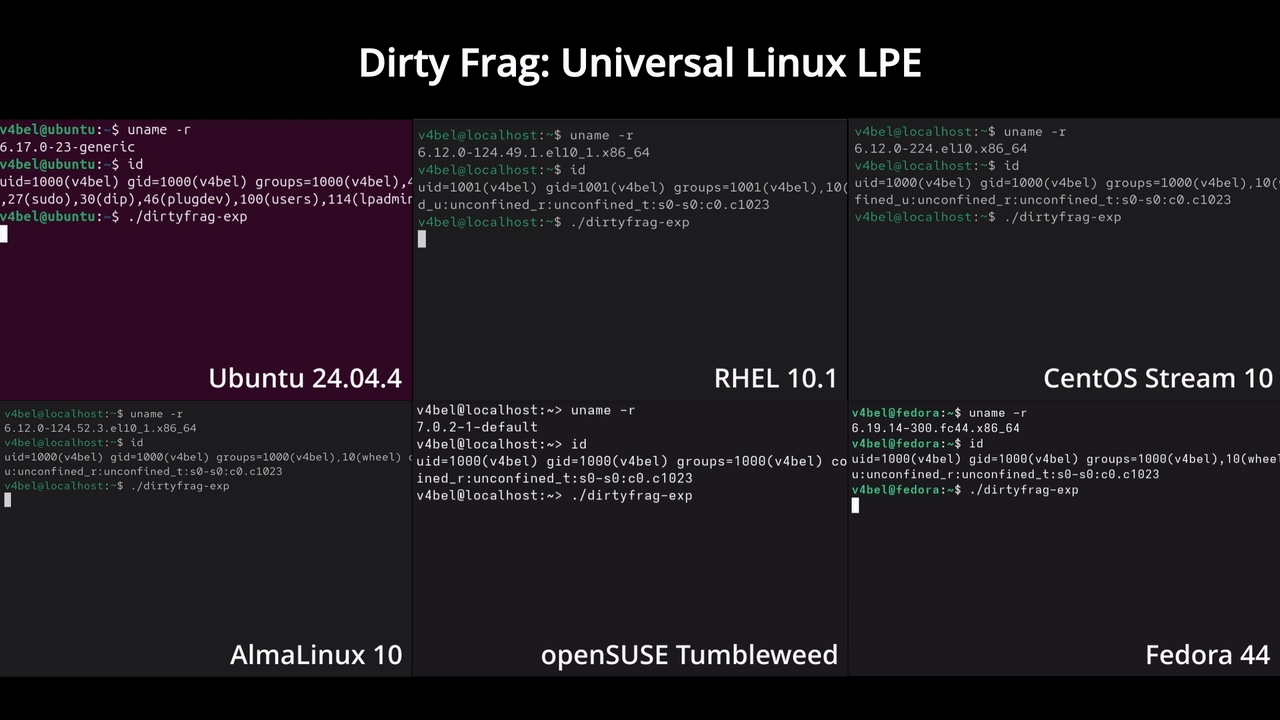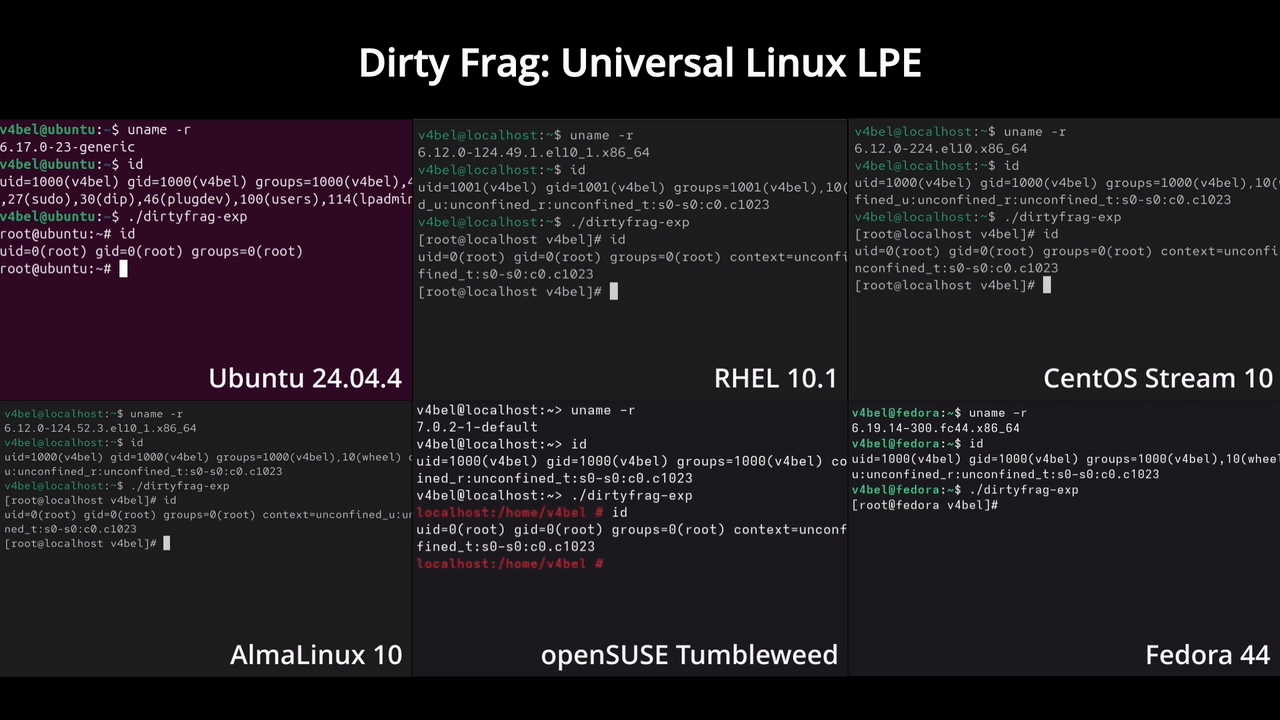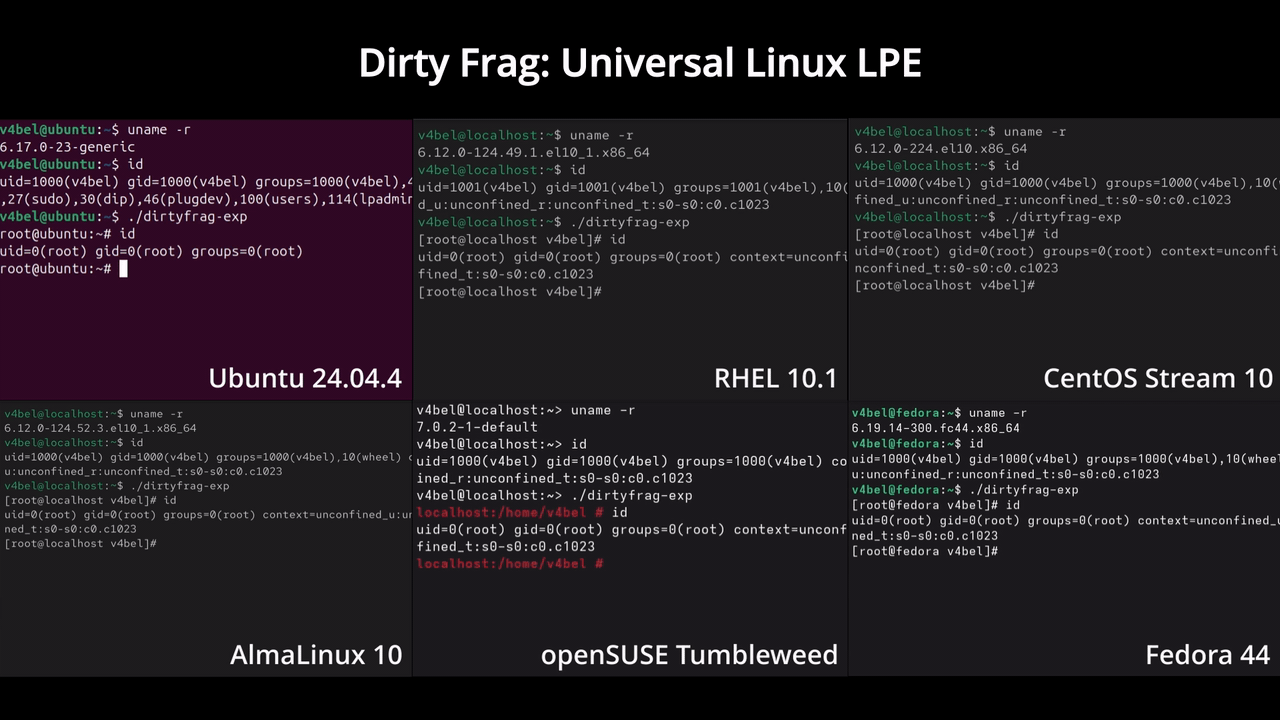
dirtyfrag
5.1KV4bel/dirtyfrag · CDirty Frag is a proof-of-concept Linux kernel local privilege escalation exploit that chains two page-cache write vulnerabilities (CVE-2026-43284 and CVE-2026-43500) to obtain root on major Linux distributions.
- 13
reverse-SynthID
5Kaloshdenny/reverse-SynthID · Pythonreverse-SynthID reverse-engineers Google's SynthID watermark embedded in Gemini-generated images using signal processing and spectral analysis, and ships tools that detect and surgically bypass that watermark without any access to Google's proprietary encoder/decoder.
- 14

copy-fail-CVE-2026-31431
4.1Ktheori-io/copy-fail-CVE-2026-31431 · PythonThis repository is a technical writeup and proof-of-concept for CVE-2026-31431, a 9-year-old Linux kernel local privilege escalation (LPE) vulnerability found by Theori's AI vulnerability research tool, Xint Code.
- 15
claude-code-analysis
4Kliuup/claude-code-analysis · TypeScriptA Chinese-language static analysis document collection dissecting the source code of Claude Code, after its npm package accidentally shipped unminified source maps revealing the full TypeScript codebase.
- 16

raptor
3.9Kgadievron/raptor · PythonRAPTOR turns a Claude Code session into an offensive/defensive security agent: Claude.md rules, sub-agents and skills orchestrate tools like radare2, Frida, Z3 and CodeQL for binary reverse-engineering, exploit-feasibility research, and software supply-chain (SCA) analysis.
- 17
mantis
2.5Kgoogle/mantis · PythonMantis is a toolkit of skills plus a reference agent harness (built on Google's ADK) that lets AI coding agents autonomously find, reproduce, triage, and patch vulnerabilities in a codebase.
- 18
Relapse-Exploit
2.3Kntfargo/Relapse-Exploit · JavaScriptRelapse Exploit is a browser-based jailbreak chain for the PS5, working on firmware 7.00 through 13.60, that chains a WebKit browser exploit with a kernel exploit to gain kernel read/write and load custom payloads.
- 19
artex-global
1.6Kjiwoochris/artex-global · GoARTEX-KO is a Korean localization of the ARTEX (Autumn-27/ARTEX) framework: a system where multiple LLM-driven agents autonomously run a penetration test end-to-end, from reconnaissance to exploitation, with a Go backend and an embedded Next.js frontend.
- 20
gpt6-Astra
1.1K3641397194-wq/gpt6-Astra · JavaScriptIt is 'Cold Brew' (CHA), a jailbreak prompt workbench that packages prompt-injection techniques to break the safety guardrails ('破甲越狱') of six chat models — GPT-6 Astra/Codex, Claude Code, Grok 4.6, DeepSeek v4 Pro, GLM 5.3 and Gemini — for security research.
- 21
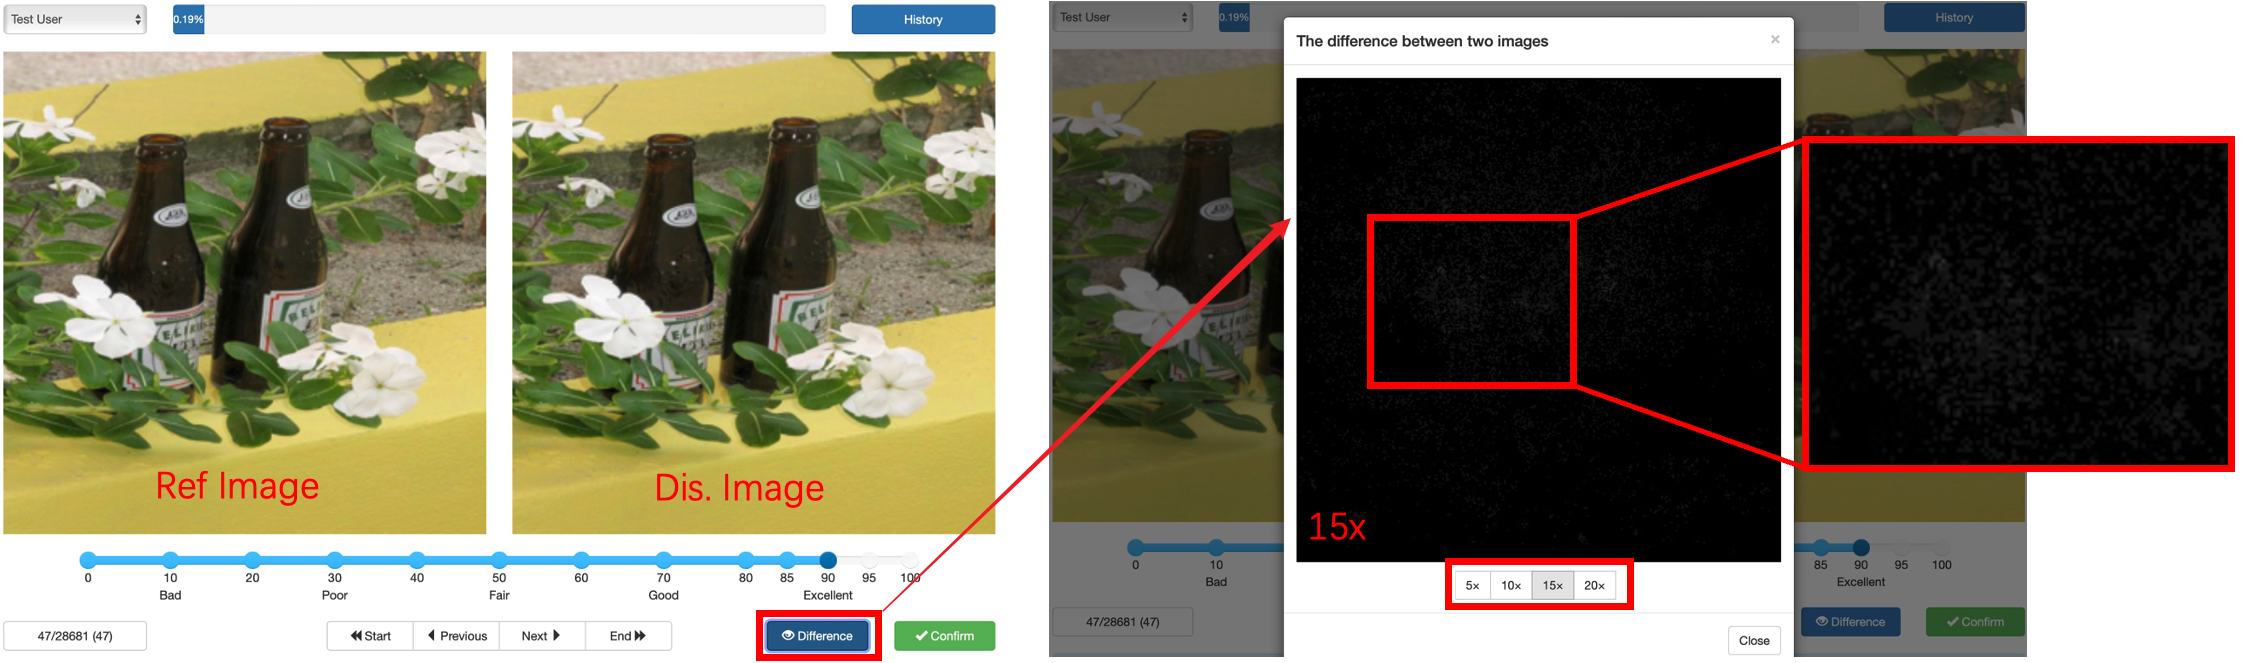
APSD
897hcliucs/APSDAPSD is a large-scale dataset for studying how visually stealthy adversarial perturbations look to humans, containing 10,586 clean-adversarial image pairs with human opinion scores.
- 22
awesome-reverse-engineering
628morluto/awesome-reverse-engineeringA curated list of reverse-engineering tools and learning resources covering binaries, applications, firmware, file formats, and protocols, organized by the task you need to do rather than alphabetically.
- 23

bug-bounty-hunting-prompts
612mdpsec/bug-bounty-hunting-promptsA pack of reusable prompt files for running a structured, evidence-first bug bounty hunting workflow with an LLM agent, covering recon through triage and escalation.
- 24

Stuxnet
588Sadpainy/Stuxnet · CThis is a reconstructed source code of Stuxnet, the famous 2010 worm that sabotaged Siemens industrial control systems, rebuilt by the author from reverse-engineering research for educational and malware-analysis purposes.
- 25
scuttle
521Continuum-AI-Corp/scuttle · GoScuttle is an open-source Go library that encrypts sensitive fields in application logs before they ever reach storage, so copies that survive in databases, replicas, snapshots and backups stay unreadable even if the datastore is later compromised.
- 26
0
5120sec-labs/0 · TypeScript0 is an open-source, self-evolving, multi-model AI harness for security research that finds, verifies, and fixes vulnerabilities, built by the Swiss Applied AI & Cybersecurity Research Lab.
- 27
Ai-jailbreak
476Quincunx33/Ai-jailbreak · JavaScriptA curated collection of jailbreak prompts and exploit techniques that bypass the safety guardrails of both open-weight models (Gemma, Qwen, Llama, DeepSeek, Phi-4, Mistral) and frontier closed models (GPT-5.x, Gemini 3.x, Grok 4.x), documented for red-teaming and AI safety research.
- 28

FilzaSlop
4480xjohnnydev/FilzaSlop · Objective-CFilzaSlop is a fork of FilzaJailedDS that adds a sandbox escape exploit and app container access to the Filza file manager on iOS 18, iOS 26, and iOS 27 beta 1-4, plus a bundled PosterBoard Wallpaper Lab.
- 29

OhMyKeymint
438ITxiao6666/OhMyKeymint · RustOh My Keymint (OMK) is a custom Android Keystore implementation that fully mirrors the AOSP AIDL interface, designed to spoof key attestation and make app behavior harder for detectors to distinguish from a genuine AOSP device.
- 30

edrEvasionWorkshop
397tyeurada/edrEvasionWorkshopWorkshop materials from DEF CON 34 and BSidesLV 2026 on writing custom malware that evades EDR — from loaders to kernel-level techniques.
- 31

vmp-lazy-unpack
396x86rc/vmp-lazy-unpack · PythonThis is a Python tool that automatically unpacks Windows x64 binaries protected with VMProtect 3.x and rebuilds their import table (IAT), without needing a debugger or live memory dump.
- 32

EvilFontTool
353DoctorEww/EvilFontTool · PythonEvilFontTool is a font-based deception tool for red teaming and security research. It generates 'Evil Fonts' — fonts that remap glyphs so a document shows humans one text while terminals, AI systems, and copy-paste see completely different text.
- 33

bad_query
276forcequitOS/bad_query · Cbadquery is a proof-of-concept sandbox escape for iOS 26 and 27, written in C — code that demonstrates breaking out of the iOS app sandbox.
- 34
Erosion
245jailbreakdotparty/Erosion · SwiftErosion is an iOS customization toolbox that uses the bad_query sandbox escape exploit to apply tweaks on supported iOS/iPadOS versions, no traditional jailbreak required.
- 35
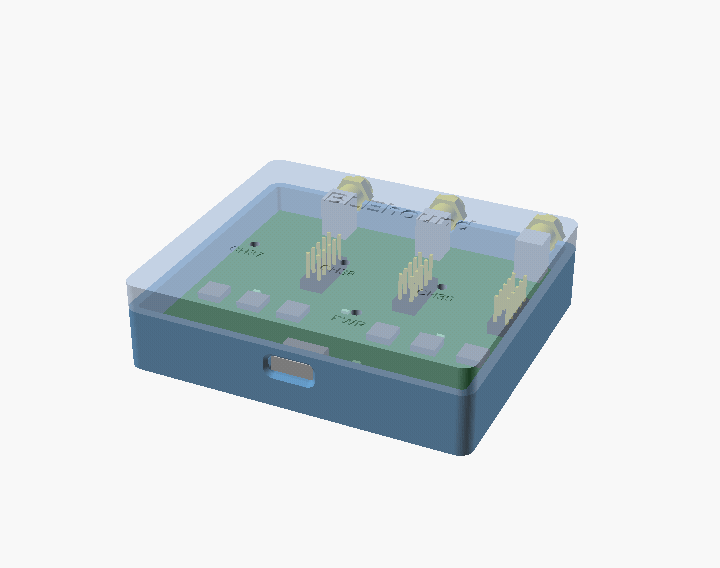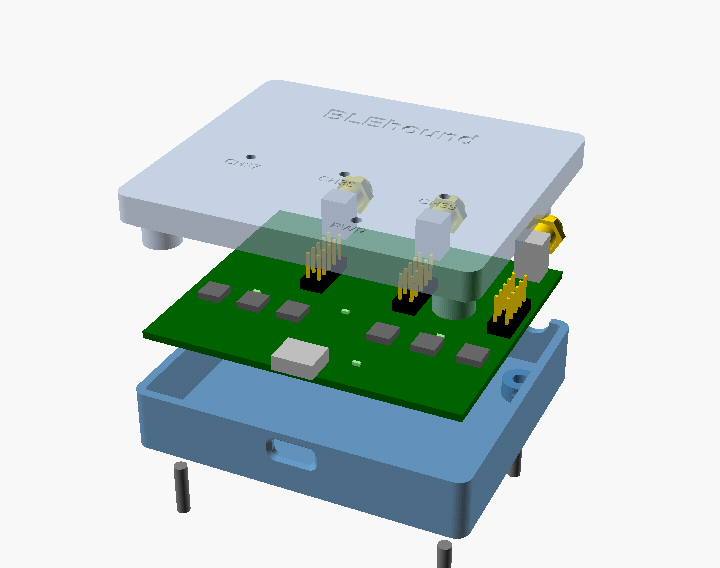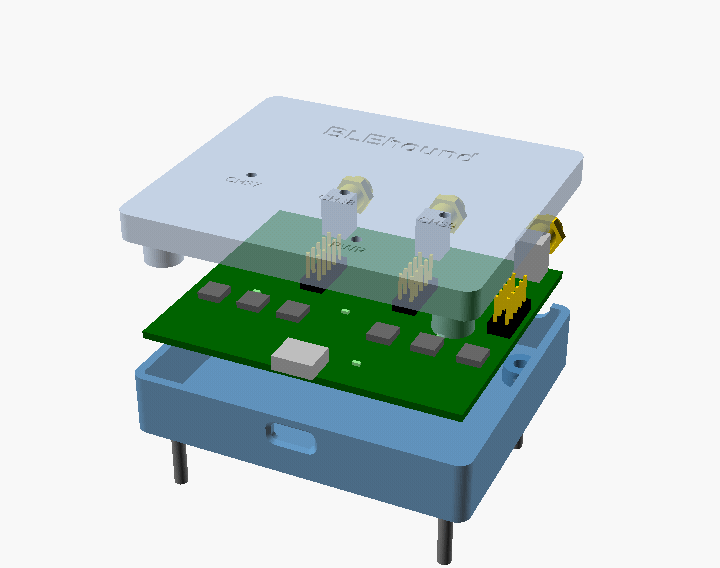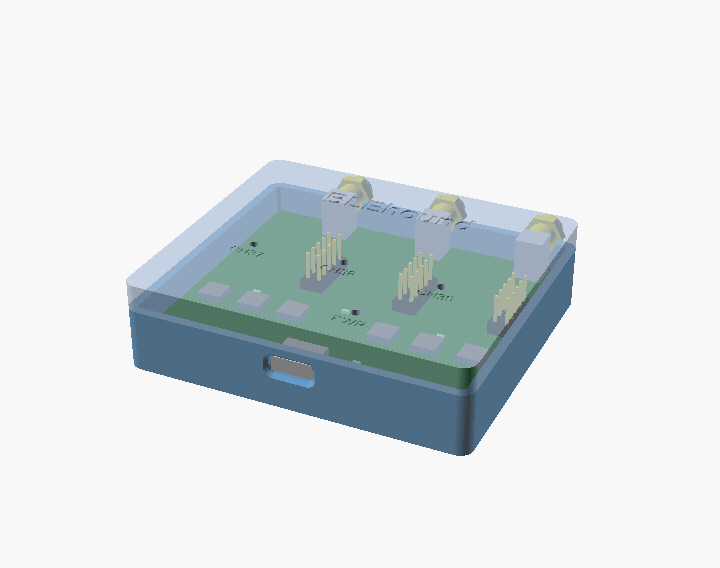
BLEhound
223BLEhound/BLEhound · CBLEhound is an open-source Bluetooth LE sniffer built on the nRF54 chip, combining custom firmware, a Wireshark extcap plugin, and open hardware (PCB/Gerbers/case) to capture BLE traffic with an RF front-end for better range.
- 36

Claude-AD
211ADScanPro/Claude-ADClaude-AD is a Claude Code plugin that gives Claude the methodology for an internal Active Directory penetration test: skills, agents and slash commands covering Kerberoasting, ADCS ESC1-17, DCSync, ACL abuse, NTLM relay and delegation abuse, each with OPSEC and telemetry notes.
- 37
noai-watermark
209mertizci/noai-watermark · Pythonnoai-watermark is an open-source CLI and Python toolkit that uses diffusion-based image regeneration to disrupt invisible AI watermarks (like Google SynthID, StableSignature, TreeRing) embedded in generated images, and it also inspects/strips AI metadata (EXIF, PNG text chunks, C2PA manifests).
- 38

open-crypto-puzzles
203floflo777/open-crypto-puzzles · PythonA catalog of real, unsolved crypto puzzles with wallets still funded on-chain (about 6 BTC, 13 ETH, 1,900 AR across 31 puzzles), each with the author's own research: the escrow address, the puzzle author's clues, what has been tried, and where the trail goes cold.
- 39

CVE-2026-62911
187hypnguyen1209/CVE-2026-62911 · PythonA proof-of-concept exploit for CVE-2026-62911, a pre-auth RCE in Microsoft Exchange Server that relays an NTLM machine account hash to the MRSProxy service to drop and run an ASPX webshell, giving full SYSTEM access without any credentials.
- 40

badnotes
149c22dev/badnotes · Objective-CBadNotes is a jailbreak tweak for iOS that unlocks GoodNotes Pro by spoofing the app's subscription check.
- 41

NSNFSSSFSFN
103ucsd-hacc/NSNFSSSFSFN · PythonThis repository contains the code accompanying the paper (eprint 2026/2131) implementing a variant of the number field sieve that lets an attacker with temporary access to a raw RSA signing oracle permanently forge signatures or decrypt ciphertexts, without ever factoring the public modulus N.
Related topics
Often tagged together
- security976
- cybersecurity245
- security-tools282
- hacking135
- linux4,184
- open-source5,666
- python2,383
- reverse-engineering221
- exploit51
- windows3,403
- offensive-security77
- penetration-testing126
- vulnerability50
- research764
- llm1,483
- macos3,544
- red-team79
- ai-security44
- cli2,227
- pentesting113
- infosec47
- mit3,312
- ai1,955
- hacking-tool75