Topics / #decompiler
Decompiler projects on GitHub
Decompilers that turn bytecode back into readable code.
As of , the most-starred Decompiler projects on GitHub are rea (290.9K stars), ghidra (89.8K stars) and jadx (51K stars). GitHub.Locker tracks 30 Decompiler repositories with 665.6K stars combined. The fastest-growing on October 16 was rea, with +17.7K stars in a day.
Hot right now
Most stars gained in a day · Oct 16
rea
morluto/rea · ★ 290.9KREA lets AI coding agents reverse engineer apps, binaries, websites, and other software through a single MCP server and CLI, returning findings with the evidence behind them so an agent can explain a feature or rebuild it.
 +757
ghidra
NationalSecurityAgency/ghidra · ★ 89.8KGhidra is a software reverse engineering (SRE) framework created and maintained by the NSA's Research Directorate, used to disassemble, decompile, graph, and analyze compiled code.
 +152
pokeheartgold
ctrl-cheeb-del/pokeheartgold · ★ 716It's a full decompilation of Pokémon HeartGold and SoulSilver for the Nintendo DS, reconstructing the entire games in source code form.
 +106
eleven
Zfinix/eleven · ★ 598Eleven is a reverse-engineering desktop app for macOS, Windows and Linux built around AI agents: you open a binary, Android APK, GPU kernel, shader or model, and any agent that speaks the Agent Client Protocol (ACP) reads the code, renames functions, leaves notes and proposes patches while you watch and approve each change.
The all-time top
30 projects · by stars
- 290.9K
#1 · morluto/rea
rea
REA lets AI coding agents reverse engineer apps, binaries, websites, and other software through a single MCP server and CLI, returning findings with the evidence behind them so an agent can explain a feature or rebuild it.
- 89.8K#2 · NationalSecurityAgency/ghidra
ghidra
Ghidra is a software reverse engineering (SRE) framework created and maintained by the NSA's Research Directorate, used to disassemble, decompile, graph, and analyze compiled code.
- 51K
 #3 · skylot/jadx
jadx
jadx is a Dex to Java decompiler: command line and GUI tools that produce Java source code from Android Dex and Apk files.
- 4
arthas
37.6Kalibaba/arthas · JavaArthas is a Java diagnostic tool from Alibaba that lets developers troubleshoot production issues on a live JVM without modifying code or restarting the server.
- 5
dnSpy
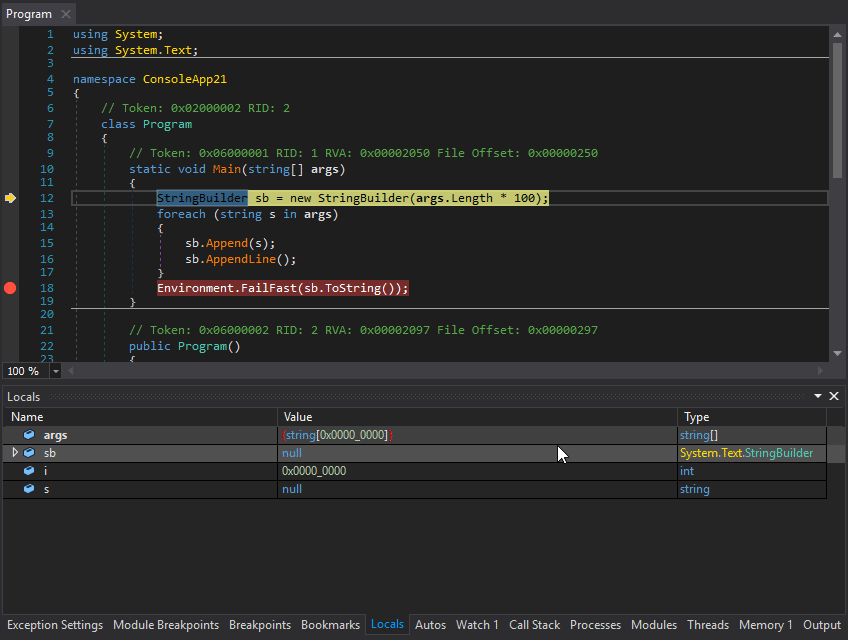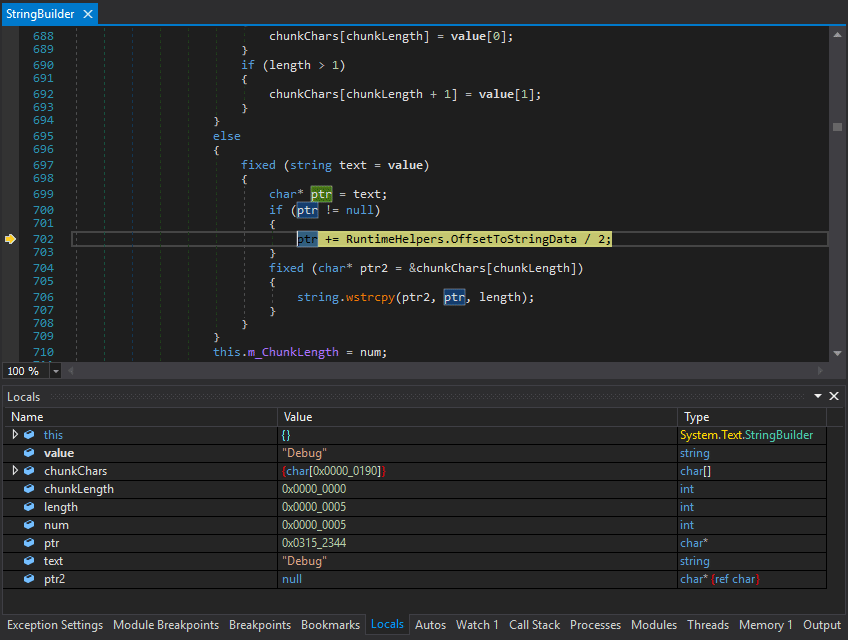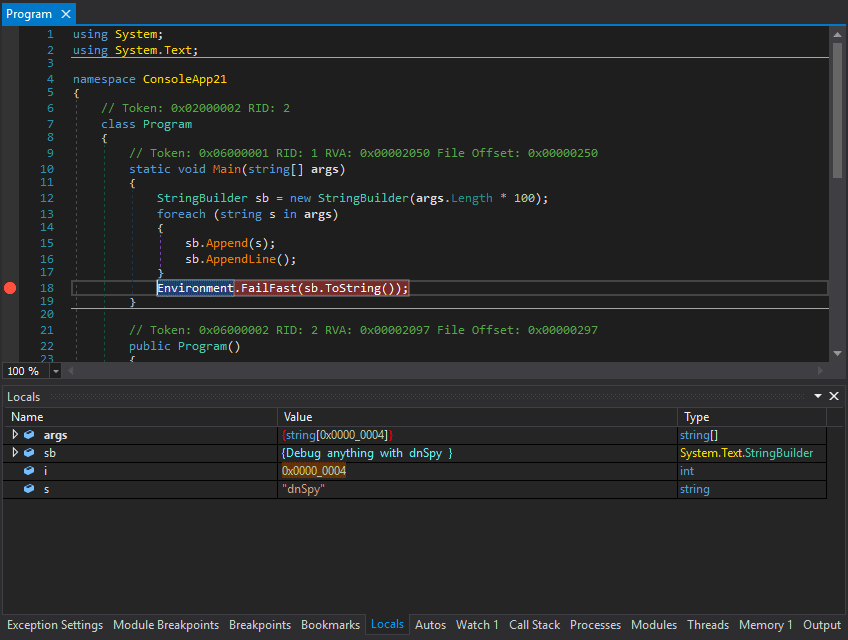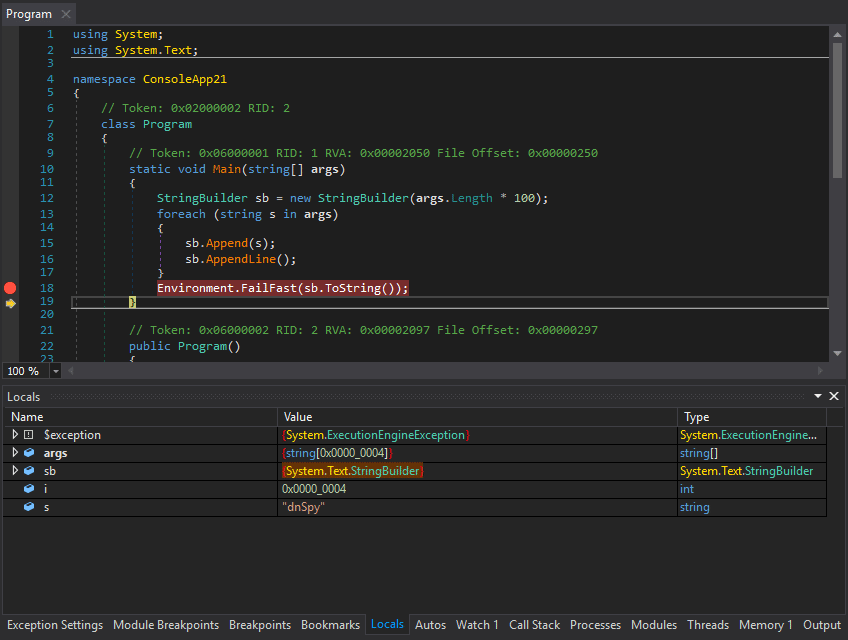
29.7KdnSpy/dnSpy · C#dnSpy is a Windows debugger and assembly editor for .NET and Unity programs - it lets you set breakpoints, step through code, and even edit methods and metadata without having the original source code.
- 6

ILSpy
26.7Kicsharpcode/ILSpy · C#It's the open-source, cross-platform .NET assembly browser and decompiler: point it at a compiled .NET assembly and it shows you the C# code behind it, on Windows, Linux, and macOS alike.
- 7

Apktool
26KiBotPeaches/Apktool · JavaApktool is a command-line tool for reverse engineering third-party, closed, binary Android apps. It decodes an APK's resources to nearly original form and rebuilds the app after you make changes.
- 8
radare2
25.1Kradareorg/radare2 · Cr2 (radare2) is a libre reverse engineering framework for Unix-like systems: a set of libraries, tools and plugins for analyzing, disassembling, emulating, debugging and modifying binaries.
- 9
bytecode-viewer
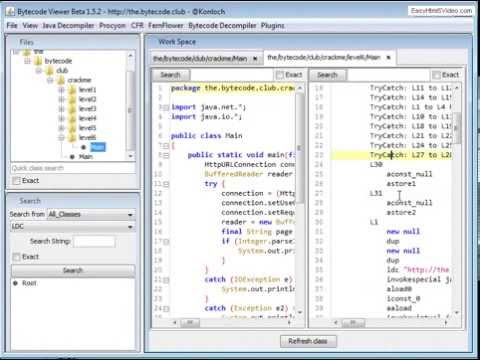
15.7KKonloch/bytecode-viewer · JavaBytecode Viewer (BCV) is a lightweight Java/Android reverse engineering suite: drag in a Jar or APK and it decompiles, disassembles, searches and debugs it, powered by several open source tools.
- 10

jd-gui
15.2Kjava-decompiler/jd-gui · JavaJD-GUI is a standalone graphical utility that decompiles Java .class files and displays the reconstructed source code.
- 11
ida-pro-mcp
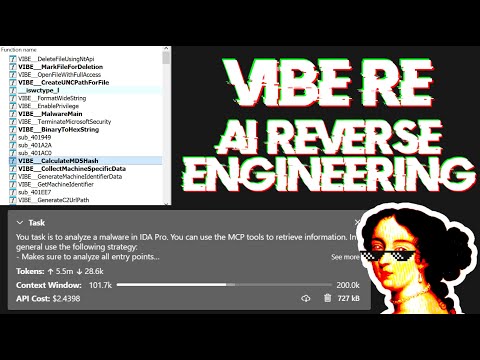
13Kmrexodia/ida-pro-mcp · PythonIt is an MCP server that bridges IDA Pro with AI language models, letting coding agents like Claude, Codex or Cursor help you reverse engineer binaries ('vibe reversing').
- 12
GhidraMCP
11.3KLaurieWired/GhidraMCP · JavaGhidraMCP is a Model Context Protocol server that lets LLMs autonomously reverse engineer applications by exposing Ghidra's core functionality (decompiling, renaming, listing imports/exports) to any MCP client.
- 13
reverse-engineering
10.6KwtsxDev/reverse-engineeringA curated list of reverse engineering resources: books, courses, practice grounds, and a big toolbox section spanning hex editors, disassemblers, debuggers, and dynamic analysis tools.
- 14

android-reverse-engineering-skill
8.2KSimoneAvogadro/android-reverse-engineering-skill · ShellA Claude Code skill that decompiles Android APK/XAPK/JAR/AAR files and extracts the HTTP APIs used by the app — Retrofit endpoints, OkHttp calls, hardcoded URLs, and authentication patterns — so you can document and reproduce them without the original source code.
- 15

Cpp2IL
3KSamboyCoding/Cpp2IL · C#Cpp2IL is a work-in-progress tool that reverses Unity's IL2CPP build process back into the original managed DLLs, letting you decompile IL2CPP Unity games into readable C#/CIL.
- 16
ASC
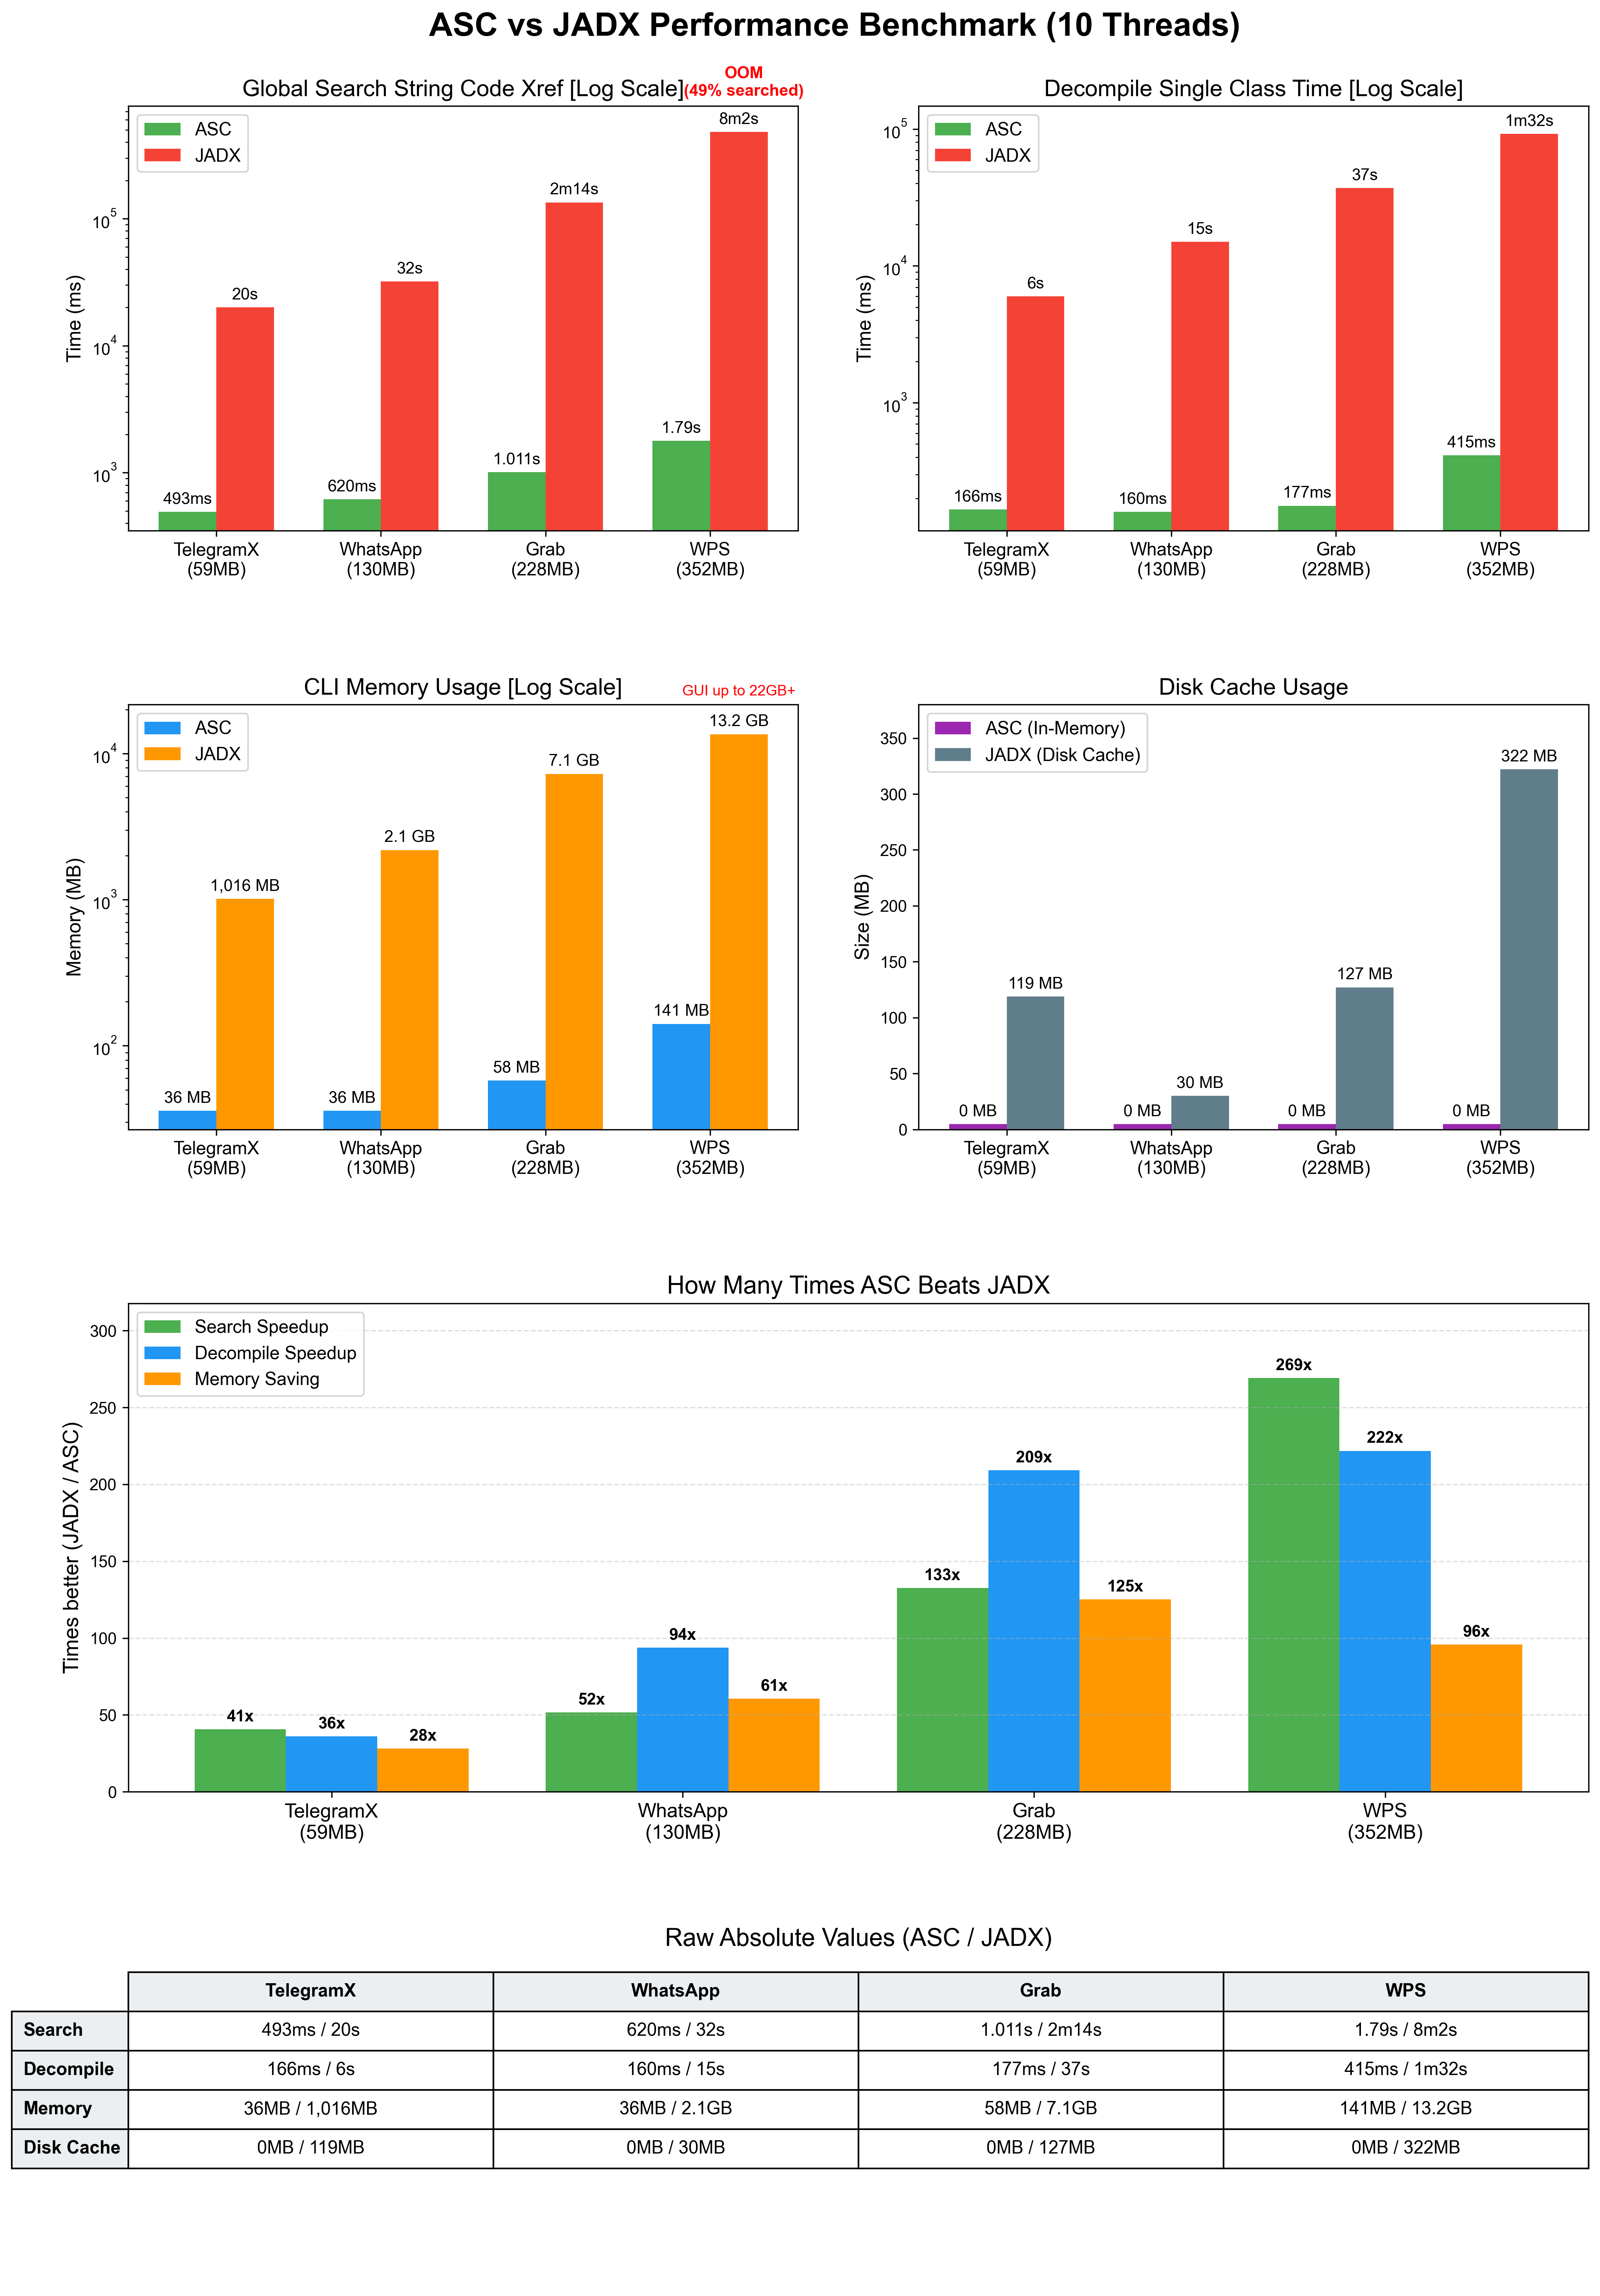
2.5KMG1937/ASC · PythonDroid ASC is a super FAST, lightweight Android decompiler built for AI agents and mobile researchers: instead of pre-indexing an APK, it extracts and decompiles code on demand in milliseconds.
- 17
OpenCE
1.6KOpenCommunityEdition/OpenCE · COpenCE is a port of the Halo: Combat Evolved decompilation (originally for the original Xbox) to Linux, Windows and Android, letting the game run natively on those platforms.
- 18
Seep-Reverse-Lab
1.6Kangusdevgo/Seep-Reverse-Lab · LuaSeep Reverse Lab is an agent-native reverse engineering and security-audit workbench that lets an AI coding agent autonomously run Radare2, JADX, Apktool and Frida to triage binaries, decompile APKs, and determine whether an app's feature gates are enforced locally or verified by a server (a CWE-602 authorization audit).
- 19

Petari
1.3KSMGCommunity/Petari · C++This is an open-source, work-in-progress decompilation of Super Mario Galaxy 1, rebuilding the game's original C++ source code by matching it against the compiled binary.
- 20
pokeheartgold
716ctrl-cheeb-del/pokeheartgold · CIt's a full decompilation of Pokémon HeartGold and SoulSilver for the Nintendo DS, reconstructing the entire games in source code form.
- 21

pinyon-shift
692arcanite24/pinyon-shift · PythonPinyon Shift is a Windows-only playable preview built from a native static recompilation of the Xbox 360 release of Forza Horizon, letting you build and run a working, imperfect version of the game from your own disc.
- 22
awesome-reverse-engineering
628morluto/awesome-reverse-engineeringA curated list of reverse-engineering tools and learning resources covering binaries, applications, firmware, file formats, and protocols, organized by the task you need to do rather than alphabetically.
- 23
bbhost
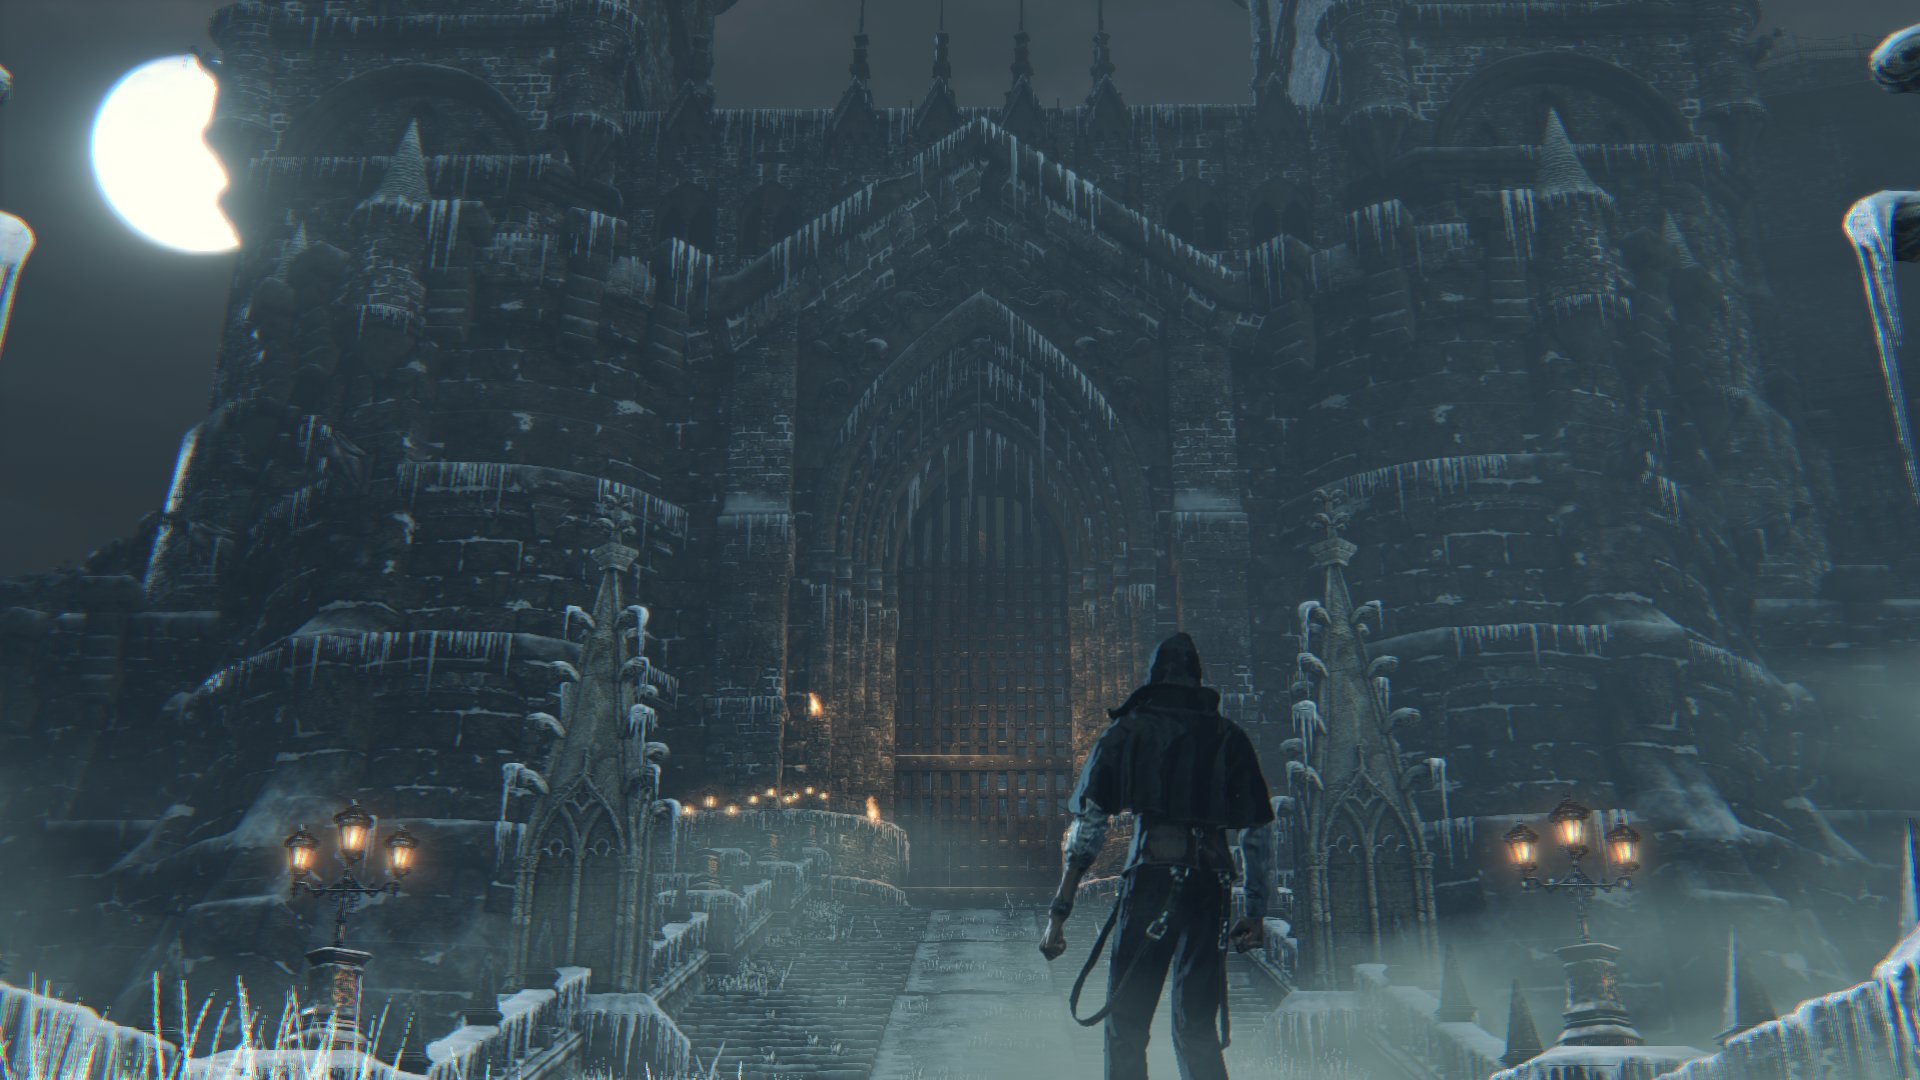
611droogie/bbhost · C++bbhost is a translation layer that runs Bloodborne's own unmodified 1.09 PS4 executable on Windows and Linux, reimplementing the PS4's system libraries and translating its GPU work (GCN shaders and draw calls) to Vulkan, aiming for a definitive PC version with any resolution, 60 fps, keyboard/mouse, mods and online play.
- 24
eleven
598Zfinix/eleven · TypeScriptEleven is a reverse-engineering desktop app for macOS, Windows and Linux built around AI agents: you open a binary, Android APK, GPU kernel, shader or model, and any agent that speaks the Agent Client Protocol (ACP) reads the code, renames functions, leaves notes and proposes patches while you watch and approve each change.
- 25
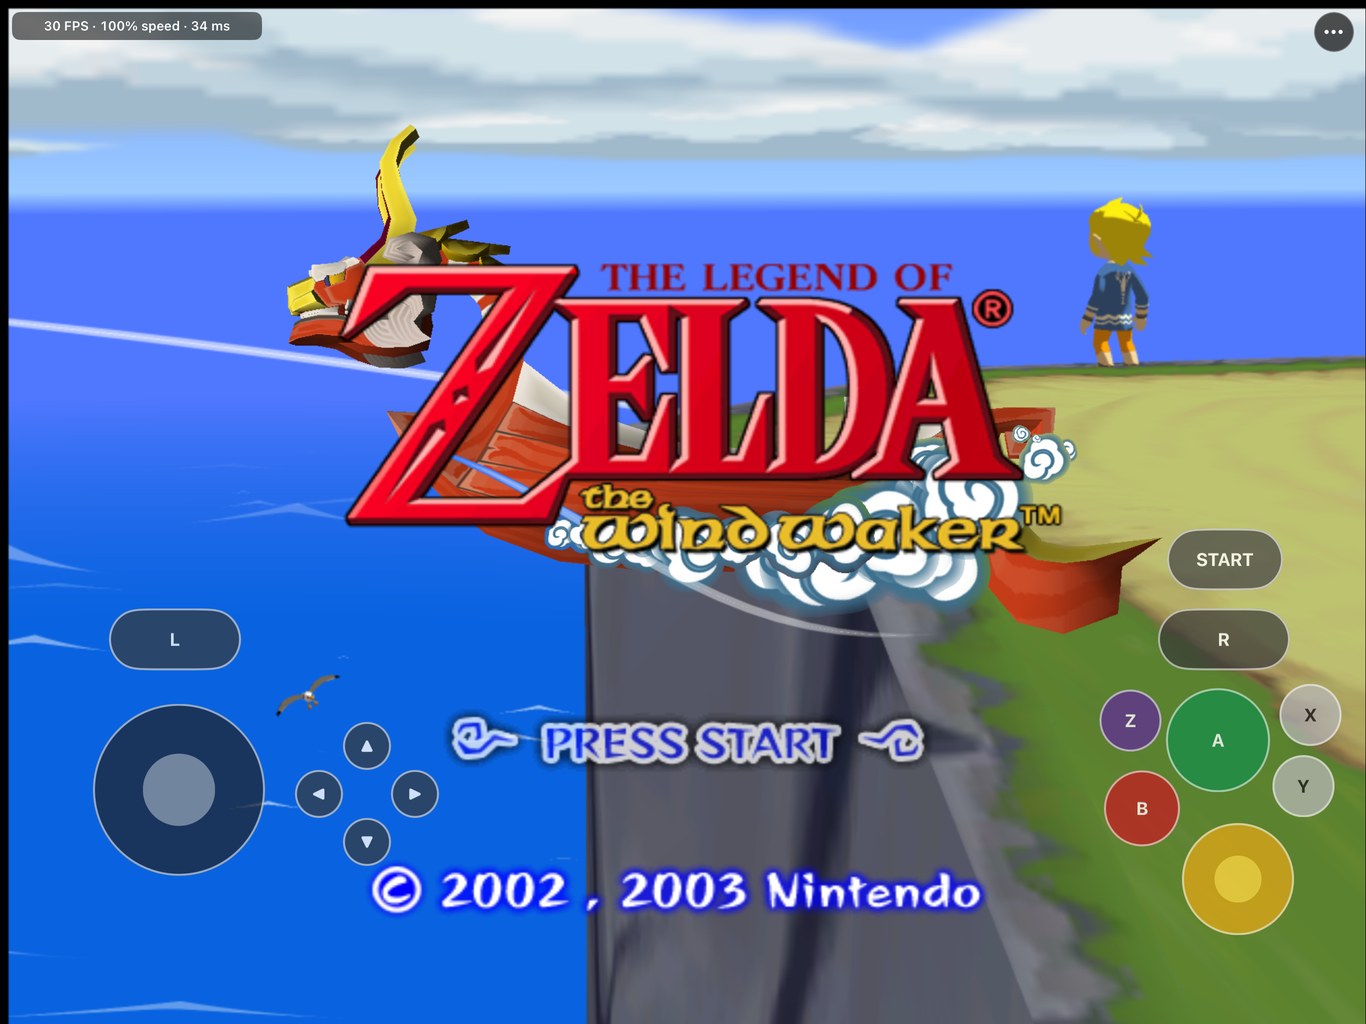
Wind-Waker-Recomp
543elliotttate/Wind-Waker-Recomp · CWind Waker Recomp is a native port of The Legend of Zelda: The Wind Waker for Windows, Mac, iPhone and iPad, made by statically recompiling the original GameCube game's PowerPC code into native machine code. It is a personal source fork of the BlueWake project with extra features like 60/120 FPS smooth motion, save states and wall climbing.
- 26
decomp.wtf
460i12bp8/decomp.wtf · Pythondecomp.wtf lets the AI coding agent you already use decompile a game you own into C code, one function at a time, then verifies each attempt compiles with the game's original compiler to the exact same bytes.
- 27

re4
349adonis-singh/re4 · C++A complete, byte-identical decompilation of Resident Evil 4 for GameCube — the G4BE08 debug build, both discs — reconstructed as readable C/C++ that rebuilds the exact original binaries.
- 28
ablation
214Ablation-Tool/ablation · PythonAblation is a reverse engineering framework that provides the same core disassembly, decompilation, and binary analysis capabilities as industry tools like Ghidra, IDA Pro, and Binary Ninja, and it's built to be driven by an AI coding agent.
- 29

Rise-6.9.5
165NoHackClient/Rise-6.9.5 · JavaRise 6.9.5 is an open-source rebuild of a Minecraft hacked/cheat client: the original closed-source RiseClient 6.9.5 was decompiled, deobfuscated, renamed and cleaned up so the source can be built and modified.
- 30
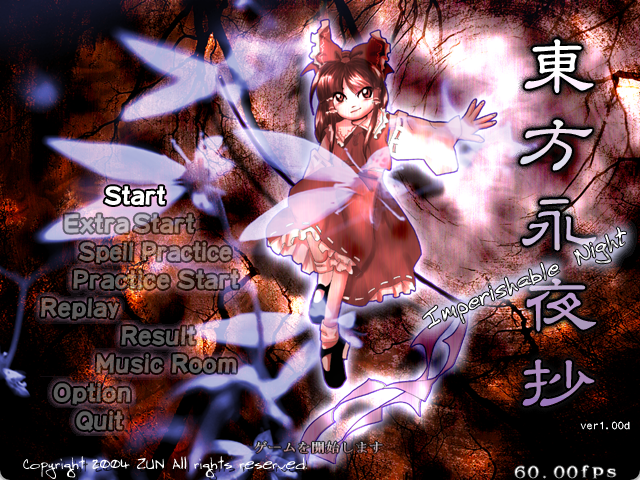
th08
117N0zoM1z0/th08 · C++A from-scratch C++ source reconstruction of the original Japanese 1.00d executable of Touhou 08 (Imperishable Night), rebuilt function-by-function until it matches the compiled game binary.
Related topics
Often tagged together
- reverse-engineering221
- windows3,403
- linux4,184
- macos3,544
- open-source5,666
- cross-platform2,623
- binary-analysis42
- developer-tools2,924
- disassembler23
- security976
- static-analysis125
- tool1,295
- android743
- cli2,227
- security-tools282
- desktop-app1,020
- game167
- gaming221
- java450
- malware-analysis34
- python2,383
- ai-agents1,289
- mcp913
- agent821