Topics / #vulnerabilities
Vulnerabilities projects on GitHub
Tools for detecting, scanning, and managing security vulnerabilities in software.
As of , the most-starred Vulnerabilities projects on GitHub are grype (13K stars), oss-fuzz (12.7K stars) and vuls (12.3K stars). GitHub.Locker tracks 5 Vulnerabilities repositories with 60.5K stars combined. The fastest-growing on October 16 was grype, with +8 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
 +8
grype
anchore/grype · ★ 13KGrype is a command-line vulnerability scanner that checks container images, filesystems, and SBOMs for known security vulnerabilities.
 +7
awesome-hacker-search-engines
edoardottt/awesome-hacker-search-engines · ★ 11.3KA curated list of search engines useful for penetration testing, vulnerability assessment, red/blue team operations, bug bounty hunting, and general OSINT work.
 +2
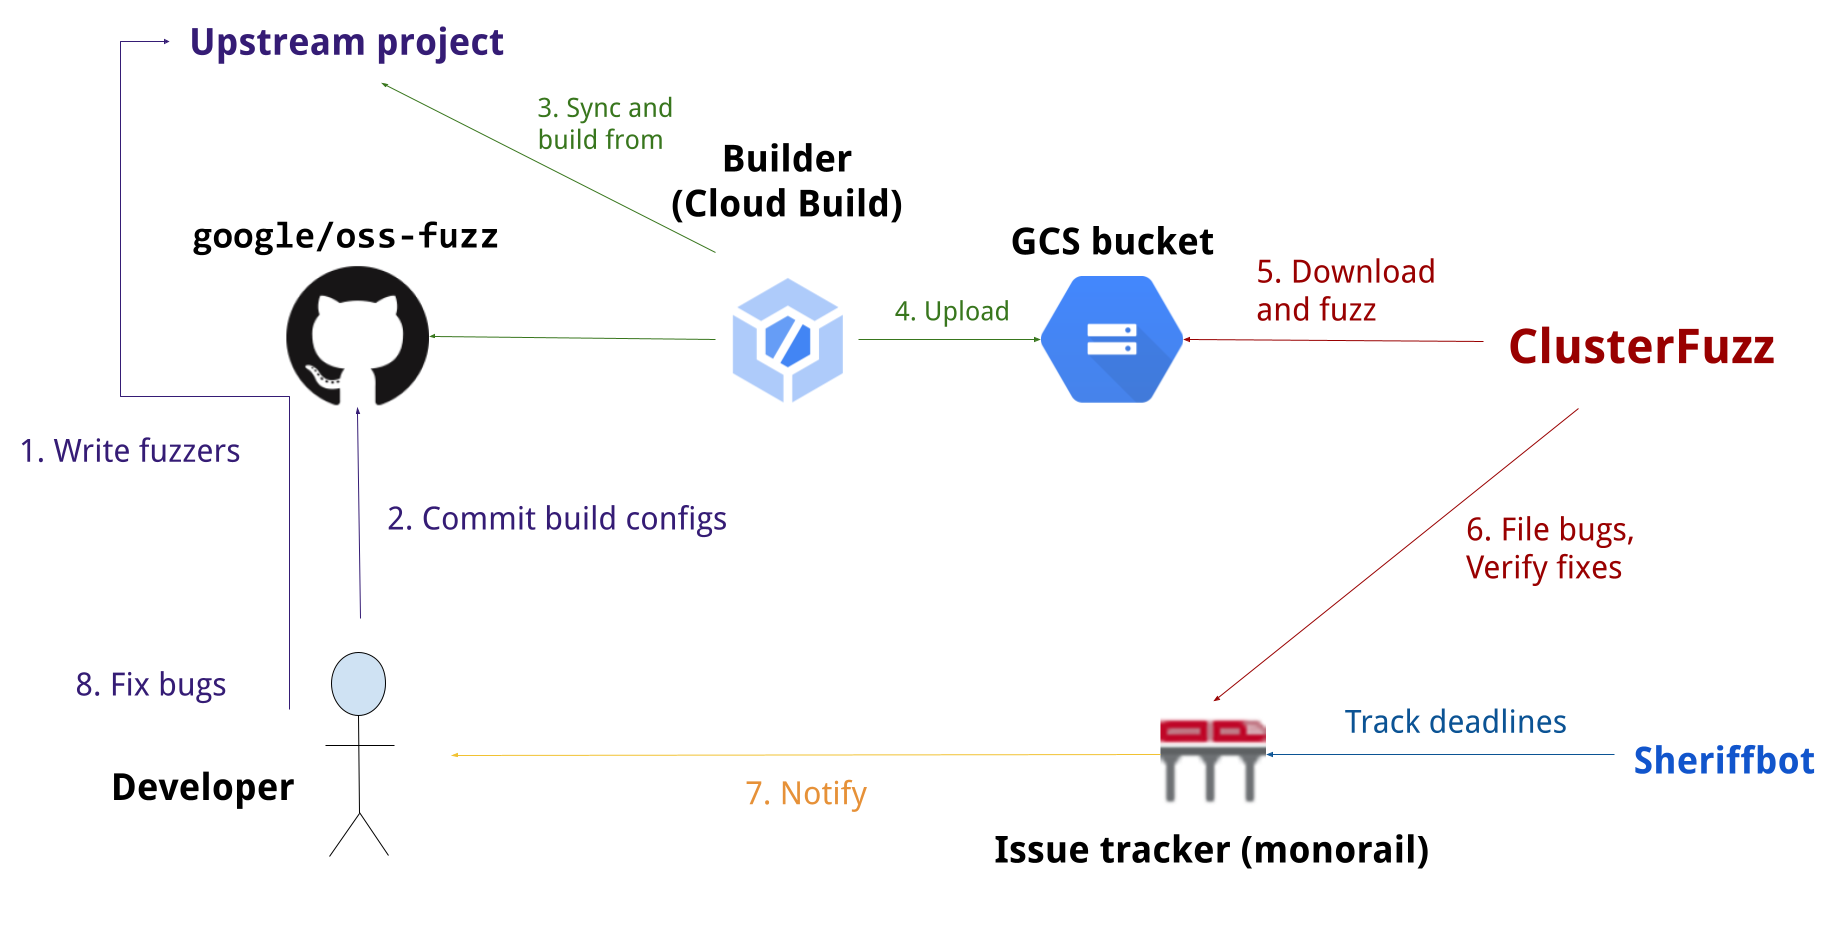
oss-fuzz
google/oss-fuzz · ★ 12.7KOSS-Fuzz is Google's free continuous fuzzing service for open source software: it runs guided fuzzing nonstop to surface security vulnerabilities and stability bugs before attackers do.
 +2
clair
quay/clair · ★ 11.1KClair is an open source tool for static analysis of vulnerabilities in application container images, covering both OCI and Docker image formats.
The all-time top
5 projects · by stars
- 13K#1 · anchore/grype
grype
Grype is a command-line vulnerability scanner that checks container images, filesystems, and SBOMs for known security vulnerabilities.
- 12.7K#2 · google/oss-fuzz
oss-fuzz
OSS-Fuzz is Google's free continuous fuzzing service for open source software: it runs guided fuzzing nonstop to surface security vulnerabilities and stability bugs before attackers do.
- 12.3K
 #3 · future-architect/vuls
vuls
Vuls is an open-source, agent-less vulnerability scanner written in Go. It automatically detects vulnerabilities affecting your servers and can generate reports on a regular basis, for example via CRON.
- 4
awesome-hacker-search-engines
11.3Kedoardottt/awesome-hacker-search-engines · ShellA curated list of search engines useful for penetration testing, vulnerability assessment, red/blue team operations, bug bounty hunting, and general OSINT work.
- 5
clair
11.1Kquay/clair · GoClair is an open source tool for static analysis of vulnerabilities in application container images, covering both OCI and Docker image formats.
Related topics
Often tagged together