Topics / #privilege-escalation
Privilege-escalation projects on GitHub
Techniques and checklists for escalating privileges on compromised systems.
As of , the most-starred Privilege-escalation projects on GitHub are PayloadsAllTheThings (81.8K stars), awesome-pentest (27.5K stars) and Awesome-Hacking-Resources (17.5K stars). GitHub.Locker tracks 15 Privilege-escalation repositories with 215.5K stars combined. The fastest-growing on October 17 was ghostlock-app, with +41 stars in a day.
Hot right now
Most stars gained in a day · Oct 17
 +41
ghostlock-app
YuKongA/ghostlock-app · ★ 2KGhostLock is a one-tap Android app that runs the CVE-2026-43499 kernel exploit to grant uid 0 (root) on a matching vulnerable kernel, optionally loading a KernelSU-style module afterward.
 +33
PayloadsAllTheThings
swisskyrepo/PayloadsAllTheThings · ★ 81.8KA massive curated collection of payloads, bypass techniques, and exploitation methodology for web application security testing, pentesting, and CTF challenges.
 +26
Claude-Red
SnailSploit/Claude-Red · ★ 7.6Kclaude-red is a curated library of offensive security skills for the Claude Skills system: structured SKILL.md files that prime Claude with expert-level methodology for one attack surface each, from SQLi to shellcode.
 +16
awesome-pentest
enaqx/awesome-pentest · ★ 27.5KA curated collection of penetration testing and offensive-security resources: tools, books, courses, conferences and practice targets for authorized security testing.
The all-time top
15 projects · by stars
- 81.8K#1 · swisskyrepo/PayloadsAllTheThings
PayloadsAllTheThings
A massive curated collection of payloads, bypass techniques, and exploitation methodology for web application security testing, pentesting, and CTF challenges.
- 27.5K#2 · enaqx/awesome-pentest
awesome-pentest
A curated collection of penetration testing and offensive-security resources: tools, books, courses, conferences and practice targets for authorized security testing.
- 17.5K
 #3 · vitalysim/Awesome-Hacking-Resources
Awesome-Hacking-Resources
A curated collection of hacking, penetration testing and AI red-teaming resources — courses, YouTube channels, CTF platforms and guides, picked to make you better at offensive security.
- 4

PENTESTING-BIBLE
14KblaCCkHatHacEEkr/PENTESTING-BIBLEA curated catalog of over 200 numbered links to pentesting articles, bug bounty write-ups, cheat sheets and other security lists — a reading collection, not software.
- 5
GTFOBins.github.io
13.8KGTFOBins/GTFOBins.github.io · YAMLGTFOBins is a curated list of Unix-like executables that can be abused to bypass local security restrictions in misconfigured systems — for example, binaries a restricted user can turn into a root shell.
- 6

PowerSploit
13.1KPowerShellMafia/PowerSploit · PowerShellPowerSploit is a collection of PowerShell modules that penetration testers use during all phases of an assessment, covering code execution, persistence, privilege escalation, credential theft, exfiltration and reconnaissance on Windows systems.
- 7

hacktricks
12.6KHackTricks-wiki/hacktricks · JavaScriptA free, open wiki of hacking tricks and techniques — everything the author has learnt from CTFs, real-world apps and security research, organized into a browsable reference with 12.5k+ GitHub stars.
- 8

Red-Teaming-Toolkit
10.8Kinfosecn1nja/Red-Teaming-ToolkitIt is a curated list of cutting-edge open-source security tools for red teamers and threat hunters, covering the full attack lifecycle from reconnaissance to exfiltration.
- 9
Claude-Red
7.6KSnailSploit/Claude-Red · Pythonclaude-red is a curated library of offensive security skills for the Claude Skills system: structured SKILL.md files that prime Claude with expert-level methodology for one attack surface each, from SQLi to shellcode.
- 10
awesome-android-root
5.2Kawesome-android-root/awesome-android-root · MarkdownA community-curated knowledge base covering over 650 root apps, Magisk/KernelSU/APatch modules, and LSPosed (Xposed) modules for rooted Android devices, plus step-by-step rooting guides.
- 11
dirtyfrag
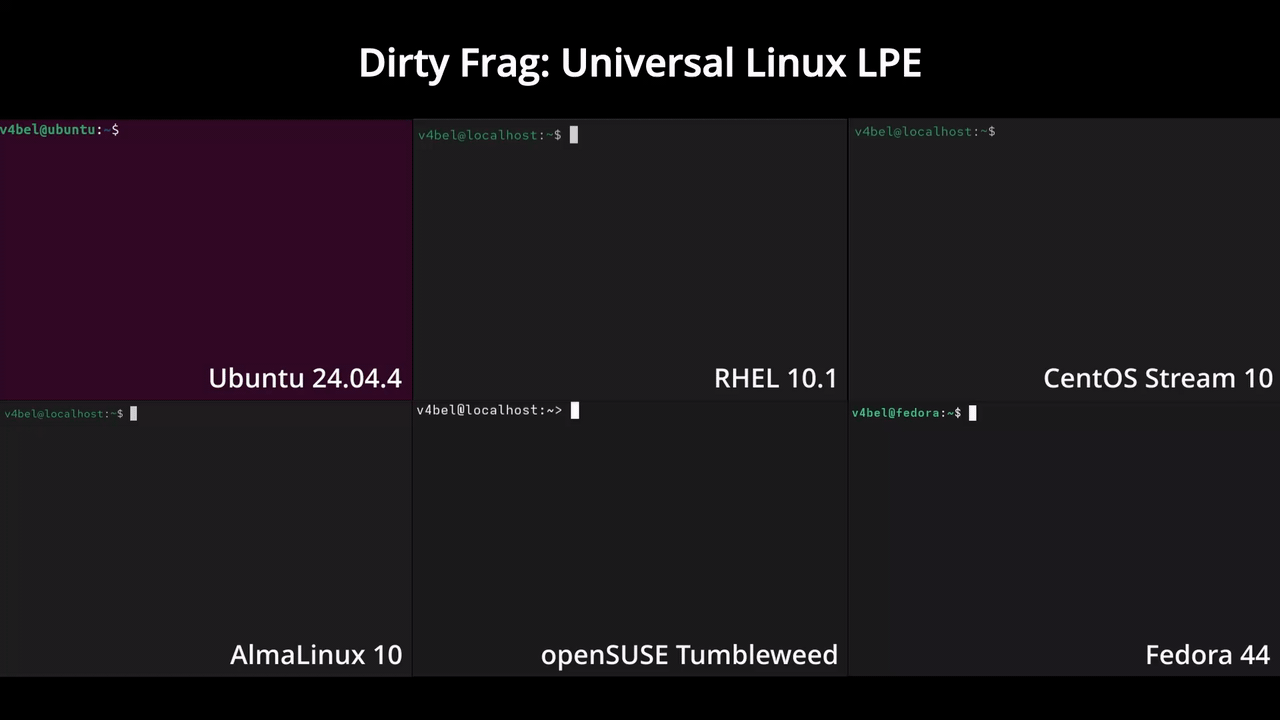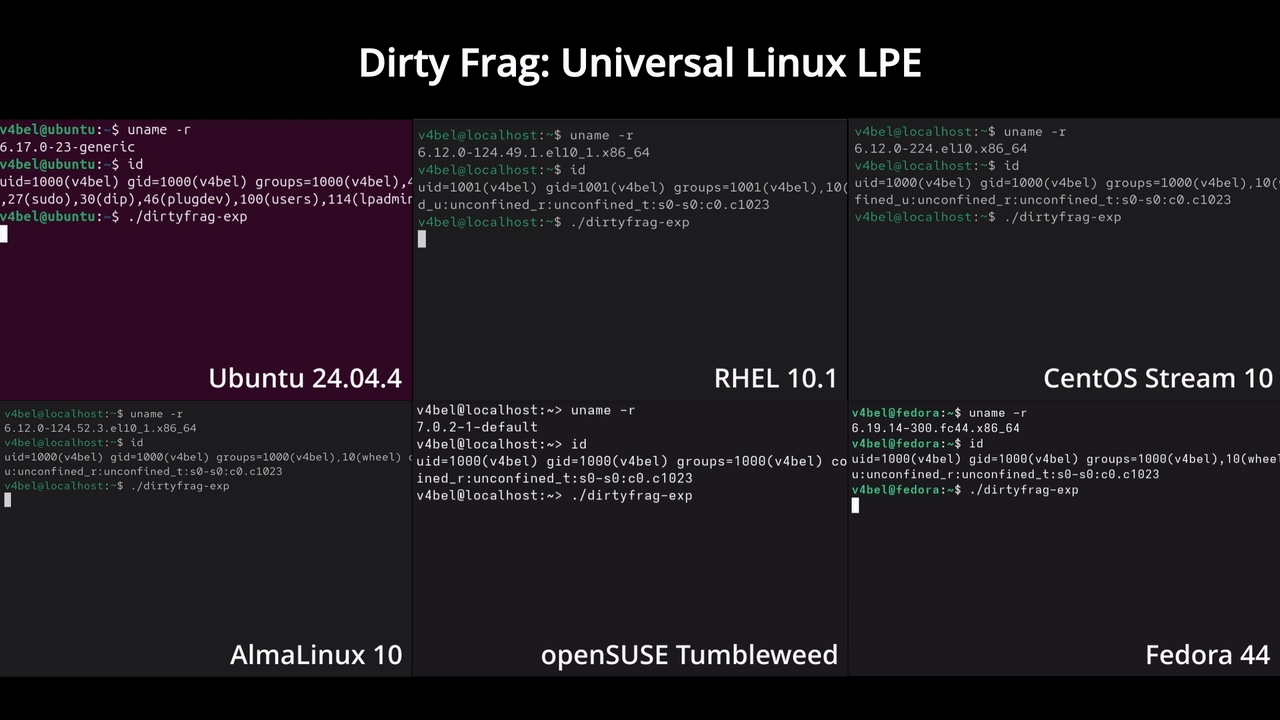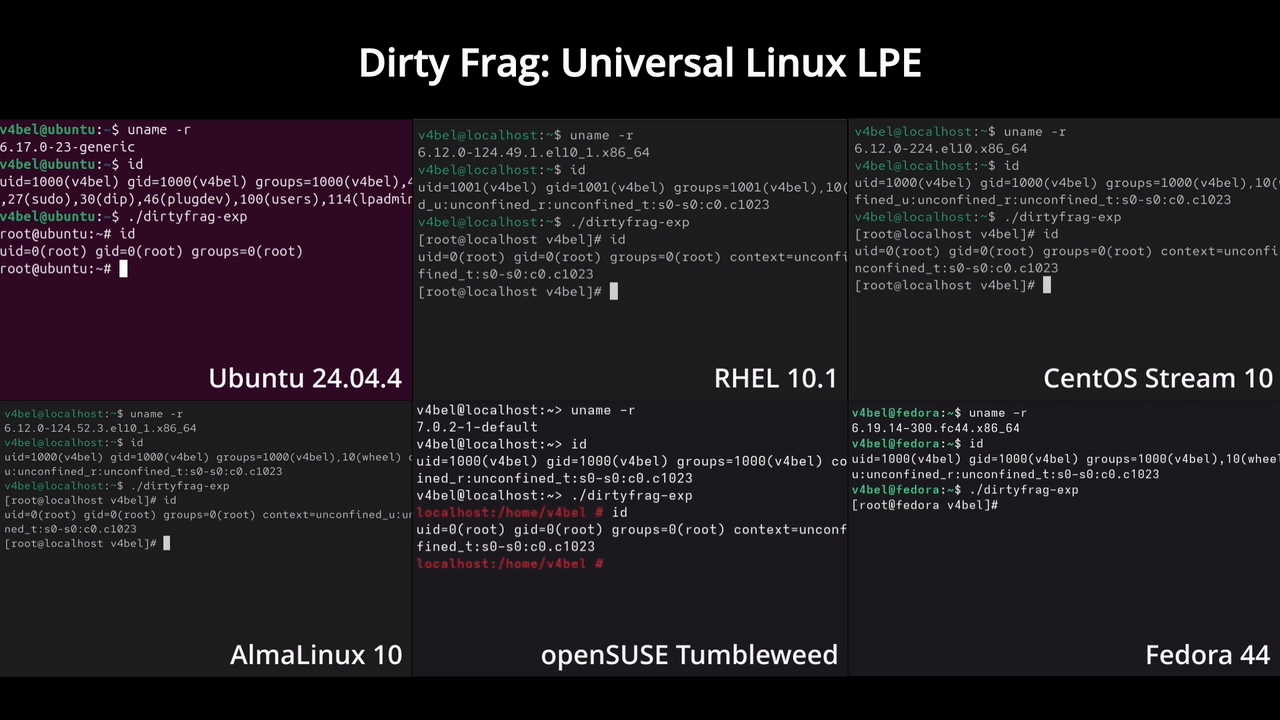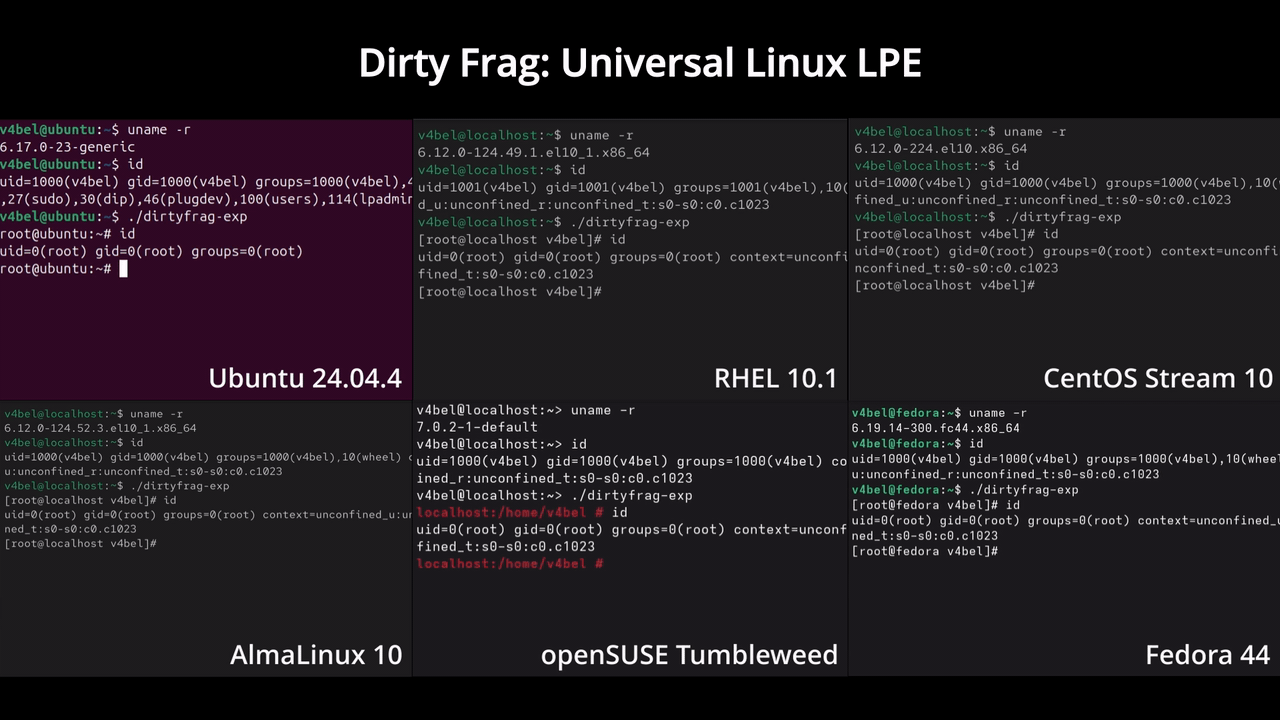
5.1KV4bel/dirtyfrag · CDirty Frag is a proof-of-concept Linux kernel local privilege escalation exploit that chains two page-cache write vulnerabilities (CVE-2026-43284 and CVE-2026-43500) to obtain root on major Linux distributions.
- 12

copy-fail-CVE-2026-31431
4.1Ktheori-io/copy-fail-CVE-2026-31431 · PythonThis repository is a technical writeup and proof-of-concept for CVE-2026-31431, a 9-year-old Linux kernel local privilege escalation (LPE) vulnerability found by Theori's AI vulnerability research tool, Xint Code.
- 13
ghostlock-app
2KYuKongA/ghostlock-app · KotlinGhostLock is a one-tap Android app that runs the CVE-2026-43499 kernel exploit to grant uid 0 (root) on a matching vulnerable kernel, optionally loading a KernelSU-style module afterward.
- 14
Erosion
247jailbreakdotparty/Erosion · SwiftErosion is an iOS customization toolbox that uses the bad_query sandbox escape exploit to apply tweaks on supported iOS/iPadOS versions, no traditional jailbreak required.
- 15

UniRoot
232kuuky29/UniRoot · KotlinUniRoot is a one-tap rooting app for Samsung Galaxy devices. It ships a new unprivileged kernel exploit (DirtyFrag, CVE-2026-43284) that roots the phone with a single button press, plus an older CVE-2026-43499-based exploit with per-device profiles, and it automatically re-roots the device on every boot.
Related topics
Often tagged together
- hacking135
- cybersecurity244
- security977
- security-tools281
- offensive-security77
- exploit51
- penetration-testing125
- pentesting112
- red-team78
- vulnerability49
- awesome-list497
- curated-list634
- infosec47
- resources706
- reverse-engineering222
- ctf36
- osint68
- pentest26
- ethical-hacking24
- exploit-development15
- exploitation12
- hacking-tool75
- kernel74
- redteam26