Topics / #pentesting-tools
Pentesting-tools projects on GitHub
Offensive security toolkits for penetration testing and automated exploitation.
As of , the most-starred Pentesting-tools projects on GitHub are strix (69.1K stars), shannon (49K stars) and social-engineer-toolkit (15.4K stars). GitHub.Locker tracks 9 Pentesting-tools repositories with 198.2K stars combined. The fastest-growing on October 16 was strix, with +214 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
 +214
strix
usestrix/strix · ★ 69.1KStrix is an open-source tool that uses autonomous AI agents to pentest your application like real hackers: it runs your code dynamically, finds vulnerabilities, and proves them with working exploits instead of just flagging suspicious patterns.
 +81
shannon
KeygraphHQ/shannon · ★ 49KShannon is an autonomous AI pentester that analyzes your web application's source code, maps attack vectors, and then executes real exploits against the running app to prove vulnerabilities before they reach production — 'no exploit, no report'.
 +49
hexstrike-ai
0x4m4/hexstrike-ai · ★ 12.9KHexStrike AI MCP Agents is an MCP server that lets AI agents like Claude, GPT, or Copilot autonomously run 150+ real cybersecurity tools for automated pentesting, bug bounty hunting, CTF challenges, and vulnerability discovery.
 +21
Claude-Red
SnailSploit/Claude-Red · ★ 7.6Kclaude-red is a curated library of offensive security skills for the Claude Skills system: structured SKILL.md files that prime Claude with expert-level methodology for one attack surface each, from SQLi to shellcode.
The all-time top
9 projects · by stars
- 69.1K#1 · usestrix/strix
strix
Strix is an open-source tool that uses autonomous AI agents to pentest your application like real hackers: it runs your code dynamically, finds vulnerabilities, and proves them with working exploits instead of just flagging suspicious patterns.
- 49K#2 · KeygraphHQ/shannon
shannon
Shannon is an autonomous AI pentester that analyzes your web application's source code, maps attack vectors, and then executes real exploits against the running app to prove vulnerabilities before they reach production — 'no exploit, no report'.
- 15.4K
 #3 · trustedsec/social-engineer-toolkit
social-engineer-toolkit
The Social-Engineer Toolkit (SET) is an open-source penetration testing framework for authorized social-engineering assessments, giving security teams guided attack vectors to test user awareness and validate controls.
- 4
hexstrike-ai
12.9K0x4m4/hexstrike-ai · PythonHexStrike AI MCP Agents is an MCP server that lets AI agents like Claude, GPT, or Copilot autonomously run 150+ real cybersecurity tools for automated pentesting, bug bounty hunting, CTF challenges, and vulnerability discovery.
- 5

hacktricks
12.6KHackTricks-wiki/hacktricks · JavaScriptA free, open wiki of hacking tricks and techniques — everything the author has learnt from CTFs, real-world apps and security research, organized into a browsable reference with 12.5k+ GitHub stars.
- 6

thc-hydra
12.4Kvanhauser-thc/thc-hydra · CHydra is a parallelized network login cracker by van Hauser / THC: a proof-of-concept tool showing researchers and security consultants how easily a remote system can be broken into through weak passwords. It supports over 50 protocols.
- 7
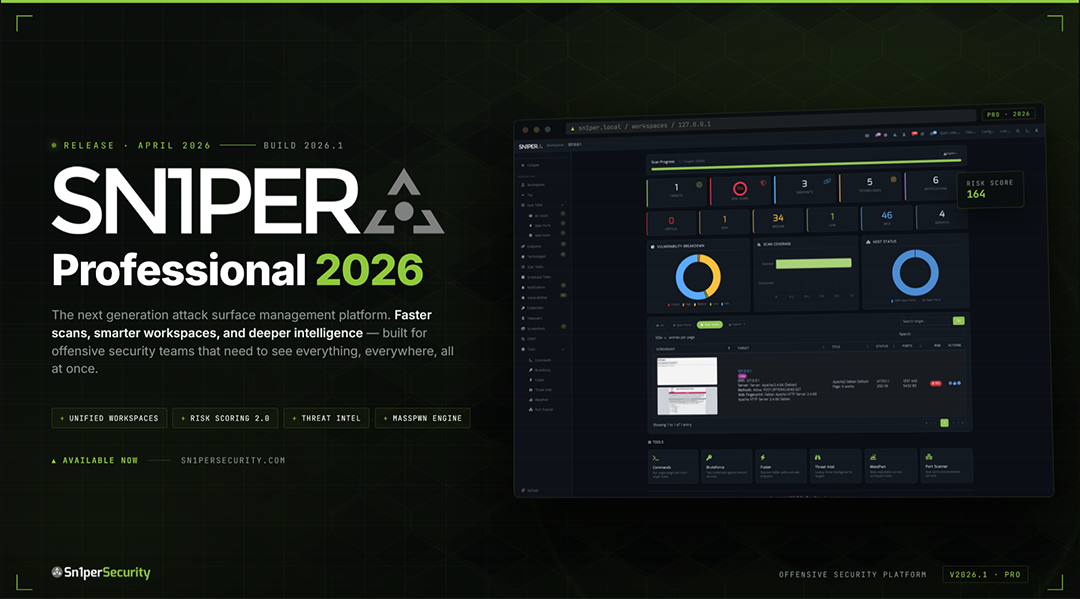
Sn1per
11.5K1N3/Sn1per · ShellSn1per is an offensive-security platform that bundles reconnaissance, vulnerability scanning, exploitation and reporting into one workspace, orchestrating 600+ exploits and 90+ third-party tools for pentesters and attack-surface-management teams.
- 8
CyberStrikeAI
7.8KAIPentest/CyberStrikeAI · GoCyberStrikeAI is an AI-native cybersecurity platform that turns natural-language intent into governed, auditable security operations, using agents, 100+ security tools, MCP integration, and attack-chain tracking for authorized penetration testing.
- 9
Claude-Red
7.6KSnailSploit/Claude-Red · Pythonclaude-red is a curated library of offensive security skills for the Claude Skills system: structured SKILL.md files that prime Claude with expert-level methodology for one attack surface each, from SQLi to shellcode.
Related topics
Often tagged together
- cybersecurity245
- penetration-testing126
- security976
- hacking135
- linux4,184
- offensive-security77
- pentesting113
- security-tools282
- docker1,660
- ethical-hacking24
- macos3,544
- open-source5,666
- python2,383
- red-team79
- self-hosted1,929
- ai1,955
- ai-penetration-testing6
- llm1,483
- network-security66
- pentest26
- vulnerability-scanner43
- windows3,403
- ai-agents1,289
- ai-hacking5