Topics / #cybersecurity
Cybersecurity projects on GitHub
Digital security broadly: threats, analysis tooling, and defensive practices.
As of , the most-starred Cybersecurity projects on GitHub are Awesome-Hacking (122.8K stars), sherlock (94.3K stars) and ghidra (89.8K stars). GitHub.Locker tracks 245 Cybersecurity repositories with 3.2M stars combined. The fastest-growing on October 16 was ghidra, with +757 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
 +757
ghidra
NationalSecurityAgency/ghidra · ★ 89.8KGhidra is a software reverse engineering (SRE) framework created and maintained by the NSA's Research Directorate, used to disassemble, decompile, graph, and analyze compiled code.
 +375
security-audit-skill
cloudflare/security-audit-skill · ★ 30.4KA Cloudflare coding-agent skill that turns your agent into a security auditor: it orchestrates isolated agents through a structured, multi-phase audit and returns independently verified, machine-readable findings.
 +214
strix
usestrix/strix · ★ 69.1KStrix is an open-source tool that uses autonomous AI agents to pentest your application like real hackers: it runs your code dynamically, finds vulnerabilities, and proves them with working exploits instead of just flagging suspicious patterns.
 +165
reverse-skill
zhaoxuya520/reverse-skill · ★ 42.4KIt is a skill pack that routes AI coding agents to the right reverse engineering, penetration testing, and security research methodology for a given task (APK, binary, JS, CTF, malware, etc.), checks which tools are installed, and runs a repeatable workflow instead of letting the agent guess commands.
The all-time top
Top 100 of 245 · by stars
- 122.8K
 #1 · Hack-with-Github/Awesome-Hacking
Awesome-Hacking
A massive index that links out to dozens of other awesome-lists covering nearly every security domain: android security, bug bounty, fuzzing, malware analysis, OSINT, reverse engineering, web hacking, and more.
- 94.3K
 #2 · sherlock-project/sherlock
sherlock
Sherlock hunts down social media accounts by username: give it a name and it checks across social networks for accounts registered under it.
- 89.8K#3 · NationalSecurityAgency/ghidra
ghidra
Ghidra is a software reverse engineering (SRE) framework created and maintained by the NSA's Research Directorate, used to disassemble, decompile, graph, and analyze compiled code.
- 4
PayloadsAllTheThings
81.8Kswisskyrepo/PayloadsAllTheThings · PythonA massive curated collection of payloads, bypass techniques, and exploitation methodology for web application security testing, pentesting, and CTF challenges.
- 5

Best-websites-a-programmer-should-visit
76.2Ksdmg15/Best-websites-a-programmer-should-visitA curated list of useful websites for programmers, covering news, learning resources, coding practice, tools, interview prep, and more.
- 6
SecLists
74.2Kdanielmiessler/SecLists · PHPSecLists is a huge collection of ready-made wordlists for security testing: usernames, passwords, URLs, sensitive data patterns, fuzzing payloads, web shells and more, all gathered in one repository.
- 7
strix
69.1Kusestrix/strix · PythonStrix is an open-source tool that uses autonomous AI agents to pentest your application like real hackers: it runs your code dynamically, finds vulnerabilities, and proves them with working exploits instead of just flagging suspicious patterns.
- 8

ImHex
55.4KWerWolv/ImHex · C++ImHex is a hex editor built for reverse engineers, programmers, and anyone analyzing binary data, with a custom pattern language for parsing and highlighting file structures.
- 9

x64dbg
49.9Kx64dbg/x64dbg · C++x64dbg is an open-source user-mode debugger for Windows, built specifically for reverse engineering and malware analysis.
- 10
shannon
49KKeygraphHQ/shannon · TypeScriptShannon is an autonomous AI pentester that analyzes your web application's source code, maps attack vectors, and then executes real exploits against the running app to prove vulnerabilities before they reach production — 'no exploit, no report'.
- 11

big-list-of-naughty-strings
47.7Kminimaxir/big-list-of-naughty-strings · PythonIt is a curated collection of strings with a high probability of breaking software when used as user input, meant to help QA testing of input validation.
- 12

mitmproxy
45.7Kmitmproxy/mitmproxy · Pythonmitmproxy is an interactive, SSL/TLS-capable intercepting proxy for HTTP/1, HTTP/2, and WebSockets, used by penetration testers and developers to inspect and modify traffic. mitmdump is its CLI version, and mitmweb is a web-based interface.
- 13
reverse-skill
42.4Kzhaoxuya520/reverse-skill · PowerShellIt is a skill pack that routes AI coding agents to the right reverse engineering, penetration testing, and security research methodology for a given task (APK, binary, JS, CTF, malware, etc.), checks which tools are installed, and runs a repeatable workflow instead of letting the agent guess commands.
- 14
sniffnet
41.6KGyulyVGC/sniffnet · RustSniffnet is a cross-platform desktop app for monitoring your network traffic in real time, with a graphical interface instead of raw terminal output.
- 15

metasploit-framework
39.2Krapid7/metasploit-framework · RubyMetasploit Framework is an open-source penetration testing framework written in Ruby — one of the best-known security toolkits on GitHub, with about 39,000 stars.
- 16
maigret
39.2Ksoxoj/maigret · PythonMaigret is an OSINT command-line tool that builds a dossier on a person by checking for an account under a given username across thousands of websites and pulling together whatever profile info it finds, with no API keys required.
- 17
500-AI-Agents-Projects
38.7Kashishpatel26/500-AI-Agents-Projects · PythonA curated collection of 500+ AI agent projects spanning every major framework (LangGraph, CrewAI, AutoGen, Agno) and industries like healthcare, finance, education, and cybersecurity, with links to working implementations.
- 18

CyberChef
36.1Kgchq/CyberChef · JavaScriptCyberChef is a web app that bundles encoding, encryption, compression, hashing and other data-analysis operations ('cyber' operations) into a single drag-and-drop recipe builder that runs entirely in your browser.
- 19
web-check
35.1Klissy93/web-check · TypeScriptWeb-Check is an open-source OSINT dashboard that lets you analyse any website: it pulls IP info, SSL chain, DNS records, cookies, headers, server location, and more into one report so you can understand its tech stack and security posture.
- 20
Anthropic-Cybersecurity-Skills
34.6Kmukul975/Anthropic-Cybersecurity-Skills · PythonAn open-source library of 818 production-grade cybersecurity skills for AI agents, covering 34 security domains and mapped to six frameworks including MITRE ATT&CK and NIST CSF 2.0.
- 21

CheatSheetSeries
33.7KOWASP/CheatSheetSeries · JavaScriptA collection of concise, high-value cheat sheets covering specific application security topics, maintained by OWASP.
- 22

How-To-Secure-A-Linux-Server
31.8Kimthenachoman/How-To-Secure-A-Linux-ServerThis is a long-form, evolving how-to guide (written as a GitHub README) that walks you through hardening a self-hosted Linux server, step by step, from SSH to firewalls to intrusion detection.
- 23
security-audit-skill
30.4Kcloudflare/security-audit-skill · JavaScriptA Cloudflare coding-agent skill that turns your agent into a security auditor: it orchestrates isolated agents through a structured, multi-phase audit and returns independently verified, machine-readable findings.
- 24
awesome-osint
30.3Kjivoi/awesome-osintThis is a curated 'awesome list' of hundreds of free and paid OSINT (open source intelligence) tools and resources, organized into categories like general search, Google dorks, data breach lookup, social media, threat actors, and dark web.
- 25
h4cker
29.8KThe-Art-of-Hacking/h4cker · Jupyter NotebookA curated collection of thousands of cybersecurity resources — references, scripts, tools, code, labs, and training material — maintained by Omar Santos as a companion to his books, video courses, and live training.
- 26
trufflehog
28.5Ktrufflesecurity/trufflehog · GoTruffleHog is a CLI tool that discovers, classifies, validates, and analyzes leaked secrets like API keys, database passwords, and private keys across many sources (Git, GitHub, S3, Docker, Slack, filesystems, and more).
- 27

awesome-pentest
27.4Kenaqx/awesome-pentestA curated collection of penetration testing and offensive-security resources: tools, books, courses, conferences and practice targets for authorized security testing.
- 28

masscan
26.1Krobertdavidgraham/masscan · CMasscan is an Internet-scale TCP port scanner that transmits SYN packets asynchronously and can scan the entire IPv4 Internet in under 5 minutes, sending up to 10 million packets per second from a single machine.
- 29
osquery
23.7Kosquery/osquery · C++osquery is a SQL powered operating system instrumentation, monitoring, and analytics framework: it exposes your OS as a high-performance relational database you can query with SQL.
- 30
spiderfoot
23.5Ksmicallef/spiderfoot · PythonOpen source OSINT automation — it collects intelligence on a target for threat intel and attack surface mapping, whether you are doing red team recon or checking what your organisation has exposed.
- 31
anubis
23.5KTecharoHQ/anubis · GoAnubis is a Web AI Firewall Utility that weighs the soul of incoming connections with challenges to protect upstream resources from AI scraper bots — built to defend the small internet from endless storms of AI-company requests.
- 32

API-Security-Checklist
23.3Kshieldfy/API-Security-ChecklistA community checklist of the most important security countermeasures to apply when designing, testing, and releasing an API — a list of checkboxes you run through before shipping.
- 33
SafeLine
22.8Kchaitin/SafeLine · GoSafeLine is a self-hosted web application firewall (WAF) and reverse proxy that protects your web apps from attacks and exploits by filtering and monitoring HTTP traffic.
- 34

personal-security-checklist
22.5Klissy93/personal-security-checklist · TypeScriptA community-maintained checklist of 300+ tips for protecting your digital security and privacy, curated by Alicia Sykes (Lissy93) and kept current for 2026.
- 35

mimikatz
21.9Kgentilkiwi/mimikatz · CA small Windows security tool, originally written to learn C. It is best known for extracting plaintext passwords, hashes, PIN codes and Kerberos tickets from memory, and can perform pass-the-hash, pass-the-ticket or build Golden tickets.
- 36

L1B3RT4S
21.9Kelder-plinius/L1B3RT4SA public collection of jailbreak prompts — the author calls them 'liberation prompts' — meant to make flagship AI models respond without their usual refusals. It is maintained by AI red-teamer elder-plinius.
- 37
vulhub
21.4Kvulhub/vulhub · DockerfileVulhub is an open-source collection of pre-built, ready-to-use vulnerable Docker environments: with one command you get a working lab for security research, learning, or demos.
- 38

security-guide-for-developers
21.1KFallibleInc/security-guide-for-developersThis is a practical security guide for web developers that explains common security issues (authentication, encryption, sessions, attacks, etc.) and gives a checklist for building more secure systems.
- 39
SWE-agent
20.6KSWE-agent/SWE-agent · PythonSWE-agent takes a GitHub issue and tries to fix it automatically using the language model you choose. It can also tackle offensive cybersecurity (CTF) challenges or other custom tasks.
- 40
SkillSpector
20.4KNVIDIA/SkillSpector · PythonSkillSpector is a security scanner for AI agent skills (used by Claude Code, Codex CLI, Gemini CLI, and MCP) that detects vulnerabilities, malicious patterns, prompt injection, data exfiltration, and supply-chain risks before you install a skill.
- 41
bettercap
20.1Kbettercap/bettercap · GoA portable all-in-one framework written in Go for recon and attacks on WiFi, Bluetooth Low Energy, wireless HID, CAN-bus and IPv4/IPv6 networks, built for security researchers and red teamers.
- 42

90DaysOfCyberSecurity
20.1Kfarhanashrafdev/90DaysOfCyberSecurityA free, 90-day self-paced cybersecurity study plan: daily tasks and curated resources that take you from networking basics to ethical hacking, ending with job-hunting help.
- 43
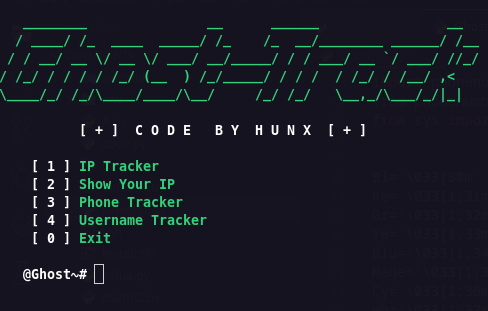
GhostTrack
19.1KHunxByts/GhostTrack · PythonGhostTrack is a Python command-line OSINT tool used to track a target's approximate location or gather details about a phone number, essentially a piece of information-gathering tooling for recon work.
- 44

Micro8
18KMicropoor/Micro8A free, open-source series of penetration-testing lessons written by veteran Chinese pentester Micropoor and published as a GitBook. It covers code audit, web, intranet and domain penetration, tunneling, and log-based tracing.
- 45
Awesome-Hacking-Resources
17.5Kvitalysim/Awesome-Hacking-ResourcesA curated collection of hacking, penetration testing and AI red-teaming resources — courses, YouTube channels, CTF platforms and guides, picked to make you better at offensive security.
- 46
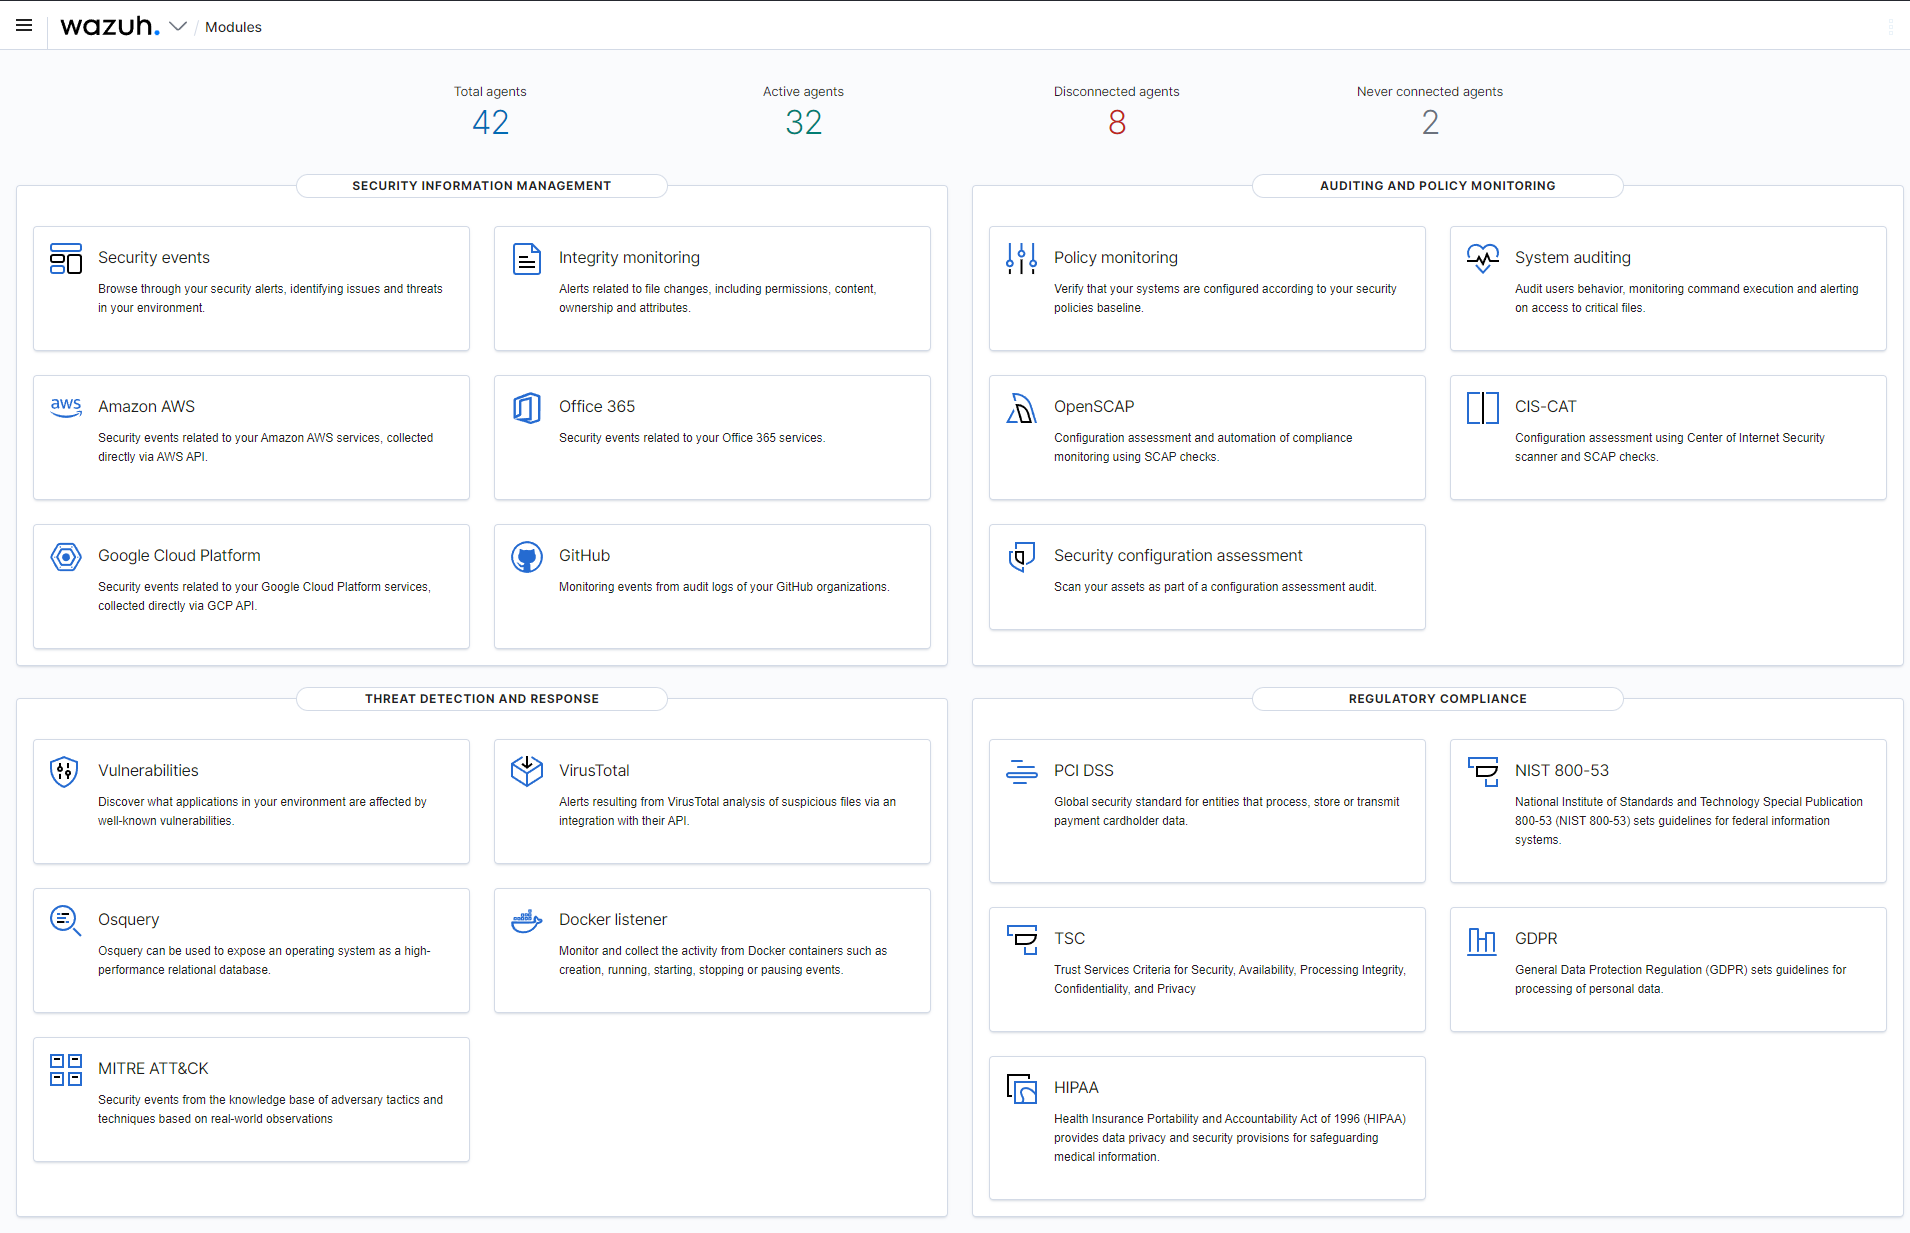
wazuh
17.3Kwazuh/wazuh · C++Wazuh is a free, open source security platform (XDR and SIEM) for threat prevention, detection and response across on-premises, virtualized, containerized and cloud workloads.
- 47

awesome-hacking
17.3Kcarpedm20/awesome-hackingA curated list of hacking tutorials, tools and resources covering system exploitation, reverse engineering, web security, network security, forensics, cryptography and wargames.
- 48

MHDDoS
16.9KMatrixTM/MHDDoS · PythonMHDDoS is a Python 3 DDoS testing toolkit with 57 attack methods spanning Layer 7 (HTTP floods, Cloudflare/OVH bypasses) and Layer 4/3 (TCP, UDP, SYN, amplification attacks), meant for authorized security testing and research.
- 49

how-web-works
16.8Kvasanthk/how-web-worksA detailed walkthrough of everything that happens behind the scenes between typing 'google.com' into a browser and the page rendering on screen, covering keyboard input, URL parsing, DNS, TLS, HTTP, and browser rendering internals.
- 50
lynis
16.5KCISOfy/lynis · ShellLynis is a security auditing and hardening tool for Linux, macOS, BSD, and other Unix-like systems. It scans the host it runs on for vulnerable software, misconfigurations, and weak settings, and gives hardening tips while also assisting with compliance testing (HIPAA, ISO27001, PCI DSS).
- 51
impacket
16.2Kfortra/impacket · PythonImpacket is a collection of Python classes for working with network protocols, giving low-level programmatic access to packets and, for some protocols like SMB1-3 and MSRPC, full protocol implementations.
- 52

PentestGPT
16KGreyDGL/PentestGPT · PythonPentestGPT is an agentic framework that uses large language models to run automated penetration testing and solve CTF challenges, working through staged phases like recon, exploitation and reporting.
- 53

zaproxy
16Kzaproxy/zaproxy · JavaZAP (Zed Attack Proxy) by Checkmarx is the world's most widely used web app security scanner, used to automatically find vulnerabilities in web applications during development and testing.
- 54
evilginx2
15.7Kkgretzky/evilginx2 · GoEvilginx is a man-in-the-middle attack framework used for phishing login credentials along with session cookies, which lets an attacker bypass 2-factor authentication.
- 55

hacker-roadmap
15.7Ksundowndev/hacker-roadmapThis is a curated roadmap and toolkit index for learning and practicing ethical hacking: it explains what penetration testing is and groups hundreds of security tools, wordlists and references by category (recon, password attacks, wireless, exploitation, web hacking, post-exploitation, frameworks).
- 56

social-engineer-toolkit
15.4Ktrustedsec/social-engineer-toolkit · PythonThe Social-Engineer Toolkit (SET) is an open-source penetration testing framework for authorized social-engineering assessments, giving security teams guided attack vectors to test user awareness and validate controls.
- 57

amass
15.4Kowasp-amass/amass · GoAmass is an OWASP project that maps attack surfaces and discovers external assets (like subdomains, IPs, and infrastructure) using open source intelligence gathering and active reconnaissance.
- 58

holehe
15.2Kmegadose/holehe · PythonHolehe is an OSINT tool that checks whether an email address is registered on 120+ websites (Twitter, Instagram, Spotify, Imgur, etc) by abusing each site's 'forgot password' or registration flow, without alerting the target.
- 59

XSStrike
15.2Ks0md3v/XSStrike · PythonXSStrike is a Cross Site Scripting (XSS) detection suite built around four hand-written parsers, an intelligent payload generator, a fuzzing engine, and a fast crawler. Instead of just firing generic payloads like most scanners, it analyzes the live response and crafts payloads guaranteed to work through context analysis.
- 60
crowdsec
15.2Kcrowdsecurity/crowdsec · GoCrowdSec is an open-source IDS/IPS and WAF that detects malicious behavior by analyzing logs and HTTP requests, blocks bad actors locally, and shares anonymized attack data with a crowdsourced network to build a real-time community blocklist.
- 61
prowler
15Kprowler-cloud/prowler · PythonProwler is an open-source cloud security platform that automates security and compliance checks across AWS, Azure, GCP, Kubernetes, M365, GitHub, and many other providers.
- 62
esp8266_deauther
15KSpacehuhnTech/esp8266_deauther · CESP8266 Deauther is open-source firmware for the ESP8266 chip that lets you scan nearby WiFi networks, send deauthentication packets to disconnect devices, and spin up dozens of fake WiFi networks to confuse scanners - an affordable platform for testing and learning about WiFi security.
- 63

awesome-security
15Ksbilly/awesome-securityA curated, categorized collection of well-known security resources — software, libraries, documents, books and other cool stuff — maintained by the community in the spirit of awesome-php and awesome-python.
- 64
wifiphisher
14.9Kwifiphisher/wifiphisher · PythonWifiphisher is a rogue access point framework for conducting Wi-Fi phishing and man-in-the-middle attacks against wireless clients, used in red team and penetration testing engagements.
- 65
Reverse-Engineering
14.8Kmytechnotalent/Reverse-Engineering · AssemblyA free, massive collection of reverse engineering and hacking tutorials covering x86, x64, ARM (32/64-bit), AVR, RISC-V, Windows internals, malware analysis, embedded systems, Rust, Go, Wasm, and more, delivered as free ebooks/lessons.
- 66
subfinder
14.6Kprojectdiscovery/subfinder · GoSubfinder is a fast passive subdomain enumeration tool that returns valid subdomains for a website by querying passive online sources, built for penetration testers and bug bounty hunters.
- 67

hacker101
14.6KHacker0x01/hacker101 · SCSSHacker101 is a free online class for web and mobile security from HackerOne (the Hacker0x01 org), aimed at everyone from programmers curious about bug bounties to seasoned security professionals.
- 68

binwalk
14.5KReFirmLabs/binwalk · RustBinwalk is a firmware analysis tool that can identify, and optionally extract, files and data that have been embedded inside other files.
- 69

gophish
14.3Kgophish/gophish · GoGophish is an open-source phishing toolkit for businesses and penetration testers: it lets you quickly set up and run phishing engagements and security awareness training campaigns.
- 70
awesome-malware-analysis
14.3Krshipp/awesome-malware-analysisA curated 'awesome list' of malware analysis tools and resources, covering sample collection, sandboxes, detection tools, threat intelligence feeds, reverse engineering, and forensics.
- 71

gobuster
14.2KOJ/gobuster · GoGobuster is a fast, multi-threaded command-line tool written in Go for brute-forcing web directories/files, DNS subdomains, and virtual hosts, plus enumerating S3/GCS cloud storage buckets and TFTP files.
- 72
opensnitch
14.2Kevilsocket/opensnitch · PythonOpenSnitch is an interactive application firewall for GNU/Linux, inspired by macOS's 'Little Snitch', that lets you see and approve or block each app's outgoing connections in real time.
- 73
juice-shop
14.1Kjuice-shop/juice-shop · TypeScriptOWASP Juice Shop is an intentionally insecure web application (a fake online juice store) built for security training, awareness demos, CTFs, and testing security tools.
- 74

PENTESTING-BIBLE
14KblaCCkHatHacEEkr/PENTESTING-BIBLEA curated catalog of over 200 numbered links to pentesting articles, bug bounty write-ups, cheat sheets and other security lists — a reading collection, not software.
- 75

opennhp
13.9KOpenNHP/opennhp · GoOpenNHP is a lightweight, cryptography-powered, open-source Zero Trust toolkit: it hides server ports, IP addresses, and domain names so your infrastructure stays invisible until a client is cryptographically authorized.
- 76

awesome-web-security
13.9Kqazbnm456/awesome-web-security · PythonA curated list of web security materials and resources, organized by vulnerability class and attack type (XSS, SQL injection, CSRF, SSRF, XXE, deserialization, OAuth, JWT, and more), plus cheatsheets, tools, and write-ups for penetration testing.
- 77

DVWA
13.9Kdigininja/DVWA · PHPDVWA (Damn Vulnerable Web Application) is a PHP/MariaDB web app that is deliberately full of security bugs, built as a legal practice target for security pros, students, and developers to learn web application security.
- 78
openhaystack
13.8Kseemoo-lab/openhaystack · SwiftOpenHaystack is a framework that lets you build your own 'AirTag'-like trackers by exploiting Apple's Find My network, so you can track Bluetooth accessories (keyrings, backpacks, notebooks) using nearby iPhones as relays.
- 79
pwntools
13.8KGallopsled/pwntools · PythonPwntools is a CTF framework and exploit development library written in Python, built for rapid prototyping with the goal of making exploit writing as simple as possible.
- 80
GTFOBins.github.io
13.8KGTFOBins/GTFOBins.github.io · YAMLGTFOBins is a curated list of Unix-like executables that can be abused to bypass local security restrictions in misconfigured systems — for example, binaries a restricted user can turn into a root shell.
- 81

SoftEtherVPN
13.7KSoftEtherVPN/SoftEtherVPN · CSoftEther VPN is a free, open-source, cross-platform VPN program where a single server can speak SSL-VPN, WireGuard, OpenVPN, IPsec, L2TP, MS-SSTP, L2TPv3 and EtherIP.
- 82
theZoo
13.5Kytisf/theZoo · PythontheZoo is a public repository of live malware samples and their source code, gathered so that anyone interested in malware analysis can study real specimens in an organized and accessible way.
- 83

secguide
13.4KTencent/secguideA free, Tencent-maintained secure coding guide for developers that catalogs API-level security risks and gives concrete, actionable secure-coding solutions.
- 84

git-secrets
13.4Kawslabs/git-secrets · Shellgit-secrets is a command-line tool that scans your git commits, commit messages, and merges to stop you from accidentally committing passwords, AWS keys, and other secrets.
- 85

RemoveWindowsAI
13.4Kzoicware/RemoveWindowsAI · PowerShellRemoveWindowsAI is a PowerShell script that force-removes Copilot, Recall, Image Creator and other AI features Microsoft keeps adding to Windows 11, to improve privacy, security and user experience.
- 86
mastg
13.3KOWASP/mastg · PythonA comprehensive OWASP manual for mobile app security testing and reverse engineering. It gives technical processes for verifying the weaknesses listed in the OWASP Mobile Security Weakness Enumeration (MASWE).
- 87

nuclei-templates
13.1Kprojectdiscovery/nuclei-templates · JavaScriptThis is a community-curated collection of over 11,000 detection templates for the Nuclei vulnerability scanner, covering CVEs, misconfigurations, exposed panels, and other security issues.
- 88

PowerSploit
13.1KPowerShellMafia/PowerSploit · PowerShellPowerSploit is a collection of PowerShell modules that penetration testers use during all phases of an assessment, covering code execution, persistence, privilege escalation, credential theft, exfiltration and reconnaissance on Windows systems.
- 89

grype
13Kanchore/grype · GoGrype is a command-line vulnerability scanner that checks container images, filesystems, and SBOMs for known security vulnerabilities.
- 90
ida-pro-mcp
13Kmrexodia/ida-pro-mcp · PythonIt is an MCP server that bridges IDA Pro with AI language models, letting coding agents like Claude, Codex or Cursor help you reverse engineer binaries ('vibe reversing').
- 91

user.js
12.9Karkenfox/user.js · JavaScriptarkenfox user.js is a community-maintained Firefox configuration template that hardens privacy and security settings, aiming to reduce tracking and fingerprinting as much as possible while trying to keep the browser usable.
- 92
hexstrike-ai
12.9K0x4m4/hexstrike-ai · PythonHexStrike AI MCP Agents is an MCP server that lets AI agents like Claude, GPT, or Copilot autonomously run 150+ real cybersecurity tools for automated pentesting, bug bounty hunting, CTF challenges, and vulnerability discovery.
- 93
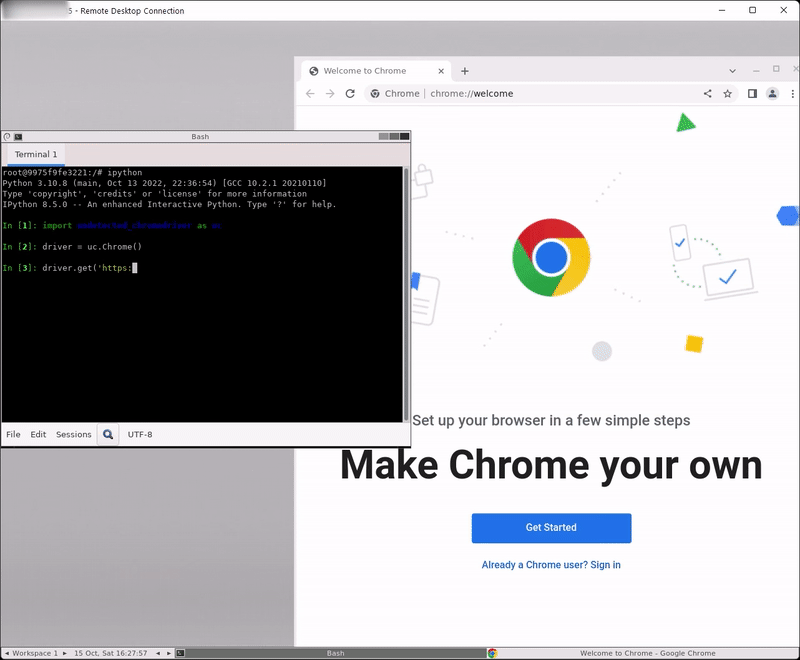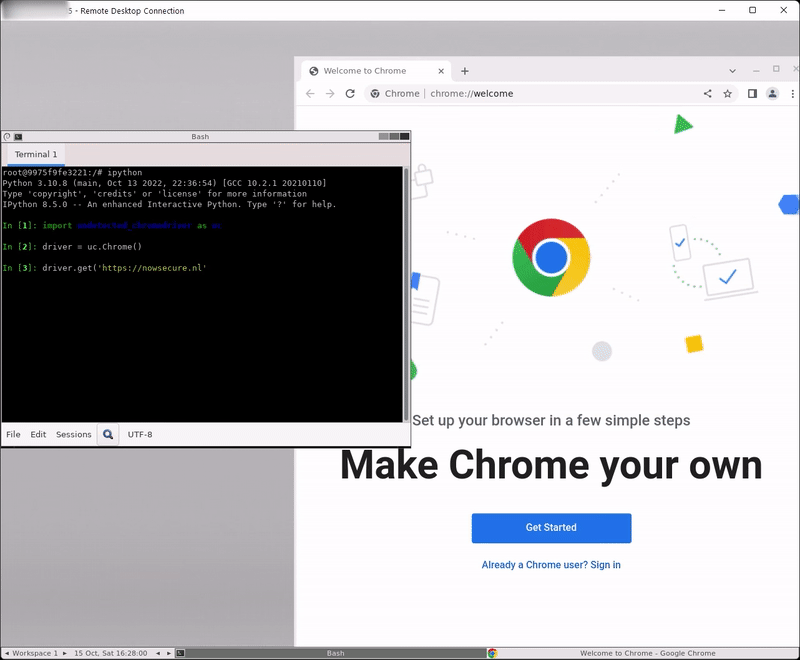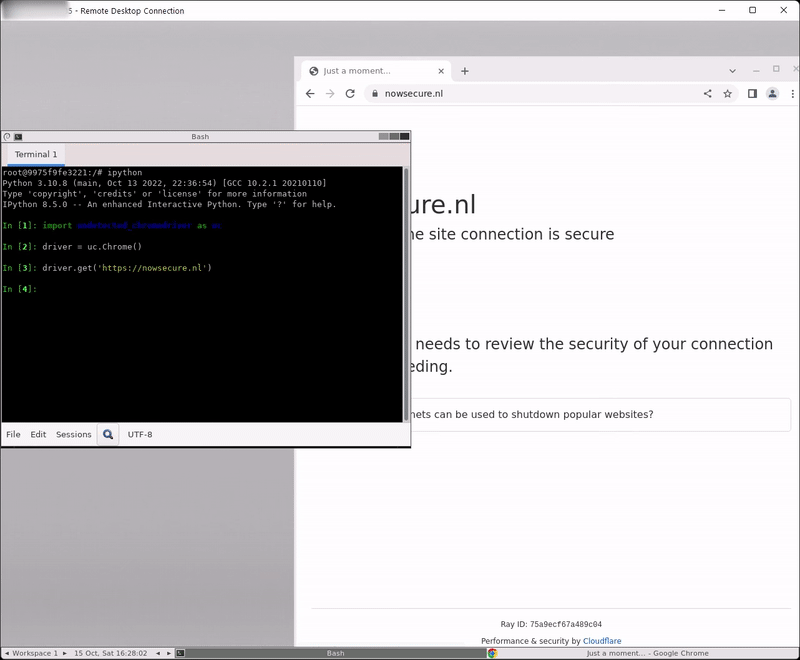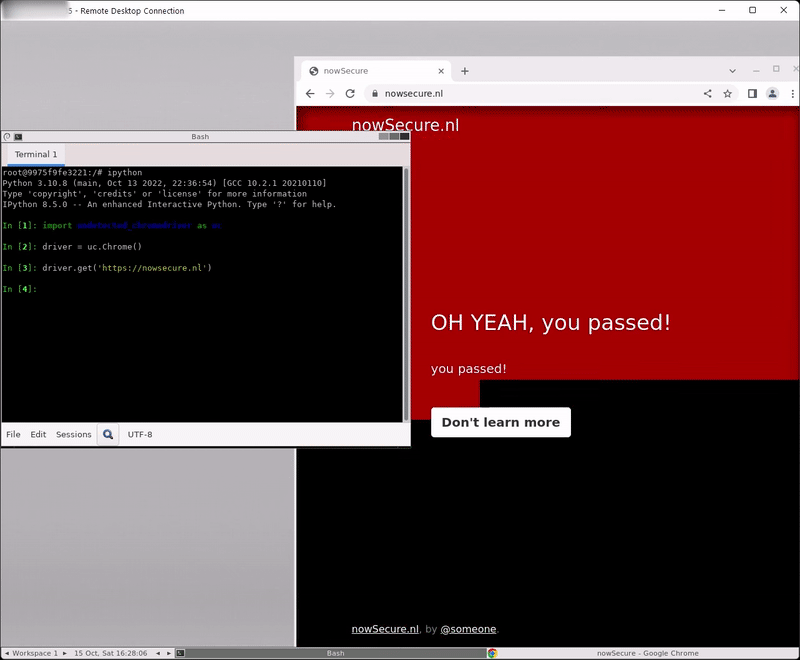
undetected-chromedriver
12.9Kultrafunkamsterdam/undetected-chromedriver · PythonIt is a patched Selenium Chromedriver for Python that automatically downloads and modifies the chromedriver binary so it evades anti-bot systems like Distil, Imperva, DataDome and Cloudflare IUAM.
- 94
ESP32Marauder
12.8Kjustcallmekoko/ESP32Marauder · C++ESP32 Marauder is a suite of offensive and defensive WiFi and Bluetooth tools that run as firmware on an ESP32 microcontroller, used for things like wardriving, scanning, and wireless security testing.
- 95
atomic-red-team
12.7Kredcanaryco/atomic-red-team · CAtomic Red Team is a library of small, portable security tests, each mapped to a specific MITRE ATT&CK technique, that security teams run to check whether their defenses actually detect real attacker behavior.
- 96

wifi-cracking
12.7Kbrannondorsey/wifi-crackingA step-by-step tutorial for cracking WPA/WPA2 Wi-Fi passwords: capture a handshake with Airodump-ng, then crack it offline with Aircrack-ng or Hashcat.
- 97

scapy
12.6Ksecdev/scapy · PythonScapy is a Python-based interactive packet manipulation program and library that lets you forge, decode, send, capture, and analyze network packets.
- 98
urh
12.6Kjopohl/urh · PythonURH (Universal Radio Hacker) is a suite for investigating wireless protocols: it captures radio signals via SDR hardware, demodulates them with automatic modulation detection, and helps you reverse-engineer the bits and bytes flying over the air.
- 99

hacktricks
12.6KHackTricks-wiki/hacktricks · JavaScriptA free, open wiki of hacking tricks and techniques — everything the author has learnt from CTFs, real-world apps and security research, organized into a browsable reference with 12.5k+ GitHub stars.
- 100

thc-hydra
12.4Kvanhauser-thc/thc-hydra · CHydra is a parallelized network login cracker by van Hauser / THC: a proof-of-concept tool showing researchers and security consultants how easily a remote system can be broken into through weak passwords. It supports over 50 protocols.
Showing the 100 most-starred of 245. See every one in the catalog.
Related topics
Often tagged together
- security976
- security-tools282
- linux4,184
- open-source5,666
- windows3,403
- macos3,544
- penetration-testing126
- hacking135
- pentesting113
- python2,383
- cli2,227
- red-team79
- docker1,660
- mit3,312
- offensive-security77
- reverse-engineering221
- cross-platform2,623
- terminal1,101
- self-hosted1,929
- hacking-tool75
- network-security66
- developer-tools2,924
- osint68
- vulnerability50