Topics / #application-security
Application-security projects on GitHub
Securing applications against common attacks and vulnerabilities.
As of , the most-starred Application-security projects on GitHub are Anthropic-Cybersecurity-Skills (34.6K stars), CheatSheetSeries (33.7K stars) and h4cker (29.8K stars). GitHub.Locker tracks 18 Application-security repositories with 217.2K stars combined. The fastest-growing on October 17 was Anthropic-Cybersecurity-Skills, with +43 stars in a day.
Hot right now
Most stars gained in a day · Oct 17
 +43
Anthropic-Cybersecurity-Skills
mukul975/Anthropic-Cybersecurity-Skills · ★ 34.6KAn open-source library of 818 production-grade cybersecurity skills for AI agents, covering 34 security domains and mapped to six frameworks including MITRE ATT&CK and NIST CSF 2.0.
 +18
Claude-BugHunter
elementalsouls/Claude-BugHunter · ★ 5.1KA drop-in skill bundle for the Claude Code skills system that turns Claude into a bug-hunting researcher or red-team operator: it ships 83 skills, 15 slash commands, and knowledge curated from 681 disclosed HackerOne reports across 24 vulnerability classes, plus enterprise identity and infrastructure attack matrices.
h4cker
The-Art-of-Hacking/h4cker · ★ 29.8KA curated collection of thousands of cybersecurity resources — references, scripts, tools, code, labs, and training material — maintained by Omar Santos as a companion to his books, video courses, and live training.
 +8
juice-shop
juice-shop/juice-shop · ★ 14.1KOWASP Juice Shop is an intentionally insecure web application (a fake online juice store) built for security training, awareness demos, CTFs, and testing security tools.
The all-time top
18 projects · by stars
- 34.6K#1 · mukul975/Anthropic-Cybersecurity-Skills
Anthropic-Cybersecurity-Skills
An open-source library of 818 production-grade cybersecurity skills for AI agents, covering 34 security domains and mapped to six frameworks including MITRE ATT&CK and NIST CSF 2.0.
- 33.7K
 #2 · OWASP/CheatSheetSeries
CheatSheetSeries
A collection of concise, high-value cheat sheets covering specific application security topics, maintained by OWASP.
- 29.8K
#3 · The-Art-of-Hacking/h4cker
h4cker
A curated collection of thousands of cybersecurity resources — references, scripts, tools, code, labs, and training material — maintained by Omar Santos as a companion to his books, video courses, and live training.
- 4

API-Security-Checklist
23.3Kshieldfy/API-Security-ChecklistA community checklist of the most important security countermeasures to apply when designing, testing, and releasing an API — a list of checkboxes you run through before shipping.
- 5
SafeLine
22.8Kchaitin/SafeLine · GoSafeLine is a self-hosted web application firewall (WAF) and reverse proxy that protects your web apps from attacks and exploits by filtering and monitoring HTTP traffic.
- 6
juice-shop
14.1Kjuice-shop/juice-shop · TypeScriptOWASP Juice Shop is an intentionally insecure web application (a fake online juice store) built for security training, awareness demos, CTFs, and testing security tools.
- 7

DVWA
13.9Kdigininja/DVWA · PHPDVWA (Damn Vulnerable Web Application) is a PHP/MariaDB web app that is deliberately full of security bugs, built as a legal practice target for security pros, students, and developers to learn web application security.
- 8

secguide
13.4KTencent/secguideA free, Tencent-maintained secure coding guide for developers that catalogs API-level security risks and gives concrete, actionable secure-coding solutions.
- 9

codex-security
11.1Kopenai/codex-security · TypeScriptCodex Security is OpenAI's CLI and TypeScript SDK for defining security policy and for finding, validating, and fixing security vulnerabilities in your code.
- 10

codeql
10.2Kgithub/codeql · CodeQLThis is the standard library and query collection for CodeQL, the code analysis engine that powers GitHub Advanced Security code scanning and GitHub's commercial security products.
- 11
Claude-BugHunter
5.1Kelementalsouls/Claude-BugHunter · PythonA drop-in skill bundle for the Claude Code skills system that turns Claude into a bug-hunting researcher or red-team operator: it ships 83 skills, 15 slash commands, and knowledge curated from 681 disclosed HackerOne reports across 24 vulnerability classes, plus enterprise identity and infrastructure attack matrices.
- 12
mantis
2.5Kgoogle/mantis · PythonMantis is a toolkit of skills plus a reference agent harness (built on Google's ADK) that lets AI coding agents autonomously find, reproduce, triage, and patch vulnerabilities in a codebase.
- 13
gh-secure
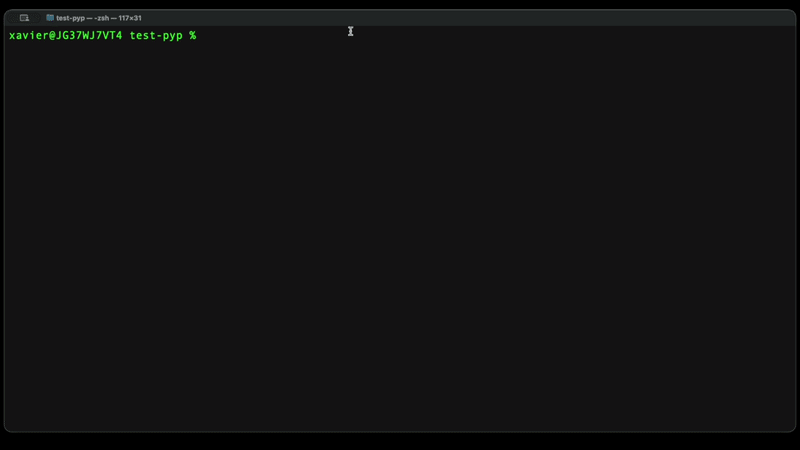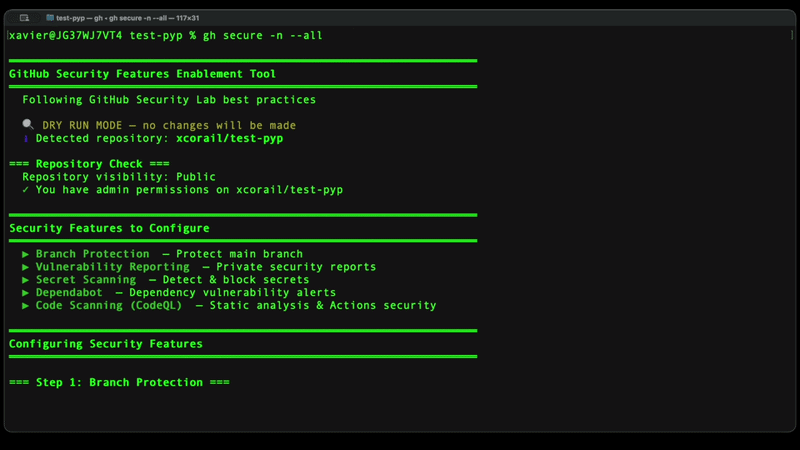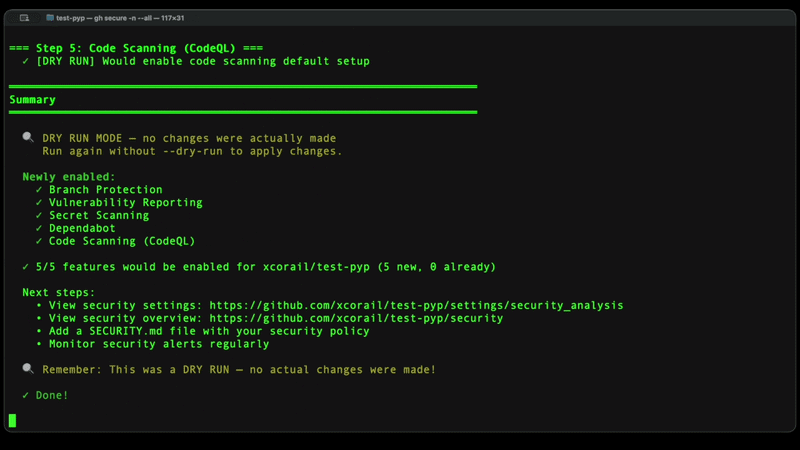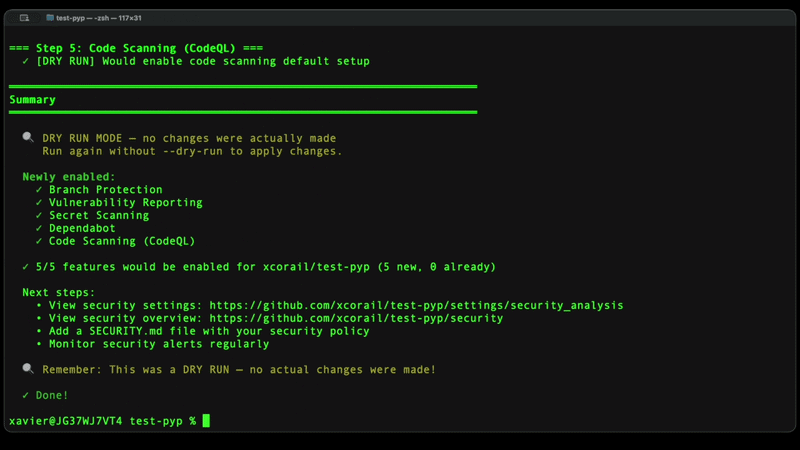
660GitHubSecurityLab/gh-secure · Shellgh-secure is a GitHub CLI extension that turns on five recommended security features on a repository — branch protection, private vulnerability reporting, secret scanning, Dependabot, and code scanning — in about 2 minutes.
- 14

bug-bounty-hunting-prompts
621mdpsec/bug-bounty-hunting-promptsA pack of reusable prompt files for running a structured, evidence-first bug bounty hunting workflow with an LLM agent, covering recon through triage and escalation.
- 15
scuttle
521Continuum-AI-Corp/scuttle · GoScuttle is an open-source Go library that encrypts sensitive fields in application logs before they ever reach storage, so copies that survive in databases, replicas, snapshots and backups stay unreadable even if the datastore is later compromised.
- 16
0
5130sec-labs/0 · TypeScript0 is an open-source, self-evolving, multi-model AI harness for security research that finds, verifies, and fixes vulnerabilities, built by the Swiss Applied AI & Cybersecurity Research Lab.
- 17
cynative
223cynative/cynative · GoCynative is an open-source AI agent framework that gives LLMs live, read-only access to your AWS, Azure, GCP, Kubernetes, GitHub and GitLab infrastructure so you can ask security questions and run cloud security posture and detection checks.
- 18

Myrqen
137stijnswapped/Myrqen · TypeScriptMyrqen is a security testing tool that runs inside a coding agent (Claude Code, Codex, or OpenCode) you already use: its own static analysis engine finds vulnerability candidates in your TypeScript/JavaScript code, then the agent dynamically verifies them against the app running on your machine.
Related topics
Often tagged together
- security977
- cybersecurity244
- security-tools281
- open-source5,666
- linux4,181
- devsecops38
- windows3,401
- macos3,544
- penetration-testing125
- ai-security44
- cli2,227
- developer-tools2,927
- llm1,483
- mit3,311
- terminal1,100
- web-security30
- pentesting112
- vulnerability49
- apache-2.01,434
- docker1,657
- red-team78
- self-hosted1,926
- vulnerability-scanner44
- agent820