Topics / #infosec
Infosec projects on GitHub
Information security broadly: hardening guides, OSINT, and defense.
As of , the most-starred Infosec projects on GitHub are Awesome-Hacking (122.8K stars), sherlock (94.3K stars) and ghidra (89.8K stars). GitHub.Locker tracks 47 Infosec repositories with 904.7K stars combined. The fastest-growing on October 16 was ghidra, with +757 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
 +757
ghidra
NationalSecurityAgency/ghidra · ★ 89.8KGhidra is a software reverse engineering (SRE) framework created and maintained by the NSA's Research Directorate, used to disassemble, decompile, graph, and analyze compiled code.
 +104
Awesome-Hacking
Hack-with-Github/Awesome-Hacking · ★ 122.8KA massive index that links out to dozens of other awesome-lists covering nearly every security domain: android security, bug bounty, fuzzing, malware analysis, OSINT, reverse engineering, web hacking, and more.
 +93
sherlock
sherlock-project/sherlock · ★ 94.3KSherlock hunts down social media accounts by username: give it a name and it checks across social networks for accounts registered under it.
 +71
Anthropic-Cybersecurity-Skills
mukul975/Anthropic-Cybersecurity-Skills · ★ 34.6KAn open-source library of 818 production-grade cybersecurity skills for AI agents, covering 34 security domains and mapped to six frameworks including MITRE ATT&CK and NIST CSF 2.0.
The all-time top
47 projects · by stars
- 122.8K#1 · Hack-with-Github/Awesome-Hacking
Awesome-Hacking
A massive index that links out to dozens of other awesome-lists covering nearly every security domain: android security, bug bounty, fuzzing, malware analysis, OSINT, reverse engineering, web hacking, and more.
- 94.3K#2 · sherlock-project/sherlock
sherlock
Sherlock hunts down social media accounts by username: give it a name and it checks across social networks for accounts registered under it.
- 89.8K#3 · NationalSecurityAgency/ghidra
ghidra
Ghidra is a software reverse engineering (SRE) framework created and maintained by the NSA's Research Directorate, used to disassemble, decompile, graph, and analyze compiled code.
- 4
PayloadsAllTheThings
81.8Kswisskyrepo/PayloadsAllTheThings · PythonA massive curated collection of payloads, bypass techniques, and exploitation methodology for web application security testing, pentesting, and CTF challenges.
- 5

metasploit-framework
39.2Krapid7/metasploit-framework · RubyMetasploit Framework is an open-source penetration testing framework written in Ruby — one of the best-known security toolkits on GitHub, with about 39,000 stars.
- 6
maigret
39.2Ksoxoj/maigret · PythonMaigret is an OSINT command-line tool that builds a dossier on a person by checking for an account under a given username across thousands of websites and pulling together whatever profile info it finds, with no API keys required.
- 7
Anthropic-Cybersecurity-Skills
34.6Kmukul975/Anthropic-Cybersecurity-Skills · PythonAn open-source library of 818 production-grade cybersecurity skills for AI agents, covering 34 security domains and mapped to six frameworks including MITRE ATT&CK and NIST CSF 2.0.
- 8
awesome-osint
30.3Kjivoi/awesome-osintThis is a curated 'awesome list' of hundreds of free and paid OSINT (open source intelligence) tools and resources, organized into categories like general search, Google dorks, data breach lookup, social media, threat actors, and dark web.
- 9

masscan
26.1Krobertdavidgraham/masscan · CMasscan is an Internet-scale TCP port scanner that transmits SYN packets asynchronously and can scan the entire IPv4 Internet in under 5 minutes, sending up to 10 million packets per second from a single machine.
- 10
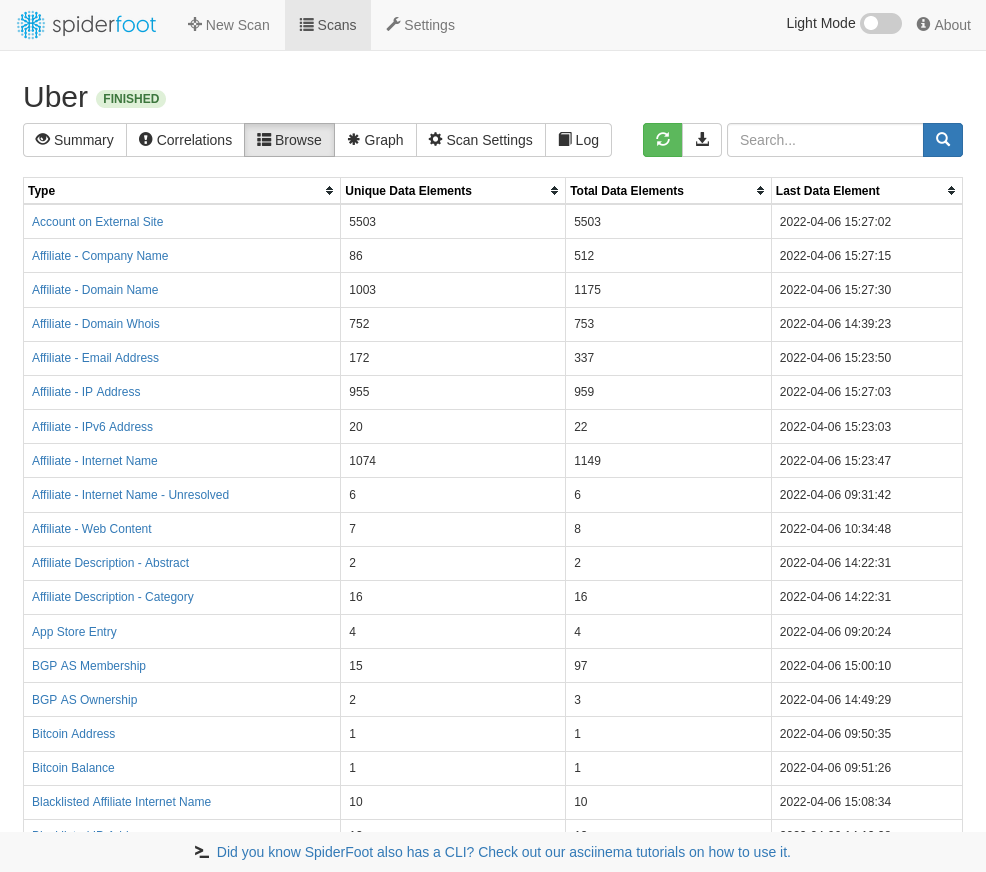
spiderfoot
23.5Ksmicallef/spiderfoot · PythonOpen source OSINT automation — it collects intelligence on a target for threat intel and attack surface mapping, whether you are doing red team recon or checking what your organisation has exposed.
- 11

macOS-Security-and-Privacy-Guide
22.6Kdrduh/macOS-Security-and-Privacy-Guide · ShellA community-maintained guide collecting techniques for improving security and privacy on macOS, written for Apple silicon Macs.
- 12

PEASS-ng
20.7Kpeass-ng/PEASS-ng · C#PEASS-ng is a suite of local privilege escalation enumeration tools: LinPEAS for Linux/Unix/macOS and WinPEAS for Windows. They scan a machine for privesc paths and print misconfigurations with nice colors so you can spot them easily.
- 13

theHarvester
18Klaramies/theHarvester · PythonAn open-source OSINT tool that gathers emails, subdomains and names about a domain or organization from public sources: search engines, certificate transparency logs, DNS datasets, code repositories and threat-intel platforms, normalizing hostnames, emails, IPs, URLs, ASNs, people and breach names.
- 14
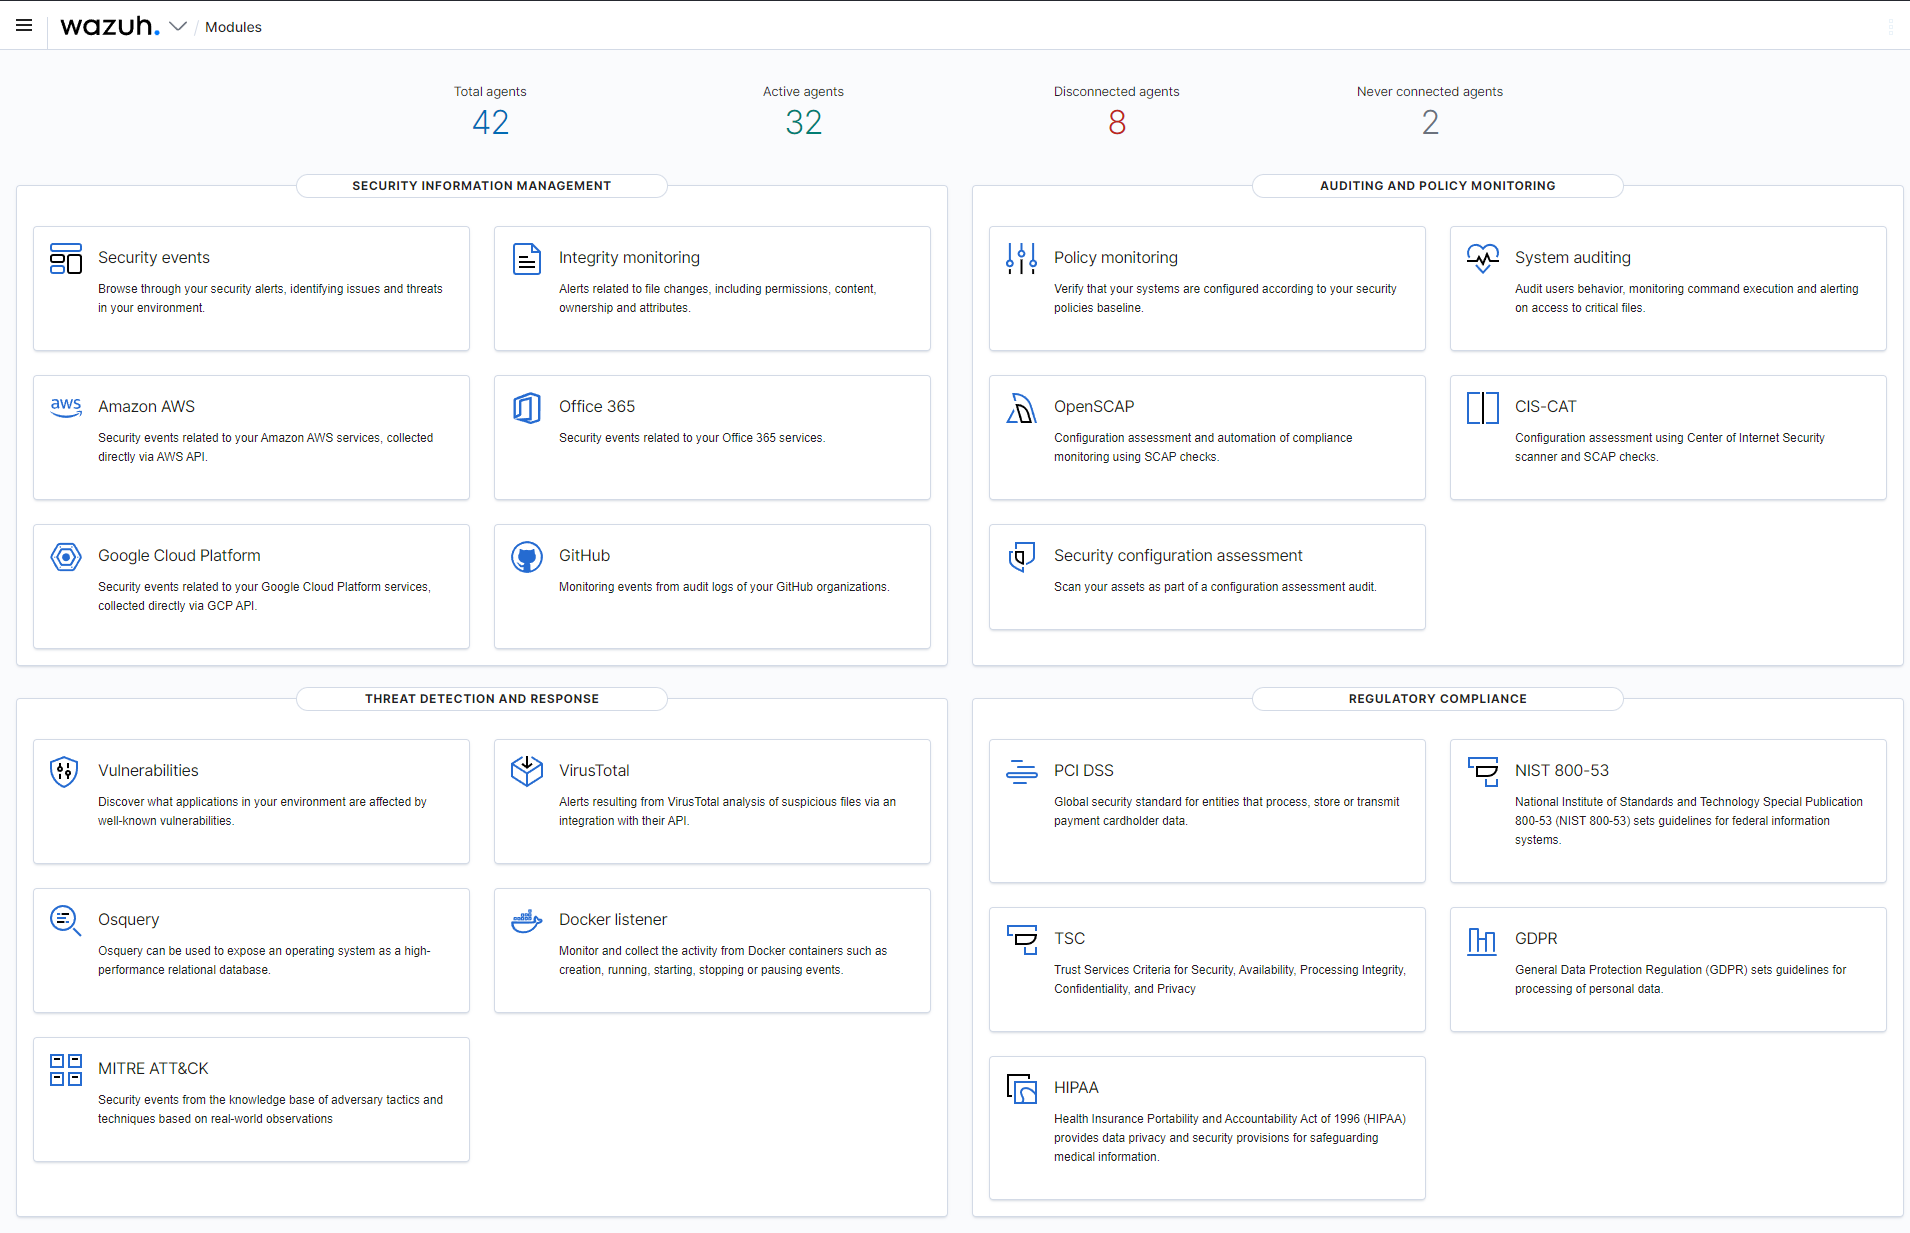
wazuh
17.3Kwazuh/wazuh · C++Wazuh is a free, open source security platform (XDR and SIEM) for threat prevention, detection and response across on-premises, virtualized, containerized and cloud workloads.
- 15
ffuf
16.9Kffuf/ffuf · Goffuf is a fast web fuzzer written in Go — a command-line tool that sends many crafted requests to a target to discover directories, virtual hosts, and fuzzable GET/POST parameters.
- 16

hacker-roadmap
15.7Ksundowndev/hacker-roadmapThis is a curated roadmap and toolkit index for learning and practicing ethical hacking: it explains what penetration testing is and groups hundreds of security tools, wordlists and references by category (recon, password attacks, wireless, exploitation, web hacking, post-exploitation, frameworks).
- 17

dirsearch
15Kmaurosoria/dirsearch · PythonDirsearch is an advanced command-line web path brute-forcer used to discover hidden files and directories on websites for security testing.
- 18
awesome-malware-analysis
14.3Krshipp/awesome-malware-analysisA curated 'awesome list' of malware analysis tools and resources, covering sample collection, sandboxes, detection tools, threat intelligence feeds, reverse engineering, and forensics.
- 19

PENTESTING-BIBLE
14KblaCCkHatHacEEkr/PENTESTING-BIBLEA curated catalog of over 200 numbered links to pentesting articles, bug bounty write-ups, cheat sheets and other security lists — a reading collection, not software.
- 20

DVWA
13.9Kdigininja/DVWA · PHPDVWA (Damn Vulnerable Web Application) is a PHP/MariaDB web app that is deliberately full of security bugs, built as a legal practice target for security pros, students, and developers to learn web application security.
- 21
theZoo
13.5Kytisf/theZoo · PythontheZoo is a public repository of live malware samples and their source code, gathered so that anyone interested in malware analysis can study real specimens in an organized and accessible way.
- 22

routersploit
13.3Kthreat9/routersploit · PythonRouterSploit is an open-source exploitation framework built specifically for testing the security of embedded devices like routers.
- 23
hetty
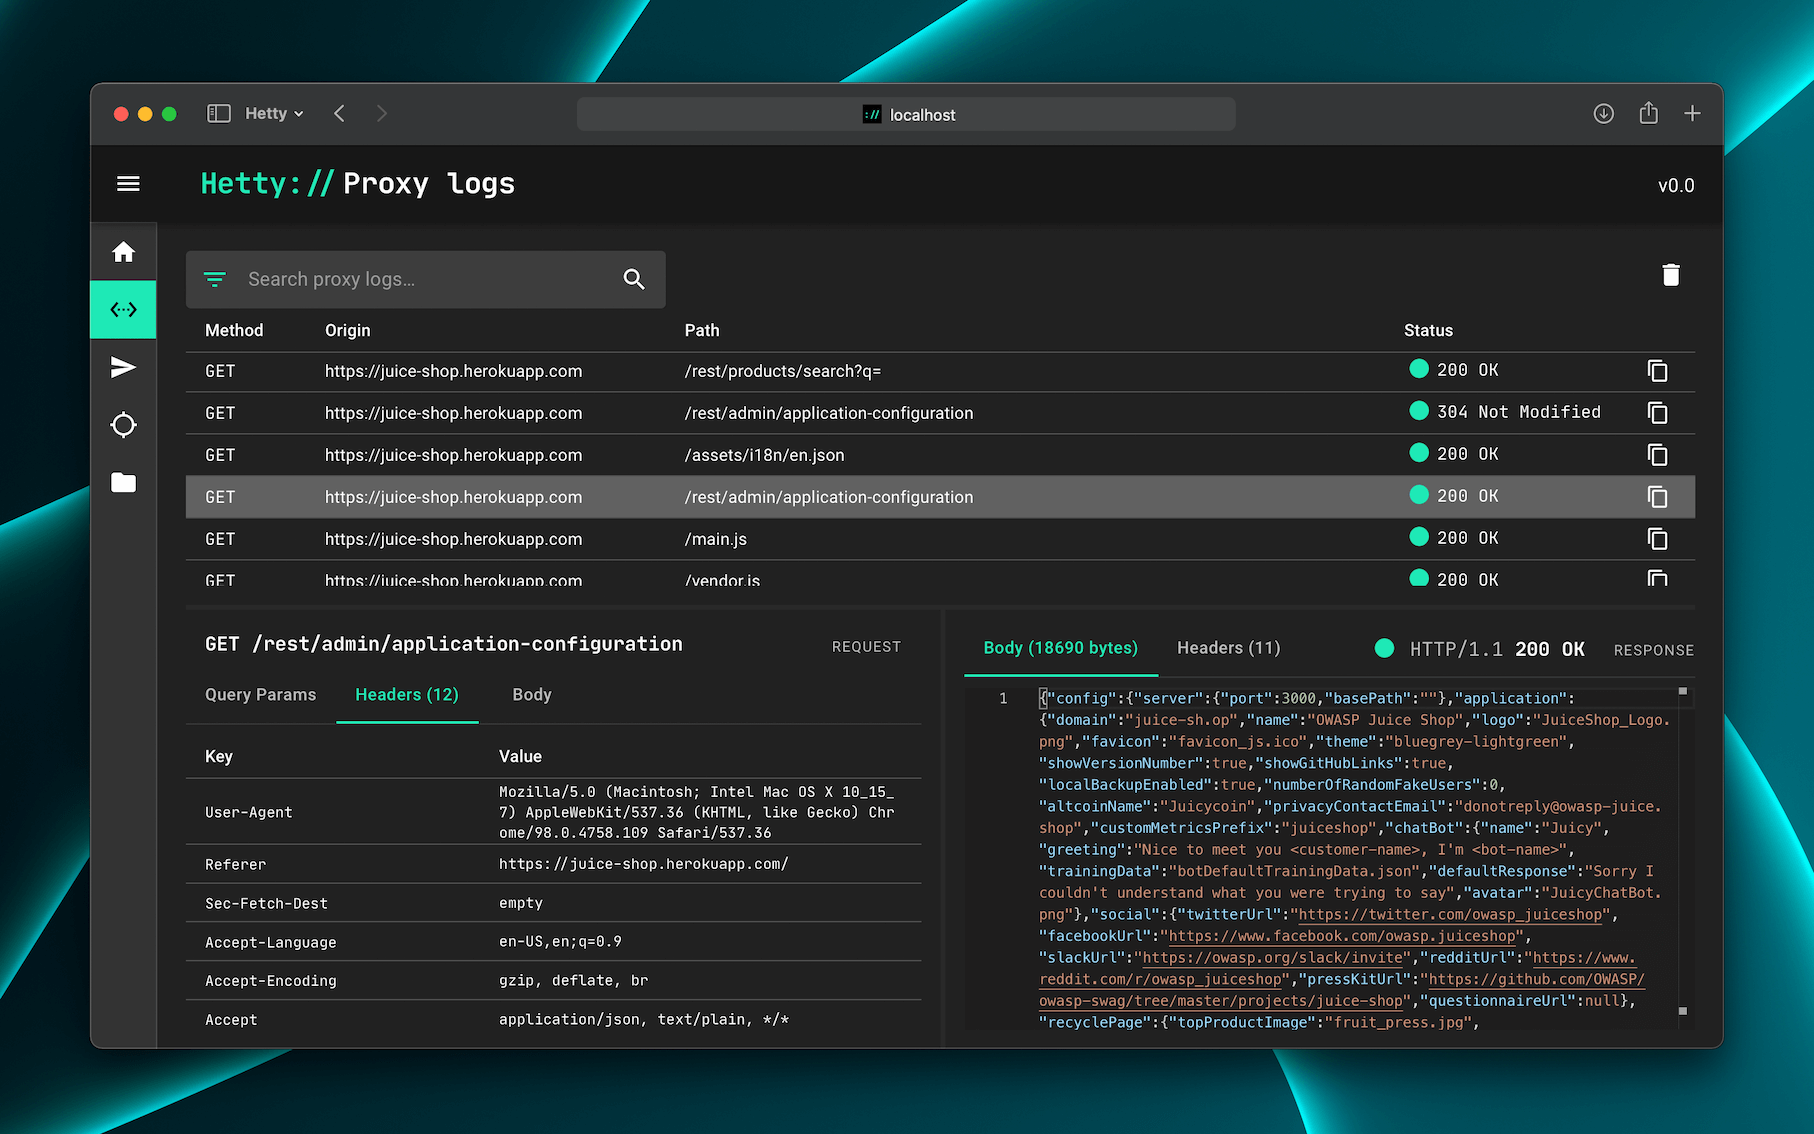
12.5Kdstotijn/hetty · GoHetty is an HTTP toolkit for security research, aiming to be an open source alternative to commercial tools like Burp Suite Pro, aimed at the infosec and bug bounty community.
- 24
sigma
11.3KSigmaHQ/sigma · PythonSigma is a generic, open signature format for describing detection patterns in log events, and this repository is the main collection of over 3000 community-written Sigma detection rules for SIEM systems.
- 25

Red-Teaming-Toolkit
10.8Kinfosecn1nja/Red-Teaming-ToolkitIt is a curated list of cutting-edge open-source security tools for red teamers and threat hunters, covering the full attack lifecycle from reconnaissance to exfiltration.
- 26

awesome-threat-intelligence
10.7Khslatman/awesome-threat-intelligenceA curated catalog of threat intelligence resources — feeds, tools, frameworks, standards and research for tracking online threats. It is a pointer list on GitHub, not software you install.
- 27
reverse-engineering
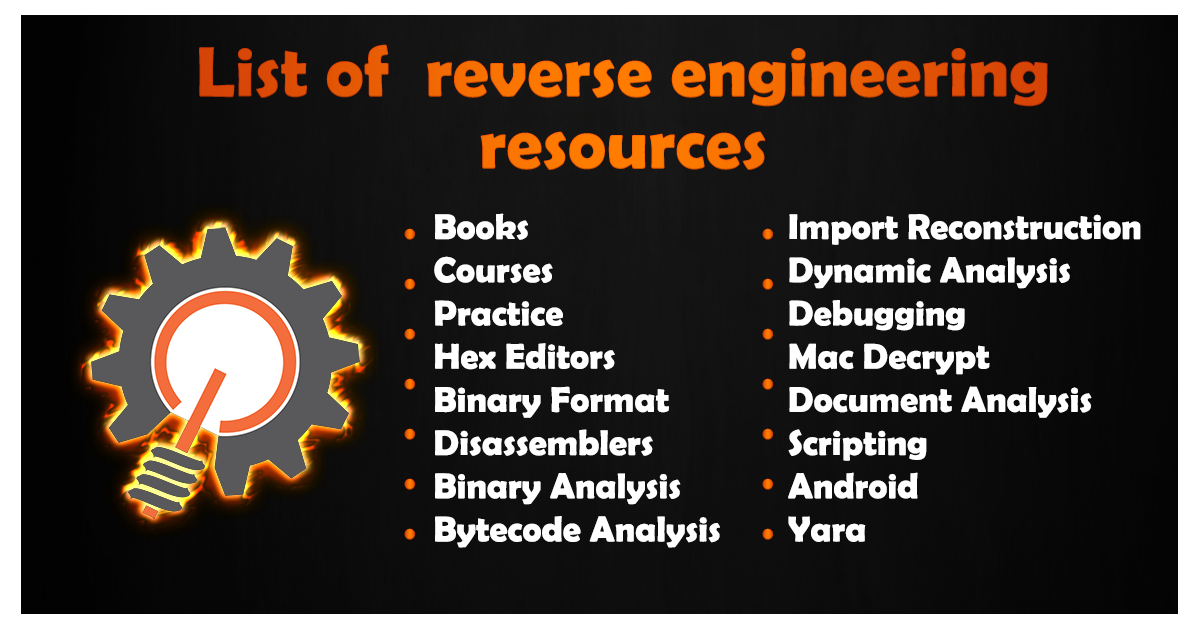
10.6KwtsxDev/reverse-engineeringA curated list of reverse engineering resources: books, courses, practice grounds, and a big toolbox section spanning hex editors, disassemblers, debuggers, and dynamic analysis tools.
- 28
httpx
10.5Kprojectdiscovery/httpx · Gohttpx is a fast, multi-purpose HTTP toolkit from ProjectDiscovery that runs many probes against lists of hosts and URLs, built on the retryablehttp library to stay reliable under high thread counts.
- 29
how-to-secure-anything
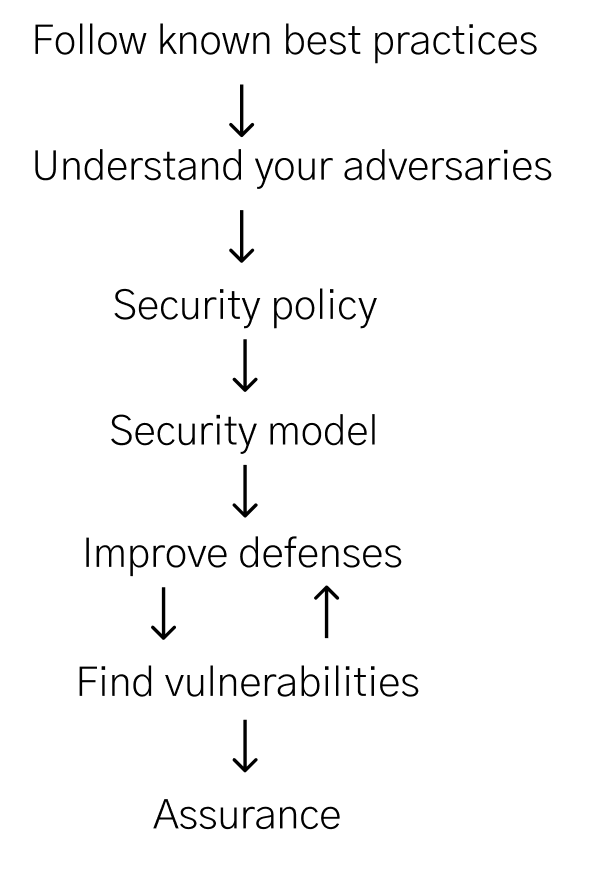
10.2Kveeral-patel/how-to-secure-anythingA curated README that documents a systematic process for security engineering: how to secure any kind of system, whether it is a medieval castle, an art museum, or a computer network, by thinking about adversaries, policies, models, and defenses.
- 30

nishang
10.2Ksamratashok/nishang · PowerShellNishang is a framework and large collection of PowerShell scripts and payloads for offensive security, penetration testing, and red teaming, covering every phase of an engagement.
- 31

Claude-Red
7.6KSnailSploit/Claude-Red · Pythonclaude-red is a curated library of offensive security skills for the Claude Skills system: structured SKILL.md files that prime Claude with expert-level methodology for one attack surface each, from SQLi to shellcode.
- 32
ProxyBridge
6.8KInterceptSuite/ProxyBridge · CProxyBridge is a cross-platform proxy client that transparently redirects TCP and UDP traffic from specific Windows/macOS/Linux applications through SOCKS5 or HTTP proxies, acting as an open-source alternative to Proxifier.
- 33
user-scanner
5.4Kkaifcodec/user-scanner · PythonUser Scanner is an OSINT (open-source intelligence) CLI tool that takes an email address or username and scans it across 2720+ platforms (210+ email vectors, 2510+ username vectors) to map digital footprints, scrape profile metadata, and surface linked accounts.
- 34

exploitarium
5.2Kbikini/exploitarium · PythonExploitarium is a single consolidated archive of the author's public proof-of-concept exploits and vulnerability research writeups, merging dozens of their former standalone PoC repos into one place.
- 35
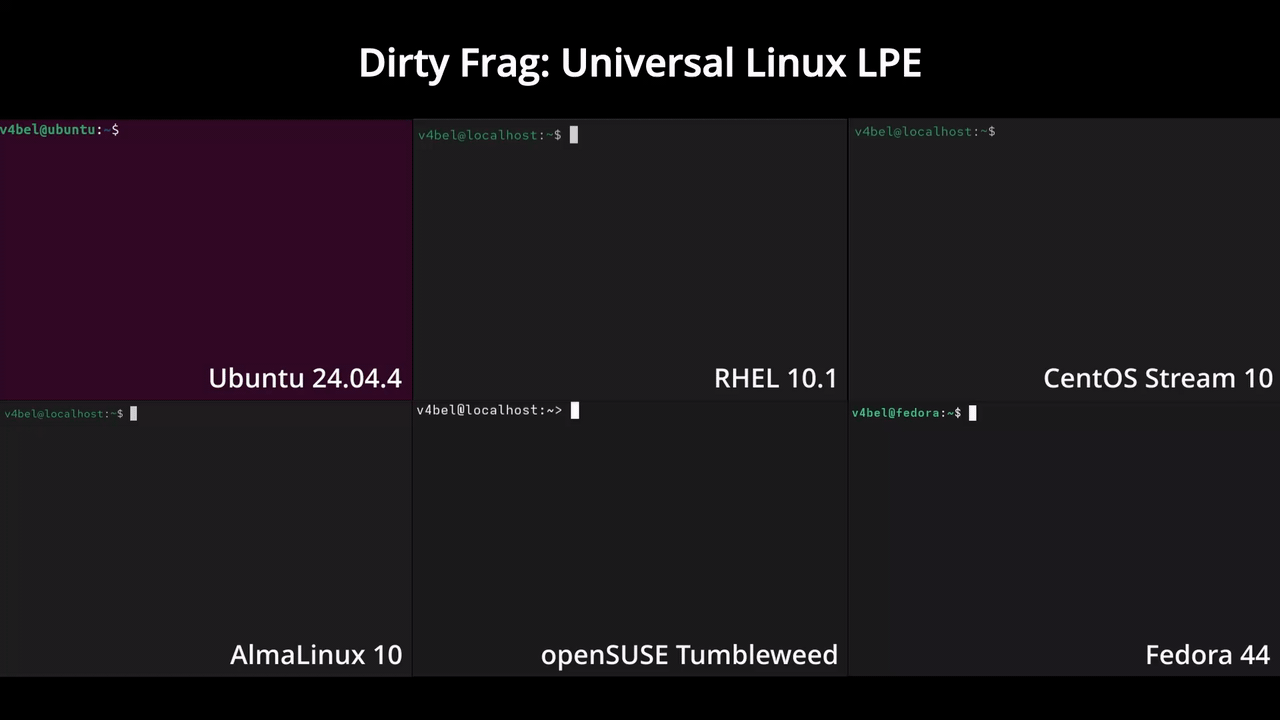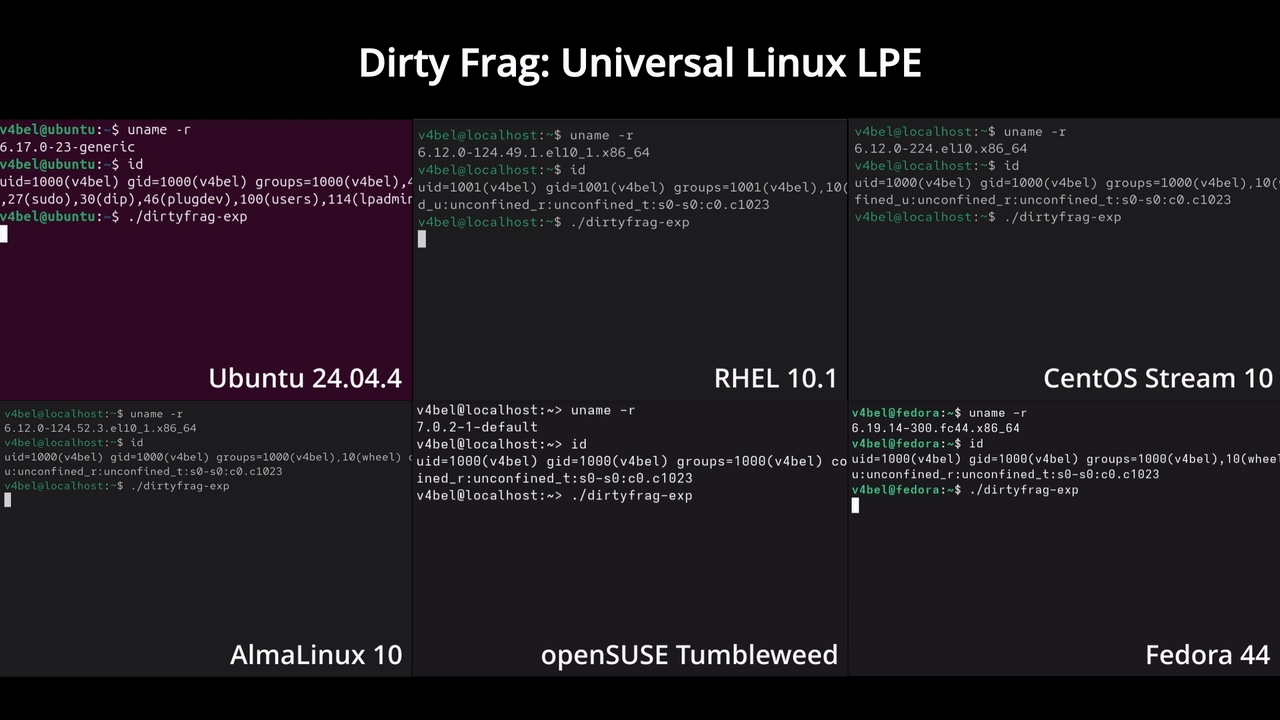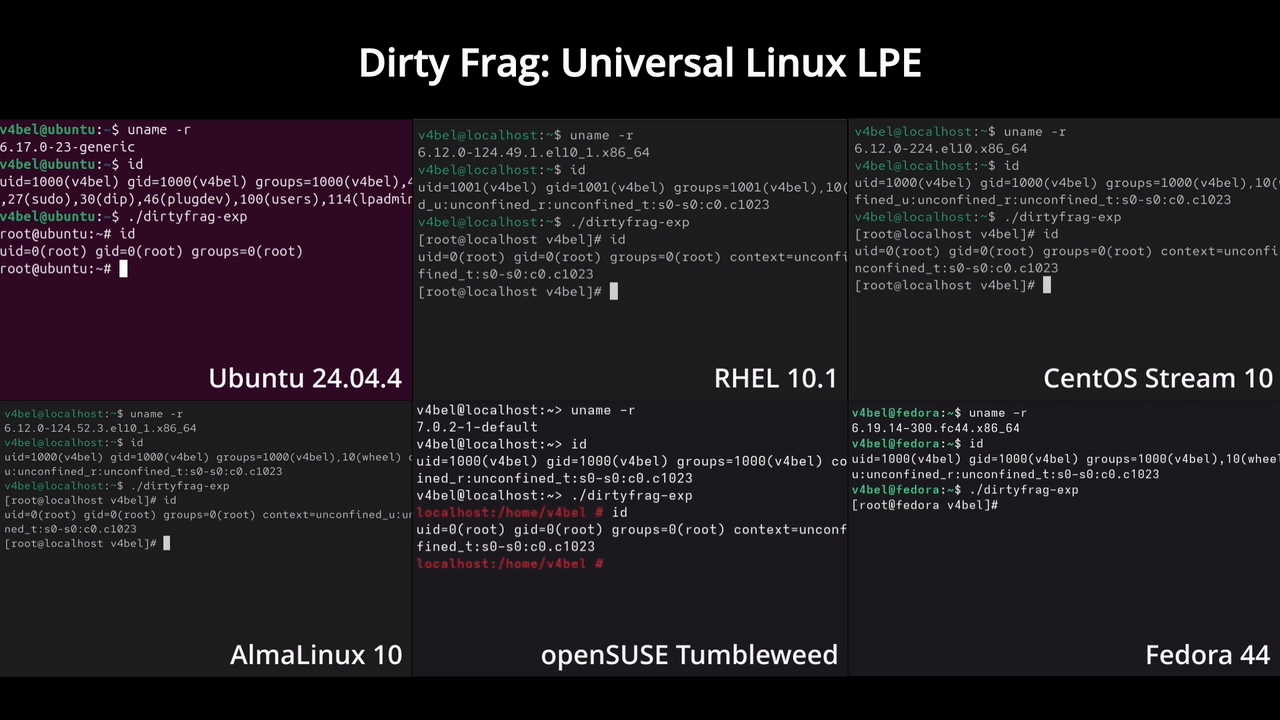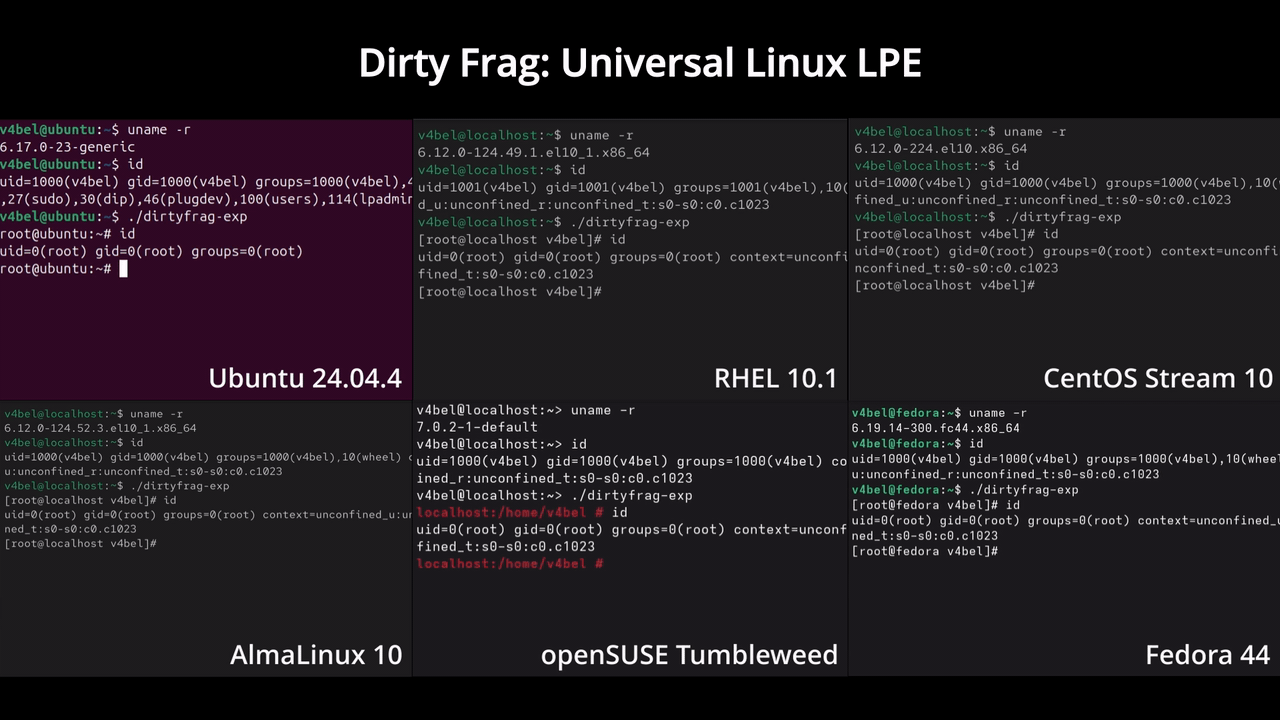
dirtyfrag
5.1KV4bel/dirtyfrag · CDirty Frag is a proof-of-concept Linux kernel local privilege escalation exploit that chains two page-cache write vulnerabilities (CVE-2026-43284 and CVE-2026-43500) to obtain root on major Linux distributions.
- 36

copy-fail-CVE-2026-31431
4.1Ktheori-io/copy-fail-CVE-2026-31431 · PythonThis repository is a technical writeup and proof-of-concept for CVE-2026-31431, a 9-year-old Linux kernel local privilege escalation (LPE) vulnerability found by Theori's AI vulnerability research tool, Xint Code.
- 37
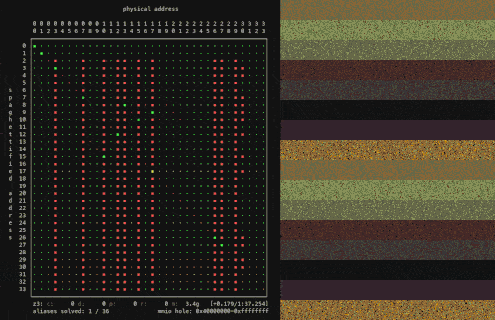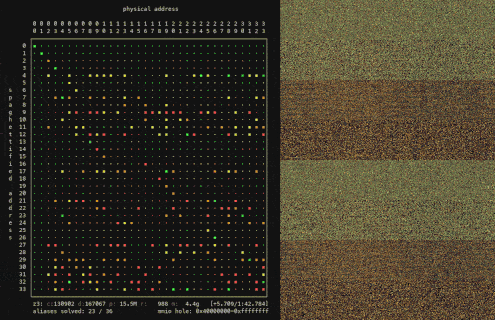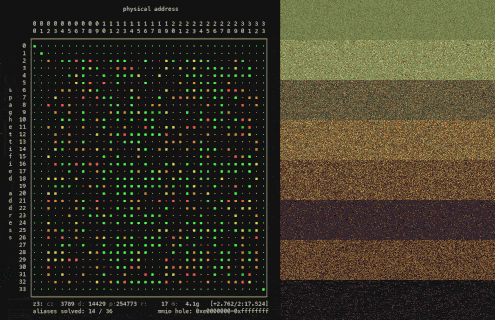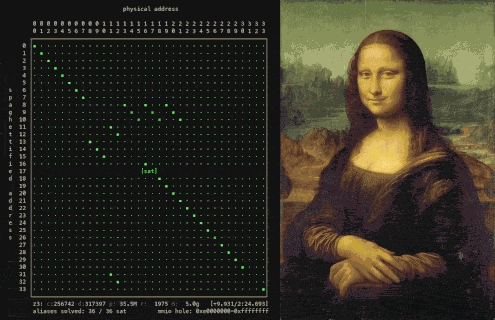
skitter-creek-bath-salts
2.1Kxoreaxeaxeax/skitter-creek-bath-salts · CA security research project that shows how to unlock protected regions on an AMD CPU — the Platform Security Processor, System Management Mode, C6 DRAM, and CPU microcode — by scrambling the DRAM controller's physical-to-DRAM address translation.
- 38
PwnPad
1.2Ktwelvesec/PwnPad · C++PwnPad is an affordable DIY hardware hacking platform that teaches embedded security through 15 hands-on challenges, covering everything from PCB assembly to side-channel and fault-injection attacks.
- 39
Cybermes
946Zyrexnn/Cybermes · PythonCybermes is an offensive security assistant and automation framework for authorized bug bounty hunting, reconnaissance, vulnerability research, and structured reporting, driven by AI agents and a library of 200+ playbooks.
- 40
gh-secure
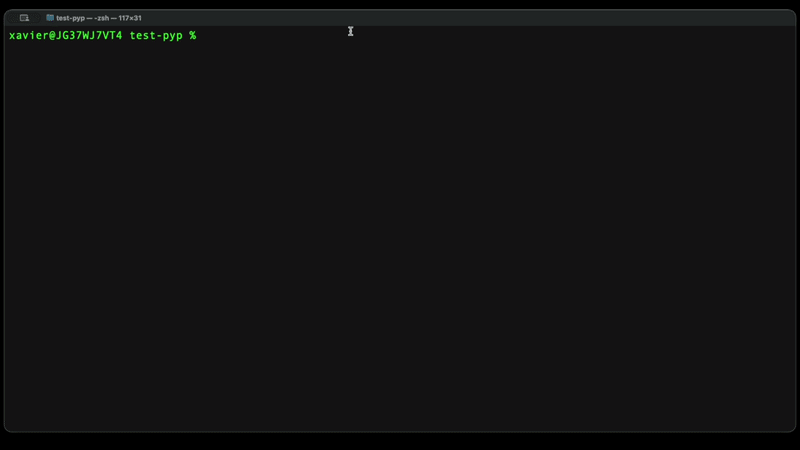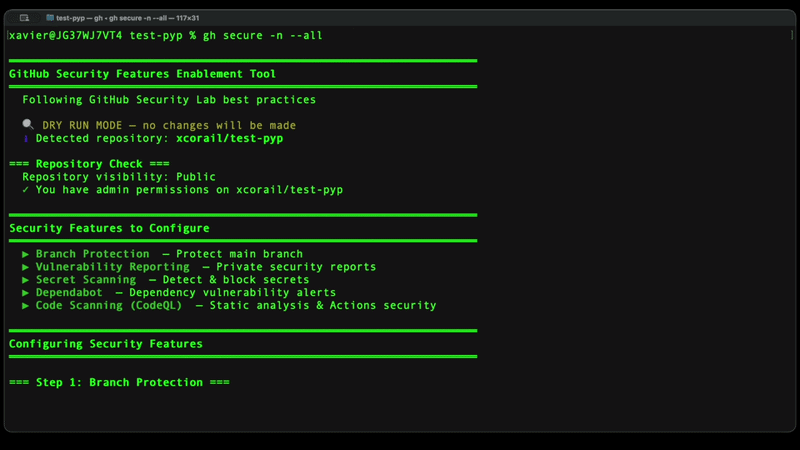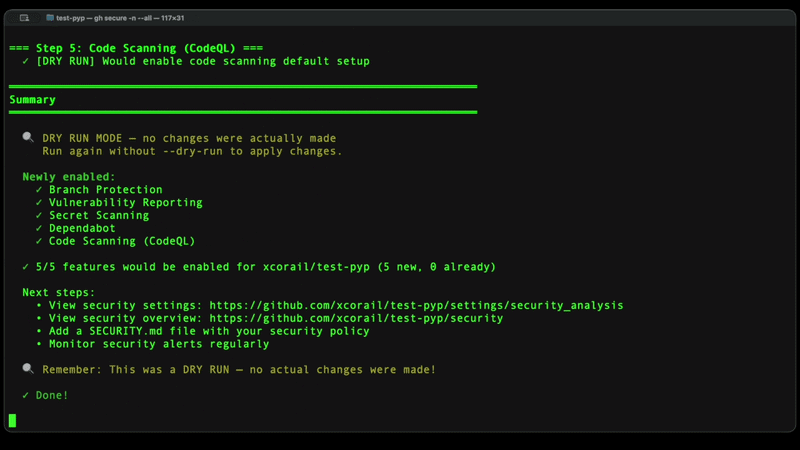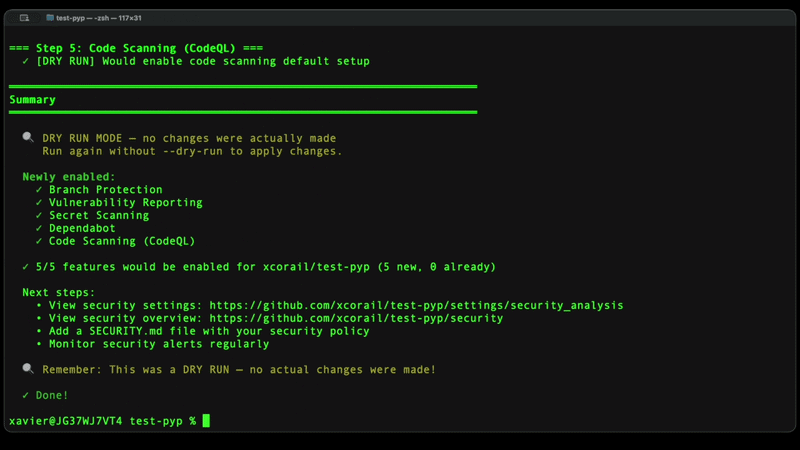
653GitHubSecurityLab/gh-secure · Shellgh-secure is a GitHub CLI extension that turns on five recommended security features on a repository — branch protection, private vulnerability reporting, secret scanning, Dependabot, and code scanning — in about 2 minutes.
- 41

Stuxnet
588Sadpainy/Stuxnet · CThis is a reconstructed source code of Stuxnet, the famous 2010 worm that sabotaged Siemens industrial control systems, rebuilt by the author from reverse-engineering research for educational and malware-analysis purposes.
- 42
scuttle
521Continuum-AI-Corp/scuttle · GoScuttle is an open-source Go library that encrypts sensitive fields in application logs before they ever reach storage, so copies that survive in databases, replicas, snapshots and backups stay unreadable even if the datastore is later compromised.
- 43
pentest-harness
422S1N6H/pentest-harness · TypeScriptA self-hosted AI agent harness for authorized penetration tests, bug bounty research, security labs, and CTF engagements, where you bring your own AI model API key.
- 44

LEAKSFORUMS
364FSECDEV/LEAKSFORUMSLEAKSFORUMS is a collection of leaked data from hacker forums — a README table listing breached communities like Breached Forums, Black Market Reloaded, and Russian boards, each with a download link.
- 45

bad_query
276forcequitOS/bad_query · Cbadquery is a proof-of-concept sandbox escape for iOS 26 and 27, written in C — code that demonstrates breaking out of the iOS app sandbox.
- 46

Claude-AD
211ADScanPro/Claude-ADClaude-AD is a Claude Code plugin that gives Claude the methodology for an internal Active Directory penetration test: skills, agents and slash commands covering Kerberoasting, ADCS ESC1-17, DCSync, ACL abuse, NTLM relay and delegation abuse, each with OPSEC and telemetry notes.
- 47

vol-rs
197daffainfo/vol-rs · Rust'vol-rs' is a line-by-line port of the Volatility 3 memory forensics framework from Python to Rust. It reads the same memory images, runs the same plugins with the same options, and prints byte-for-byte identical output, just much faster.
Related topics
Often tagged together
- security976
- cybersecurity245
- security-tools282
- linux4,184
- pentesting113
- macos3,544
- windows3,403
- hacking135
- penetration-testing126
- open-source5,666
- cli2,227
- offensive-security77
- osint68
- python2,383
- terminal1,101
- cross-platform2,623
- reverse-engineering221
- red-team79
- docker1,660
- hacking-tool75
- exploit51
- malware-analysis34
- threat-intelligence22
- awesome-list495