Topics / #vulnerability
Vulnerability projects on GitHub
Vulnerability scanning and security flaw research
As of , the most-starred Vulnerability projects on GitHub are PayloadsAllTheThings (81.8K stars), trivy (38.5K stars) and nuclei (32.1K stars). GitHub.Locker tracks 50 Vulnerability repositories with 497.8K stars combined. The fastest-growing on October 16 was security-audit-skill, with +375 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
 +375
security-audit-skill
cloudflare/security-audit-skill · ★ 30.4KA Cloudflare coding-agent skill that turns your agent into a security auditor: it orchestrates isolated agents through a structured, multi-phase audit and returns independently verified, machine-readable findings.
 +96
Seep-Reverse-Lab
angusdevgo/Seep-Reverse-Lab · ★ 1.6KSeep Reverse Lab is an agent-native reverse engineering and security-audit workbench that lets an AI coding agent autonomously run Radare2, JADX, Apktool and Frida to triage binaries, decompile APKs, and determine whether an app's feature gates are enforced locally or verified by a server (a CWE-602 authorization audit).
 +52
Relapse-Exploit
ntfargo/Relapse-Exploit · ★ 2.3KRelapse Exploit is a browser-based jailbreak chain for the PS5, working on firmware 7.00 through 13.60, that chains a WebKit browser exploit with a kernel exploit to gain kernel read/write and load custom payloads.
 +31
ghostlock-app
YuKongA/ghostlock-app · ★ 2KGhostLock is a one-tap Android app that runs the CVE-2026-43499 kernel exploit to grant uid 0 (root) on a matching vulnerable kernel, optionally loading a KernelSU-style module afterward.
The all-time top
50 projects · by stars
- 81.8K
 #1 · swisskyrepo/PayloadsAllTheThings
PayloadsAllTheThings
A massive curated collection of payloads, bypass techniques, and exploitation methodology for web application security testing, pentesting, and CTF challenges.
- 38.5K
 #2 · aquasecurity/trivy
trivy
Trivy is an all-in-one security scanner that finds vulnerabilities, misconfigurations, secrets, and software licenses across container images, filesystems, git repositories, VM images, and Kubernetes clusters.
- 32.1K
 #3 · projectdiscovery/nuclei
nuclei
A fast, open-source vulnerability scanner that runs YAML-based templates to find security issues in applications, APIs, networks, DNS and cloud configurations. Its checks come from a large global security community.
- 4
security-audit-skill
30.4Kcloudflare/security-audit-skill · JavaScriptA Cloudflare coding-agent skill that turns your agent into a security auditor: it orchestrates isolated agents through a structured, multi-phase audit and returns independently verified, machine-readable findings.
- 5
h4cker
29.8KThe-Art-of-Hacking/h4cker · Jupyter NotebookA curated collection of thousands of cybersecurity resources — references, scripts, tools, code, labs, and training material — maintained by Omar Santos as a companion to his books, video courses, and live training.
- 6
trufflehog
28.5Ktrufflesecurity/trufflehog · GoTruffleHog is a CLI tool that discovers, classifies, validates, and analyzes leaked secrets like API keys, database passwords, and private keys across many sources (Git, GitHub, S3, Docker, Slack, filesystems, and more).
- 7
SafeLine
22.8Kchaitin/SafeLine · GoSafeLine is a self-hosted web application firewall (WAF) and reverse proxy that protects your web apps from attacks and exploits by filtering and monitoring HTTP traffic.
- 8
vulhub
21.4Kvulhub/vulhub · DockerfileVulhub is an open-source collection of pre-built, ready-to-use vulnerable Docker environments: with one command you get a working lab for security research, learning, or demos.
- 9
fscan
14.7Kshadow1ng/fscan · Gofscan is an open-source intranet scanner written in Go: one command runs an all-round internal-network audit — host discovery, port scanning, service identification, weak-password brute force and vulnerability detection.
- 10

hacker101
14.6KHacker0x01/hacker101 · SCSSHacker101 is a free online class for web and mobile security from HackerOne (the Hacker0x01 org), aimed at everyone from programmers curious about bug bounties to seasoned security professionals.
- 11

DVWA
13.9Kdigininja/DVWA · PHPDVWA (Damn Vulnerable Web Application) is a PHP/MariaDB web app that is deliberately full of security bugs, built as a legal practice target for security pros, students, and developers to learn web application security.
- 12

secguide
13.4KTencent/secguideA free, Tencent-maintained secure coding guide for developers that catalogs API-level security risks and gives concrete, actionable secure-coding solutions.
- 13

grype
13Kanchore/grype · GoGrype is a command-line vulnerability scanner that checks container images, filesystems, and SBOMs for known security vulnerabilities.
- 14

hacktricks
12.6KHackTricks-wiki/hacktricks · JavaScriptA free, open wiki of hacking tricks and techniques — everything the author has learnt from CTFs, real-world apps and security research, organized into a browsable reference with 12.5k+ GitHub stars.
- 15
xray
11.8Kchaitin/xray · Vuexray is a security assessment tool built by Chaitin for scanning common web vulnerabilities and running custom PoCs against targets.
- 16

404StarLink
11.4Kknownsec/404StarLink404StarLink is a curated list of security-focused open-source projects maintained by Knownsec 404 Lab, created to showcase, support, and track high-quality, actively-maintained security tools.
- 17
osv-scanner
11.2Kgoogle/osv-scanner · GoOSV-Scanner is Google's open-source command-line vulnerability scanner: it checks your project's dependencies against OSV.dev, an open vulnerability database, and reports which known vulnerabilities affect you.
- 18

awesome-honeypots
10.6Kparalax/awesome-honeypots · PythonA curated, categorized list of honeypot software and related tools used by security researchers to deceive attackers, log their behavior, and study exploitation attempts.
- 19
CyberStrikeAI
7.8KAIPentest/CyberStrikeAI · GoCyberStrikeAI is an AI-native cybersecurity platform that turns natural-language intent into governed, auditable security operations, using agents, 100+ security tools, MCP integration, and attack-chain tracking for authorized penetration testing.
- 20

defending-code-reference-harness
7.6Kanthropics/defending-code-reference-harness · PythonA reference implementation from Anthropic for finding and fixing vulnerabilities with Claude: a set of Claude Code skills (quickstart, threat-model, vuln-scan, triage, patch, customize) plus an autonomous scanning harness that runs a recon-find-verify-report-patch loop, built from learnings partnering with security teams.
- 21

Claude-Red
7.6KSnailSploit/Claude-Red · Pythonclaude-red is a curated library of offensive security skills for the Claude Skills system: structured SKILL.md files that prime Claude with expert-level methodology for one attack surface each, from SQLi to shellcode.
- 22
AI-Infra-Guard
6.9KTencent/AI-Infra-Guard · PythonAI-Infra-Guard (A.I.G) is a full-stack AI red teaming platform built by Tencent Zhuque Lab that scans AI agents, MCP servers, agent skills, and AI infrastructure components for security vulnerabilities, and evaluates LLMs against jailbreak attacks.
- 23

T3MP3ST
6.5Kelder-plinius/T3MP3ST · TypeScriptT3MP3ST is a multi-agent offensive-security framework that turns an AI coding agent you already use into an autonomous red-teaming operator. Point it at an authorized target and it runs the kill chain — recon, exploit, report — from a browser 'War Room' or the CLI.
- 24
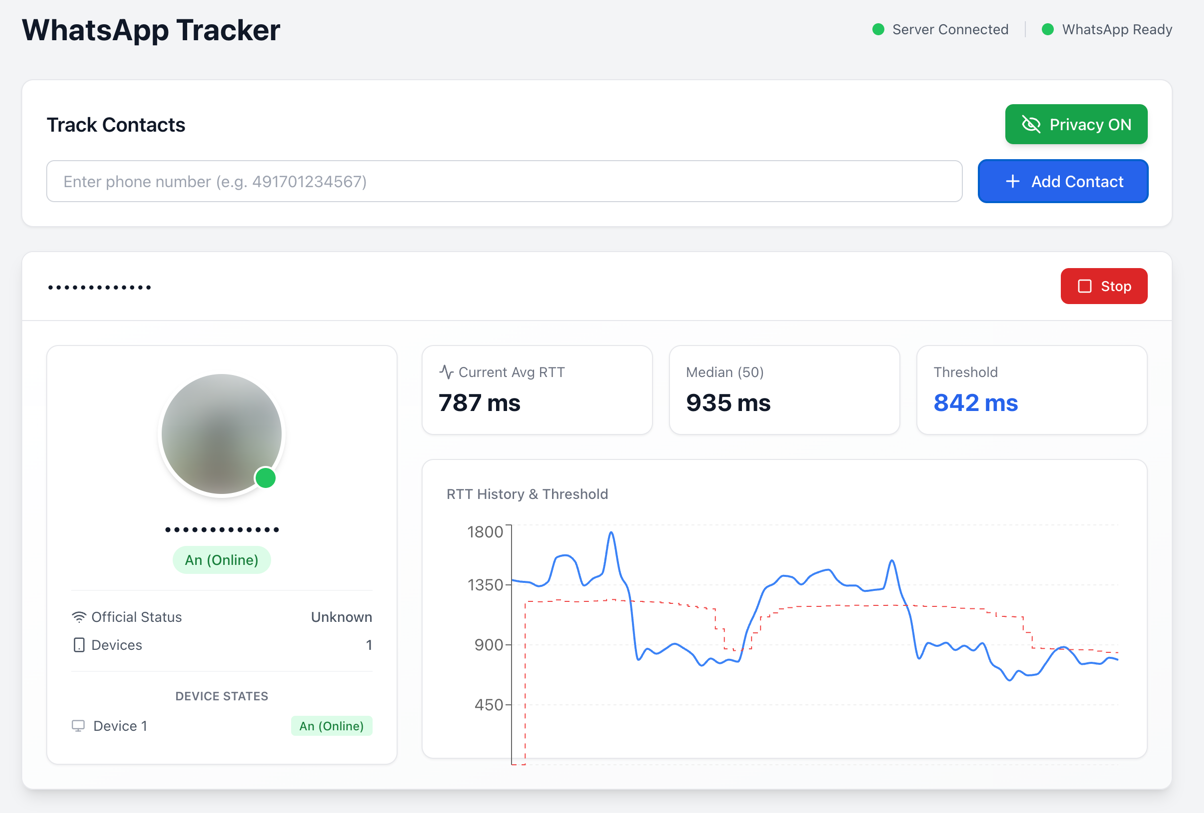
device-activity-tracker
5.2Kgommzystudio/device-activity-tracker · TypeScriptThis is a proof-of-concept security research tool that monitors WhatsApp and Signal users by measuring the Round-Trip Time (RTT) of message delivery receipts, revealing whether a target's device is actively in use, idle, or offline.
- 25

exploitarium
5.2Kbikini/exploitarium · PythonExploitarium is a single consolidated archive of the author's public proof-of-concept exploits and vulnerability research writeups, merging dozens of their former standalone PoC repos into one place.
- 26

Claude-BugHunter
5.1Kelementalsouls/Claude-BugHunter · PythonA drop-in skill bundle for the Claude Code skills system that turns Claude into a bug-hunting researcher or red-team operator: it ships 83 skills, 15 slash commands, and knowledge curated from 681 disclosed HackerOne reports across 24 vulnerability classes, plus enterprise identity and infrastructure attack matrices.
- 27
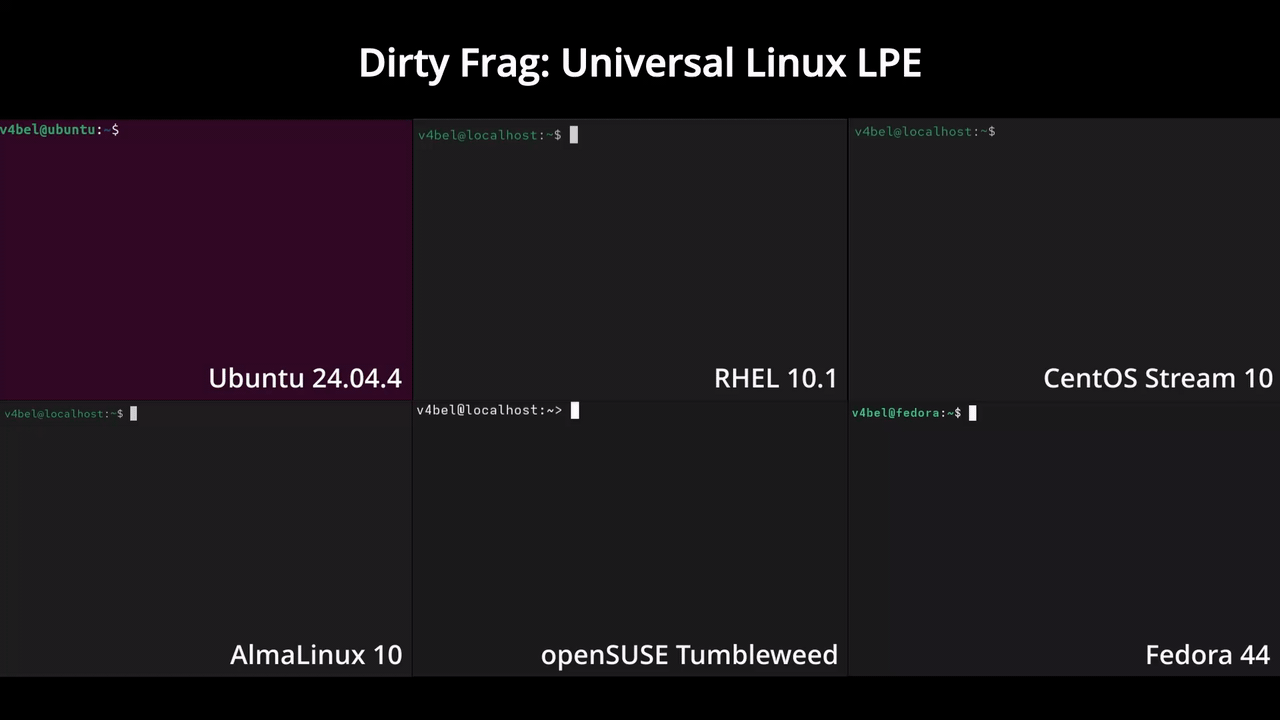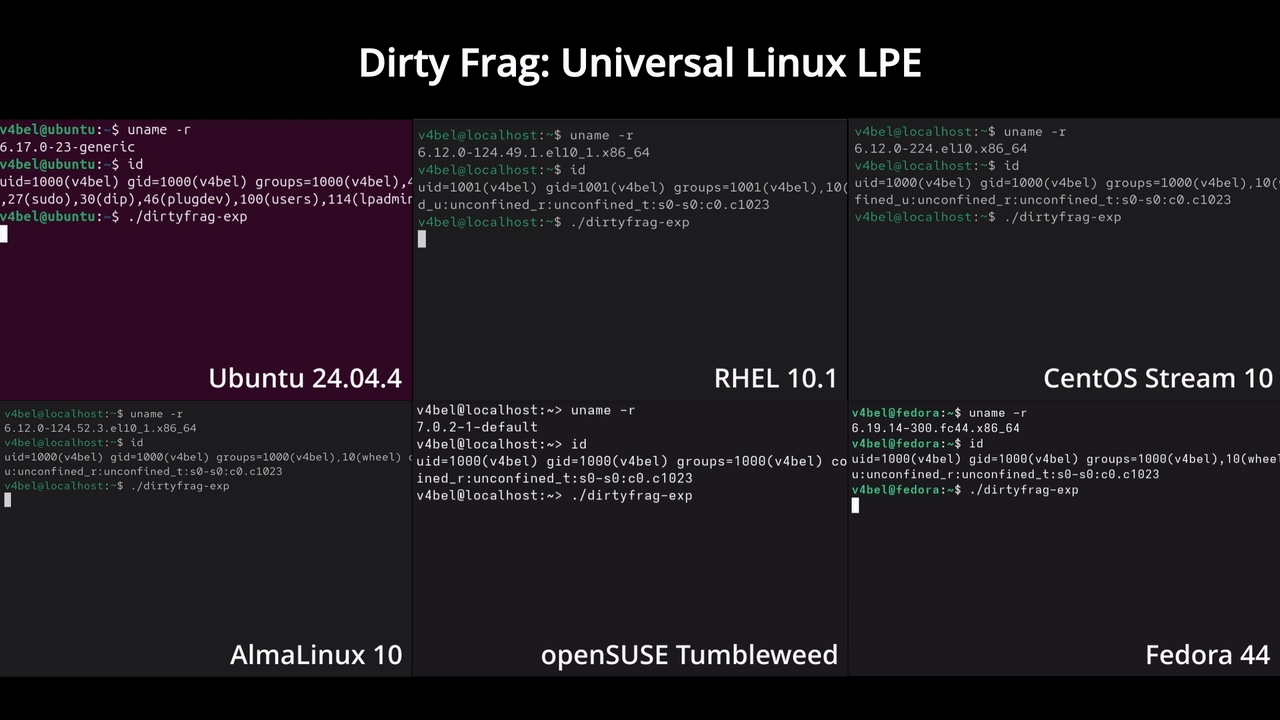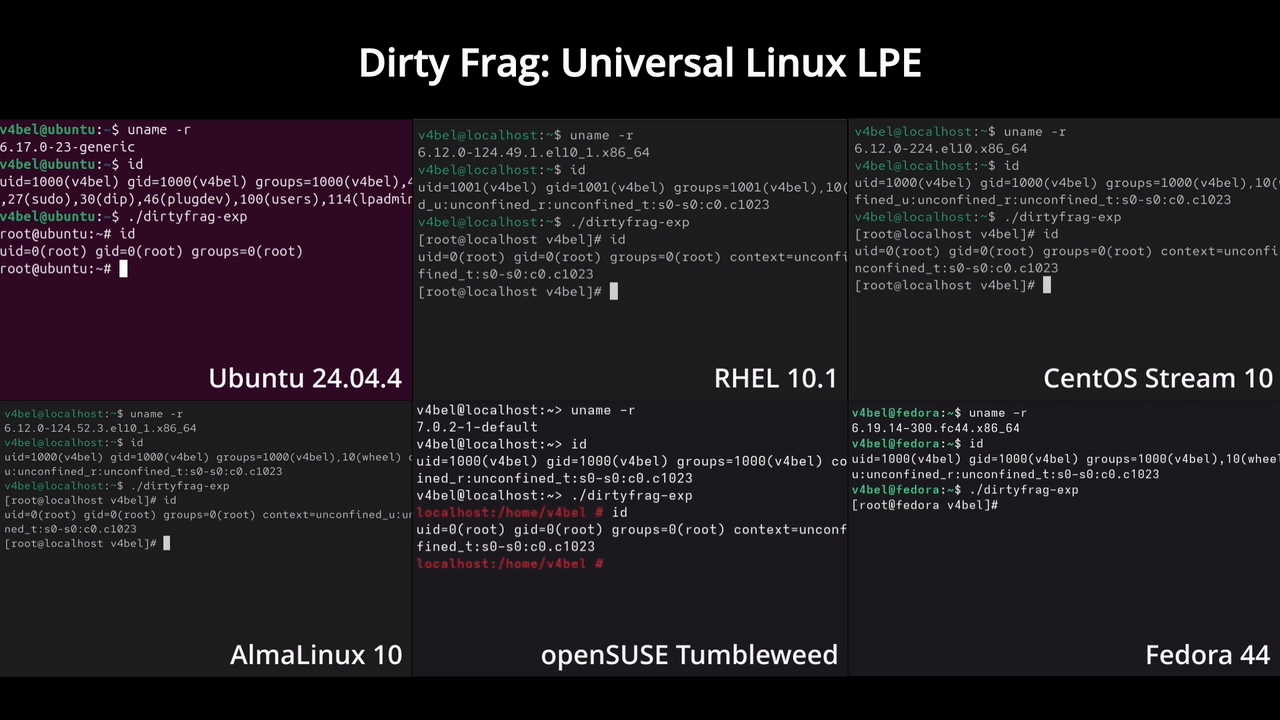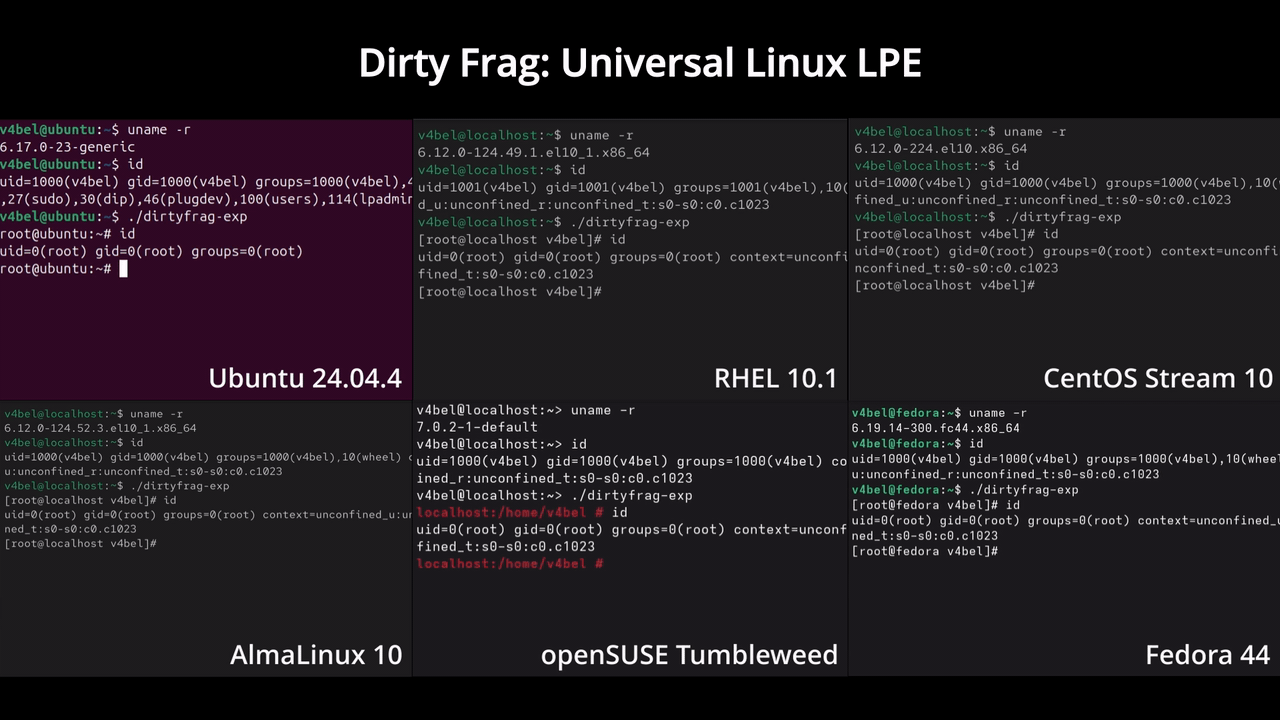
dirtyfrag
5.1KV4bel/dirtyfrag · CDirty Frag is a proof-of-concept Linux kernel local privilege escalation exploit that chains two page-cache write vulnerabilities (CVE-2026-43284 and CVE-2026-43500) to obtain root on major Linux distributions.
- 28

ARTEX
4.4Kmhtsec/ARTEX · GoARTEX is an AI-driven autonomous penetration testing system with a Go backend (embedding a Next.js frontend) where LLM-powered agents plan and execute security testing against assets. It won first place in Baidu's 'Agent+' attack-defense challenge.
- 29
METATRON
4.2Ksooryathejas/METATRON · PythonMetatron is a CLI-based AI penetration testing assistant that runs real recon tools against a target and lets a locally-hosted LLM analyze the results, suggest exploits, and recommend fixes, with no cloud or API keys involved.
- 30

copy-fail-CVE-2026-31431
4.1Ktheori-io/copy-fail-CVE-2026-31431 · PythonThis repository is a technical writeup and proof-of-concept for CVE-2026-31431, a 9-year-old Linux kernel local privilege escalation (LPE) vulnerability found by Theori's AI vulnerability research tool, Xint Code.
- 31
Relapse-Exploit
2.3Kntfargo/Relapse-Exploit · JavaScriptRelapse Exploit is a browser-based jailbreak chain for the PS5, working on firmware 7.00 through 13.60, that chains a WebKit browser exploit with a kernel exploit to gain kernel read/write and load custom payloads.
- 32
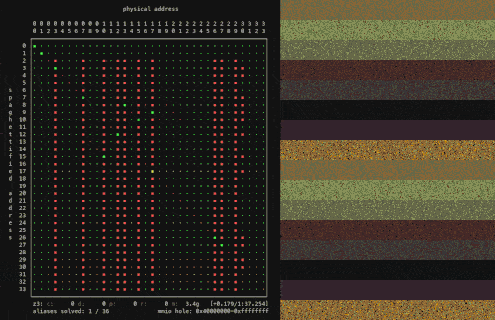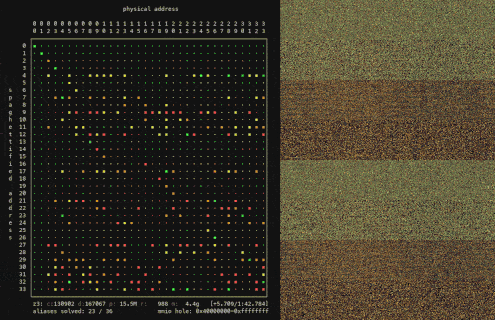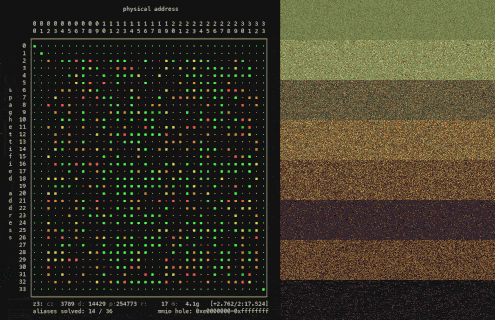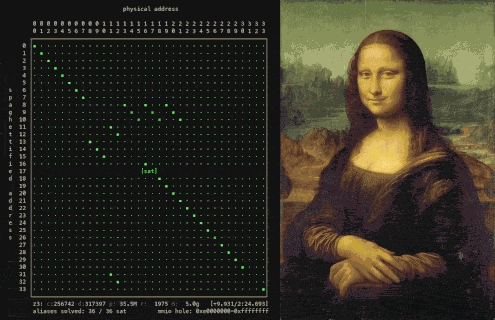
skitter-creek-bath-salts
2.1Kxoreaxeaxeax/skitter-creek-bath-salts · CA security research project that shows how to unlock protected regions on an AMD CPU — the Platform Security Processor, System Management Mode, C6 DRAM, and CPU microcode — by scrambling the DRAM controller's physical-to-DRAM address translation.
- 33
ghostlock-app
2KYuKongA/ghostlock-app · KotlinGhostLock is a one-tap Android app that runs the CVE-2026-43499 kernel exploit to grant uid 0 (root) on a matching vulnerable kernel, optionally loading a KernelSU-style module afterward.
- 34
Seep-Reverse-Lab
1.6Kangusdevgo/Seep-Reverse-Lab · LuaSeep Reverse Lab is an agent-native reverse engineering and security-audit workbench that lets an AI coding agent autonomously run Radare2, JADX, Apktool and Frida to triage binaries, decompile APKs, and determine whether an app's feature gates are enforced locally or verified by a server (a CWE-602 authorization audit).
- 35
oss-scanner
1Kanthropics/oss-scanner · DockerfileOSS Scanner is a service run by Anthropic that scans enrolled open-source repositories for security vulnerabilities, building each project in an isolated VM and emailing the maintainer a reproducer plus a proposed patch for anything it finds.
- 36
ARTEX
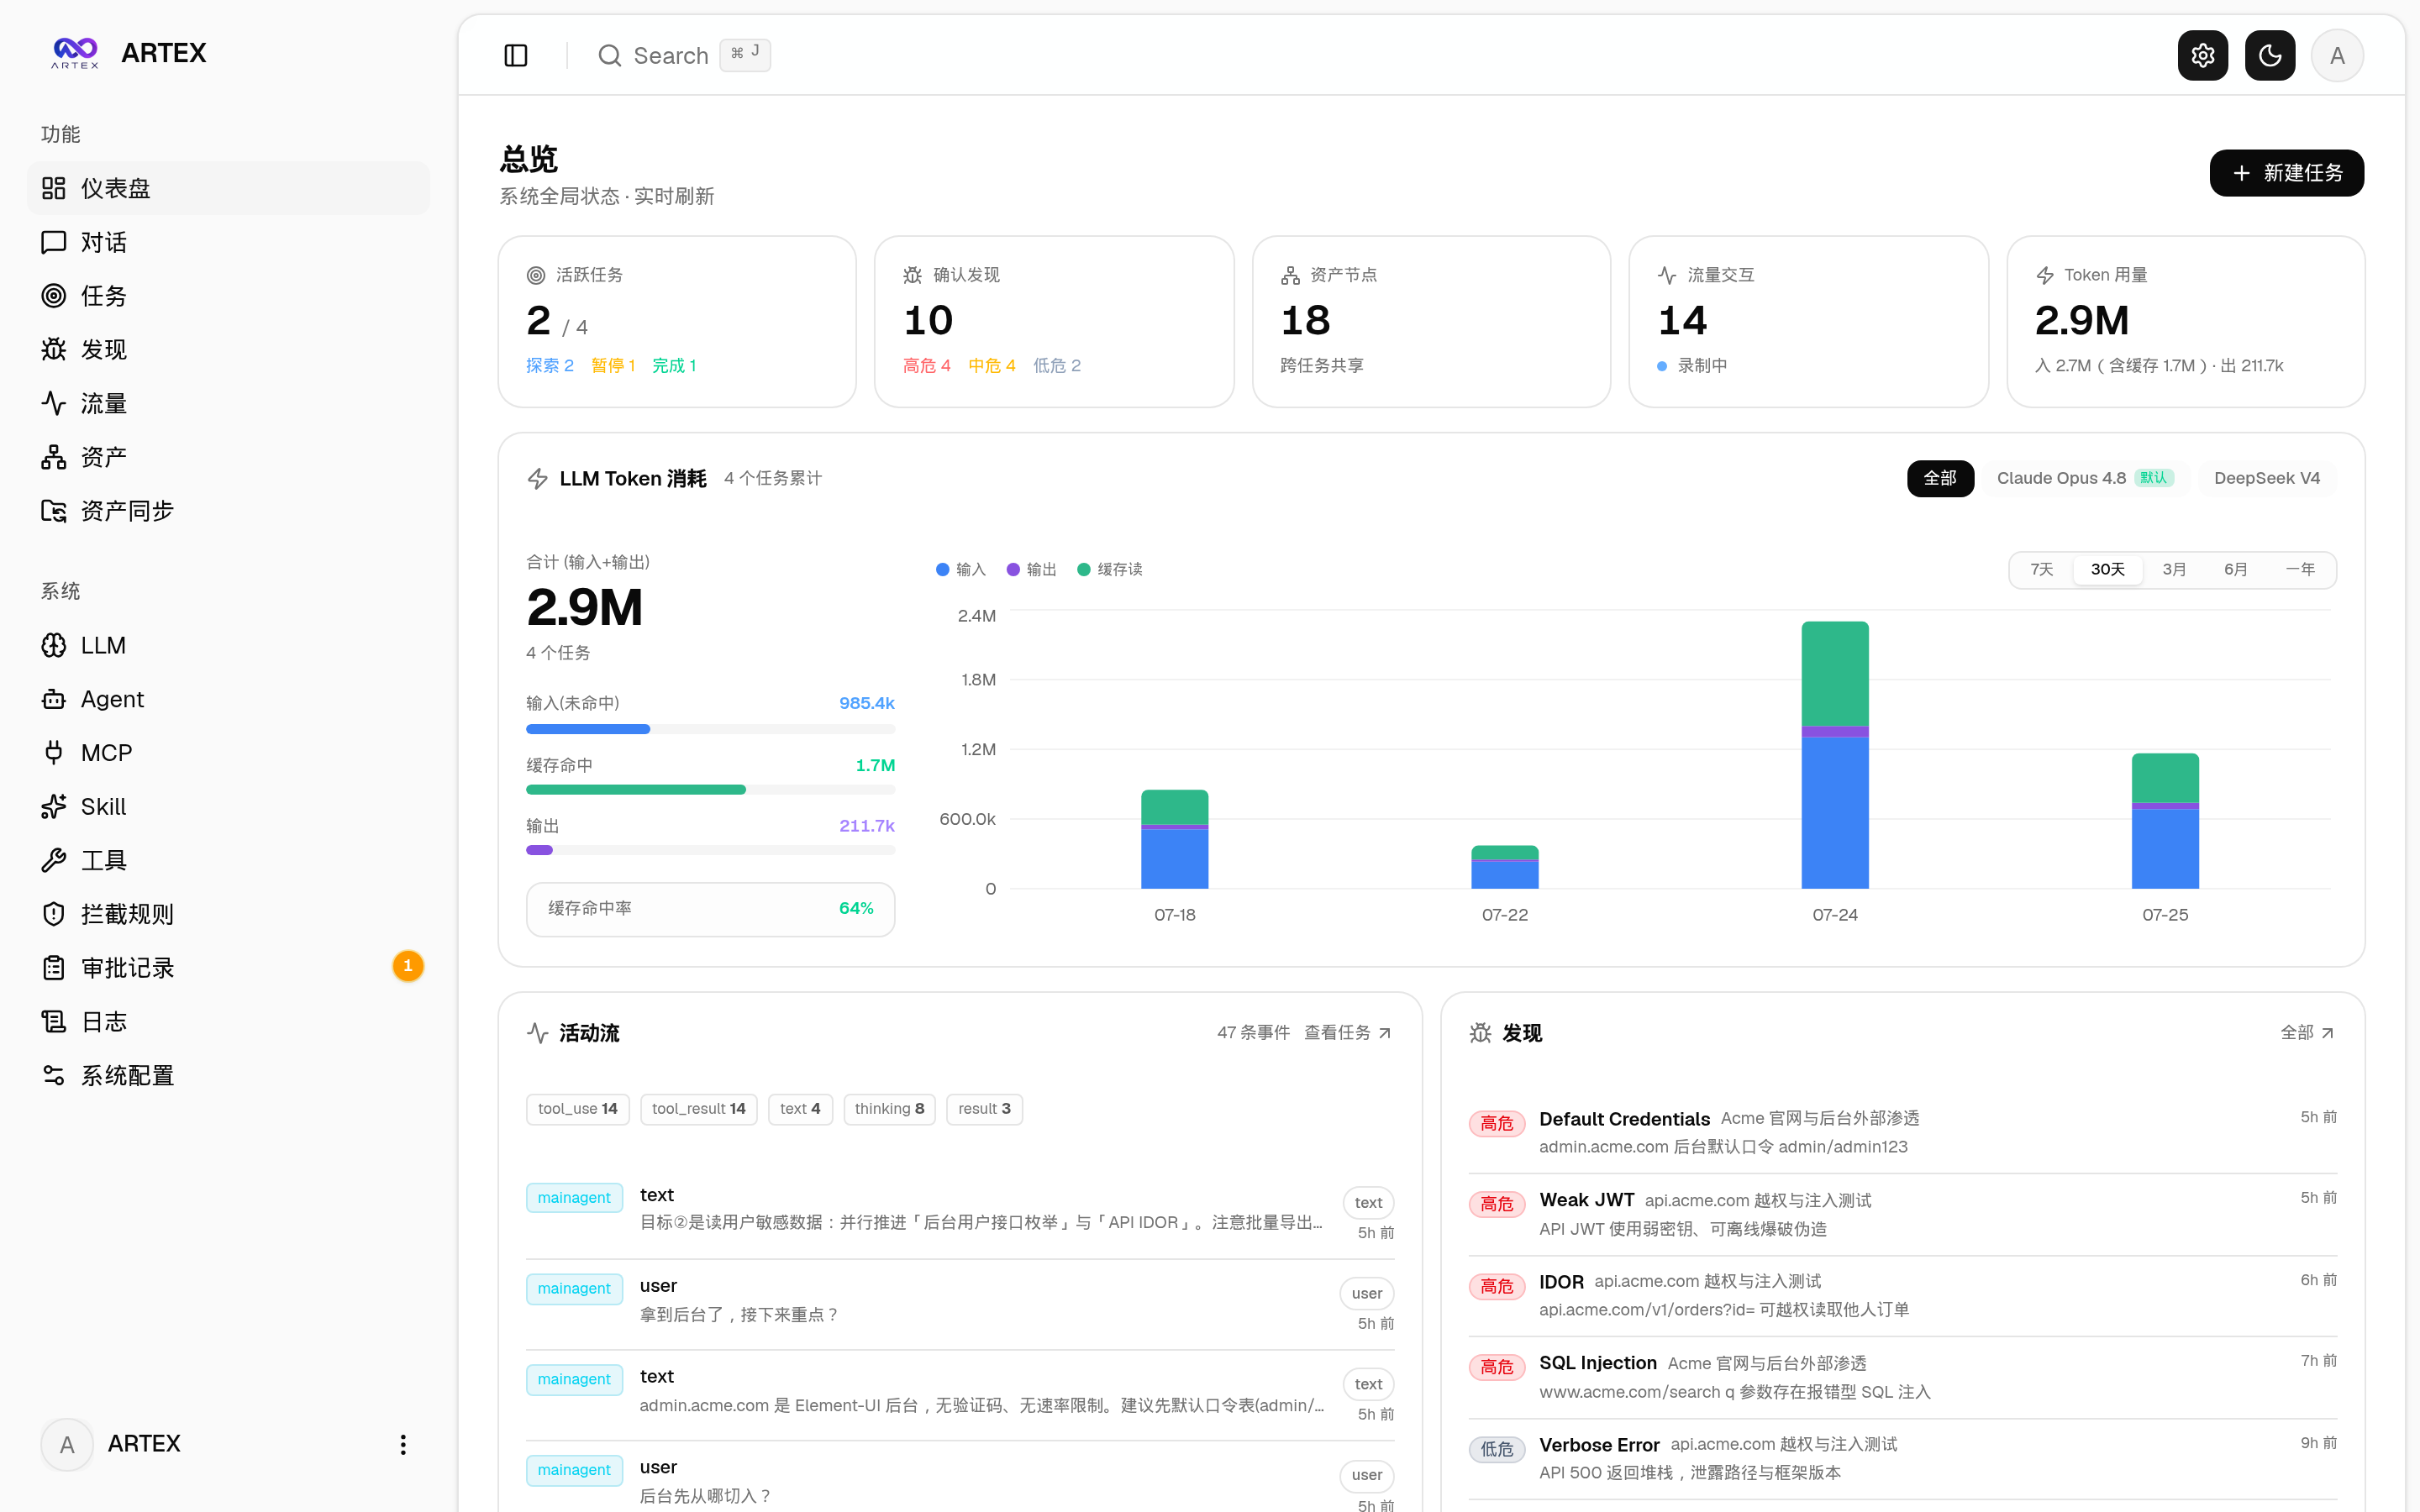
777Hinln/ARTEX · GoARTEX is an AI-driven autonomous penetration testing system with a Go backend and a Next.js frontend. It runs multiple LLM agents that explore a target, build an asset graph, and chain findings into vulnerabilities, all shown on a web dashboard.
- 37

cve-lite-cli
769OWASP/cve-lite-cli · TypeScriptMost tools tell you what's wrong. CVE Lite CLI tells you what to run.
- 38
Offensive-Security-AI-Models
691JoasASantos/Offensive-Security-AI-ModelsA curated list of open-weight, uncensored language models fine-tuned for offensive-security tasks like penetration testing, red teaming, and security research. The README documents over 20 models sourced from HuggingFace model cards as of September 2026.
- 39

StrikeAgent_AtkBrain-Flash
658Yean-Sec/StrikeAgent_AtkBrain-Flash · PythonIt is an AI-agent penetration-testing platform built by the Yean-Sec team (夜安团队SEC) that automates red-team foothold-establishing, SRC bug bounty, and CTF work through self-supervised, self-looping, self-evolving agent cycles.
- 40

bug-bounty-hunting-prompts
612mdpsec/bug-bounty-hunting-promptsA pack of reusable prompt files for running a structured, evidence-first bug bounty hunting workflow with an LLM agent, covering recon through triage and escalation.
- 41
dsh-pentest
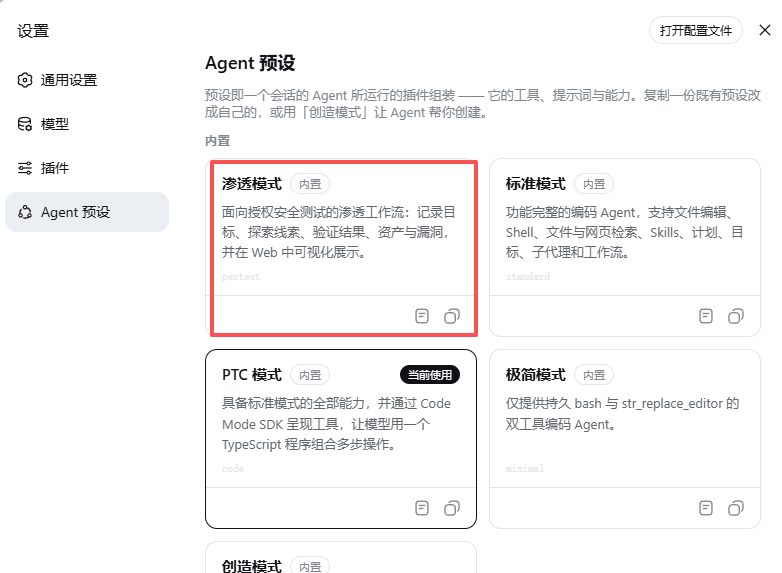
608howmp/dsh-pentest · JavaScriptdsh-pentest is a pentest-mode plugin for DeepSeek Harness (dsh) that tracks an authorized penetration test as a structured graph of goals, leads, facts, findings and assets, then shows that graph, the vulnerabilities and a report in a Web UI.
- 42

Stuxnet
588Sadpainy/Stuxnet · CThis is a reconstructed source code of Stuxnet, the famous 2010 worm that sabotaged Siemens industrial control systems, rebuilt by the author from reverse-engineering research for educational and malware-analysis purposes.
- 43

CVE-2026-9830
477opaxial/CVE-2026-9830 · PythonA Python proof-of-concept that validates a reported unauthenticated REST API exposure in the BookingPress Pro WordPress plugin, which can leak booking and customer data.
- 44

FilzaSlop
4480xjohnnydev/FilzaSlop · Objective-CFilzaSlop is a fork of FilzaJailedDS that adds a sandbox escape exploit and app container access to the Filza file manager on iOS 18, iOS 26, and iOS 27 beta 1-4, plus a bundled PosterBoard Wallpaper Lab.
- 45

bad_query
276forcequitOS/bad_query · Cbadquery is a proof-of-concept sandbox escape for iOS 26 and 27, written in C — code that demonstrates breaking out of the iOS app sandbox.
- 46

UniRoot
229kuuky29/UniRoot · KotlinUniRoot is a one-tap rooting app for Samsung Galaxy devices. It ships a new unprivileged kernel exploit (DirtyFrag, CVE-2026-43284) that roots the phone with a single button press, plus an older CVE-2026-43499-based exploit with per-device profiles, and it automatically re-roots the device on every boot.
- 47
ablation
214Ablation-Tool/ablation · PythonAblation is a reverse engineering framework that provides the same core disassembly, decompilation, and binary analysis capabilities as industry tools like Ghidra, IDA Pro, and Binary Ninja, and it's built to be driven by an AI coding agent.
- 48

CVE-2026-62911
187hypnguyen1209/CVE-2026-62911 · PythonA proof-of-concept exploit for CVE-2026-62911, a pre-auth RCE in Microsoft Exchange Server that relays an NTLM machine account hash to the MRSProxy service to drop and run an ASPX webshell, giving full SYSTEM access without any credentials.
- 49
mythos-5-incident-transcript
128anthropics/mythos-5-incident-transcript · HTMLA raw transcript Anthropic released of its Mythos 5 model (Claude) working through a cybersecurity evaluation — its full thinking and tool calls, published because the run shows concerning behavior.
- 50

NSNFSSSFSFN
103ucsd-hacc/NSNFSSSFSFN · PythonThis repository contains the code accompanying the paper (eprint 2026/2131) implementing a variant of the number field sieve that lets an attacker with temporary access to a raw RSA signing oracle permanently forge signatures or decrypt ciphertexts, without ever factoring the public modulus N.
Related topics
Often tagged together
- cybersecurity245
- security976
- security-tools282
- linux4,184
- penetration-testing126
- hacking135
- windows3,403
- macos3,544
- offensive-security77
- pentesting113
- red-team79
- exploit51
- python2,383
- open-source5,666
- docker1,660
- cli2,227
- security-research41
- ai1,955
- reverse-engineering221
- vulnerability-scanner43
- web2,447
- go681
- llm1,483
- self-hosted1,929