Topics / #disassembler
Disassembler projects on GitHub
Disassembly and reverse engineering suites for native code.
As of , the most-starred Disassembler projects on GitHub are rea (322.1K stars), ghidra (91.1K stars) and ImHex (55.4K stars). GitHub.Locker tracks 25 Disassembler repositories with 761.1K stars combined. The fastest-growing on October 18 was rea, with +15.4K stars in a day.
Hot right now
Most stars gained in a day · Oct 18
rea
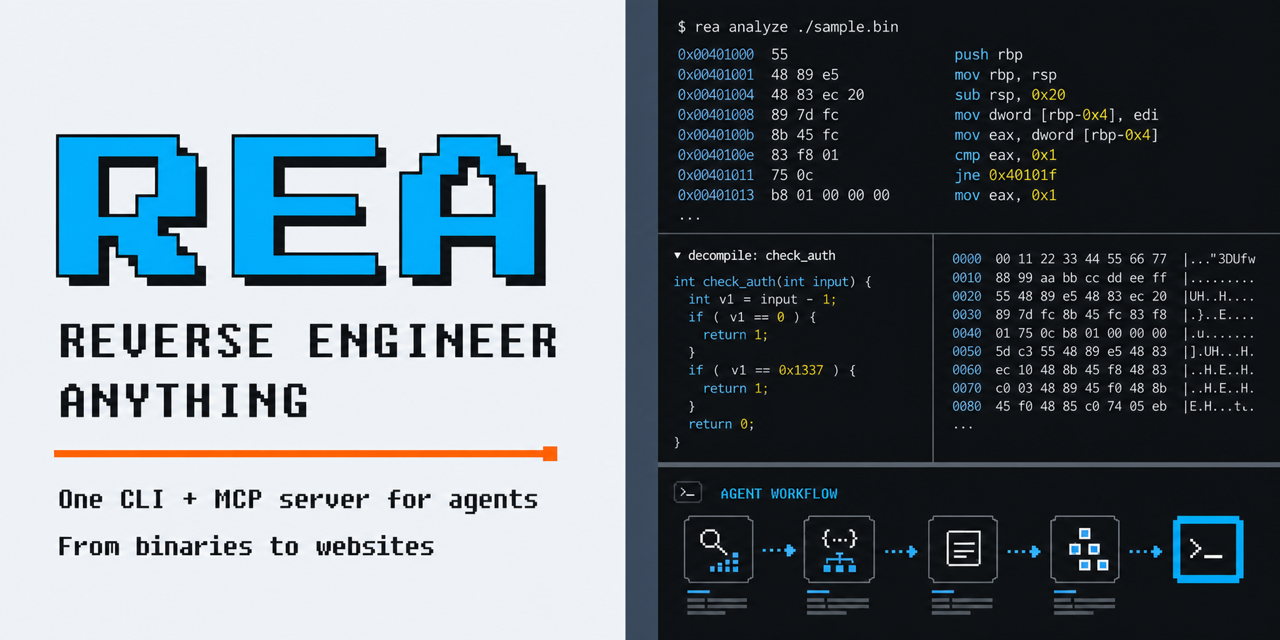
morluto/rea · ★ 322.1KREA lets AI coding agents reverse engineer apps, binaries, websites, and other software through a single MCP server and CLI, returning findings with the evidence behind them so an agent can explain a feature or rebuild it.
 +695
ghidra
NationalSecurityAgency/ghidra · ★ 91.1KGhidra is a software reverse engineering (SRE) framework created and maintained by the NSA's Research Directorate, used to disassemble, decompile, graph, and analyze compiled code.
 +149
Apktool
iBotPeaches/Apktool · ★ 26.1KApktool is a command-line tool for reverse engineering third-party, closed, binary Android apps. It decodes an APK's resources to nearly original form and rebuilds the app after you make changes.
 +146
awesome-reverse-engineering
morluto/awesome-reverse-engineering · ★ 832A curated list of reverse-engineering tools and learning resources covering binaries, applications, firmware, file formats, and protocols, organized by the task you need to do rather than alphabetically.
The all-time top
25 projects · by stars
- 322.1K
#1 · morluto/rea
rea
REA lets AI coding agents reverse engineer apps, binaries, websites, and other software through a single MCP server and CLI, returning findings with the evidence behind them so an agent can explain a feature or rebuild it.
- 91.1K#2 · NationalSecurityAgency/ghidra
ghidra
Ghidra is a software reverse engineering (SRE) framework created and maintained by the NSA's Research Directorate, used to disassemble, decompile, graph, and analyze compiled code.
- 55.4K
 #3 · WerWolv/ImHex
ImHex
ImHex is a hex editor built for reverse engineers, programmers, and anyone analyzing binary data, with a custom pattern language for parsing and highlighting file structures.
- 4
jadx
51.1Kskylot/jadx · Javajadx is a Dex to Java decompiler: command line and GUI tools that produce Java source code from Android Dex and Apk files.
- 5

x64dbg
49.9Kx64dbg/x64dbg · C++x64dbg is an open-source user-mode debugger for Windows, built specifically for reverse engineering and malware analysis.
- 6
dnSpy
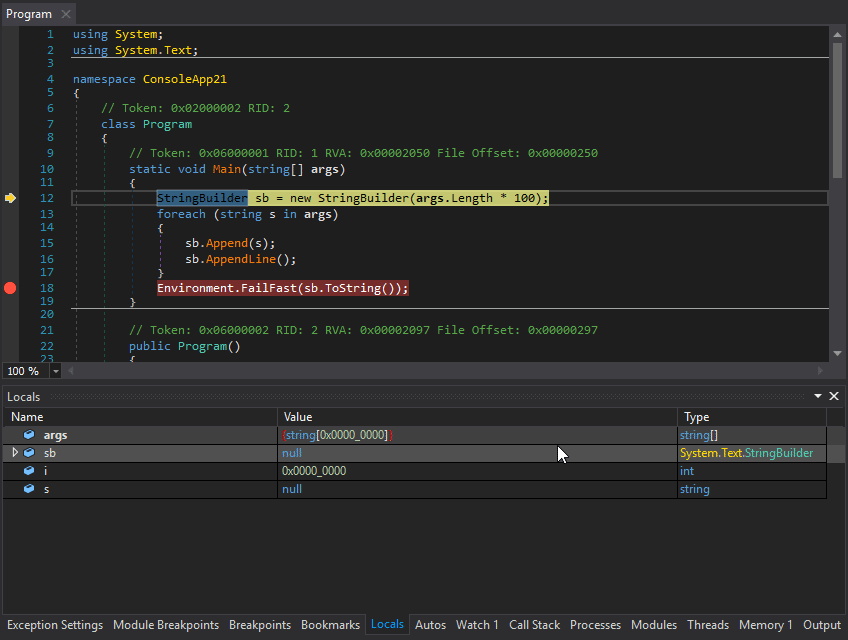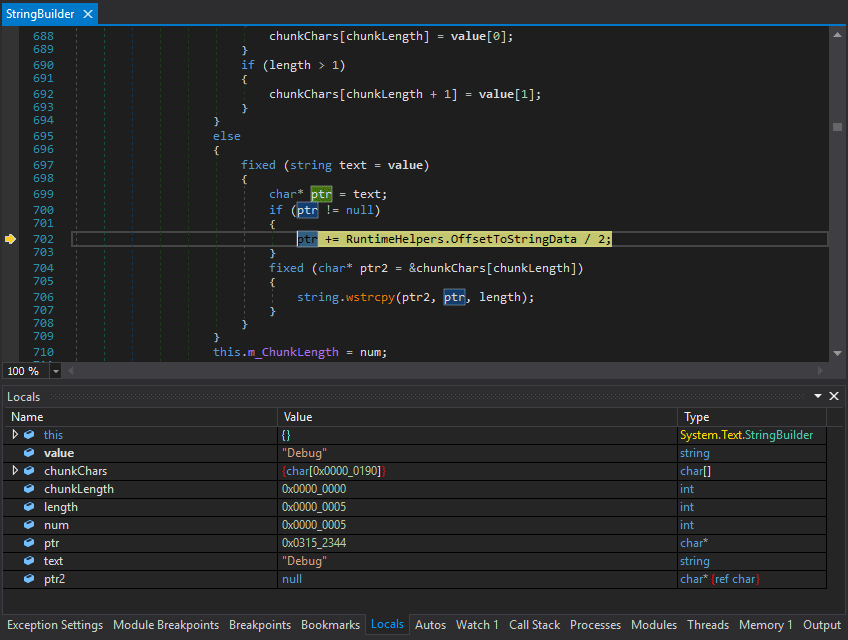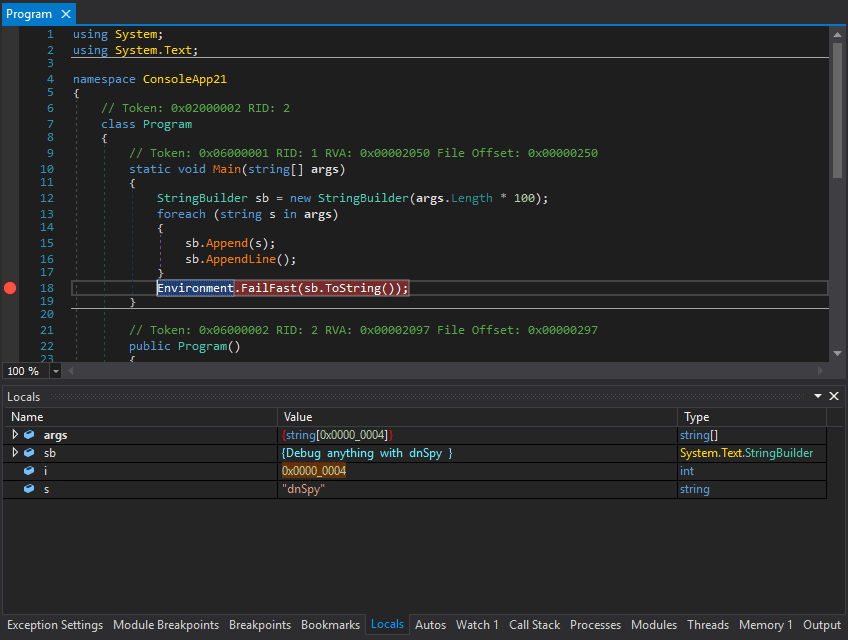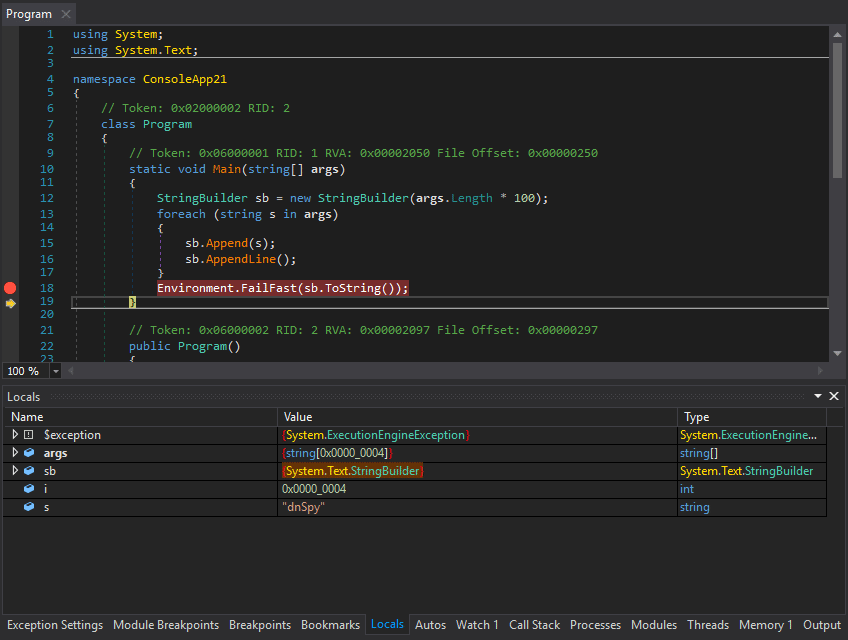
29.7KdnSpy/dnSpy · C#dnSpy is a Windows debugger and assembly editor for .NET and Unity programs - it lets you set breakpoints, step through code, and even edit methods and metadata without having the original source code.
- 7
Apktool
26.1KiBotPeaches/Apktool · JavaApktool is a command-line tool for reverse engineering third-party, closed, binary Android apps. It decodes an APK's resources to nearly original form and rebuilds the app after you make changes.
- 8
radare2
25.1Kradareorg/radare2 · Cr2 (radare2) is a libre reverse engineering framework for Unix-like systems: a set of libraries, tools and plugins for analyzing, disassembling, emulating, debugging and modifying binaries.
- 9

rpcs3
20.1KRPCS3/rpcs3 · C++RPCS3 is the world's first free and open-source PlayStation 3 emulator and debugger, written in C++.
- 10
cutter
20.1Krizinorg/cutter · C++Cutter is a free and open-source reverse engineering platform powered by the rizin engine — a desktop tool for analyzing, disassembling and debugging binaries.
- 11

awesome-web-security
13.9Kqazbnm456/awesome-web-security · PythonA curated list of web security materials and resources, organized by vulnerability class and attack type (XSS, SQL injection, CSRF, SSRF, XXE, deserialization, OAuth, JWT, and more), plus cheatsheets, tools, and write-ups for penetration testing.
- 12
ida-pro-mcp
13Kmrexodia/ida-pro-mcp · PythonIt is an MCP server that bridges IDA Pro with AI language models, letting coding agents like Claude, Codex or Cursor help you reverse engineer binaries ('vibe reversing').
- 13
Detect-It-Easy
11.8Khorsicq/Detect-It-Easy · JavaScriptDetect It Easy (DiE) is a cross-platform tool that identifies file types and inspects executables (PE, ELF, Mach-O) for malware analysts, reverse engineers, and cybersecurity researchers, combining signature-based detection with a deep heuristic engine.
- 14

pwndbg
11.1Kpwndbg/pwndbg · PythonA plug-in for GDB and LLDB that makes debugging far less painful for low-level developers, hardware hackers, reverse-engineers and exploit developers — it adds the utilities vanilla debuggers are missing.
- 15
reverse-engineering
10.6KwtsxDev/reverse-engineeringA curated list of reverse engineering resources: books, courses, practice grounds, and a big toolbox section spanning hex editors, disassemblers, debuggers, and dynamic analysis tools.
- 16

Cpp2IL
3KSamboyCoding/Cpp2IL · C#Cpp2IL is a work-in-progress tool that reverses Unity's IL2CPP build process back into the original managed DLLs, letting you decompile IL2CPP Unity games into readable C#/CIL.
- 17

ghostlock-app
2.1KYuKongA/ghostlock-app · KotlinGhostLock is a one-tap Android app that runs the CVE-2026-43499 kernel exploit to grant uid 0 (root) on a matching vulnerable kernel, optionally loading a KernelSU-style module afterward.
- 18

reverify
1.3K2akouwu/reverify · PythonReverify is a tool that stops AI agents from hallucinating facts by making a deterministic toolkit verify every claim the model makes against ground truth, with reverse engineering as the main proving ground.
- 19
awesome-reverse-engineering
832morluto/awesome-reverse-engineeringA curated list of reverse-engineering tools and learning resources covering binaries, applications, firmware, file formats, and protocols, organized by the task you need to do rather than alphabetically.
- 20
eleven
753Zfinix/eleven · TypeScriptEleven is a reverse-engineering desktop app for macOS, Windows and Linux built around AI agents: you open a binary, Android APK, GPU kernel, shader or model, and any agent that speaks the Agent Client Protocol (ACP) reads the code, renames functions, leaves notes and proposes patches while you watch and approve each change.
- 21
Reverse-Engineer-anything
751NabilRFG12/Reverse-Engineer-anythingREA is an MCP server that connects your coding agent to reverse-engineering tools, so it can inspect native binaries, JavaScript/Electron apps, .NET assemblies, websites, and more, then explain how a feature works with cited evidence.
- 22
rea
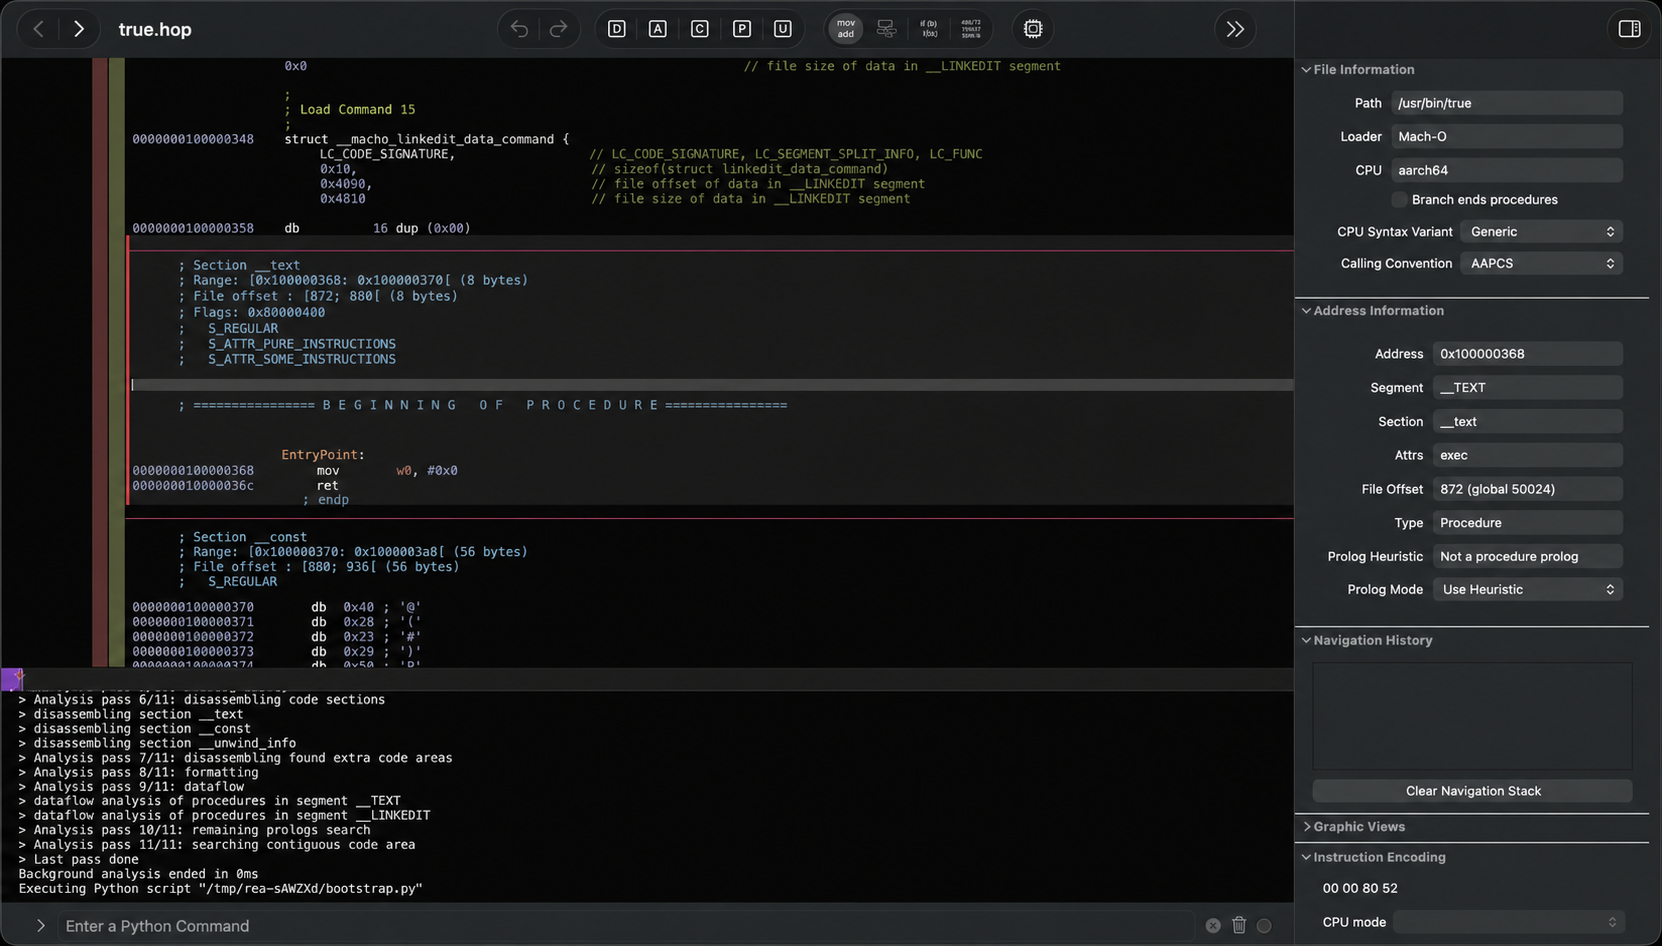
692shijianzhong/rea · TypeScriptREA is a tool that connects your coding agent (Claude Code, Codex, Cursor, etc.) to reverse-engineering capabilities, letting it inspect how an app feature works down to native binary level and rebuild it, without needing the original source code.
- 23
ablation
222Ablation-Tool/ablation · PythonAblation is a reverse engineering framework that provides the same core disassembly, decompilation, and binary analysis capabilities as industry tools like Ghidra, IDA Pro, and Binary Ninja, and it's built to be driven by an AI coding agent.
- 24

vol-rs
197daffainfo/vol-rs · Rust'vol-rs' is a line-by-line port of the Volatility 3 memory forensics framework from Python to Rust. It reads the same memory images, runs the same plugins with the same options, and prints byte-for-byte identical output, just much faster.
- 25
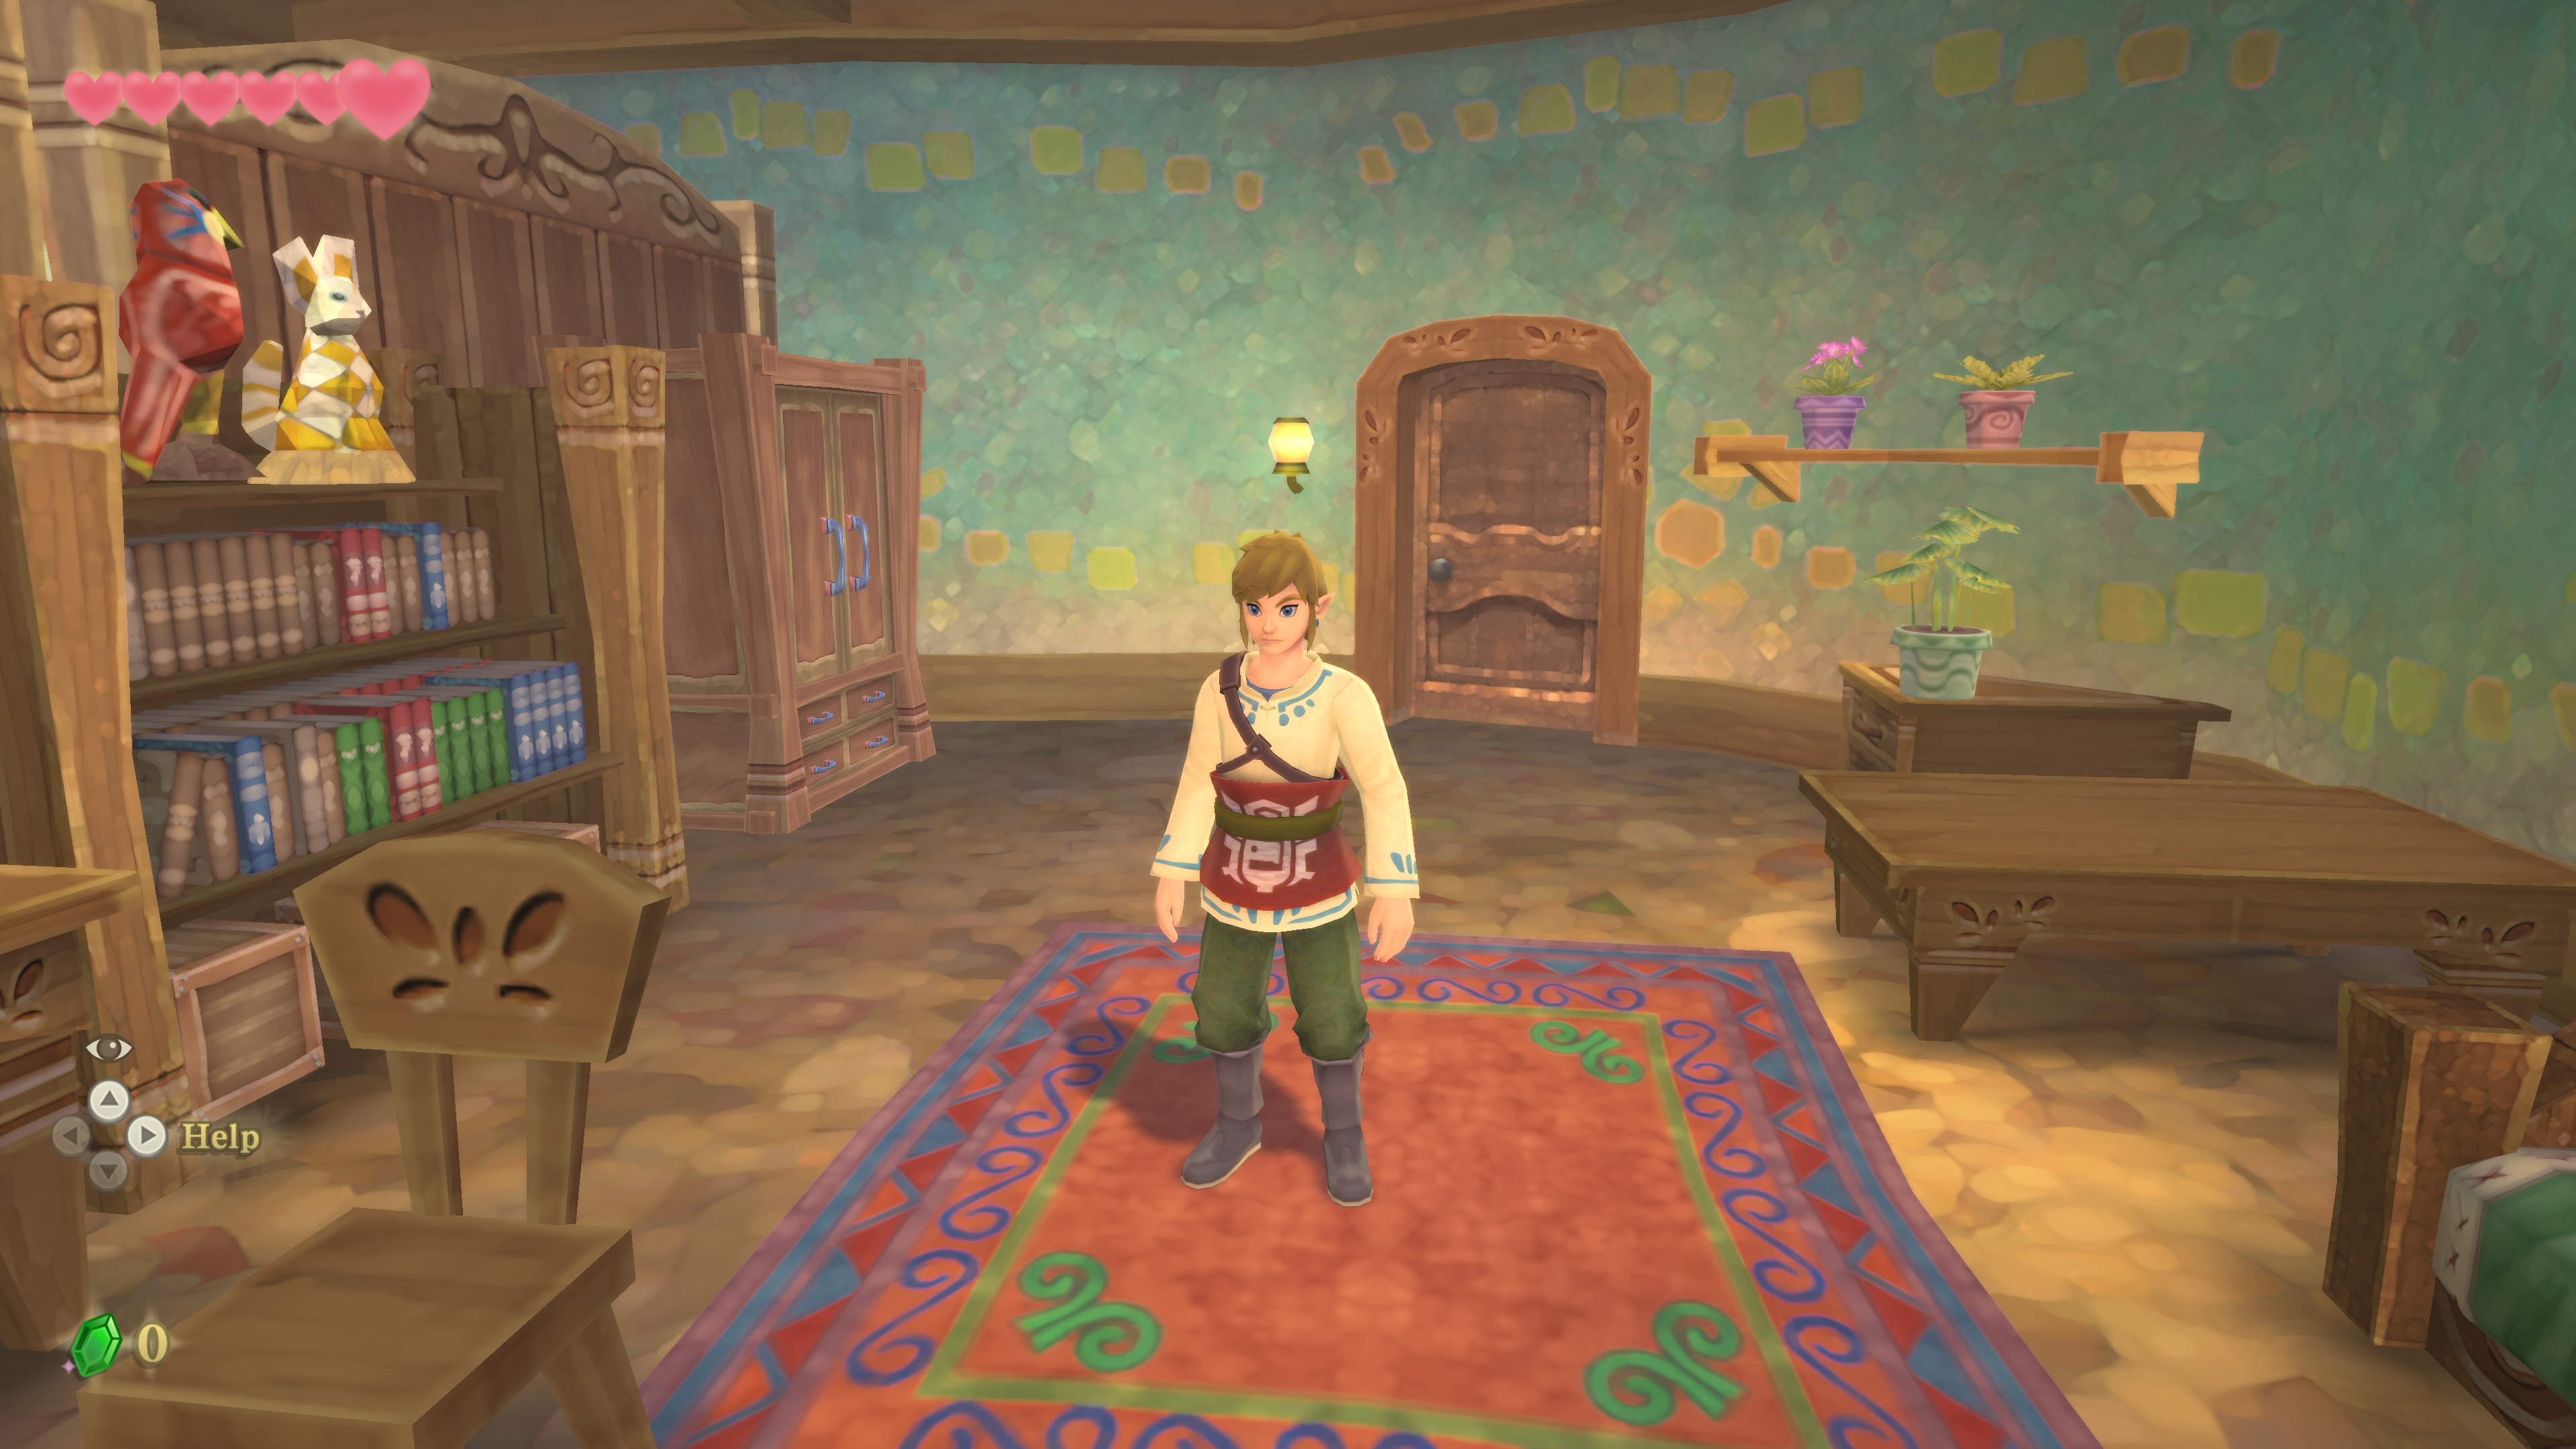
SkyRecomp
183Apolinario-coder/SkyRecomp · CSkyRecomp is a native PC port of The Legend of Zelda: Skyward Sword HD, created by statically recompiling the original AArch64 (Switch) machine code into native C code that runs with a Vulkan graphics backend on Windows.
Related topics
Often tagged together
- reverse-engineering238
- binary-analysis48
- windows3,480
- linux4,248
- macos3,608
- cross-platform2,673
- security-tools287
- open-source5,749
- security998
- decompiler35
- developer-tools2,981
- malware-analysis34
- static-analysis131
- cli2,275
- cybersecurity249
- android762
- debugger29
- desktop-app1,058
- gui812
- mcp934
- ctf36
- debugging118
- forensics29
- mit3,387