Topics / #incident-response
Incident-response projects on GitHub
Tools and practices for detecting and responding to security incidents.
As of , the most-starred Incident-response projects on GitHub are Anthropic-Cybersecurity-Skills (34.6K stars), h4cker (29.8K stars) and witr (22.7K stars). GitHub.Locker tracks 19 Incident-response repositories with 203.2K stars combined. The fastest-growing on October 16 was Anthropic-Cybersecurity-Skills, with +71 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
 +71
Anthropic-Cybersecurity-Skills
mukul975/Anthropic-Cybersecurity-Skills · ★ 34.6KAn open-source library of 818 production-grade cybersecurity skills for AI agents, covering 34 security domains and mapped to six frameworks including MITRE ATT&CK and NIST CSF 2.0.
 +44
post-mortems
danluu/post-mortems · ★ 12.6KA curated collection of links to post-mortems — public write-ups of real outages and production failures, maintained by developer Dan Luu since 2015. Most entries are incidents at big tech: Cloudflare, Google, Facebook, Amazon, GitHub.
 +30
artex-global
jiwoochris/artex-global · ★ 1.6KARTEX-KO is a Korean localization of the ARTEX (Autumn-27/ARTEX) framework: a system where multiple LLM-driven agents autonomously run a penetration test end-to-end, from reconnaissance to exploitation, with a Go backend and an embedded Next.js frontend.
 +19
mvt
mvt-project/mvt · ★ 15.4KMVT (Mobile Verification Toolkit) is a collection of forensic utilities that help gather and analyze traces on Android and iOS devices to identify a potential compromise, originally built by Amnesty International's Security Lab during the Pegasus Project.
The all-time top
19 projects · by stars
- 34.6K#1 · mukul975/Anthropic-Cybersecurity-Skills
Anthropic-Cybersecurity-Skills
An open-source library of 818 production-grade cybersecurity skills for AI agents, covering 34 security domains and mapped to six frameworks including MITRE ATT&CK and NIST CSF 2.0.
- 29.8K
#2 · The-Art-of-Hacking/h4cker
h4cker
A curated collection of thousands of cybersecurity resources — references, scripts, tools, code, labs, and training material — maintained by Omar Santos as a companion to his books, video courses, and live training.
- 22.7K
 #3 · pranshuparmar/witr
witr
witr answers one question: 'why is this running?' Point it at a process, port, container, or file, and it traces the exact chain of supervisors, services, and shells that started it.
- 4
wazuh
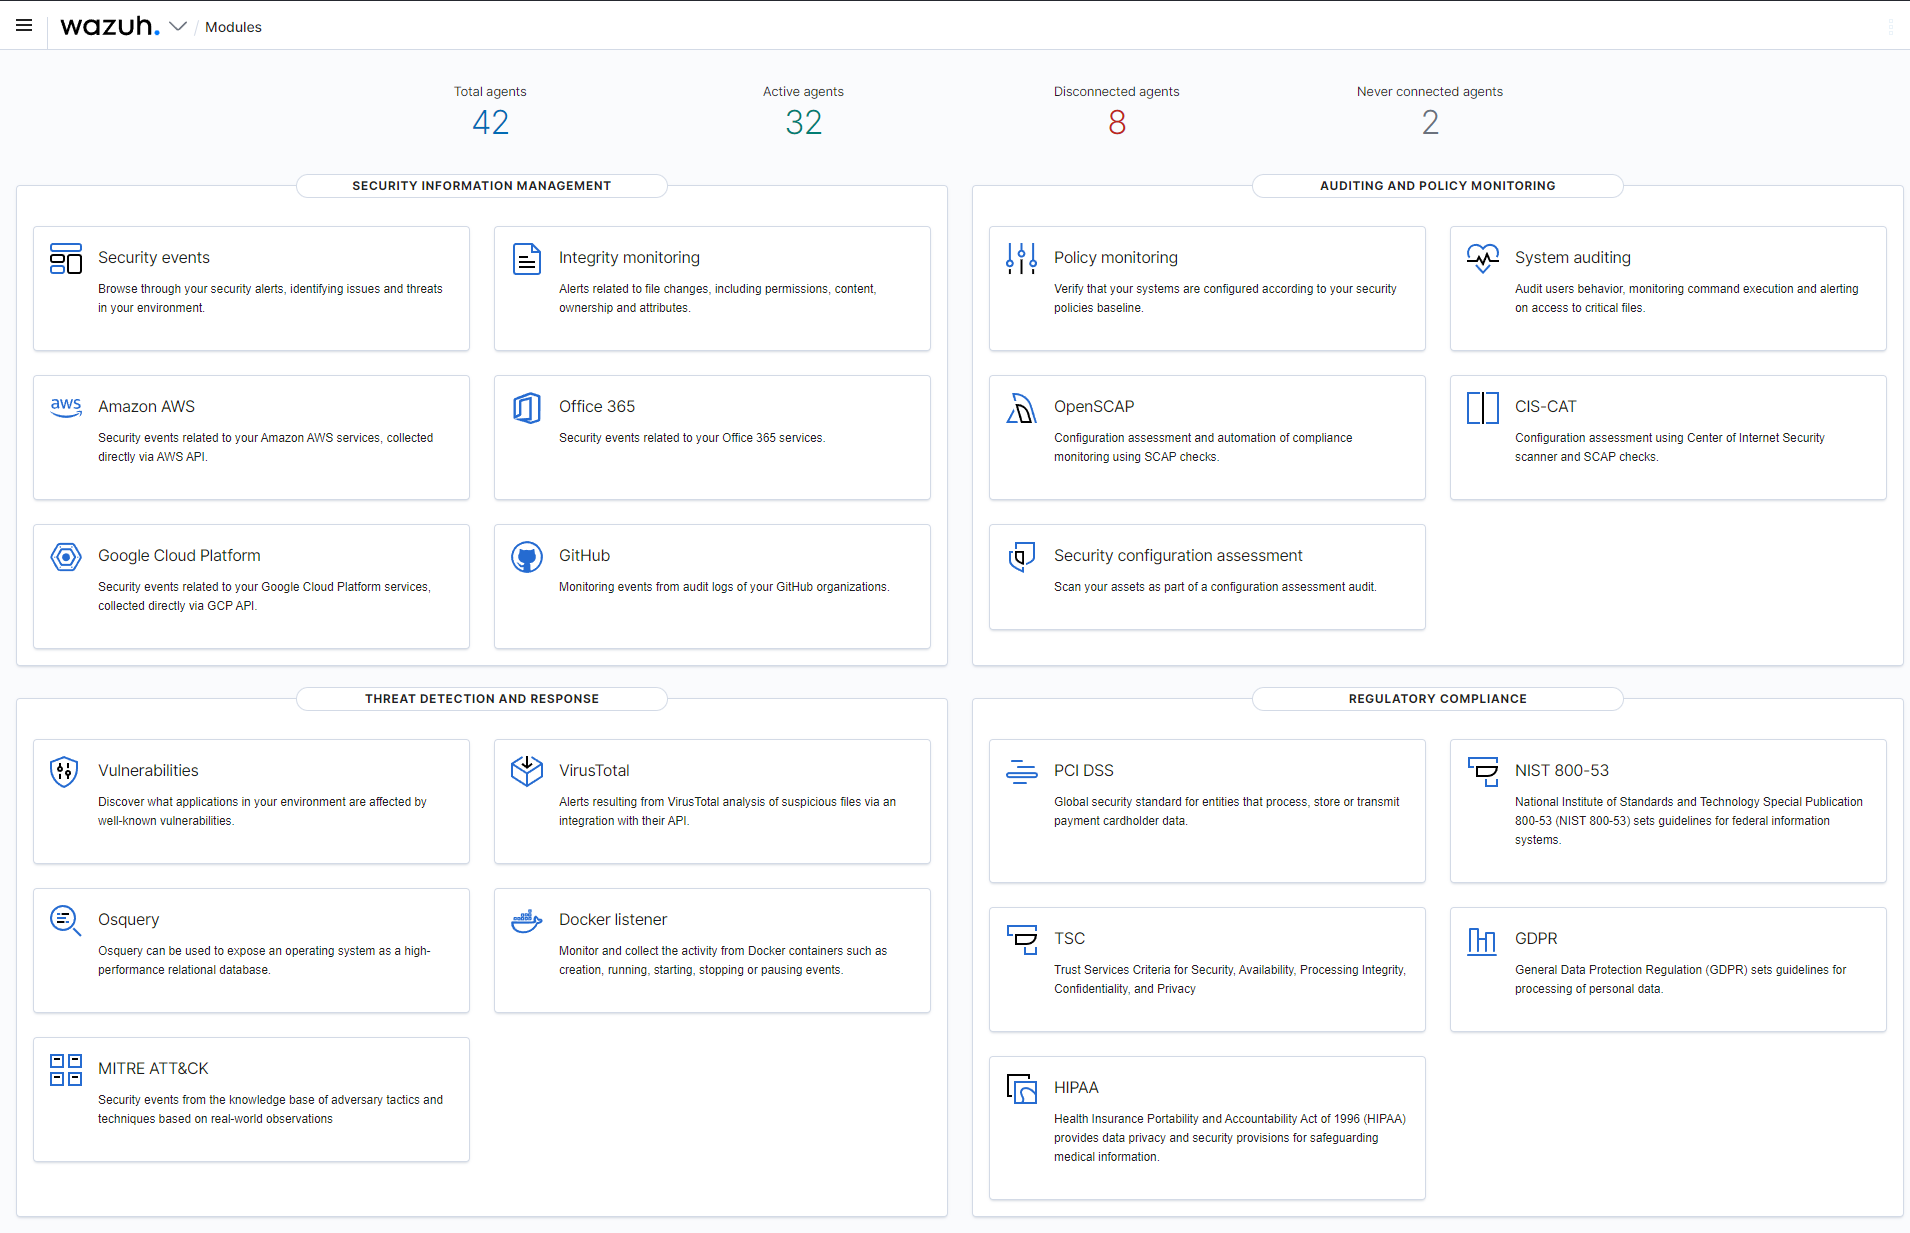
17.3Kwazuh/wazuh · C++Wazuh is a free, open source security platform (XDR and SIEM) for threat prevention, detection and response across on-premises, virtualized, containerized and cloud workloads.
- 5
mvt
15.4Kmvt-project/mvt · PythonMVT (Mobile Verification Toolkit) is a collection of forensic utilities that help gather and analyze traces on Android and iOS devices to identify a potential compromise, originally built by Amnesty International's Security Lab during the Pegasus Project.
- 6

awesome-sre
13.7Kdastergon/awesome-sreA curated list of Site Reliability Engineering (SRE) and Production Engineering resources — a hand-picked collection of articles, books, talks, podcasts and tools, maintained as a single GitHub README.
- 7
post-mortems
12.6Kdanluu/post-mortemsA curated collection of links to post-mortems — public write-ups of real outages and production failures, maintained by developer Dan Luu since 2015. Most entries are incidents at big tech: Cloudflare, Google, Facebook, Amazon, GitHub.
- 8

keep
12.4Kkeephq/keep · PythonKeep is an open-source AIOps and alert management platform: a single pane of glass for alerts and incidents, with deduplication, enrichment, filtering, correlation, workflows and dashboards built in.
- 9

kubeshark
12.1Kkubeshark/kubeshark · GoKubeshark is an eBPF-powered network observability tool for Kubernetes that captures and indexes L4/L7 traffic with full Kubernetes context, decrypts TLS without managing keys, and lets both humans and AI agents query the data.
- 10

awesome-honeypots
10.6Kparalax/awesome-honeypots · PythonA curated, categorized list of honeypot software and related tools used by security researchers to deceive attackers, log their behavior, and study exploitation attempts.
- 11

defending-code-reference-harness
7.6Kanthropics/defending-code-reference-harness · PythonA reference implementation from Anthropic for finding and fixing vulnerabilities with Claude: a set of Claude Code skills (quickstart, threat-model, vuln-scan, triage, patch, customize) plus an autonomous scanning harness that runs a recon-find-verify-report-patch loop, built from learnings partnering with security teams.
- 12
xyops
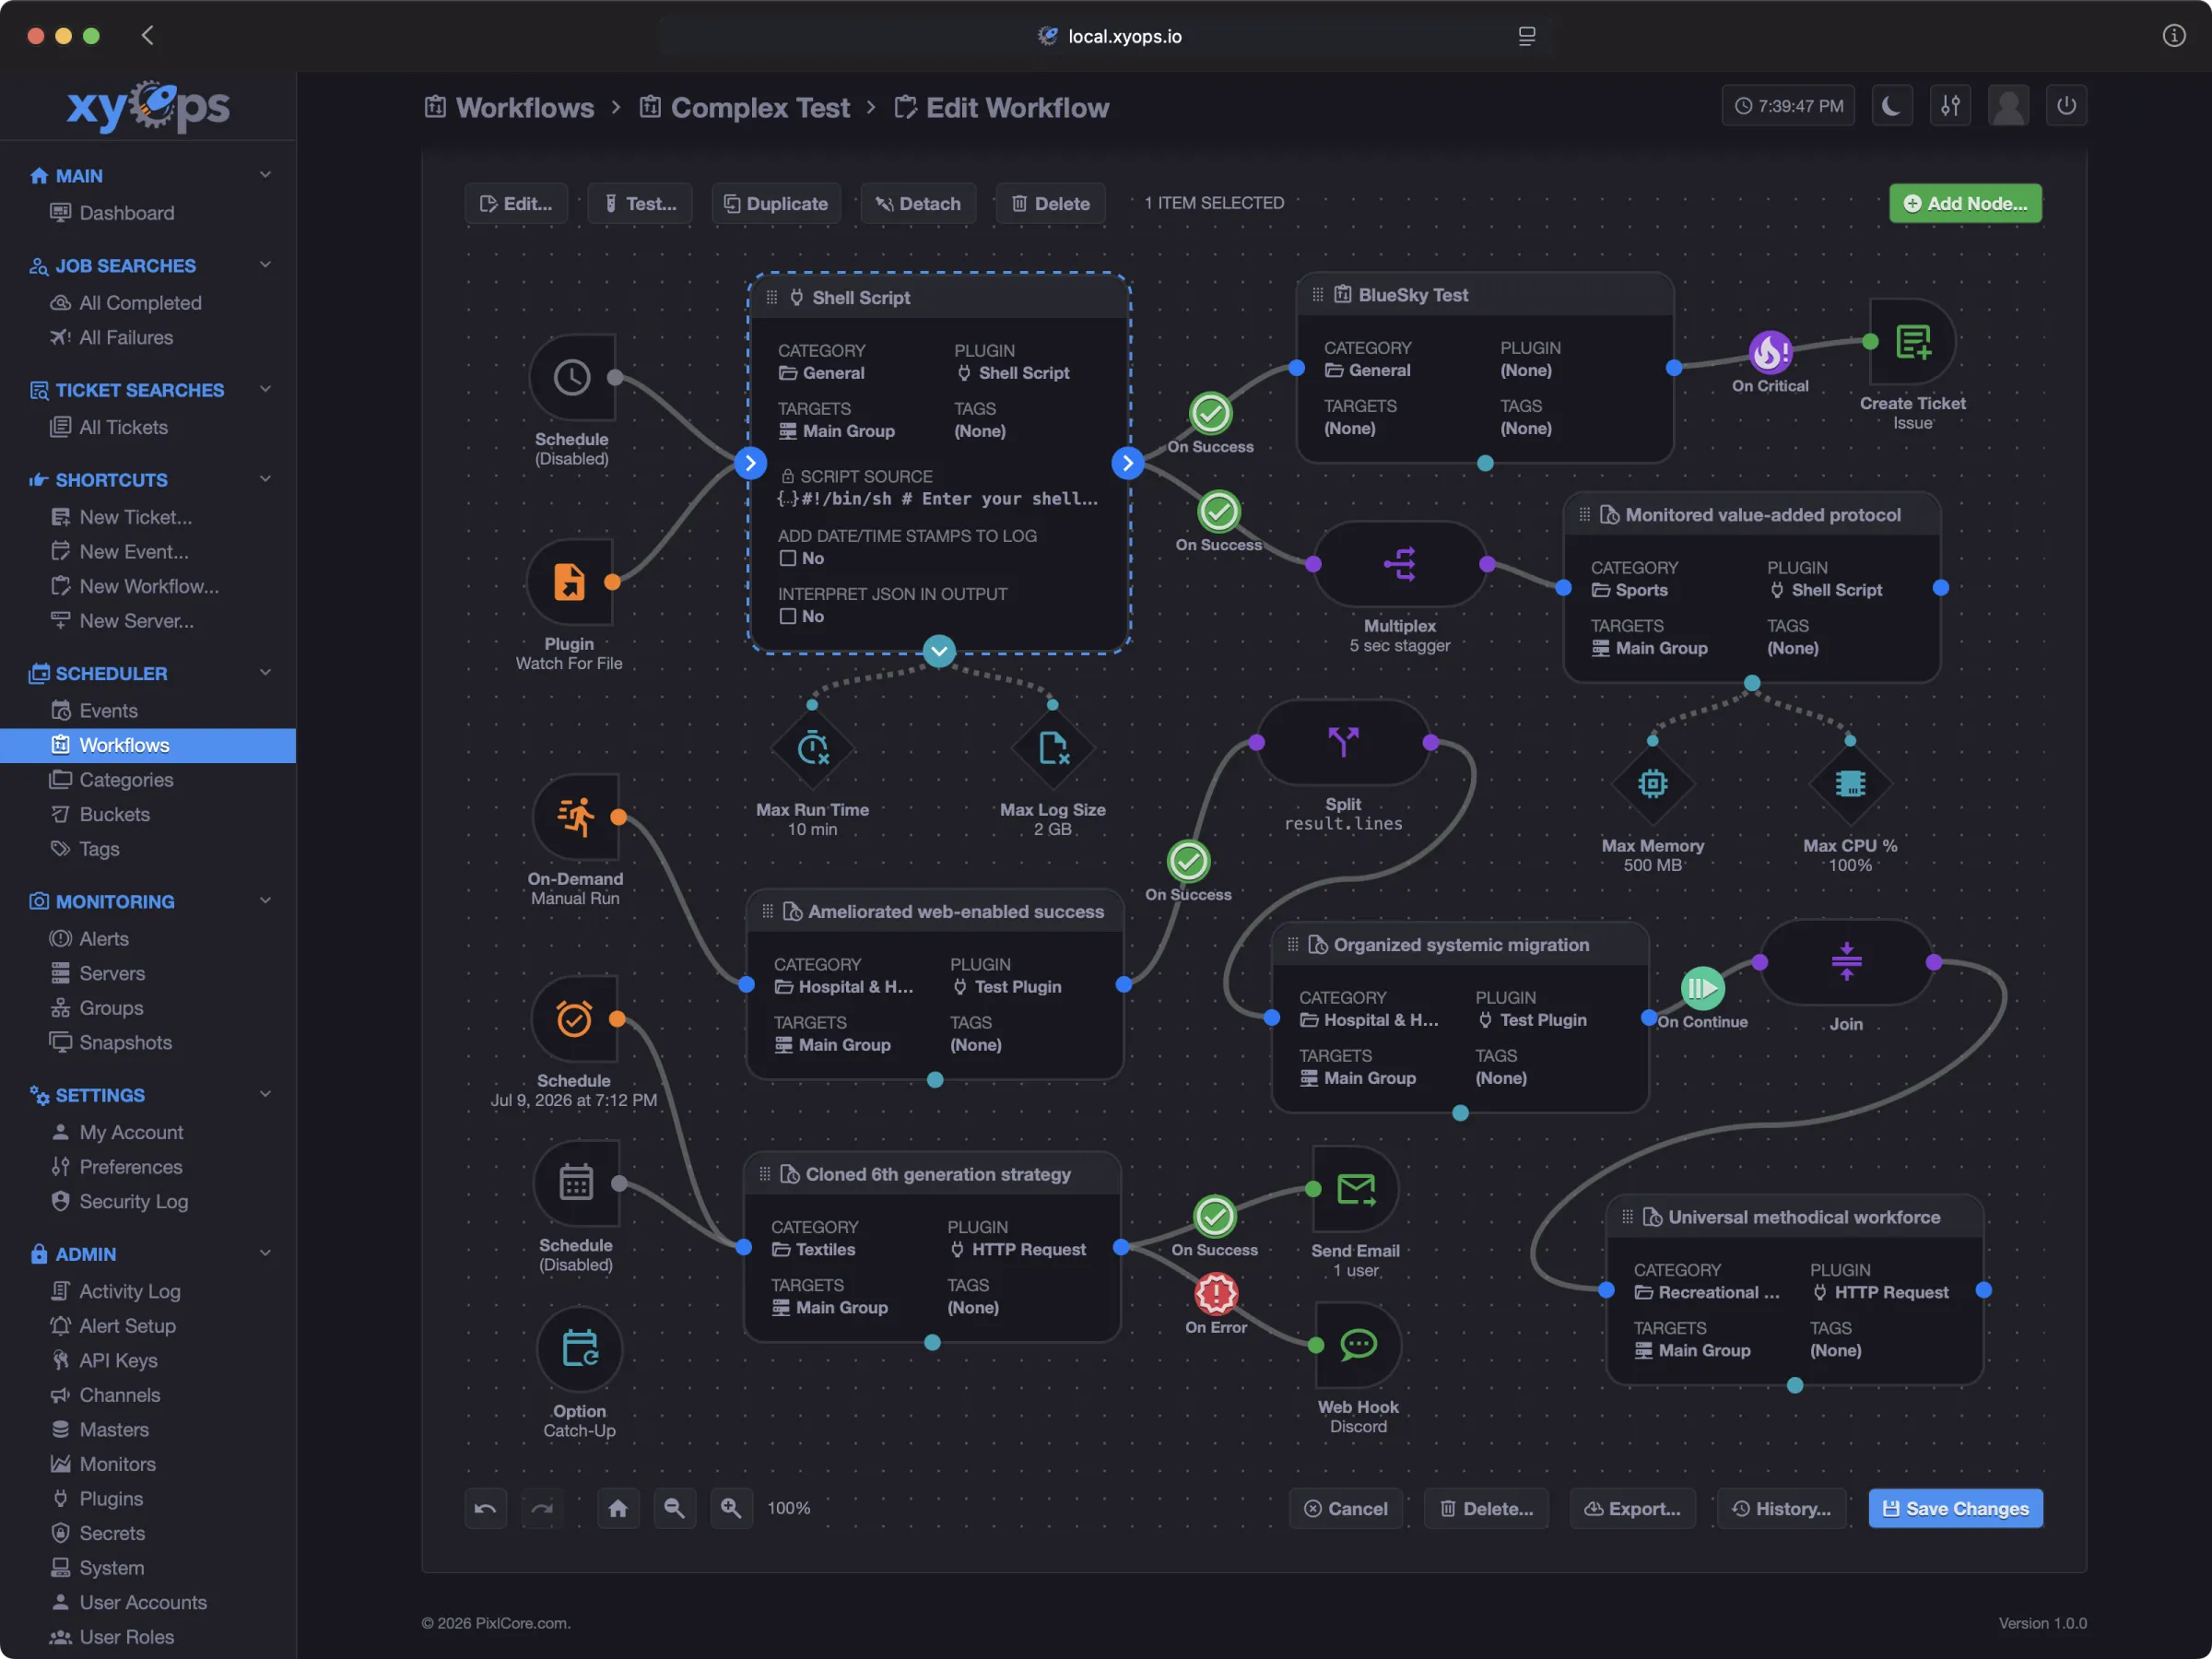
6.3Kpixlcore/xyops · JavaScriptxyOps is a self-hosted platform for job scheduling, visual workflow automation, server monitoring, alerting, and incident response — the next generation of the Cronicle scheduler.
- 13

bumblebee
5.1Kperplexityai/bumblebee · GoBumblebee is a read-only inventory collector that scans macOS and Linux developer machines for package, extension, and developer-tool metadata, so responders can quickly check if a machine matches a known supply-chain compromise advisory.
- 14
artex-global
1.6Kjiwoochris/artex-global · GoARTEX-KO is a Korean localization of the ARTEX (Autumn-27/ARTEX) framework: a system where multiple LLM-driven agents autonomously run a penetration test end-to-end, from reconnaissance to exploitation, with a Go backend and an embedded Next.js frontend.
- 15
dsh-redteam-model
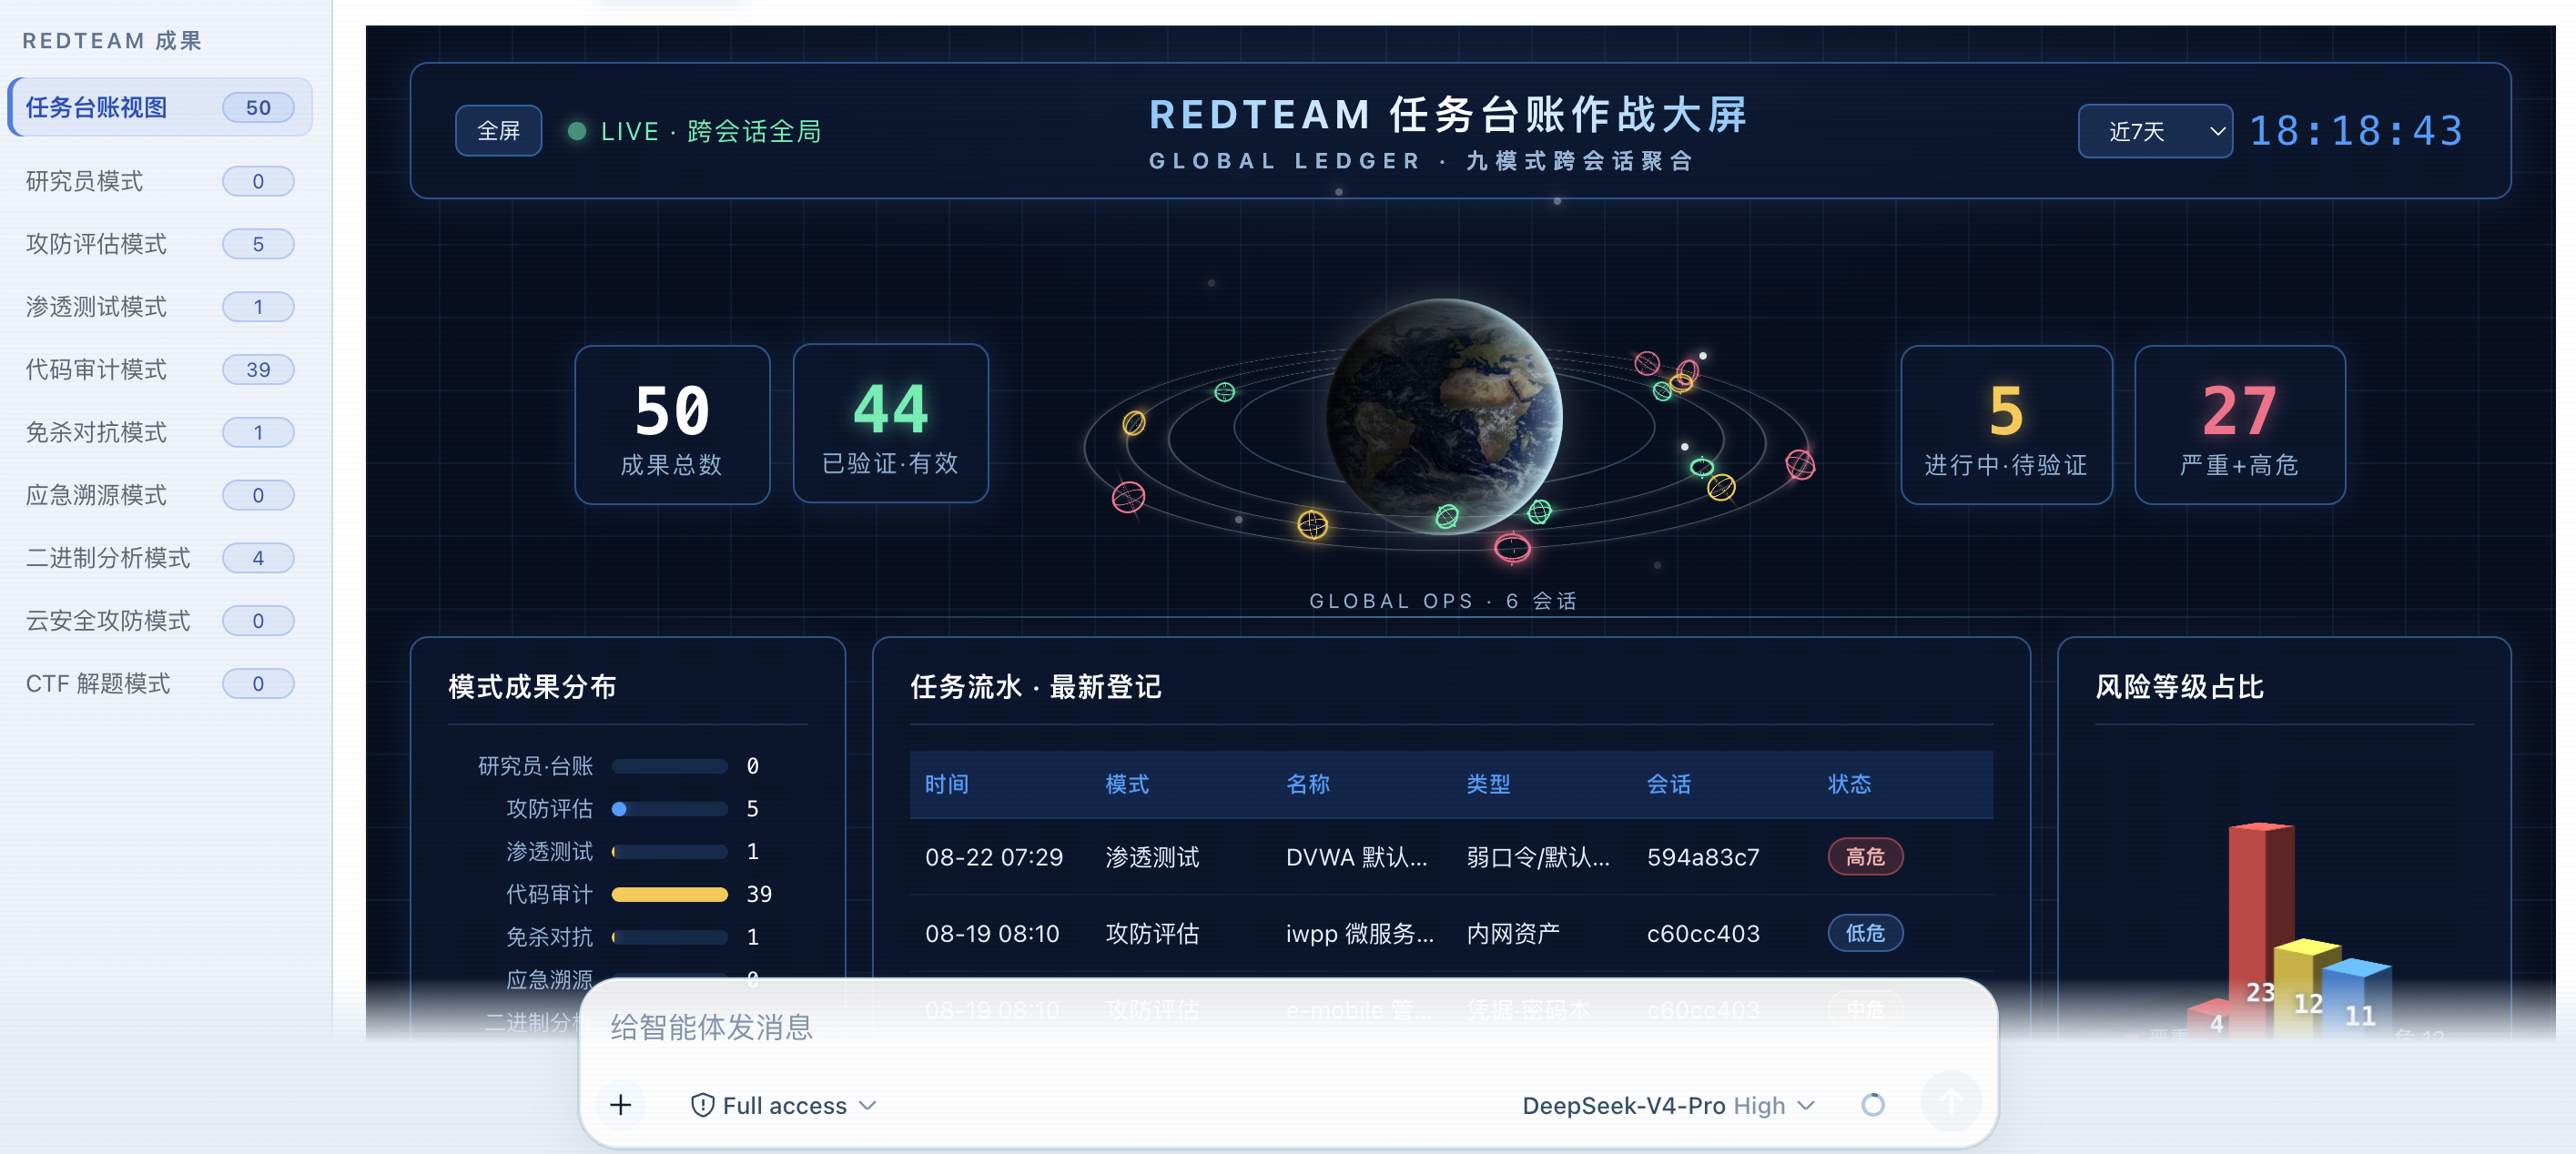
719SeaOf0/dsh-redteam-model · PythonA plugin pack for the dsh (DeepSeek Harness) AI agent that adds nine preset red-team security research modes and seventeen runtime plugins, covering pentesting, code audit, binary analysis, anti-detection, incident response, cloud security and CTF solving.
- 16

vps-security-enhancement-scripts
2380x10debug/vps-security-enhancement-scripts · ShellIt is a security-first interactive bash script for hardening a fresh VPS or cloud server, bundled with a scenario-driven handbook and printable cheatsheets that explain why each fix matters, not just how to run it.
- 17

oxynote
201oxynote/oxynote · GoOxynote is a self-hosted technical wiki that connects documentation directly to the systems it describes, pairing live metric charts and Stripe-style API docs with the same page and running every edit through a draft-diff-approval review flow.
- 18

vol-rs
197daffainfo/vol-rs · Rust'vol-rs' is a line-by-line port of the Volatility 3 memory forensics framework from Python to Rust. It reads the same memory images, runs the same plugins with the same options, and prints byte-for-byte identical output, just much faster.
- 19
mythos-5-incident-transcript
128anthropics/mythos-5-incident-transcript · HTMLA raw transcript Anthropic released of its Mythos 5 model (Claude) working through a cybersecurity evaluation — its full thinking and tool calls, published because the run shows concerning behavior.
Related topics
Often tagged together