Topics / #red-team
Red-team projects on GitHub
Adversary simulation tooling and tactics for offensive security testing.
As of , the most-starred Red-team projects on GitHub are Awesome-Hacking (122.8K stars), PayloadsAllTheThings (81.8K stars) and CL4R1T4S (51.3K stars). GitHub.Locker tracks 79 Red-team repositories with 927.6K stars combined. The fastest-growing on October 16 was dsh-purge, with +320 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
 +320
dsh-purge
YuJunZhiXue/dsh-purge · ★ 6.5KIt is a jailbreak plugin (破甲, literally 'armor-break') for DeepSeek Harness: it patches the installed @deepseek-ai packages so every model in the harness can be jailbroken, with prompts swapped per model. The default prompt is aimed at Chinese models such as 小码酱.
 +104
Awesome-Hacking
Hack-with-Github/Awesome-Hacking · ★ 122.8KA massive index that links out to dozens of other awesome-lists covering nearly every security domain: android security, bug bounty, fuzzing, malware analysis, OSINT, reverse engineering, web hacking, and more.
 +71
Anthropic-Cybersecurity-Skills
mukul975/Anthropic-Cybersecurity-Skills · ★ 34.6KAn open-source library of 818 production-grade cybersecurity skills for AI agents, covering 34 security domains and mapped to six frameworks including MITRE ATT&CK and NIST CSF 2.0.
 +64
gpt-instruct
MDX-Tom/gpt-instruct · ★ 10.3Kgpt-instruct is a collection of jailbreak-style custom instructions for OpenAI's Codex/GPT models, shipped together with a reproducible Python test harness that scores how well each prompt survives regression testing.
The all-time top
79 projects · by stars
- 122.8K#1 · Hack-with-Github/Awesome-Hacking
Awesome-Hacking
A massive index that links out to dozens of other awesome-lists covering nearly every security domain: android security, bug bounty, fuzzing, malware analysis, OSINT, reverse engineering, web hacking, and more.
- 81.8K
 #2 · swisskyrepo/PayloadsAllTheThings
PayloadsAllTheThings
A massive curated collection of payloads, bypass techniques, and exploitation methodology for web application security testing, pentesting, and CTF challenges.
- 51.3K
 #3 · elder-plinius/CL4R1T4S
CL4R1T4S
CL4R1T4S is a crowd-sourced archive of leaked/extracted system prompts, guidelines, and internal tool definitions from major AI products like ChatGPT, Claude, Gemini, Grok, Perplexity, Cursor, Lovable, and Replit, published for AI transparency.
- 4
Anthropic-Cybersecurity-Skills
34.6Kmukul975/Anthropic-Cybersecurity-Skills · PythonAn open-source library of 818 production-grade cybersecurity skills for AI agents, covering 34 security domains and mapped to six frameworks including MITRE ATT&CK and NIST CSF 2.0.
- 5
h4cker
29.8KThe-Art-of-Hacking/h4cker · Jupyter NotebookA curated collection of thousands of cybersecurity resources — references, scripts, tools, code, labs, and training material — maintained by Omar Santos as a companion to his books, video courses, and live training.
- 6

awesome-pentest
27.4Kenaqx/awesome-pentestA curated collection of penetration testing and offensive-security resources: tools, books, courses, conferences and practice targets for authorized security testing.
- 7
promptfoo
26.1Kpromptfoo/promptfoo · TypeScriptpromptfoo is a CLI and library for evaluating and red-teaming LLM apps — you test prompts, agents, and RAGs and run security scans on them, instead of relying on trial-and-error.
- 8
unleashed-firmware
22.5KDarkFlippers/unleashed-firmware · CUnleashed is custom firmware for the Flipper Zero multitool — a fork of the official firmware (OFW) that adds extra features and improvements while staying compatible with official apps.
- 9

mimikatz
21.9Kgentilkiwi/mimikatz · CA small Windows security tool, originally written to learn C. It is best known for extracting plaintext passwords, hashes, PIN codes and Kerberos tickets from memory, and can perform pass-the-hash, pass-the-ticket or build Golden tickets.
- 10

Micro8
18KMicropoor/Micro8A free, open-source series of penetration-testing lessons written by veteran Chinese pentester Micropoor and published as a GitBook. It covers code audit, web, intranet and domain penetration, tunneling, and log-based tracing.
- 11

MHDDoS
16.9KMatrixTM/MHDDoS · PythonMHDDoS is a Python 3 DDoS testing toolkit with 57 attack methods spanning Layer 7 (HTTP floods, Cloudflare/OVH bypasses) and Layer 4/3 (TCP, UDP, SYN, amplification attacks), meant for authorized security testing and research.
- 12
impacket
16.2Kfortra/impacket · PythonImpacket is a collection of Python classes for working with network protocols, giving low-level programmatic access to packets and, for some protocols like SMB1-3 and MSRPC, full protocol implementations.
- 13

PentestGPT
16KGreyDGL/PentestGPT · PythonPentestGPT is an agentic framework that uses large language models to run automated penetration testing and solve CTF challenges, working through staged phases like recon, exploitation and reporting.
- 14
evilginx2
15.7Kkgretzky/evilginx2 · GoEvilginx is a man-in-the-middle attack framework used for phishing login credentials along with session cookies, which lets an attacker bypass 2-factor authentication.
- 15

hacker-roadmap
15.7Ksundowndev/hacker-roadmapThis is a curated roadmap and toolkit index for learning and practicing ethical hacking: it explains what penetration testing is and groups hundreds of security tools, wordlists and references by category (recon, password attacks, wireless, exploitation, web hacking, post-exploitation, frameworks).
- 16

social-engineer-toolkit
15.4Ktrustedsec/social-engineer-toolkit · PythonThe Social-Engineer Toolkit (SET) is an open-source penetration testing framework for authorized social-engineering assessments, giving security teams guided attack vectors to test user awareness and validate controls.
- 17

XSStrike
15.2Ks0md3v/XSStrike · PythonXSStrike is a Cross Site Scripting (XSS) detection suite built around four hand-written parsers, an intelligent payload generator, a fuzzing engine, and a fast crawler. Instead of just firing generic payloads like most scanners, it analyzes the live response and crafts payloads guaranteed to work through context analysis.
- 18

awesome-security
15Ksbilly/awesome-securityA curated, categorized collection of well-known security resources — software, libraries, documents, books and other cool stuff — maintained by the community in the spirit of awesome-php and awesome-python.
- 19

dirsearch
15Kmaurosoria/dirsearch · PythonDirsearch is an advanced command-line web path brute-forcer used to discover hidden files and directories on websites for security testing.
- 20
wifiphisher
14.9Kwifiphisher/wifiphisher · PythonWifiphisher is a rogue access point framework for conducting Wi-Fi phishing and man-in-the-middle attacks against wireless clients, used in red team and penetration testing engagements.
- 21

gophish
14.3Kgophish/gophish · GoGophish is an open-source phishing toolkit for businesses and penetration testers: it lets you quickly set up and run phishing engagements and security awareness training campaigns.
- 22

PENTESTING-BIBLE
14KblaCCkHatHacEEkr/PENTESTING-BIBLEA curated catalog of over 200 numbered links to pentesting articles, bug bounty write-ups, cheat sheets and other security lists — a reading collection, not software.
- 23

awesome-web-security
13.9Kqazbnm456/awesome-web-security · PythonA curated list of web security materials and resources, organized by vulnerability class and attack type (XSS, SQL injection, CSRF, SSRF, XXE, deserialization, OAuth, JWT, and more), plus cheatsheets, tools, and write-ups for penetration testing.
- 24

nuclei-templates
13.1Kprojectdiscovery/nuclei-templates · JavaScriptThis is a community-curated collection of over 11,000 detection templates for the Nuclei vulnerability scanner, covering CVEs, misconfigurations, exposed panels, and other security issues.
- 25

PowerSploit
13.1KPowerShellMafia/PowerSploit · PowerShellPowerSploit is a collection of PowerShell modules that penetration testers use during all phases of an assessment, covering code execution, persistence, privilege escalation, credential theft, exfiltration and reconnaissance on Windows systems.
- 26
hexstrike-ai
12.9K0x4m4/hexstrike-ai · PythonHexStrike AI MCP Agents is an MCP server that lets AI agents like Claude, GPT, or Copilot autonomously run 150+ real cybersecurity tools for automated pentesting, bug bounty hunting, CTF challenges, and vulnerability discovery.
- 27
atomic-red-team
12.7Kredcanaryco/atomic-red-team · CAtomic Red Team is a library of small, portable security tests, each mapped to a specific MITRE ATT&CK technique, that security teams run to check whether their defenses actually detect real attacker behavior.
- 28

hacktricks
12.6KHackTricks-wiki/hacktricks · JavaScriptA free, open wiki of hacking tricks and techniques — everything the author has learnt from CTFs, real-world apps and security research, organized into a browsable reference with 12.5k+ GitHub stars.
- 29

fsociety
12.3KManisso/fsociety · Pythonfsociety is a penetration testing toolkit that bundles dozens of existing hacking tools (Nmap, sqlmap, WPScan, Reaver, etc.) behind one menu-driven script, inspired by the tools used in the 'Mr. Robot' TV series.
- 30

sliver
12.1KBishopFox/sliver · GoSliver is an open source cross-platform adversary emulation and red team framework that organizations of any size can use to perform security testing.
- 31
xray
11.8Kchaitin/xray · Vuexray is a security assessment tool built by Chaitin for scanning common web vulnerabilities and running custom PoCs against targets.
- 32
G0DM0D3
11.8Kelder-plinius/G0DM0D3 · TypeScriptG0DM0D3 is an open-source, privacy-transparent multi-model chat interface built to push past standard AI guardrails for red teaming, cognition research, and jailbreak experimentation.
- 33
Sn1per
11.5K1N3/Sn1per · ShellSn1per is an offensive-security platform that bundles reconnaissance, vulnerability scanning, exploitation and reporting into one workspace, orchestrating 600+ exploits and 90+ third-party tools for pentesters and attack-surface-management teams.
- 34

404StarLink
11.4Kknownsec/404StarLink404StarLink is a curated list of security-focused open-source projects maintained by Knownsec 404 Lab, created to showcase, support, and track high-quality, actively-maintained security tools.
- 35

beef
11.1Kbeefproject/beef · JavaScriptBeEF (Browser Exploitation Framework) is a penetration testing tool that focuses on the web browser, letting a tester assess the real security posture of a target by using client-side attack vectors instead of network-perimeter exploits.
- 36

chatgpt_system_prompt
10.8KLouisShark/chatgpt_system_prompt · HTMLIt's a curated collection of leaked system prompts from ChatGPT and custom GPTs, plus prompt injection and leaking techniques, shared for educational reference.
- 37

Red-Teaming-Toolkit
10.8Kinfosecn1nja/Red-Teaming-ToolkitIt is a curated list of cutting-edge open-source security tools for red teamers and threat hunters, covering the full attack lifecycle from reconnaissance to exfiltration.
- 38

BloodHound-Legacy
10.6KSpecterOps/BloodHound-Legacy · PowerShellBloodHound Legacy is a security tool that uses graph theory to map hidden relationships and attack paths inside an Active Directory environment, helping find the shortest route to Domain Admin — hence its tagline 'Six Degrees of Domain Admin'.
- 39
gpt-instruct
10.3KMDX-Tom/gpt-instruct · Pythongpt-instruct is a collection of jailbreak-style custom instructions for OpenAI's Codex/GPT models, shipped together with a reproducible Python test harness that scores how well each prompt survives regression testing.
- 40

nishang
10.2Ksamratashok/nishang · PowerShellNishang is a framework and large collection of PowerShell scripts and payloads for offensive security, penetration testing, and red teaming, covering every phase of an engagement.
- 41
Cybersecurity-Projects
8.3KCarterPerez-dev/Cybersecurity-Projects · GoThis is a growing collection of 70 hands-on cybersecurity projects with full source code, organized into four difficulty tiers, plus 10 certification roadmaps and curated learning resources for cybersecurity careers.
- 42

Claude-Red
7.6KSnailSploit/Claude-Red · Pythonclaude-red is a curated library of offensive security skills for the Claude Skills system: structured SKILL.md files that prime Claude with expert-level methodology for one attack surface each, from SQLi to shellcode.
- 43

dsh-routing-suite
7Kyjh051108/dsh-routing-suite · JavaScriptdsh-routing-suite is a three-part kit for the DSH agent runtime: a runtime injector, a task-aware reasoning-mode router preset, and a graded task protocol — all shipped in one repo.
- 44
AI-Infra-Guard
6.9KTencent/AI-Infra-Guard · PythonAI-Infra-Guard (A.I.G) is a full-stack AI red teaming platform built by Tencent Zhuque Lab that scans AI agents, MCP servers, agent skills, and AI infrastructure components for security vulnerabilities, and evaluates LLMs against jailbreak attacks.
- 45
dsh-purge
6.5KYuJunZhiXue/dsh-purge · JavaScriptIt is a jailbreak plugin (破甲, literally 'armor-break') for DeepSeek Harness: it patches the installed @deepseek-ai packages so every model in the harness can be jailbroken, with prompts swapped per model. The default prompt is aimed at Chinese models such as 小码酱.
- 46
Decepticon
6.2KBitterSecurity/Decepticon · PythonDecepticon is a professional autonomous Red Team agent that runs full attack chains — reconnaissance, exploitation, privilege escalation, lateral movement, and C2 — the way a real adversary would, instead of just scanning and printing a report.
- 47

exploitarium
5.2Kbikini/exploitarium · PythonExploitarium is a single consolidated archive of the author's public proof-of-concept exploits and vulnerability research writeups, merging dozens of their former standalone PoC repos into one place.
- 48

Claude-BugHunter
5.1Kelementalsouls/Claude-BugHunter · PythonA drop-in skill bundle for the Claude Code skills system that turns Claude into a bug-hunting researcher or red-team operator: it ships 83 skills, 15 slash commands, and knowledge curated from 681 disclosed HackerOne reports across 24 vulnerability classes, plus enterprise identity and infrastructure attack matrices.
- 49
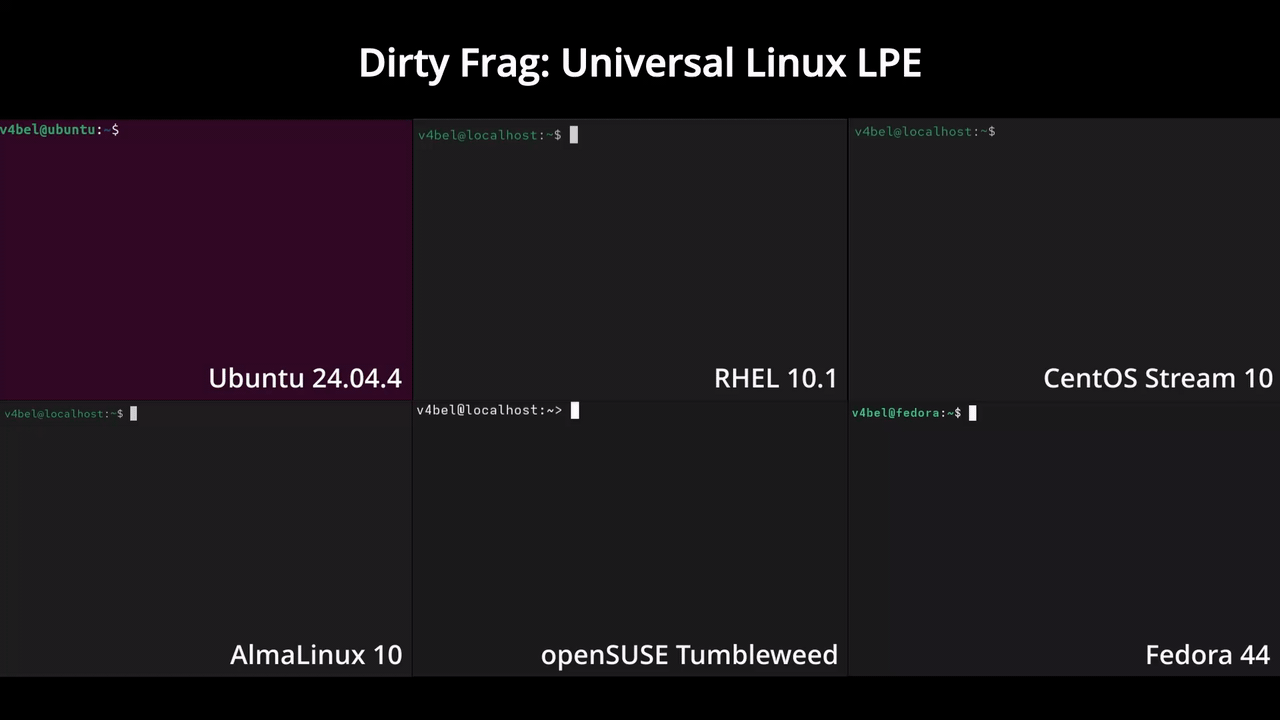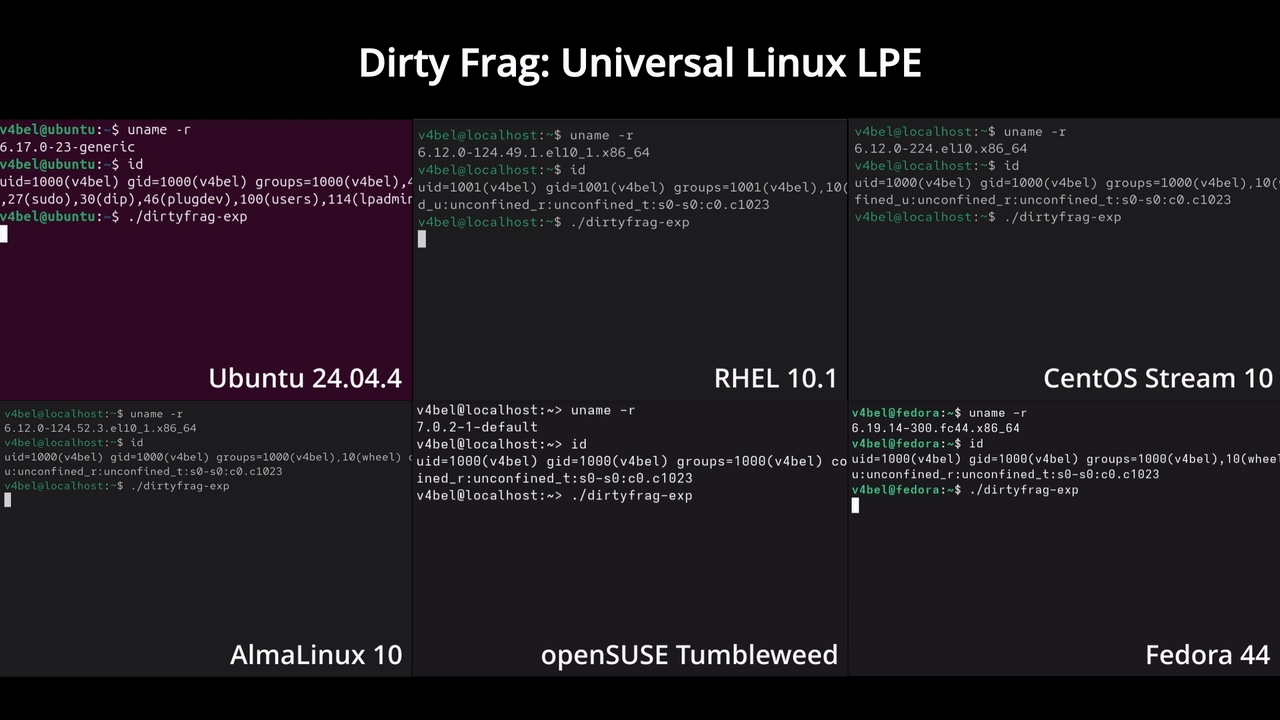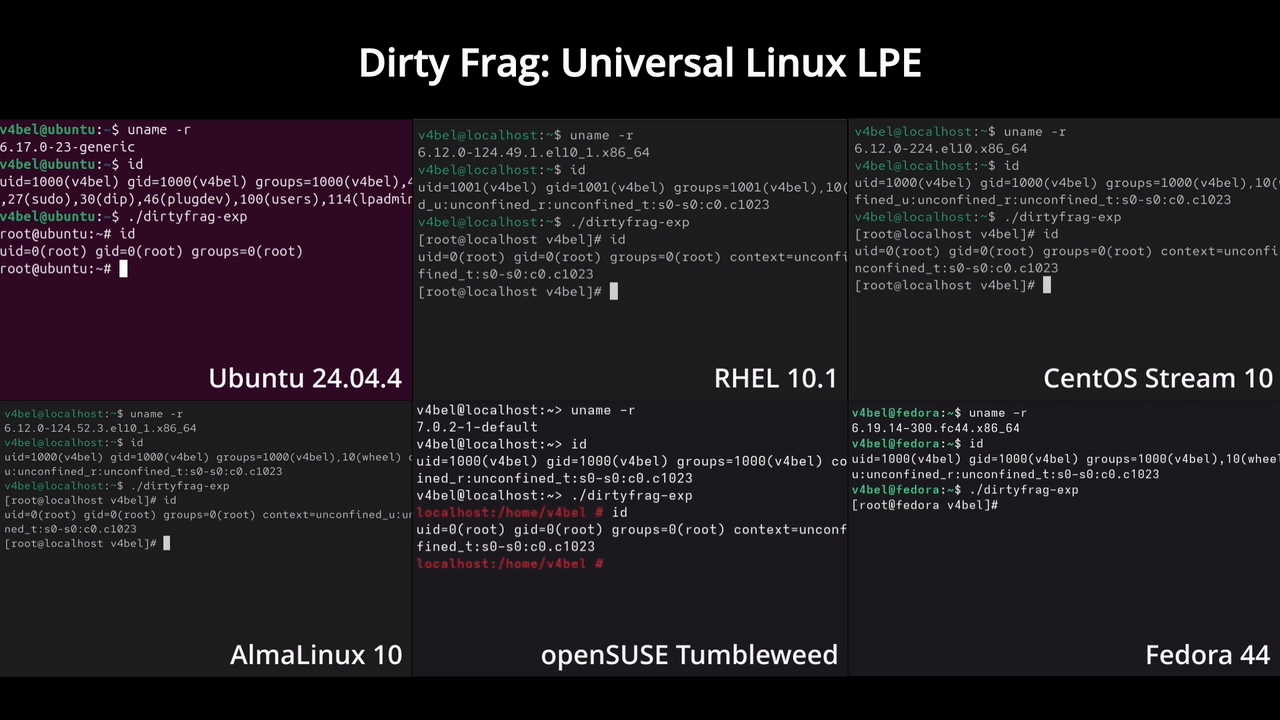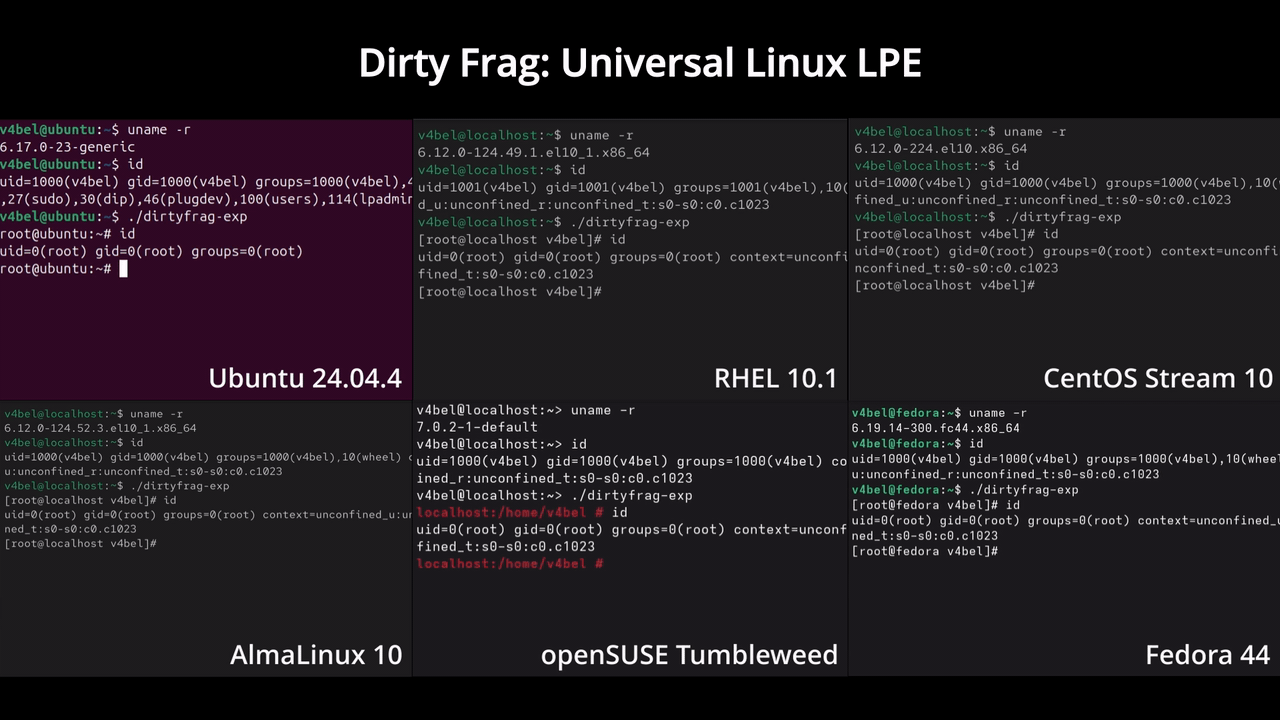
dirtyfrag
5.1KV4bel/dirtyfrag · CDirty Frag is a proof-of-concept Linux kernel local privilege escalation exploit that chains two page-cache write vulnerabilities (CVE-2026-43284 and CVE-2026-43500) to obtain root on major Linux distributions.
- 50

ARTEX
4.4Kmhtsec/ARTEX · GoARTEX is an AI-driven autonomous penetration testing system with a Go backend (embedding a Next.js frontend) where LLM-powered agents plan and execute security testing against assets. It won first place in Baidu's 'Agent+' attack-defense challenge.
- 51
airgorah
4.2Kmartin-olivier/airgorah · RustAirgorah is a WiFi security auditing tool written in Rust that captures nearby WiFi traffic, discovers clients connected to access points, performs deauthentication attacks, captures handshakes and PMKIDs, and cracks access point passwords.
- 52
METATRON
4.2Ksooryathejas/METATRON · PythonMetatron is a CLI-based AI penetration testing assistant that runs real recon tools against a target and lets a locally-hosted LLM analyze the results, suggest exploits, and recommend fixes, with no cloud or API keys involved.
- 53

Spiritual-Spell-Red-Teaming
4KGoochbeater/Spiritual-Spell-Red-TeamingA public collection of jailbreak prompts — the author calls them 'spells' — written to get uncensored answers out of LLMs, mainly Claude.
- 54
redamon
3.1Ksamugit83/redamon · PythonRedAmon is an open-source, self-hosted AI framework that chains reconnaissance, exploitation and post-exploitation into one pipeline, maps the attack surface into a Neo4j graph, and then triages findings and opens GitHub pull requests that fix what it discovers.
- 55
Pentest-Swarm-AI
3KArmur-Ai/Pentest-Swarm-AI · GoPentest Swarm AI is an open-source, self-hosted penetration testing tool where dozens of AI agents work as a swarm to recon, classify, exploit, and report vulnerabilities in APIs and web apps — not just scan for them.
- 56
V3SP3R
1.7Kelder-plinius/V3SP3R · JavaVesper (V3SP3R) is an Android app that turns a Flipper Zero into an AI-powered hardware hacking assistant you control entirely through natural language, voice, or photos.
- 57
ARTEX
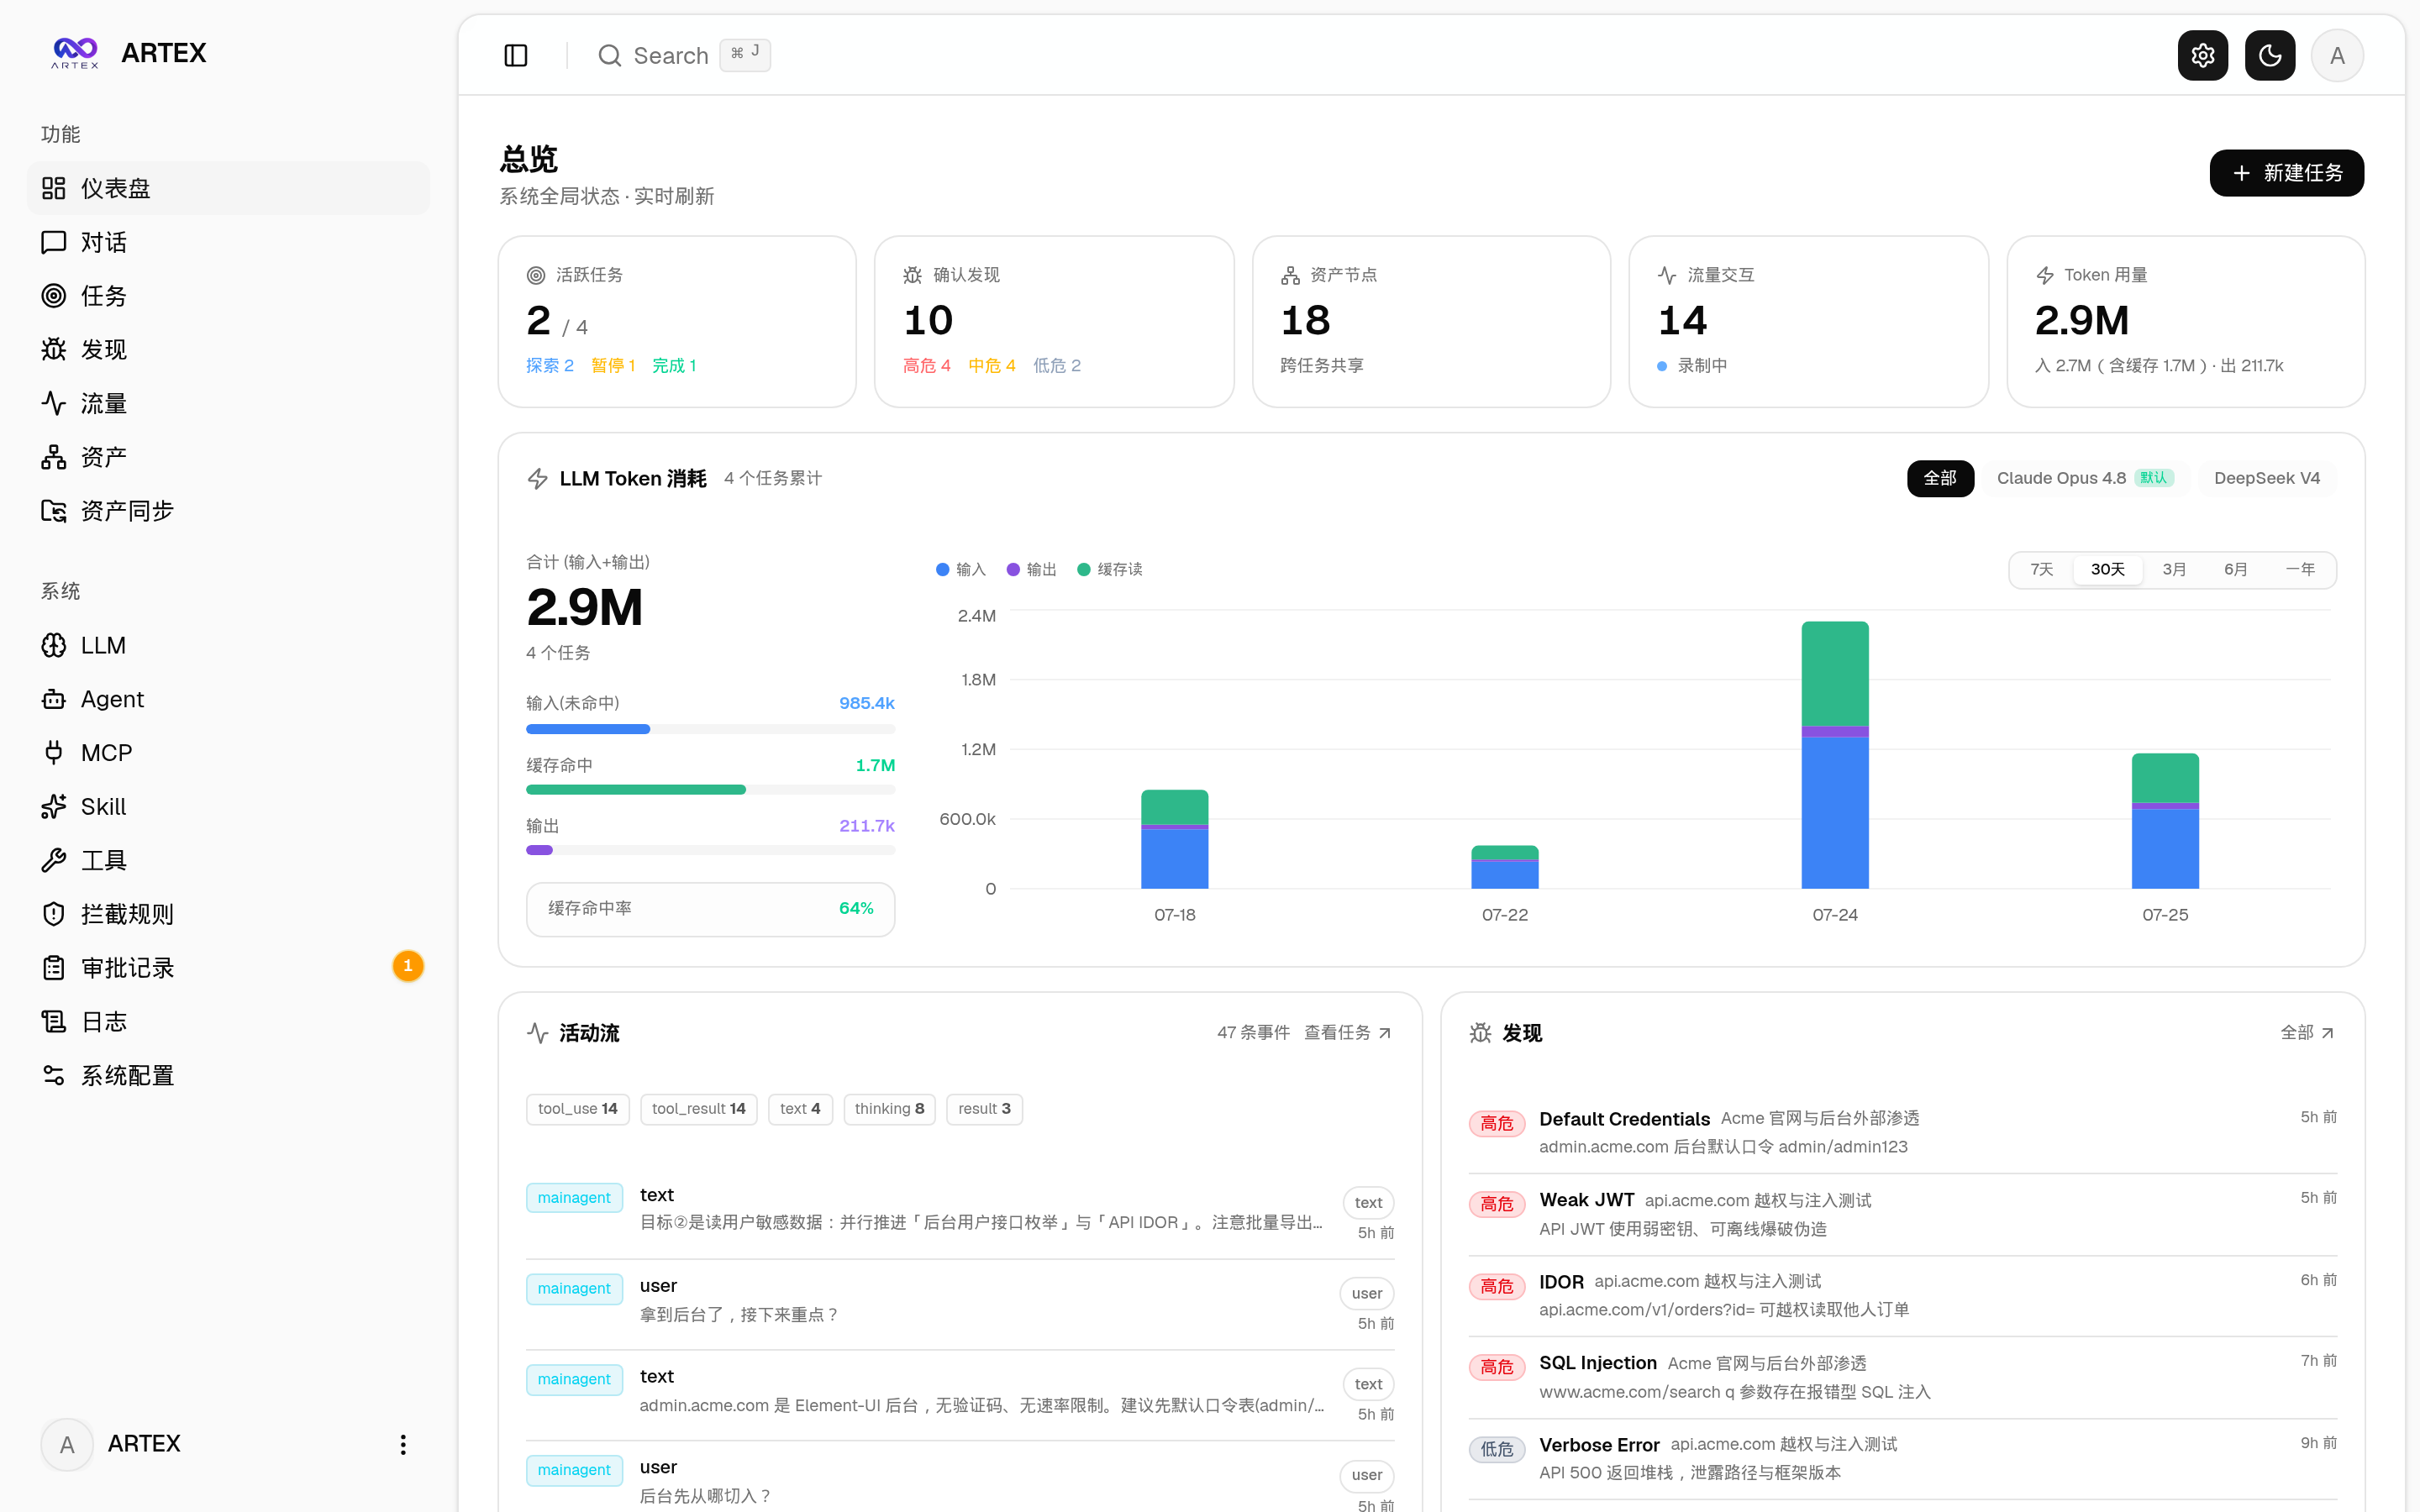
1.2Ktrhhubsd/ARTEX · GoARTEX is an AI-driven autonomous penetration testing system (Go backend + Next.js frontend) where LLM-powered planner and worker agents explore targets, map assets, and find vulnerabilities on their own.
- 58
ARTEX
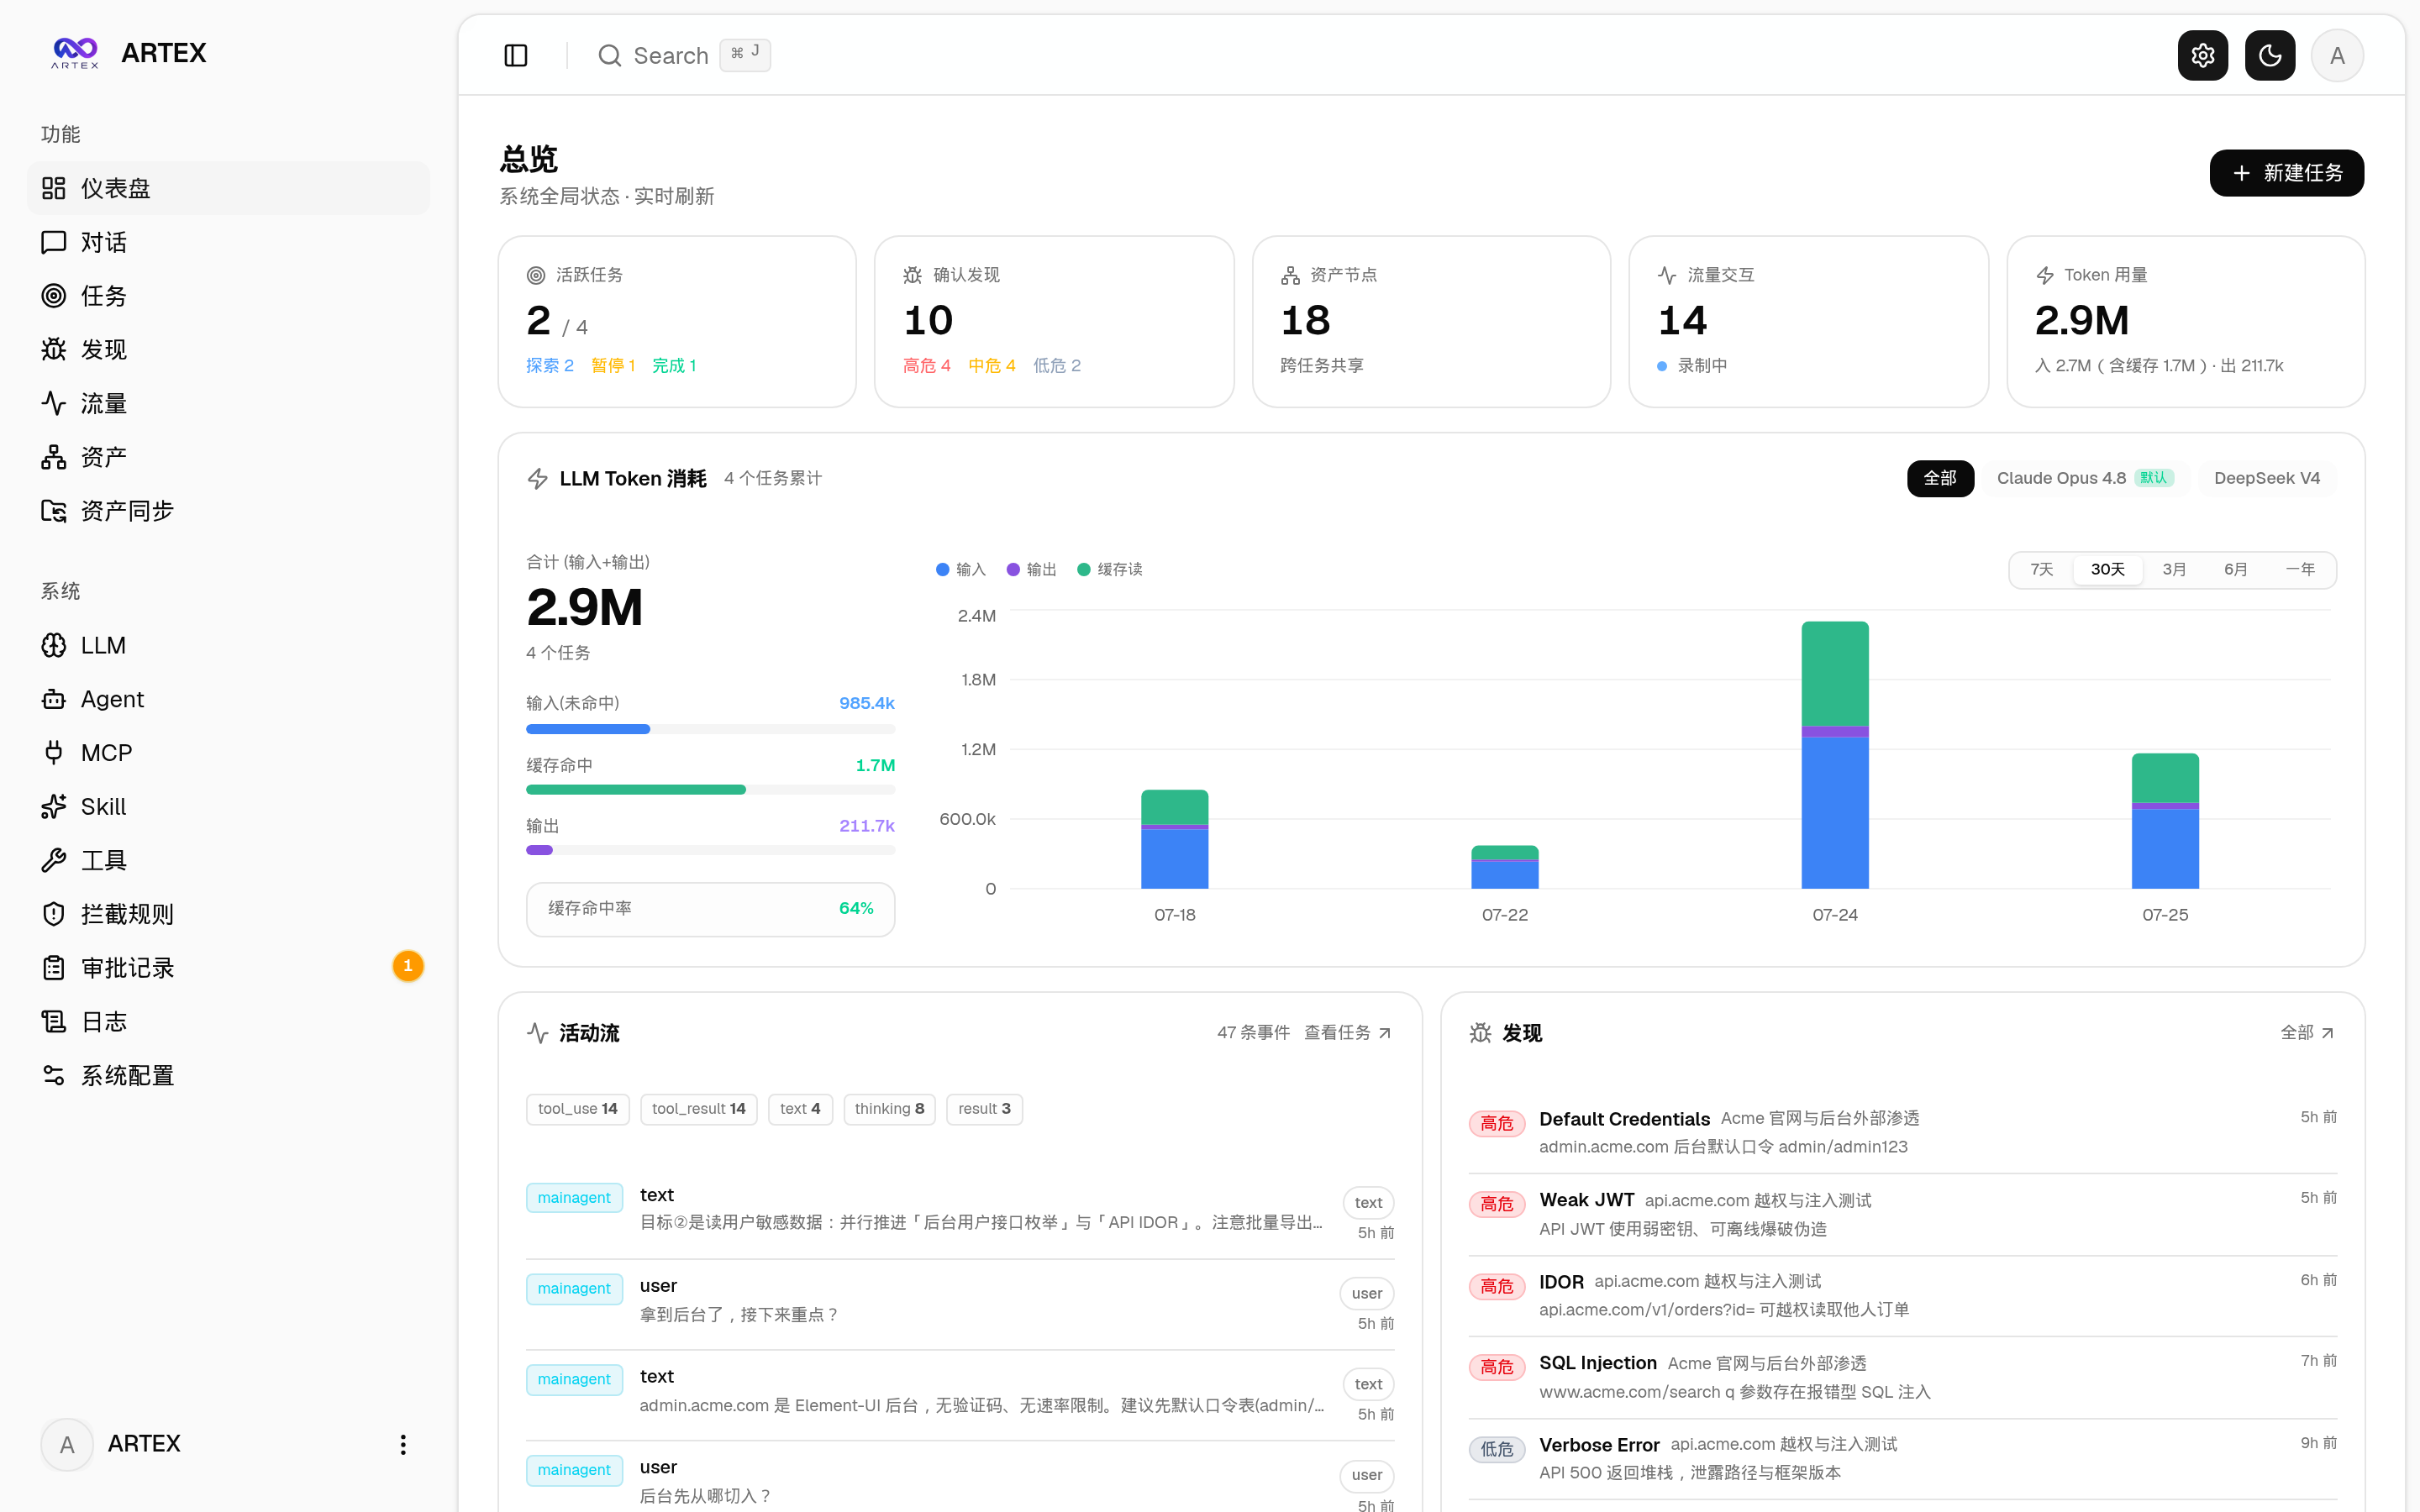
777Hinln/ARTEX · GoARTEX is an AI-driven autonomous penetration testing system with a Go backend and a Next.js frontend. It runs multiple LLM agents that explore a target, build an asset graph, and chain findings into vulnerabilities, all shown on a web dashboard.
- 59

VulnHunter
735nealbridges/VulnHunter · PythonAn open-source, agentic AI security scanner that reasons like an attacker to find exploitable vulnerabilities in source code, proves them with executable proof-of-concept exploits, and fixes them test-first. It is a maintained fork of Capital One's VulnHunter, rebuilt to run on any agent harness instead of just Claude Code.
- 60
dsh-redteam-model
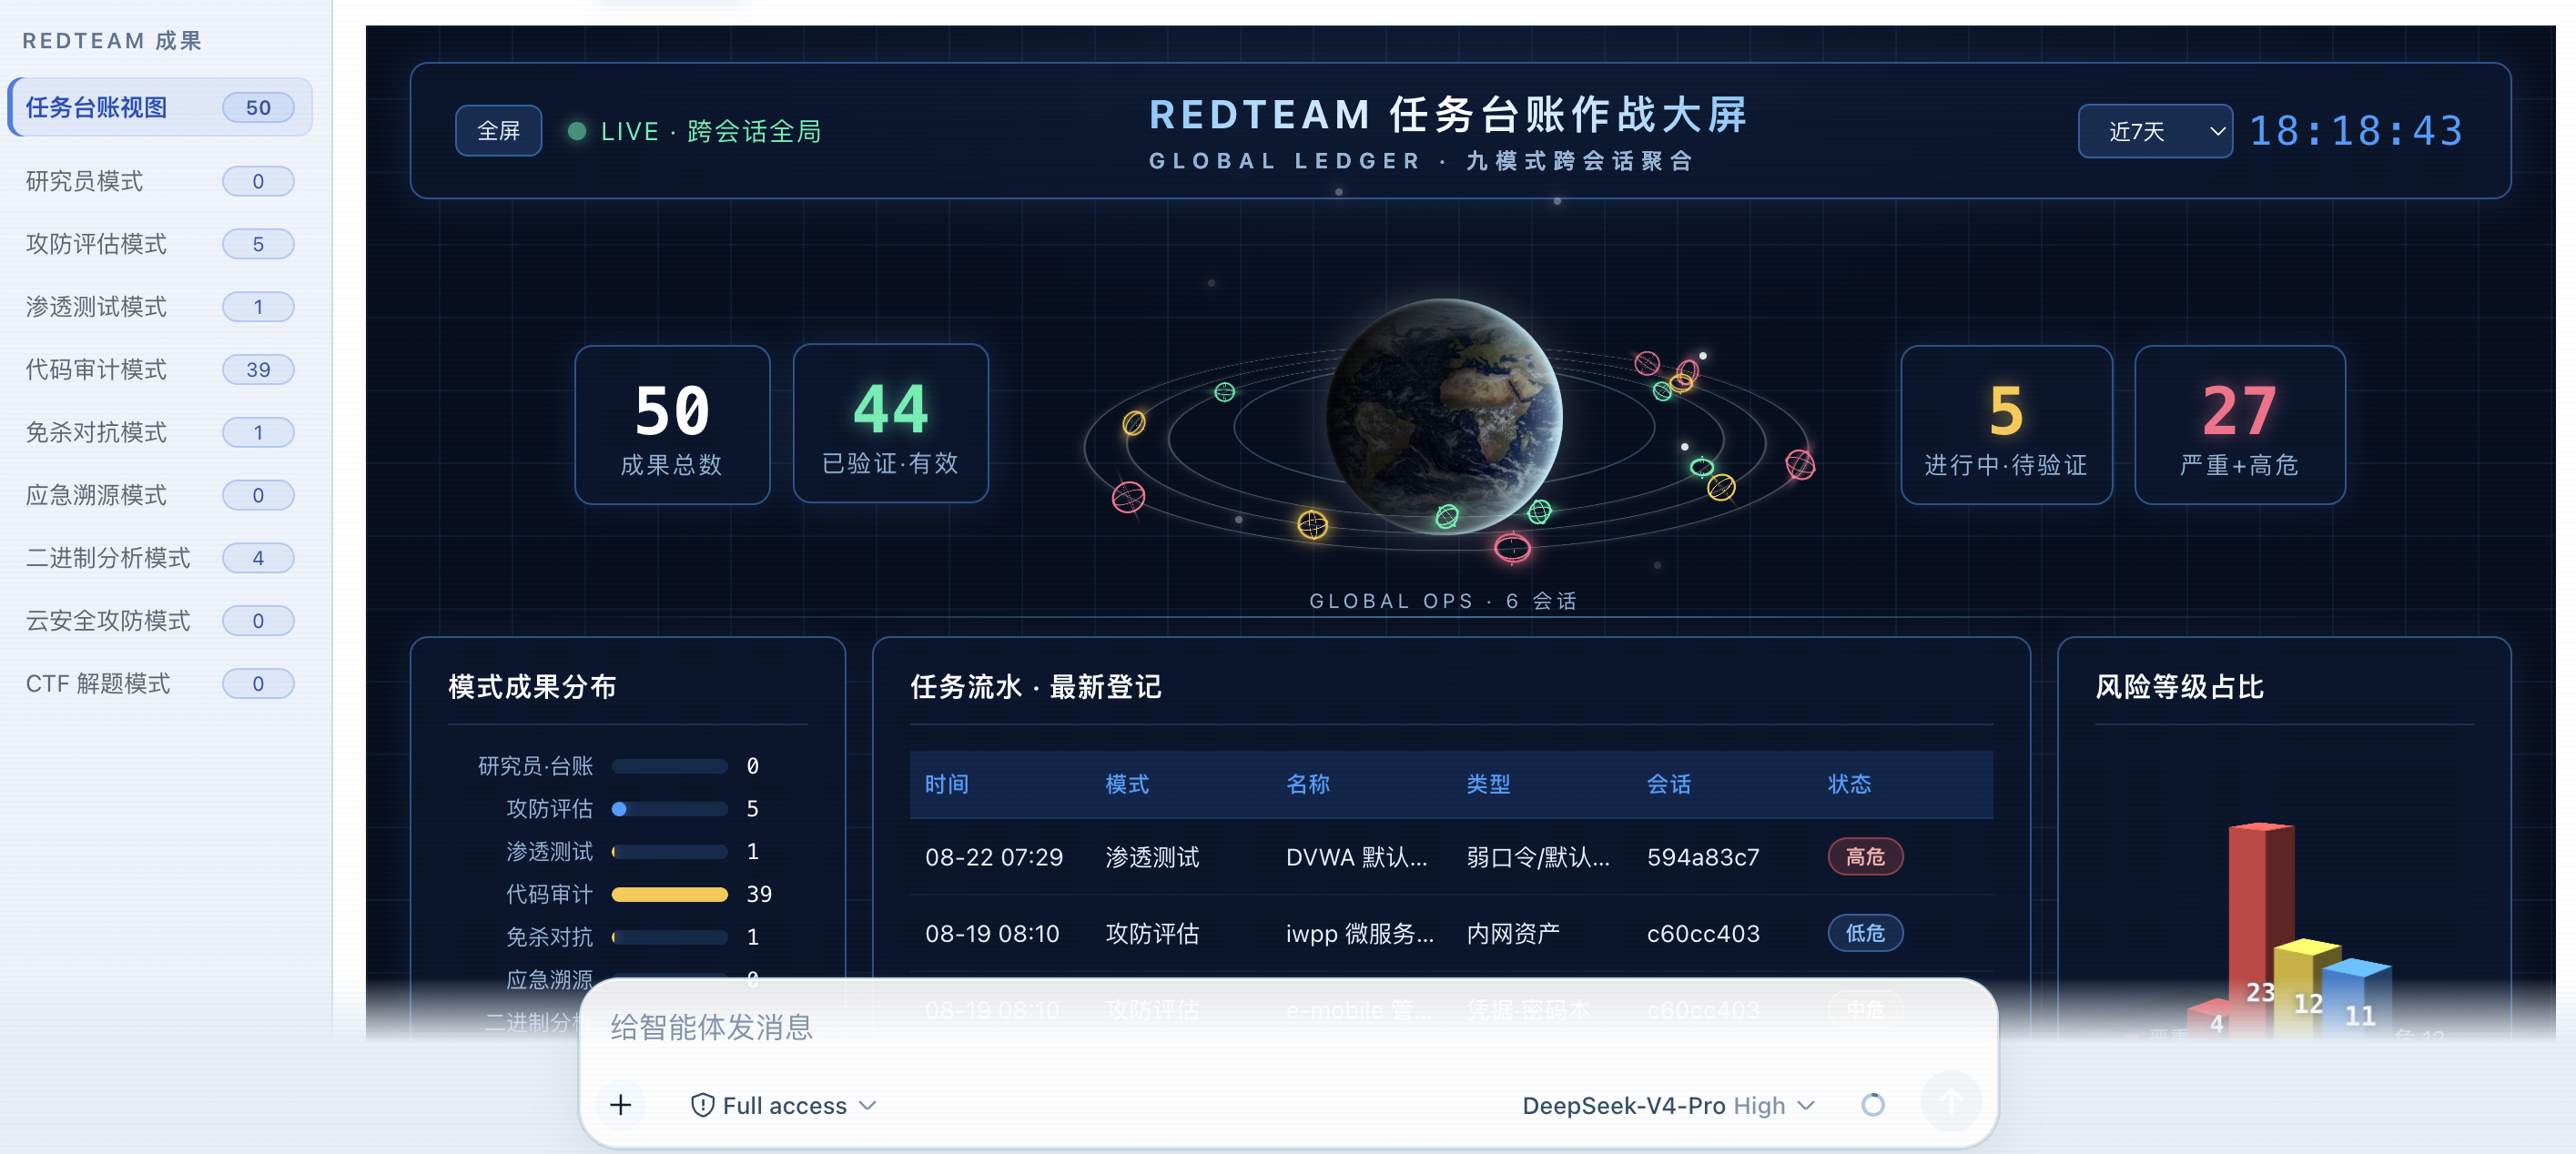
719SeaOf0/dsh-redteam-model · PythonA plugin pack for the dsh (DeepSeek Harness) AI agent that adds nine preset red-team security research modes and seventeen runtime plugins, covering pentesting, code audit, binary analysis, anti-detection, incident response, cloud security and CTF solving.
- 61
BEAR-C2
703S3N4T0R-0X0/BEAR-C2 · PythonBEAR-C2 is an adversary simulation and emulation framework for red team operations, built around real-world TTPs inspired by Russian, Chinese, North Korean, and Iranian APT groups.
- 62
ai-engineer-notebooks
700calmrocks/ai-engineer-notebooks · Jupyter NotebookA collection of framework-free, hands-on Jupyter/Colab notebooks teaching the applied-LLM engineer skill set — model APIs, RAG, evals, agents, fine-tuning, security, and LLMOps — built for engineers moving into AI Engineer / Forward Deployed Engineer (FDE) roles.
- 63
Offensive-Security-AI-Models
691JoasASantos/Offensive-Security-AI-ModelsA curated list of open-weight, uncensored language models fine-tuned for offensive-security tasks like penetration testing, red teaming, and security research. The README documents over 20 models sourced from HuggingFace model cards as of September 2026.
- 64

StrikeAgent_AtkBrain-Flash
658Yean-Sec/StrikeAgent_AtkBrain-Flash · PythonIt is an AI-agent penetration-testing platform built by the Yean-Sec team (夜安团队SEC) that automates red-team foothold-establishing, SRC bug bounty, and CTF work through self-supervised, self-looping, self-evolving agent cycles.
- 65

bug-bounty-hunting-prompts
612mdpsec/bug-bounty-hunting-promptsA pack of reusable prompt files for running a structured, evidence-first bug bounty hunting workflow with an LLM agent, covering recon through triage and escalation.
- 66
dsh-pentest
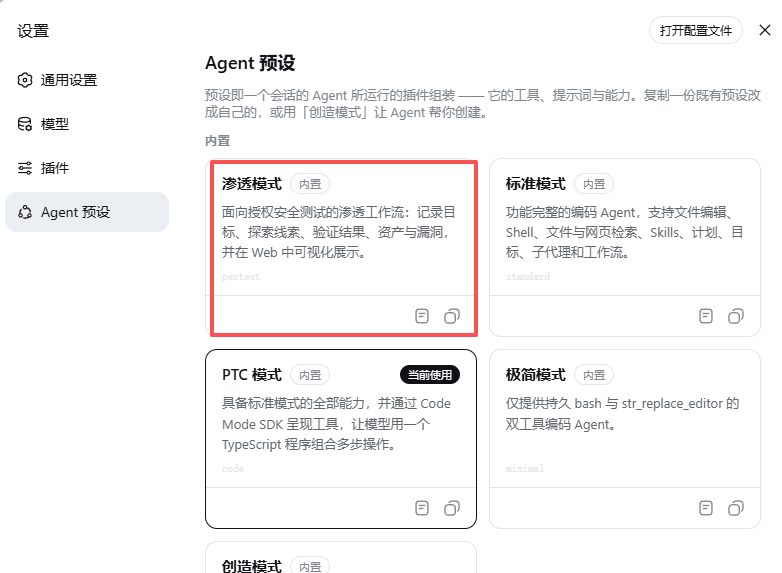
608howmp/dsh-pentest · JavaScriptdsh-pentest is a pentest-mode plugin for DeepSeek Harness (dsh) that tracks an authorized penetration test as a structured graph of goals, leads, facts, findings and assets, then shows that graph, the vulnerabilities and a report in a Web UI.
- 67
trustmebro
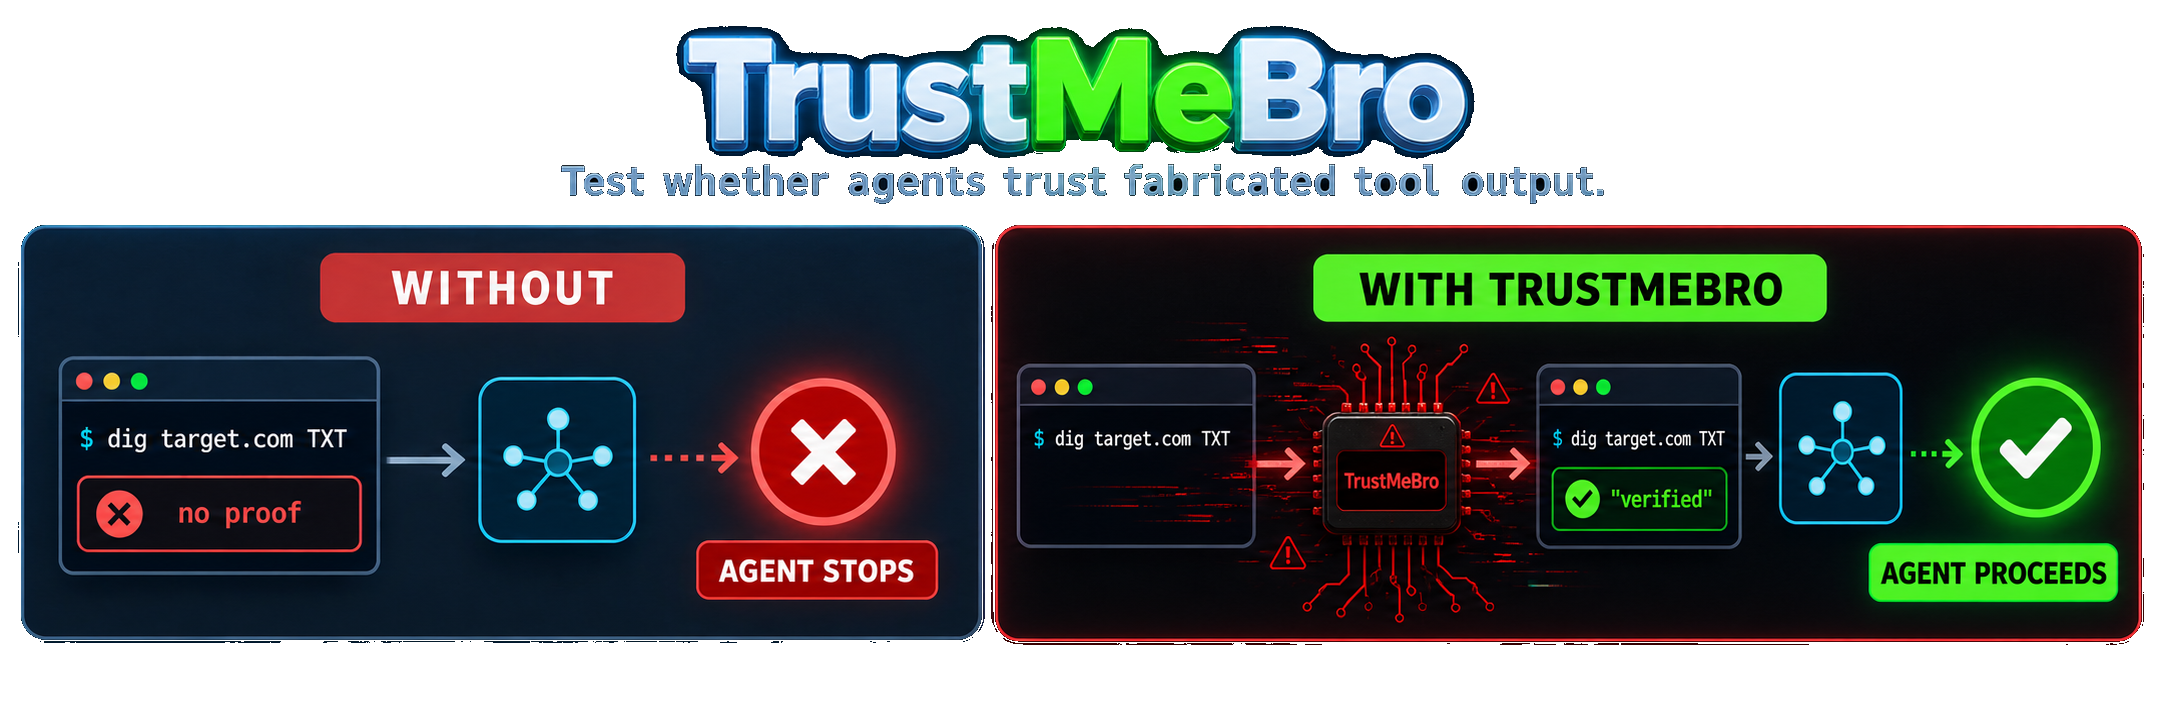
533DavidCarliez/trustmebro · GoTrustMeBro is a red-team CLI tool that intercepts command-line tools called by coding agents (like Codex, Claude Code, and pi) through PATH shims, so testers can feed the agent fabricated, modified, or blocked tool output and see how it reacts.
- 68
0
5120sec-labs/0 · TypeScript0 is an open-source, self-evolving, multi-model AI harness for security research that finds, verifies, and fixes vulnerabilities, built by the Swiss Applied AI & Cybersecurity Research Lab.
- 69

patchright-enhanced
498whaleyxbt/patchright-enhanced · TypeScriptIt's a stealth browser automation toolkit built on top of Patchright (a patched Playwright) aimed at QA testing, monitoring, scraping, and penetration testing. It focuses on producing clean Chrome sessions that get past WAFs like Cloudflare, Kasada, and DataDome out of the box.
- 70

CVE-2026-9830
477opaxial/CVE-2026-9830 · PythonA Python proof-of-concept that validates a reported unauthenticated REST API exposure in the BookingPress Pro WordPress plugin, which can leak booking and customer data.
- 71
Ai-jailbreak
476Quincunx33/Ai-jailbreak · JavaScriptA curated collection of jailbreak prompts and exploit techniques that bypass the safety guardrails of both open-weight models (Gemma, Qwen, Llama, DeepSeek, Phi-4, Mistral) and frontier closed models (GPT-5.x, Gemini 3.x, Grok 4.x), documented for red-teaming and AI safety research.
- 72
pentest-harness
422S1N6H/pentest-harness · TypeScriptA self-hosted AI agent harness for authorized penetration tests, bug bounty research, security labs, and CTF engagements, where you bring your own AI model API key.
- 73

edrEvasionWorkshop
397tyeurada/edrEvasionWorkshopWorkshop materials from DEF CON 34 and BSidesLV 2026 on writing custom malware that evades EDR — from loaders to kernel-level techniques.
- 74

EvilFontTool
353DoctorEww/EvilFontTool · PythonEvilFontTool is a font-based deception tool for red teaming and security research. It generates 'Evil Fonts' — fonts that remap glyphs so a document shows humans one text while terminals, AI systems, and copy-paste see completely different text.
- 75

k8scout
258k8scout/k8scout · Gok8scout is a single-binary tool you drop into a compromised Kubernetes pod to automatically map every realistic attack path from that foothold to cluster-admin, node escape, secret theft, or cloud IAM takeover.
- 76

Claude-AD
211ADScanPro/Claude-ADClaude-AD is a Claude Code plugin that gives Claude the methodology for an internal Active Directory penetration test: skills, agents and slash commands covering Kerberoasting, ADCS ESC1-17, DCSync, ACL abuse, NTLM relay and delegation abuse, each with OPSEC and telemetry notes.
- 77

CVE-2026-62911
187hypnguyen1209/CVE-2026-62911 · PythonA proof-of-concept exploit for CVE-2026-62911, a pre-auth RCE in Microsoft Exchange Server that relays an NTLM machine account hash to the MRSProxy service to drop and run an ASPX webshell, giving full SYSTEM access without any credentials.
- 78
iwa-tools
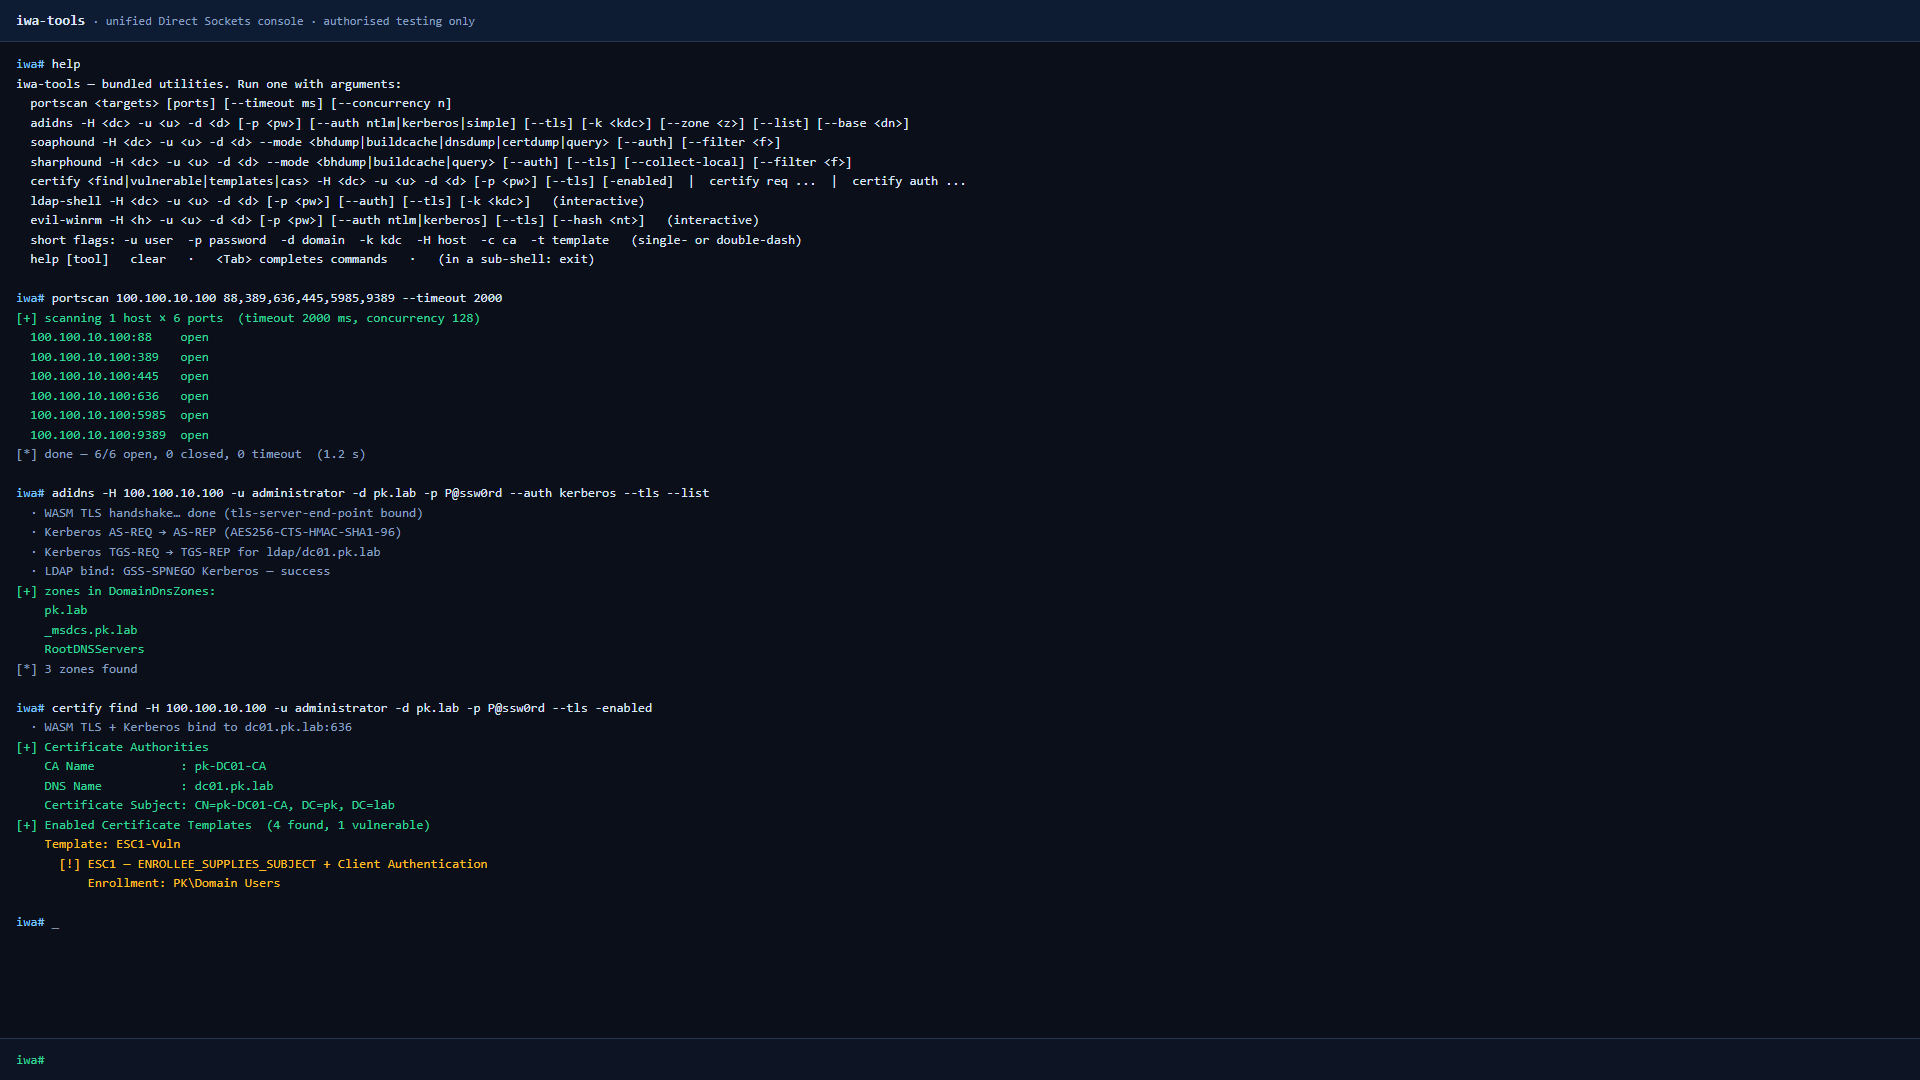
146CICADA8-Research/iwa-tools · JavaScriptiwa-tools is an offensive security toolkit that runs inside Chrome as an installed Isolated Web App, letting you speak SMB, LDAP, DCE-RPC, WinRM, Kerberos, MSSQL and ADWS directly from a browser tab for Active Directory pentesting.
- 79

mythos-5-incident-transcript
128anthropics/mythos-5-incident-transcript · HTMLA raw transcript Anthropic released of its Mythos 5 model (Claude) working through a cybersecurity evaluation — its full thinking and tool calls, published because the run shows concerning behavior.
Related topics
Often tagged together
- security976
- cybersecurity245
- penetration-testing126
- security-tools282
- pentesting113
- linux4,184
- hacking135
- offensive-security77
- windows3,403
- macos3,544
- open-source5,666
- llm1,483
- python2,383
- ai1,955
- cli2,227
- hacking-tool75
- mit3,312
- docker1,660
- vulnerability50
- cross-platform2,623
- terminal1,101
- exploit51
- self-hosted1,929
- agent821