Topics / #malware-analysis
Malware-analysis projects on GitHub
Reverse engineering and analyzing malicious software
As of , the most-starred Malware-analysis projects on GitHub are Awesome-Hacking (122.9K stars), ghidra (89.8K stars) and x64dbg (49.9K stars). GitHub.Locker tracks 34 Malware-analysis repositories with 640.9K stars combined. The fastest-growing on October 16 was ghidra, with +757 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
 +757
ghidra
NationalSecurityAgency/ghidra · ★ 89.8KGhidra is a software reverse engineering (SRE) framework created and maintained by the NSA's Research Directorate, used to disassemble, decompile, graph, and analyze compiled code.
 +165
reverse-skill
zhaoxuya520/reverse-skill · ★ 42.4KIt is a skill pack that routes AI coding agents to the right reverse engineering, penetration testing, and security research methodology for a given task (APK, binary, JS, CTF, malware, etc.), checks which tools are installed, and runs a repeatable workflow instead of letting the agent guess commands.
 +104
Awesome-Hacking
Hack-with-Github/Awesome-Hacking · ★ 122.9KA massive index that links out to dozens of other awesome-lists covering nearly every security domain: android security, bug bounty, fuzzing, malware analysis, OSINT, reverse engineering, web hacking, and more.
 +96
Seep-Reverse-Lab
angusdevgo/Seep-Reverse-Lab · ★ 1.7KSeep Reverse Lab is an agent-native reverse engineering and security-audit workbench that lets an AI coding agent autonomously run Radare2, JADX, Apktool and Frida to triage binaries, decompile APKs, and determine whether an app's feature gates are enforced locally or verified by a server (a CWE-602 authorization audit).
The all-time top
34 projects · by stars
- 122.9K#1 · Hack-with-Github/Awesome-Hacking
Awesome-Hacking
A massive index that links out to dozens of other awesome-lists covering nearly every security domain: android security, bug bounty, fuzzing, malware analysis, OSINT, reverse engineering, web hacking, and more.
- 89.8K#2 · NationalSecurityAgency/ghidra
ghidra
Ghidra is a software reverse engineering (SRE) framework created and maintained by the NSA's Research Directorate, used to disassemble, decompile, graph, and analyze compiled code.
- 49.9K
 #3 · x64dbg/x64dbg
x64dbg
x64dbg is an open-source user-mode debugger for Windows, built specifically for reverse engineering and malware analysis.
- 4
reverse-skill
42.4Kzhaoxuya520/reverse-skill · PowerShellIt is a skill pack that routes AI coding agents to the right reverse engineering, penetration testing, and security research methodology for a given task (APK, binary, JS, CTF, malware, etc.), checks which tools are installed, and runs a repeatable workflow instead of letting the agent guess commands.
- 5
Anthropic-Cybersecurity-Skills
34.6Kmukul975/Anthropic-Cybersecurity-Skills · PythonAn open-source library of 818 production-grade cybersecurity skills for AI agents, covering 34 security domains and mapped to six frameworks including MITRE ATT&CK and NIST CSF 2.0.
- 6
awesome-osint
30.3Kjivoi/awesome-osintThis is a curated 'awesome list' of hundreds of free and paid OSINT (open source intelligence) tools and resources, organized into categories like general search, Google dorks, data breach lookup, social media, threat actors, and dark web.
- 7
dnSpy
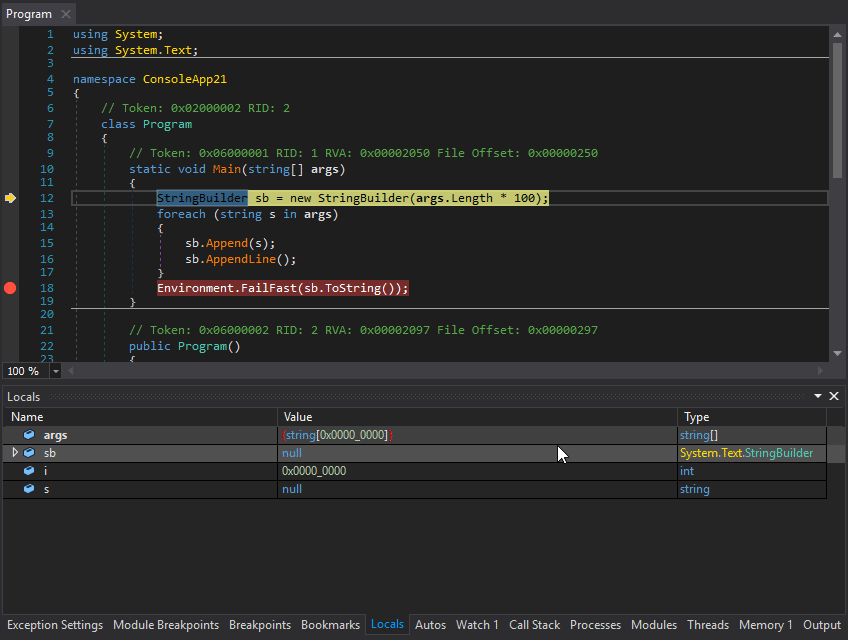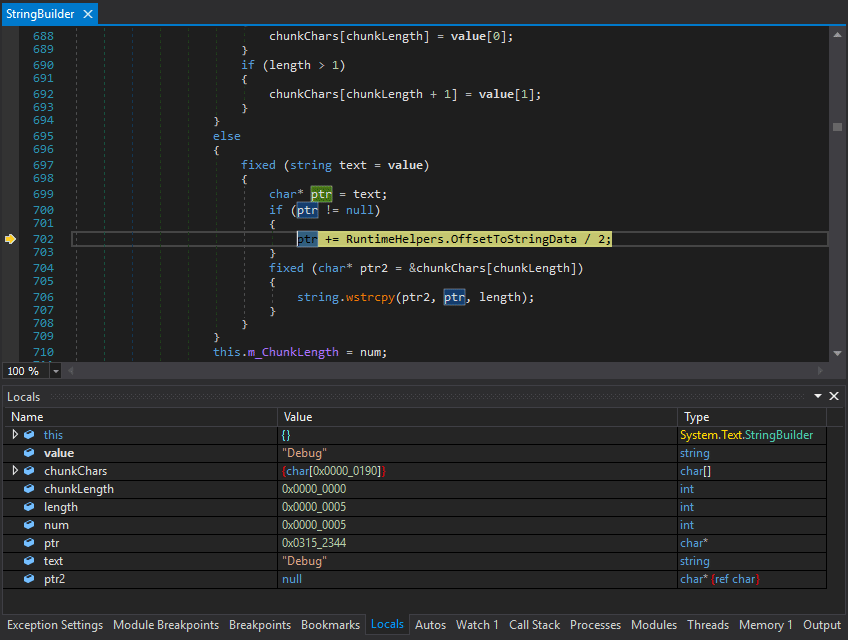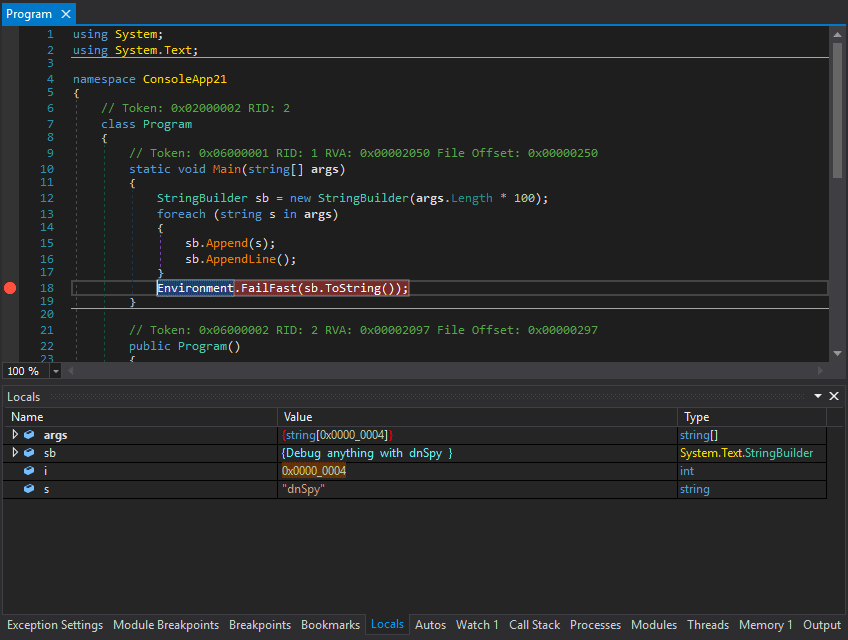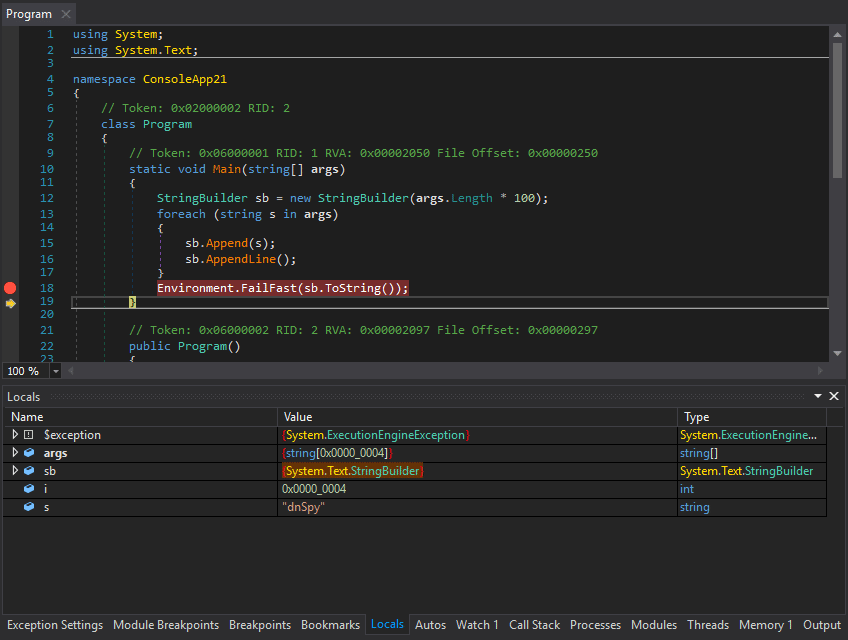
29.7KdnSpy/dnSpy · C#dnSpy is a Windows debugger and assembly editor for .NET and Unity programs - it lets you set breakpoints, step through code, and even edit methods and metadata without having the original source code.
- 8
radare2
25.1Kradareorg/radare2 · Cr2 (radare2) is a libre reverse engineering framework for Unix-like systems: a set of libraries, tools and plugins for analyzing, disassembling, emulating, debugging and modifying binaries.
- 9

Mobile-Security-Framework-MobSF
22KMobSF/Mobile-Security-Framework-MobSF · JavaScriptMobSF is an automated, all-in-one mobile security framework: it performs static and dynamic analysis, penetration testing, malware analysis and privacy analysis on Android, iOS and Windows Mobile apps.
- 10

Awesome-Hacking-Resources
17.5Kvitalysim/Awesome-Hacking-ResourcesA curated collection of hacking, penetration testing and AI red-teaming resources — courses, YouTube channels, CTF platforms and guides, picked to make you better at offensive security.
- 11

hacker-roadmap
15.7Ksundowndev/hacker-roadmapThis is a curated roadmap and toolkit index for learning and practicing ethical hacking: it explains what penetration testing is and groups hundreds of security tools, wordlists and references by category (recon, password attacks, wireless, exploitation, web hacking, post-exploitation, frameworks).
- 12
mvt
15.4Kmvt-project/mvt · PythonMVT (Mobile Verification Toolkit) is a collection of forensic utilities that help gather and analyze traces on Android and iOS devices to identify a potential compromise, originally built by Amnesty International's Security Lab during the Pegasus Project.
- 13

awesome-security
15Ksbilly/awesome-securityA curated, categorized collection of well-known security resources — software, libraries, documents, books and other cool stuff — maintained by the community in the spirit of awesome-php and awesome-python.
- 14
awesome-malware-analysis
14.3Krshipp/awesome-malware-analysisA curated 'awesome list' of malware analysis tools and resources, covering sample collection, sandboxes, detection tools, threat intelligence feeds, reverse engineering, and forensics.
- 15

PENTESTING-BIBLE
14KblaCCkHatHacEEkr/PENTESTING-BIBLEA curated catalog of over 200 numbered links to pentesting articles, bug bounty write-ups, cheat sheets and other security lists — a reading collection, not software.
- 16
theZoo
13.5Kytisf/theZoo · PythontheZoo is a public repository of live malware samples and their source code, gathered so that anyone interested in malware analysis can study real specimens in an organized and accessible way.
- 17
ida-pro-mcp
13Kmrexodia/ida-pro-mcp · PythonIt is an MCP server that bridges IDA Pro with AI language models, letting coding agents like Claude, Codex or Cursor help you reverse engineer binaries ('vibe reversing').
- 18
Detect-It-Easy
11.7Khorsicq/Detect-It-Easy · JavaScriptDetect It Easy (DiE) is a cross-platform tool that identifies file types and inspects executables (PE, ELF, Mach-O) for malware analysts, reverse engineers, and cybersecurity researchers, combining signature-based detection with a deep heuristic engine.
- 19
GhidraMCP
11.4KLaurieWired/GhidraMCP · JavaGhidraMCP is a Model Context Protocol server that lets LLMs autonomously reverse engineer applications by exposing Ghidra's core functionality (decompiling, renaming, listing imports/exports) to any MCP client.
- 20

pwndbg
11.1Kpwndbg/pwndbg · PythonA plug-in for GDB and LLDB that makes debugging far less painful for low-level developers, hardware hackers, reverse-engineers and exploit developers — it adds the utilities vanilla debuggers are missing.
- 21
reverse-engineering
10.6KwtsxDev/reverse-engineeringA curated list of reverse engineering resources: books, courses, practice grounds, and a big toolbox section spanning hex editors, disassemblers, debuggers, and dynamic analysis tools.
- 22

awesome-honeypots
10.6Kparalax/awesome-honeypots · PythonA curated, categorized list of honeypot software and related tools used by security researchers to deceive attackers, log their behavior, and study exploitation attempts.
- 23

skills
7.6Ktrailofbits/skills · PythonThis is Trail of Bits' Claude Code plugin marketplace: a curated collection of AI-agent skills for security research, vulnerability detection, and audit workflows, covering everything from smart contract audits to malware analysis and reverse engineering.
- 24

raptor
3.9Kgadievron/raptor · PythonRAPTOR turns a Claude Code session into an offensive/defensive security agent: Claude.md rules, sub-agents and skills orchestrate tools like radare2, Frida, Z3 and CodeQL for binary reverse-engineering, exploit-feasibility research, and software supply-chain (SCA) analysis.
- 25
x64dbg-mcp-server
2.5Kduty1g/x64dbg-mcp-server · Zigx64dbg-MCP Server is a native plugin for the x64dbg debugger that exposes its full functionality over HTTP via the Model Context Protocol (MCP), letting any MCP-compatible AI assistant programmatically set breakpoints, step through code, read memory, dump registers, and more.
- 26
Seep-Reverse-Lab
1.7Kangusdevgo/Seep-Reverse-Lab · LuaSeep Reverse Lab is an agent-native reverse engineering and security-audit workbench that lets an AI coding agent autonomously run Radare2, JADX, Apktool and Frida to triage binaries, decompile APKs, and determine whether an app's feature gates are enforced locally or verified by a server (a CWE-602 authorization audit).
- 27

reverify
1.3K2akouwu/reverify · PythonReverify is a tool that stops AI agents from hallucinating facts by making a deterministic toolkit verify every claim the model makes against ground truth, with reverse engineering as the main proving ground.
- 28
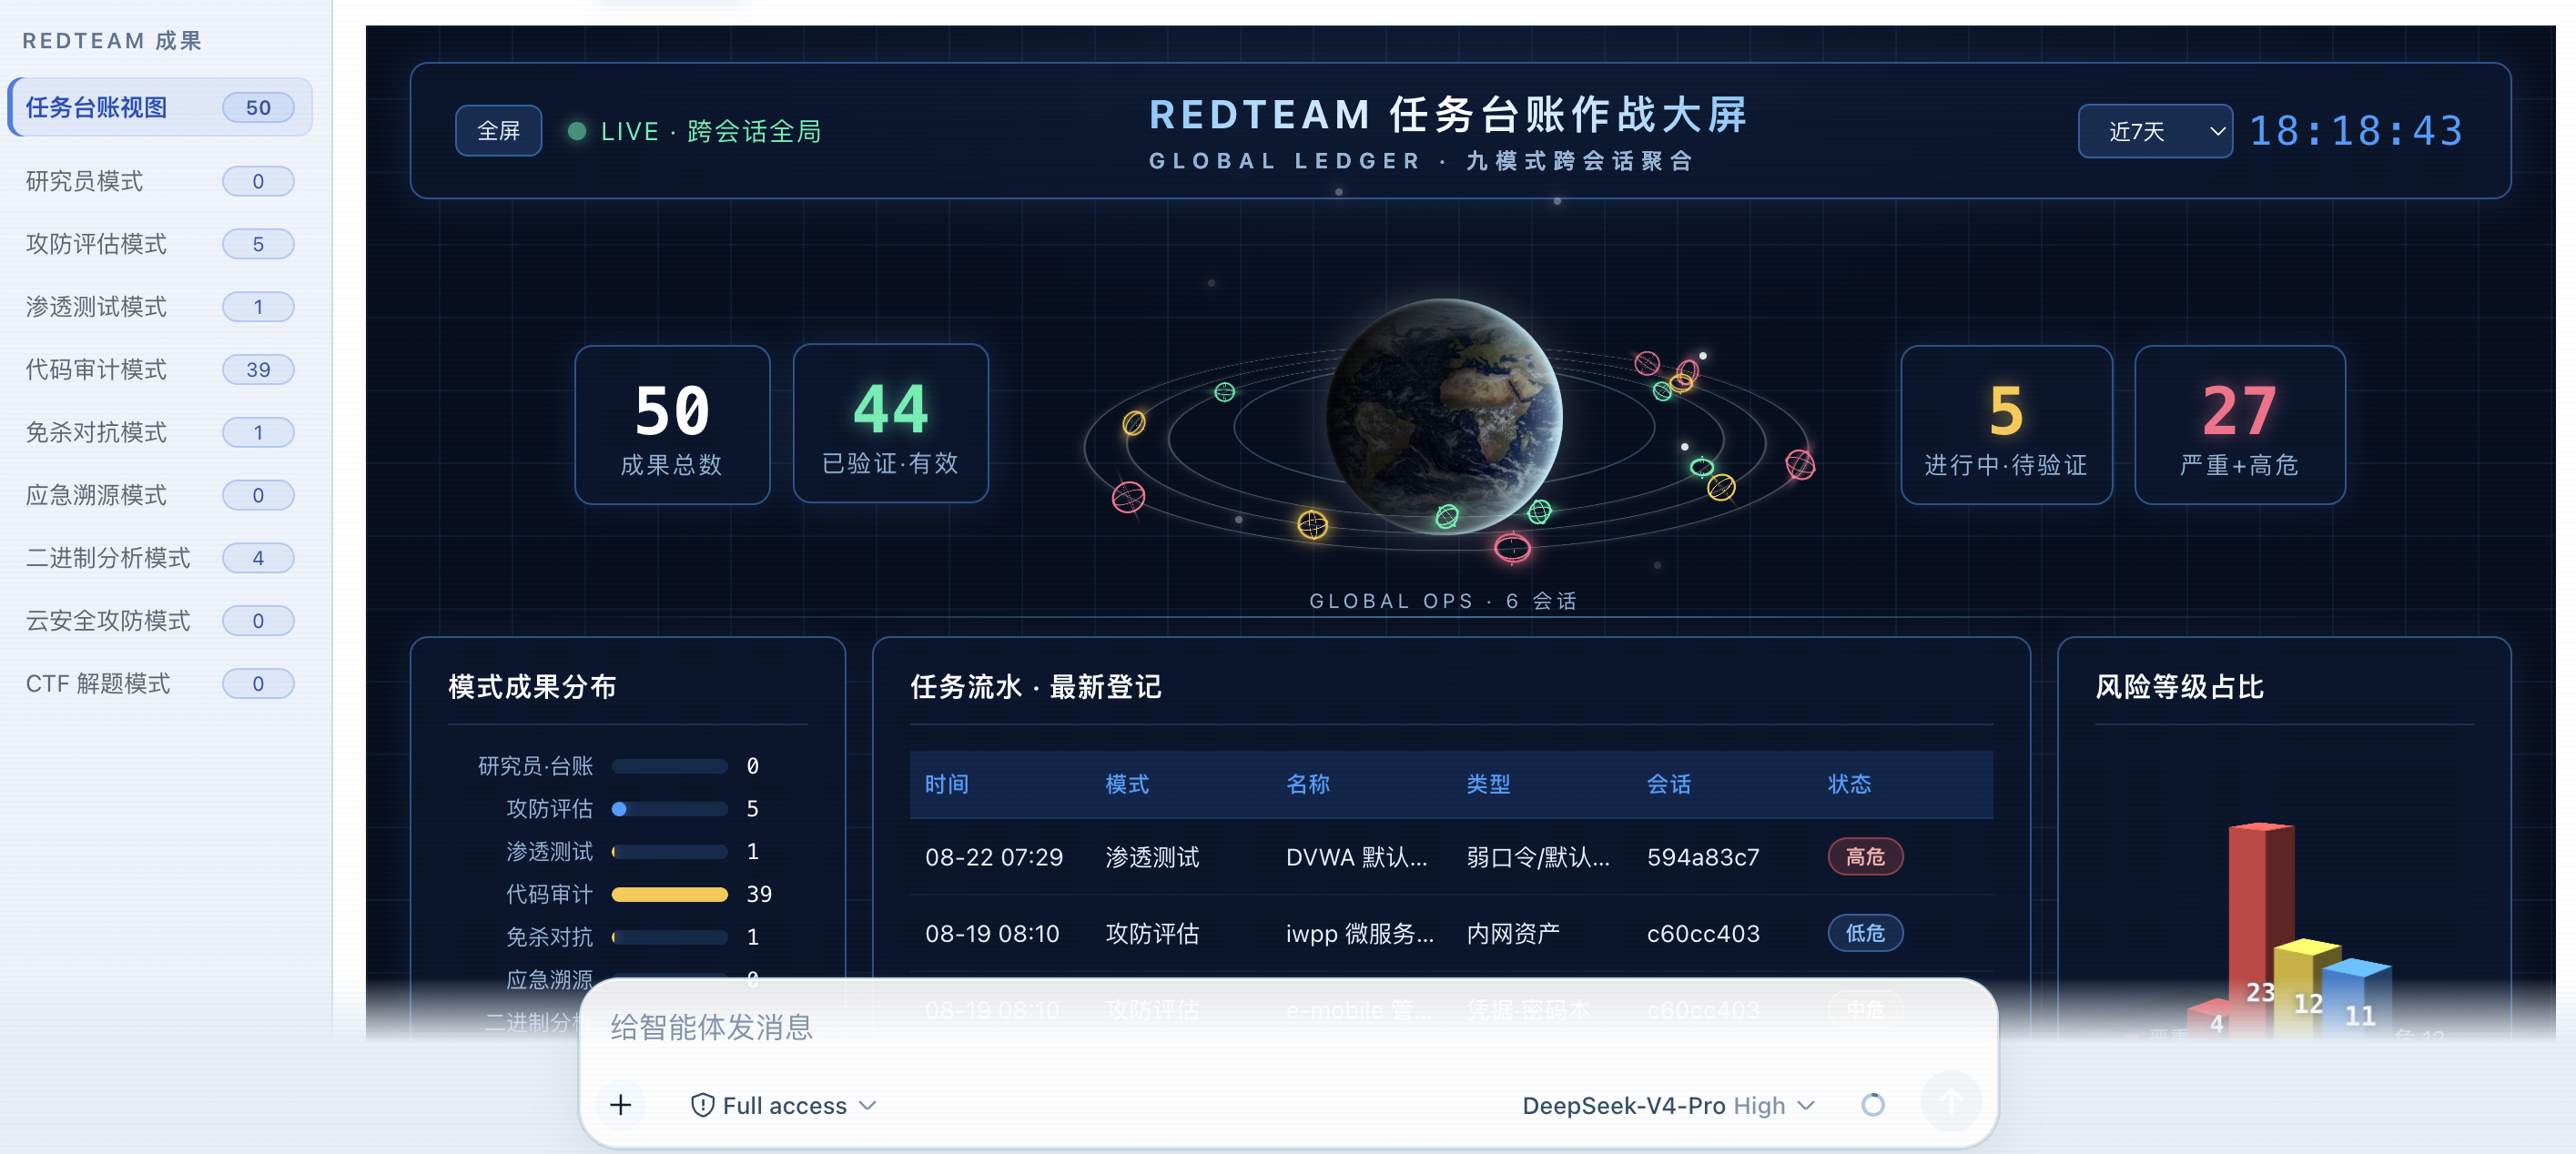
dsh-redteam-model
719SeaOf0/dsh-redteam-model · PythonA plugin pack for the dsh (DeepSeek Harness) AI agent that adds nine preset red-team security research modes and seventeen runtime plugins, covering pentesting, code audit, binary analysis, anti-detection, incident response, cloud security and CTF solving.
- 29
Offensive-Security-AI-Models
691JoasASantos/Offensive-Security-AI-ModelsA curated list of open-weight, uncensored language models fine-tuned for offensive-security tasks like penetration testing, red teaming, and security research. The README documents over 20 models sourced from HuggingFace model cards as of September 2026.
- 30
awesome-reverse-engineering
691morluto/awesome-reverse-engineeringA curated list of reverse-engineering tools and learning resources covering binaries, applications, firmware, file formats, and protocols, organized by the task you need to do rather than alphabetically.
- 31

Stuxnet
588Sadpainy/Stuxnet · CThis is a reconstructed source code of Stuxnet, the famous 2010 worm that sabotaged Siemens industrial control systems, rebuilt by the author from reverse-engineering research for educational and malware-analysis purposes.
- 32

vmp-lazy-unpack
402x86rc/vmp-lazy-unpack · PythonThis is a Python tool that automatically unpacks Windows x64 binaries protected with VMProtect 3.x and rebuilds their import table (IAT), without needing a debugger or live memory dump.
- 33
ablation
214Ablation-Tool/ablation · PythonAblation is a reverse engineering framework that provides the same core disassembly, decompilation, and binary analysis capabilities as industry tools like Ghidra, IDA Pro, and Binary Ninja, and it's built to be driven by an AI coding agent.
- 34

vol-rs
197daffainfo/vol-rs · Rust'vol-rs' is a line-by-line port of the Volatility 3 memory forensics framework from Python to Rust. It reads the same memory images, runs the same plugins with the same options, and prints byte-for-byte identical output, just much faster.
Related topics
Often tagged together
- reverse-engineering222
- security977
- cybersecurity244
- security-tools281
- windows3,401
- binary-analysis42
- linux4,182
- macos3,544
- open-source5,666
- python2,396
- forensics27
- hacking135
- ctf36
- disassembler23
- penetration-testing125
- awesome-list497
- cli2,227
- curated-list634
- developer-tools2,927
- infosec47
- pentesting112
- static-analysis126
- cross-platform2,622
- mcp917