Topics / #ethical-hacking
Ethical-hacking projects on GitHub
Learning resources and tools for legal, authorized security testing.
As of , the most-starred Ethical-hacking projects on GitHub are strix (69.1K stars), shannon (49K stars) and Anthropic-Cybersecurity-Skills (34.6K stars). GitHub.Locker tracks 24 Ethical-hacking repositories with 348.3K stars combined. The fastest-growing on October 16 was strix, with +214 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
 +214
strix
usestrix/strix · ★ 69.1KStrix is an open-source tool that uses autonomous AI agents to pentest your application like real hackers: it runs your code dynamically, finds vulnerabilities, and proves them with working exploits instead of just flagging suspicious patterns.
 +81
shannon
KeygraphHQ/shannon · ★ 49KShannon is an autonomous AI pentester that analyzes your web application's source code, maps attack vectors, and then executes real exploits against the running app to prove vulnerabilities before they reach production — 'no exploit, no report'.
 +71
Anthropic-Cybersecurity-Skills
mukul975/Anthropic-Cybersecurity-Skills · ★ 34.6KAn open-source library of 818 production-grade cybersecurity skills for AI agents, covering 34 security domains and mapped to six frameworks including MITRE ATT&CK and NIST CSF 2.0.
 +26
90DaysOfCyberSecurity
farhanashrafdev/90DaysOfCyberSecurity · ★ 20.1KA free, 90-day self-paced cybersecurity study plan: daily tasks and curated resources that take you from networking basics to ethical hacking, ending with job-hunting help.
The all-time top
24 projects · by stars
- 69.1K#1 · usestrix/strix
strix
Strix is an open-source tool that uses autonomous AI agents to pentest your application like real hackers: it runs your code dynamically, finds vulnerabilities, and proves them with working exploits instead of just flagging suspicious patterns.
- 49K#2 · KeygraphHQ/shannon
shannon
Shannon is an autonomous AI pentester that analyzes your web application's source code, maps attack vectors, and then executes real exploits against the running app to prove vulnerabilities before they reach production — 'no exploit, no report'.
- 34.6K#3 · mukul975/Anthropic-Cybersecurity-Skills
Anthropic-Cybersecurity-Skills
An open-source library of 818 production-grade cybersecurity skills for AI agents, covering 34 security domains and mapped to six frameworks including MITRE ATT&CK and NIST CSF 2.0.
- 4
h4cker
29.8KThe-Art-of-Hacking/h4cker · Jupyter NotebookA curated collection of thousands of cybersecurity resources — references, scripts, tools, code, labs, and training material — maintained by Omar Santos as a companion to his books, video courses, and live training.
- 5

awesome-pentest
27.5Kenaqx/awesome-pentestA curated collection of penetration testing and offensive-security resources: tools, books, courses, conferences and practice targets for authorized security testing.
- 6
90DaysOfCyberSecurity
20.1Kfarhanashrafdev/90DaysOfCyberSecurityA free, 90-day self-paced cybersecurity study plan: daily tasks and curated resources that take you from networking basics to ethical hacking, ending with job-hunting help.
- 7
evilginx2
15.7Kkgretzky/evilginx2 · GoEvilginx is a man-in-the-middle attack framework used for phishing login credentials along with session cookies, which lets an attacker bypass 2-factor authentication.
- 8

hacker-roadmap
15.7Ksundowndev/hacker-roadmapThis is a curated roadmap and toolkit index for learning and practicing ethical hacking: it explains what penetration testing is and groups hundreds of security tools, wordlists and references by category (recon, password attacks, wireless, exploitation, web hacking, post-exploitation, frameworks).
- 9

social-engineer-toolkit
15.4Ktrustedsec/social-engineer-toolkit · PythonThe Social-Engineer Toolkit (SET) is an open-source penetration testing framework for authorized social-engineering assessments, giving security teams guided attack vectors to test user awareness and validate controls.
- 10

hacker101
14.6KHacker0x01/hacker101 · SCSSHacker101 is a free online class for web and mobile security from HackerOne (the Hacker0x01 org), aimed at everyone from programmers curious about bug bounties to seasoned security professionals.
- 11

hacktricks
12.6KHackTricks-wiki/hacktricks · JavaScriptA free, open wiki of hacking tricks and techniques — everything the author has learnt from CTFs, real-world apps and security research, organized into a browsable reference with 12.5k+ GitHub stars.
- 12

Claude-Red
7.6KSnailSploit/Claude-Red · Pythonclaude-red is a curated library of offensive security skills for the Claude Skills system: structured SKILL.md files that prime Claude with expert-level methodology for one attack surface each, from SQLi to shellcode.
- 13
user-scanner
5.4Kkaifcodec/user-scanner · PythonUser Scanner is an OSINT (open-source intelligence) CLI tool that takes an email address or username and scans it across 2720+ platforms (210+ email vectors, 2510+ username vectors) to map digital footprints, scrape profile metadata, and surface linked accounts.
- 14
Agentic-Bug-Hunter
5.4Kawarexone/Agentic-Bug-Hunter · PythonAgentic Bug Hunter is an AI-powered bug bounty toolkit that runs recon, tests for vulnerabilities, validates findings against a strict gate, and writes submission-ready reports for HackerOne, Bugcrowd, Intigriti, or Immunefi, right from your terminal.
- 15

exploitarium
5.2Kbikini/exploitarium · PythonExploitarium is a single consolidated archive of the author's public proof-of-concept exploits and vulnerability research writeups, merging dozens of their former standalone PoC repos into one place.
- 16

Claude-BugHunter
5.1Kelementalsouls/Claude-BugHunter · PythonA drop-in skill bundle for the Claude Code skills system that turns Claude into a bug-hunting researcher or red-team operator: it ships 83 skills, 15 slash commands, and knowledge curated from 681 disclosed HackerOne reports across 24 vulnerability classes, plus enterprise identity and infrastructure attack matrices.
- 17
airgorah
4.2Kmartin-olivier/airgorah · RustAirgorah is a WiFi security auditing tool written in Rust that captures nearby WiFi traffic, discovers clients connected to access points, performs deauthentication attacks, captures handshakes and PMKIDs, and cracks access point passwords.
- 18

copy-fail-CVE-2026-31431
4.1Ktheori-io/copy-fail-CVE-2026-31431 · PythonThis repository is a technical writeup and proof-of-concept for CVE-2026-31431, a 9-year-old Linux kernel local privilege escalation (LPE) vulnerability found by Theori's AI vulnerability research tool, Xint Code.
- 19
redamon
3.1Ksamugit83/redamon · PythonRedAmon is an open-source, self-hosted AI framework that chains reconnaissance, exploitation and post-exploitation into one pipeline, maps the attack surface into a Neo4j graph, and then triages findings and opens GitHub pull requests that fix what it discovers.
- 20
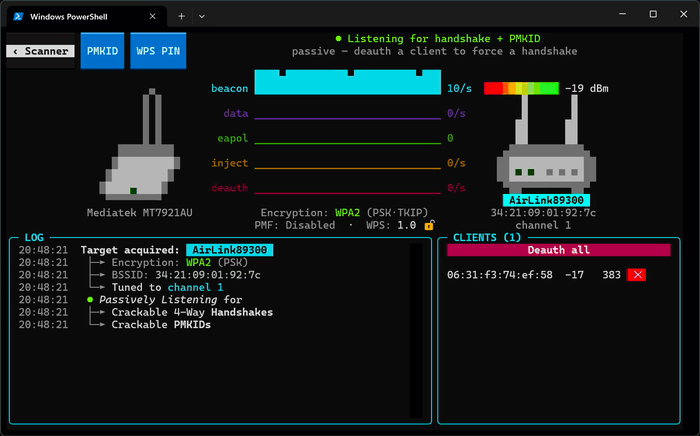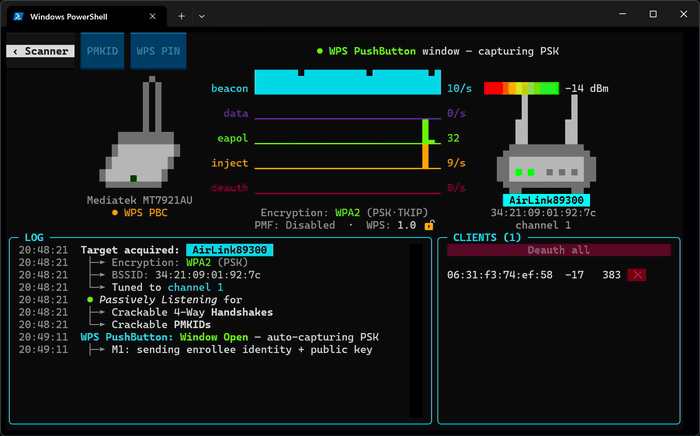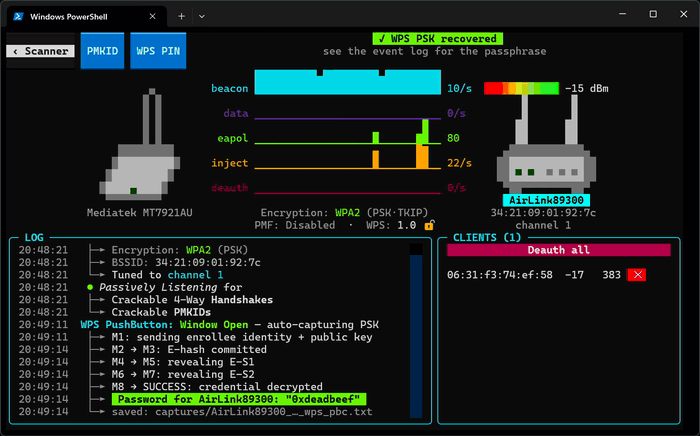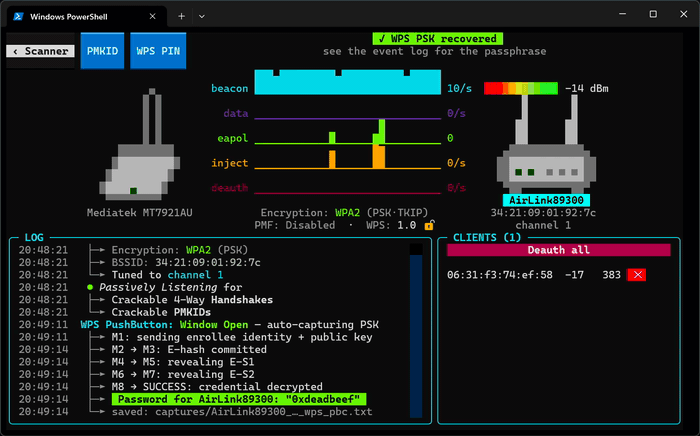
wifit3
2.4Kderv82/wifit3 · Pythonwifit3 is a standalone Wi-Fi security auditing tool that scans networks, captures WPA/WPA2 handshakes, and exploits WPS/WEP weaknesses using a supported USB Wi-Fi adapter, without relying on aircrack-ng or OS kernel drivers.
- 21

bug-bounty-hunting-prompts
621mdpsec/bug-bounty-hunting-promptsA pack of reusable prompt files for running a structured, evidence-first bug bounty hunting workflow with an LLM agent, covering recon through triage and escalation.
- 22
Ai-jailbreak
479Quincunx33/Ai-jailbreak · JavaScriptA curated collection of jailbreak prompts and exploit techniques that bypass the safety guardrails of both open-weight models (Gemma, Qwen, Llama, DeepSeek, Phi-4, Mistral) and frontier closed models (GPT-5.x, Gemini 3.x, Grok 4.x), documented for red-teaming and AI safety research.
- 23

CVE-2026-9830
477opaxial/CVE-2026-9830 · PythonA Python proof-of-concept that validates a reported unauthenticated REST API exposure in the BookingPress Pro WordPress plugin, which can leak booking and customer data.
- 24

Claude-AD
212ADScanPro/Claude-ADClaude-AD is a Claude Code plugin that gives Claude the methodology for an internal Active Directory penetration test: skills, agents and slash commands covering Kerberoasting, ADCS ESC1-17, DCSync, ACL abuse, NTLM relay and delegation abuse, each with OPSEC and telemetry notes.
Related topics
Often tagged together