Topics / #mitm
Mitm projects on GitHub
Man-in-the-middle proxies for intercepting and inspecting traffic.
As of , the most-starred Mitm projects on GitHub are learn_python3_spider (22.2K stars), bettercap (20.1K stars) and Awesome-Hacking-Resources (17.5K stars). GitHub.Locker tracks 21 Mitm repositories with 172.6K stars combined. The fastest-growing on October 16 was billion-context, with +144 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
 +144
billion-context
ranxianglei/billion-context · ★ 1.5Kbillion-context is a context-compression proxy that sits between any coding agent and its model API, rewriting Anthropic/OpenAI streams so a 100K context window is enough and a single session can run for months across billions of tokens.
 +14
mimic
littledivy/mimic · ★ 2.8Kmimic intercepts traffic from any app (mobile or web) and turns it into a plain Python client you can call like a library — you capture one real request and an AI generates the named methods for you instead of you writing them by hand.
 +11
ARTEX
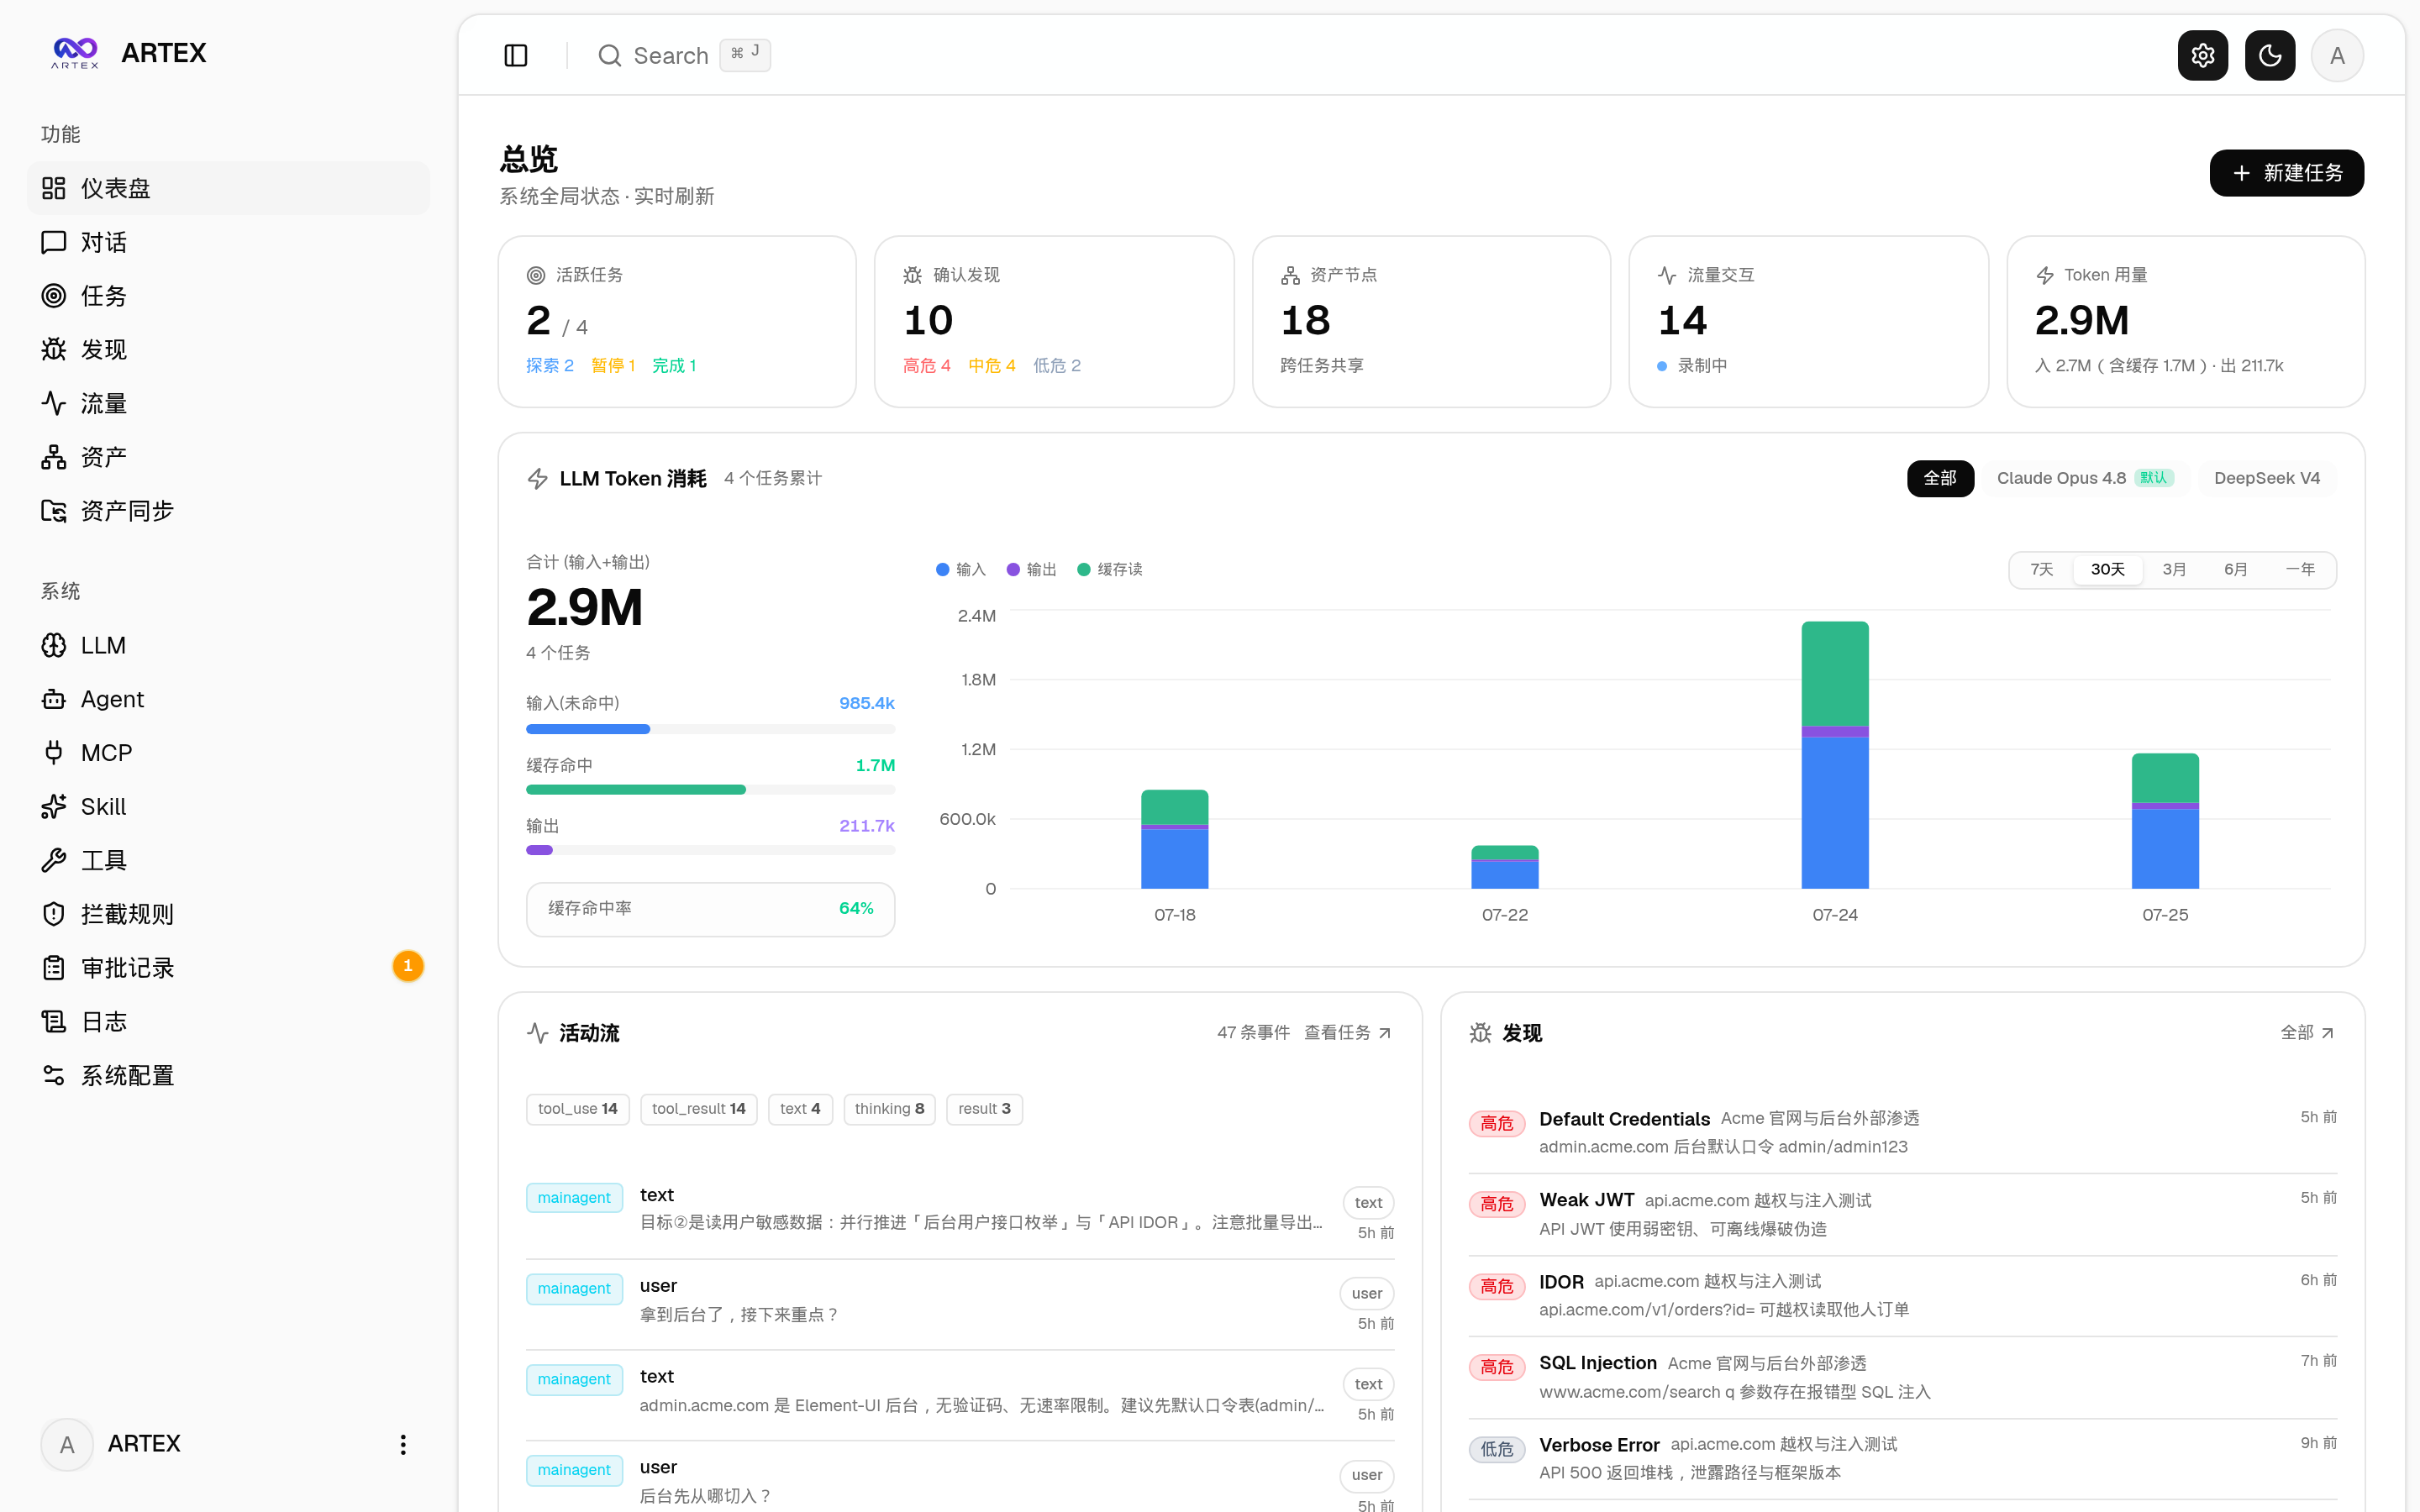
Hinln/ARTEX · ★ 777ARTEX is an AI-driven autonomous penetration testing system with a Go backend and a Next.js frontend. It runs multiple LLM agents that explore a target, build an asset graph, and chain findings into vulnerabilities, all shown on a web dashboard.
 +10
ARTEX
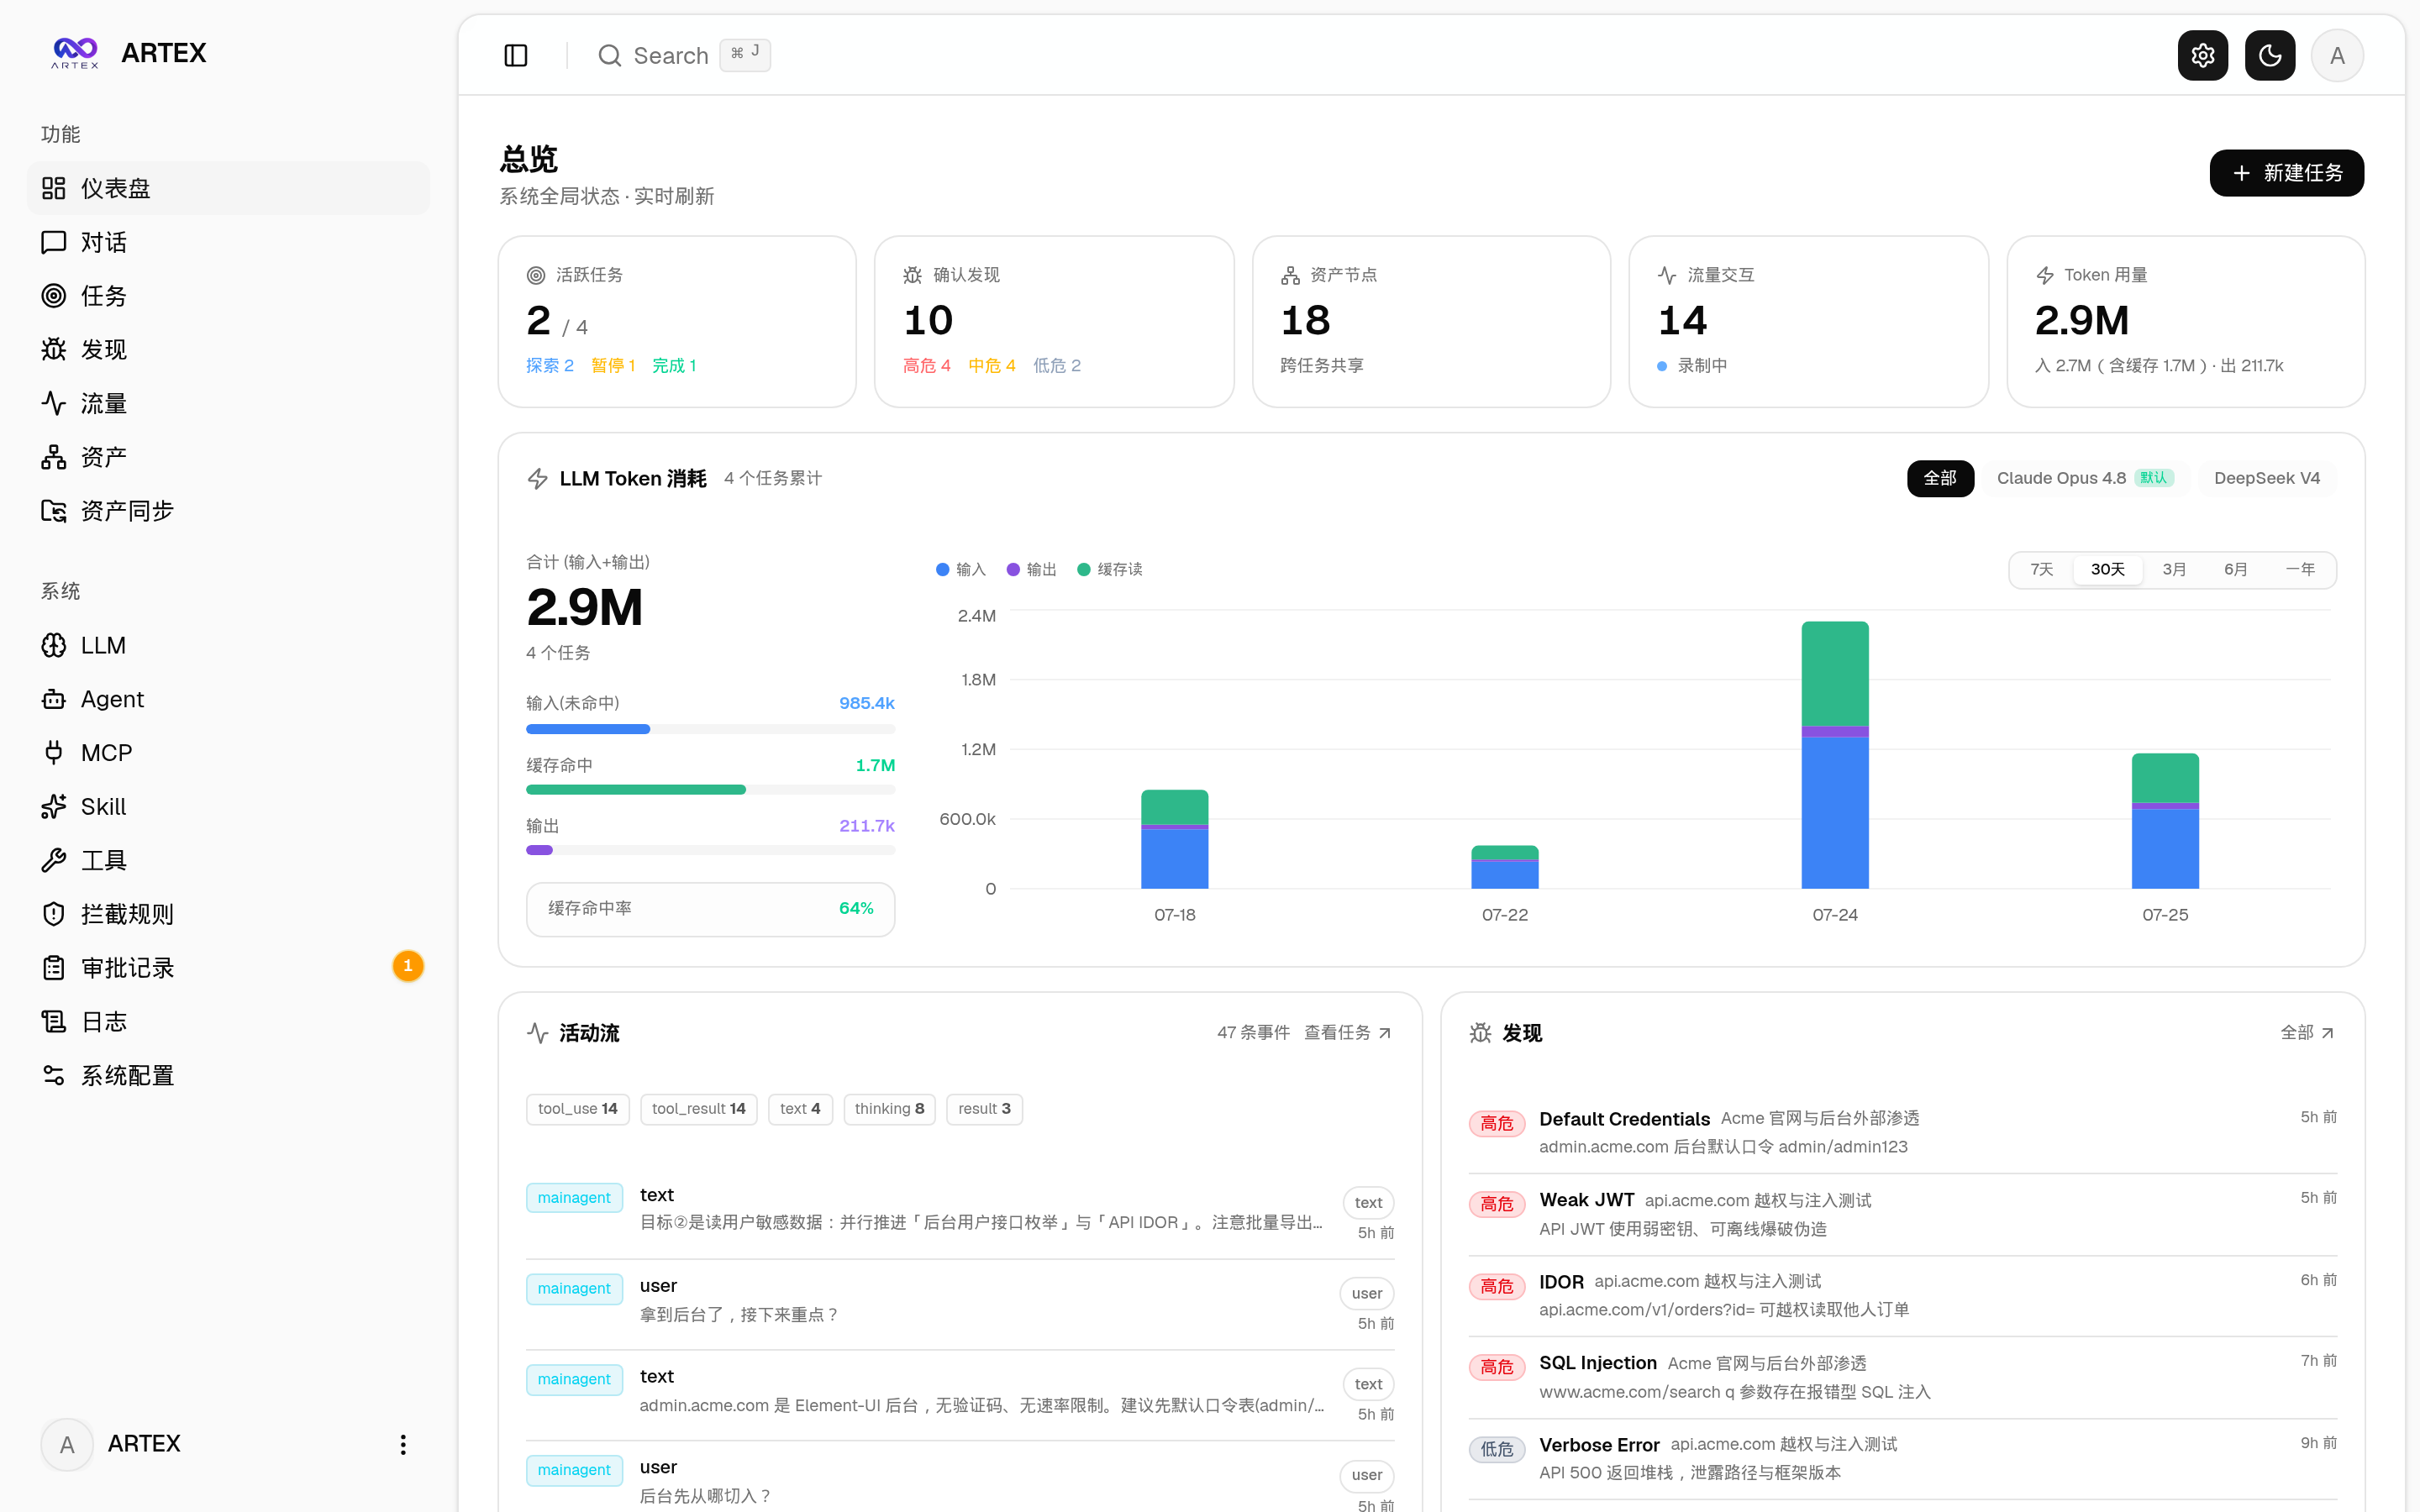
trhhubsd/ARTEX · ★ 1.2KARTEX is an AI-driven autonomous penetration testing system (Go backend + Next.js frontend) where LLM-powered planner and worker agents explore targets, map assets, and find vulnerabilities on their own.
The all-time top
21 projects · by stars
- 22.2K
 #1 · wistbean/learn_python3_spider
learn_python3_spider
A free Chinese-language tutorial series that teaches Python web scraping from zero — 30+ numbered lessons and mitmproxy guides, from first packet capture to distributed crawling, with source code for the practice projects.
- 20.1K
 #2 · bettercap/bettercap
bettercap
A portable all-in-one framework written in Go for recon and attacks on WiFi, Bluetooth Low Energy, wireless HID, CAN-bus and IPv4/IPv6 networks, built for security researchers and red teamers.
- 17.5K
 #3 · vitalysim/Awesome-Hacking-Resources
Awesome-Hacking-Resources
A curated collection of hacking, penetration testing and AI red-teaming resources — courses, YouTube channels, CTF platforms and guides, picked to make you better at offensive security.
- 4
evilginx2
15.7Kkgretzky/evilginx2 · GoEvilginx is a man-in-the-middle attack framework used for phishing login credentials along with session cookies, which lets an attacker bypass 2-factor authentication.
- 5

whistle
15.7Kavwo/whistle · JavaScriptWhistle is a cross-platform web debugging proxy built on Node.js — it captures and lets you modify HTTP, HTTPS, HTTP/2, WebSocket and TCP traffic, in the same niche as Charles or Fiddler (both are among its GitHub topics).
- 6

brook
15.2Ktxthinking/brook · GoBrook is a cross-platform programmable network tool that works as both a server and a client, giving you SOCKS5 proxying, TLS encryption, traffic decryption/MITM inspection, and packet capture in one toolkit.
- 7

proxypin
14.1Kwanghongenpin/proxypin · DartProxyPin is a free, open source tool for capturing HTTP(S) traffic: it intercepts, inspects and rewrites requests and responses, and it can even capture traffic from Flutter apps. Think of it as an open alternative to Charles or Fiddler.
- 8
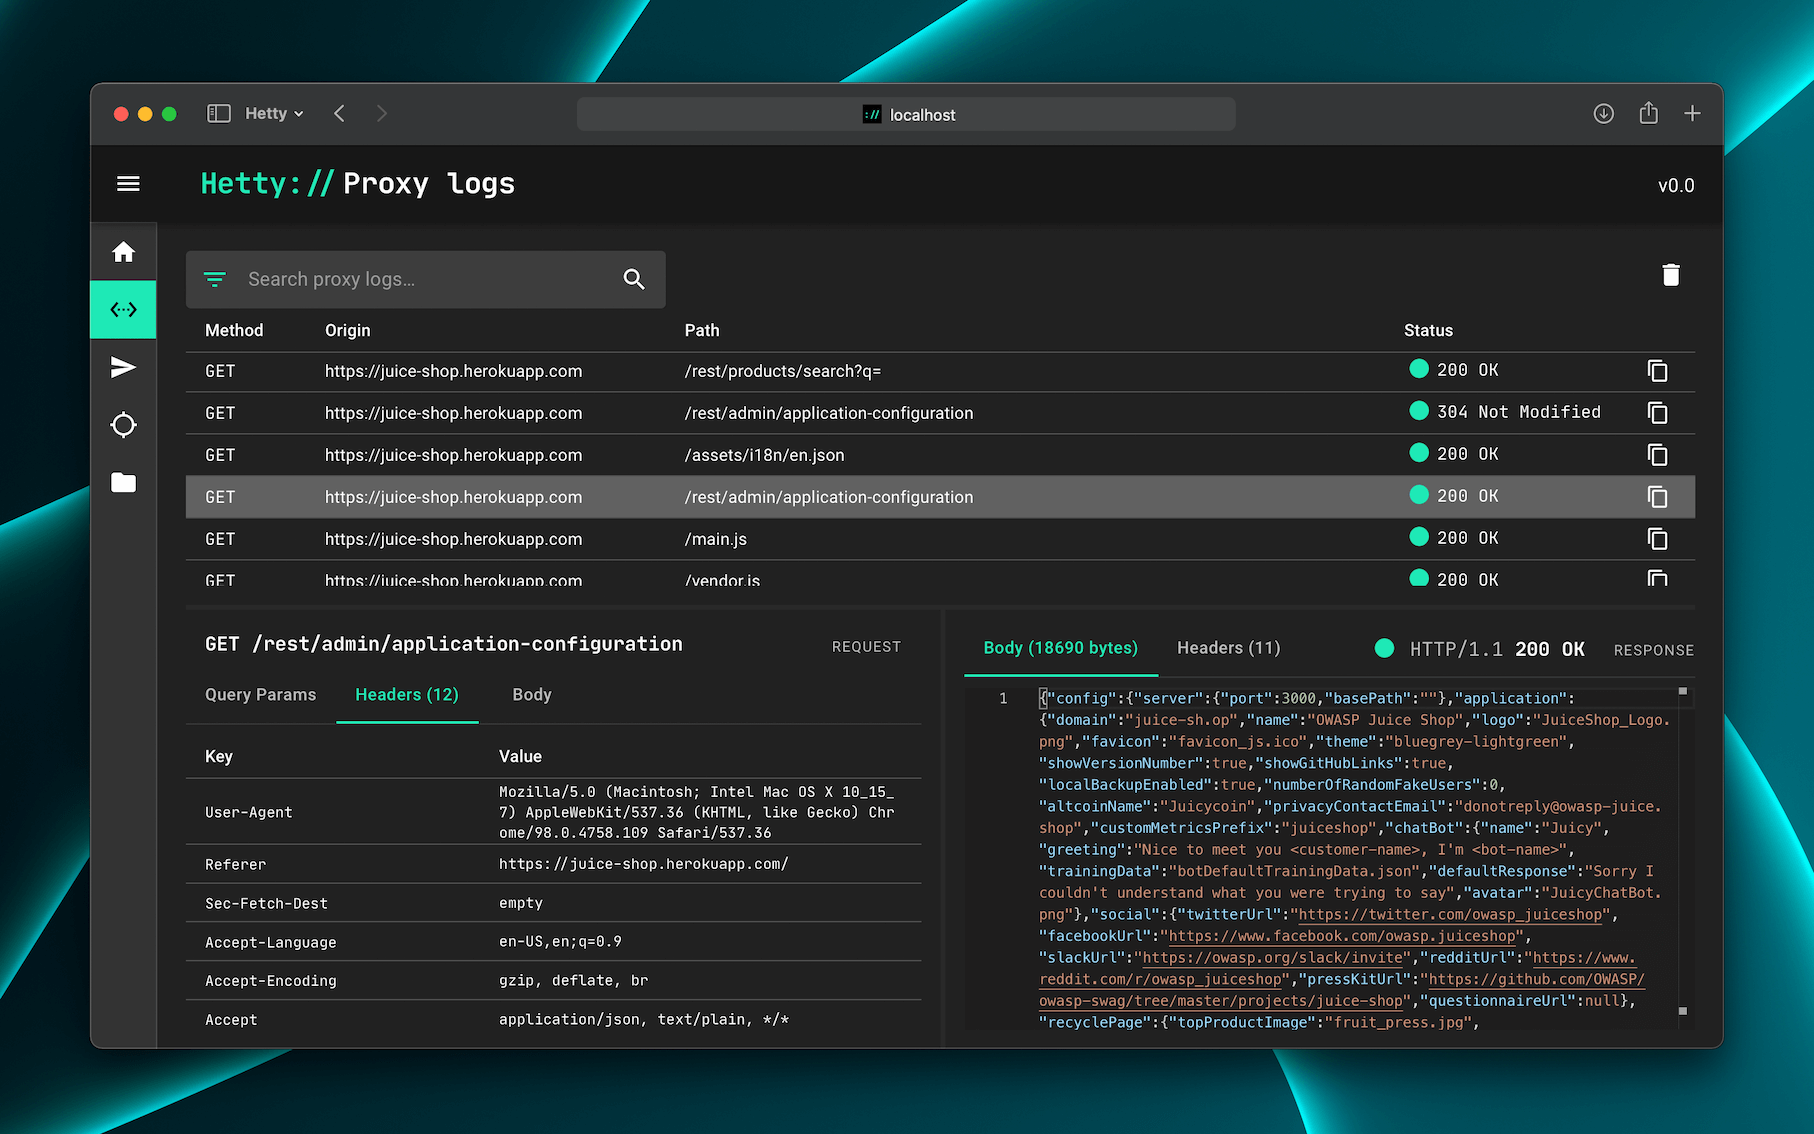
hetty
12.5Kdstotijn/hetty · GoHetty is an HTTP toolkit for security research, aiming to be an open source alternative to commercial tools like Burp Suite Pro, aimed at the infosec and bug bounty community.
- 9

iRingo
10.6KNSRingo/iRingoiRingo is a set of rewrite/MitM rule modules that unlock the full versions of Apple services (Weather, Maps, Siri/Spotlight search, News, TV, TestFlight, Watch, and a BoxJs config panel) on devices where Apple limits or disables them, by rewriting the app's network requests.
- 10

ios-location-spoofer
4.5Kmekos2772/ios-location-spoofer · JavaScriptA set of MITM rewrite modules for proxy apps that intercept Apple's location service traffic and rewrite the returned Wi-Fi/cell-tower coordinates, making an iPhone believe it is anywhere in the world without jailbreaking it.
- 11
mhr-cfw
4.4Kdenuitt1/mhr-cfw · PythonMHR-CFW is a domain-fronting relay that disguises your traffic as requests to an allowed domain like Google, routing it through Google Apps Script and a Cloudflare Worker before fetching the real site. It's built to bypass DPI (deep packet inspection) based network filtering.
- 12

ARTEX
4.4Kmhtsec/ARTEX · GoARTEX is an AI-driven autonomous penetration testing system with a Go backend (embedding a Next.js frontend) where LLM-powered agents plan and execute security testing against assets. It won first place in Baidu's 'Agent+' attack-defense challenge.
- 13

MasterHttpRelayVPN
3.9Kmasterking32/MasterHttpRelayVPN · PythonMasterHttpRelayVPN is a local proxy that routes your browser traffic through a Google Apps Script relay using domain fronting and MITM TLS interception, designed to evade DPI and censorship.
- 14

MasterHttpRelayVPN-RUST
3.6Ktherealaleph/MasterHttpRelayVPN-RUST · RustIt is a Rust port of MasterHttpRelayVPN, a free DPI/censorship-bypass tool that routes your traffic through a Google Apps Script you deploy in your own Google account, using TLS SNI concealment so your ISP only sees a connection to www.google.com.
- 15
mimic
2.8Klittledivy/mimic · Pythonmimic intercepts traffic from any app (mobile or web) and turns it into a plain Python client you can call like a library — you capture one real request and an AI generates the named methods for you instead of you writing them by hand.
- 16
billion-context
1.5Kranxianglei/billion-context · TypeScriptbillion-context is a context-compression proxy that sits between any coding agent and its model API, rewriting Anthropic/OpenAI streams so a 100K context window is enough and a single session can run for months across billions of tokens.
- 17
ARTEX
1.2Ktrhhubsd/ARTEX · GoARTEX is an AI-driven autonomous penetration testing system (Go backend + Next.js frontend) where LLM-powered planner and worker agents explore targets, map assets, and find vulnerabilities on their own.
- 18

local_roborock_server
935Python-roborock/local_roborock_server · PythonA self-hosted local HTTPS and MQTT server that emulates Roborock's cloud backend on your own LAN, letting your Roborock vacuum keep live maps and local control without reaching the internet, and without rooting or modifying hardware.
- 19
ARTEX
777Hinln/ARTEX · GoARTEX is an AI-driven autonomous penetration testing system with a Go backend and a Next.js frontend. It runs multiple LLM agents that explore a target, build an asset graph, and chain findings into vulnerabilities, all shown on a web dashboard.
- 20

mlmvpn_android
411mlmvpn/mlmvpn_android · KotlinMLM VPN is an Android app that bundles many independent connectivity engines — Xray-core (VLESS/VMess/Trojan), AmneziaWG, WARP, Psiphon, Tor, Geph, OpenVPN and a custom MASQUE-based engine — behind one UI, plus an adaptive per-app router, a Cloudflare Worker control panel, and a game-latency booster, aimed at bypassing network restrictions.
- 21

badnotes
149c22dev/badnotes · Objective-CBadNotes is a jailbreak tweak for iOS that unlocks GoodNotes Pro by spoofing the app's subscription check.
Related topics
Often tagged together