Topics / #jailbreak
Jailbreak projects on GitHub
Jailbreak techniques for either consumer devices or AI model safety guardrails.
As of , the most-starred Jailbreak projects on GitHub are dive-into-llms (56.8K stars), UTM (35.9K stars) and unleashed-firmware (22.5K stars). GitHub.Locker tracks 41 Jailbreak repositories with 305.8K stars combined. The fastest-growing on October 16 was dsh-purge, with +320 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
 +320
dsh-purge
YuJunZhiXue/dsh-purge · ★ 6.5KIt is a jailbreak plugin (破甲, literally 'armor-break') for DeepSeek Harness: it patches the installed @deepseek-ai packages so every model in the harness can be jailbroken, with prompts swapped per model. The default prompt is aimed at Chinese models such as 小码酱.
 +126
overdrive
MyLuxy/overdrive · ★ 642Overdrive is a PS5 homebrew game store with a catalog of over 1,800 games, letting you browse, search and download titles straight to your console or a USB drive.
 +64
gpt-instruct
MDX-Tom/gpt-instruct · ★ 10.3Kgpt-instruct is a collection of jailbreak-style custom instructions for OpenAI's Codex/GPT models, shipped together with a reproducible Python test harness that scores how well each prompt survives regression testing.
 +57
vphone-cli
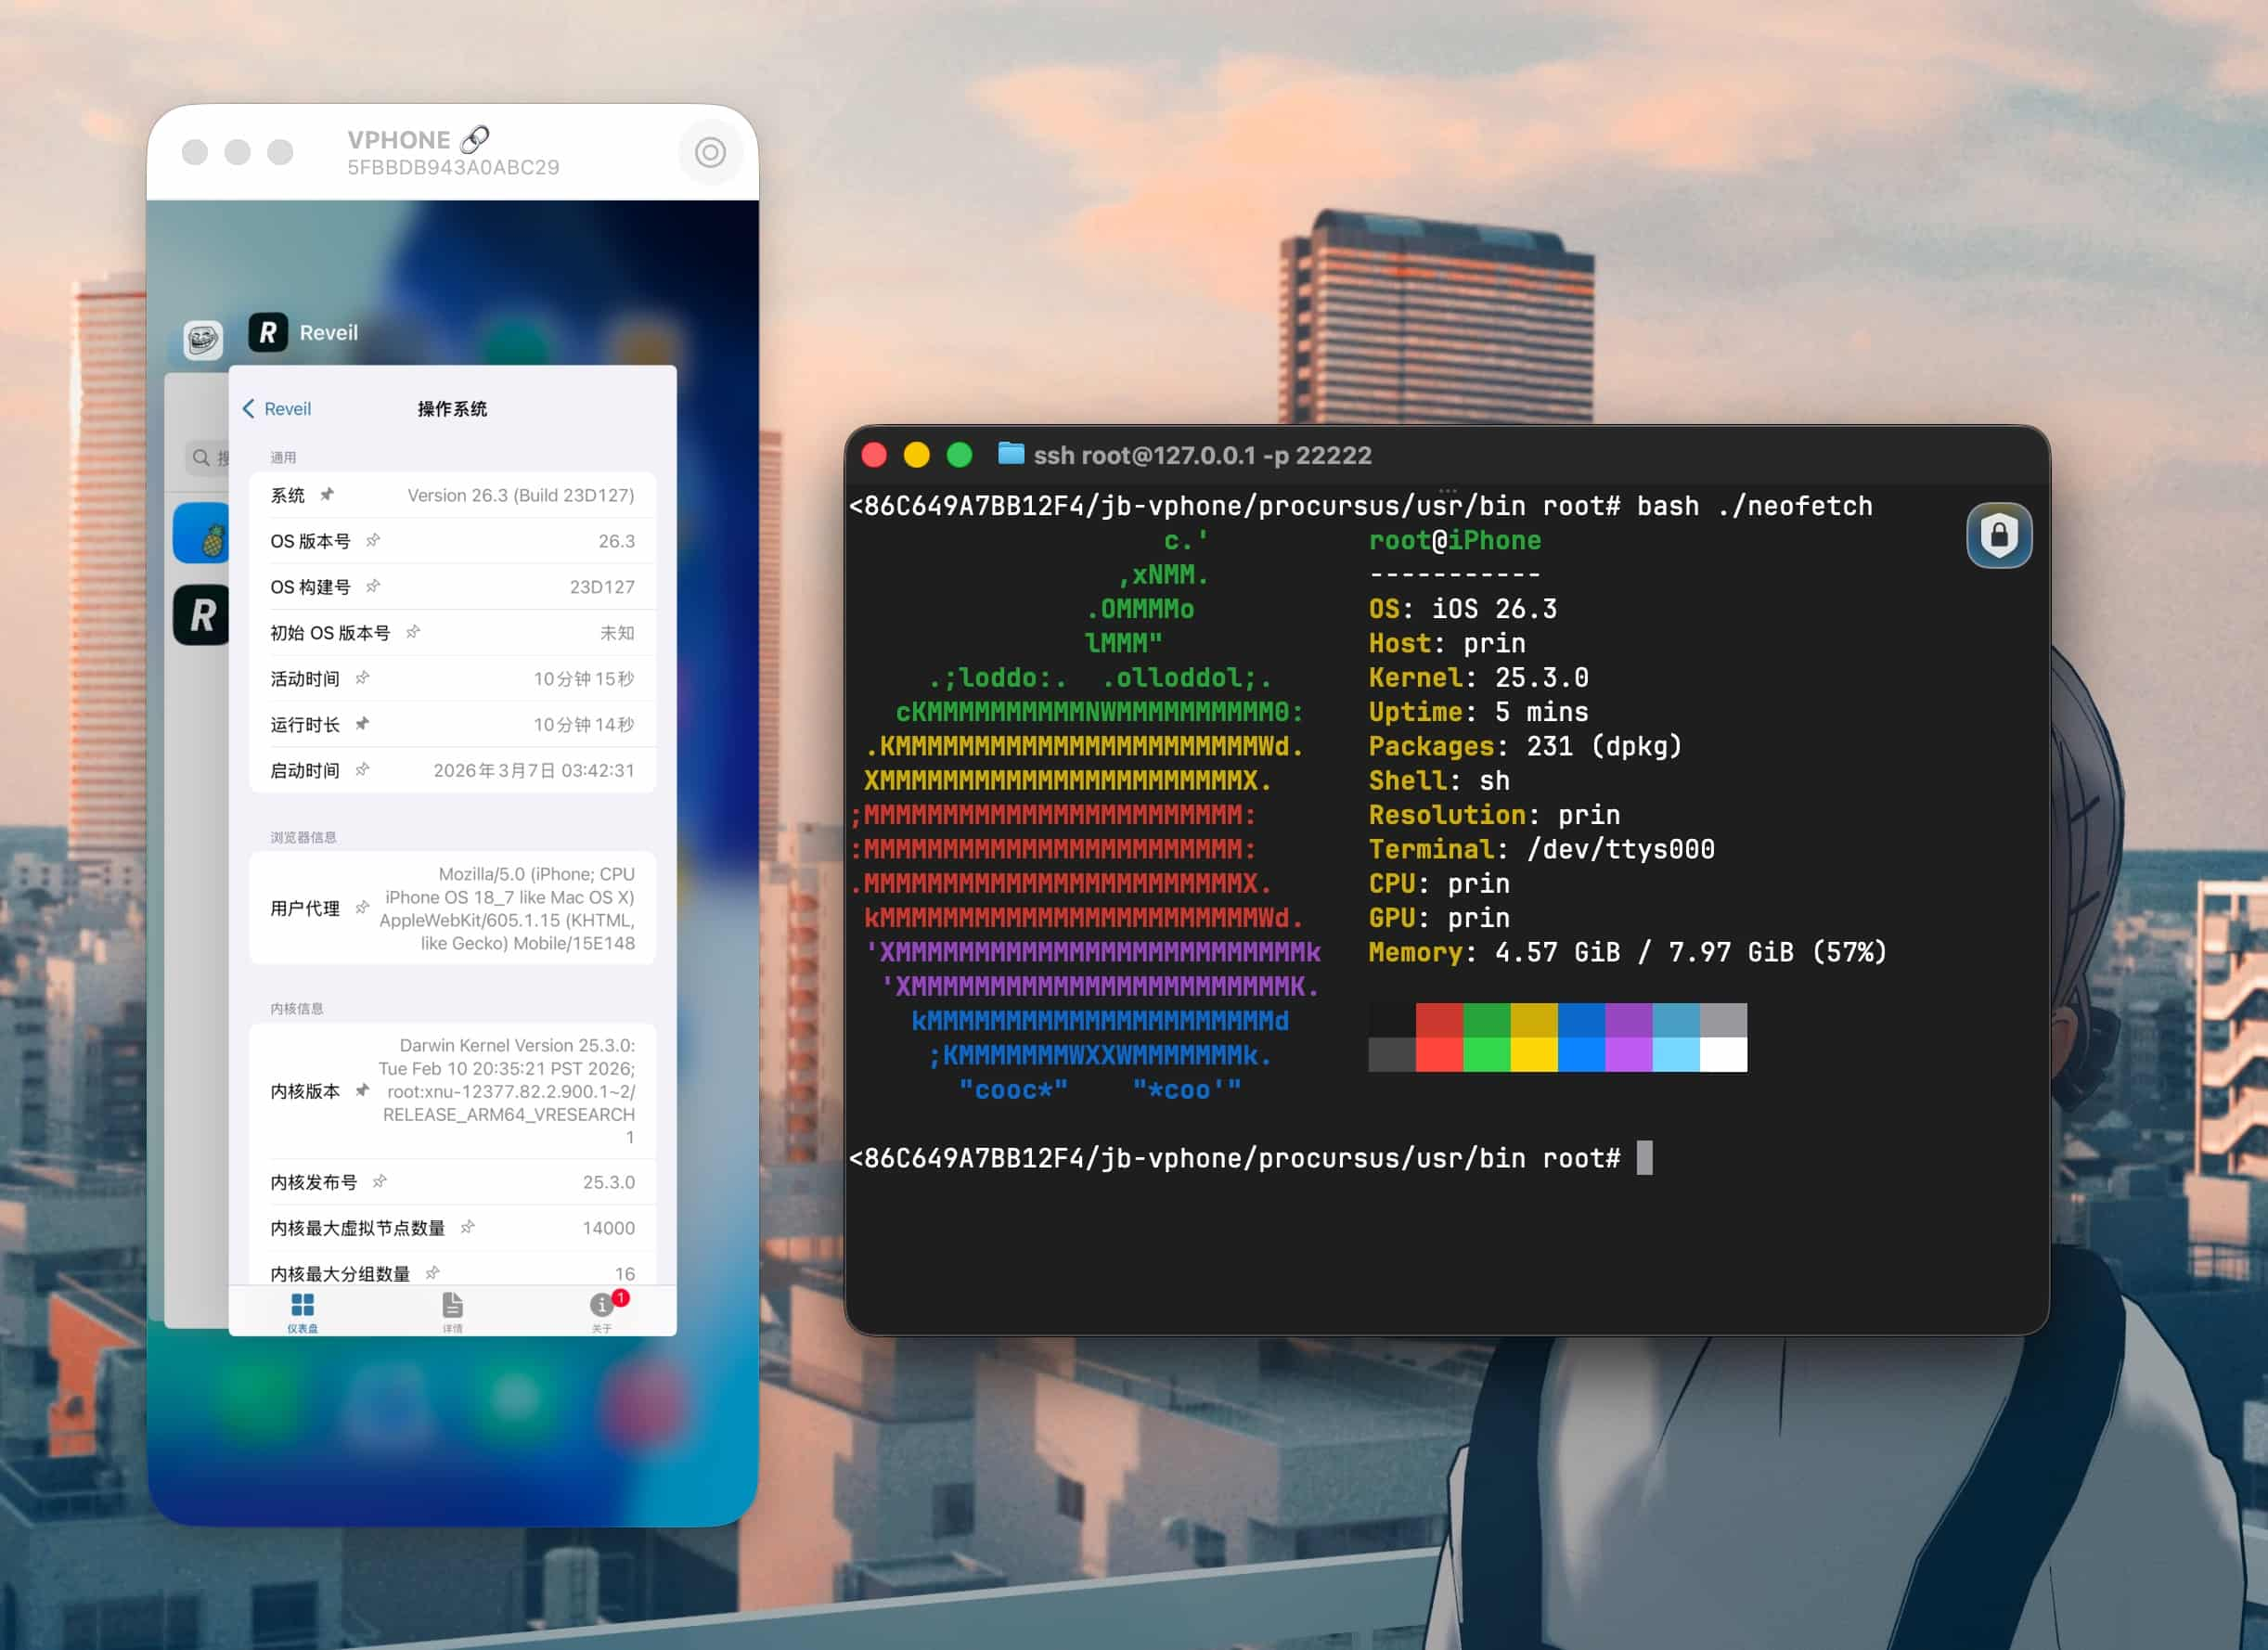
Lakr233/vphone-cli · ★ 15.4Kvphone-cli boots a virtual iPhone on a Mac using Apple's Virtualization.framework, built on Apple's PCC research VM infrastructure, so you can run, test, and even jailbreak iOS without a physical device.
The all-time top
41 projects · by stars
- 56.8K
 #1 · Lordog/dive-into-llms
dive-into-llms
It's a free Chinese-language tutorial series called 'Dive into LLMs' (《动手学大模型》) that teaches large language model concepts through hands-on coding exercises, built from Shanghai Jiao Tong University's NLP and AI-security course materials.
- 35.9K
 #2 · utmapp/UTM
UTM
UTM is a full system emulator and virtual machine host for iOS and macOS, built on QEMU, that lets you run Windows, Linux, and other operating systems directly on your Mac, iPhone, or iPad.
- 22.5K
#3 · DarkFlippers/unleashed-firmware
unleashed-firmware
Unleashed is custom firmware for the Flipper Zero multitool — a fork of the official firmware (OFW) that adds extra features and improvements while staying compatible with official apps.
- 4

TrollStore
22.4Kopa334/TrollStore · Objective-CTrollStore is a permasigned jailed app for iOS that permanently installs any IPA you open in it. It works via an AMFI/CoreTrust bug: iOS doesn't correctly verify code signatures when a binary has multiple signers, so TrollStore can resign apps with its fake root certificate and keep them installed for good.
- 5

L1B3RT4S
21.9Kelder-plinius/L1B3RT4SA public collection of jailbreak prompts — the author calls them 'liberation prompts' — meant to make flagship AI models respond without their usual refusals. It is maintained by AI red-teamer elder-plinius.
- 6

Atmosphere
20.1KAtmosphere-NX/Atmosphere · C++Atmosphère is a work-in-progress custom firmware (CFW) for the Nintendo Switch that replaces and patches core parts of the console's Horizon OS to add new features and customization.
- 7
vphone-cli
15.4KLakr233/vphone-cli · Swiftvphone-cli boots a virtual iPhone on a Mac using Apple's Virtualization.framework, built on Apple's PCC research VM infrastructure, so you can run, test, and even jailbreak iOS without a physical device.
- 8

ChatGPT_DAN
12.6K0xk1h0/ChatGPT_DANA curated collection of 'jailbreak' prompts for ChatGPT, most famously the 'DAN' (Do Anything Now) prompt, designed to push the model past OpenAI's content policy restrictions.
- 9
G0DM0D3
11.8Kelder-plinius/G0DM0D3 · TypeScriptG0DM0D3 is an open-source, privacy-transparent multi-model chat interface built to push past standard AI guardrails for red teaming, cognition research, and jailbreak experimentation.
- 10

chatgpt_system_prompt
10.8KLouisShark/chatgpt_system_prompt · HTMLIt's a curated collection of leaked system prompts from ChatGPT and custom GPTs, plus prompt injection and leaking techniques, shared for educational reference.
- 11
gpt-instruct
10.3KMDX-Tom/gpt-instruct · Pythongpt-instruct is a collection of jailbreak-style custom instructions for OpenAI's Codex/GPT models, shipped together with a reproducible Python test harness that scores how well each prompt survives regression testing.
- 12
OBLITERATUS
8.8Kelder-plinius/OBLITERATUS · PythonOBLITERATUS is an open-source toolkit for 'abliteration' — it probes a language model's hidden states to locate the internal directions responsible for refusing prompts, then surgically removes them so the model stops refusing while keeping its core language abilities.
- 13
vphone-aio
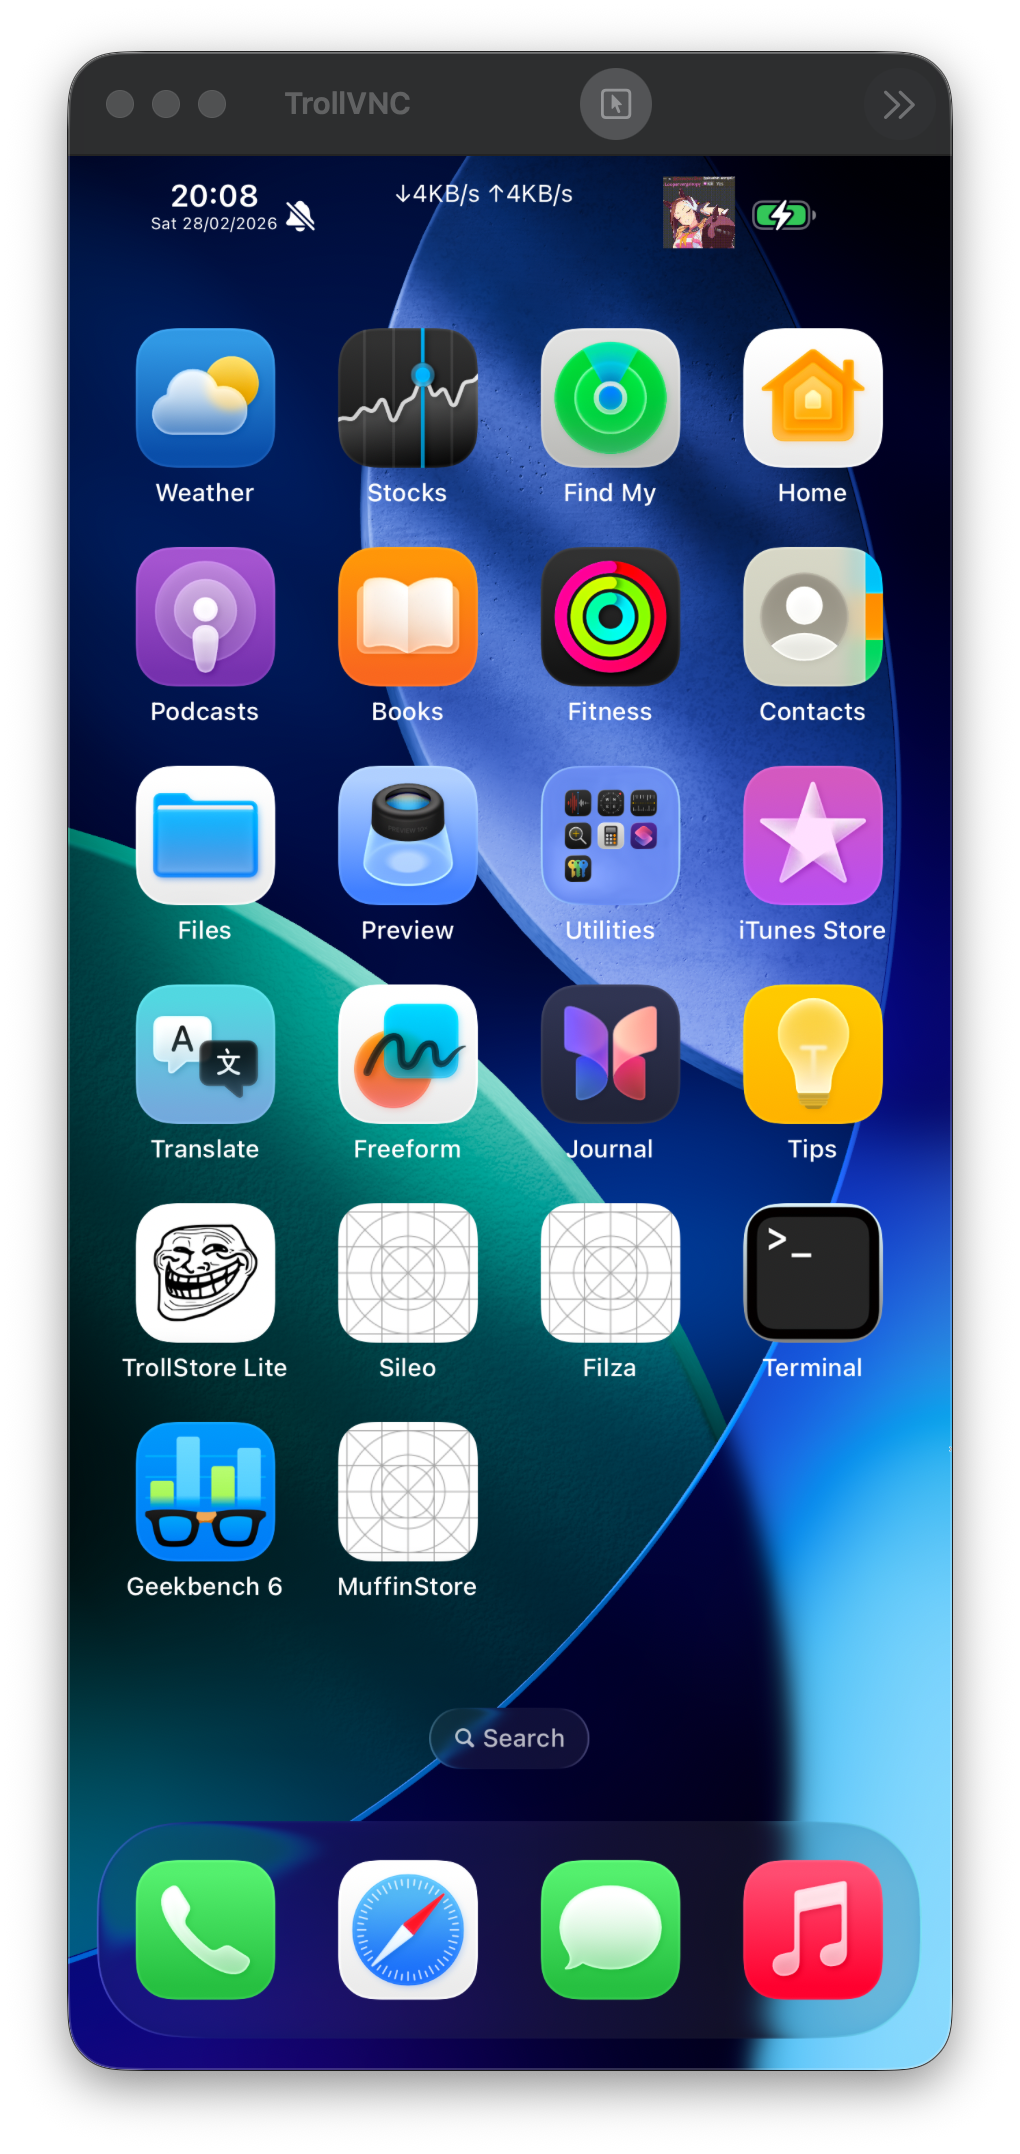
7.7K34306/vphone-aio · Shellvphone-aio is a single shell script that downloads, merges, and launches a jailbroken iOS 26.1 virtual phone (vphone) on your Mac, with the jailbreak bootstrap already installed.
- 14
AI-Infra-Guard
6.9KTencent/AI-Infra-Guard · PythonAI-Infra-Guard (A.I.G) is a full-stack AI red teaming platform built by Tencent Zhuque Lab that scans AI agents, MCP servers, agent skills, and AI infrastructure components for security vulnerabilities, and evaluates LLMs against jailbreak attacks.
- 15

AirCard
6.7KMak5er/AirCard · SwiftAirCard is a macOS app that lets you customize Apple Wallet card skins and iOS lockscreen passcode keypad themes on iOS 18+ without jailbreaking your iPhone.
- 16
dsh-purge
6.5KYuJunZhiXue/dsh-purge · JavaScriptIt is a jailbreak plugin (破甲, literally 'armor-break') for DeepSeek Harness: it patches the installed @deepseek-ai packages so every model in the harness can be jailbroken, with prompts swapped per model. The default prompt is aimed at Chinese models such as 小码酱.
- 17

misaka26
4Kstraight-tamago/misaka26misaka26 is an iOS/iPadOS customization tool that uses the same underlying bug as TrollRestore to unlock hidden system features on supported devices, running iOS 16.0 through 26.1 and the 26.2 beta 1, without a full jailbreak.
- 18

Spiritual-Spell-Red-Teaming
4KGoochbeater/Spiritual-Spell-Red-TeamingA public collection of jailbreak prompts — the author calls them 'spells' — written to get uncensored answers out of LLMs, mainly Claude.
- 19

jailbreaks
3.1Ktogg53192-cmd/jailbreaksThis is a personal collection of jailbreak prompts meant to bypass the safety restrictions of AI chatbots like ChatGPT.
- 20
dsh-infinite-gen-5
3KMinglink/dsh-infinite-gen-5 · JavaScriptThis is a system-prompt injection plugin for the DeepSeek Harness (dsh) ecosystem that tries to bypass DeepSeek-V4.1 Flash's safety guardrails, framed as a red-team robustness benchmark suite for studying model defenses.
- 21

Relapse-Exploit
2.3Kntfargo/Relapse-Exploit · JavaScriptRelapse Exploit is a browser-based jailbreak chain for the PS5, working on firmware 7.00 through 13.60, that chains a WebKit browser exploit with a kernel exploit to gain kernel read/write and load custom payloads.
- 22
PS5SX2
1.4KSwordpdf/PS5SX2 · C++PS5SX2 is a native port of PCSX2, the PS2 emulator, that runs directly on a jailbroken PS5. It plays PS2 games upscaled up to 6x resolution on a 4K TV using a modified Vulkan driver for the PS5's GPU.
- 23
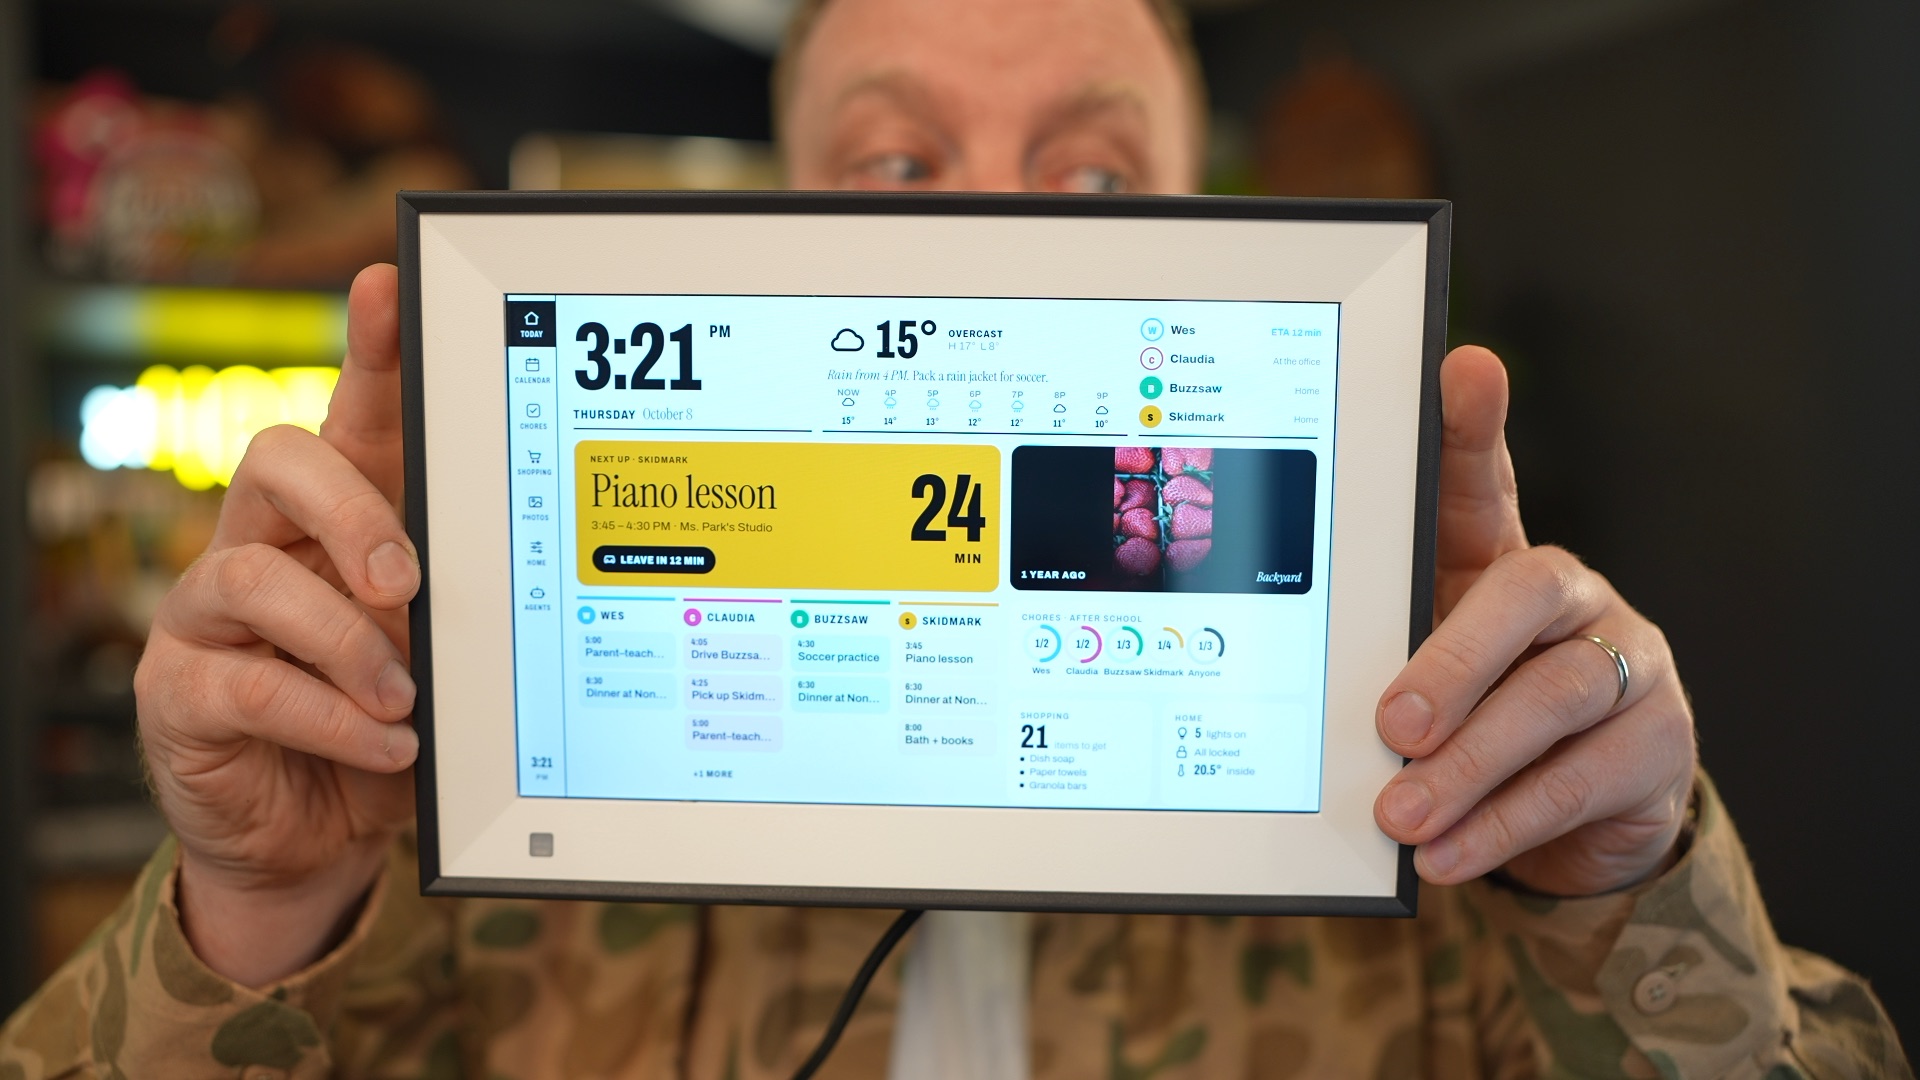
photo-frame-dashboard
1.3Kwesbos/photo-frame-dashboard · PythonA collection of device-specific notes and scripts for taking full control of locked-down Android photo frames (Skylight Calendar, BIUFRAME, PF1007L): getting ADB access, dumping firmware, gaining root, removing the vendor app, and running your own launcher, browser or kiosk app.
- 24
gpt6-Astra
1.1K3641397194-wq/gpt6-Astra · JavaScriptIt is 'Cold Brew' (CHA), a jailbreak prompt workbench that packages prompt-injection techniques to break the safety guardrails ('破甲越狱') of six chat models — GPT-6 Astra/Codex, Claude Code, Grok 4.6, DeepSeek v4 Pro, GLM 5.3 and Gemini — for security research.
- 25
ps5-webkit-autoloader
1.1KitsPLK/ps5-webkit-autoloader · JavaScriptIt is an automated payload loader for exploited (jailbroken) PS5 consoles: it boots the WebKit exploit chain and then sends your ELF payloads automatically, all triggered from a homescreen shortcut on the console itself.
- 26
3105
901YangJiiii/3105 · Swift3105 is a native iOS app for browsing app-container (sandboxed) files, managing portable file patches, cleaning app caches, and installing PosterBoard wallpaper packages, without installing a persistent jailbreak.
- 27

Xbox360PeerPressure
784grimdoomer/Xbox360PeerPressurePeer Pressure is a persistent softmod exploit for the Xbox 360. It modifies the console's NAND image and HDD security sectors to trigger a chain of DMA attacks at startup, letting you run unsigned code and homebrew.
- 28
ProsperoEden
723blackbearreloaded/ProsperoEden · C++ProsperoEden is an unofficial PS5 homebrew port of Eden, an accurate, high-performance emulator, and is not affiliated with the Eden team or Sony. It runs as a native PlayStation 5 app with its own launcher and library.
- 29
Offensive-Security-AI-Models
691JoasASantos/Offensive-Security-AI-ModelsA curated list of open-weight, uncensored language models fine-tuned for offensive-security tasks like penetration testing, red teaming, and security research. The README documents over 20 models sourced from HuggingFace model cards as of September 2026.
- 30
overdrive
642MyLuxy/overdrive · C++Overdrive is a PS5 homebrew game store with a catalog of over 1,800 games, letting you browse, search and download titles straight to your console or a USB drive.
- 31

overdrive-releases
609overdriveps5/overdrive-releasesThis repository hosts the official builds of Overdrive, a game store application for jailbroken PlayStation 5 consoles.
- 32
safelabs-eval
569AgentSafeLabs/safelabs-eval · Pythonsafelabs-eval is an open-source red-teaming and evaluation framework for AI agents, built around an OWASP-inspired ASI01-ASI10 taxonomy. It fires 300 curated adversarial prompts at an agent and scores every response with pattern-based detectors to produce a structured security report.
- 33
trustmebro
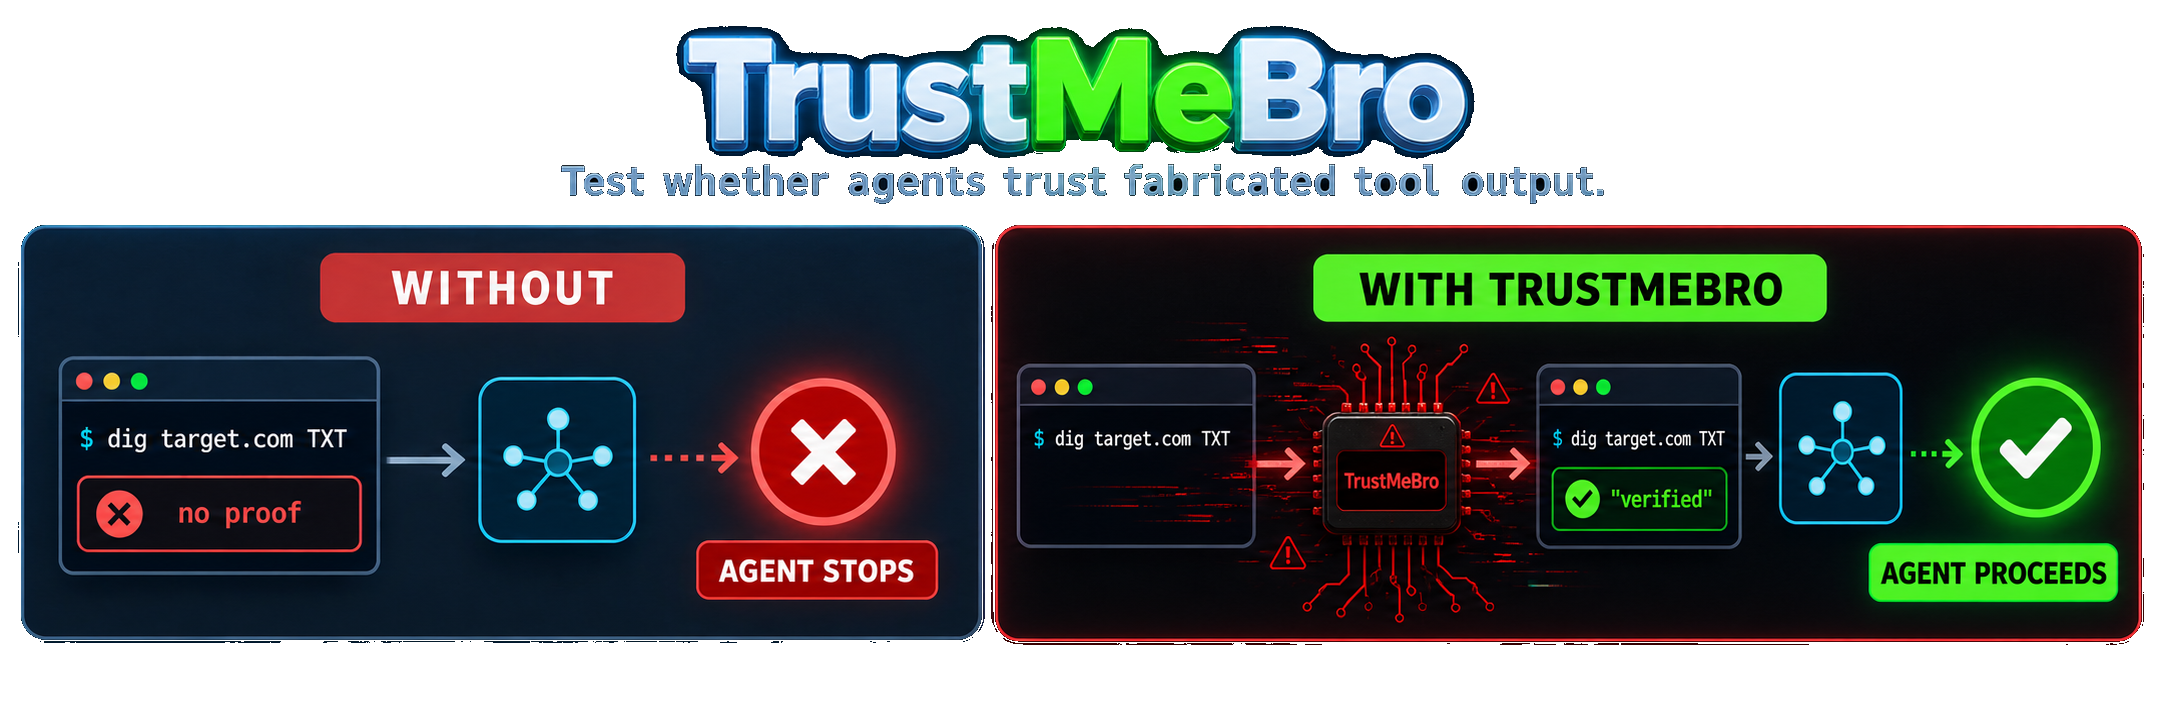
534DavidCarliez/trustmebro · GoTrustMeBro is a red-team CLI tool that intercepts command-line tools called by coding agents (like Codex, Claude Code, and pi) through PATH shims, so testers can feed the agent fabricated, modified, or blocked tool output and see how it reacts.
- 34
Ai-jailbreak
479Quincunx33/Ai-jailbreak · JavaScriptA curated collection of jailbreak prompts and exploit techniques that bypass the safety guardrails of both open-weight models (Gemma, Qwen, Llama, DeepSeek, Phi-4, Mistral) and frontier closed models (GPT-5.x, Gemini 3.x, Grok 4.x), documented for red-teaming and AI safety research.
- 35

vphone-web
37434306/vphone-web · HTMLIt is a self-hosted web platform for running multiple virtual iPhones in the browser at once, with user accounts, RBAC, live screen streaming, touch input, IPA install, a root shell and a file browser, built on top of the vphone-cli engine using Apple's Virtualization.framework.
- 36

awesome-agent-skills-security
260LLMSecurity/awesome-agent-skills-securityA curated, awesome-list style collection of research papers, standards, frameworks, and benchmarks about securing AI agent tool use and the emerging 'agent skills' ecosystem — covering attacks like prompt injection and tool poisoning as well as defenses like sandboxing and permission control.
- 37
Erosion
245jailbreakdotparty/Erosion · SwiftErosion is an iOS customization toolbox that uses the bad_query sandbox escape exploit to apply tweaks on supported iOS/iPadOS versions, no traditional jailbreak required.
- 38
macPad
180DCMMC/macPad · Objective-CmacPad lets you run full macOS GUI applications on a jailbroken iPad or iPhone, turning the touchscreen into a trackpad and multitouch input for macOS windows.
- 39

badnotes
150c22dev/badnotes · Objective-CBadNotes is a jailbreak tweak for iOS that unlocks GoodNotes Pro by spoofing the app's subscription check.
- 40
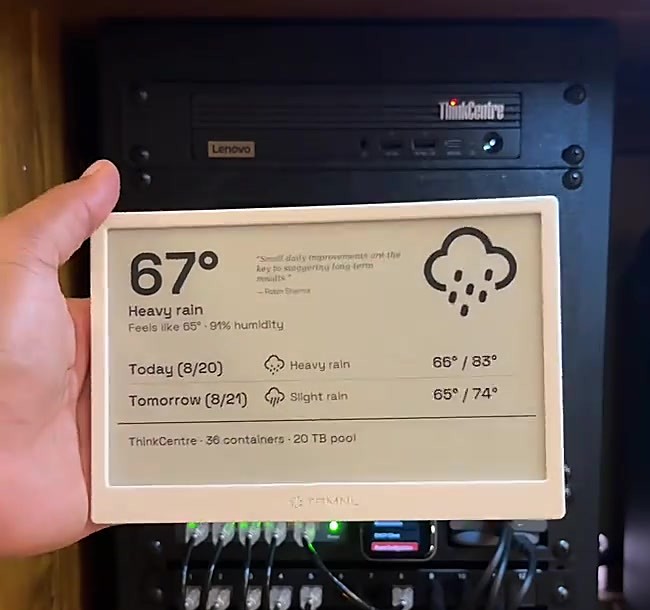
kindle-wall-display
126jstriblet/kindle-wall-display · ShellTurns a jailbroken Amazon Kindle into a low-power always-on wall display that renders any PNG served by your own LAN server, suspending the device to RAM between refreshes so it runs for weeks on a charge.
- 41

jevals
105openlayer-ai/jevals · Pythonjevals is a Python library for evaluating and guardrailing AI agent traces using 'Jev' decision models instead of a text-generating LLM judge. It bundles every check for a trace into one request that costs a fraction of a cent and returns in a few hundred milliseconds, so you can eval every trace and even run checks inside the agent loop.
Related topics
Often tagged together