Topics / #vulnerability-scanners
Vulnerability-scanners projects on GitHub
Scanners that detect vulnerabilities in containers, code, and dependencies.
As of , the most-starred Vulnerability-scanners projects on GitHub are trivy (38.5K stars), promptfoo (26.1K stars) and lynis (16.5K stars). GitHub.Locker tracks 5 Vulnerability-scanners repositories with 94.7K stars combined. The fastest-growing on October 18 was ARTEX, with +45 stars in a day.
Hot right now
Most stars gained in a day · Oct 18
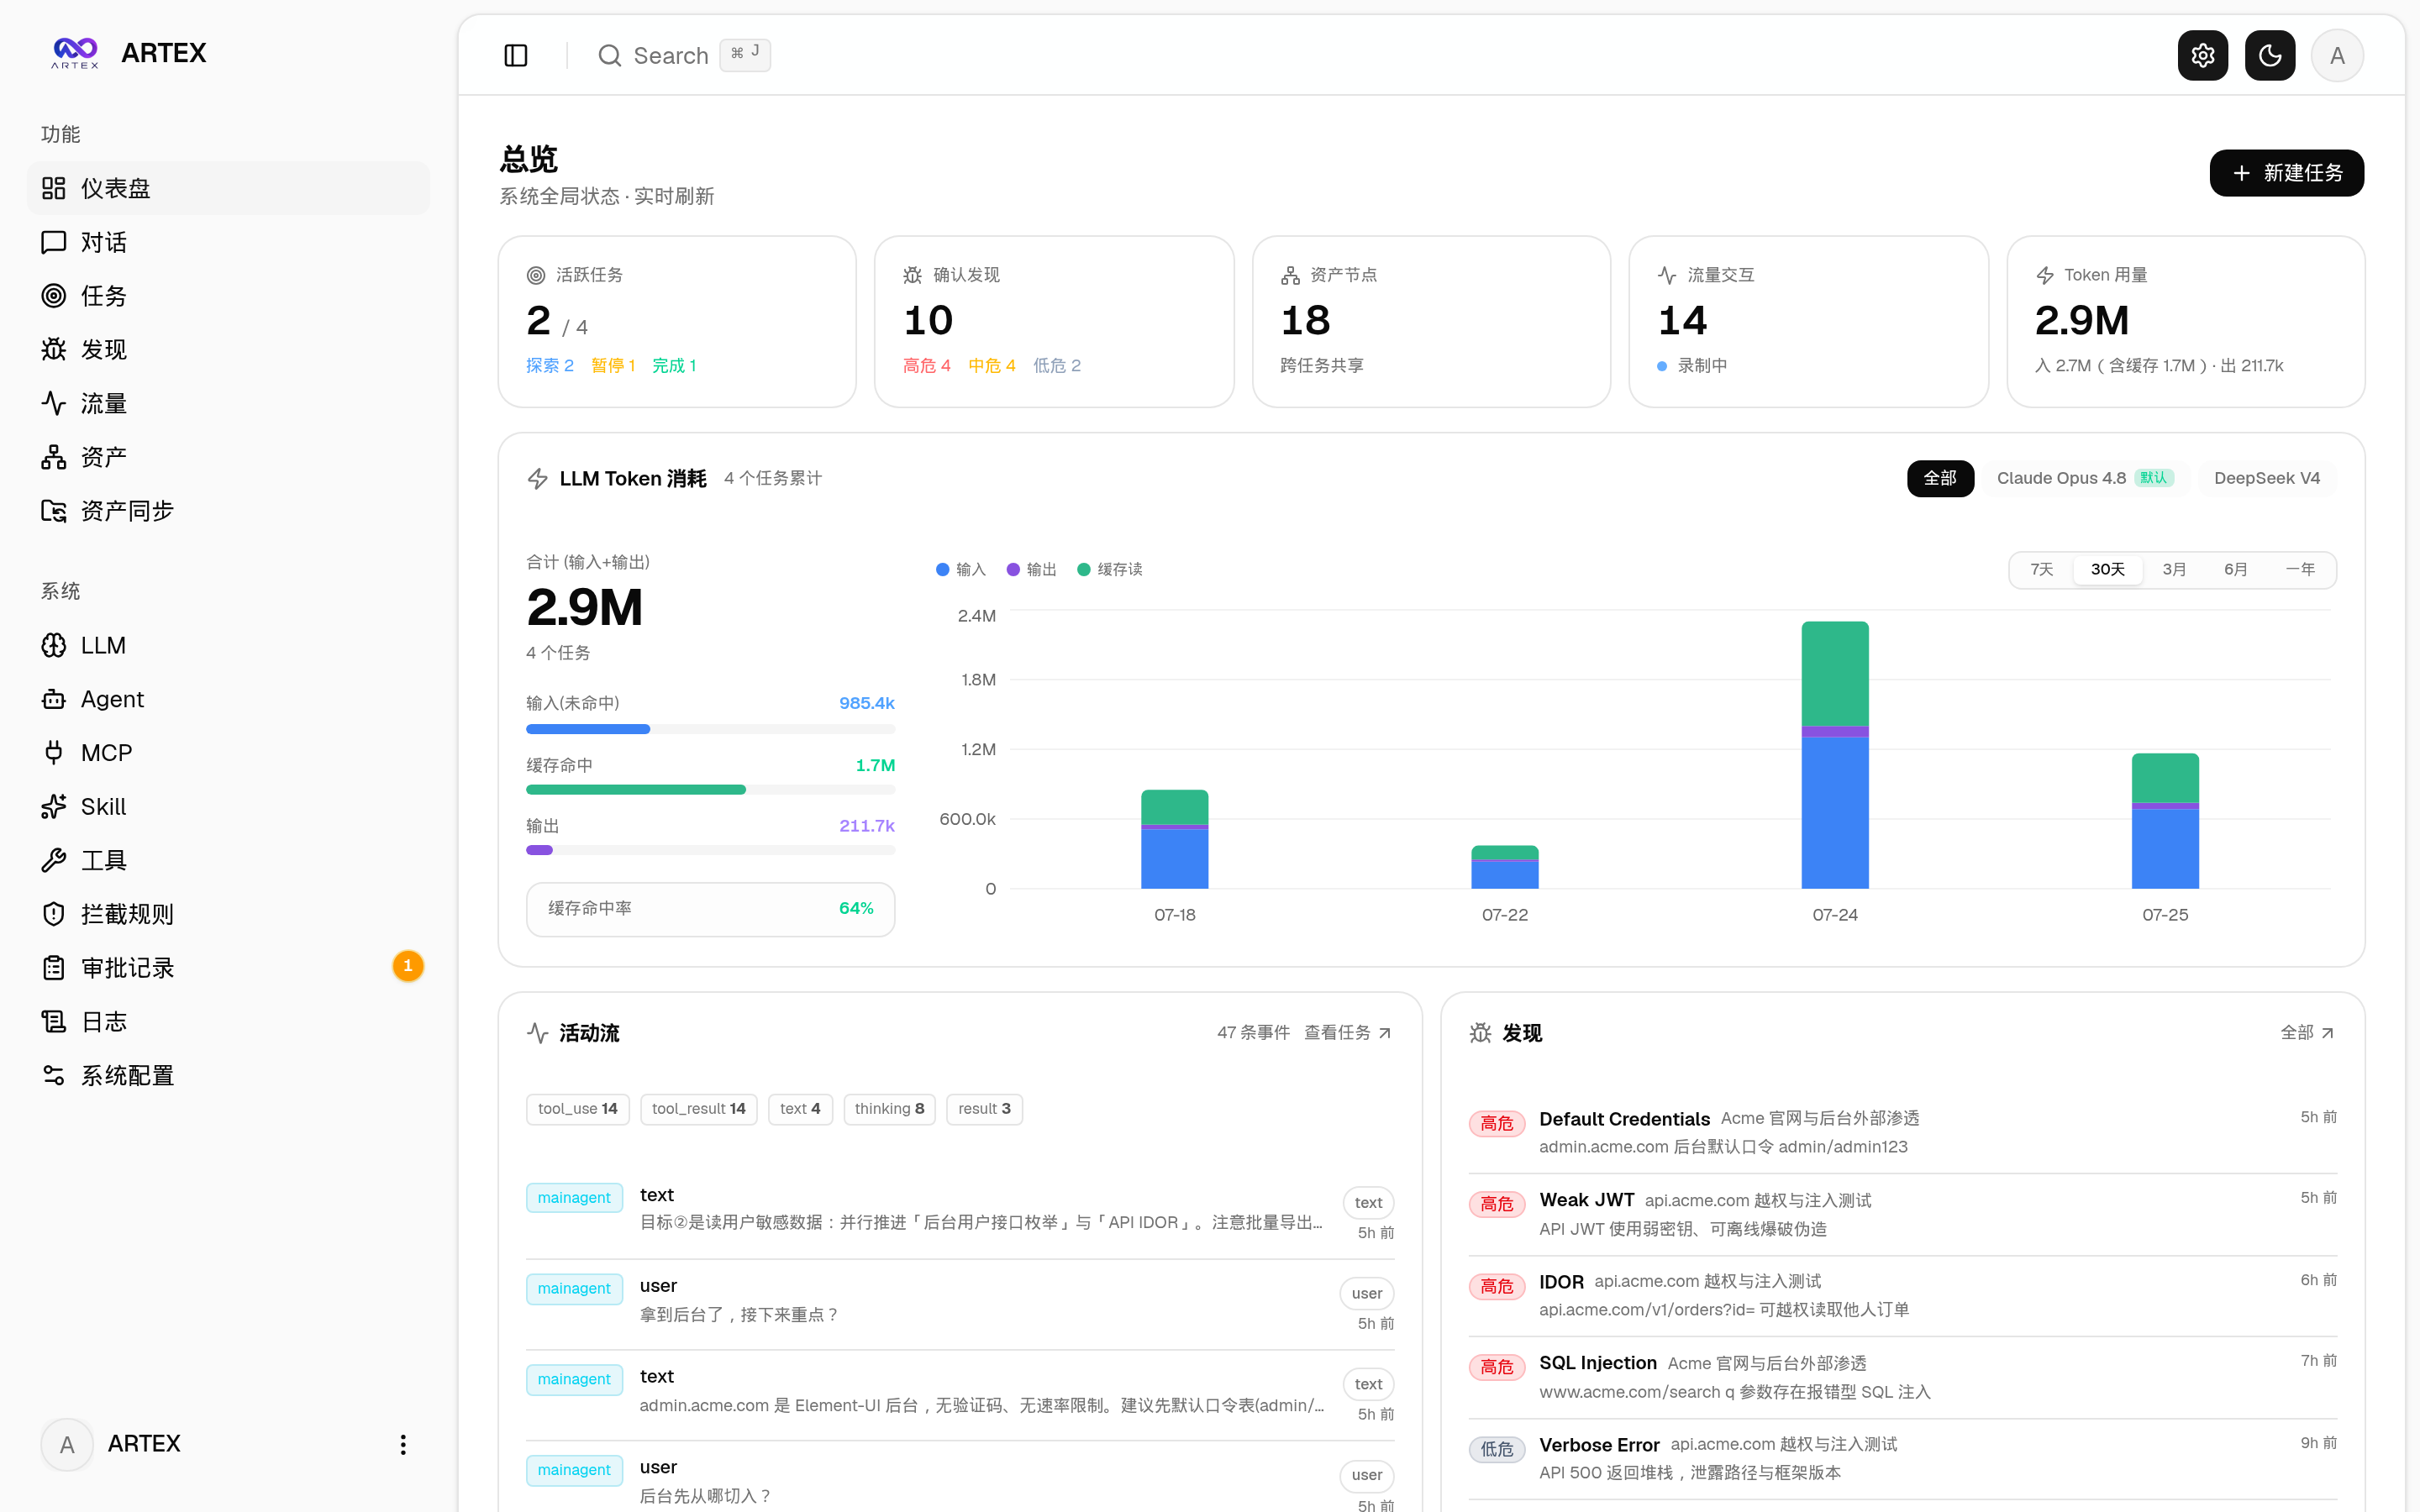 +45
ARTEX
trhhubsd/ARTEX · ★ 1.3KARTEX is an AI-driven autonomous penetration testing system (Go backend + Next.js frontend) where LLM-powered planner and worker agents explore targets, map assets, and find vulnerabilities on their own.
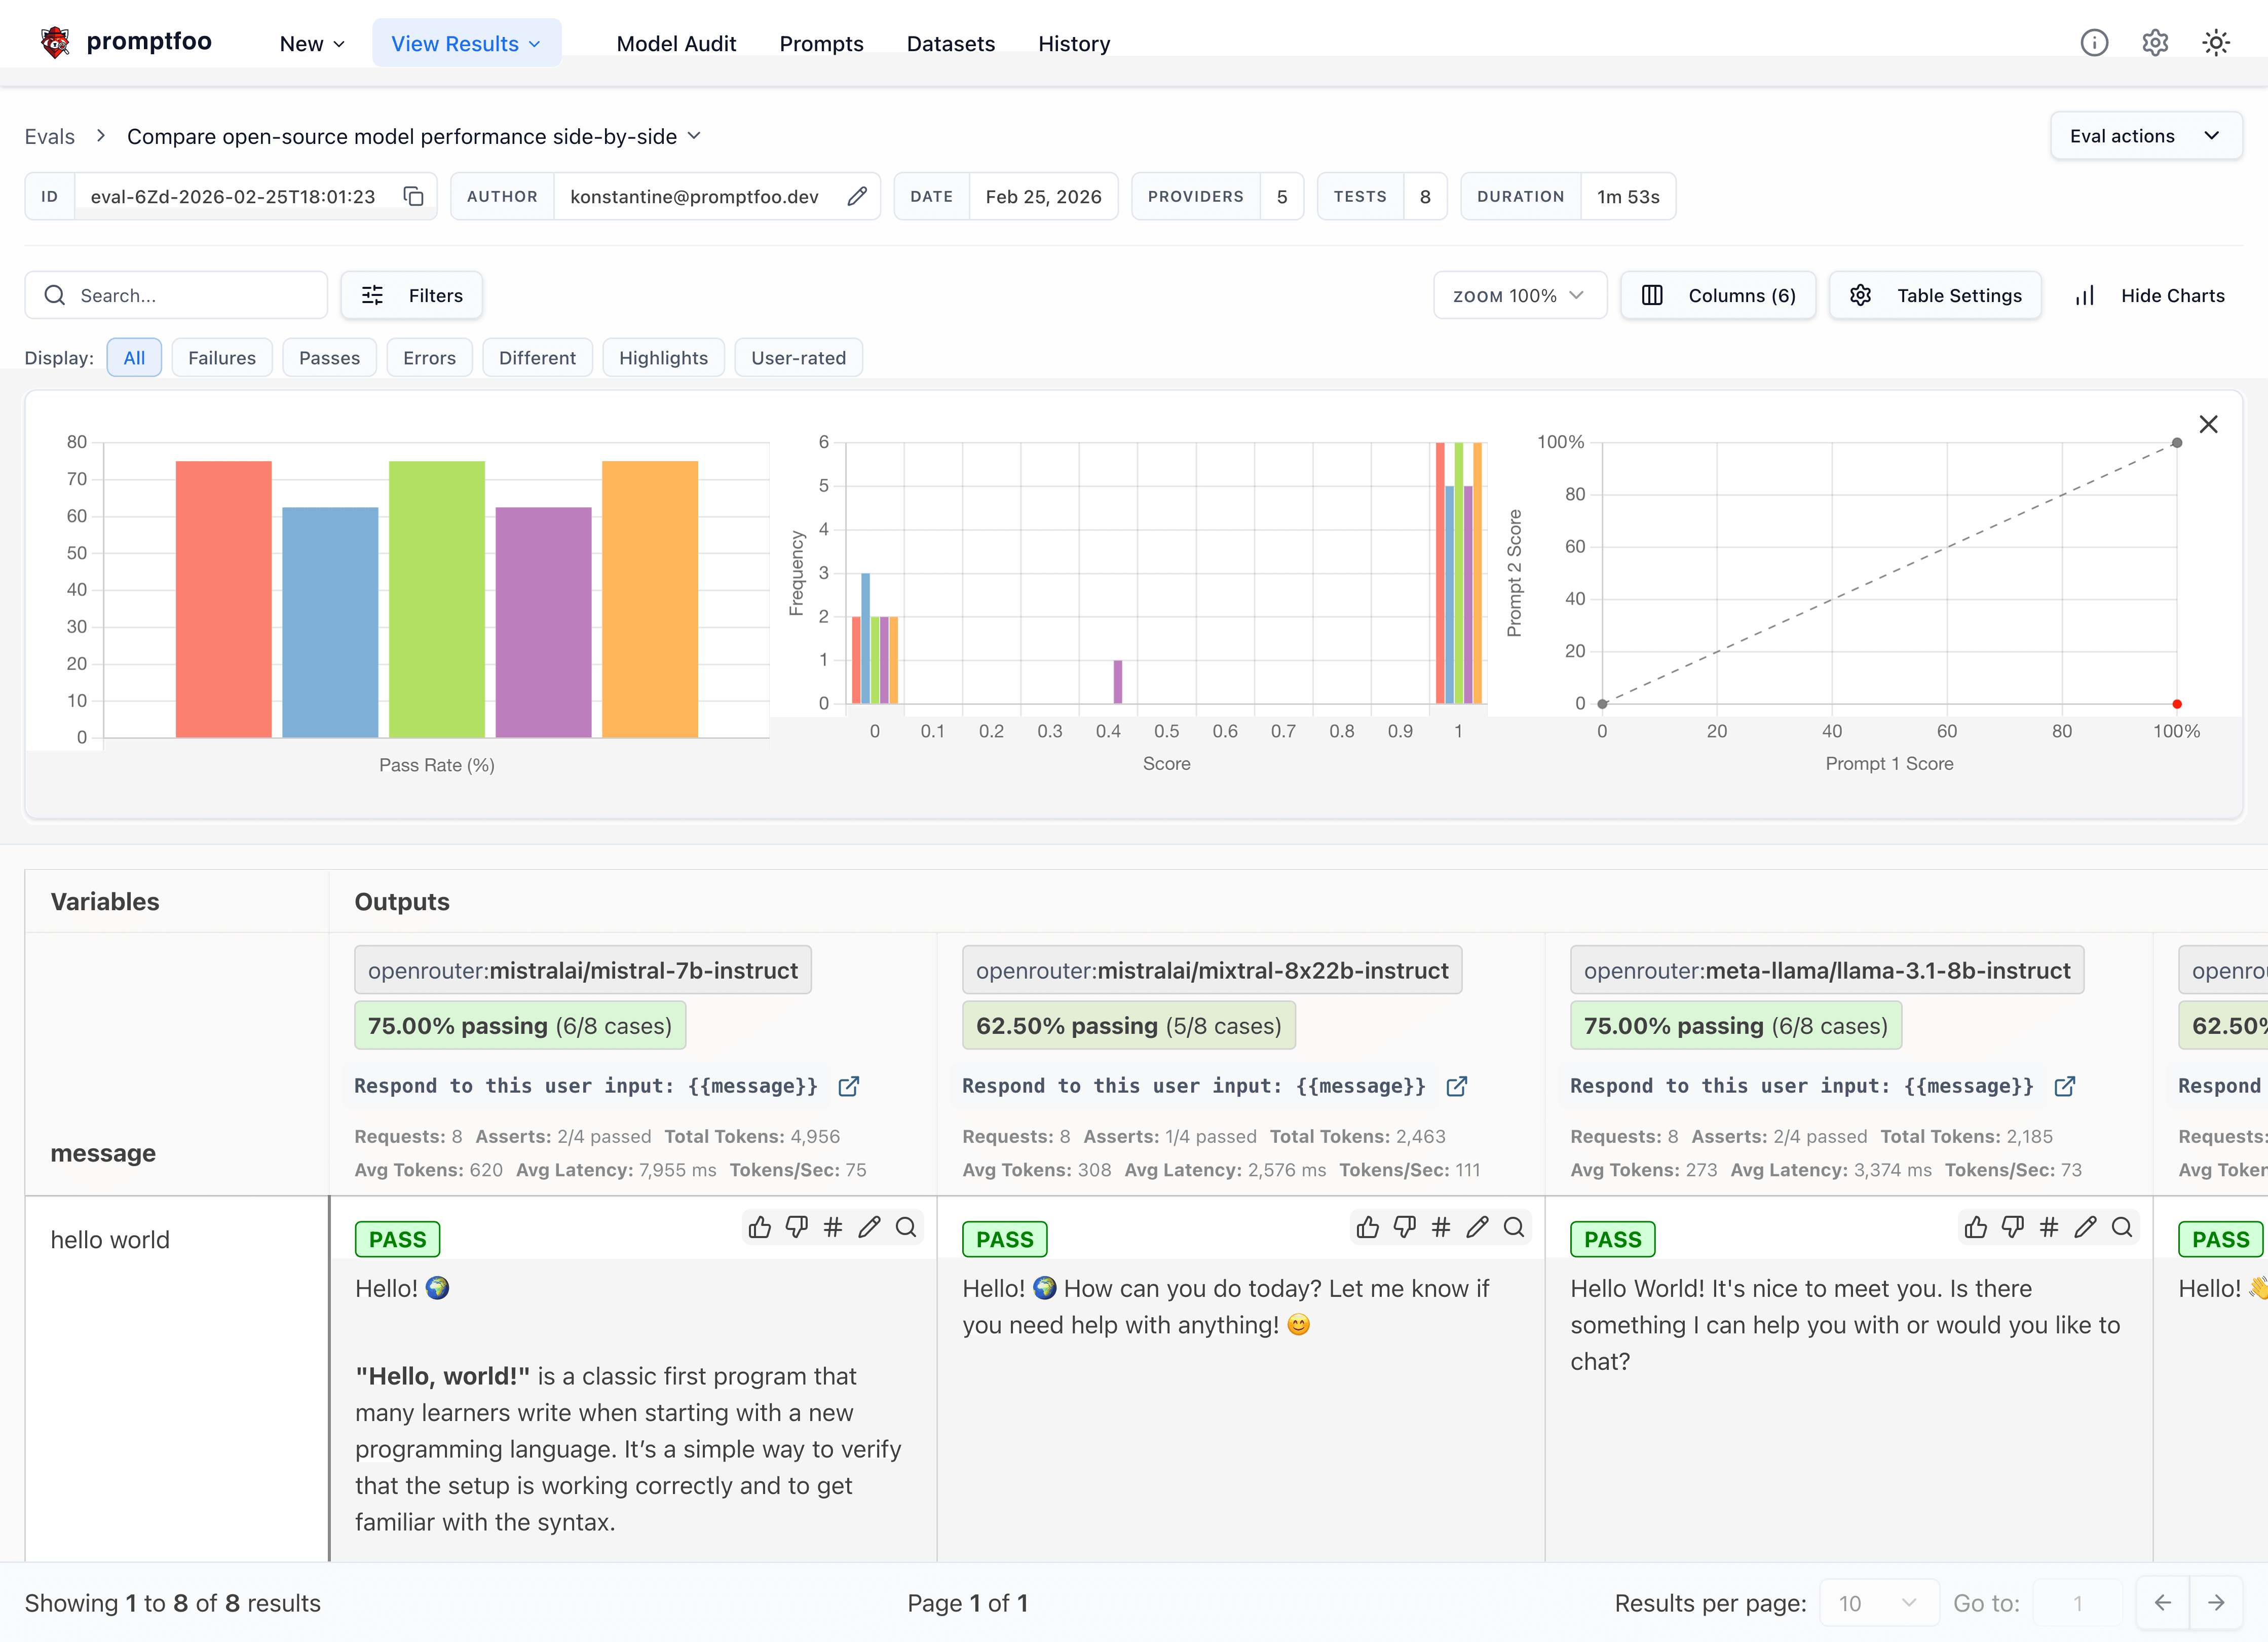 +31
promptfoo
promptfoo/promptfoo · ★ 26.1Kpromptfoo is a CLI and library for evaluating and red-teaming LLM apps — you test prompts, agents, and RAGs and run security scans on them, instead of relying on trial-and-error.
 +16
trivy
aquasecurity/trivy · ★ 38.5KTrivy is an all-in-one security scanner that finds vulnerabilities, misconfigurations, secrets, and software licenses across container images, filesystems, git repositories, VM images, and Kubernetes clusters.
lynis
CISOfy/lynis · ★ 16.5KLynis is a security auditing and hardening tool for Linux, macOS, BSD, and other Unix-like systems. It scans the host it runs on for vulnerable software, misconfigurations, and weak settings, and gives hardening tips while also assisting with compliance testing (HIPAA, ISO27001, PCI DSS).
The all-time top
5 projects · by stars
- 38.5K#1 · aquasecurity/trivy
trivy
Trivy is an all-in-one security scanner that finds vulnerabilities, misconfigurations, secrets, and software licenses across container images, filesystems, git repositories, VM images, and Kubernetes clusters.
- 26.1K#2 · promptfoo/promptfoo
promptfoo
promptfoo is a CLI and library for evaluating and red-teaming LLM apps — you test prompts, agents, and RAGs and run security scans on them, instead of relying on trial-and-error.
- 16.5K
#3 · CISOfy/lynis
lynis
Lynis is a security auditing and hardening tool for Linux, macOS, BSD, and other Unix-like systems. It scans the host it runs on for vulnerable software, misconfigurations, and weak settings, and gives hardening tips while also assisting with compliance testing (HIPAA, ISO27001, PCI DSS).
- 4
vuls
12.3Kfuture-architect/vuls · GoVuls is an open-source, agent-less vulnerability scanner written in Go. It automatically detects vulnerabilities affecting your servers and can generate reports on a regular basis, for example via CRON.
- 5
ARTEX
1.3Ktrhhubsd/ARTEX · GoARTEX is an AI-driven autonomous penetration testing system (Go backend + Next.js frontend) where LLM-powered planner and worker agents explore targets, map assets, and find vulnerabilities on their own.
Related topics
Often tagged together
- linux4,248
- macos3,608
- security998
- cli2,275
- docker1,684
- open-source5,749
- security-tools287
- windows3,480
- cybersecurity249
- go695
- vulnerability-detection11
- vulnerability-scanner45
- ai1,993
- ai-security47
- cicd23
- cross-platform2,673
- devops458
- devsecops39
- freebsd65
- golang271
- llm1,516
- penetration-testing128
- pentesting114
- red-team82