Topics / #sarif
Sarif projects on GitHub
Tooling around security scan result formats, likely SARIF reporting.
As of , the most-starred Sarif projects on GitHub are shannon (49K stars), SkillSpector (20.4K stars) and pgbot (1.4K stars). GitHub.Locker tracks 7 Sarif repositories with 71.5K stars combined. The fastest-growing on October 16 was shannon, with +81 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
 +81
shannon
KeygraphHQ/shannon · ★ 49KShannon is an autonomous AI pentester that analyzes your web application's source code, maps attack vectors, and then executes real exploits against the running app to prove vulnerabilities before they reach production — 'no exploit, no report'.
SkillSpector
NVIDIA/SkillSpector · ★ 20.4KSkillSpector is a security scanner for AI agent skills (used by Claude Code, Codex CLI, Gemini CLI, and MCP) that detects vulnerabilities, malicious patterns, prompt injection, data exfiltration, and supply-chain risks before you install a skill.
 +8
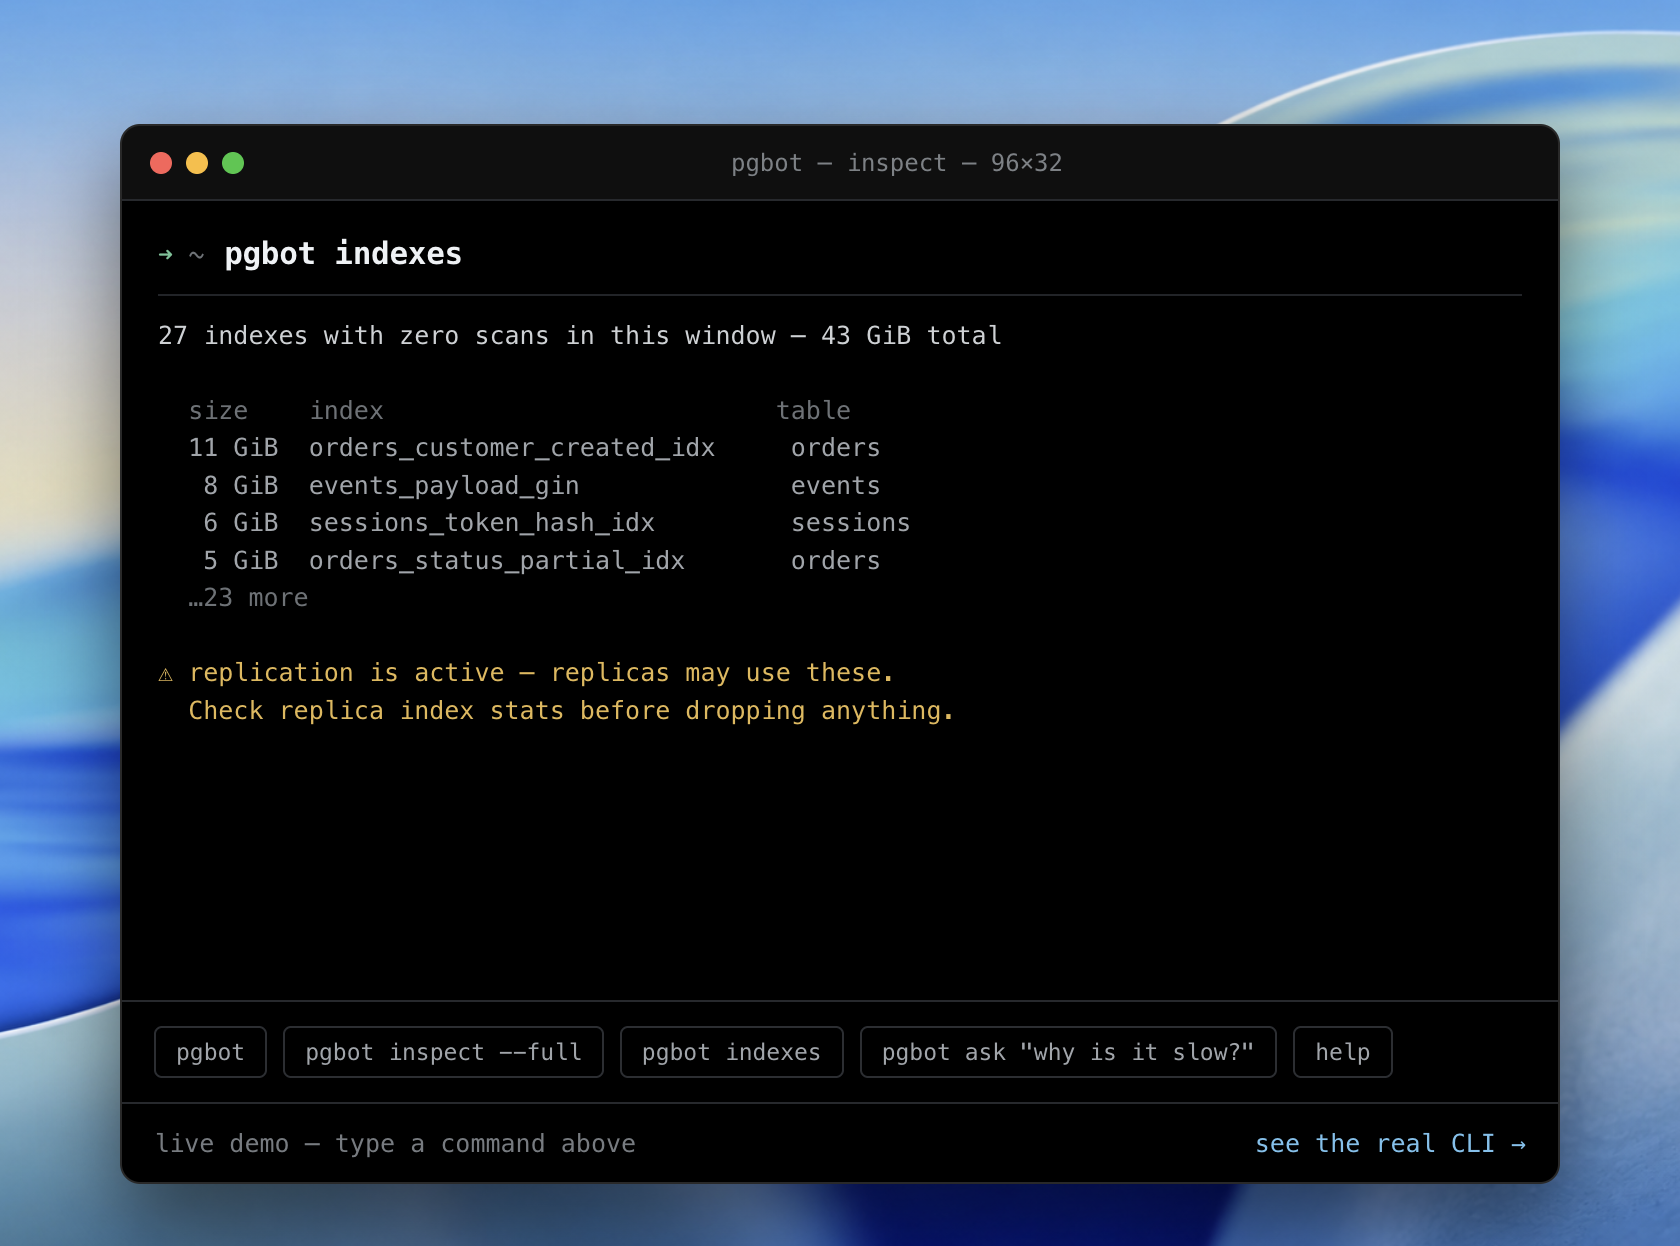
pgbot
pgrundev/pgbot · ★ 1.4Kpgbot is a static binary that connects read-only to a PostgreSQL database, reads its own statistics views, and prints a findings-first health report plus what changed since the last run.
The all-time top
7 projects · by stars
- 49K#1 · KeygraphHQ/shannon
shannon
Shannon is an autonomous AI pentester that analyzes your web application's source code, maps attack vectors, and then executes real exploits against the running app to prove vulnerabilities before they reach production — 'no exploit, no report'.
- 20.4K
#2 · NVIDIA/SkillSpector
SkillSpector
SkillSpector is a security scanner for AI agent skills (used by Claude Code, Codex CLI, Gemini CLI, and MCP) that detects vulnerabilities, malicious patterns, prompt injection, data exfiltration, and supply-chain risks before you install a skill.
- 1.4K#3 · pgrundev/pgbot
pgbot
pgbot is a static binary that connects read-only to a PostgreSQL database, reads its own statistics views, and prints a findings-first health report plus what changed since the last run.
- 4
EvalForge
210jsdhwfmax/EvalForge · PythonEvalForge turns AI evaluation results into reviewable, vendor-neutral release evidence for RAG applications and AI assistants, combining an offline RAG evaluator, a portable JSON artifact, and policy-as-code gates that output JSON, JUnit, and SARIF for CI systems.
- 5

Airsec
150bas3line/Airsec · TypeScriptAirsec is a CLI tool that drives a coding agent you already have installed (Claude Code, Codex, OpenCode, Command Code) through a structured, multi-pass security audit of your code, then turns the findings into an actionable report.
- 6

workbooklens
142chenweixin123/workbooklens · PythonWorkbookLens is a local-first tool that lints, regression-tests, semantic-diffs, and conservatively repairs Excel workbooks, running entirely on your machine without Excel, LibreOffice, an AI key, or a cloud service.
- 7

Myrqen
137stijnswapped/Myrqen · TypeScriptMyrqen is a security testing tool that runs inside a coding agent (Claude Code, Codex, or OpenCode) you already use: its own static analysis engine finds vulnerability candidates in your TypeScript/JavaScript code, then the agent dynamically verifies them against the app running on your machine.
Related topics
Often tagged together
- linux4,184
- macos3,544
- windows3,403
- cli2,227
- developer-tools2,924
- open-source5,666
- security976
- cross-platform2,623
- docker1,660
- security-tools282
- ci208
- claude-code903
- command-line-tool715
- devsecops38
- github-actions167
- nodejs1,506
- python2,383
- static-analysis125
- typescript1,821
- vulnerability-scanner43
- ai1,955
- ai-agent556
- ai-agents1,289
- ai-security44