

What is this?
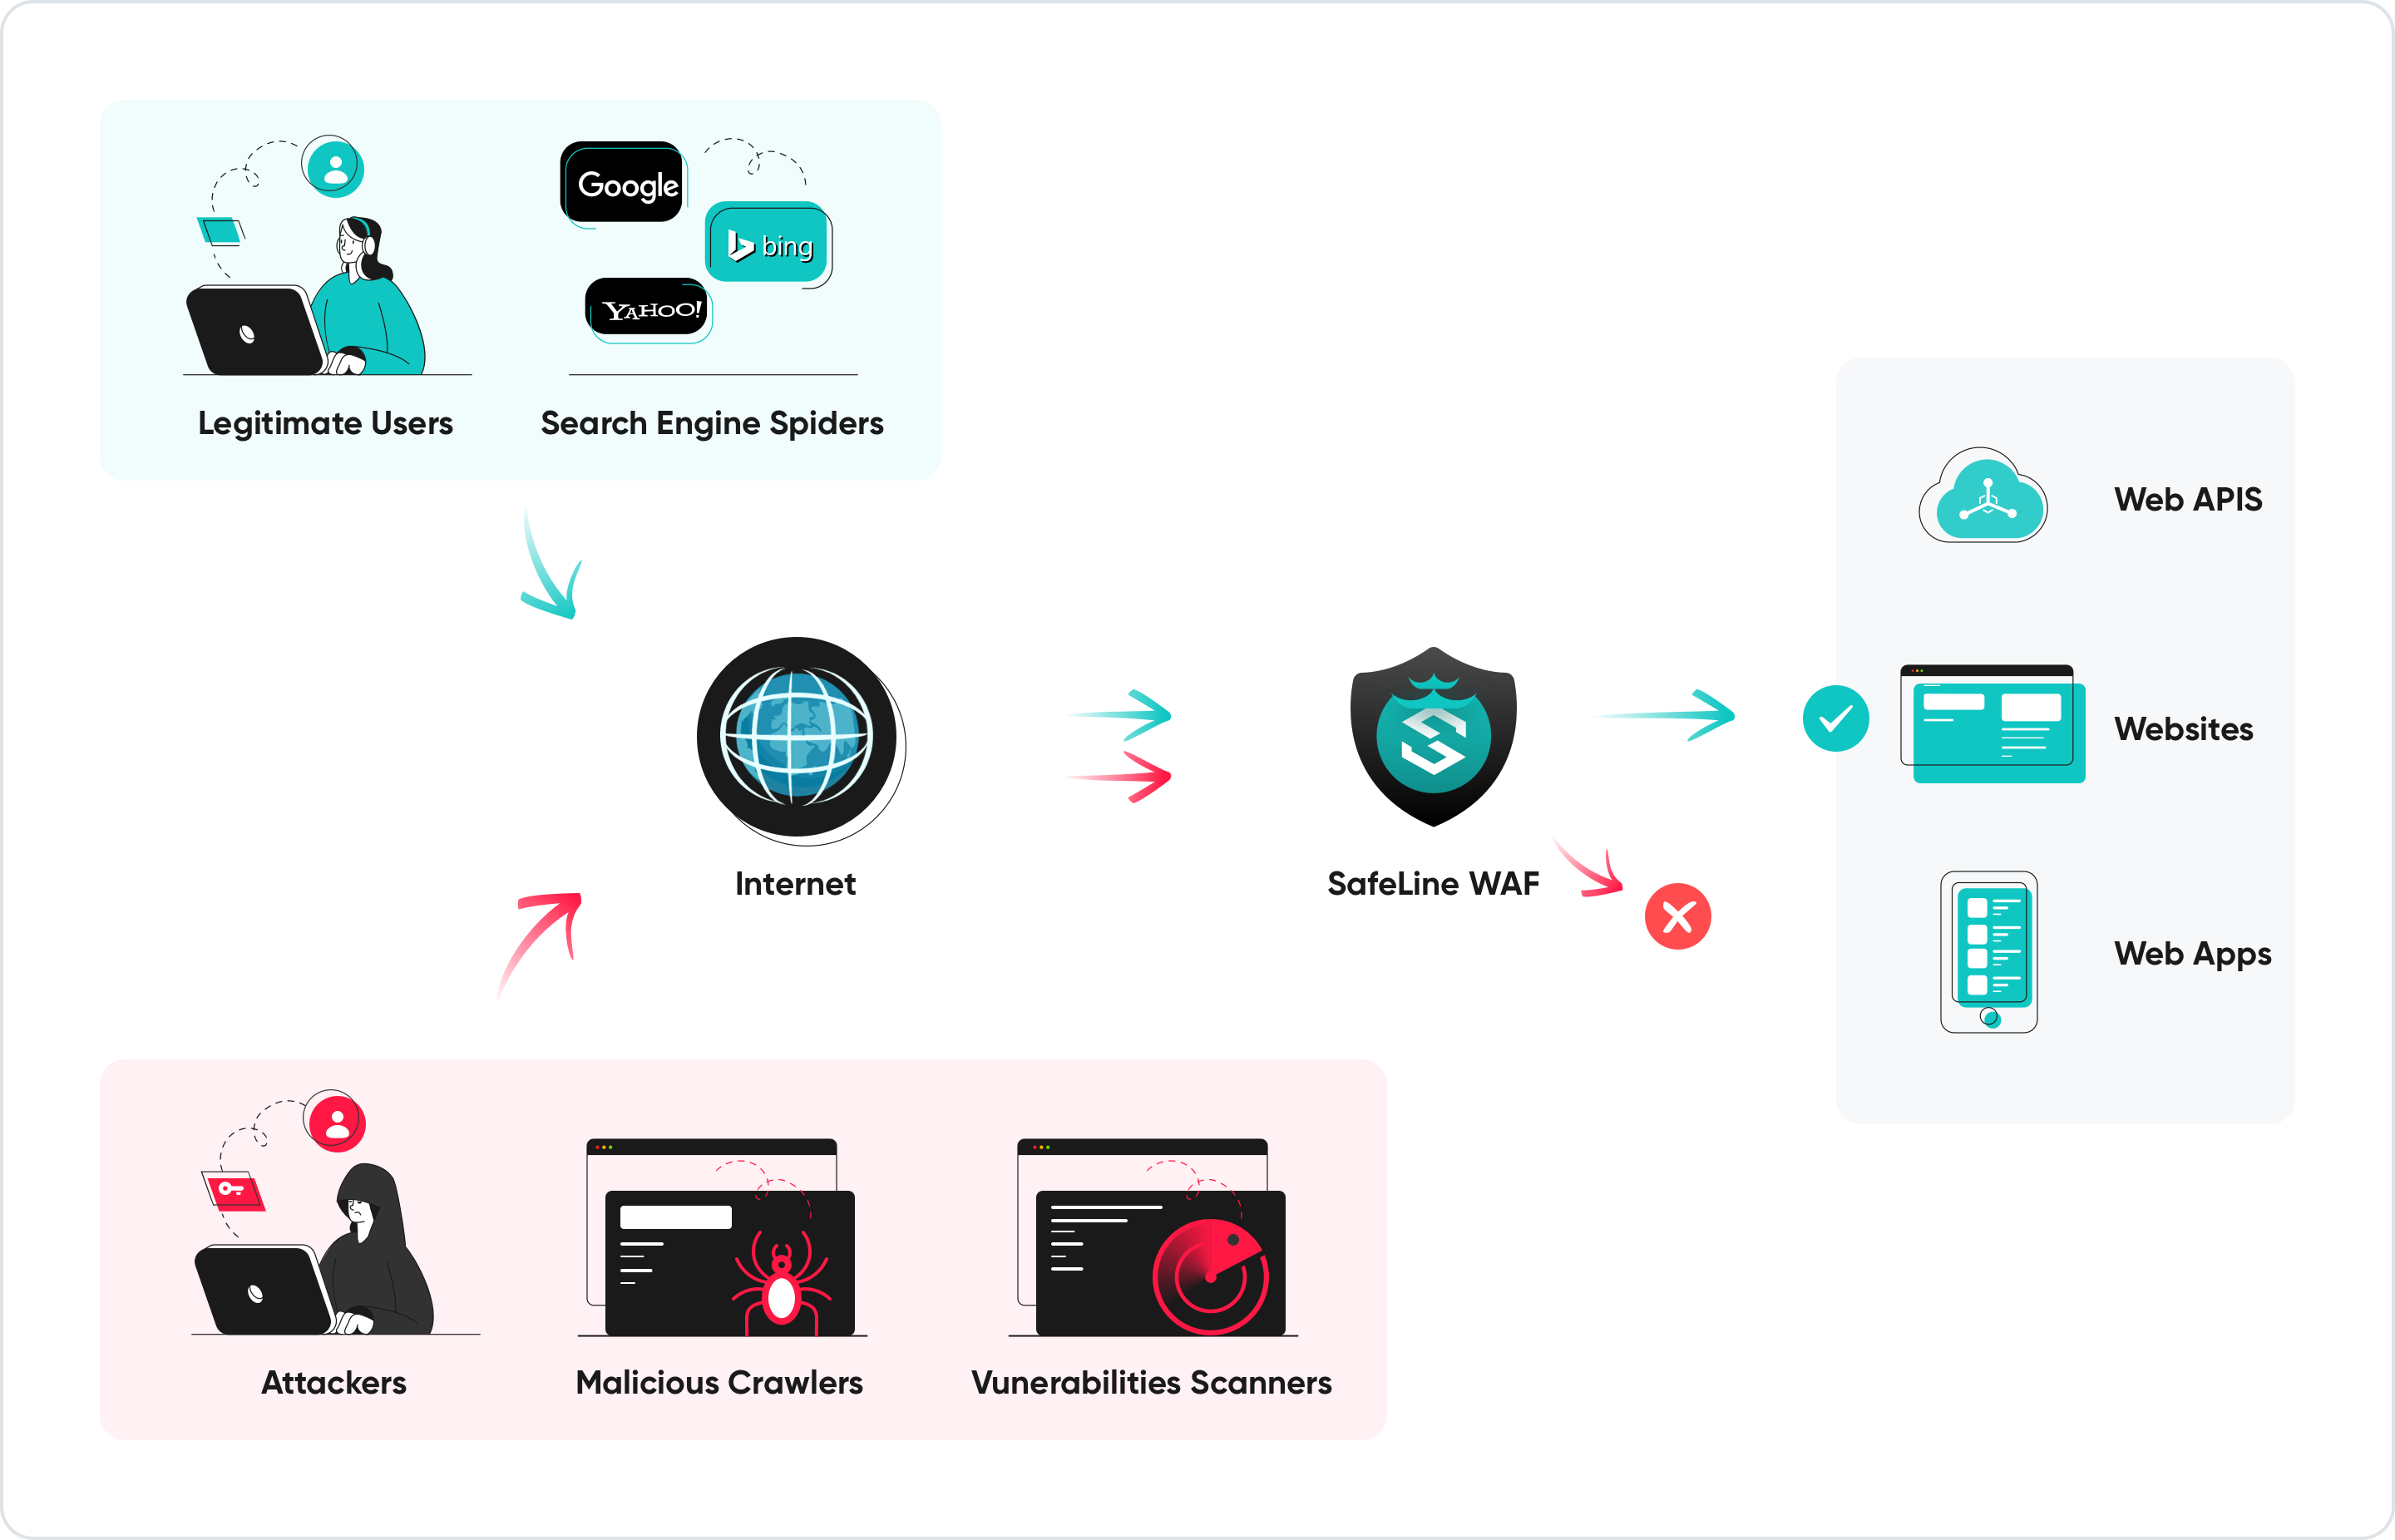
 SafeLine is a self-hosted web application firewall (WAF) and reverse proxy that protects your web apps from attacks and exploits by filtering and monitoring HTTP traffic.
Does it run inside my app, or in front of it?In front: it works as a reverse proxy, so client traffic passes through SafeLine before reaching your server, and it filters, monitors and blocks malicious HTTP/S requests on the way in.
In front: it works as a reverse proxy, so client traffic passes through SafeLine before reaching your server, and it filters, monitors and blocks malicious HTTP/S requests on the way in.Do I need to modify my application's code?No. SafeLine acts as a shield between the Internet and your app and enforces its policies on the passing traffic, so the app itself stays untouched.
No. SafeLine acts as a shield between the Internet and your app and enforces its policies on the passing traffic, so the app itself stays untouched.Are there any setup gotchas?Mainland-China users should install with the Chinese-edition docs: the international edition can fail to connect to SafeLine's cloud services.
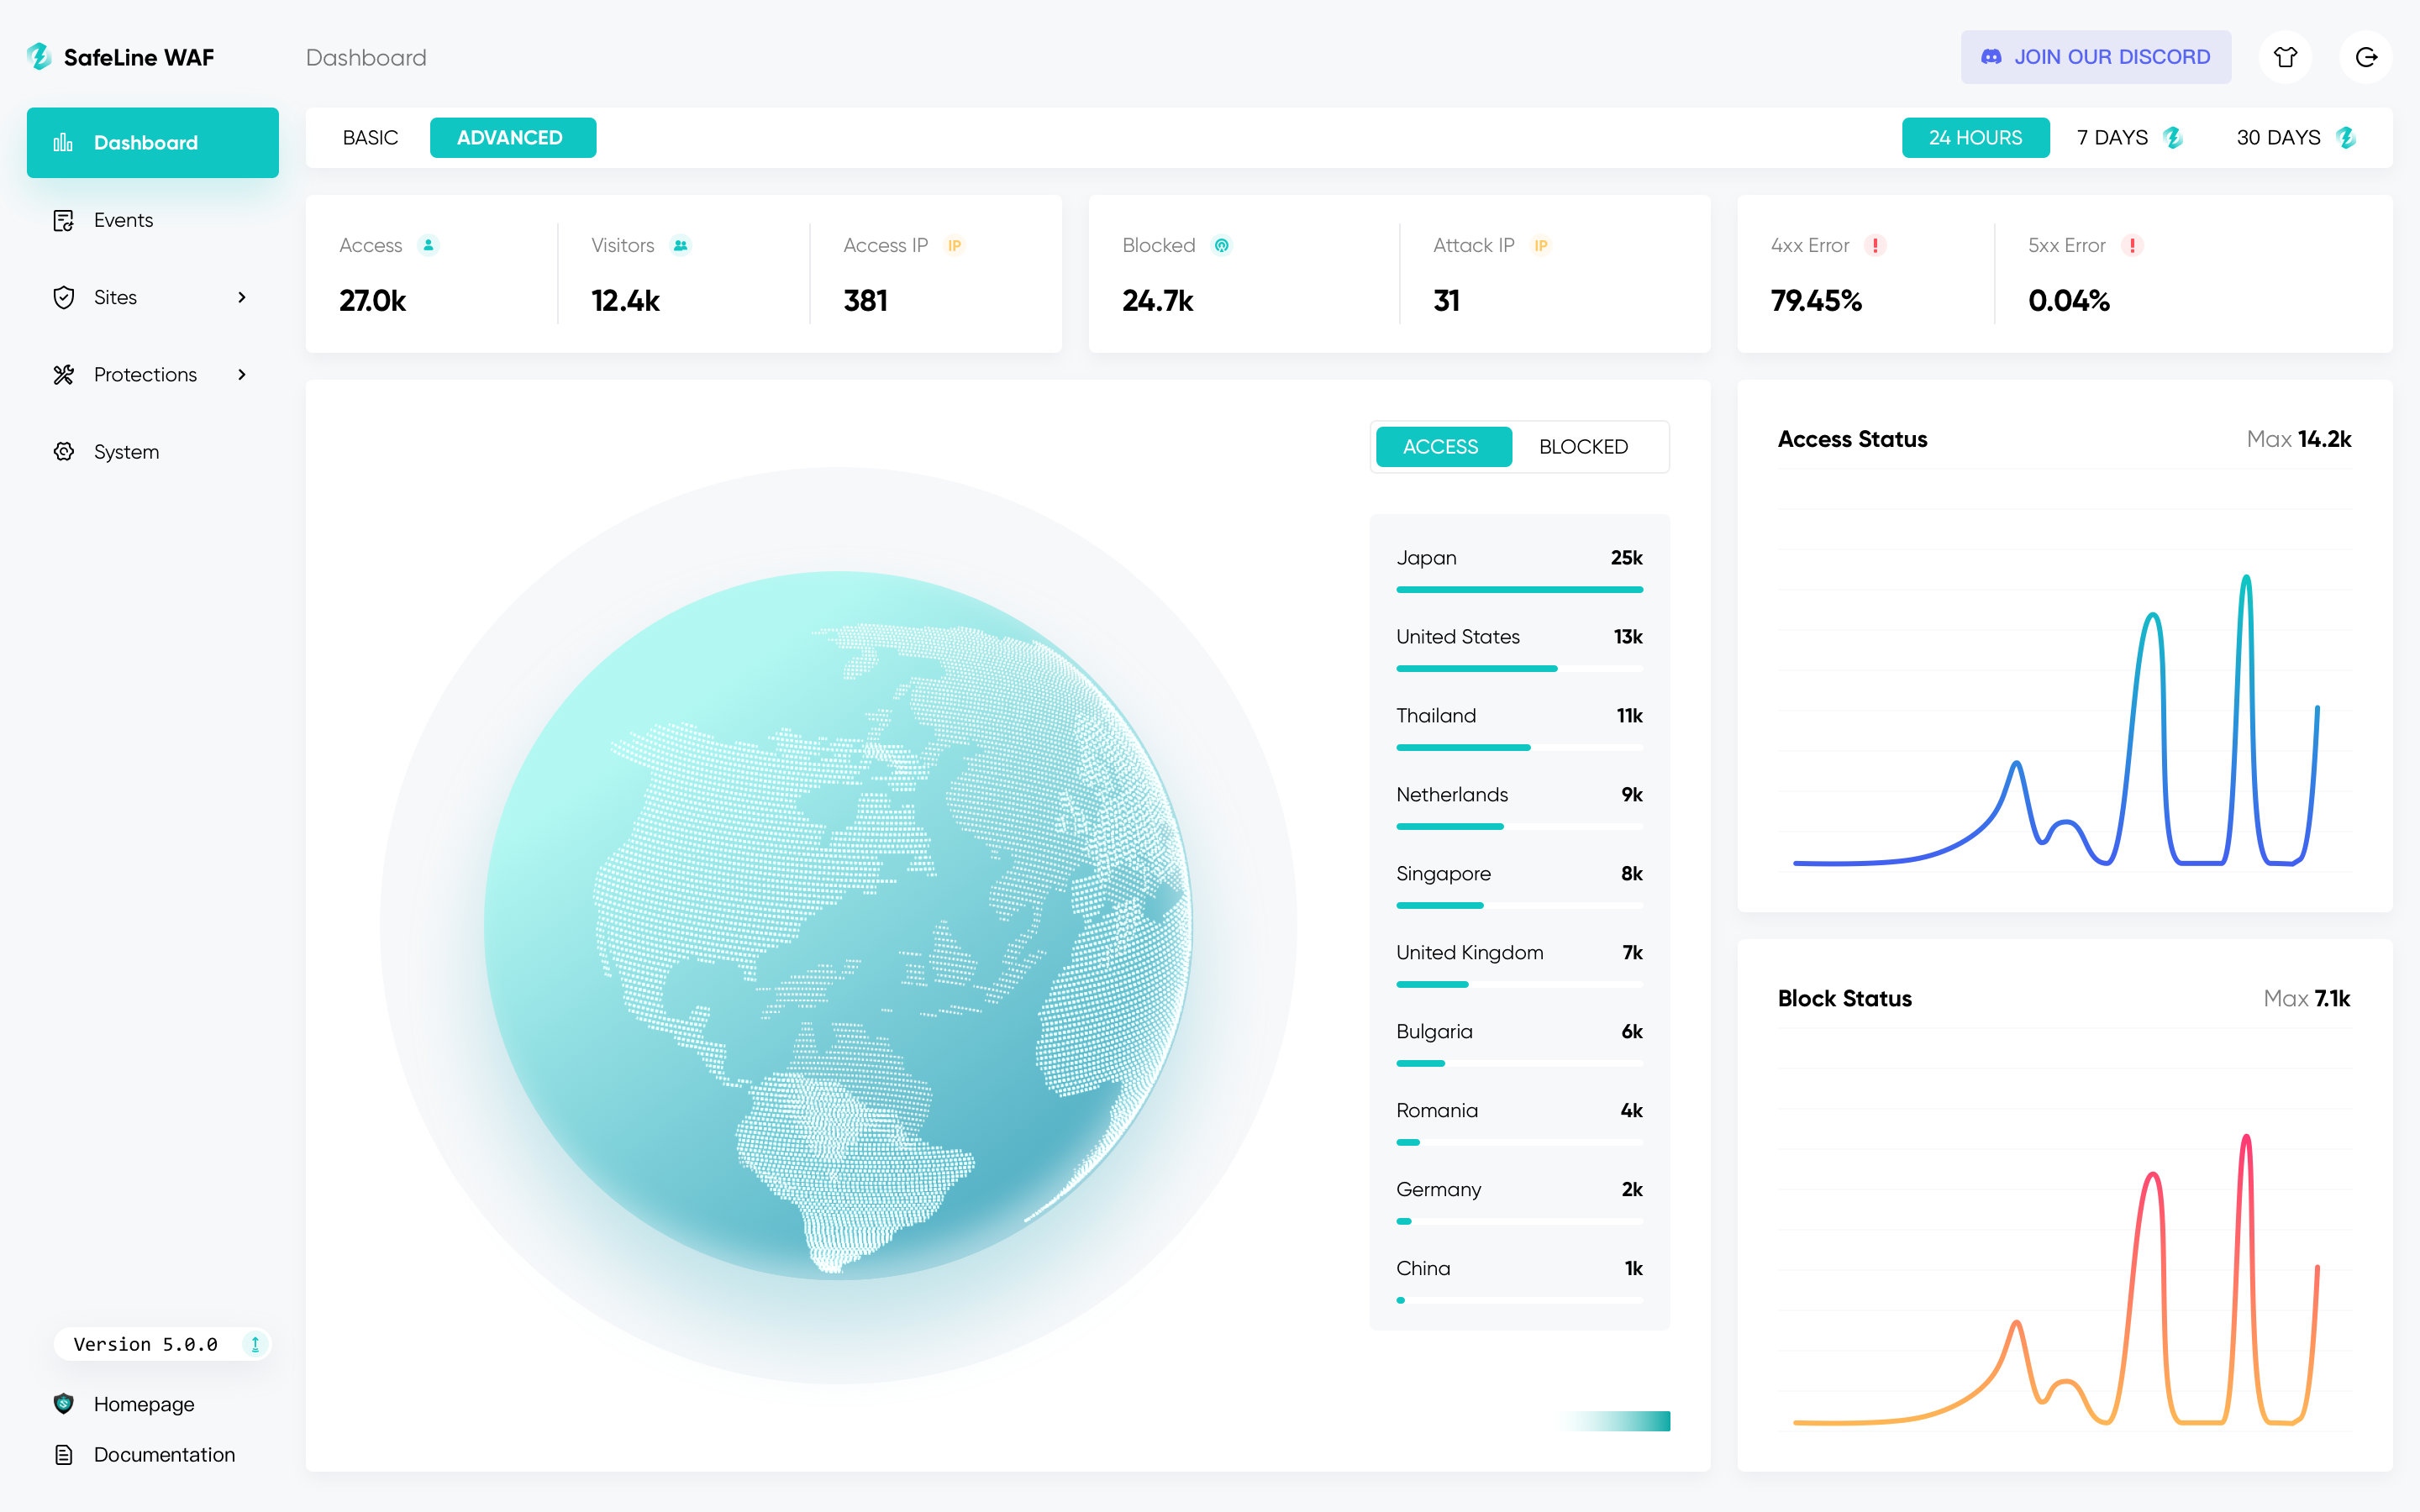
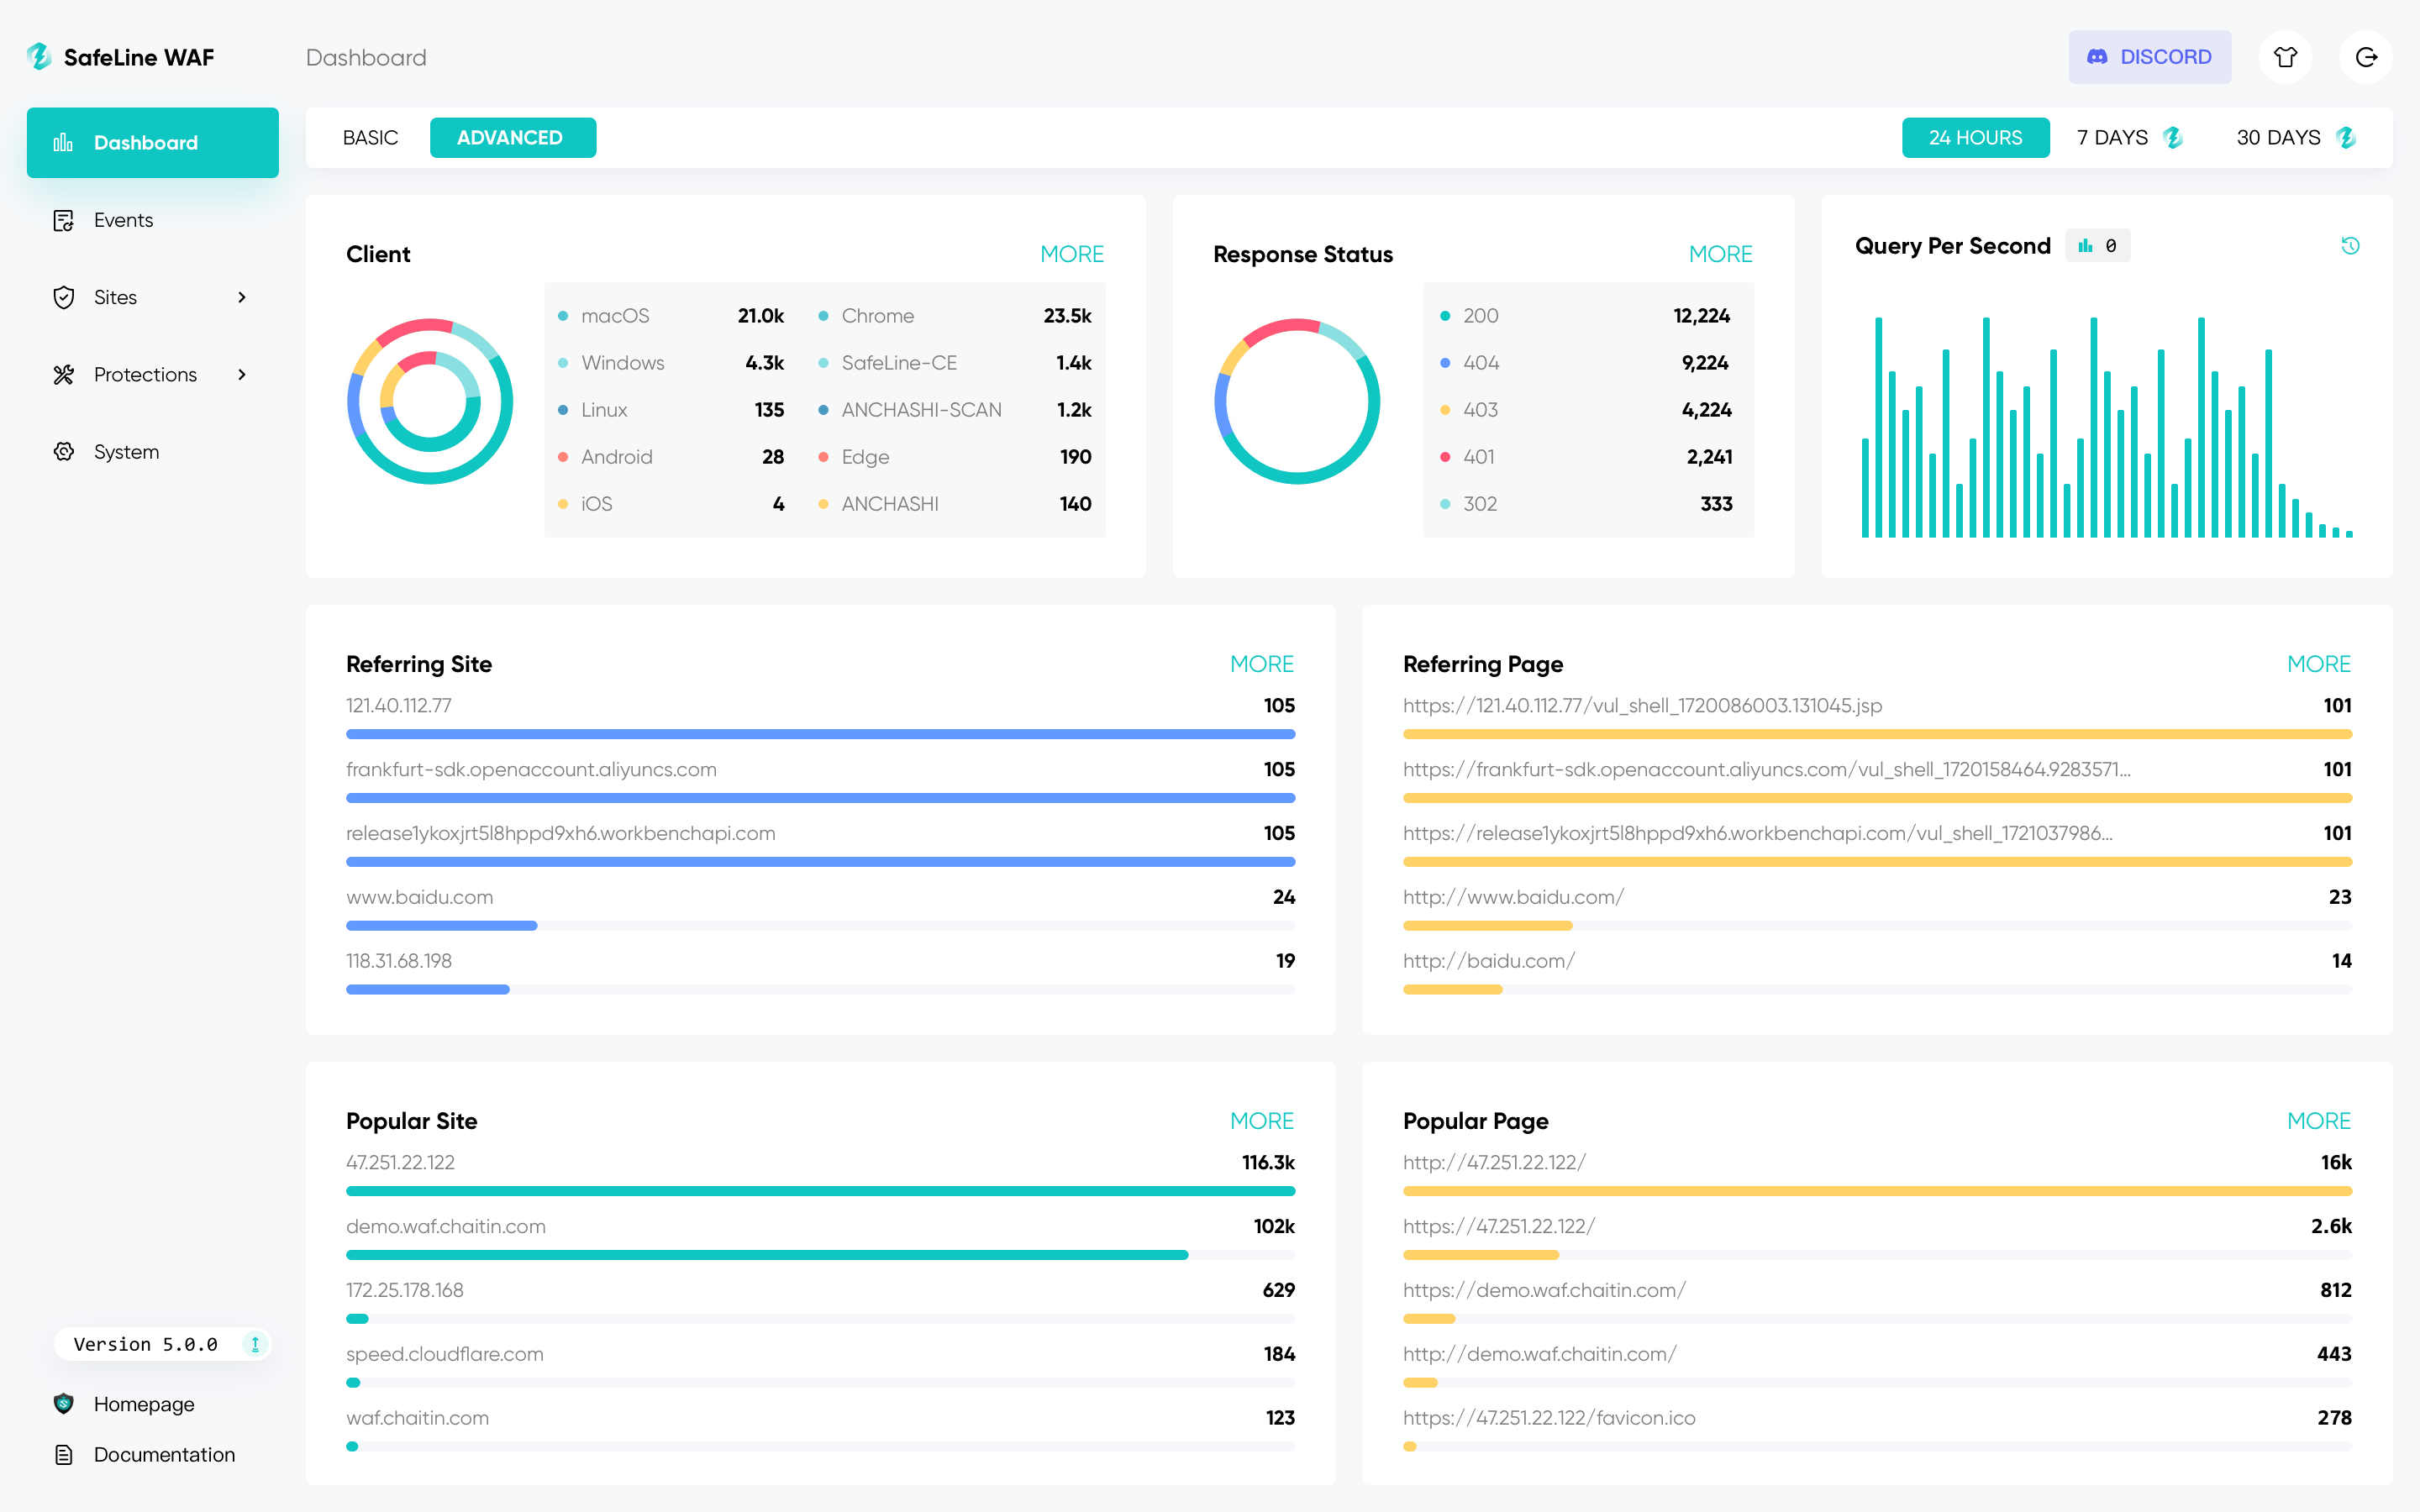
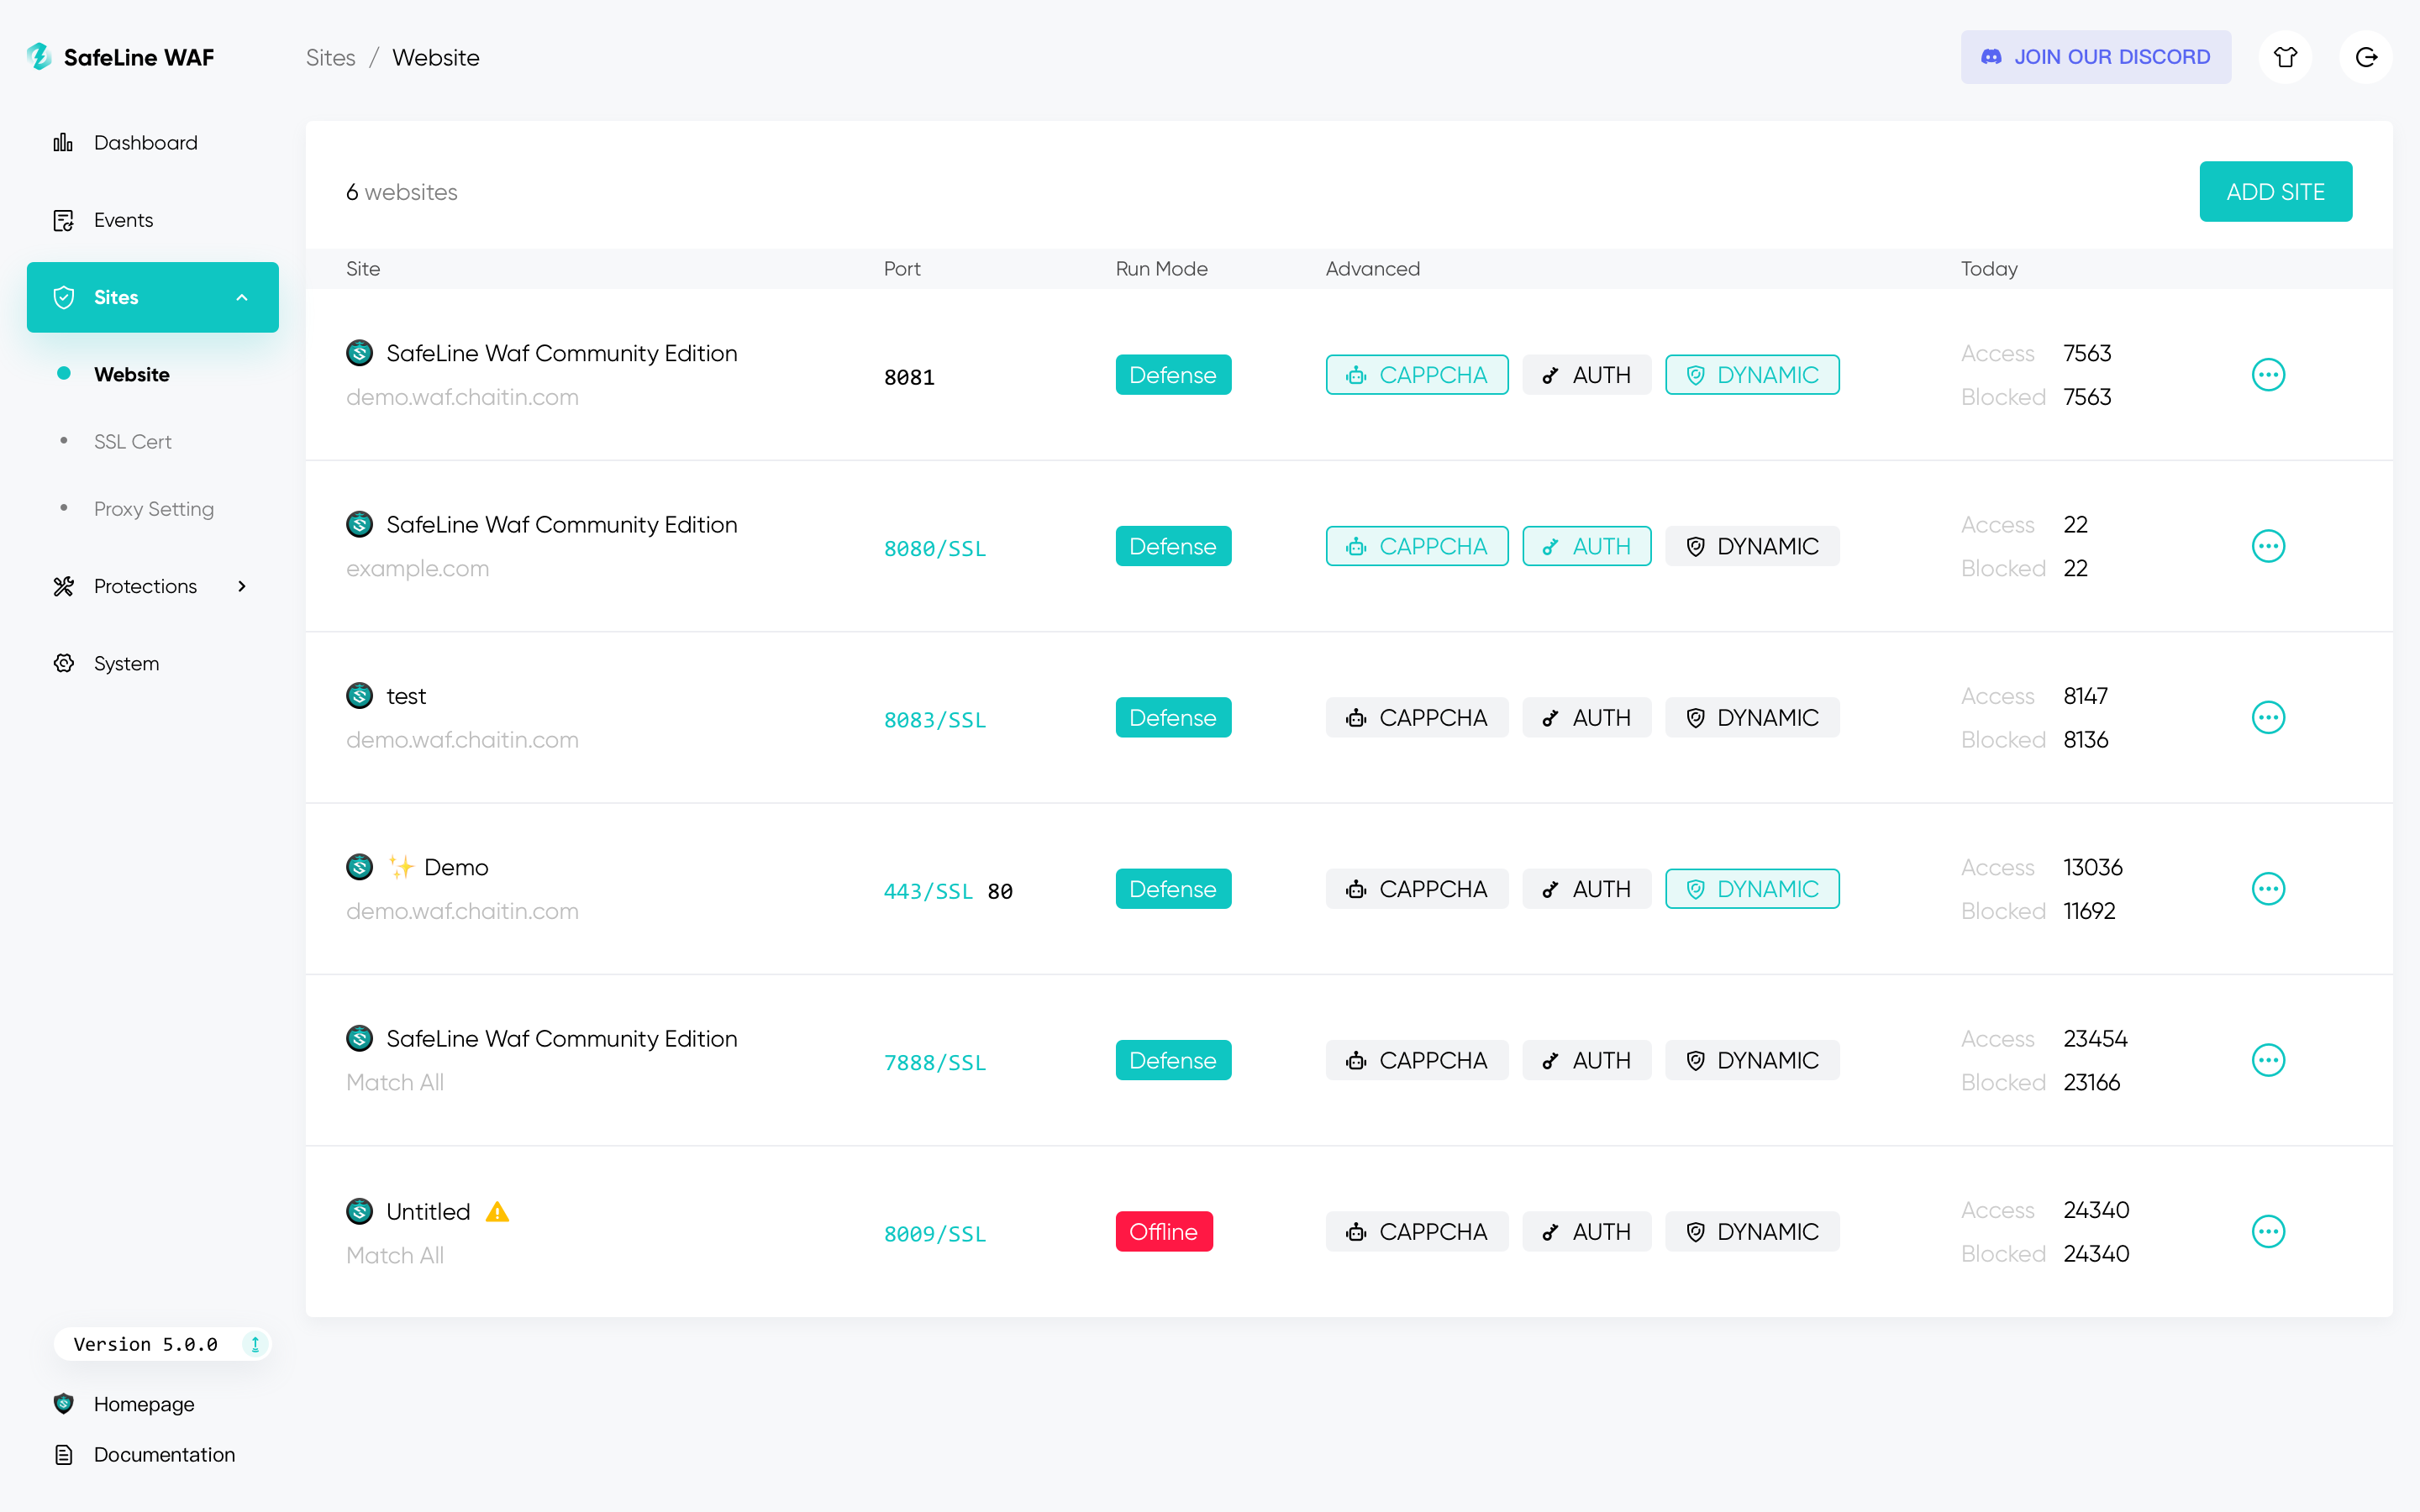
Mainland-China users should install with the Chinese-edition docs: the international edition can fail to connect to SafeLine's cloud services.Where does it run?On your own infrastructure: it is self-hosted software you deploy in front of the web apps you want to protect, managed from its own web console.
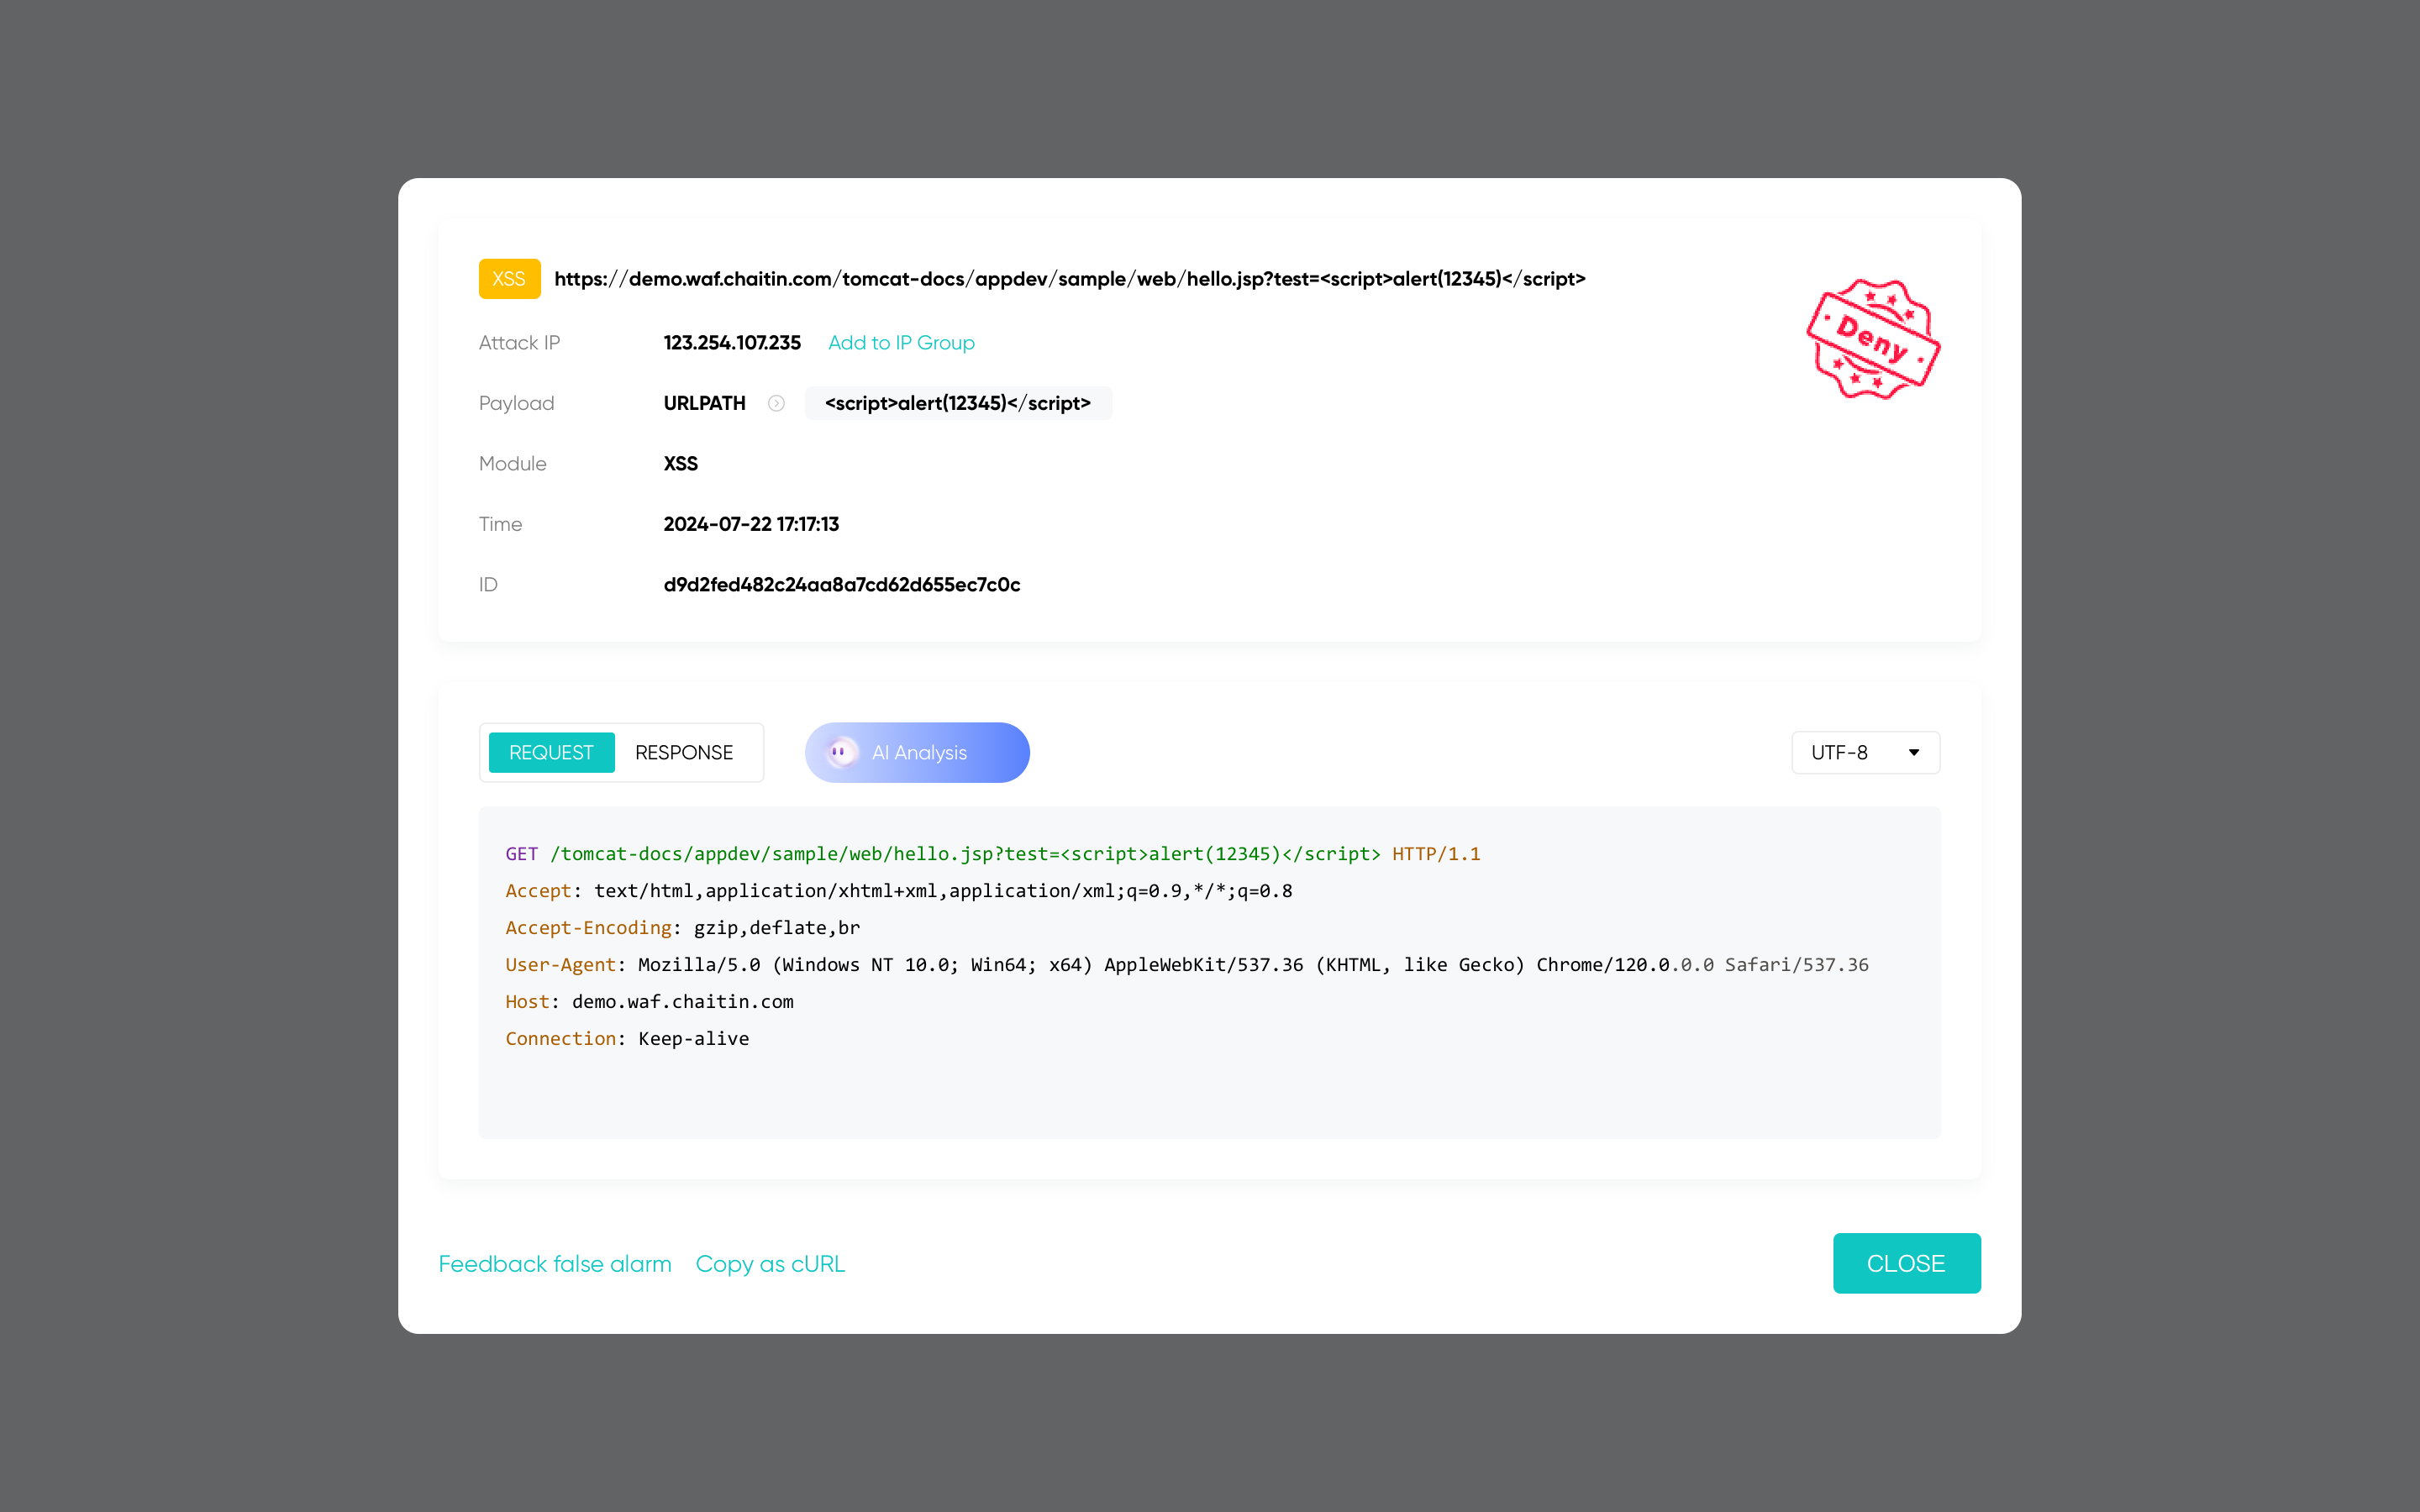
On your own infrastructure: it is self-hosted software you deploy in front of the web apps you want to protect, managed from its own web console.Which attacks does it block?The usual web attack surface: SQL injection, XSS, code and OS command injection, CRLF, LDAP and XPath injection, RCE, XXE, SSRF, path traversal, backdoors, plus brute force, HTTP floods and bot abuse.
The usual web attack surface: SQL injection, XSS, code and OS command injection, CRLF, LDAP and XPath injection, RCE, XXE, SSRF, path traversal, backdoors, plus brute force, HTTP floods and bot abuse.What can it do besides blocking attacks?Rate limiting against DoS, brute force and traffic surges, anti-bot challenges that let humans in while blocking crawlers, an authentication challenge that gates visitors behind a password, and dynamic protection that re-encrypts your pages' HTML and JS on every visit.
Rate limiting against DoS, brute force and traffic surges, anti-bot challenges that let humans in while blocking crawlers, an authentication challenge that gates visitors behind a password, and dynamic protection that re-encrypts your pages' HTML and JS on every visit.How does its detection compare to ModSecurity or Cloudflare?On SafeLine's 33,669-sample benchmark, Balance mode detected 71.65% of attacks with 0.07% false positives (99.45% accuracy) and Strict mode 76.17%, versus 69.74% with 17.58% false positives for ModSecurity Level 1 and 10.70% detection for Cloudflare Free.
On SafeLine's 33,669-sample benchmark, Balance mode detected 71.65% of attacks with 0.07% false positives (99.45% accuracy) and Strict mode 76.17%, versus 69.74% with 17.58% false positives for ModSecurity Level 1 and 10.70% detection for Cloudflare Free.Is it battle-tested?Yes — the README calls it production-ready, with over 400,000 installations worldwide, more than 1,000,000 websites protected, and over 30 billion HTTP requests handled daily.
Yes — the README calls it production-ready, with over 400,000 installations worldwide, more than 1,000,000 websites protected, and over 30 billion HTTP requests handled daily.Which topics is it in?web-application-firewall, sql-injection, waf, bruteforce, xss, cve, appsec, bot-detection, application-security, rate-limiting, captcha, web-security
web-application-firewall, sql-injection, waf, bruteforce, xss, cve, appsec, bot-detection, application-security, rate-limiting, captcha, web-security