Topics / #network-security
Network-security projects on GitHub
Tools for testing, attacking, and defending network infrastructure.
As of , the most-starred Network-security projects on GitHub are web-check (35.1K stars), Anthropic-Cybersecurity-Skills (34.6K stars) and netbird (30K stars). GitHub.Locker tracks 66 Network-security repositories with 757.1K stars combined. The fastest-growing on October 16 was Anthropic-Cybersecurity-Skills, with +71 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
 +71
Anthropic-Cybersecurity-Skills
mukul975/Anthropic-Cybersecurity-Skills · ★ 34.6KAn open-source library of 818 production-grade cybersecurity skills for AI agents, covering 34 security domains and mapped to six frameworks including MITRE ATT&CK and NIST CSF 2.0.
 +49
hexstrike-ai
0x4m4/hexstrike-ai · ★ 12.9KHexStrike AI MCP Agents is an MCP server that lets AI agents like Claude, GPT, or Copilot autonomously run 150+ real cybersecurity tools for automated pentesting, bug bounty hunting, CTF challenges, and vulnerability discovery.
 +45
Fieldwatch
OffGridPete/Fieldwatch · ★ 3.9KFieldwatch is a receive-only Android app that passively listens for nearby Wi-Fi access points and Bluetooth LE advertisements, so you can see what wireless devices are around you.
 +34
dns-blocklists
hagezi/dns-blocklists · ★ 27.5KA set of DNS blocklists that block ads, trackers, telemetry, phishing, malware, scams and other junk domains network-wide. They work for any region and with every common DNS server, ad blocker, and content blocker.
The all-time top
66 projects · by stars
- 35.1K
#1 · lissy93/web-check
web-check
Web-Check is an open-source OSINT dashboard that lets you analyse any website: it pulls IP info, SSL chain, DNS records, cookies, headers, server location, and more into one report so you can understand its tech stack and security posture.
- 34.6K#2 · mukul975/Anthropic-Cybersecurity-Skills
Anthropic-Cybersecurity-Skills
An open-source library of 818 production-grade cybersecurity skills for AI agents, covering 34 security domains and mapped to six frameworks including MITRE ATT&CK and NIST CSF 2.0.
- 30K
 #3 · netbirdio/netbird
netbird
NetBird is an open-source Zero Trust networking platform: it builds a configuration-free peer-to-peer WireGuard overlay network with centralized access control, so you can create secure private networks without open ports, complex firewall rules or VPN gateways.
- 4
dns-blocklists
27.5Khagezi/dns-blocklists · TextA set of DNS blocklists that block ads, trackers, telemetry, phishing, malware, scams and other junk domains network-wide. They work for any region and with every common DNS server, ad blocker, and content blocker.
- 5

masscan
26.1Krobertdavidgraham/masscan · CMasscan is an Internet-scale TCP port scanner that transmits SYN packets asynchronously and can scan the entire IPv4 Internet in under 5 minutes, sending up to 10 million packets per second from a single machine.
- 6
cilium
25.7Kcilium/cilium · GoCilium is open-source networking, security, and observability software built on an eBPF dataplane, used mainly as the networking layer of Kubernetes clusters.
- 7

NemoClaw
22.8KNVIDIA/NemoClaw · TypeScriptAn open source reference stack from NVIDIA for running AI agents like OpenClaw, Hermes and LangChain Deep Agents more safely inside NVIDIA OpenShell sandboxes, with managed inference, network policy and lifecycle operations via its CLI.
- 8
bettercap
20.1Kbettercap/bettercap · GoA portable all-in-one framework written in Go for recon and attacks on WiFi, Bluetooth Low Energy, wireless HID, CAN-bus and IPv4/IPv6 networks, built for security researchers and red teamers.
- 9

90DaysOfCyberSecurity
20.1Kfarhanashrafdev/90DaysOfCyberSecurityA free, 90-day self-paced cybersecurity study plan: daily tasks and curated resources that take you from networking basics to ethical hacking, ending with job-hunting help.
- 10

Micro8
18KMicropoor/Micro8A free, open-source series of penetration-testing lessons written by veteran Chinese pentester Micropoor and published as a GitBook. It covers code audit, web, intranet and domain penetration, tunneling, and log-based tracing.
- 11

Awesome-Hacking-Resources
17.5Kvitalysim/Awesome-Hacking-ResourcesA curated collection of hacking, penetration testing and AI red-teaming resources — courses, YouTube channels, CTF platforms and guides, picked to make you better at offensive security.
- 12

awesome-hacking
17.3Kcarpedm20/awesome-hackingA curated list of hacking tutorials, tools and resources covering system exploitation, reverse engineering, web security, network security, forensics, cryptography and wargames.
- 13

shadowsocks-c
16.2Kshadowsocks/shadowsocks-c · C++shadowsocks-c is a lightweight, secured SOCKS5 proxy written in pure C, built on libuv with asynchronous DNS, designed to run on embedded devices and low-end boxes as well as desktops and servers.
- 14
evilginx2
15.7Kkgretzky/evilginx2 · GoEvilginx is a man-in-the-middle attack framework used for phishing login credentials along with session cookies, which lets an attacker bypass 2-factor authentication.
- 15
ecapture
15.5Kgojue/ecapture · CAn open-source command-line security tool that uses eBPF to capture SSL/TLS traffic in plaintext — no CA certificate installation or MITM proxy needed. It can also audit shell commands and database queries on the host.
- 16

amass
15.4Kowasp-amass/amass · GoAmass is an OWASP project that maps attack surfaces and discovers external assets (like subdomains, IPs, and infrastructure) using open source intelligence gathering and active reconnaissance.
- 17

brook
15.2Ktxthinking/brook · GoBrook is a cross-platform programmable network tool that works as both a server and a client, giving you SOCKS5 proxying, TLS encryption, traffic decryption/MITM inspection, and packet capture in one toolkit.
- 18
esp8266_deauther
15KSpacehuhnTech/esp8266_deauther · CESP8266 Deauther is open-source firmware for the ESP8266 chip that lets you scan nearby WiFi networks, send deauthentication packets to disconnect devices, and spin up dozens of fake WiFi networks to confuse scanners - an affordable platform for testing and learning about WiFi security.
- 19

awesome-security
15Ksbilly/awesome-securityA curated, categorized collection of well-known security resources — software, libraries, documents, books and other cool stuff — maintained by the community in the spirit of awesome-php and awesome-python.
- 20
wifiphisher
14.9Kwifiphisher/wifiphisher · PythonWifiphisher is a rogue access point framework for conducting Wi-Fi phishing and man-in-the-middle attacks against wireless clients, used in red team and penetration testing engagements.
- 21
fscan
14.7Kshadow1ng/fscan · Gofscan is an open-source intranet scanner written in Go: one command runs an all-round internal-network audit — host discovery, port scanning, service identification, weak-password brute force and vulnerability detection.
- 22
opensnitch
14.2Kevilsocket/opensnitch · PythonOpenSnitch is an interactive application firewall for GNU/Linux, inspired by macOS's 'Little Snitch', that lets you see and approve or block each app's outgoing connections in real time.
- 23
portmaster
13.9Ksafing/portmaster · GoPortmaster is a free, open-source application firewall for Windows and Linux that intercepts all network traffic on your machine, letting you monitor and block connections per app, filter DNS, and block trackers and malware with good defaults out of the box.
- 24
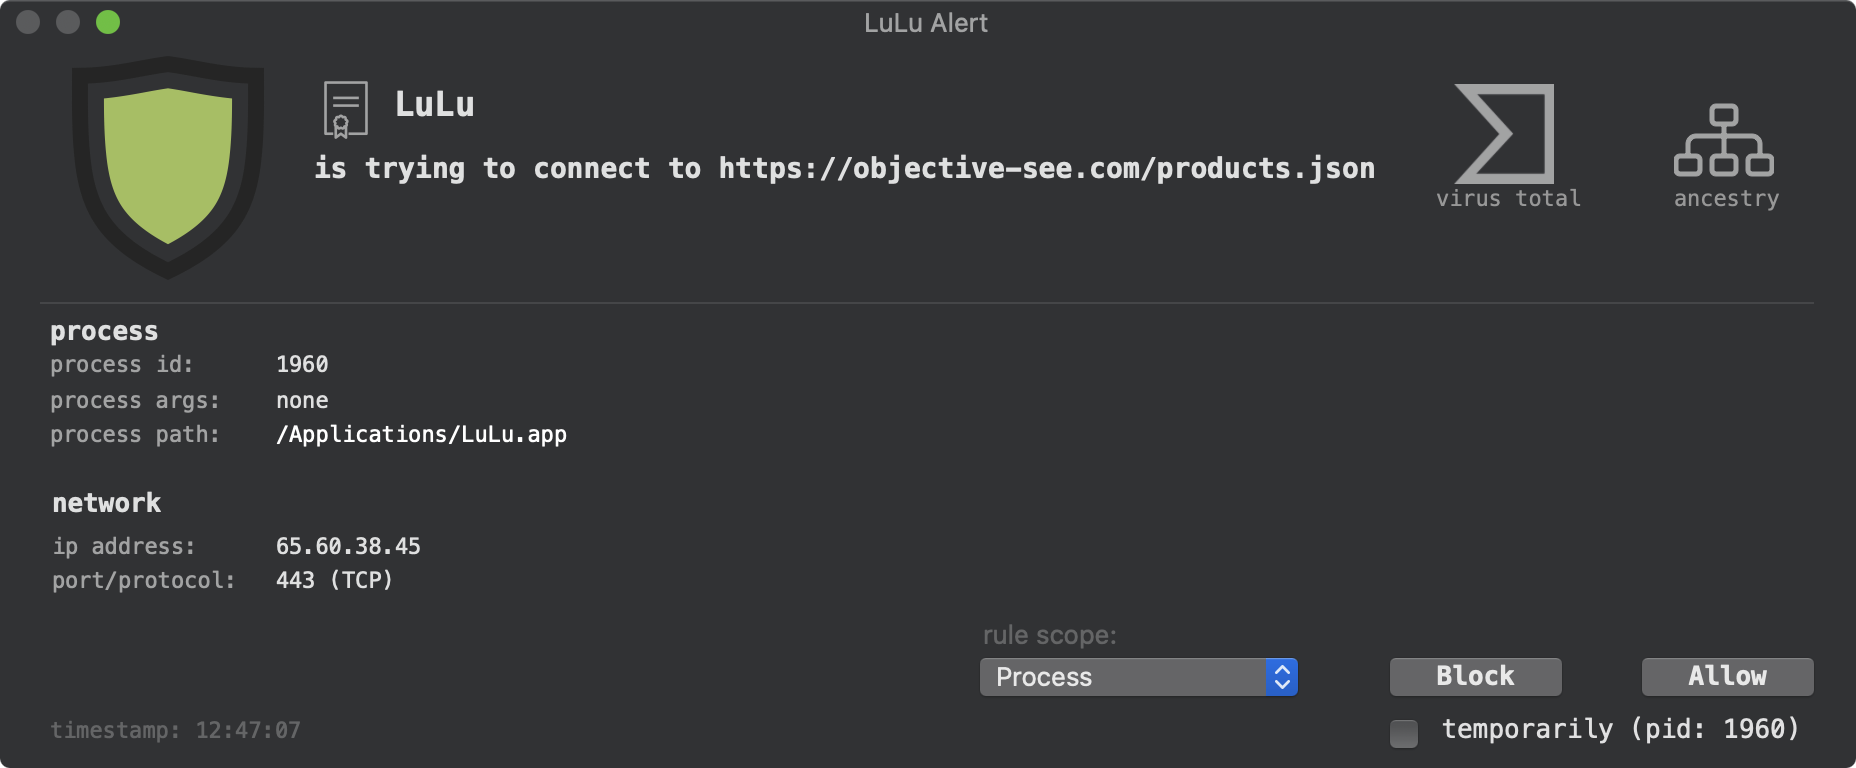
LuLu
13.3Kobjective-see/LuLu · Objective-CLuLu is a free, open-source firewall for macOS: it watches the network connections apps on your Mac try to make and lets you allow or block them.
- 25

routersploit
13.3Kthreat9/routersploit · PythonRouterSploit is an open-source exploitation framework built specifically for testing the security of embedded devices like routers.
- 26

PowerSploit
13.1KPowerShellMafia/PowerSploit · PowerShellPowerSploit is a collection of PowerShell modules that penetration testers use during all phases of an assessment, covering code execution, persistence, privilege escalation, credential theft, exfiltration and reconnaissance on Windows systems.
- 27

user.js
12.9Karkenfox/user.js · JavaScriptarkenfox user.js is a community-maintained Firefox configuration template that hardens privacy and security settings, aiming to reduce tracking and fingerprinting as much as possible while trying to keep the browser usable.
- 28
hexstrike-ai
12.9K0x4m4/hexstrike-ai · PythonHexStrike AI MCP Agents is an MCP server that lets AI agents like Claude, GPT, or Copilot autonomously run 150+ real cybersecurity tools for automated pentesting, bug bounty hunting, CTF challenges, and vulnerability discovery.
- 29

wifi-cracking
12.7Kbrannondorsey/wifi-crackingA step-by-step tutorial for cracking WPA/WPA2 Wi-Fi passwords: capture a handshake with Airodump-ng, then crack it offline with Aircrack-ng or Hashcat.
- 30

scapy
12.6Ksecdev/scapy · PythonScapy is a Python-based interactive packet manipulation program and library that lets you forge, decode, send, capture, and analyze network packets.
- 31

thc-hydra
12.4Kvanhauser-thc/thc-hydra · CHydra is a parallelized network login cracker by van Hauser / THC: a proof-of-concept tool showing researchers and security consultants how easily a remote system can be broken into through weak passwords. It supports over 50 protocols.
- 32

fsociety
12.3KManisso/fsociety · Pythonfsociety is a penetration testing toolkit that bundles dozens of existing hacking tools (Nmap, sqlmap, WPScan, Reaver, etc.) behind one menu-driven script, inspired by the tools used in the 'Mr. Robot' TV series.
- 33

kubeshark
12.1Kkubeshark/kubeshark · GoKubeshark is an eBPF-powered network observability tool for Kubernetes that captures and indexes L4/L7 traffic with full Kubernetes context, decrypts TLS without managing keys, and lets both humans and AI agents query the data.
- 34
xray
11.8Kchaitin/xray · Vuexray is a security assessment tool built by Chaitin for scanning common web vulnerabilities and running custom PoCs against targets.
- 35
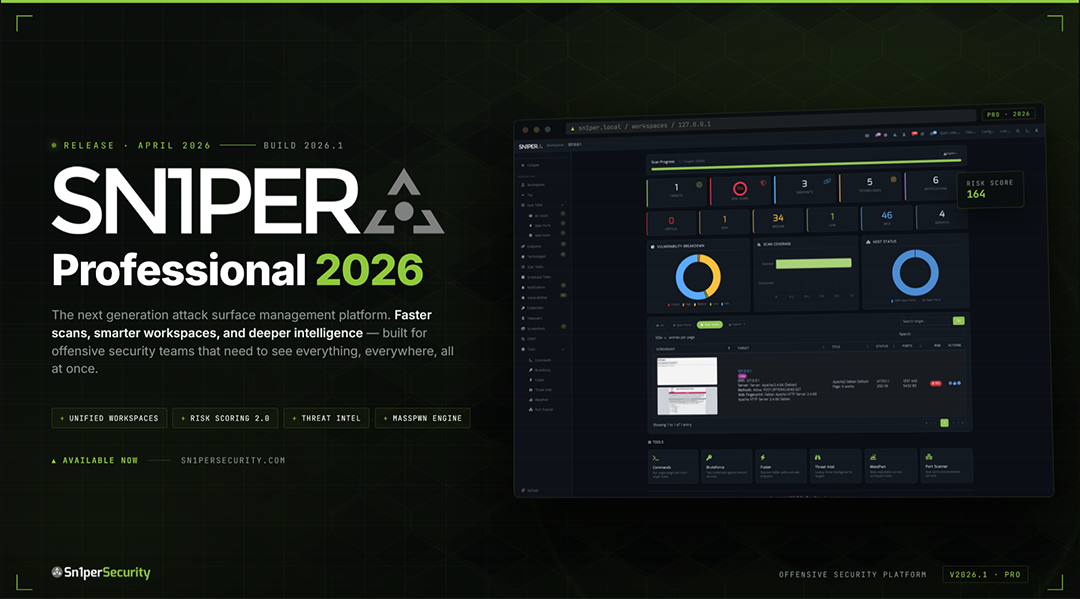
Sn1per
11.5K1N3/Sn1per · ShellSn1per is an offensive-security platform that bundles reconnaissance, vulnerability scanning, exploitation and reporting into one workspace, orchestrating 600+ exploits and 90+ third-party tools for pentesters and attack-surface-management teams.
- 36

404StarLink
11.4Kknownsec/404StarLink404StarLink is a curated list of security-focused open-source projects maintained by Knownsec 404 Lab, created to showcase, support, and track high-quality, actively-maintained security tools.
- 37
smartdns
11.3Kpymumu/smartdns · CSmartDNS is a local DNS server that forwards each query to multiple upstream DNS servers, measures which resolved IP responds fastest, and returns that IP to the client for a faster browsing experience. It also supports DoT, DoH, DoQ and DoH3 for privacy and can act as an ad filter by mapping specific domains to chosen IPs.
- 38

netshoot
11Knicolaka/netshoot · Shellnetshoot is a Docker and Kubernetes network troubleshooting container, a 'swiss-army' image packed with networking, DNS, performance, and security tools for debugging container and host network issues.
- 39

nikto
10.8Ksullo/nikto · PerlNikto is an open-source web server scanner that checks servers for dangerous files, outdated software versions, and other common vulnerabilities.
- 40

IPQuality
10.7Kxykt/IPQuality · ShellIPQuality is a shell script that checks the quality of a server or VPS IP address: geolocation, risk score, blacklist status, streaming unlock status, and mail provider connectivity, all in one report.
- 41

awesome-threat-intelligence
10.7Khslatman/awesome-threat-intelligenceA curated catalog of threat intelligence resources — feeds, tools, frameworks, standards and research for tracking online threats. It is a pointer list on GitHub, not software you install.
- 42

awesome-honeypots
10.6Kparalax/awesome-honeypots · PythonA curated, categorized list of honeypot software and related tools used by security researchers to deceive attackers, log their behavior, and study exploitation attempts.
- 43
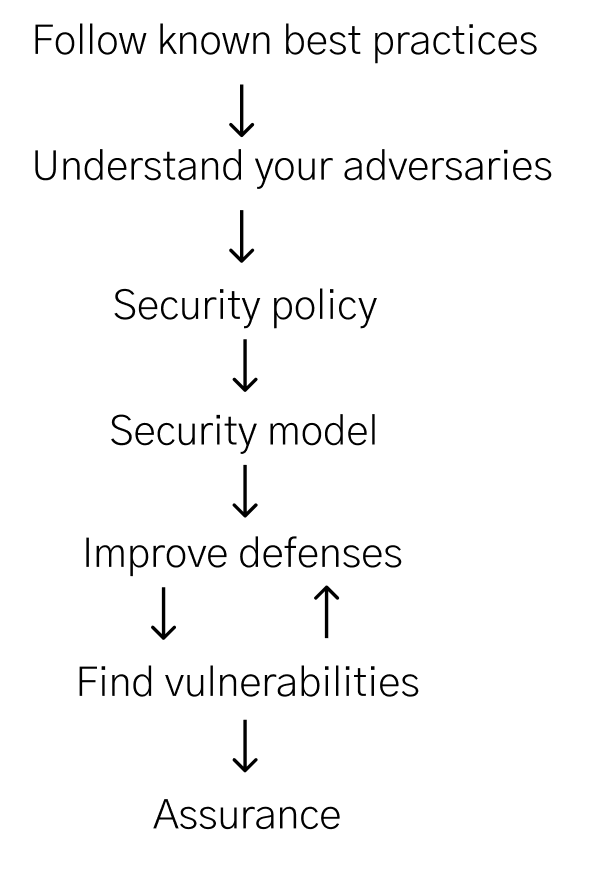
how-to-secure-anything
10.2Kveeral-patel/how-to-secure-anythingA curated README that documents a systematic process for security engineering: how to secure any kind of system, whether it is a medieval castle, an art museum, or a computer network, by thinking about adversaries, policies, models, and defenses.
- 44

Claude-Red
7.6KSnailSploit/Claude-Red · Pythonclaude-red is a curated library of offensive security skills for the Claude Skills system: structured SKILL.md files that prime Claude with expert-level methodology for one attack surface each, from SQLi to shellcode.
- 45

MasterDnsVPN
7.1Kmasterking32/MasterDnsVPN · GoMasterDnsVPN is a DNS tunneling VPN that smuggles TCP traffic inside DNS queries and responses to get online when regular connections are blocked, aiming for the same goal as DNSTT or SlipStream but using its own lower-overhead protocol.
- 46
ProxyBridge
6.8KInterceptSuite/ProxyBridge · CProxyBridge is a cross-platform proxy client that transparently redirects TCP and UDP traffic from specific Windows/macOS/Linux applications through SOCKS5 or HTTP proxies, acting as an open-source alternative to Proxifier.
- 47
Agentic-Bug-Hunter
5.4Kawarexone/Agentic-Bug-Hunter · PythonAgentic Bug Hunter is an AI-powered bug bounty toolkit that runs recon, tests for vulnerabilities, validates findings against a strict gate, and writes submission-ready reports for HackerOne, Bugcrowd, Intigriti, or Immunefi, right from your terminal.
- 48
antigravity-proxy
4.5Kyuaotian/antigravity-proxy · C++Antigravity-Proxy is a Windows DLL injector that forces the Antigravity code editor (and its CLI) to route its network traffic through your SOCKS5/HTTP proxy, without needing Clash's TUN mode.
- 49
airgorah
4.2Kmartin-olivier/airgorah · RustAirgorah is a WiFi security auditing tool written in Rust that captures nearby WiFi traffic, discovers clients connected to access points, performs deauthentication attacks, captures handshakes and PMKIDs, and cracks access point passwords.
- 50
METATRON
4.2Ksooryathejas/METATRON · PythonMetatron is a CLI-based AI penetration testing assistant that runs real recon tools against a target and lets a locally-hosted LLM analyze the results, suggest exploits, and recommend fixes, with no cloud or API keys involved.
- 51
donutbrowser
4.1Kdonutbrowser/donutbrowser · RustDonut Browser is an open-source anti-detect browser built on a privacy-focused Chromium fork. It lets you run unlimited isolated browser profiles, each with its own fingerprint, cookies, extensions, and proxy, to stay hidden from fingerprinting and anti-bot services.
- 52
Fieldwatch
3.9KOffGridPete/Fieldwatch · KotlinFieldwatch is a receive-only Android app that passively listens for nearby Wi-Fi access points and Bluetooth LE advertisements, so you can see what wireless devices are around you.
- 53
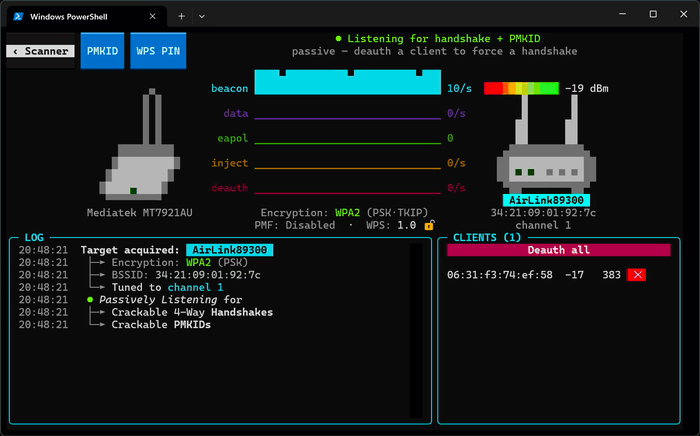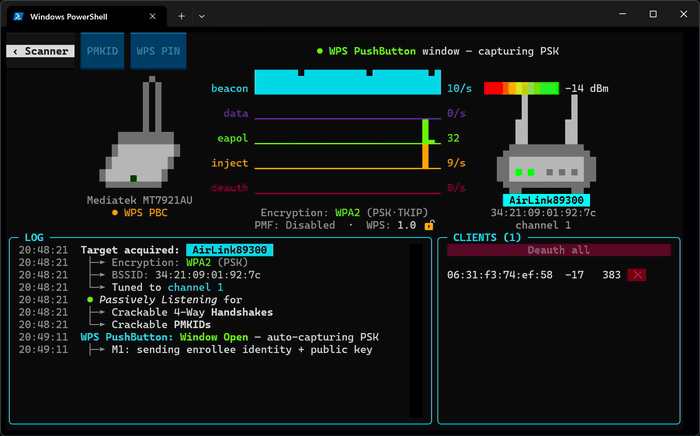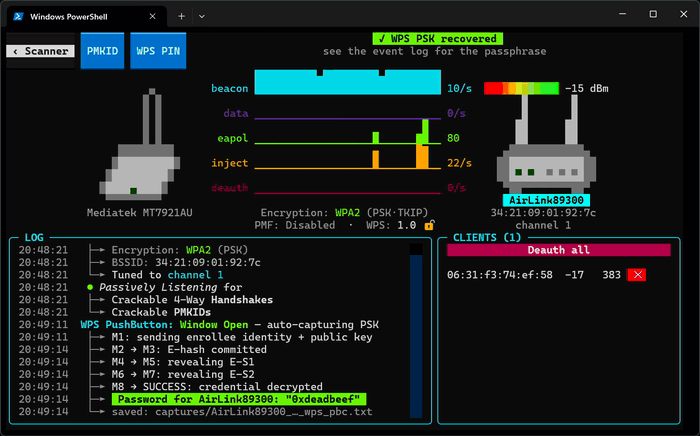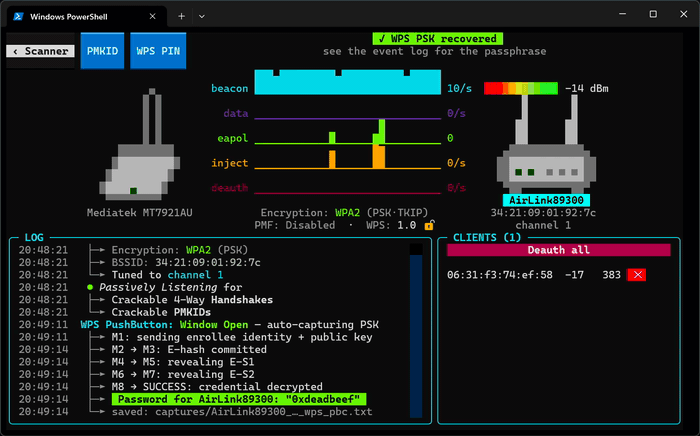
wifit3
2.4Kderv82/wifit3 · Pythonwifit3 is a standalone Wi-Fi security auditing tool that scans networks, captures WPA/WPA2 handshakes, and exploits WPS/WEP weaknesses using a supported USB Wi-Fi adapter, without relying on aircrack-ng or OS kernel drivers.
- 54
anti-mage
2.1KN4darae/anti-mage · GoAnti-Mage is a free, open-source Go project that detects anti-detect browsers and spoofed browser profiles by checking whether a browser's own reported surfaces (fonts, timezone, WebGL, screen geometry, audio, etc.) are internally consistent, instead of matching known-tool signatures.
- 55

artex-global
1.6Kjiwoochris/artex-global · GoARTEX-KO is a Korean localization of the ARTEX (Autumn-27/ARTEX) framework: a system where multiple LLM-driven agents autonomously run a penetration test end-to-end, from reconnaissance to exploitation, with a Go backend and an embedded Next.js frontend.
- 56
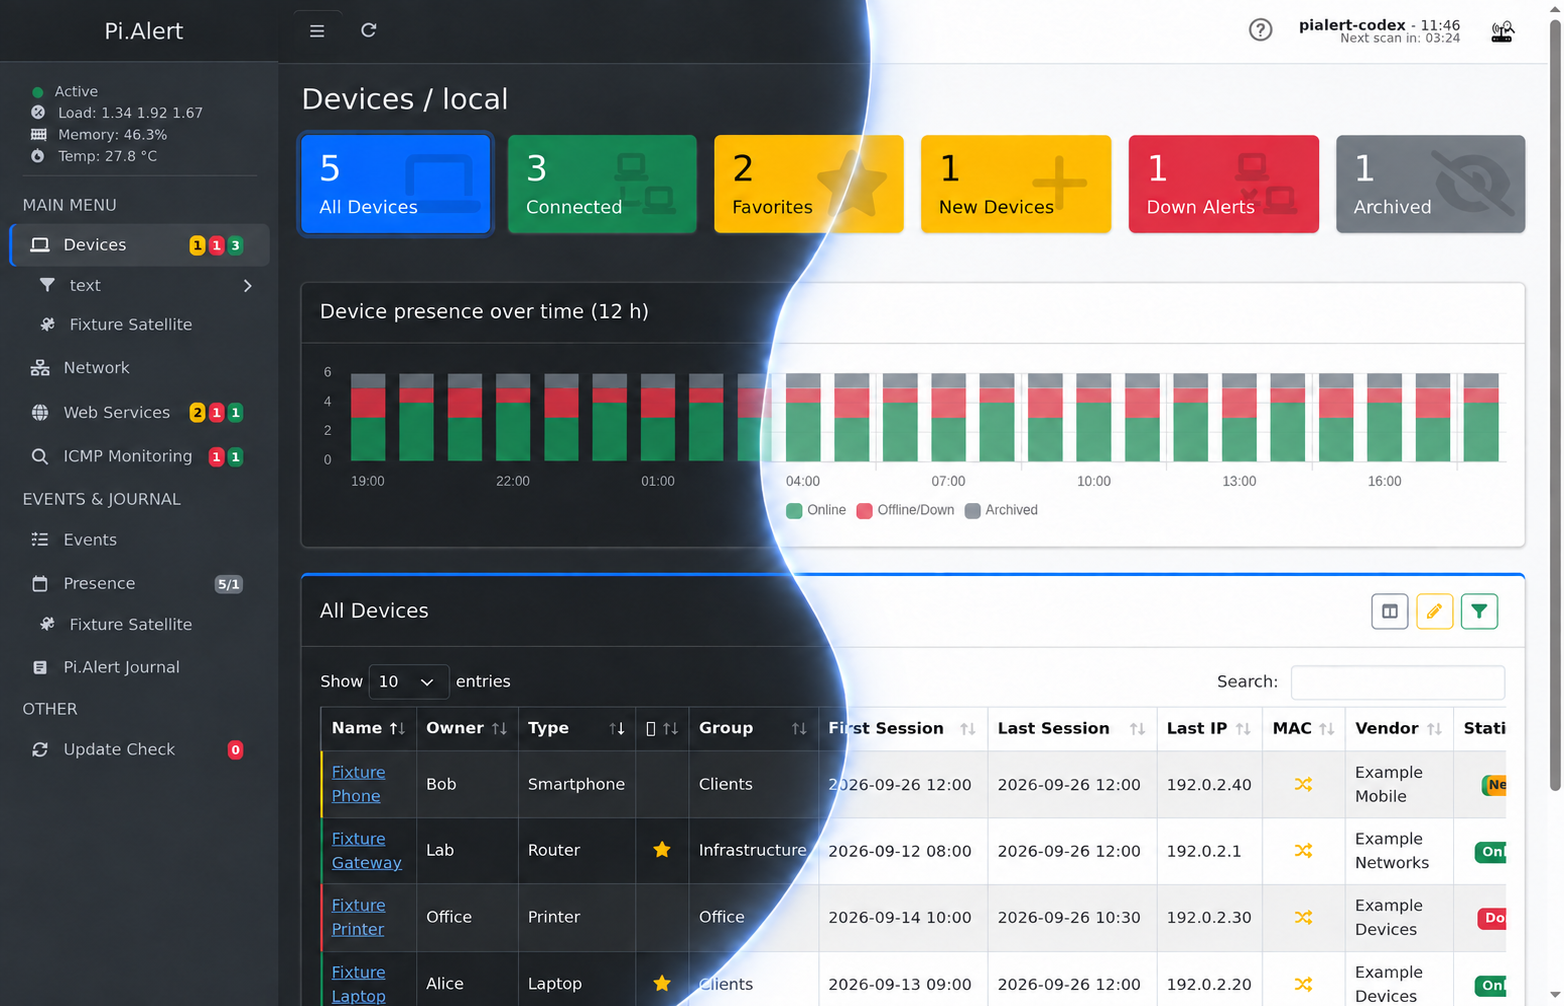
Pi.Alert
1.2Kleiweibau/Pi.Alert · PHPPi.Alert watches your Wi-Fi or LAN and alerts you when an unknown device connects, a known device disconnects, or a monitored web service goes down. It also checks HTTP status, response time, and SSL certificates for web services you configure.
- 57
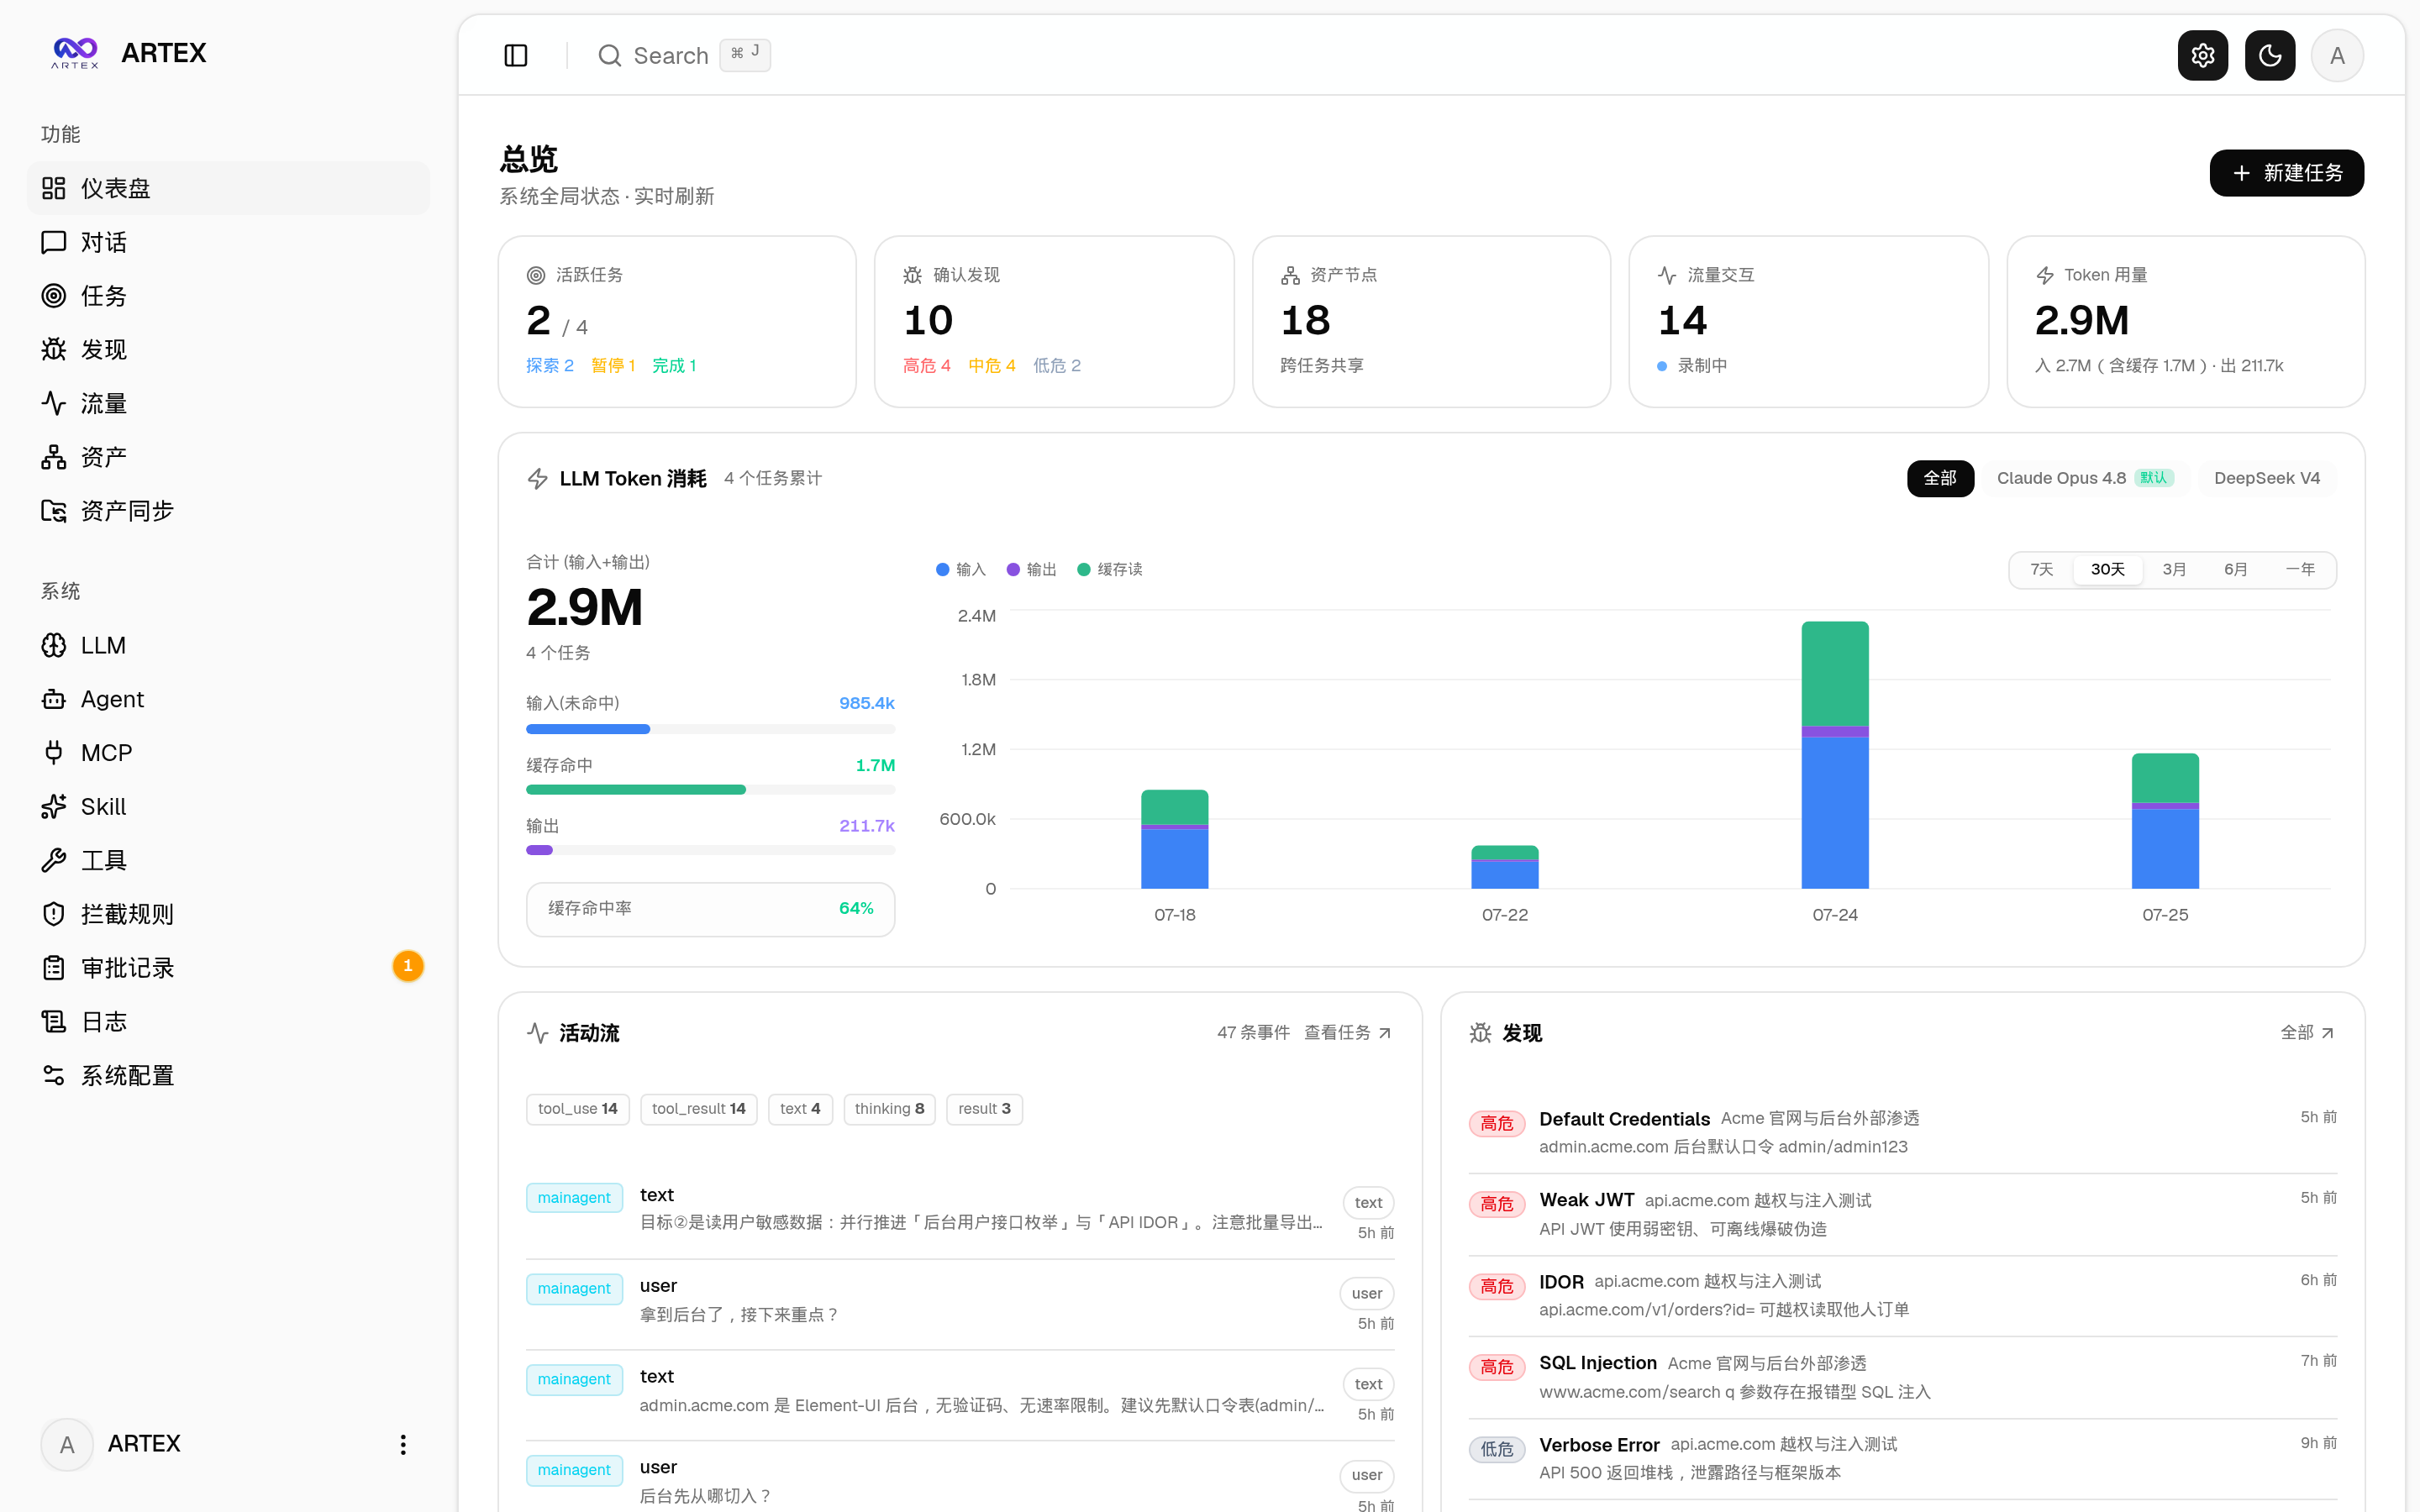
ARTEX
1.2Ktrhhubsd/ARTEX · GoARTEX is an AI-driven autonomous penetration testing system (Go backend + Next.js frontend) where LLM-powered planner and worker agents explore targets, map assets, and find vulnerabilities on their own.
- 58

blocklist-abuseipdb
600borestad/blocklist-abuseipdb · ShellA continuously updated set of IP blocklists aggregating AbuseIPDB's worst IPv4 and IPv6 offenders (~99% confidence), plus other free public threat sources, meant to be loaded straight into a firewall to block malicious traffic.
- 59

OhMyKeymint
438ITxiao6666/OhMyKeymint · RustOh My Keymint (OMK) is a custom Android Keystore implementation that fully mirrors the AOSP AIDL interface, designed to spoof key attestation and make app behavior harder for detectors to distinguish from a genuine AOSP device.
- 60
box
417strands-agents/box · RustBox is an open-source sandbox for running AI agents that restricts what they can execute, read, write, and reach on the network, combining OS-level isolation with a policy engine (Dogwood) and credential injection so secrets never reach the agent.
- 61

mlmvpn_android
411mlmvpn/mlmvpn_android · KotlinMLM VPN is an Android app that bundles many independent connectivity engines — Xray-core (VLESS/VMess/Trojan), AmneziaWG, WARP, Psiphon, Tor, Geph, OpenVPN and a custom MASQUE-based engine — behind one UI, plus an adaptive per-app router, a Cloudflare Worker control panel, and a game-latency booster, aimed at bypassing network restrictions.
- 62

vps-security-enhancement-scripts
2380x10debug/vps-security-enhancement-scripts · ShellIt is a security-first interactive bash script for hardening a fresh VPS or cloud server, bundled with a scenario-driven handbook and printable cheatsheets that explain why each fix matters, not just how to run it.
- 63
cynative
223cynative/cynative · GoCynative is an open-source AI agent framework that gives LLMs live, read-only access to your AWS, Azure, GCP, Kubernetes, GitHub and GitLab infrastructure so you can ask security questions and run cloud security posture and detection checks.
- 64

CVE-2026-62911
187hypnguyen1209/CVE-2026-62911 · PythonA proof-of-concept exploit for CVE-2026-62911, a pre-auth RCE in Microsoft Exchange Server that relays an NTLM machine account hash to the MRSProxy service to drop and run an ASPX webshell, giving full SYSTEM access without any credentials.
- 65
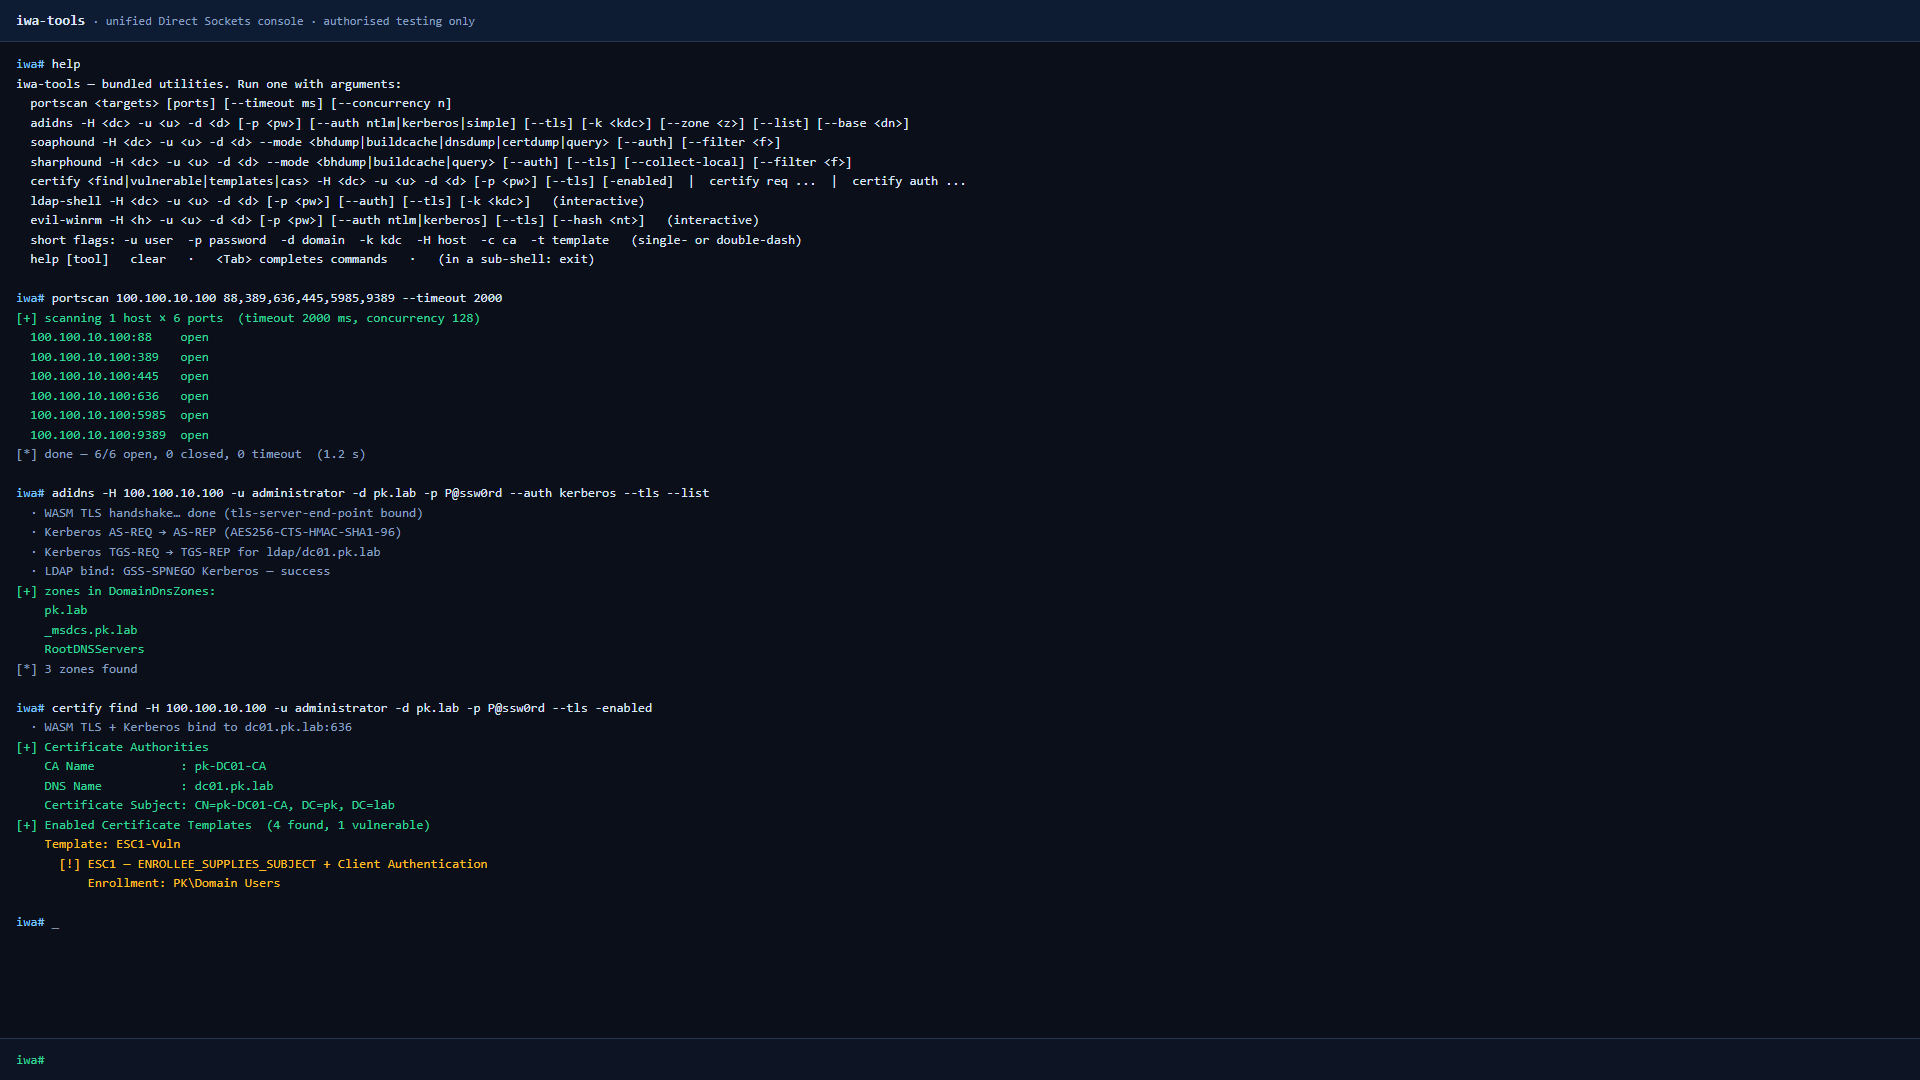
iwa-tools
146CICADA8-Research/iwa-tools · JavaScriptiwa-tools is an offensive security toolkit that runs inside Chrome as an installed Isolated Web App, letting you speak SMB, LDAP, DCE-RPC, WinRM, Kerberos, MSSQL and ADWS directly from a browser tab for Active Directory pentesting.
- 66
xdp-dns-evadeproxy
131Oihalitz/xdp-dns-evadeproxy · RustA DNS proxy in Rust that sidesteps blanket ISP IP blocks: when an operator cuts off an anycast address shared by hundreds of Cloudflare sites, it rewrites that IP in the DNS response to an unblocked neighbor of the same prefix.
Related topics
Often tagged together
- security976
- cybersecurity245
- linux4,184
- security-tools282
- open-source5,666
- networking565
- penetration-testing126
- windows3,403
- cli2,227
- macos3,544
- hacking135
- pentesting113
- cross-platform2,623
- docker1,660
- privacy886
- self-hosted1,929
- mit3,312
- terminal1,101
- red-team79
- go681
- offensive-security77
- hacking-tool75
- python2,383
- proxy383