Topics / #devsecops
Devsecops projects on GitHub
Integrating security practices into devops pipelines
As of , the most-starred Devsecops projects on GitHub are shannon (49.1K stars), trivy (38.5K stars) and Anthropic-Cybersecurity-Skills (34.6K stars). GitHub.Locker tracks 38 Devsecops repositories with 579.7K stars combined. The fastest-growing on October 17 was shannon, with +67 stars in a day.
Hot right now
Most stars gained in a day · Oct 17
 +67
shannon
KeygraphHQ/shannon · ★ 49.1KShannon is an autonomous AI pentester that analyzes your web application's source code, maps attack vectors, and then executes real exploits against the running app to prove vulnerabilities before they reach production — 'no exploit, no report'.
SkillSpector
NVIDIA/SkillSpector · ★ 20.4KSkillSpector is a security scanner for AI agent skills (used by Claude Code, Codex CLI, Gemini CLI, and MCP) that detects vulnerabilities, malicious patterns, prompt injection, data exfiltration, and supply-chain risks before you install a skill.
 +50
oss-scanner
anthropics/oss-scanner · ★ 1.1KOSS Scanner is a service run by Anthropic that scans enrolled open-source repositories for security vulnerabilities, building each project in an isolated VM and emailing the maintainer a reproducer plus a proposed patch for anything it finds.
 +43
Anthropic-Cybersecurity-Skills
mukul975/Anthropic-Cybersecurity-Skills · ★ 34.6KAn open-source library of 818 production-grade cybersecurity skills for AI agents, covering 34 security domains and mapped to six frameworks including MITRE ATT&CK and NIST CSF 2.0.
The all-time top
38 projects · by stars
- 49.1K#1 · KeygraphHQ/shannon
shannon
Shannon is an autonomous AI pentester that analyzes your web application's source code, maps attack vectors, and then executes real exploits against the running app to prove vulnerabilities before they reach production — 'no exploit, no report'.
- 38.5K
 #2 · aquasecurity/trivy
trivy
Trivy is an all-in-one security scanner that finds vulnerabilities, misconfigurations, secrets, and software licenses across container images, filesystems, git repositories, VM images, and Kubernetes clusters.
- 34.6K#3 · mukul975/Anthropic-Cybersecurity-Skills
Anthropic-Cybersecurity-Skills
An open-source library of 818 production-grade cybersecurity skills for AI agents, covering 34 security domains and mapped to six frameworks including MITRE ATT&CK and NIST CSF 2.0.
- 4
nuclei
32.1Kprojectdiscovery/nuclei · GoA fast, open-source vulnerability scanner that runs YAML-based templates to find security issues in applications, APIs, networks, DNS and cloud configurations. Its checks come from a large global security community.
- 5

gitleaks
30.1Kgitleaks/gitleaks · GoGitleaks is a tool for detecting secrets like passwords, API keys, and tokens in git repos, files, or anything you pipe in via stdin.
- 6
infisical
29.9KInfisical/infisical · TypeScriptInfisical is an open-source security platform teams use to centralize secrets, certificates, and privileged access, with syncing, rotation, and leak prevention built in.
- 7
90DaysOfDevOps
29.8KMichaelCade/90DaysOfDevOps · ShellA structured learning curriculum for DevOps that grew out of a personal 90-day public learning challenge, now covering principles, processes, tooling, and real-world use cases like Kubernetes, Terraform, and Ansible.
- 8
trufflehog
28.6Ktrufflesecurity/trufflehog · GoTruffleHog is a CLI tool that discovers, classifies, validates, and analyzes leaked secrets like API keys, database passwords, and private keys across many sources (Git, GitHub, S3, Docker, Slack, filesystems, and more).
- 9
promptfoo
26.1Kpromptfoo/promptfoo · TypeScriptpromptfoo is a CLI and library for evaluating and red-teaming LLM apps — you test prompts, agents, and RAGs and run security scans on them, instead of relying on trial-and-error.
- 10
slim
23.4Kslimtoolkit/slim · GoSlimToolkit (formerly DockerSlim) is a free, open-source CLI toolkit that inspects, optimizes and debugs container images. It can shrink an image by up to 30x without you changing anything in your Dockerfile — and makes the result more secure too.
- 11

sops
23.4Kgetsops/sops · GoSOPS (Secrets OPerationS) is an editor for encrypted files that supports YAML, JSON, ENV, INI and BINARY formats, encrypting values with AWS KMS, GCP KMS, Azure Key Vault, HuaweiCloud KMS, age, or PGP.
- 12

API-Security-Checklist
23.3Kshieldfy/API-Security-ChecklistA community checklist of the most important security countermeasures to apply when designing, testing, and releasing an API — a list of checkboxes you run through before shipping.
- 13

Mobile-Security-Framework-MobSF
22KMobSF/Mobile-Security-Framework-MobSF · JavaScriptMobSF is an automated, all-in-one mobile security framework: it performs static and dynamic analysis, penetration testing, malware analysis and privacy analysis on Android, iOS and Windows Mobile apps.
- 14
SkillSpector
20.4KNVIDIA/SkillSpector · PythonSkillSpector is a security scanner for AI agent skills (used by Claude Code, Codex CLI, Gemini CLI, and MCP) that detects vulnerabilities, malicious patterns, prompt injection, data exfiltration, and supply-chain risks before you install a skill.
- 15
semgrep
17.1Ksemgrep/semgrep · CSemgrep is a fast, open-source static analysis tool that scans source code to find bugs, security issues, and enforce coding standards using rules that look like ordinary code rather than abstract syntax trees or regex.
- 16
prowler
15.1Kprowler-cloud/prowler · PythonProwler is an open-source cloud security platform that automates security and compliance checks across AWS, Azure, GCP, Kubernetes, M365, GitHub, and many other providers.
- 17
bytebase
14.6Kbytebase/bytebase · GoBytebase is an open-source database governance platform that acts as a control plane between users (humans and AI agents) and databases, governing change management, access control, and compliance so every change and query is reviewed, controlled, and recorded.
- 18

secguide
13.4KTencent/secguideA free, Tencent-maintained secure coding guide for developers that catalogs API-level security risks and gives concrete, actionable secure-coding solutions.
- 19

grype
13Kanchore/grype · GoGrype is a command-line vulnerability scanner that checks container images, filesystems, and SBOMs for known security vulnerabilities.
- 20
netmaker
11.8Kgravitl/netmaker · GoNetmaker is a tool that automates creating and managing virtual networks (mesh VPNs, remote access gateways, site-to-site links) using WireGuard.
- 21
osv-scanner
11.2Kgoogle/osv-scanner · GoOSV-Scanner is Google's open-source command-line vulnerability scanner: it checks your project's dependencies against OSV.dev, an open vulnerability database, and reports which known vulnerabilities affect you.
- 22

codex-security
11.1Kopenai/codex-security · TypeScriptCodex Security is OpenAI's CLI and TypeScript SDK for defining security policy and for finding, validating, and fixing security vulnerabilities in your code.
- 23
bunkerweb
11.1Kbunkerity/bunkerweb · PythonBunkerWeb is an open-source, next-generation Web Application Firewall (WAF) built as a full-featured web server on top of NGINX. It protects your web applications and APIs 'secure by default' while integrating as a reverse proxy into your existing environment.
- 24

clair
11.1Kquay/clair · GoClair is an open source tool for static analysis of vulnerabilities in application container images, covering both OCI and Docker image formats.
- 25

codeql
10.2Kgithub/codeql · CodeQLThis is the standard library and query collection for CodeQL, the code analysis engine that powers GitHub Advanced Security code scanning and GitHub's commercial security products.
- 26
defending-code-reference-harness
7.6Kanthropics/defending-code-reference-harness · PythonA reference implementation from Anthropic for finding and fixing vulnerabilities with Claude: a set of Claude Code skills (quickstart, threat-model, vuln-scan, triage, patch, customize) plus an autonomous scanning harness that runs a recon-find-verify-report-patch loop, built from learnings partnering with security teams.
- 27
DeepAudit
7.2Klintsinghua/DeepAudit · PythonDeepAudit is a multi-agent AI platform for code security auditing. It mimics how a security expert thinks, using cooperating agents (Orchestrator, Recon, Analysis, Verification) to find vulnerabilities and then verify them with automated sandbox PoC exploitation.
- 28
agent-governance-toolkit
6.4Kmicrosoft/agent-governance-toolkit · PythonA toolkit from Microsoft that governs autonomous AI agents in production: it enforces policies on tool calls, verifies agent identity, sandboxes execution, and provides SRE controls like kill switches and SLO monitoring. It covers all 10 of the OWASP Agentic Top 10 risks.
- 29
mantis
2.5Kgoogle/mantis · PythonMantis is a toolkit of skills plus a reference agent harness (built on Google's ADK) that lets AI coding agents autonomously find, reproduce, triage, and patch vulnerabilities in a codebase.
- 30
oss-scanner
1.1Kanthropics/oss-scanner · DockerfileOSS Scanner is a service run by Anthropic that scans enrolled open-source repositories for security vulnerabilities, building each project in an isolated VM and emailing the maintainer a reproducer plus a proposed patch for anything it finds.
- 31
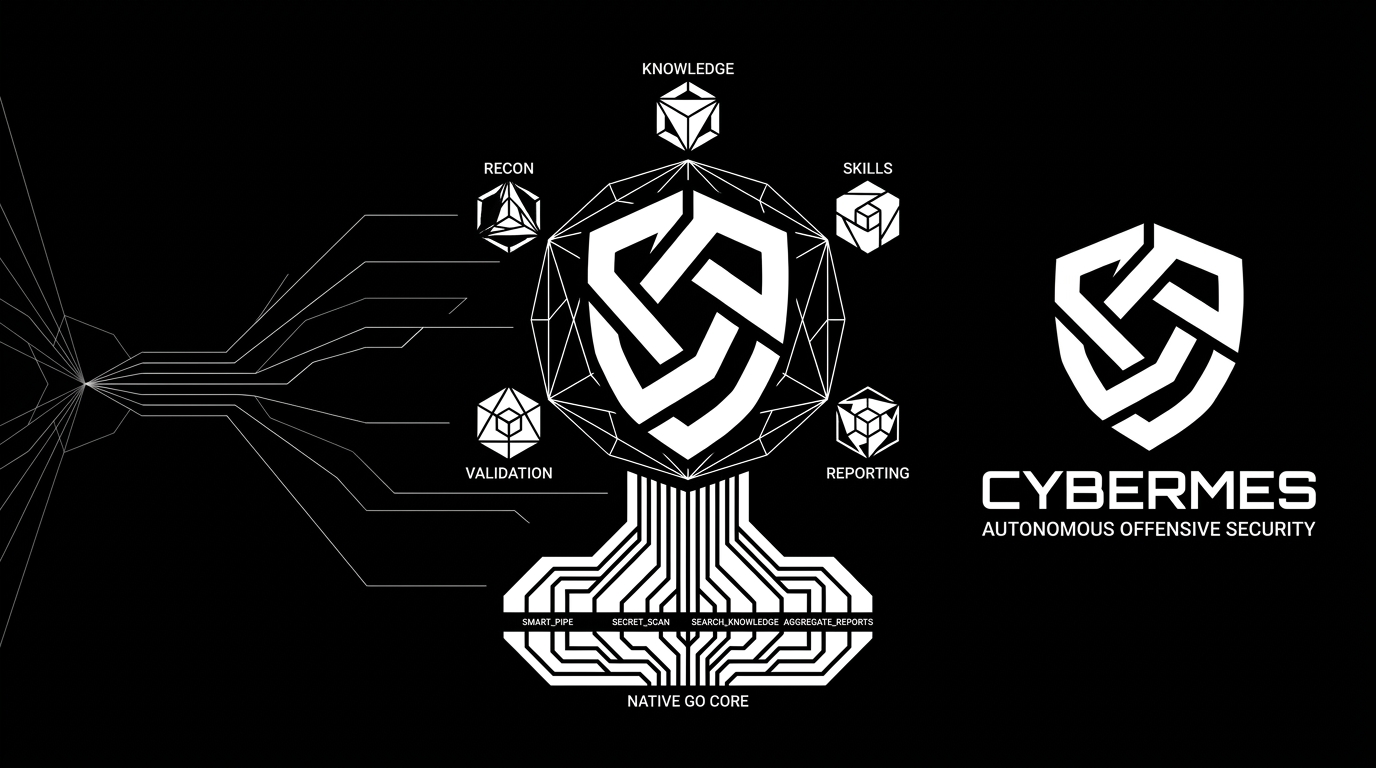
Cybermes
948Zyrexnn/Cybermes · PythonCybermes is an offensive security assistant and automation framework for authorized bug bounty hunting, reconnaissance, vulnerability research, and structured reporting, driven by AI agents and a library of 200+ playbooks.
- 32

VulnHunter
741nealbridges/VulnHunter · PythonAn open-source, agentic AI security scanner that reasons like an attacker to find exploitable vulnerabilities in source code, proves them with executable proof-of-concept exploits, and fixes them test-first. It is a maintained fork of Capital One's VulnHunter, rebuilt to run on any agent harness instead of just Claude Code.
- 33
gh-secure
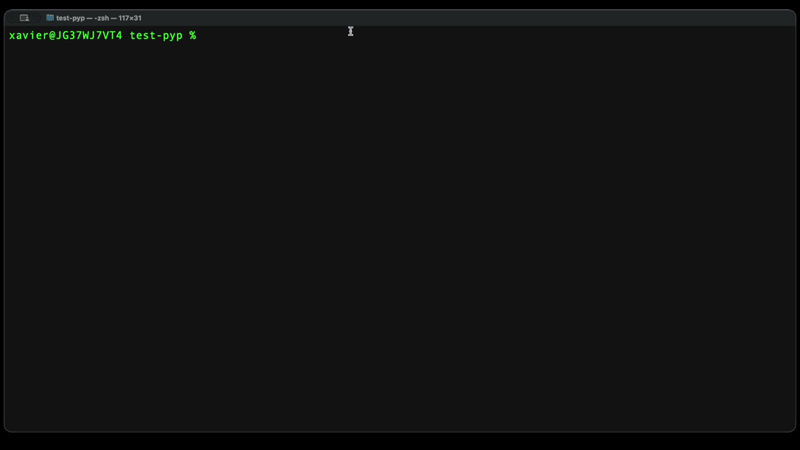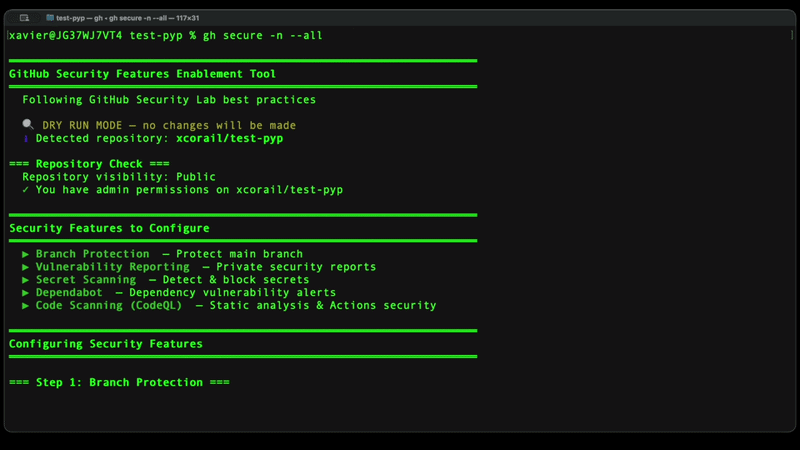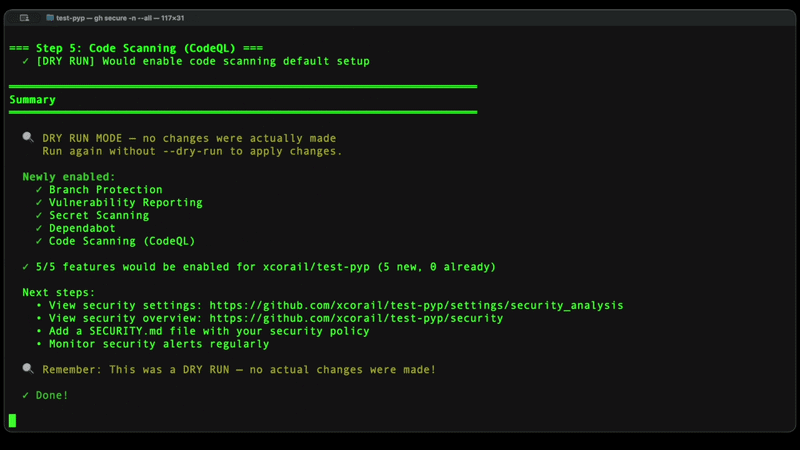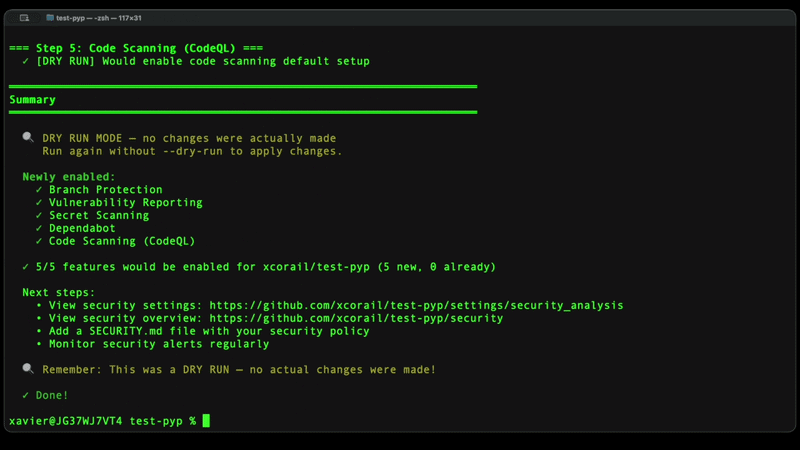
660GitHubSecurityLab/gh-secure · Shellgh-secure is a GitHub CLI extension that turns on five recommended security features on a repository — branch protection, private vulnerability reporting, secret scanning, Dependabot, and code scanning — in about 2 minutes.
- 34
0
5130sec-labs/0 · TypeScript0 is an open-source, self-evolving, multi-model AI harness for security research that finds, verifies, and fixes vulnerabilities, built by the Swiss Applied AI & Cybersecurity Research Lab.
- 35

bashka
243dmtrKovalenko/bashka · Rustbashka is a drop-in safety guard for the curl | bash install pattern: it parses the incoming install script, scores it against many checks, and follows forwarded scripts so every layer gets analyzed.
- 36
cynative
223cynative/cynative · GoCynative is an open-source AI agent framework that gives LLMs live, read-only access to your AWS, Azure, GCP, Kubernetes, GitHub and GitLab infrastructure so you can ask security questions and run cloud security posture and detection checks.
- 37
forge
213cisco-open/forge · HCLForgeMT is an open-source platform from Cisco for running self-hosted GitHub Actions runners on your own AWS accounts — ephemeral EC2 runners and Kubernetes ARC runner scale sets, operated as code across many tenant repos.
- 38

Myrqen
137stijnswapped/Myrqen · TypeScriptMyrqen is a security testing tool that runs inside a coding agent (Claude Code, Codex, or OpenCode) you already use: its own static analysis engine finds vulnerability candidates in your TypeScript/JavaScript code, then the agent dynamically verifies them against the app running on your machine.
Related topics
Often tagged together
- linux4,182
- security977
- open-source5,667
- docker1,659
- macos3,545
- security-tools281
- windows3,403
- cli2,229
- cybersecurity245
- go690
- self-hosted1,928
- vulnerability-scanner43
- python2,418
- apache-2.01,434
- developer-tools2,930
- static-analysis129
- cross-platform2,623
- devops455
- llm1,489
- terminal1,100
- application-security18
- penetration-testing126
- server1,460
- ai1,957