Topics / #supply-chain-security
Supply-chain-security projects on GitHub
Tools that secure software supply chains by verifying artifacts and flagging risky dependencies.
As of , the most-starred Supply-chain-security projects on GitHub are distroless (23.1K stars), SkillSpector (20.4K stars) and semgrep (17.1K stars). GitHub.Locker tracks 17 Supply-chain-security repositories with 126.9K stars combined. The fastest-growing on October 16 was SkillSpector, with +73 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
SkillSpector
NVIDIA/SkillSpector · ★ 20.4KSkillSpector is a security scanner for AI agent skills (used by Claude Code, Codex CLI, Gemini CLI, and MCP) that detects vulnerabilities, malicious patterns, prompt injection, data exfiltration, and supply-chain risks before you install a skill.
 +26
nono
nolabs-ai/nono · ★ 4.5Knono is a zero-setup, zero-latency sandbox that runs AI coding agents (Claude Code, Codex, OpenCode, etc.) with least-privilege access, so they can't touch your SSH keys, cloud credentials, or the rest of your disk by default.
 +18
artifactproof
MaxHu-xuan/artifactproof · ★ 858ArtifactProof is an offline, local command-line tool that hashes a final PPTX with SHA-256, runs basic structural checks, and binds caller-supplied QA evidence into a tamper-evident HMAC-SHA256 receipt, so you can reverify before delivery or after receipt that nothing was swapped.
 +15
semgrep
semgrep/semgrep · ★ 17.1KSemgrep is a fast, open-source static analysis tool that scans source code to find bugs, security issues, and enforce coding standards using rules that look like ordinary code rather than abstract syntax trees or regex.
The all-time top
17 projects · by stars
- 23.1K
 #1 · GoogleContainerTools/distroless
distroless
A set of minimal container base images that contain only your application and its runtime dependencies — no package managers, shells or other programs you would expect in a normal Linux distribution.
- 20.4K
#2 · NVIDIA/SkillSpector
SkillSpector
SkillSpector is a security scanner for AI agent skills (used by Claude Code, Codex CLI, Gemini CLI, and MCP) that detects vulnerabilities, malicious patterns, prompt injection, data exfiltration, and supply-chain risks before you install a skill.
- 17.1K#3 · semgrep/semgrep
semgrep
Semgrep is a fast, open-source static analysis tool that scans source code to find bugs, security issues, and enforce coding standards using rules that look like ordinary code rather than abstract syntax trees or regex.
- 4

grype
13Kanchore/grype · GoGrype is a command-line vulnerability scanner that checks container images, filesystems, and SBOMs for known security vulnerabilities.
- 5
xray
11.8Kchaitin/xray · Vuexray is a security assessment tool built by Chaitin for scanning common web vulnerabilities and running custom PoCs against targets.
- 6
osv-scanner
11.2Kgoogle/osv-scanner · GoOSV-Scanner is Google's open-source command-line vulnerability scanner: it checks your project's dependencies against OSV.dev, an open vulnerability database, and reports which known vulnerabilities affect you.
- 7

fresh-start
6.2Knirholas/fresh-startThis is the repository formerly known as nirholas/claude-code, the most widely forked mirror of the Claude Code source leak from 31 March 2026. The leaked source itself was stripped out after Anthropic's DMCA notice, which has not been retracted, so the repo now just explains what happened.
- 8
awesome-agent-skills
5.2Klibukai/awesome-agent-skillsThis is a curated Chinese-language guide to Agent Skills: a quickstart to the open Skill spec, a catalog of official docs and tutorials, a list of recommended skills grouped by category, and guidance on building and security-reviewing your own skills.
- 9

bumblebee
5.1Kperplexityai/bumblebee · GoBumblebee is a read-only inventory collector that scans macOS and Linux developer machines for package, extension, and developer-tool metadata, so responders can quickly check if a machine matches a known supply-chain compromise advisory.
- 10
nono
4.5Knolabs-ai/nono · Rustnono is a zero-setup, zero-latency sandbox that runs AI coding agents (Claude Code, Codex, OpenCode, etc.) with least-privilege access, so they can't touch your SSH keys, cloud credentials, or the rest of your disk by default.
- 11

raptor
3.9Kgadievron/raptor · PythonRAPTOR turns a Claude Code session into an offensive/defensive security agent: Claude.md rules, sub-agents and skills orchestrate tools like radare2, Frida, Z3 and CodeQL for binary reverse-engineering, exploit-feasibility research, and software supply-chain (SCA) analysis.
- 12
npmx.dev
3.6Knpmx-dev/npmx.dev · TypeScriptnpmx.dev is a fast, modern browser for the npm registry that gives you a quicker, more informative UI for looking up packages, users, and organizations without replacing the registry itself.
- 13
artifactproof
858MaxHu-xuan/artifactproof · PythonArtifactProof is an offline, local command-line tool that hashes a final PPTX with SHA-256, runs basic structural checks, and binds caller-supplied QA evidence into a tamper-evident HMAC-SHA256 receipt, so you can reverify before delivery or after receipt that nothing was swapped.
- 14

awesome-agent-skills-security
260LLMSecurity/awesome-agent-skills-securityA curated, awesome-list style collection of research papers, standards, frameworks, and benchmarks about securing AI agent tool use and the emerging 'agent skills' ecosystem — covering attacks like prompt injection and tool poisoning as well as defenses like sandboxing and permission control.
- 15

bashka
244dmtrKovalenko/bashka · Rustbashka is a drop-in safety guard for the curl | bash install pattern: it parses the incoming install script, scores it against many checks, and follows forwarded scripts so every layer gets analyzed.
- 16
vet
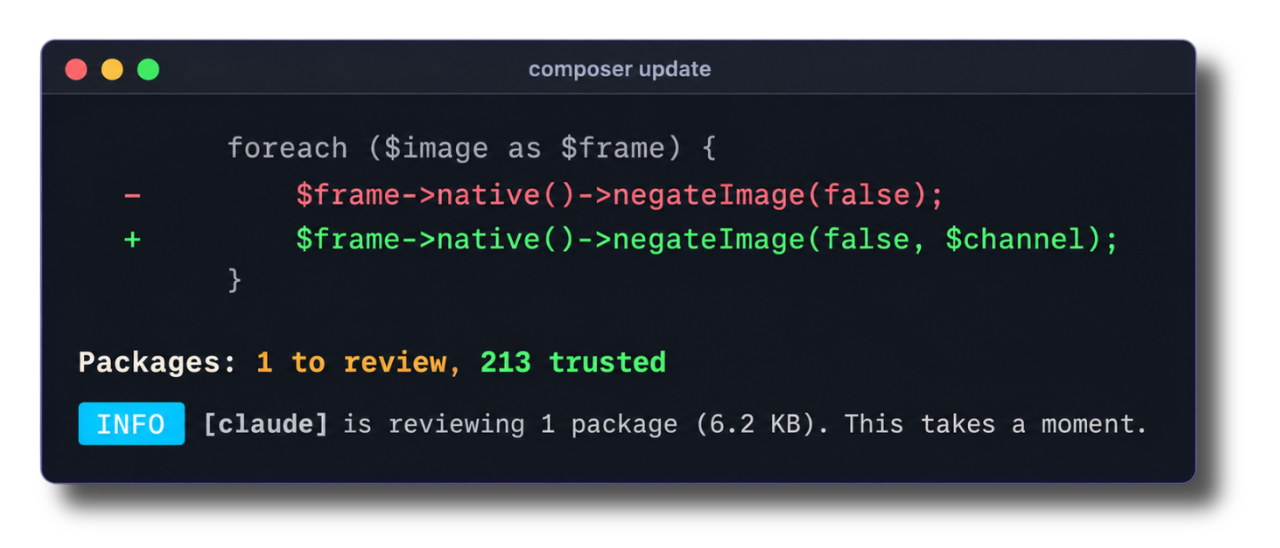
181laravel/vet · PHPLaravel Vet is a dependency audit for PHP: it shows you the code a composer update is about to write into your vendor/ directory and records the packages you trust in a vet.json file, so each next update only asks about what changed.
- 17

Airsec
150bas3line/Airsec · TypeScriptAirsec is a CLI tool that drives a coding agent you already have installed (Claude Code, Codex, OpenCode, Command Code) through a structured, multi-pass security audit of your code, then turns the findings into an actionable report.
Related topics
Often tagged together
- security977
- linux4,182
- cli2,227
- open-source5,666
- macos3,544
- developer-tools2,927
- cybersecurity244
- security-tools281
- windows3,401
- command-line-tool715
- claude-code908
- ai-agents1,293
- apache-2.01,434
- cross-platform2,622
- static-analysis126
- devsecops38
- docker1,658
- vulnerability-scanner44
- devops455
- go684
- llm1,484
- mcp917
- mit3,311
- npm1,019