Topics / #android-security
Android-security projects on GitHub
Security analysis and hardening of Android apps, including reverse engineering defenses
As of , the most-starred Android-security projects on GitHub are Mobile-Security-Framework-MobSF (22.3K stars), bla (6.1K stars) and NOIR (3.6K stars). GitHub.Locker tracks 5 Android-security repositories with 33.6K stars combined. The fastest-growing on November 17 was bla, with +101 stars in a day.
Hot right now
Most stars gained in a day · Nov 17
 +101
bla
qybaihe/bla · ★ 6.1KBLA (Blind LLM Agents) is a defensive tool you run against your own shipped build (binaries, Electron apps, JS bundles, Python, WASM) to sabotage AI reverse-engineering agents like REA that try to analyze it, while your users still get the same runtime behavior.
 +33
DirtyFrag
mitschud/DirtyFrag · ★ 1.4KDirtyFrag is a hardened fork of diabl0w's DFRoot that exploits CVE-2026-43284, a kernel page-cache write primitive, to temporarily root Samsung and other Android phones without an unlocked bootloader or a custom kernel.
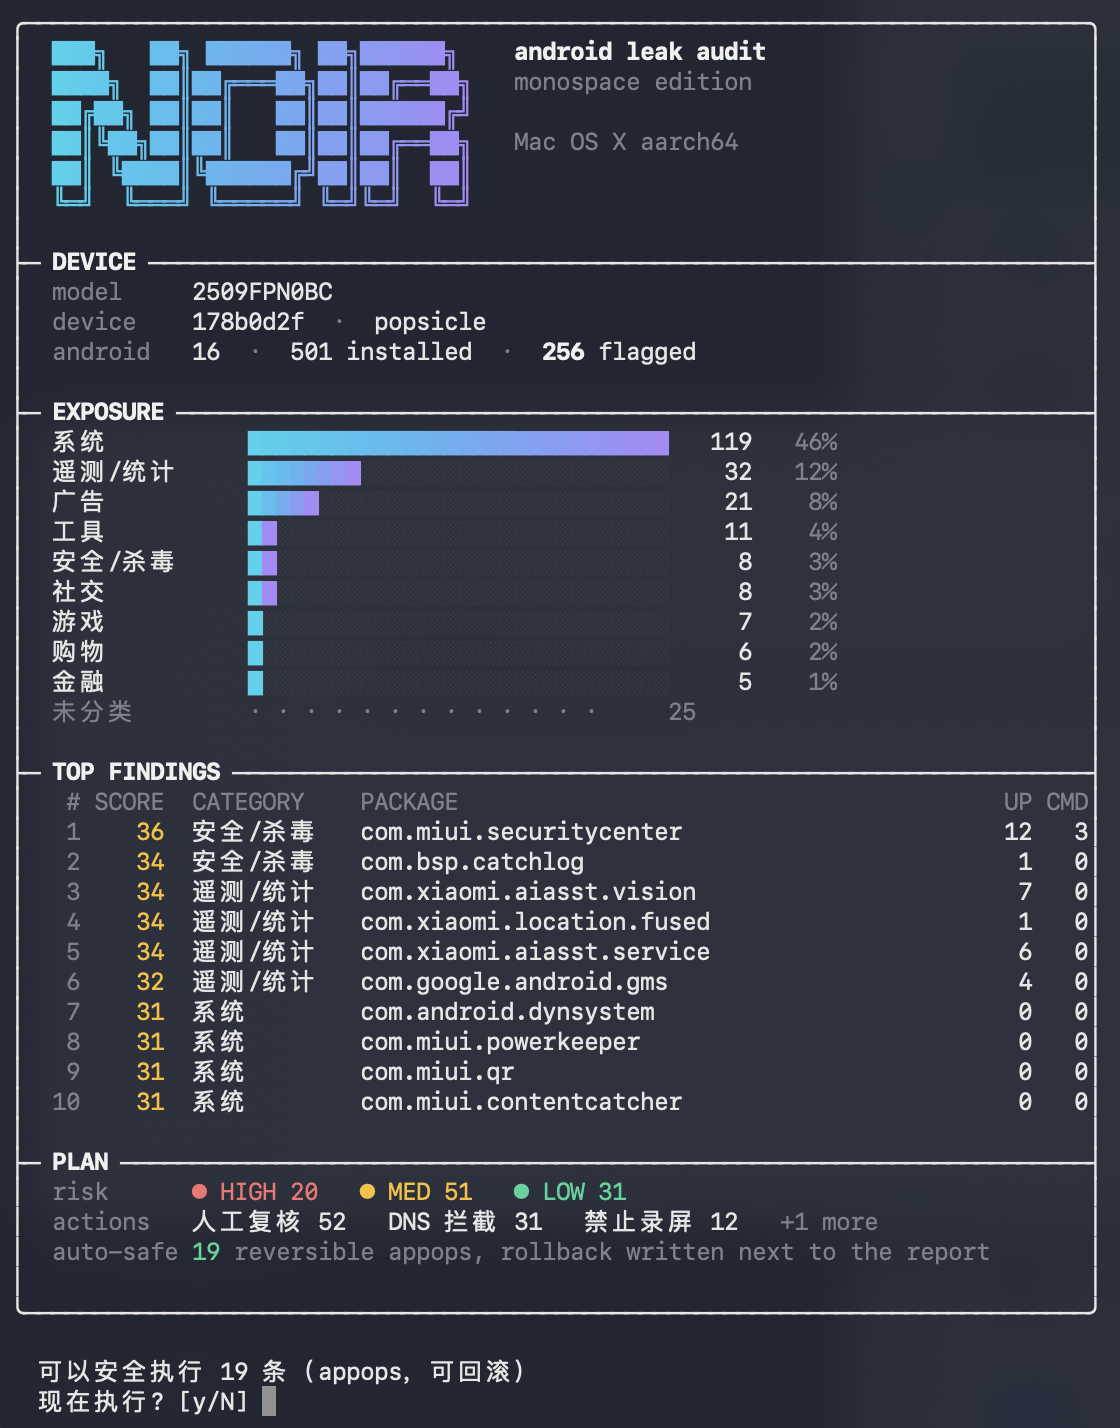 +16
NOIR
Verlintas/NOIR · ★ 3.6KNOIR is a desktop audit tool for Android. Over adb it reads each installed app's permissions and the network endpoints inside its APK, then gives categories, risk scores and reversible fix suggestions.
 +10
Mobile-Security-Framework-MobSF
MobSF/Mobile-Security-Framework-MobSF · ★ 22.3KMobSF is an automated, all-in-one mobile security framework: it performs static and dynamic analysis, penetration testing, malware analysis and privacy analysis on Android, iOS and Windows Mobile apps.
The all-time top
5 projects · by stars
- 22.3K#1 · MobSF/Mobile-Security-Framework-MobSF
Mobile-Security-Framework-MobSF
MobSF is an automated, all-in-one mobile security framework: it performs static and dynamic analysis, penetration testing, malware analysis and privacy analysis on Android, iOS and Windows Mobile apps.
Deploy on Railway - 6.1K#2 · qybaihe/bla
bla
BLA (Blind LLM Agents) is a defensive tool you run against your own shipped build (binaries, Electron apps, JS bundles, Python, WASM) to sabotage AI reverse-engineering agents like REA that try to analyze it, while your users still get the same runtime behavior.
- 3.6K#3 · Verlintas/NOIR
NOIR
NOIR is a desktop audit tool for Android. Over adb it reads each installed app's permissions and the network endpoints inside its APK, then gives categories, risk scores and reversible fix suggestions.
- 4
DirtyFrag
1.4Kmitschud/DirtyFrag · JavaDirtyFrag is a hardened fork of diabl0w's DFRoot that exploits CVE-2026-43284, a kernel page-cache write primitive, to temporarily root Samsung and other Android phones without an unlocked bootloader or a custom kernel.
- 5

qufz
323yooma1/qufz · JavaAn LSPosed module that cuts off the ColorOS phone manager's AI anti-fraud telemetry and cloud reporting, while local scam warnings keep working.
Related topics
Often tagged together