Topics / #agent-security
Agent-security projects on GitHub
Security scanning and protection tooling for AI agents and their skills.
As of , the most-starred Agent-security projects on GitHub are NemoClaw (22.8K stars), SkillSpector (20.4K stars) and nasiko (9.5K stars). GitHub.Locker tracks 16 Agent-security repositories with 73.5K stars combined. The fastest-growing on October 16 was SkillSpector, with +73 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
SkillSpector
NVIDIA/SkillSpector · ★ 20.4KSkillSpector is a security scanner for AI agent skills (used by Claude Code, Codex CLI, Gemini CLI, and MCP) that detects vulnerabilities, malicious patterns, prompt injection, data exfiltration, and supply-chain risks before you install a skill.
 +26
nono
nolabs-ai/nono · ★ 4.5Knono is a zero-setup, zero-latency sandbox that runs AI coding agents (Claude Code, Codex, OpenCode, etc.) with least-privilege access, so they can't touch your SSH keys, cloud credentials, or the rest of your disk by default.
 +9
NemoClaw
NVIDIA/NemoClaw · ★ 22.8KAn open source reference stack from NVIDIA for running AI agents like OpenClaw, Hermes and LangChain Deep Agents more safely inside NVIDIA OpenShell sandboxes, with managed inference, network policy and lifecycle operations via its CLI.
 +9
nordef-matrix-open-control
MORTEN-BUUR/nordef-matrix-open-control · ★ 741A model-independent safety belt for AI agents: it puts deterministic 0/1/2 policy decisions, Ed25519-signed human approval, replay protection, and a hash-chained evidence log outside the language model itself.
The all-time top
16 projects · by stars
- 22.8K#1 · NVIDIA/NemoClaw
NemoClaw
An open source reference stack from NVIDIA for running AI agents like OpenClaw, Hermes and LangChain Deep Agents more safely inside NVIDIA OpenShell sandboxes, with managed inference, network policy and lifecycle operations via its CLI.
- 20.4K
#2 · NVIDIA/SkillSpector
SkillSpector
SkillSpector is a security scanner for AI agent skills (used by Claude Code, Codex CLI, Gemini CLI, and MCP) that detects vulnerabilities, malicious patterns, prompt injection, data exfiltration, and supply-chain risks before you install a skill.
- 9.5K
 #3 · Nasiko-Labs/nasiko
nasiko
Nasiko is a single control-plane server that deploys, routes, secures, and observes AI agents built on the A2A protocol, acting as the one checkpoint every agent-to-agent call passes through.
- 4
AI-Infra-Guard
6.9KTencent/AI-Infra-Guard · PythonAI-Infra-Guard (A.I.G) is a full-stack AI red teaming platform built by Tencent Zhuque Lab that scans AI agents, MCP servers, agent skills, and AI infrastructure components for security vulnerabilities, and evaluates LLMs against jailbreak attacks.
- 5
nono
4.5Knolabs-ai/nono · Rustnono is a zero-setup, zero-latency sandbox that runs AI coding agents (Claude Code, Codex, OpenCode, etc.) with least-privilege access, so they can't touch your SSH keys, cloud credentials, or the rest of your disk by default.
- 6
mantis
2.5Kgoogle/mantis · PythonMantis is a toolkit of skills plus a reference agent harness (built on Google's ADK) that lets AI coding agents autonomously find, reproduce, triage, and patch vulnerabilities in a codebase.
- 7
agent-beacon
1.8KAsymptote-Labs/agent-beacon · GoAn open-source memory layer for AI coding agents: it captures session history across Claude Code, Cursor, Codex, OpenCode and 20+ other harnesses, then turns useful workflows, corrections and debugging patterns into knowledge future agents can reuse.
- 8
OpenAPPA
1.6Karchestra-ai/OpenAPPA · RustOpenAPPA is a deterministic guardrail layer that sits between an AI agent and its tools, checking every tool call to decide whether the data involved is allowed to reach that destination.
- 9
nordef-matrix-open-control
741MORTEN-BUUR/nordef-matrix-open-control · PythonA model-independent safety belt for AI agents: it puts deterministic 0/1/2 policy decisions, Ed25519-signed human approval, replay protection, and a hash-chained evidence log outside the language model itself.
- 10

VulnHunter
735nealbridges/VulnHunter · PythonAn open-source, agentic AI security scanner that reasons like an attacker to find exploitable vulnerabilities in source code, proves them with executable proof-of-concept exploits, and fixes them test-first. It is a maintained fork of Capital One's VulnHunter, rebuilt to run on any agent harness instead of just Claude Code.
- 11
agent-safe-pipeline
688decionis/agent-safe-pipeline · TypeScriptAgent-Safe Pipeline is a reference implementation of an 'Execution Authority' architecture that sits between AI agents or APIs and consequential HTTP actions: it intercepts the action, asks Decionis whether it is authorized, and only forwards it if a single-use grant is issued, otherwise holding it for a human or refusing it, with every decision leaving tamper-evident evidence.
- 12
safelabs-eval
569AgentSafeLabs/safelabs-eval · Pythonsafelabs-eval is an open-source red-teaming and evaluation framework for AI agents, built around an OWASP-inspired ASI01-ASI10 taxonomy. It fires 300 curated adversarial prompts at an agent and scores every response with pattern-based detectors to produce a structured security report.
- 13
huashu-mac-use
307alchaincyf/huashu-mac-use · SwiftAn Agent Skill that lets coding agents like Claude Code, Codex and Cursor drive macOS apps that have no API — reading screens, clicking and typing — and leaves reproducible evidence of every step.
- 14

awesome-agent-skills-security
260LLMSecurity/awesome-agent-skills-securityA curated, awesome-list style collection of research papers, standards, frameworks, and benchmarks about securing AI agent tool use and the emerging 'agent skills' ecosystem — covering attacks like prompt injection and tool poisoning as well as defenses like sandboxing and permission control.
- 15
geiger
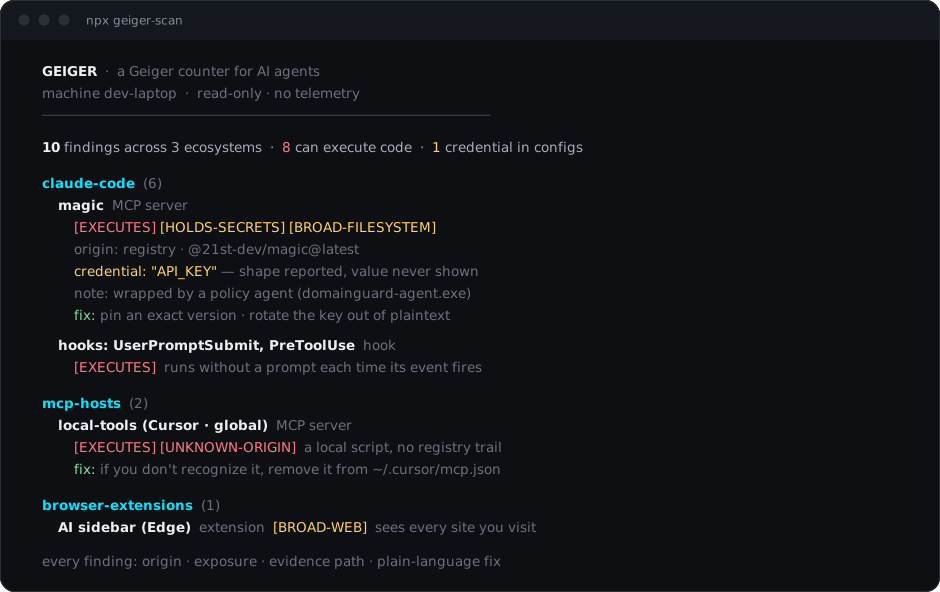
166Atomburstofficial/geiger · JavaScriptGeiger is a read-only scanner for AI tooling: one command inventories every AI agent, harness, MCP server, plugin and AI extension on a machine and says in plain language what each one can touch.
- 16

defender
127StackOneHQ/defender · TypeScriptIt's an open-source shield against indirect prompt injection: Defender inspects tool results (emails, docs, PRs) your AI agent consumes for hidden injection attacks before they reach the LLM, and returns a sanitized copy plus an allow/block verdict.
Related topics
Often tagged together
- security976
- ai-agents1,289
- open-source5,666
- linux4,184
- macos3,544
- cli2,227
- developer-tools2,924
- windows3,403
- ai-security44
- llm1,483
- security-tools282
- agent821
- cybersecurity245
- mcp913
- ai1,955
- ai-safety28
- apache-2.01,434
- llm-security24
- claude-code903
- python2,383
- agentic-ai310
- cross-platform2,623
- docker1,660
- prompt-injection21