


What is this?
 NetBird is an open-source Zero Trust networking platform: it builds a configuration-free peer-to-peer WireGuard overlay network with centralized access control, so you can create secure private networks without open ports, complex firewall rules or VPN gateways.
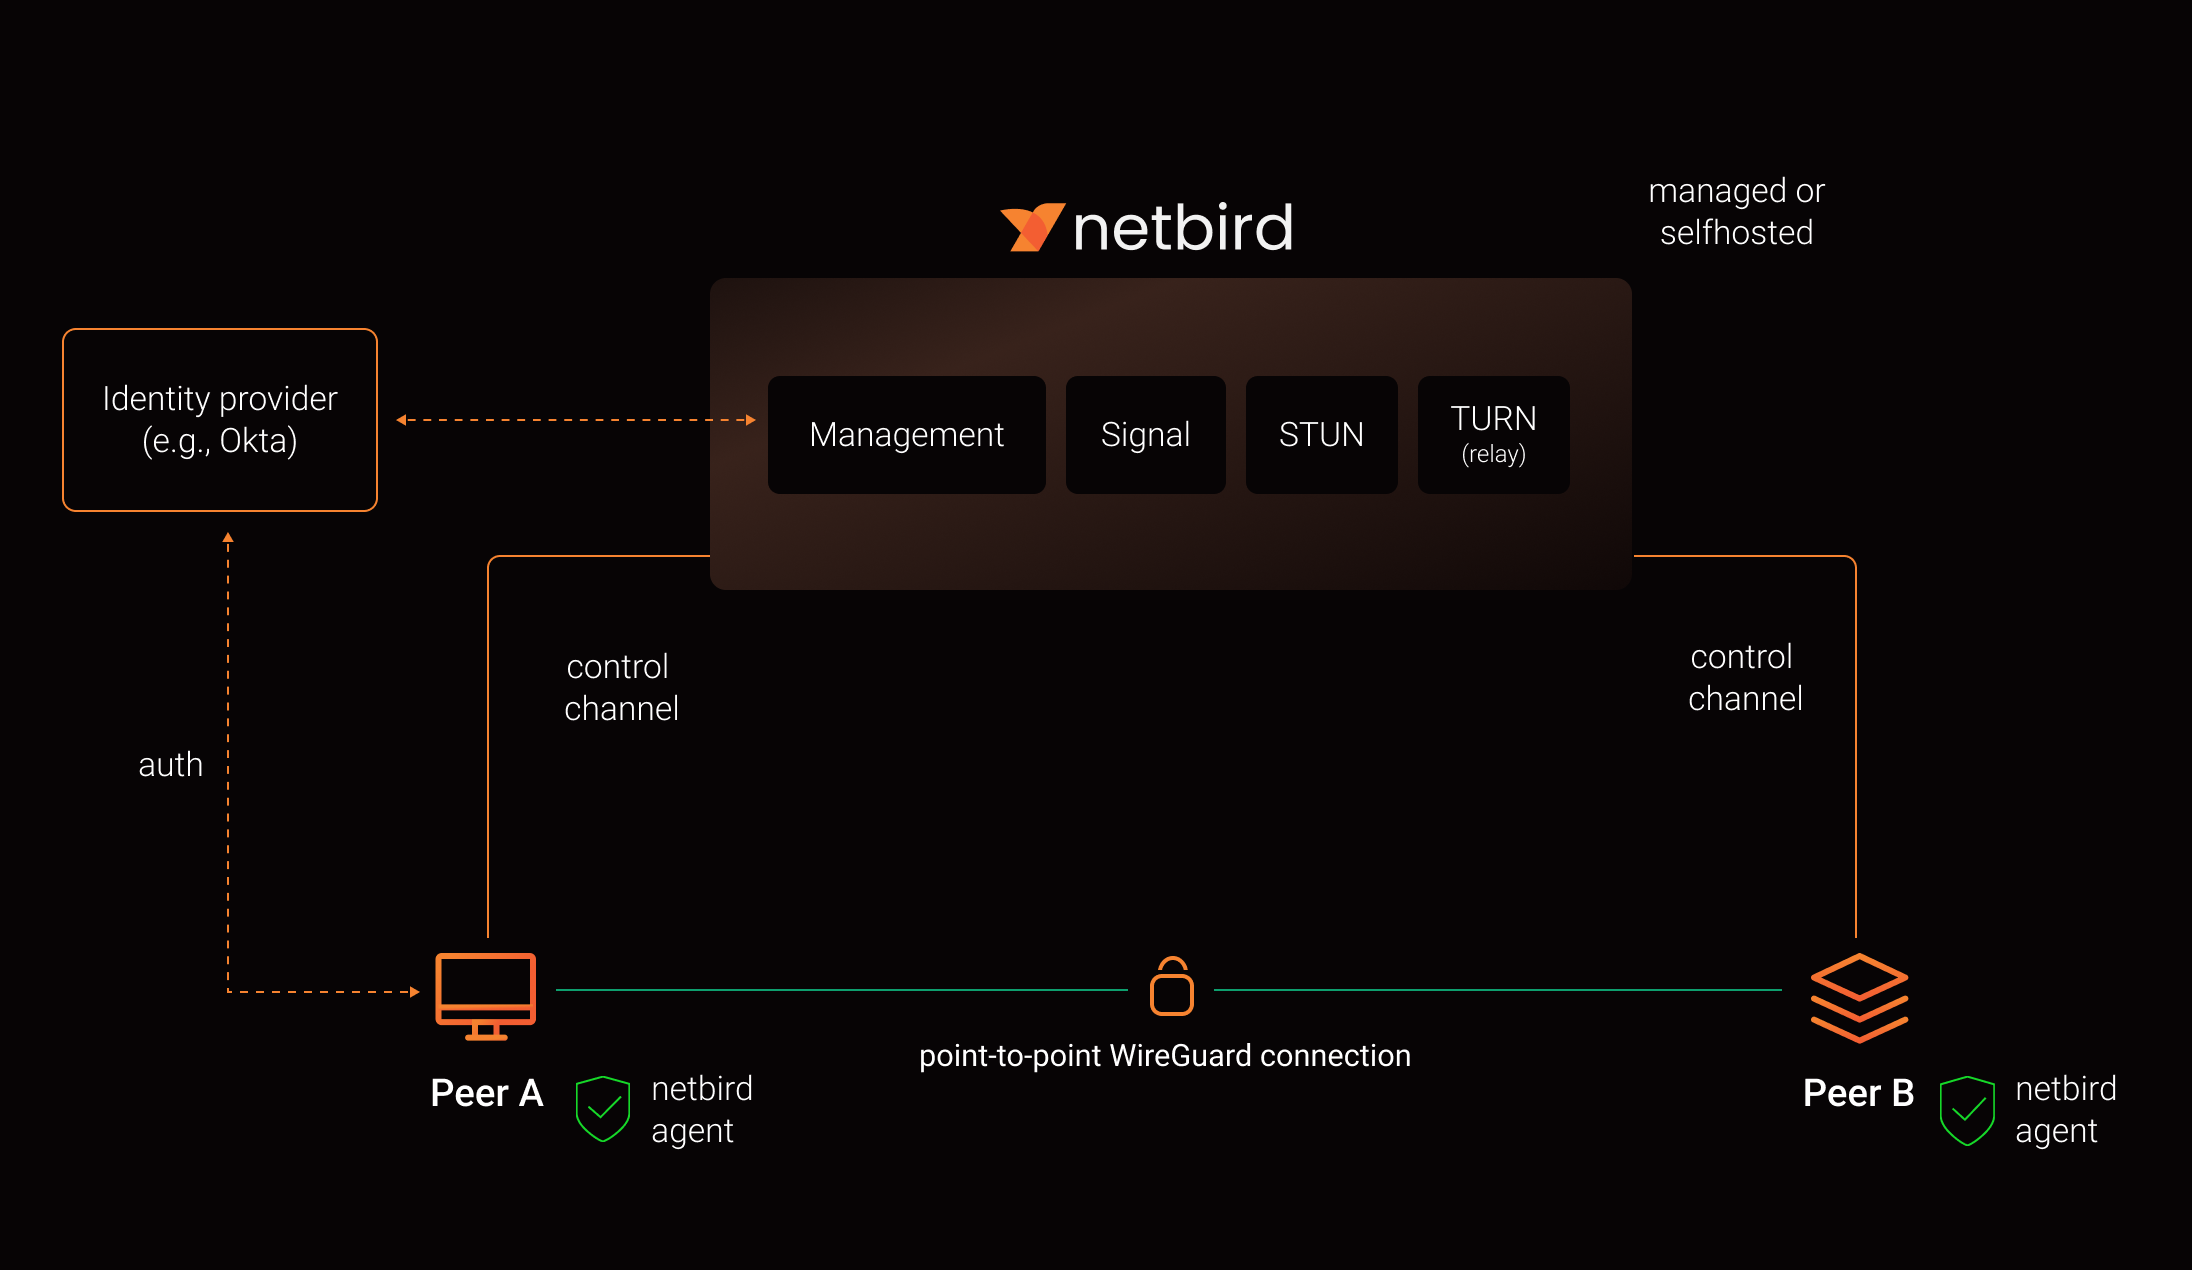
Is this an app I install, or a whole platform I have to run?Both parts: every machine runs a NetBird agent that manages WireGuard, while a Management Service holds the network state — either NetBird Cloud or your own self-hosted instance, all managed from an admin web UI.
Both parts: every machine runs a NetBird agent that manages WireGuard, while a Management Service holds the network state — either NetBird Cloud or your own self-hosted instance, all managed from an admin web UI.How do I get started with it?Install the NetBird app and sign up with Google, Microsoft, GitHub or your email, then check the admin web UI. For self-hosting, run the quickstart script on a Linux VM (1 CPU, 2 GB RAM) with Docker Compose v2+ and a public domain — it takes about 5 minutes.
Install the NetBird app and sign up with Google, Microsoft, GitHub or your email, then check the admin web UI. For self-hosting, run the quickstart script on a Linux VM (1 CPU, 2 GB RAM) with Docker Compose v2+ and a public domain — it takes about 5 minutes.Does the peer-to-peer connection always work?Not always — behind carrier-grade NAT a direct p2p connection may fail, and NetBird then establishes the secure WireGuard tunnel through a Relay Service instead.
Not always — behind carrier-grade NAT a direct p2p connection may fail, and NetBird then establishes the secure WireGuard tunnel through a Relay Service instead.Which devices and systems can run it?Linux, macOS, Windows, FreeBSD, iOS, Android and Apple TV, Raspberry Pi, plus pfSense, OPNsense, MikroTik RouterOS, OpenWRT, Synology, TrueNAS, Proxmox, containers and serverless.
Linux, macOS, Windows, FreeBSD, iOS, Android and Apple TV, Raspberry Pi, plus pfSense, OPNsense, MikroTik RouterOS, OpenWRT, Synology, TrueNAS, Proxmox, containers and serverless.Is it fully open source?Mostly: BSD-3-Clause covers the whole repository except the management/, signal/ and relay/ directories, which are licensed under AGPLv3.
Mostly: BSD-3-Clause covers the whole repository except the management/, signal/ and relay/ directories, which are licensed under AGPLv3.How do I control who can access what in the network?From the admin web UI: access policies built on groups and rules, SSO and MFA support, IdP integrations, device posture checks, and SSH gated by central access policies.
From the admin web UI: access policies built on groups and rules, SSO and MFA support, IdP integrations, device posture checks, and SSH gated by central access policies.What is the NetBird Agent Network?A beta feature: identity-aware access control for AI agents — keyless access to LLM APIs and private resources over the encrypted NetBird tunnel.
A beta feature: identity-aware access control for AI agents — keyless access to LLM APIs and private resources over the encrypted NetBird tunnel.Can traffic be routed beyond my own peers?Yes: routes to external networks, domain-based DNS routes, exit nodes, private and custom DNS zones, and an IPv6 dual-stack overlay.
Yes: routes to external networks, domain-based DNS routes, exit nodes, private and custom DNS zones, and an IPv6 dual-stack overlay.How do I provision many machines at once?Use setup keys for bulk provisioning, the public API, the Terraform provider or the Ansible collection; IdP groups sync over JWT keeps membership in step with your identity provider.
Use setup keys for bulk provisioning, the public API, the Terraform provider or the Ansible collection; IdP groups sync over JWT keeps membership in step with your identity provider.Is the main branch safe to deploy?No — it can be unstable or even broken during development; use the releases for stable versions.
No — it can be unstable or even broken during development; use the releases for stable versions.What are similar projects?pangolin, nebula, tailscale, algo, EasyTier, netmaker, SoftEtherVPN, tailcat
pangolin, nebula, tailscale, algo, EasyTier, netmaker, SoftEtherVPN, tailcatWhich topics is it in?wireguard-vpn, nat-traversal, ansible, terraform, wireguard, firewall, remote-access, sso, network-security, p2p, raspberry-pi, vpn
wireguard-vpn, nat-traversal, ansible, terraform, wireguard, firewall, remote-access, sso, network-security, p2p, raspberry-pi, vpn