Topics / #access-control
Access-control projects on GitHub
Managing permissions, roles, and authorization in applications.
As of , the most-starred Access-control projects on GitHub are nocodb (65.3K stars), graphql-engine (32.1K stars) and jumpserver (31.8K stars). GitHub.Locker tracks 26 Access-control repositories with 330.9K stars combined. The fastest-growing on October 18 was TencentDB-Agent-Memory, with +72 stars in a day.
Hot right now
Most stars gained in a day · Oct 18
 +72
TencentDB-Agent-Memory
TencentCloud/TencentDB-Agent-Memory · ★ 29.5KA team-level memory hub for AI agents. It turns conversations, docs, and code into four reusable memory assets — Chat Memory, Skills, Wiki, and CodeGraph — that agents across a team can share, govern, and equip.
 +58
OpenLore
aakarim/OpenLore · ★ 1.5KOpenLore is a self-hosted, agent-native knowledge server: point it at a folder of Markdown and every agent on the team (Claude Code, Codex, Cursor, CI jobs) reads the same files over SSH and MCP, with control over who can see and change what.
 +28
run-ai
dsx-ai-factory/run-ai · ★ 487NVIDIA Run:ai is an open-source AI workload and GPU orchestration platform for managing shared AI infrastructure on Kubernetes, handling GPU scheduling, resource quotas, and governance across teams.
 +12
bytebase
bytebase/bytebase · ★ 14.6KBytebase is an open-source database governance platform that acts as a control plane between users (humans and AI agents) and databases, governing change management, access control, and compliance so every change and query is reviewed, controlled, and recorded.
The all-time top
26 projects · by stars
- 65.3K
 #1 · nocodb/nocodb
nocodb
NocoDB is a free, self-hostable Airtable alternative: an online database builder that gives your data a rich, no-code spreadsheet interface.
- 32.1K
 #2 · hasura/graphql-engine
graphql-engine
Hasura is an open source engine that instantly generates realtime GraphQL (and REST) APIs over your databases, with fine-grained access control and the ability to trigger webhooks on database events.
- 31.8K
 #3 · jumpserver/jumpserver
jumpserver
JumpServer is an open-source Privileged Access Management (PAM) platform — a bastion host that gives DevOps and IT teams secure, on-demand access to SSH, RDP, Kubernetes, database, RemoteApp and other endpoints through a web browser.
- 4
chatgpt-web
31.4KChanzhaoyu/chatgpt-web · VueA self-hosted ChatGPT demo web page built with Express and Vue3: a browser chat UI you connect to ChatGPT either through the official OpenAI API or through an unofficial web accessToken proxy.
- 5
TencentDB-Agent-Memory
29.5KTencentCloud/TencentDB-Agent-Memory · TypeScriptA team-level memory hub for AI agents. It turns conversations, docs, and code into four reusable memory assets — Chat Memory, Skills, Wiki, and CodeGraph — that agents across a team can share, govern, and equip.
- 6
gin-vue-admin
25.1Kflipped-aurora/gin-vue-admin · GoA full-stack admin development platform: a Vue 3 + Element frontend and a Go (Gin) backend, pre-wired with JWT auth, casbin permissions, dynamic routes and menus, and code/form generators so you start on business logic instead of boilerplate.
- 7
casbin
20.5Kapache/casbin · GoAn open-source access control library for Go projects: it enforces authorization based on configurable models like ACL, RBAC and ABAC.
- 8
docs
16.9Ksuitenumerique/docs · PythonDocs is an open-source collaborative text editor - a self-hostable alternative to Notion or Google Docs, built on Django and React. Teams write, organize and share documents together in real time.
- 9
bytebase
14.6Kbytebase/bytebase · GoBytebase is an open-source database governance platform that acts as a control plane between users (humans and AI agents) and databases, governing change management, access control, and compliance so every change and query is reviewed, controlled, and recorded.
- 10
laravel-permission
13Kspatie/laravel-permission · PHPA Laravel package that lets you manage user permissions and roles through your database, and checks them via Laravel's built-in Gate system.
- 11

dufs
10.9Ksigoden/dufs · RustDufs is a command-line file server written in Rust that supports static file serving, uploads, search, access control, and WebDAV.
- 12
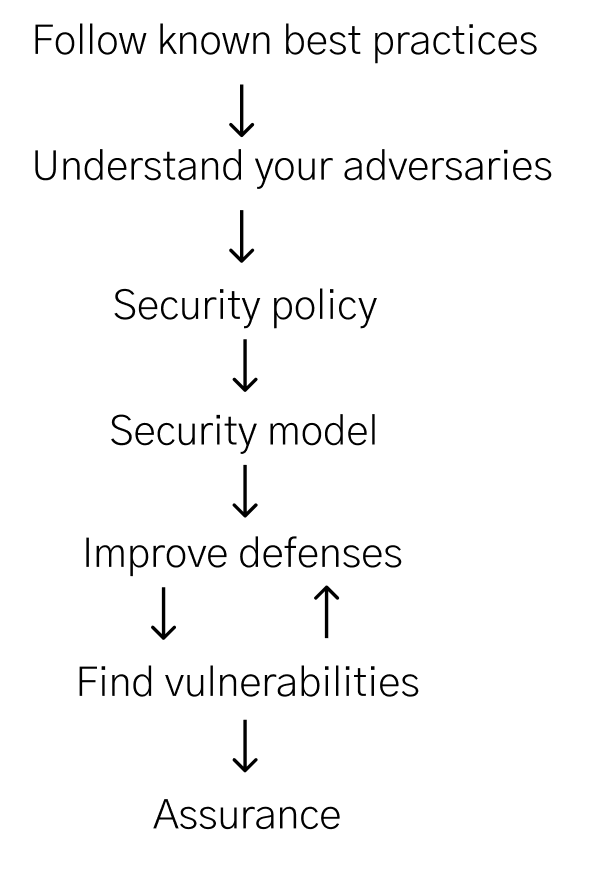
how-to-secure-anything
10.2Kveeral-patel/how-to-secure-anythingA curated README that documents a systematic process for security engineering: how to secure any kind of system, whether it is a medieval castle, an art museum, or a computer network, by thinking about adversaries, policies, models, and defenses.
- 13
filebrowser
8.8Kgtsteffaniak/filebrowser · GoFileBrowser Quantum is a self-hosted web app that lets you browse, manage, preview, and edit your files through a browser, with a modern responsive UI.
- 14
vouch
5.1Kmitchellh/vouch · NushellVouch is a community trust management system where trusted maintainers explicitly vouch for or denounce contributors, and only vouched people are allowed to interact with certain parts of a project, like opening issues or pull requests.
- 15

rfcs
4.2Kastrid-runtime/rfcs · PythonThis repository holds RFCs (design proposals) that define any substantial change to the contract between Astrid's kernel and user-space, covering the host ABI, IPC protocol, capability model, manifest schema, VFS semantics, capsule interface standards, and the SDK's public API.
- 16
executor
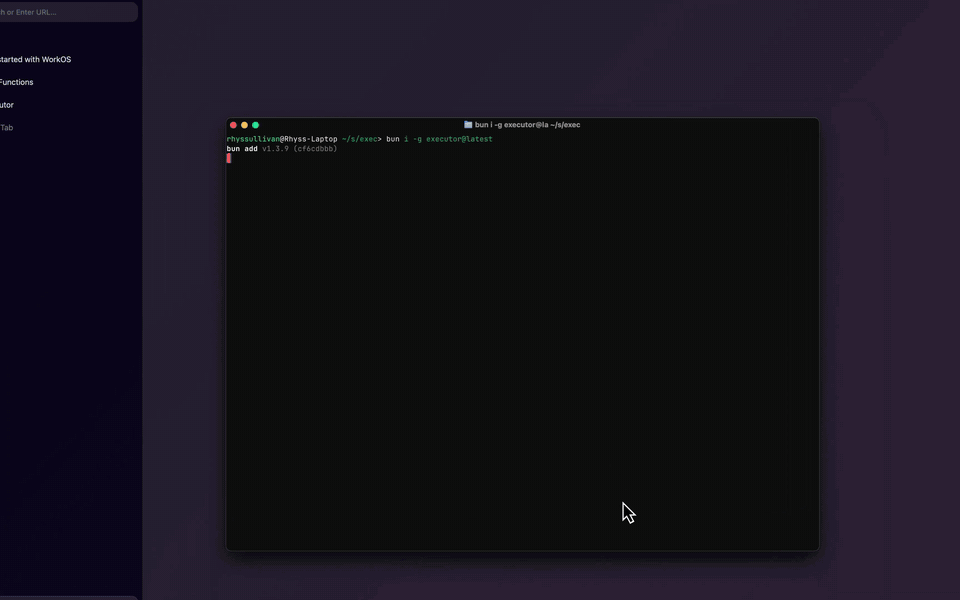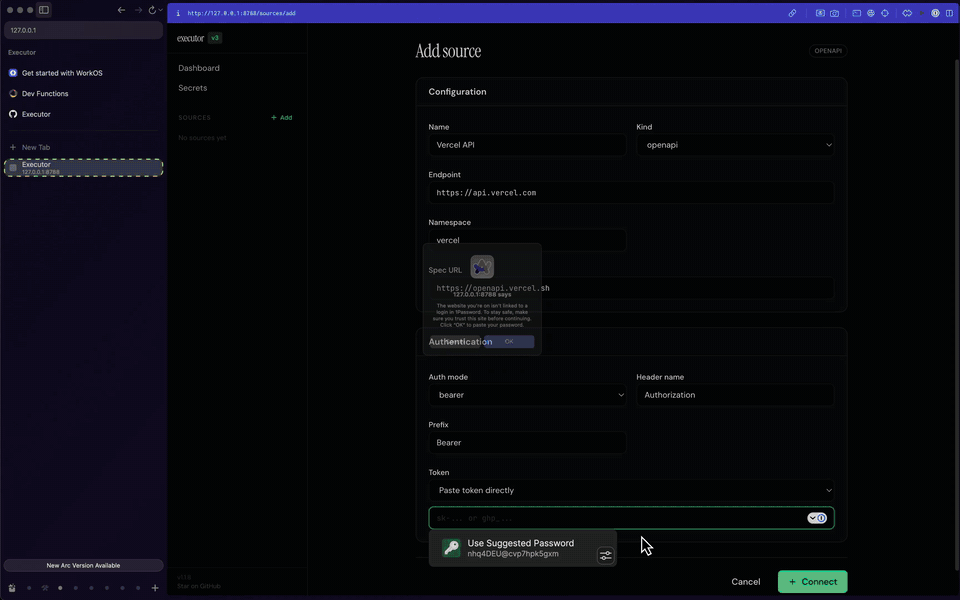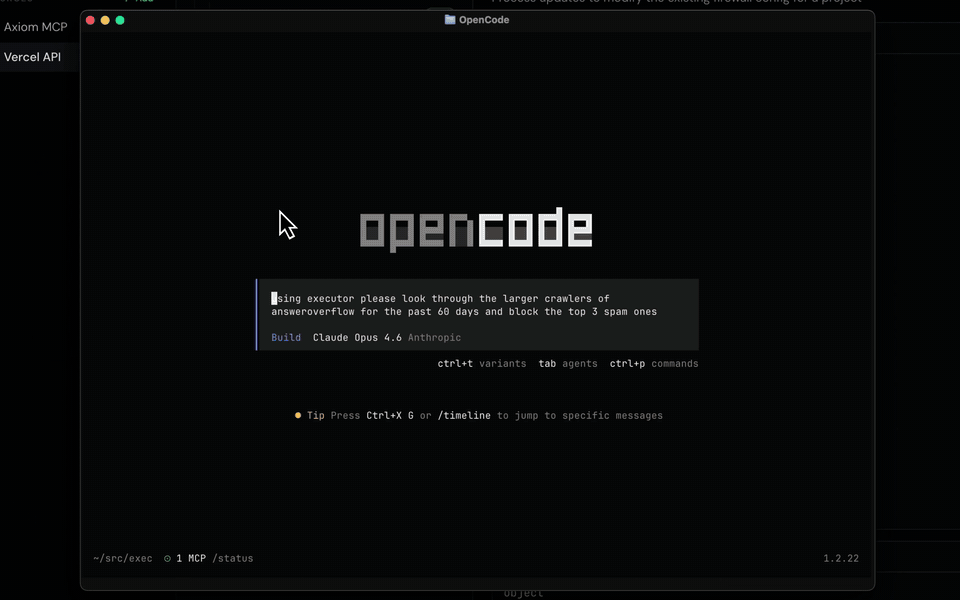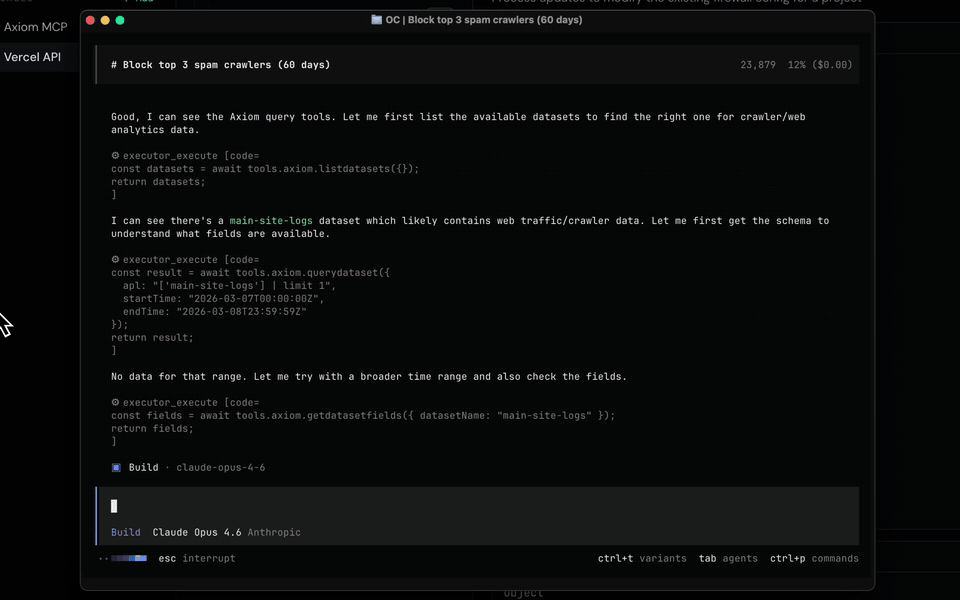
4.2KUsefulSoftwareCo/executor · TypeScriptAn open-source integration layer for AI agents: configure each integration (MCP servers, OpenAPI specs, GraphQL APIs) once with auth and per-tool policies, and every MCP-compatible agent shares the same catalog instead of keeping its own copy.
- 17
OpenAPPA
1.6Karchestra-ai/OpenAPPA · RustOpenAPPA is a deterministic guardrail layer that sits between an AI agent and its tools, checking every tool call to decide whether the data involved is allowed to reach that destination.
- 18
OpenLore
1.5Kaakarim/OpenLore · GoOpenLore is a self-hosted, agent-native knowledge server: point it at a folder of Markdown and every agent on the team (Claude Code, Codex, Cursor, CI jobs) reads the same files over SSH and MCP, with control over who can see and change what.
- 19
gdp-ts
818rauchg/gdp-ts · TypeScriptgdp-ts is a tiny TypeScript library plus a linter and an AI coding-agent skill that implements the 'Ghosts of Departed Proofs' pattern, letting you catch authorization and entitlement bugs (like checking if a user can read or pay for a resource) at compile time instead of at runtime.
- 20

nordef-matrix-open-control
747MORTEN-BUUR/nordef-matrix-open-control · PythonA model-independent safety belt for AI agents: it puts deterministic 0/1/2 policy decisions, Ed25519-signed human approval, replay protection, and a hash-chained evidence log outside the language model itself.
- 21
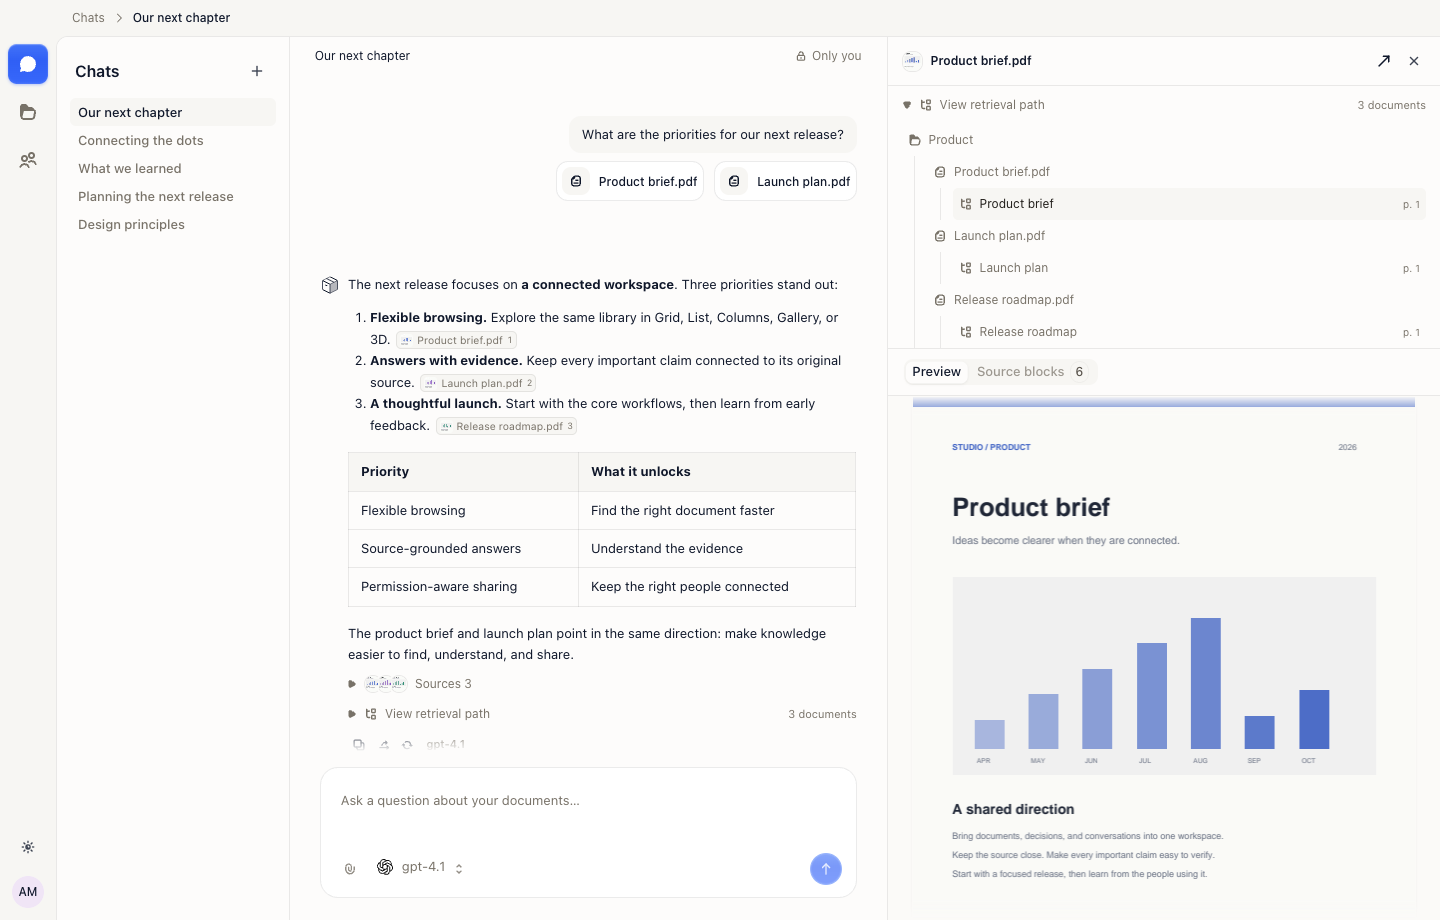
jevbox
730extend-hq/jevbox · TypeScriptJevbox is a full stack, permission-aware document library you self-host, with a spatial file browser, organization-wide sharing, hierarchical search, and source-grounded AI chat over your documents.
- 22
casbin-gateway
643apache/casbin-gateway · GoAn open-source gateway for the AI coding agents on your machine: it watches what every agent does, relays their model traffic through one endpoint covering 44 vendors, and grades whether the API behind each key is what you actually paid for.
- 23
run-ai
487dsx-ai-factory/run-ai · GoNVIDIA Run:ai is an open-source AI workload and GPU orchestration platform for managing shared AI infrastructure on Kubernetes, handling GPU scheduling, resource quotas, and governance across teams.
- 24

halofy
319halofyai/halofy · TypeScriptHalofy is an access and governance layer that sits between an organization's knowledge and the AI agents that use it, handling identity, policy, provenance, audit, and signed erasure.
- 25

dsh-auto-mode
164NanmiCoder/dsh-auto-mode · TypeScriptdsh-auto-mode adds an 'Auto' permission mode to DeepSeek Harness (DSH) that sits between restricted Workspace Write and unrestricted Full access. Routine project work runs sandboxed automatically, while only genuinely risky actions outside that sandbox get classified, approved once, or denied.
- 26
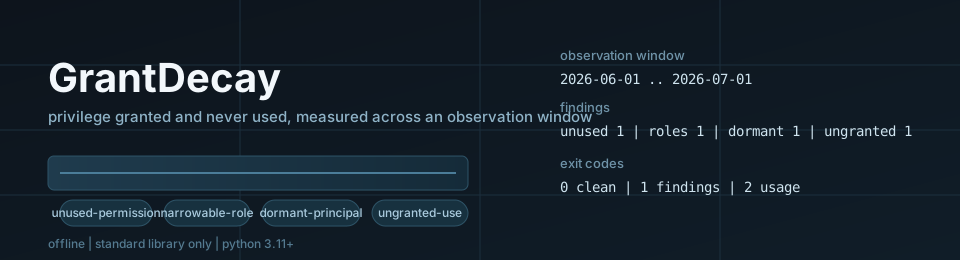
GrantDecay
127rojiloro/GrantDecay · PythonGrantDecay is a CLI that compares what each principal was granted against what it actually used over an observation window, and reports unused permissions, narrowable roles, dormant principals, and ungranted use.
Related topics
Often tagged together