这是什么?
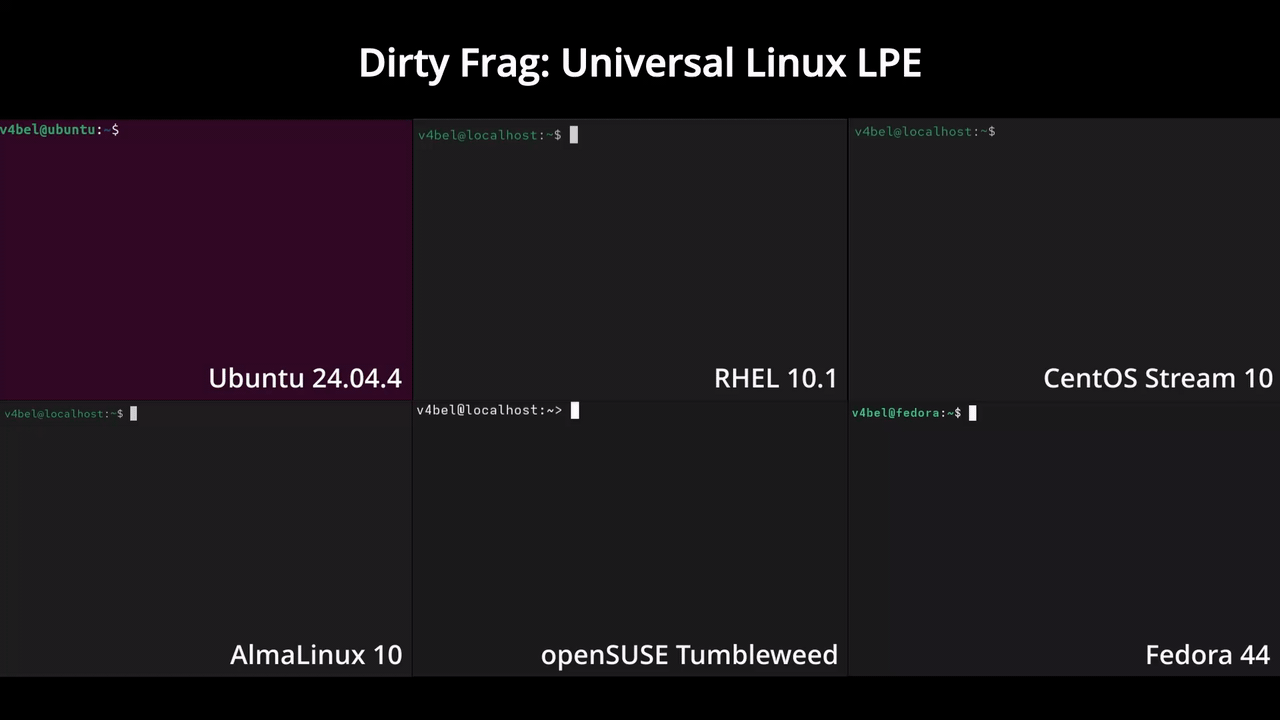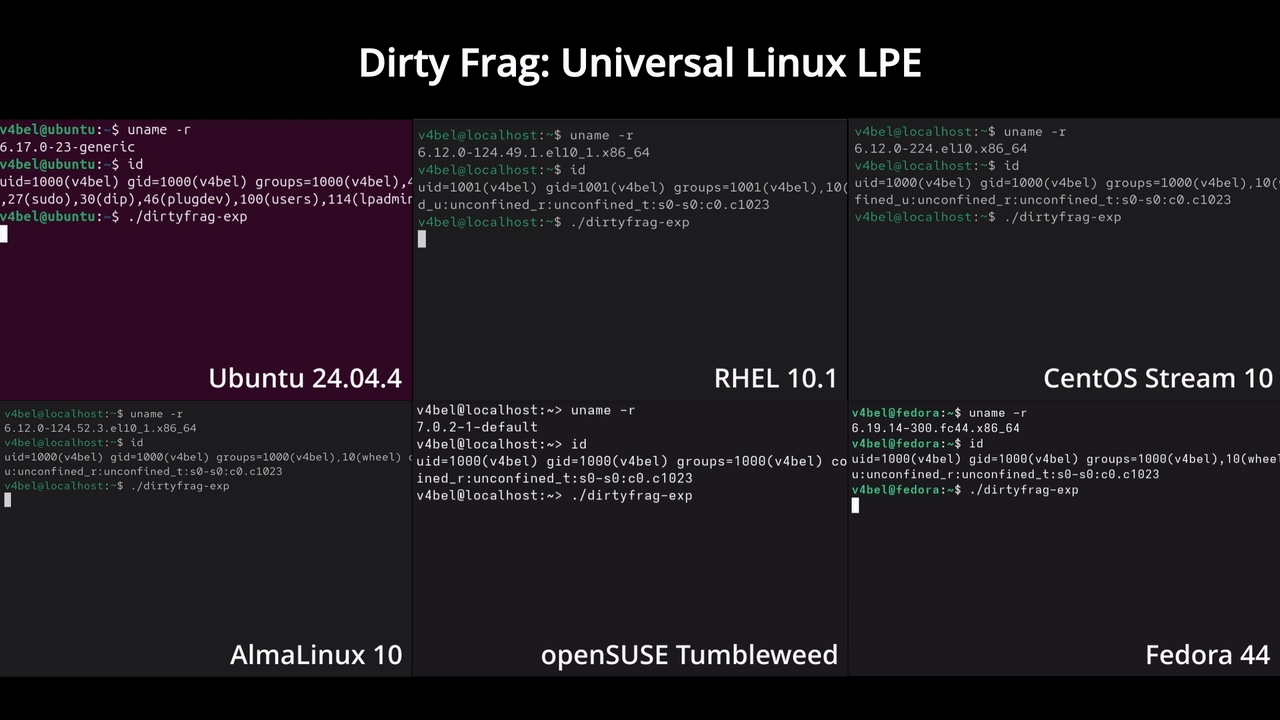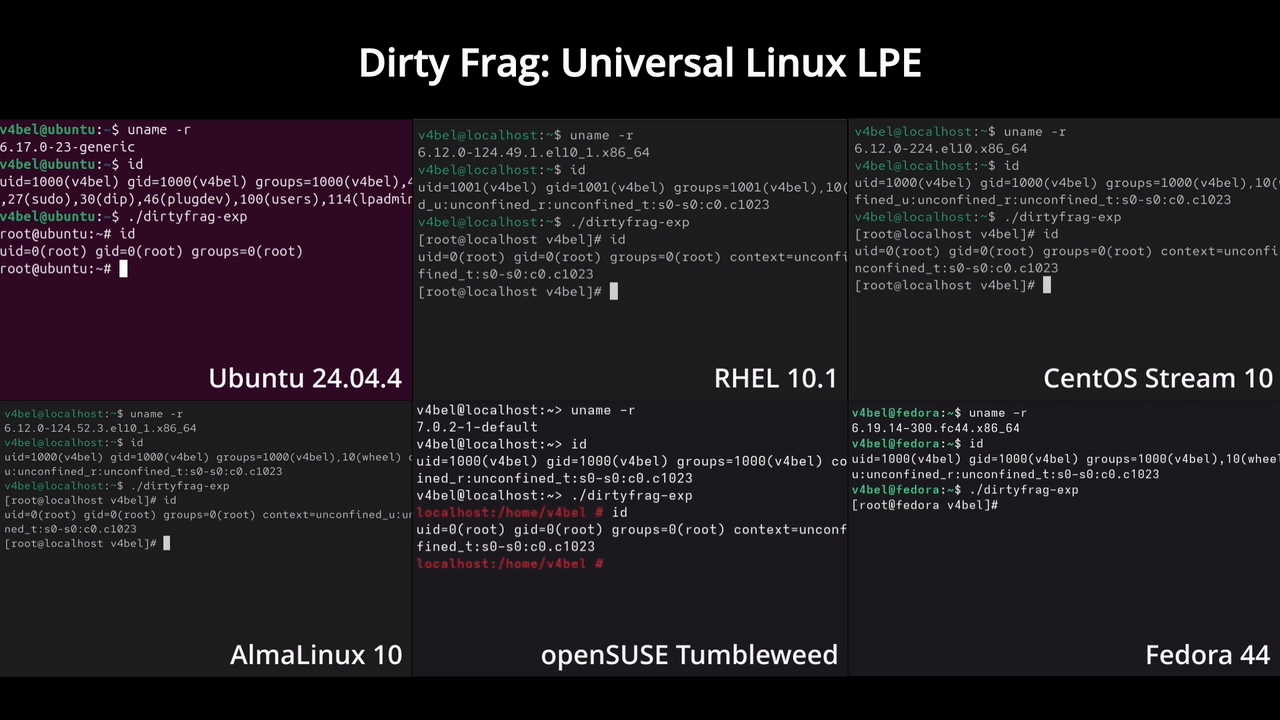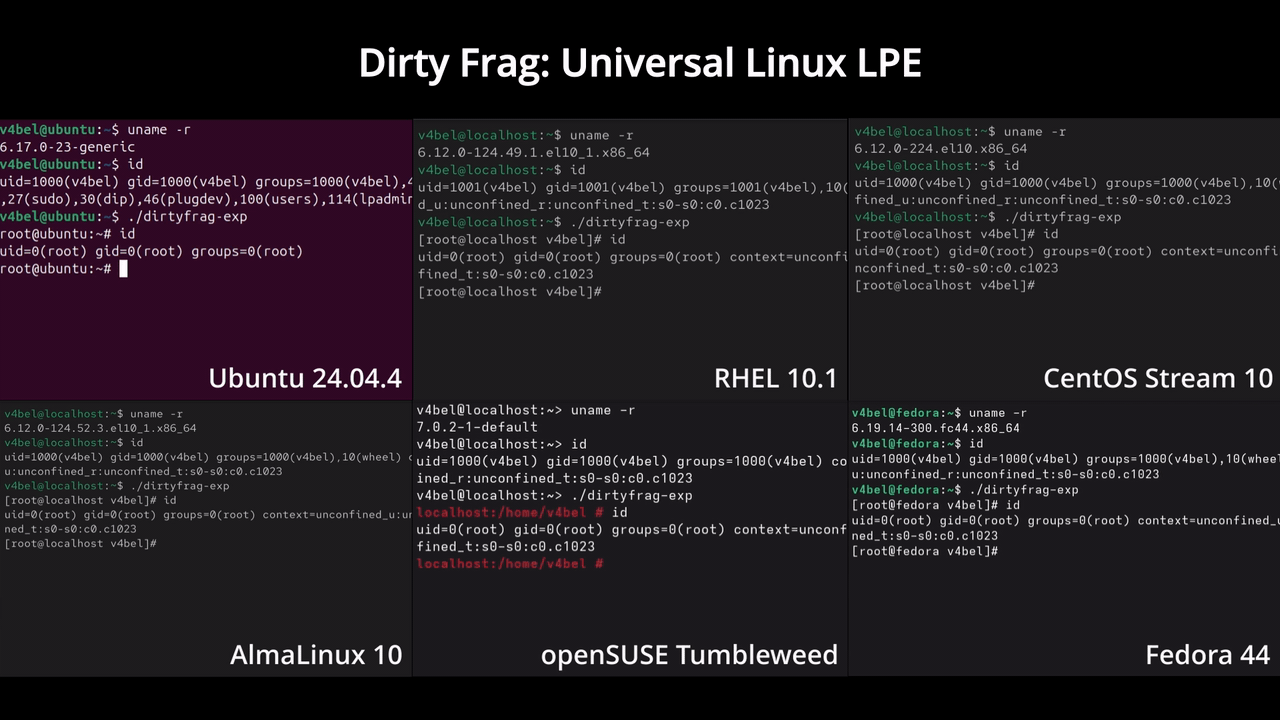
 Dirty Frag 是一个 Linux 内核本地提权概念验证(PoC)漏洞利用,串联两个页缓存写入漏洞(CVE-2026-43284 和 CVE-2026-43500),在主流 Linux 发行版上获取 root。
这是一个拿来就能跑的漏洞利用工具,还是只是技术分析文章?两者都是:既是一个可用的 PoC 漏洞利用,也附带一份描述该漏洞类型的研究文档;它是对与 Dirty Pipe 和 Copy Fail 相同漏洞家族的延伸。
两者都是:既是一个可用的 PoC 漏洞利用,也附带一份描述该漏洞类型的研究文档;它是对与 Dirty Pipe 和 Copy Fail 相同漏洞家族的延伸。这个漏洞利用怎么运行?针对受影响版本范围内存在漏洞的内核编译附带的 PoC,然后在你拥有或获准评估的系统上作为授权测试运行它。
针对受影响版本范围内存在漏洞的内核编译附带的 PoC,然后在你拥有或获准评估的系统上作为授权测试运行它。这个漏洞利用需要什么权限?xfrm-ESP 原语需要创建用户命名空间的权限(在 Ubuntu 上有时会被 AppArmor 策略阻止);RxRPC 原语不需要命名空间权限,但依赖 rxrpc.ko 模块已加载,Ubuntu 默认就会加载它。
xfrm-ESP 原语需要创建用户命名空间的权限(在 Ubuntu 上有时会被 AppArmor 策略阻止);RxRPC 原语不需要命名空间权限,但依赖 rxrpc.ko 模块已加载,Ubuntu 默认就会加载它。运行它之后我的系统会处于糟糕状态吗?会。运行该漏洞利用会污染页缓存;你必须运行提供的清理命令或重启系统才能恢复稳定。
会。运行该漏洞利用会污染页缓存;你必须运行提供的清理命令或重启系统才能恢复稳定。它实际在哪些发行版上测试过?已在 Ubuntu 24.04.4、RHEL 10.1、openSUSE Tumbleweed、CentOS Stream 10、AlmaLinux 10 和 Fedora 44 上验证,基本覆盖了所有主流 Linux 发行版。
已在 Ubuntu 24.04.4、RHEL 10.1、openSUSE Tumbleweed、CentOS Stream 10、AlmaLinux 10 和 Fedora 44 上验证,基本覆盖了所有主流 Linux 发行版。为什么串联两个不同的漏洞,而不是只用一个?每个原语在某些发行版上都有盲区:xfrm-ESP 需要创建命名空间(Ubuntu 的 AppArmor 会阻止),RxRPC 需要 rxrpc.ko 模块(除 Ubuntu 外大多数发行版都缺)。两者串联可以互补缺口,因此在哪都能拿到 root。
每个原语在某些发行版上都有盲区:xfrm-ESP 需要创建命名空间(Ubuntu 的 AppArmor 会阻止),RxRPC 需要 rxrpc.ko 模块(除 Ubuntu 外大多数发行版都缺)。两者串联可以互补缺口,因此在哪都能拿到 root。这和 Copy Fail 漏洞有什么关系?Copy Fail 启发了这项研究,且 xfrm-ESP 原语与 Copy Fail 使用相同的内存汇(memory sink),但即使应用了公开的 Copy Fail 缓解措施(将 algifaead 列入黑名单),它依然有效,因此针对 Copy Fail 打过补丁的系统仍然易受攻击。
Copy Fail 启发了这项研究,且 xfrm-ESP 原语与 Copy Fail 使用相同的内存汇(memory sink),但即使应用了公开的 Copy Fail 缓解措施(将 algifaead 列入黑名单),它依然有效,因此针对 Copy Fail 打过补丁的系统仍然易受攻击。如果失败,漏洞利用会让内核崩溃吗?不会。Dirty Frag 是确定性的逻辑漏洞而非竞态条件,不依赖时间窗口,尝试失败也不会导致内核崩溃(panic),因此成功率非常高。
不会。Dirty Frag 是确定性的逻辑漏洞而非竞态条件,不依赖时间窗口,尝试失败也不会导致内核崩溃(panic),因此成功率非常高。怎么保护我的系统免受这个漏洞影响?作为紧急缓解措施,移除受影响的内核模块(xfrm/ESP 和 RxRPC)并清空页缓存,然后在各发行版的向后移植补丁可用后及时应用。
作为紧急缓解措施,移除受影响的内核模块(xfrm/ESP 和 RxRPC)并清空页缓存,然后在各发行版的向后移植补丁可用后及时应用。What are similar projects?skitter-creek-bath-salts, UniRoot, Claude-Red, copy-fail-CVE-2026-31431, exploitarium, ghostlock-app, CVE-2026-62911, Relapse-Exploit
skitter-creek-bath-salts, UniRoot, Claude-Red, copy-fail-CVE-2026-31431, exploitarium, ghostlock-app, CVE-2026-62911, Relapse-ExploitWhich topics is it in?vulnerability-research, poc, exploitation, cve, exploit-development, privilege-escalation, linux-kernel, security-research, infosec, vulnerability, exploit, kernel
vulnerability-research, poc, exploitation, cve, exploit-development, privilege-escalation, linux-kernel, security-research, infosec, vulnerability, exploit, kernel