Что это?
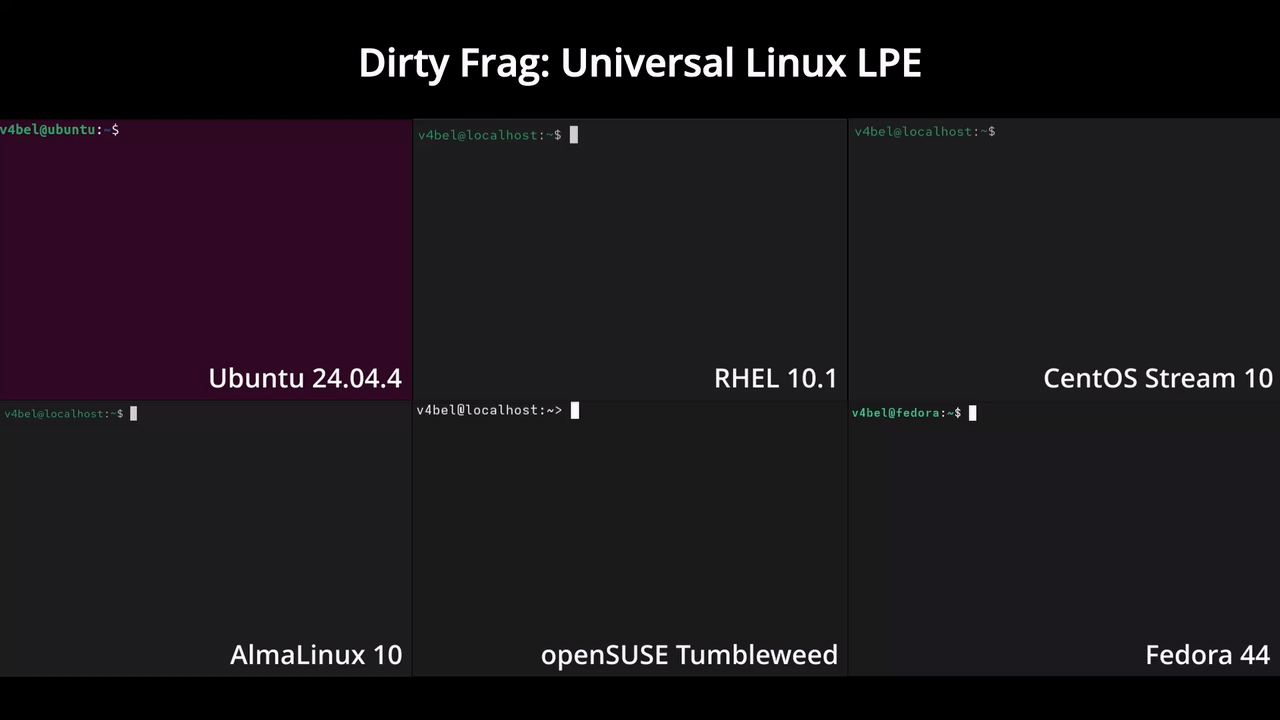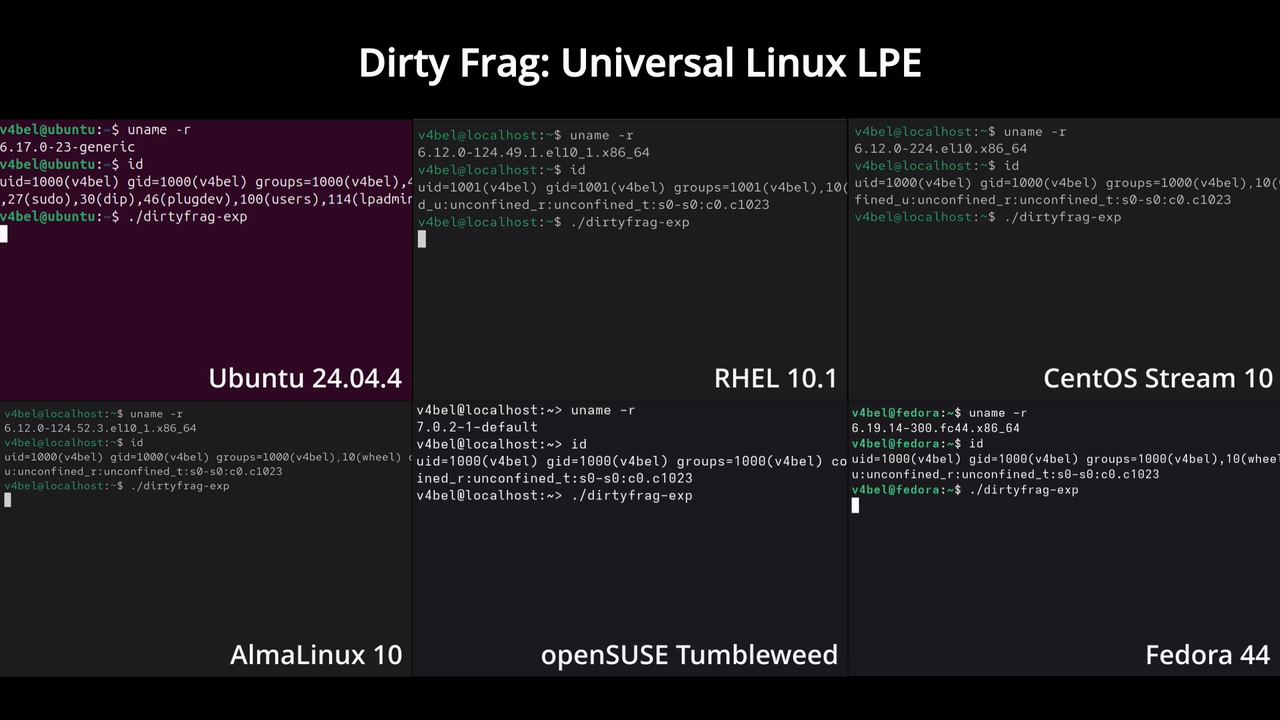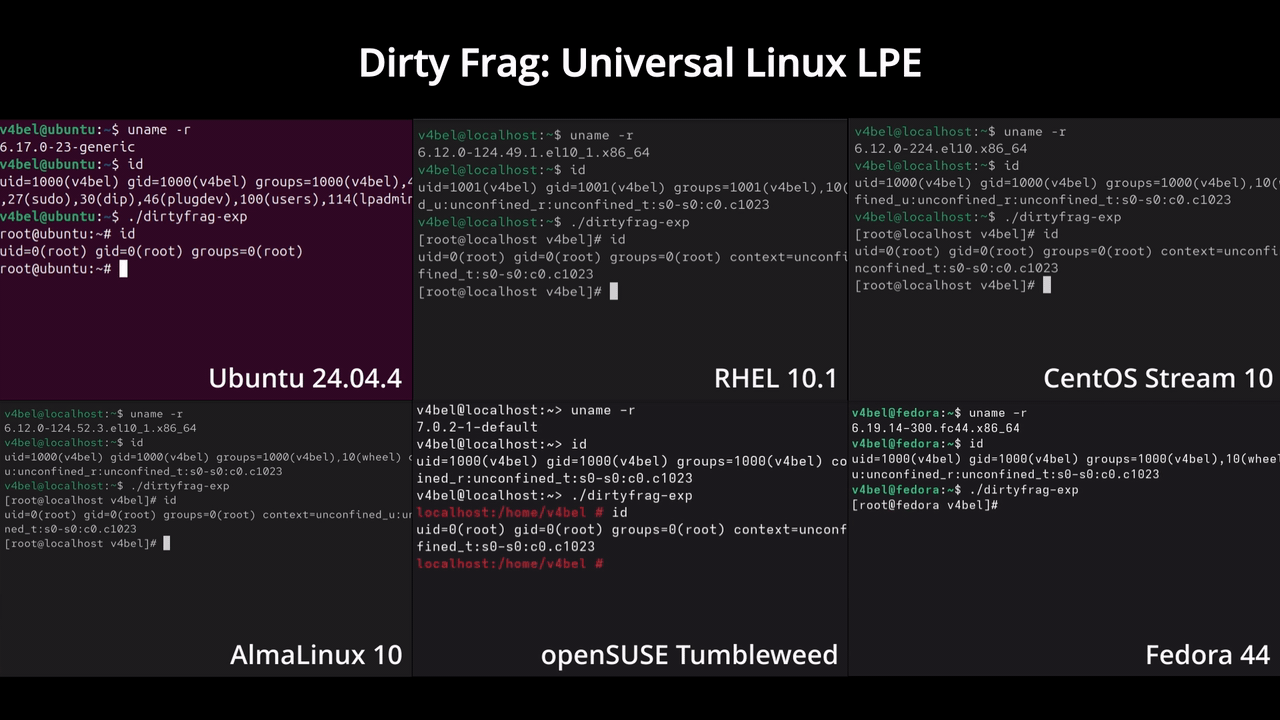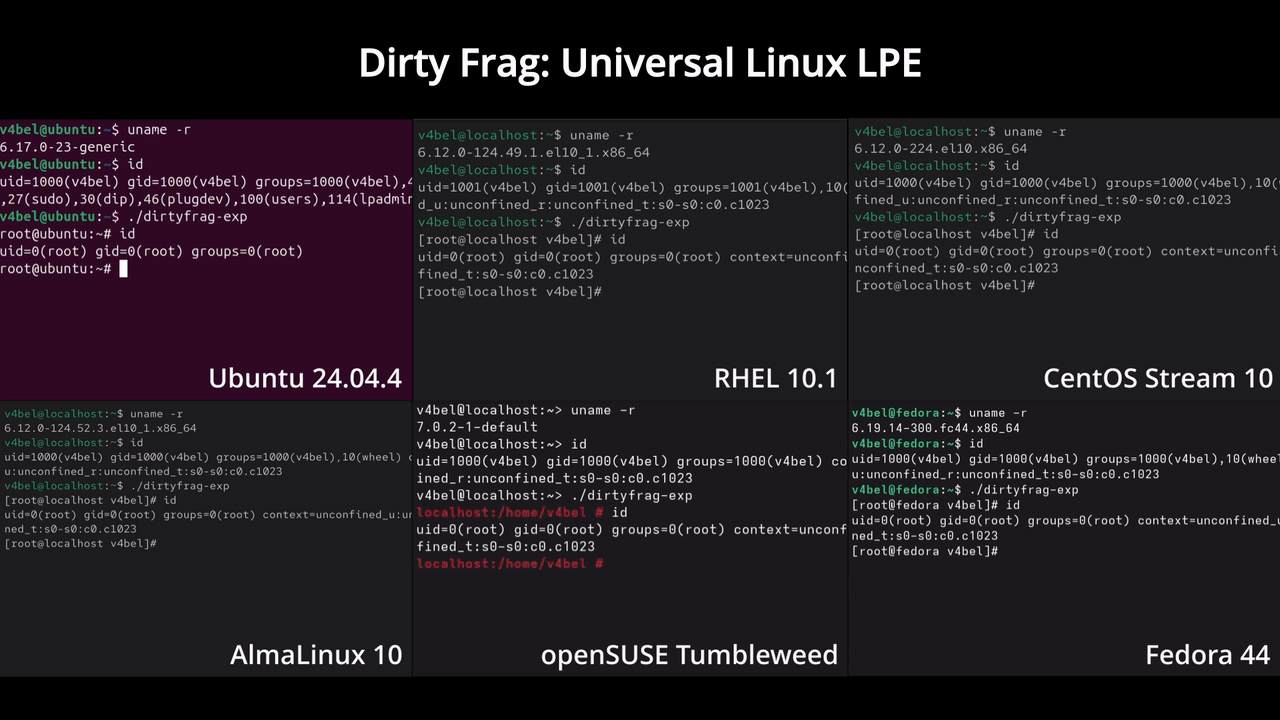
 Dirty Frag — это PoC-эксплойт локального повышения привилегий для ядра Linux, объединяющий в цепочку две уязвимости записи в page cache (CVE-2026-43284 и CVE-2026-43500), чтобы получить root на основных Linux-дистрибутивах.
Это готовый к запуску инструмент-эксплойт или просто технический разбор?И то и другое: рабочий PoC-эксплойт и сопровождающий исследовательский документ, описывающий класс уязвимостей, который расширяет то же семейство багов, что Dirty Pipe и Copy Fail.
И то и другое: рабочий PoC-эксплойт и сопровождающий исследовательский документ, описывающий класс уязвимостей, который расширяет то же семейство багов, что Dirty Pipe и Copy Fail.Как запустить эксплойт?Соберите включённый в репозиторий PoC под уязвимое ядро из затронутого диапазона версий, затем запустите его как санкционированный тест на системе, которой владеете или на проверку которой имеете разрешение.
Соберите включённый в репозиторий PoC под уязвимое ядро из затронутого диапазона версий, затем запустите его как санкционированный тест на системе, которой владеете или на проверку которой имеете разрешение.Какие привилегии нужны эксплойту?Примитиву xfrm-ESP нужна возможность создавать user namespace (иногда блокируется политикой AppArmor в Ubuntu), а примитиву RxRPC привилегии на namespace не нужны, но требуется, чтобы был загружен модуль rxrpc.ko, что Ubuntu делает по умолчанию.
Примитиву xfrm-ESP нужна возможность создавать user namespace (иногда блокируется политикой AppArmor в Ubuntu), а примитиву RxRPC привилегии на namespace не нужны, но требуется, чтобы был загружен модуль rxrpc.ko, что Ubuntu делает по умолчанию.Не оставит ли запуск моей системы в плохом состоянии после себя?Да, запуск эксплойта «загрязняет» page cache; нужно либо выполнить прилагаемую команду очистки, либо перезагрузить систему, чтобы вернуть стабильность.
Да, запуск эксплойта «загрязняет» page cache; нужно либо выполнить прилагаемую команду очистки, либо перезагрузить систему, чтобы вернуть стабильность.На каких дистрибутивах это реально проверялось?Проверено на Ubuntu 24.04.4, RHEL 10.1, openSUSE Tumbleweed, CentOS Stream 10, AlmaLinux 10 и Fedora 44 — то есть практически на каждом крупном Linux-дистрибутиве.
Проверено на Ubuntu 24.04.4, RHEL 10.1, openSUSE Tumbleweed, CentOS Stream 10, AlmaLinux 10 и Fedora 44 — то есть практически на каждом крупном Linux-дистрибутиве.Зачем объединять в цепочку две разные уязвимости вместо одной?У каждого примитива есть слепая зона на отдельных дистрибутивах: xfrm-ESP требует создания namespace (блокируется AppArmor в Ubuntu), а RxRPC нужен модуль rxrpc.ko (его нет в большинстве дистрибутивов, кроме Ubuntu). Связка обоих закрывает пробелы друг друга, так что root достижим везде.
У каждого примитива есть слепая зона на отдельных дистрибутивах: xfrm-ESP требует создания namespace (блокируется AppArmor в Ubuntu), а RxRPC нужен модуль rxrpc.ko (его нет в большинстве дистрибутивов, кроме Ubuntu). Связка обоих закрывает пробелы друг друга, так что root достижим везде.Как это связано с уязвимостью Copy Fail?Copy Fail вдохновила это исследование, и примитив xfrm-ESP использует тот же «сток» в памяти, что и Copy Fail, но он срабатывает даже при применении публичной защиты от Copy Fail (внесении algifaead в чёрный список), так что системы, пропатченные против Copy Fail, остаются уязвимы.
Copy Fail вдохновила это исследование, и примитив xfrm-ESP использует тот же «сток» в памяти, что и Copy Fail, но он срабатывает даже при применении публичной защиты от Copy Fail (внесении algifaead в чёрный список), так что системы, пропатченные против Copy Fail, остаются уязвимы.Крашит ли эксплойт ядро, если не сработал?Нет, Dirty Frag — это детерминированный логический баг, а не состояние гонки, поэтому не требует временных окон, и ядро не паникует при неудачной попытке, что даёт очень высокий процент успеха.
Нет, Dirty Frag — это детерминированный логический баг, а не состояние гонки, поэтому не требует временных окон, и ядро не паникует при неудачной попытке, что даёт очень высокий процент успеха.Как защитить свою систему от этого?В качестве немедленной меры удалите затронутые модули ядра (xfrm/ESP и RxRPC) и очистите page cache, а затем, когда они появятся, установите бэкпортированные патчи своего дистрибутива.
В качестве немедленной меры удалите затронутые модули ядра (xfrm/ESP и RxRPC) и очистите page cache, а затем, когда они появятся, установите бэкпортированные патчи своего дистрибутива.What are similar projects?skitter-creek-bath-salts, CVE-2026-41940-PoC, UniRoot, Claude-Red, copy-fail-CVE-2026-31431, exploitarium, ghostlock-app, DirtyFrag
skitter-creek-bath-salts, CVE-2026-41940-PoC, UniRoot, Claude-Red, copy-fail-CVE-2026-31431, exploitarium, ghostlock-app, DirtyFragWhich topics is it in?vulnerability-research, poc, exploitation, cve, exploit-development, privilege-escalation, linux-kernel, security-research, infosec, vulnerability, exploit, offensive-security
vulnerability-research, poc, exploitation, cve, exploit-development, privilege-escalation, linux-kernel, security-research, infosec, vulnerability, exploit, offensive-security