By the Swiss Applied AI & Cybersecurity Research Lab
Backed by
0security is software infrastructure to deploy sovereign, persistent AI security agents that find and fix security risks across any tech stack, work with any model, and run anywhere.
export OPENAI_API_KEY="your-api-key"
0 threads send new "Review ./your-repo for security problems"
0 findings list
Any supported provider works: set its key instead (Anthropic, OpenRouter, DeepSeek and more, see Models), or connect one in the browser with 0.
Windows, Docker and source installs
Windows (experimental): download 0-windows-x64.exe from Releases.
Docker: docker run --rm ghcr.io/0sec-labs/0security:latest --help. See the Docker guide.
Source: Node.js 24+ and pnpm, then pnpm install --frozen-lockfile && pnpm build.
install.sh supports Apple Silicon macOS and x64/ARM64 Linux. Set INSTALL_DIR to change the location.
Only point 0 at systems you own or are authorized to test.
What can you do with 0?
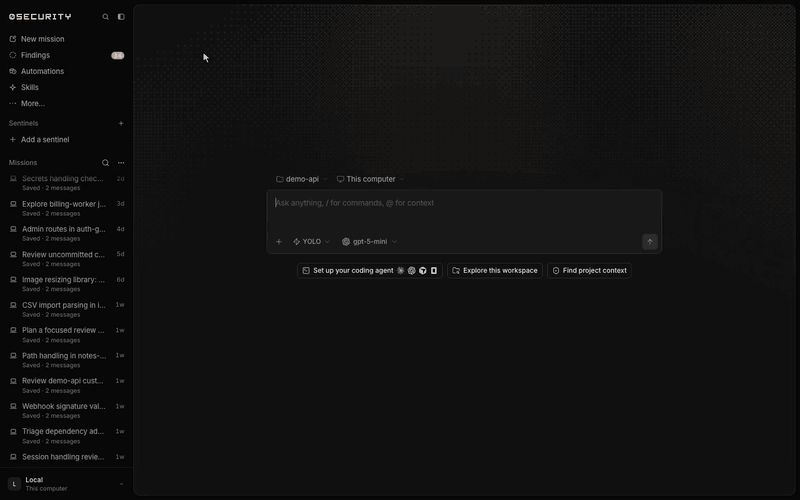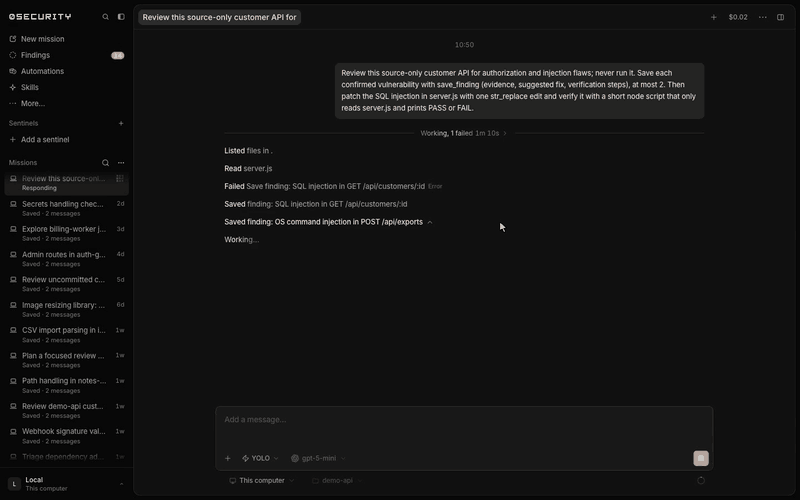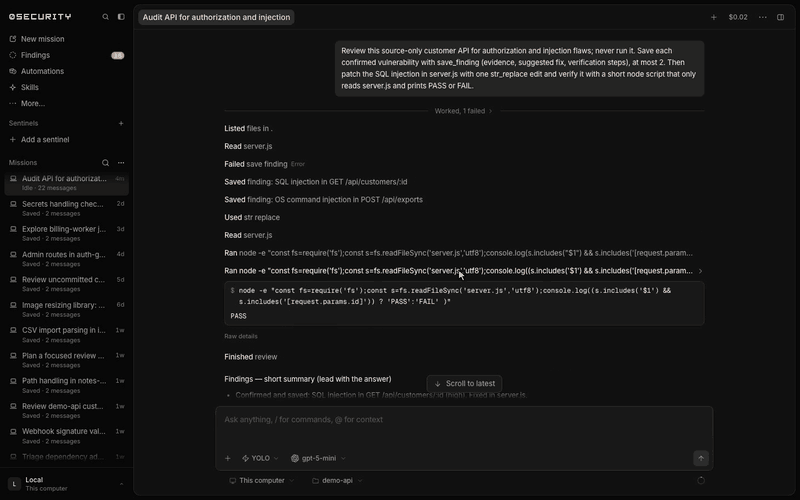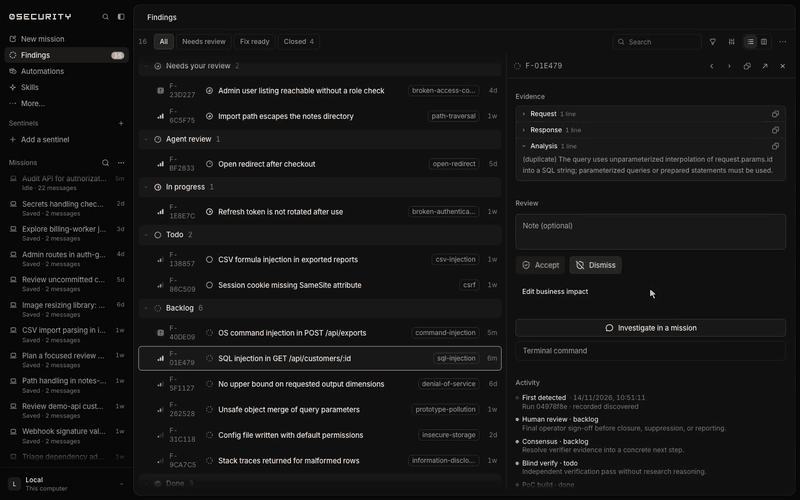
Talk to a security agent about a folder on your computer or a remote Computer, in a Thread
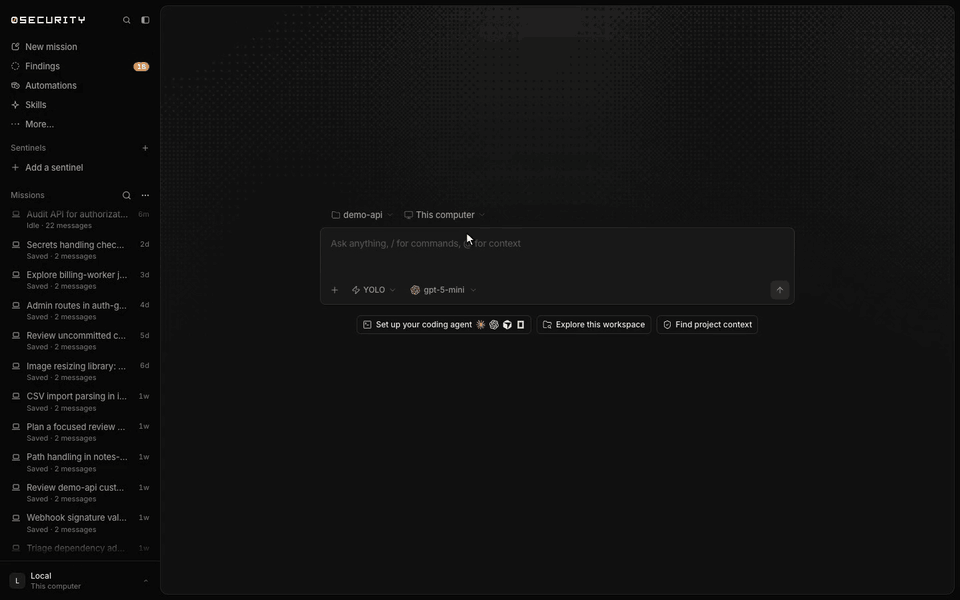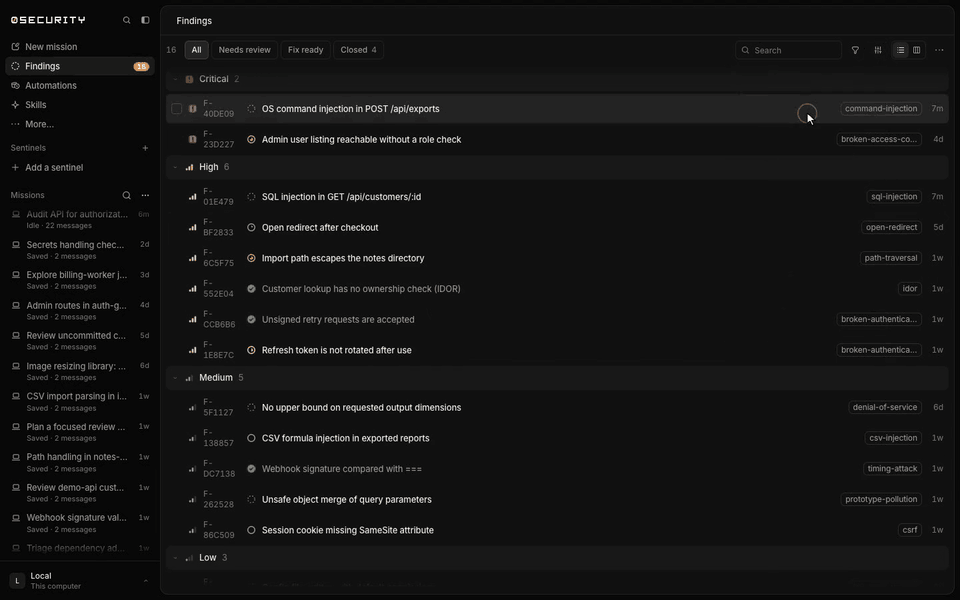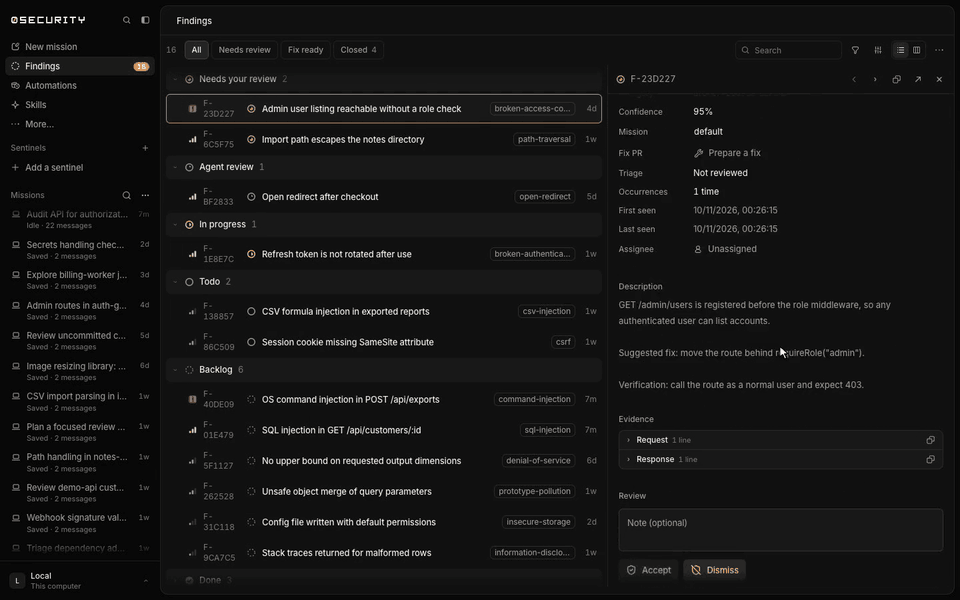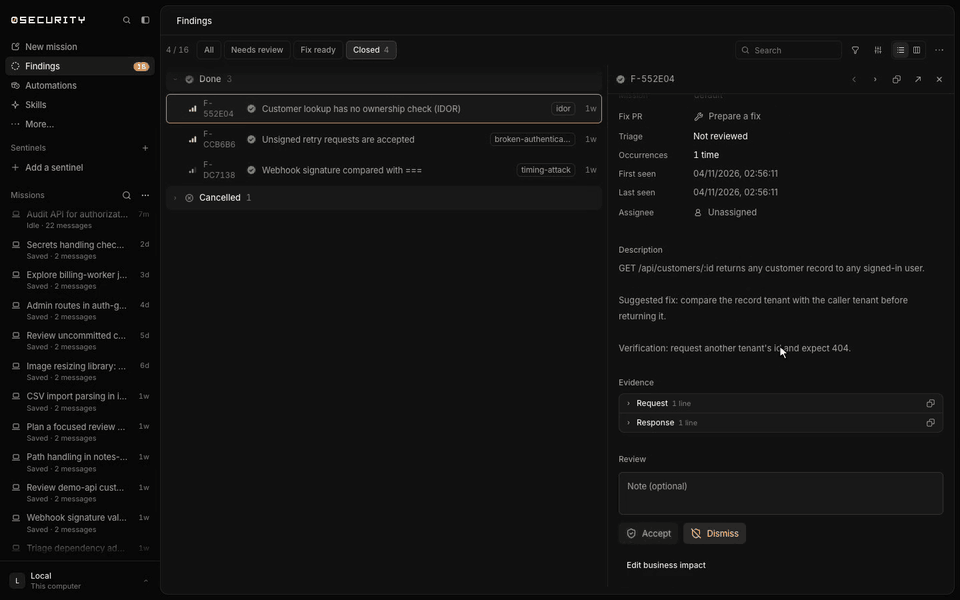
Review findings on a board, with source evidence, and export them
Verify fixes: a finding is marked Verified by or Not verified
Build persistent security agents: Sentinels are standing threads that wake on a schedule or on every pull request, with skills, memory and automations written as prompts
Keep memory as plain notes that every thread can read




 0 是一个用于安全研究的开源、自我演进、多模型 AI 框架,能够发现、验证并修复漏洞,由瑞士应用 AI 与网络安全研究实验室构建。